LinkedIn thought leader ad examples
130 thought leader ads are live on LinkedIn right now, from 138 companies. Browse real ones, filtered by industry.
- Concentric AIRecorded 14 Sept 2026
GenAI is accelerating faster than most organizations’ data-security programs and that gap is becoming a board-level risk. Read our article on what enterprises can do to address it - https://lnkd.in/g7Dw7wrF * Traditional data-security models no longer apply. GenAI introduces new exposure paths (prompts, shadow AI use, inadvertent data leakage) that legacy DLP and policy checklists can’t detect. * Quantifying risk is not optional. Executives need visibility into what data is being exposed, by whom, and the financial impact of potential misuse, enabling informed decisions, not blanket restrictions. * Data hygiene is now a strategic imperative. You can’t secure GenAI workflows without knowing what data you have, where it resides, and who can access it. * Governance should enable innovation, not slow it. Clear guardrails, monitored usage, and role-based controls let teams adopt GenAI safely while preserving speed and productivity. Bottom line: GenAI adoption is inevitable but unmanaged risk isn't. Leadership must modernize data-security governance now to protect the business while unlocking AI’s competitive upside.
- Brooklyn PartnersSince 30 Aug 2026
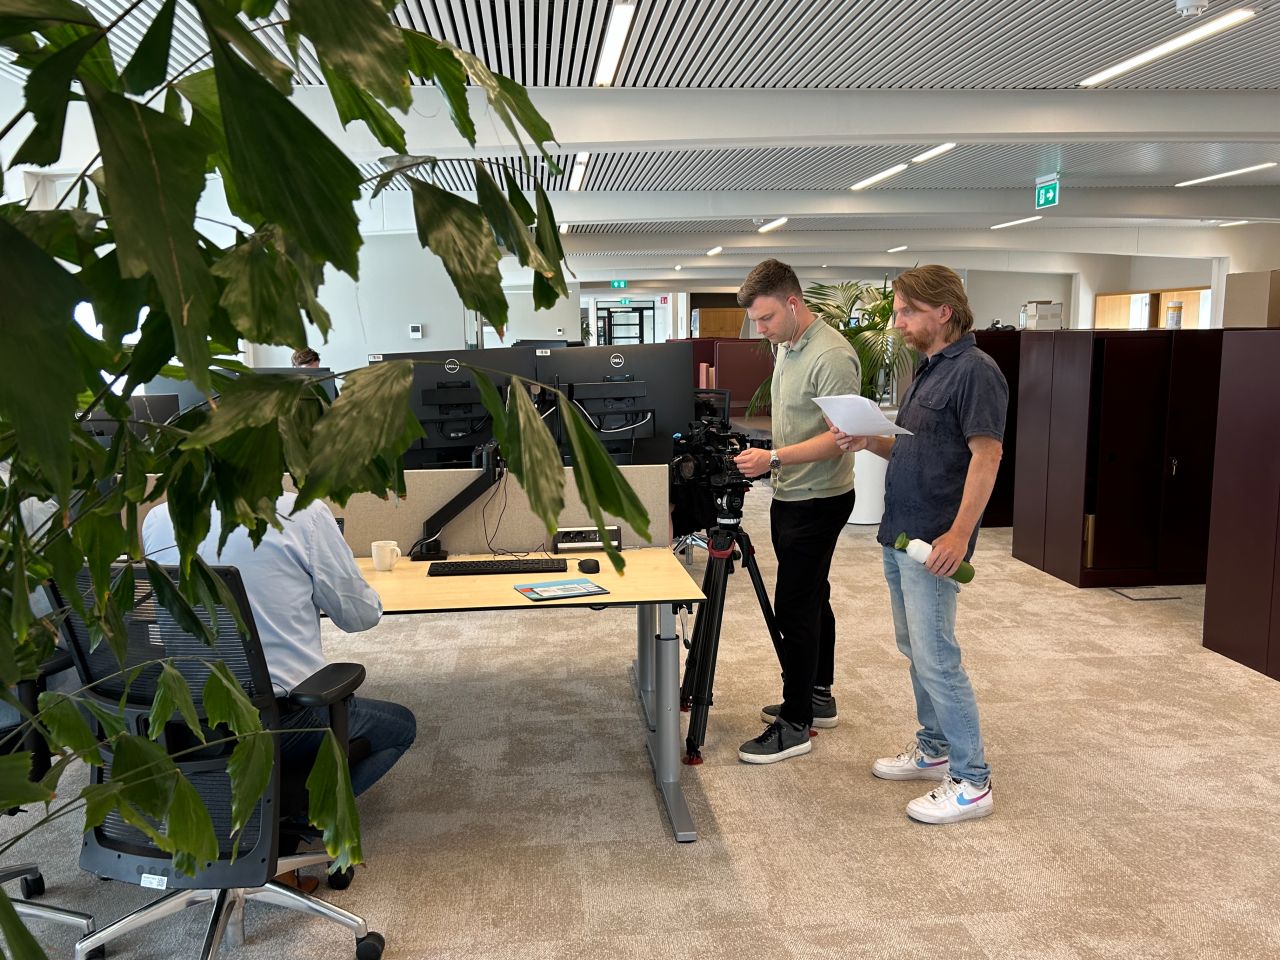
Met veel lokale enthousiaste figuranten nam Arnout Cornelissen vorige week het gemeentehuis van Gemeente Apeldoorn over, voor de opnamen van de Study Clips over het herkennen van phishing. Bedankt voor deze fijne samenwerking Mitchell Van der Hoef van Video Huys.
- BlockaidSince 29 Sept 2025
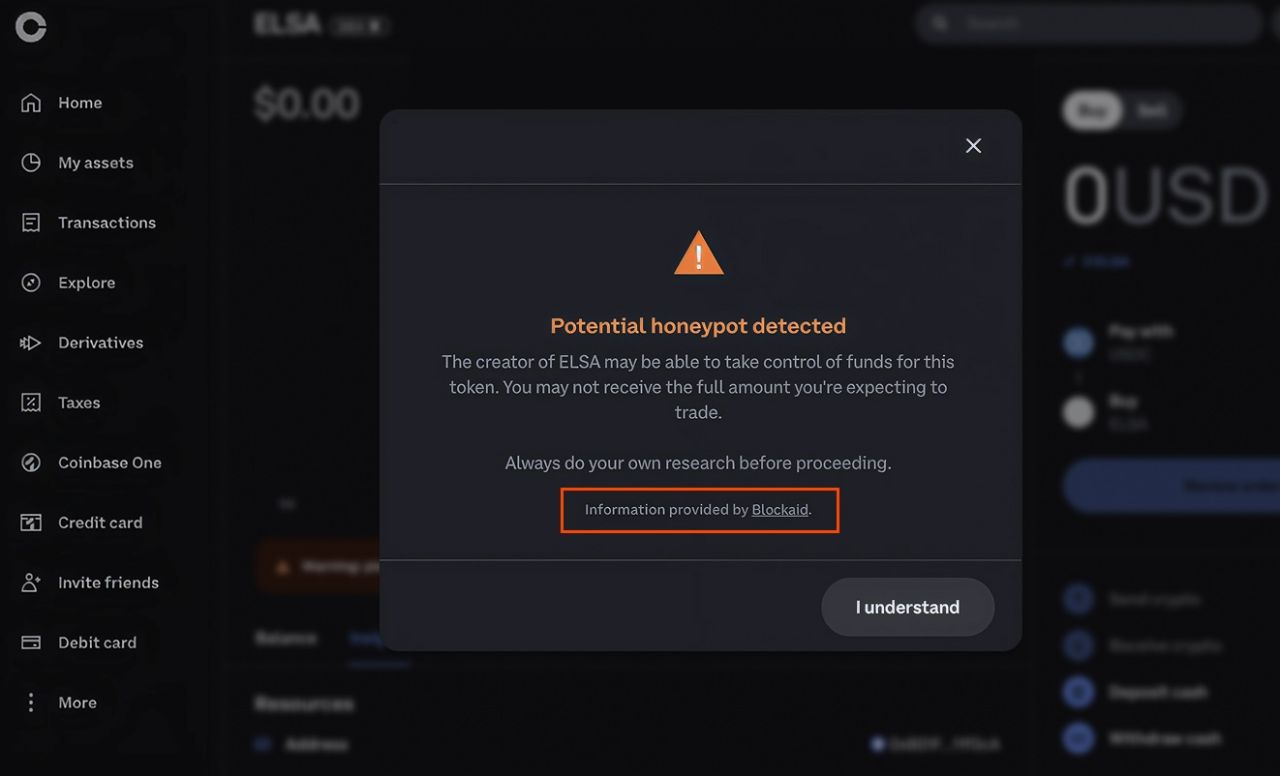
When users trade on Coinbase, malicious tokens now trigger a Blockaid-powered warning. Scanning for honeypots, rug pulls, spoofed tokens, and wallet drainers before users sign. Together, Coinbase and Blockaid are protecting users in the moments that matter most.
- Bfore | The PreCrime™ CompanyRecorded 10 Sept 2026
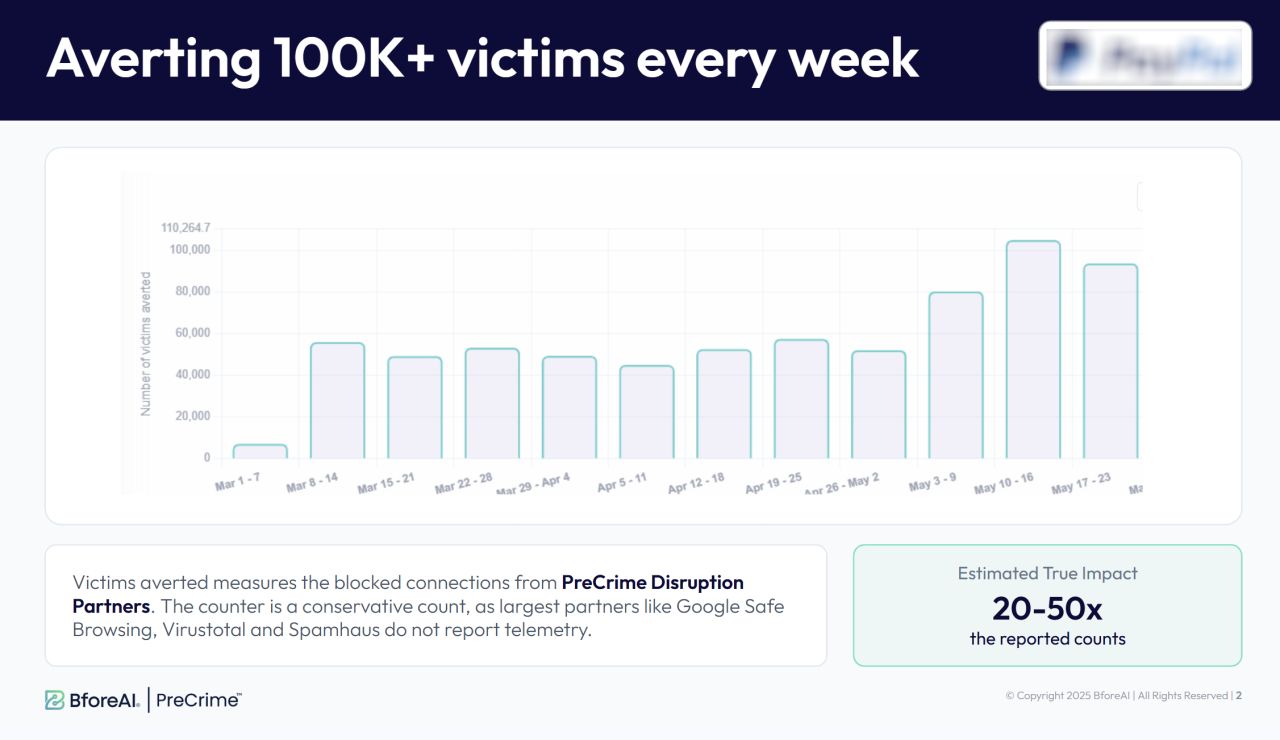
We recently signed as new customer a leading fintech ... and yesterday had a review with their CISO..... hearing the satisfaction form his team on reduction of false positives, increased automation and overall impact ... another raving fan for #victimsaverted ROI measure embedded in #PreCrime Extremely proud of what the whole team is deliverying daily , and so motivated to keep pushing as each day we avoid more and more cyberfraud and cybercrime victims. Crime Stoppers International World Economic Forum Cybersecurity FinTech Innovation Lab Google for Startups
- Base OperationsRecorded 10 Sept 2026
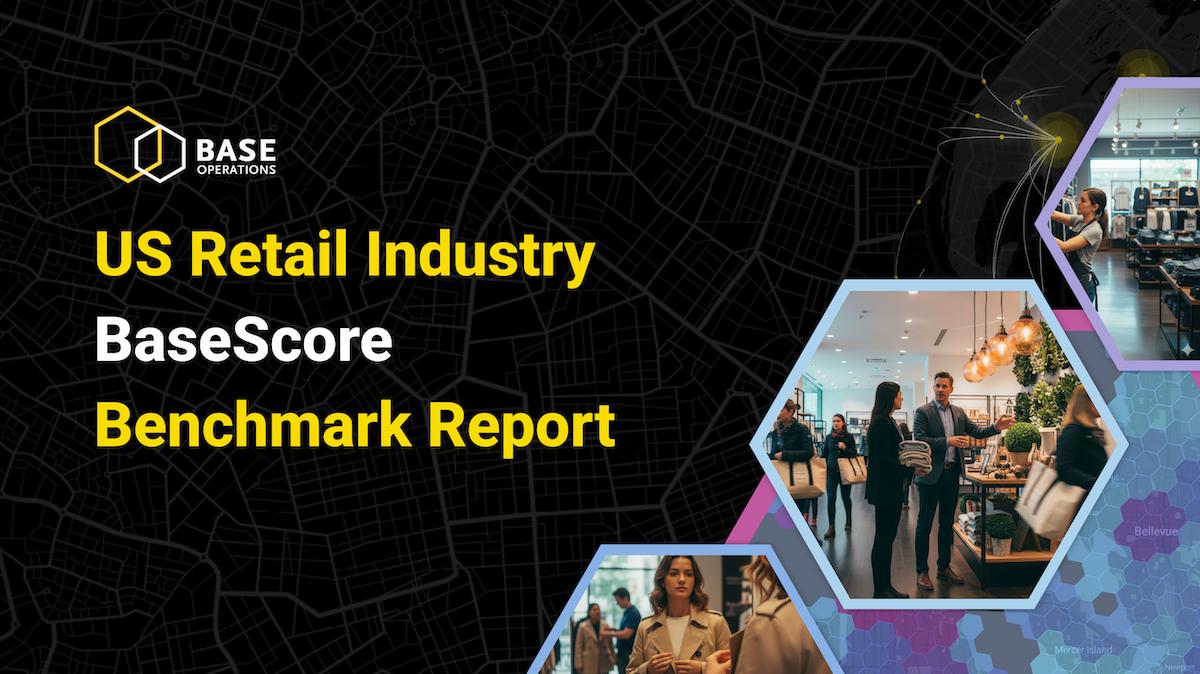
Incredible response to our US Retail Industry BaseScore Benchmark Report so far. You can go right in and search any retailer from National Retail Federation's top 100. We’ve made our analysis publicly available in this interactive tool. Here’s how different regions rank vs the national benchmark of 24: • Midwest = 20 • South = 22 • Northeast = 25 • West = 32 The devil (and nuance) is always in the details. Eg, while the West has a higher average BaseScore, the Northeast has 10x more locations in the Very High Risk tier than any other region at 1m radius of analysis. Security leaders use BaseScore benchmark data like this to: • Get apples to apples comparison of risk across footprint • Prioritize high risk sites and build tiered approach to security • Make data-driven decisions about resource allocation We broke the data down by region, state, and even company to help security leaders benchmark their performance. If you want a custom BaseScore analysis of your location footprint, drop a comment here or send me a DM.
- Base OperationsRecorded 10 Sept 2026
We analyzed the immediate threat landscape at 75,434 retail locations across America to create the most comprehensive benchmarks ever. And we’re making all of that analysis available for free. Retailers lack a universal standard for security risks across their company footprint. Too many security teams are stuck prioritizing resources based on gut instinct, lagging incident reports, or city-wide crime stats that miss what's actually happening at your stores. Our US Retail Industry BaseScore Benchmark Report gives you the framework to allocate resources with precision using street-level threat intelligence within 0.25 miles of each location. Inside the free interactive tool available here: https://lnkd.in/eECVYmFM • National and regional risk benchmarks (regional variation is big) • Individual benchmarks for the top 100 US retailers by sales • State-by-state comparisons • Granular threat breakdowns (property crime, violent crime, unrest) • A case study showing how to benchmark your entire footprint, identify your 10 highest-risk sites, and conduct standardized threat assessments This isn't city-wide, generic crime data. This is sub-mile intelligence broken down by threat type at 75,434 specific locations. Without a universal risk standard, retail security teams are left guessing. You're defending budget requests with anecdotes. You're reacting to incidents instead of preventing them. This benchmark shows what becomes possible when your entire security strategy is grounded in granular, standardized threat intelligence. Prove which stores need security infrastructure. Optimize guard deployments with data. Defend your budget with evidence executives actually understand. The gap between reactive security and strategic security is intelligence.
- BalbixSince 12 Nov 2025
I could not be more proud of our team here at Balbix! It is a privilege to share that Balbix has been named a Visionary in the 2025 Gartner® Magic Quadrant™ for Exposure Assessment Platforms, the first report defining this category. From the beginning, our goal has been to treat cyber exposure as an engineering and data problem rather than a checklist exercise. We built Balbix on the Cyber Risk Graph to unify telemetry, context, and business data at scale, enabling every asset, control, and vulnerability to be analyzed in real time and in the context of what it means to the business. The strength of our platform lies in its architecture. A highly optimized graph data layer, large-scale correlation engines, and explainable models work together to transform billions of telemetry points into insights that drive measurable outcomes. What differentiates Balbix is not just the analytics and workflows, but the system design that makes this speed and precision possible. This recognition reflects the work of an extraordinary team. Engineers who obsess over scalability and correctness. Product and design teams who turn complexity into clarity. The AI team that ensures every model and inference remains transparent and grounded in reality. And customer-facing teams who continuously translate feedback into meaningful enhancements. To our customers and partners, thank you for your trust and collaboration. This milestone validates our approach and reinforces our commitment to building the most reliable and transparent platform for understanding and reducing cyber exposure. Gartner subscribers can read the full report here: https://lnkd.in/gp8zN2JA #ctem #gartnermq #balbix #eap #exposure #vulnerabilitymanagement
- BalbixSince 16 Nov 2025
I’m thrilled to share that Balbix has been recognized as a Visionary in the 2025 Gartner® Magic Quadrant™ for Exposure Assessment Platforms. Security leaders everywhere are feeling the frustration — endless vulnerabilities, constant noise from threat intel, and mounting pressure from boards and regulators to demonstrate real risk reduction. This recognition reflects Balbix’s differentiated approach to: - Business-aligned exposure assessment and risk quantification built on our Cyber Risk Graph - AI-native exposure discovery and prioritization to cut through the noise - Executive-ready insights that tie exposures directly to business impact - Full slew of exposure mobilization capabilities Our mission is simple, to help organizations move from raw vulnerabilities to prioritized action, measurable risk reduction and increased cyber resilience. Being named a Visionary reinforces what our customers already know: 10× better attack surface visibility, 90% less remediation/mitigation workload, and 95% faster remediation. We’re helping security teams focus on what truly matters! Kudos to the incredible Balbix team for pushing boundaries, innovating every day with our domain-specfic AI models, and delivering real results for our customers. 📘 Gartner subscribers can read the full Magic Quadrant report here: https://lnkd.in/gp8zN2JA #GartnerMQ #CyberRisk #CTEM #ExposureManagement #AI #Balbix
- Beyond IdentityRecorded 10 Sept 2026
Last week, a CISO told me his MFA with push notifications is phishing-resistant. Yet Okta, Cisco, and Uber were breached using the attack method shown in this video. - Okta MFA Fatigue Attack (January 2022): The Lapsus$ hacking group bombarded an Okta third-party support engineer with endless push notifications. Eventually, they clicked “approve,” giving attackers Remote Desktop Protocol (RDP) access to Okta’s customer support panel and data related to two customers over a five-day period. - Cisco Attack (2022): Attackers used voice phishing to steal an employee’s credentials, then overwhelmed them with push notifications. One accidental approval later, Cisco’s network was breached. - Uber Breach (September 2022): MFA fatigue strikes again. Attackers sent nonstop push notifications to an Uber contractor until they gave in. That single click led to unauthorized access to Uber’s internal systems. The solution isn’t better detection or more security awareness training, we know employees will eventually click. The real solution is technology that makes phishing irrelevant by eliminating phishable factors like passwords, one-time codes, and push notifications altogether. At Beyond identity, we engineer the only phishing-resistant MFA that makes all identity-based attacks irrelevant. If you’re interested in seeing the technology that Defcon hackers calls “a pain in the ass,” reach out to us here: https://lnkd.in/gUKNYViX
- Beyond IdentityRecorded 10 Sept 2026
Dan L., a CEO in IT, was drowning in security complexity: employees authenticated 30 times/day with cumbersome codes and easily phishable push notifications for MFA, contractors accessed critical SaaS apps with no way to verify their device security, MDM & EDR configurations were unknown until he conducted painful, manual audits. That is, until he implemented Beyond Identity’s phishing-resistant MFA, which he describes as so secure that hackers at DEFCON walked away saying “it’s too difficult, we can’t hack it.” I know you hear from me a lot on how we have a transformative product for identity security, but this time you can hear directly from one of our customers how we were able to protect his complicated environment by eliminating identity-based attacks. He’s technical too so for those of you who are into the tech, you know who you are, he articulates precisely the functionalities that make this end state possible. What could your life be like if your security solution actually prevented, not just reduced, the biggest threats you’re facing today (i.e. identity and device security)? Dan’s full story is in the comments, check it out. #IAM #Cybersecurity #IdentitySecurity Beyond Identity Red Cup IT
- Mailock by Beyond EncryptionRecorded 10 Sept 2026
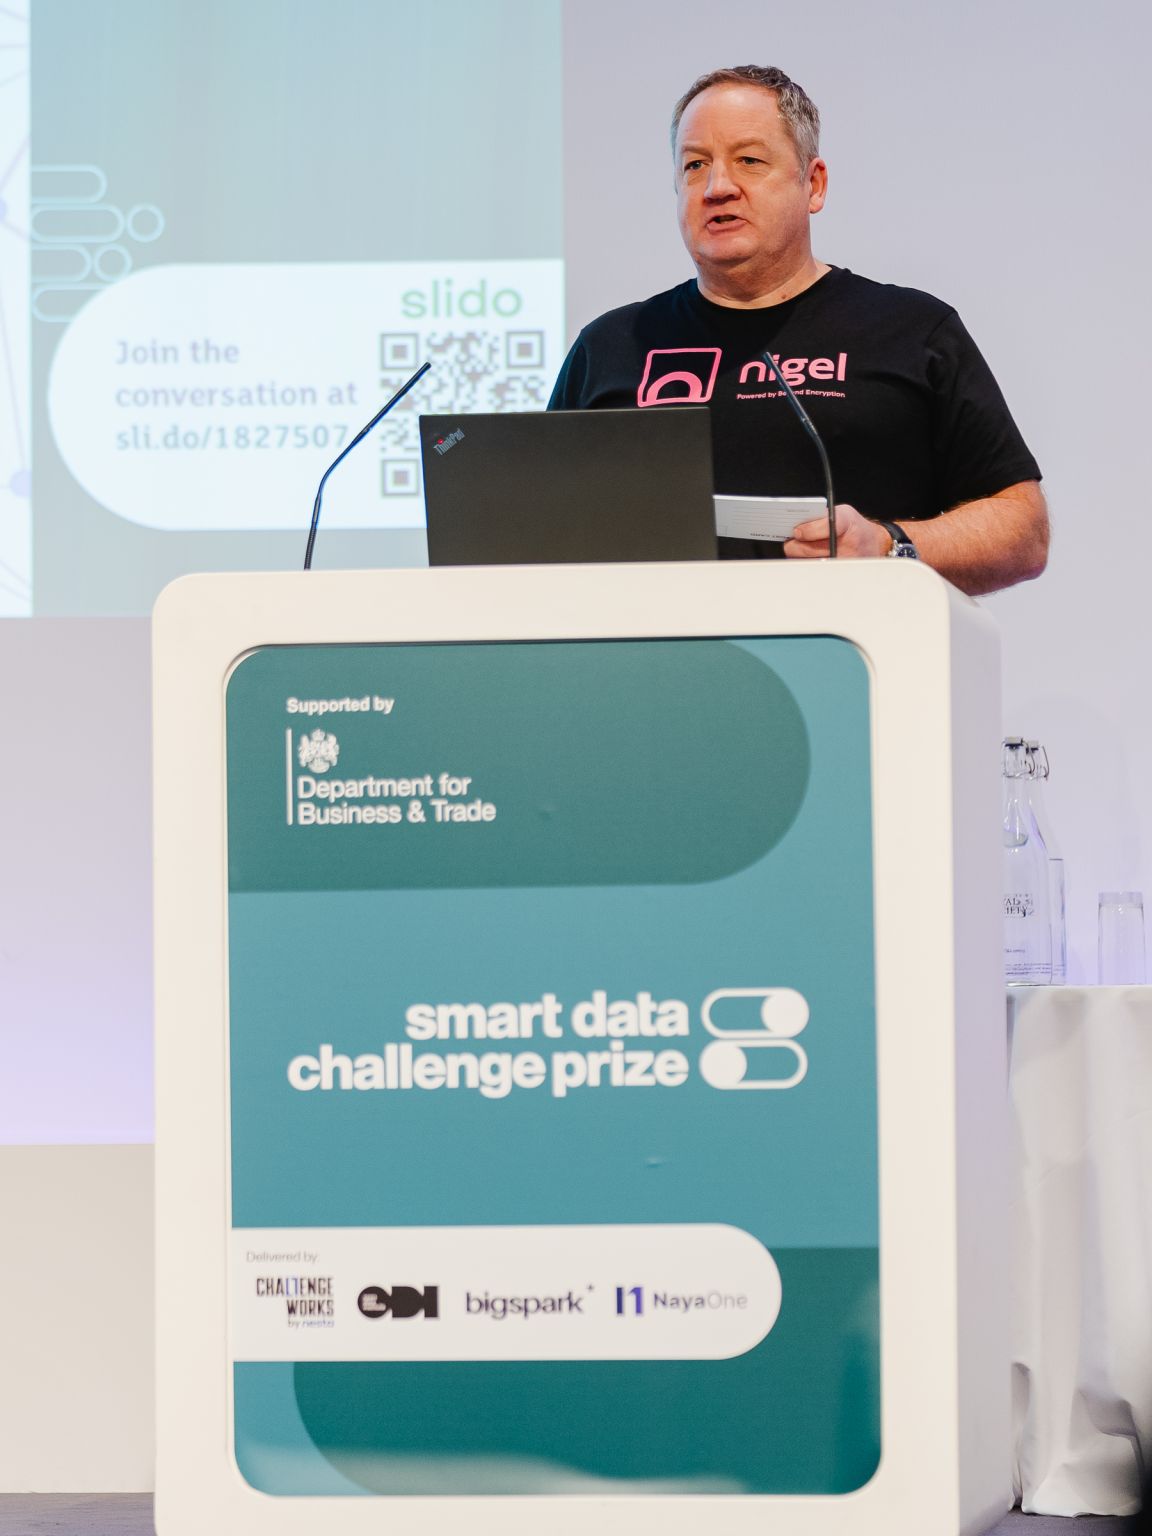
Who owns it? What breaks first? What happens when a customer gets stuck? Big ideas are easy to agree with. The operational reality is often much further away. Most teams are already stretched. They’re managing onboarding flows, authentication, compliance checks, legacy systems - all while trying not to slow customers down. So when people talk about improving how information is shared, what they’re really saying is: please don’t make this harder to run. The next stage of building our smart data assistant, Nigel, isn’t about asking organisations to change how they work. It’s about fitting in with how they work now. No new portals to nurse along. No extra steps that customers resent. No grey areas that make teams hesitate before hitting send. If this is going to stick, it has to feel routine, reduce cost, and make processes better. What we’ve learned from bringing Mailock secure email to the market is that delivery only scales when it becomes the easiest option. Learn more about Nigel: https://lnkd.in/eDNaTuF2
- AxalonRecorded 9 Sept 2026
„Alle dürfen alles sehen?“ Warum blindes Vertrauen im IAM gefährlich ist. Aus falschem Vertrauen oder um nicht der „Böse“ zu sein, erhalten oft alle Mitarbeitenden unbegrenzten Datenzugriff. Im professionellen Kontext braucht es aber klare Regeln ... Zugriff erfolgt rein zielgerichtet nach dem „Need-to-Know“-Prinzip. Das schützt sensible Unternehmensdaten und vor allem die Mitarbeitenden selbst! Denn wer für einen Bereich gar keine Rechte besitzt, gerät im Ernstfall bei Datenpannen erst gar nicht unter Verdacht. Wie du für klare und sichere Strukturen sorgst: https://www.axalon.ch/
- AxalonRecorded 9 Sept 2026
Würdest du deinem Ex-Partner den Wohnungsschlüssel überlassen? Wohl kaum. 🔑 Doch im Business passiert genau das ... Ex-Mitarbeitende behalten oft unbemerkt Zugriff auf IT-Systeme. Warum? Weil der Fokus meist nur auf dem Onboarding (Joiner-Prozess) liegt. Die Komplexität von Mover- und Lever-Prozessen wird massiv unterschätzt was ein riesiges Sicherheitsrisiko ist! Ein strukturierter Offboarding-Prozess ist essenziell für die IT-Sicherheit. Wie ihr eure Zugänge gut schützen könnt? Mehr auf: https://www.axalon.ch/
- AsteliaSince 7 Sept 2026
100+ companies signed OpenAI's open letter warning that AI-enabled cyber attacks will become far more widespread and sophisticated in the coming months. Each cyber defense instruction in this letter leaves an open question: ▪️ Fix the highest-risk weaknesses at incident speed. What does "high-risk" mean in your network? ▪️ Verify results without disrupting services. Is the attacker's route closed, or did a patch just go out? ▪️ Use compensating controls where you can't patch. Which control breaks the path? You can't answer any of these without network reachability. 👉Here's the breakdown and what you can do about it: https://lnkd.in/ep7E-xKb
- AsteliaSince 7 Sept 2026
Mythos Didn't Just Change the Conversation. It Changed the Market. Last week, three Fortune 500 security teams opened POCs with Astelia. Their CISOs walked into Monday morning meetings and realized their vulnerability programs were built for a world where time to exploit was measured in years. It's now measured in hours, every patch ships as an exploit blueprint, and the 2.3-year window between disclosure and weaponization has collapsed to under 20 hours. They didn't come in asking how to patch faster. They came in with harder questions: 𝟭. Which of the millions of vulnerabilities in our environment can an attacker actually reach? 𝟮. When a patch isn't available or can't be deployed, what's our move? 𝟯. How do we walk into the next board meeting with specifics instead of severity charts? Those are the questions Astelia was built to answer. We pinpoint the small fraction of vulnerabilities that are genuinely reachable and exploitable in your specific environment. We show the full attack path. And when patching isn't on the table, we surface the compensating controls, segmentation changes, and network-level mitigations that close the exposure while the patch catches up. These teams aren't outliers. They're the leading edge of a shift happening in every CISO conversation right now. If you're sitting with the same questions, let's talk.
- Attic SecuritySince 1 Sept 2026
Veelgestelde vraag: we hebben al Microsoft Defender, wat voegt MDR toe? Het antwoord: Defender is uitstekend gereedschap. Maar het blijft slechts gereedschap: een camera zonder bewaker. Ofwel: er moet iemand mee werken. Dat is bij de meeste organisaties niet geregeld, of de IT-er heeft er geen tijd voor. Daarom hebben wij IVON gebouwd. De AI-agent doet de triage, onderzoekt en sluit af met een oordeel en mitigerende maatregelen waar nodig. Geen alarm-doorstuurdienst dus, met de vraag of jij ergens naar wil kijken. Identity-First MDR op Microsoft 365. Nu leverbaar, over 10 minuten actief. Check de tarieven op onze website.
- Attic SecuritySince 1 Sept 2026
MSP vraagje: Wat betekent "agentic" nou precies, want iedereen roept het. Bij Attic Security is het dit: een AI-agent die triage uitvoert na security signalen. De agent onderzoekt een incident, komt met een oordeel, en adviseert waar nodig over mitigerende maatregelen. Een IR-rapport dat normaal twee dagen werk kost, heb je nu binnen zes minuten, ongeacht tijdstip. Wat het NIET betekent: autonoom zonder mens. Wij controleren wat de agent doet, beoordelen mee in geval van onzekerheid, en zijn beschikbaar bij vragen of uitzonderingen. Alles binnen de dienst en via onze portals. Verder interessant voor MSPs: geen minimale inkoop, geen unit-minimum. Geschikt voor de kleinste accounts. Prijzen transparant, geen verrassingen of langdurige offertetrajecten.
- AxoflowRecorded 9 Sept 2026
As Anton Chuvakin said on the Cloud Security Podcast by Google, in capturing the shift: Pipelines aren't cost-cutting tech, they're data quality tech. He’s right. When normalization and enrichment happen early, it makes the whole stack more reliable. Not magically, but just because the data finally reflects reality. This is the part that most architectures still miss. You can distribute the storage all day, but if the events are wrong, your conclusions will be too. In the blog, I go in-depth into why fixing data before it lands anywhere is becoming the backbone of modern security design. If you value accuracy over aesthetics, the full write-up is worth a read. Link in comments. #SecurityArchitecture #datapipelines #SOCengineering #telemetryquality
- AxurRecorded 9 Sept 2026
We've never had more data. We've never been more overwhelmed. That's the paradox I keep coming back to when I think about 2025. A few days ago, we released our Threat Landscape Report for 2025. I wanted to share the letter I wrote to open it, because honestly, this year forced all of us to confront some hard truths about where we are in cybersecurity. We have more data, more visibility, more tools than ever before. And yet, security teams are drowning in alerts. The challenge isn't knowing what's happening anymore. It's turning information into action. The threat landscape shifted under our feet. Supply chain attacks became routine, targeting the repositories, libraries, and solutions that entire ecosystems depend on. Insiders became the preferred vector for sophisticated threat actors who know that precision beats brute force. At Axur, we've been laser-focused on one thing: delivering data that's structured, enriched, and actually prioritized. Our recent launch of Axur Command takes this further, enabling autonomous validation policies so teams can finally move beyond reactive alert fatigue. Looking ahead to 2026, I believe the winners will be those who can consolidate data and act in an integrated way. We want Axur to be for the attack surface what observability platforms are for engineering: a central nervous system. One place where everything connects, prioritizes, and resolves. This report is our best reading of what happened in 2025 and what's coming next. My hope is it helps security teams prioritize better, move faster, and anticipate risks before they become incidents. Technology keeps advancing. Our job is to make sure that advancement happens with security, confidence, and responsibility built in from the start. If you're leading a security team or care about where this field is headed, I'd love to hear your thoughts on the report. 📄 Read more: https://lnkd.in/eDFriJtj
- ART2SECRecorded 8 Sept 2026
Si hace 10 años me hubieran dicho que una de nuestras soluciones de ciberseguridad sería monitorear Instagram o páginas web, me habría reído. En el 2016, la ciberseguridad era una cuestión de perímetros: se aseguraba la oficina y con eso era suficiente. Pero hoy, el perímetro no existe. Las marcas viven en el bolsillo de miles de personas, en sus celulares, en sus redes y hasta en nubes de las que no tienes el control. En esta década aprendí que no podemos ser estáticos. Si el fraude evoluciona, nosotros tenemos que ser más rápidos. ¿Han estado monitoreando la presencia digital de su empresa? ¿Sabes dónde es mencionada tu empresa o tú como fundador? ¿Hay una posible copia de tu información que potencialmente robe a tus clientes? Hemos estado adentrandonos este nuevo reto digital y construyendo ShieldBrand 360. Nuestra apuesta: pasar de la defensa pasiva a la protección activa de la marca en todo el ecosistema digital. Si eres una empresa y te suena esto, hablemos.
- ART2SECRecorded 8 Sept 2026
Como founders, vivimos por y para el momentum. Queremos conquistar mercados, cerrar rondas y crecer a doble dígito. Pero hay una verdad incómoda que pocos se atreven a decir: La velocidad sin resiliencia es un riesgo de quiebra reputacional. Hace poco vivimos de cerca un caso crítico: un ecommerce en plena expansión regional, con los ojos de los inversionistas encima y una ronda de inversión agresiva en curso. De un momento a otro: Ransomware. 100% de la contabilidad cifrada. El núcleo transaccional fuera de servicio. En ese punto, el problema no es solo "un virus"; es que tu credibilidad está secuestrada. En ART2SEC , a través de nuestro CCI (Ciber Centro de Inteligencia) , no entramos a "eliminar un virus". Entramos a salvar la continuidad del negocio. Porque no puedes conquistar Latinoamérica si tu base de operación no es capaz de recibir un golpe y levantarse en minutos. La ciberseguridad no es solo un "check" en un listado de cosas por hacer para evitar ataques (porque los ataques van a llegar). Es el sistema que garantiza que, pase lo que pase, tu negocio siga operando. ¿te suena? Hablemos de resiliencia real #CyberResilience #StartupsLatam #Ciberseguridad #Art2sec #GrowthStrategies
- ArmisSince 2 Sept 2026
For years, security tools perpetuated a single promise: 𝘣𝘶𝘺 𝘮𝘰𝘳𝘦, 𝘴𝘤𝘢𝘯 𝘧𝘢𝘴𝘵𝘦𝘳, 𝘩𝘰𝘱𝘦 𝘧𝘰𝘳 𝘣𝘦𝘵𝘵𝘦𝘳. But CISOs aren't asking for more tools. They're asking for outcomes. Recently at Black Hat, I had the opportunity to sit down with Dave Gruber from Omdia to explore how ServiceNow's full Autonomous Security portfolio delivers the shift that security teams are demanding. Our vision at Armis has always been obsessively security focused. Our work was independently validated by Omdia earlier this year (https://lnkd.in/dJhRYyjm), quantifying the measurable outcomes our customers achieved with total visibility - including: • 𝐅𝐢𝐧𝐚𝐧𝐜𝐢𝐚𝐥 𝐢𝐦𝐩𝐚𝐜𝐭: 351% total ROI* • 𝐑𝐢𝐬𝐤 𝐫𝐞𝐝𝐮𝐜𝐭𝐢𝐨𝐧: faster detection with investigation and remediation time reduced by up to 90%* • 𝐎𝐩𝐞𝐫𝐚𝐭𝐢𝐨𝐧𝐚𝐥 𝐞𝐟𝐟𝐢𝐜𝐢𝐞𝐧𝐜𝐲: 10-20 hours saved per analyst per week* Now, with ServiceNow Security, Armis, and Veza as one united business unit, we have something even more rare: the ability to tackle the biggest challenges CISOs face end-to-end. This is not about adding more products to our tech stack, but about truly recognizing security as its own business, understanding security teams as their own ecosystem, and serving their needs as they evolve. The opportunity at hand is significant. It demands a true partner that thinks about the security agenda holistically. That understands the extreme asymmetry between attackers and defenders. And that sets a standard for continuous, autonomous self-healing. That's Shift Zero. And that’s what we are delivering with our newly formed team of experts, stationed in ServiceNow’s 𝐀𝐈 𝐂𝐞𝐧𝐭𝐞𝐫 𝐟𝐨𝐫 𝐂𝐲𝐛𝐞𝐫 𝐃𝐞𝐟𝐞𝐧𝐬𝐞, which I couldn’t be more excited to lead. My thanks to Dave for our discussion. You can watch the full conversation hosted by BrightTALK here: https://lnkd.in/dV2KDxcu You can also access our latest research into the gaps created by traditional response times, and how we’re closing them with intelligence-driven detection: https://lnkd.in/d5Gq4iAb #ShiftZero #AICenterForCyberDefense #VulnerabilityManagement #ThreatDetection #BlackHat2026 #ServiceNow *𝘛𝘩𝘦𝘴𝘦 𝘧𝘪𝘨𝘶𝘳𝘦𝘴 𝘢𝘳𝘦 𝘵𝘩𝘦 𝘳𝘦𝘴𝘶𝘭𝘵 𝘰𝘧 𝘖𝘮𝘥𝘪𝘢’𝘴 𝘦𝘤𝘰𝘯𝘰𝘮𝘪𝘤 𝘮𝘰𝘥𝘦𝘭𝘪𝘯𝘨 𝘥𝘦𝘳𝘪𝘷𝘦𝘥 𝘧𝘳𝘰𝘮 𝘮𝘶𝘭𝘵𝘪𝘱𝘭𝘦 𝘥𝘢𝘵𝘢 𝘴𝘰𝘶𝘳𝘤𝘦𝘴: 𝘖𝘮𝘥𝘪𝘢 𝘭𝘦𝘷𝘦𝘳𝘢𝘨𝘦𝘥 𝘪𝘯𝘴𝘪𝘨𝘩𝘵𝘴 𝘧𝘳𝘰𝘮 𝘤𝘶𝘴𝘵𝘰𝘮𝘦𝘳 𝘪𝘯𝘵𝘦𝘳𝘷𝘪𝘦𝘸𝘴, 𝘷𝘦𝘯𝘥𝘰𝘳-𝘱𝘳𝘰𝘷𝘪𝘥𝘦𝘥 𝘮𝘢𝘵𝘦𝘳𝘪𝘢𝘭𝘴, 𝘱𝘶𝘣𝘭𝘪𝘤 𝘢𝘯𝘥 𝘪𝘯𝘥𝘶𝘴𝘵𝘳𝘺 𝘣𝘦𝘯𝘤𝘩𝘮𝘢𝘳𝘬𝘴, 𝘢𝘯𝘥 𝘪𝘵𝘴 𝘰𝘸𝘯 𝘬𝘯𝘰𝘸𝘭𝘦𝘥𝘨𝘦 𝘰𝘧 𝘤𝘺𝘣𝘦𝘳𝘴𝘦𝘤𝘶𝘳𝘪𝘵𝘺 𝘵𝘦𝘤𝘩𝘯𝘰𝘭𝘰𝘨𝘪𝘦𝘴 𝘢𝘯𝘥 𝘤𝘰𝘴𝘵 𝘴𝘵𝘳𝘶𝘤𝘵𝘶𝘳𝘦𝘴.
- Anonyome Labs, Inc.Recorded 8 Sept 2026
Think about the average insurance customer: 🔐 Hundreds of online accounts 🕵 No idea where their data lives ⚠️ No plan if it’s breached This isn’t just a technical problem. It’s a trust opportunity. At Anonyome Labs, the Assess phase of our AOCUR method helps insurers give customers a clear view of: ✅ Where they’re exposed ✅ Which companies have had breaches ✅ What actions to take next It’s more than breach detection. It’s proactive guidance, action, and value delivered before a claim ever comes in. In a digital-first world, being the first to inform means being the first they trust. 🔗 https://lnkd.in/gpvCJa-v #DigitalResilience #InsuranceTech #PrivacyProtection #DigitalIdentity #AnonyomeLabs #CustomerValue #AOCURmethod #InsuranceInnovation
- ARMOSince 1 Dec 2025
CSPM and CNAPP tell you you’re secure. An attacker will gladly prove otherwise. I’ve seen this gap up close too many times, which is why we built CTRL - Cloud Threat Readiness Lab. A free, safe environment to test how your existing cloud and runtime security tools respond to real attacks. We’re kicking it off with a live simulation on Dec 3rd at 12pm EST, where Ben Hirschberg will walk through an end-to-end exploit from web entry point to container compromise. Join us if you want a clear, unfiltered view of how your defenses really behave https://lnkd.in/d8QDMgb6 #CloudSecurity #RuntimeSecurity #CADR #ARMOCTRL
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.