On air · 1 of 3 networks
Beyond Identity
- beyondidentity.com
- Cybersecurity
- US
- 64 employees
Beyond Identity’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 57. Watch Beyond Identity with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 57 | Checked 30 Oct 2026 | See all 57 ads → | ||
| Meta | Not checked | — | |||
| Recently | 24 | Ads on the Google Ads Transparency Center | Checked 10 Oct 2026 | Collect them with the API → |
Beyond Identity has 57 live LinkedIn ads. We recorded 24 Google ads on 10 Oct 2026.
Latest ads
- LINKEDIN · VIDEORecorded 10 Sept 2026
CISOs facing the rise of deepfake threats need to understand one key distinction: probabilistic vs. deterministic security. Deterministic security ensures you can always prove: - the person is who they claim to be - they’re operating from the device you know and expect - with the security controls you require — and never a deepfake. Listen to the full conversation on the Cloud Security Podcast: https://lnkd.in/eSNzTA-b Beyond Identity
- LINKEDIN · VIDEORecorded 10 Sept 2026
SAP Taulia faced a coordinated attack on over 200 Okta accounts. Not one was compromised. When attackers targeted Taulia’s identity provider, they hit a wall: identity defenses that verify both the user and the device with cryptographic proof — something attackers can't steal. Without passwords, OTPs, or push notifications existing, attackers had nothing to phish, social engineer, or bypass. Why does that matter? Because Taulia serves Fortune 500 clients that expect uncompromising security at every login. Security is often hard to quantify. This time, it wasn’t: - 1,800+ hours saved per month from password friction alone - Zero identity-related incidents since becoming a customer - The #1 cause of security incidents, credential compromise, now prevented every time We’re proud to work with forward-thinking leaders like Duke H. Le, Taulia’s Sr. Director of Corporate IT, who understand that identity is the first line of defense, and that security can be a competitive advantage. See how Taulia turned identity security into a measurable business advantage: https://lnkd.in/eKVkuNjw Beyond Identity
- LINKEDIN · VIDEORecorded 10 Sept 2026
Dan L., a CEO in IT, was drowning in security complexity: employees authenticated 30 times/day with cumbersome codes and easily phishable push notifications for MFA, contractors accessed critical SaaS apps with no way to verify their device security, MDM & EDR configurations were unknown until he conducted painful, manual audits. That is, until he implemented Beyond Identity’s phishing-resistant MFA, which he describes as so secure that hackers at DEFCON walked away saying “it’s too difficult, we can’t hack it.” I know you hear from me a lot on how we have a transformative product for identity security, but this time you can hear directly from one of our customers how we were able to protect his complicated environment by eliminating identity-based attacks. He’s technical too so for those of you who are into the tech, you know who you are, he articulates precisely the functionalities that make this end state possible. What could your life be like if your security solution actually prevented, not just reduced, the biggest threats you’re facing today (i.e. identity and device security)? Dan’s full story is in the comments, check it out. #IAM #Cybersecurity #IdentitySecurity Beyond Identity Red Cup IT
- LINKEDIN · VIDEORecorded 10 Sept 2026
Last week, a CISO told me his MFA with push notifications is phishing-resistant. Yet Okta, Cisco, and Uber were breached using the attack method shown in this video. - Okta MFA Fatigue Attack (January 2022): The Lapsus$ hacking group bombarded an Okta third-party support engineer with endless push notifications. Eventually, they clicked “approve,” giving attackers Remote Desktop Protocol (RDP) access to Okta’s customer support panel and data related to two customers over a five-day period. - Cisco Attack (2022): Attackers used voice phishing to steal an employee’s credentials, then overwhelmed them with push notifications. One accidental approval later, Cisco’s network was breached. - Uber Breach (September 2022): MFA fatigue strikes again. Attackers sent nonstop push notifications to an Uber contractor until they gave in. That single click led to unauthorized access to Uber’s internal systems. The solution isn’t better detection or more security awareness training, we know employees will eventually click. The real solution is technology that makes phishing irrelevant by eliminating phishable factors like passwords, one-time codes, and push notifications altogether. At Beyond identity, we engineer the only phishing-resistant MFA that makes all identity-based attacks irrelevant. If you’re interested in seeing the technology that Defcon hackers calls “a pain in the ass,” reach out to us here: https://lnkd.in/gUKNYViX
- LINKEDIN · VIDEORecorded 10 Sept 2026
Recently one of our customers stopped a breach and made phishing training obsolete. Brandt Hospitality, builder and operator of Marriott, Hilton, and Hyatt hotels, was under pressure from their cyber insurance provider to implement phishing-resistant MFA. If they didn’t, premiums would go up. As they evaluated options, they found most solutions came with friction: MFA apps that required personal phones, or hardware keys that frontline employees could lose or forget. None of it was simple or scalable. With Beyond Identity, Brandt now has: - Device-bound, phishing-resistant MFA - Passwordless, frictionless logins: no phones, hardware keys, or one-time codes - Seamless integration with existing infrastructure (no heavy IT lifting) And when their Head of IT got a call from a manager urgently asking to reset their password, they knew it was a phishing attempt. Without passwords, codes, or push notifications in Beyond Identity's technology, there’s nothing for attackers to phish or steal. This reinforces something we see again and again: You can’t rely on users to detect phishing or approve the “right” MFA prompt. You have to remove the decision altogether, with the right technology. This technology exists with Beyond Identity. If this resonates, read the full story below or reach out. Beyond Identity Brandt Hospitality Group Joshua Johansen
- LINKEDIN · IMAGERecorded 10 Sept 2026
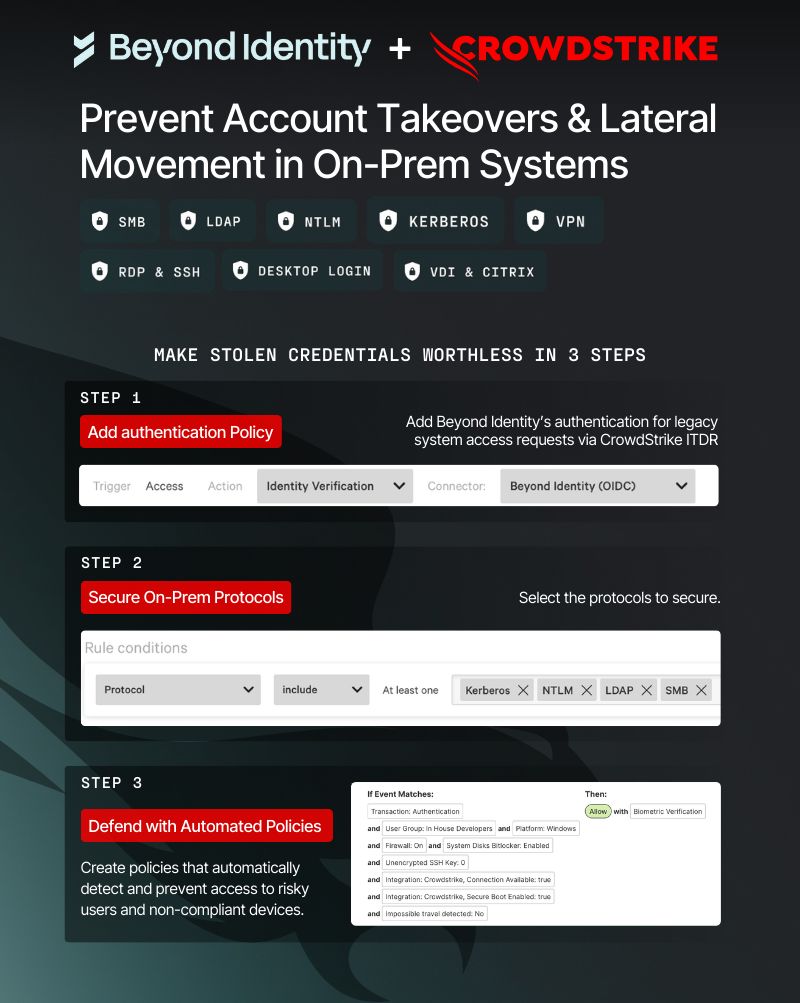
🚀 Proud to share a new feature we just released: Universal Identity Defense for Legacy and On-Prem Applications. The challenge: On-prem apps are easier to exploit than cloud apps. They still rely on protocols like NTLM and Kerberos that use hardcoded username/passwords or global admin privilege which attackers exploit for initial access, lateral movement, and privilege escalation. I’m excited to share that Beyond Identity, together with CrowdStrike, has closed this gap by launching modern identity defense to on-prem apps. Here’s why it matters: • You can make stolen credentials worthless—because without the right device, posture, and cryptographic token, the login attempt fails • You can secure RDP, SSH, and VPN without rewriting code or changing infrastructure • You can enforce device trust by automatically detecting and preventing access to non-compliant, risky devices I made a quick demo video here, please share any feedback! https://lnkd.in/g4er49TQ
6 of 57 adsSign up to see every Beyond Identity ad, filter by format and date, and get alerts on new ones.
See all 57 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.