On air · 1 of 3 networks
Armis
- armis.com
- Cybersecurity
- US
- 904 employees
Armis’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 735. Watch Armis with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 389 | Checked 30 Oct 2026 | See all 735 ads → | ||
| Meta | Not checked | — | |||
| Recently | 26 | Ads on the Google Ads Transparency Center | Checked 5 Oct 2026 | Collect them with the API → |
Armis has 389 live LinkedIn ads. We recorded 26 Google ads on 5 Oct 2026.
Latest ads
- LINKEDIN · IMAGESince 25 Sept 2026
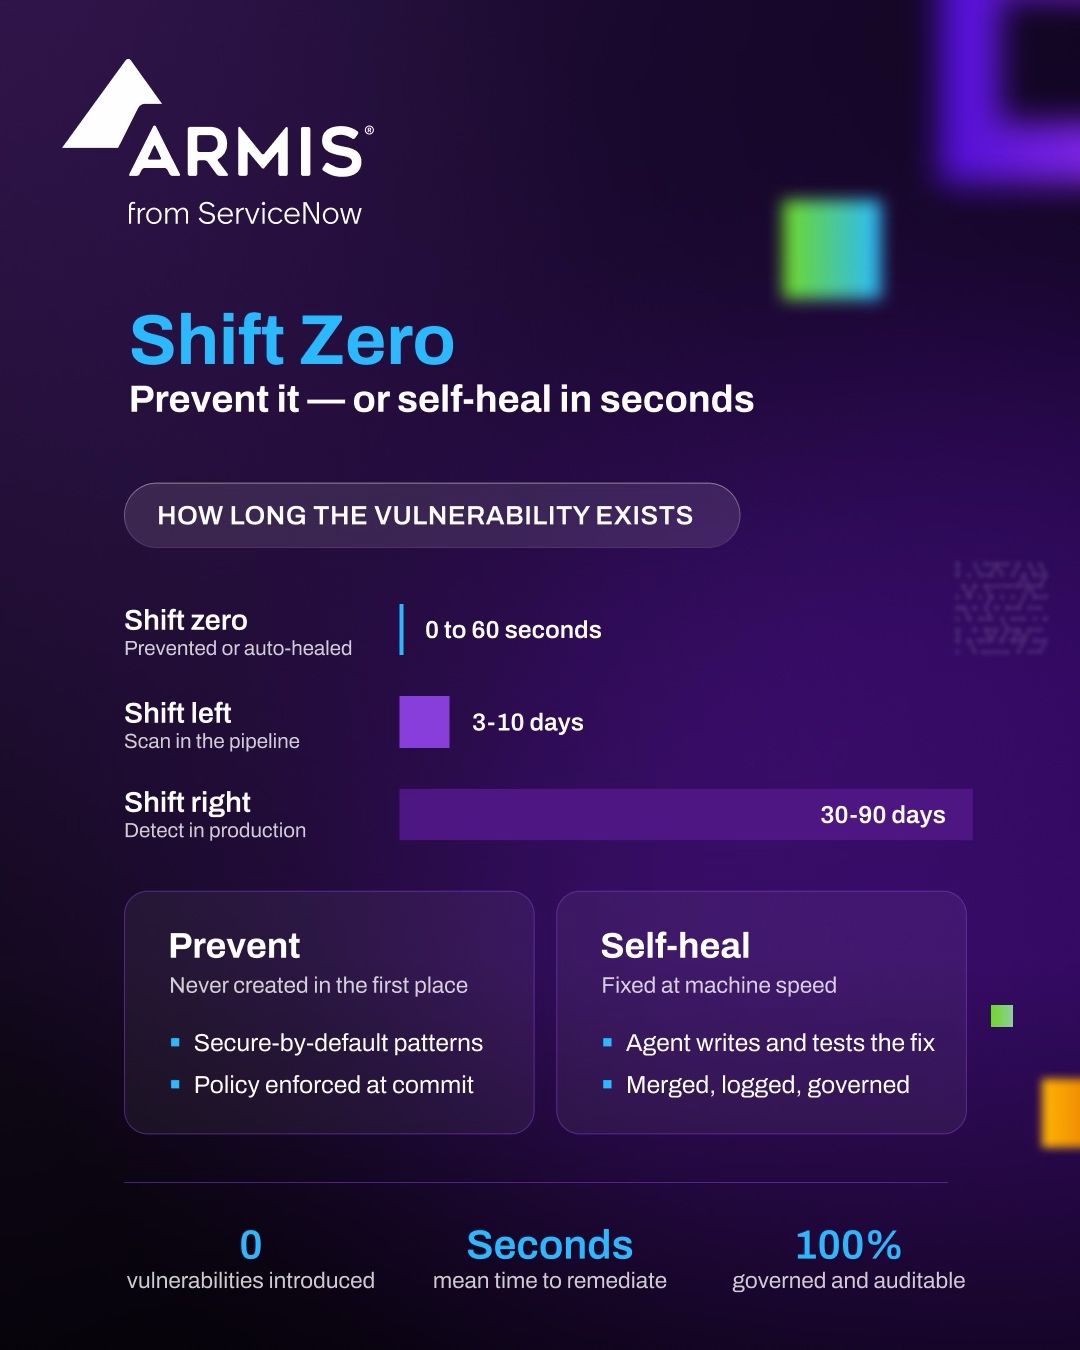
A vulnerability that lives in your pipeline for even 10 days is a risk. One that lives in production for 90 is basically an open invitation. "Shift left" got us real progress: detection time dropped from months to days. But days is still a long time when the other side is running autonomous AI that scans, weaponizes and exploits code around the clock. So the number I actually care about now isn't detection speed. It's exposure time: how long a flaw exists, from the moment it's created to the moment it's gone. The answer we've been building towards at Armis (by ServiceNow) is as close to zero as possible. Either the vulnerability never exists because secure patterns are enforced at commit, or it's caught and self-healed in seconds: patched, tested and merged before it ever reaches a human queue. We call this Shift Zero, and it's a genuinely different way to do the AppSec math. I went deeper on it, and the four layers behind it, in a recent piece here: https://armis.ly/4xG0Wx6 What's your team's real exposure window right now? Not your detection time. Your exposure time. #ApplicationSecurity #ShiftZero #ProductSecurity
- LINKEDIN · CAROUSELSince 9 Sept 2026
Legacy AppSec tools were built for a different era. Your attack surface has moved on. Armis Centrix™ for Application Security catches AI-generated and variant code risks before they ship, cutting false positives by up to 70%. Stop scanning. Start seeing.
- LINKEDIN · IMAGESince 9 Sept 2026
Tool sprawl and template-based noise are pulling your developers off roadmap work, buried under false positives from fragmented AppSec tools. Armis Centrix™ for Application Security unifies detection, context, and remediation into a single AI-native platform, cutting false positives by up to 70% and tying every finding to real business context. Replace fragmented SAST, SCA, DAST, IaC, secrets and SBOM tools with one platform, and lower your total cost of ownership under a single license.
- LINKEDIN · IMAGESince 9 Sept 2026
Your developers are shipping AI-generated code faster than your AppSec tools can understand it. Template-based scanners were built for a different era — they flag noise, miss novel variants, and bury the risks that actually reach production. Armis Centrix™ for Application Security uses AI-native detection to catch what template-based scanners can't, with full coverage across SAST, SCA, DAST, IaC, secrets, and SBOMs in one platform.
- LINKEDIN · VIDEOSince 2 Sept 2026
For years, security tools perpetuated a single promise: 𝘣𝘶𝘺 𝘮𝘰𝘳𝘦, 𝘴𝘤𝘢𝘯 𝘧𝘢𝘴𝘵𝘦𝘳, 𝘩𝘰𝘱𝘦 𝘧𝘰𝘳 𝘣𝘦𝘵𝘵𝘦𝘳. But CISOs aren't asking for more tools. They're asking for outcomes. Recently at Black Hat, I had the opportunity to sit down with Dave Gruber from Omdia to explore how ServiceNow's full Autonomous Security portfolio delivers the shift that security teams are demanding. Our vision at Armis has always been obsessively security focused. Our work was independently validated by Omdia earlier this year (https://lnkd.in/dJhRYyjm), quantifying the measurable outcomes our customers achieved with total visibility - including: • 𝐅𝐢𝐧𝐚𝐧𝐜𝐢𝐚𝐥 𝐢𝐦𝐩𝐚𝐜𝐭: 351% total ROI* • 𝐑𝐢𝐬𝐤 𝐫𝐞𝐝𝐮𝐜𝐭𝐢𝐨𝐧: faster detection with investigation and remediation time reduced by up to 90%* • 𝐎𝐩𝐞𝐫𝐚𝐭𝐢𝐨𝐧𝐚𝐥 𝐞𝐟𝐟𝐢𝐜𝐢𝐞𝐧𝐜𝐲: 10-20 hours saved per analyst per week* Now, with ServiceNow Security, Armis, and Veza as one united business unit, we have something even more rare: the ability to tackle the biggest challenges CISOs face end-to-end. This is not about adding more products to our tech stack, but about truly recognizing security as its own business, understanding security teams as their own ecosystem, and serving their needs as they evolve. The opportunity at hand is significant. It demands a true partner that thinks about the security agenda holistically. That understands the extreme asymmetry between attackers and defenders. And that sets a standard for continuous, autonomous self-healing. That's Shift Zero. And that’s what we are delivering with our newly formed team of experts, stationed in ServiceNow’s 𝐀𝐈 𝐂𝐞𝐧𝐭𝐞𝐫 𝐟𝐨𝐫 𝐂𝐲𝐛𝐞𝐫 𝐃𝐞𝐟𝐞𝐧𝐬𝐞, which I couldn’t be more excited to lead. My thanks to Dave for our discussion. You can watch the full conversation hosted by BrightTALK here: https://lnkd.in/dV2KDxcu You can also access our latest research into the gaps created by traditional response times, and how we’re closing them with intelligence-driven detection: https://lnkd.in/d5Gq4iAb #ShiftZero #AICenterForCyberDefense #VulnerabilityManagement #ThreatDetection #BlackHat2026 #ServiceNow *𝘛𝘩𝘦𝘴𝘦 𝘧𝘪𝘨𝘶𝘳𝘦𝘴 𝘢𝘳𝘦 𝘵𝘩𝘦 𝘳𝘦𝘴𝘶𝘭𝘵 𝘰𝘧 𝘖𝘮𝘥𝘪𝘢’𝘴 𝘦𝘤𝘰𝘯𝘰𝘮𝘪𝘤 𝘮𝘰𝘥𝘦𝘭𝘪𝘯𝘨 𝘥𝘦𝘳𝘪𝘷𝘦𝘥 𝘧𝘳𝘰𝘮 𝘮𝘶𝘭𝘵𝘪𝘱𝘭𝘦 𝘥𝘢𝘵𝘢 𝘴𝘰𝘶𝘳𝘤𝘦𝘴: 𝘖𝘮𝘥𝘪𝘢 𝘭𝘦𝘷𝘦𝘳𝘢𝘨𝘦𝘥 𝘪𝘯𝘴𝘪𝘨𝘩𝘵𝘴 𝘧𝘳𝘰𝘮 𝘤𝘶𝘴𝘵𝘰𝘮𝘦𝘳 𝘪𝘯𝘵𝘦𝘳𝘷𝘪𝘦𝘸𝘴, 𝘷𝘦𝘯𝘥𝘰𝘳-𝘱𝘳𝘰𝘷𝘪𝘥𝘦𝘥 𝘮𝘢𝘵𝘦𝘳𝘪𝘢𝘭𝘴, 𝘱𝘶𝘣𝘭𝘪𝘤 𝘢𝘯𝘥 𝘪𝘯𝘥𝘶𝘴𝘵𝘳𝘺 𝘣𝘦𝘯𝘤𝘩𝘮𝘢𝘳𝘬𝘴, 𝘢𝘯𝘥 𝘪𝘵𝘴 𝘰𝘸𝘯 𝘬𝘯𝘰𝘸𝘭𝘦𝘥𝘨𝘦 𝘰𝘧 𝘤𝘺𝘣𝘦𝘳𝘴𝘦𝘤𝘶𝘳𝘪𝘵𝘺 𝘵𝘦𝘤𝘩𝘯𝘰𝘭𝘰𝘨𝘪𝘦𝘴 𝘢𝘯𝘥 𝘤𝘰𝘴𝘵 𝘴𝘵𝘳𝘶𝘤𝘵𝘶𝘳𝘦𝘴.
- LINKEDIN · CAROUSELSince 13 Aug 2026
Periodic scans miss 70% of your assets and leave 4-6 weeks of blind spots while your team drowns in false positives. Static scanners were built for a different era—your attack surface has moved on. Stop waiting. Start seeing. 🛡️
6 of 735 adsSign up to see every Armis ad, filter by format and date, and get alerts on new ones.
See all 735 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.