On air · 1 of 3 networks
Astelia
- astelia.io
- Cybersecurity
- US
- 64 employees
Astelia’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 213. Watch Astelia with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 179 | Checked 30 Oct 2026 | See all 213 ads → | ||
| Meta | Not checked | — | |||
| Recently | 13 | Ads on the Google Ads Transparency Center | Checked 6 Oct 2026 | Collect them with the API → |
Astelia has 179 live LinkedIn ads. We recorded 13 Google ads on 6 Oct 2026.
Latest ads
- LINKEDIN · IMAGESince 24 Sept 2026
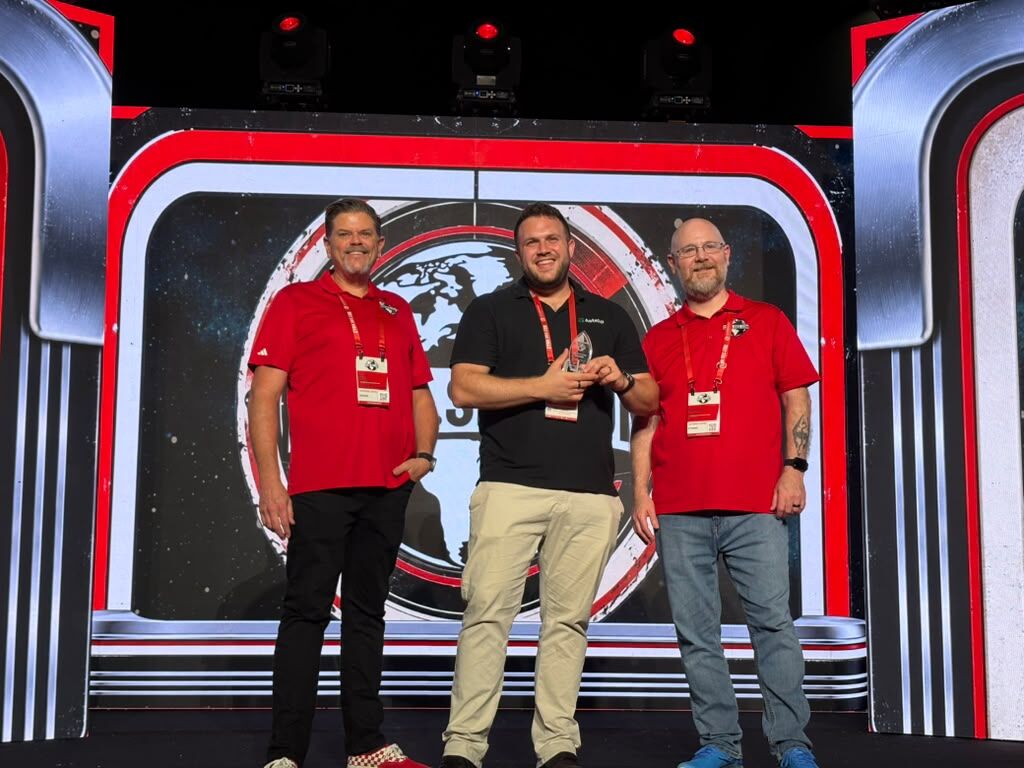
First place! 🏆 I'm thrilled to share that Astelia 𝗷𝘂𝘀𝘁 𝘄𝗼𝗻 𝘁𝗵𝗲 CYBR.SEC.CON 𝟮𝟬𝟮𝟲 𝗟𝗮𝘂𝗻𝗰𝗵𝗣𝗮𝗱 𝗰𝗼𝗺𝗽𝗲𝘁𝗶𝘁𝗶𝗼𝗻, picked from a strong field of early-stage security companies pitching to practitioners, CISOs, investors, and operators in Houston. Houston always feels like home, and helping some of the biggest names in oil and gas defend against cyberthreats is one of the things I'm proudest of at Astelia. Haven't run into you yet? Catch me on the Energy Stage at 1:15 PM, talking about how my Red Team years shaped my approach to defending against Mythos threats, or find me at the Astelia booth in Innovation Station. Huge thank you to Cybersecevents and this whole community for the warmth this week: Michael Farnum, Sam Van Ryder, John Barrow, Andy Ellis, Allan Alford, Kristen Twining, Patricia Matthews, Jesse Martinez. 🎉 Check out the announcement: https://lnkd.in/e9wwHPv5
- LINKEDIN · IMAGESince 17 Sept 2026
I'm proud to share that Gartner just named Astelia a Sample Vendor in Unified Exposure Management Platforms, in its new Emerging Tech Impact Radar for Preemptive Cybersecurity. This validates something we've believed since we started the company: reachability analysis is foundational, even when AI is turning vulnerability management on its head. My main takeaways: • AI now chains vulnerabilities faster, making severity scores irrelevant • UEMPs unify discovery, validation, and remediation in one platform • UEMPs projected to exceed 50% of exposure management tools by 2028 • Defending against AI-driven threats requires UEMPs grounded in reachability 👉 Check out the full breakdown here: https://lnkd.in/gAsAgFTY
- LINKEDIN · IMAGESince 7 Sept 2026
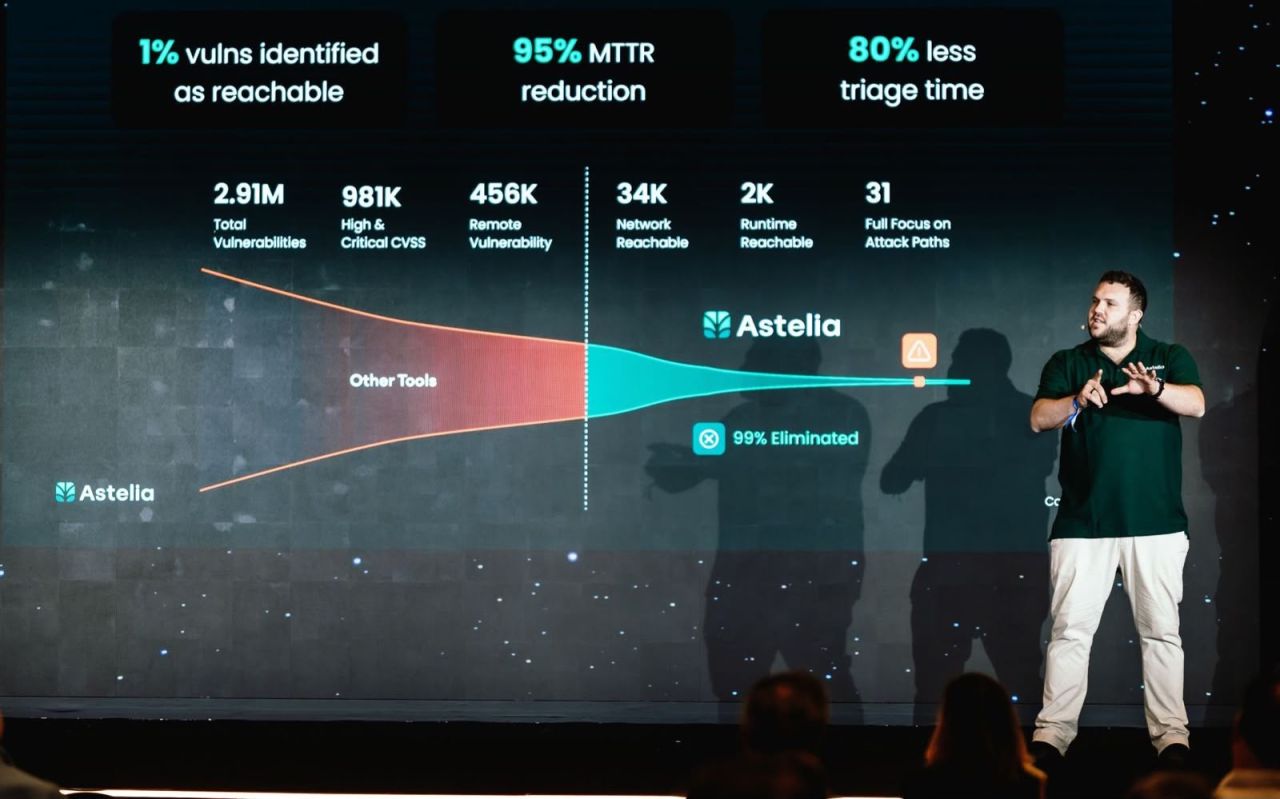
I watched a CISO at a Fortune 500 company go quiet in the middle of our demo. He was going through our funnel, following one attack path, port by port, all the way down to the single asset it reached. He looked at it for a while and then said something like, "I've looked at a lot of these dashboards. This is the first time I can actually see why a vulnerability is critical, instead of relying on a score telling me it is." That's the part that matters to me. Not the deal, not the signature. The moment reachability clicks as the thing that actually matters. Most of this market sells risk management, which is really just a smarter guess at what might matter. We don't rank guesses. We show the actual network path an attacker would have to take, and whether it's open. It's a binary question: reachable or not. That's usually what gets us the next conversation with large enterprises like his, because a team that's already seen every tool on the market is looking at real evidence instead of another score.
- LINKEDIN · IMAGESince 7 Sept 2026
𝗠𝘆𝘁𝗵𝗼𝘀 𝗰𝗵𝗮𝗻𝗴𝗲𝗱 𝗲𝘃𝗲𝗿𝘆𝘁𝗵𝗶𝗻𝗴. The boards are not asking technical questions anymore. They are asking the question CISOs cannot answer in CVSS language: “How are you protecting the organization from Mythos attacks?” I just spent two weeks in face-to-face meetings with Fortune 500 and Fortune 2000 CISOs across Houston and Miami. Different industries, different stacks, same conversation in different words. The smartest CISOs in the room are not asking whether they are ready for Mythos. They already know Mythos is a symptom, not the disease. They are asking the bigger question: how do we run a security program when the time-to-exploit keeps collapsing, while security teams cannot scale fast enough to keep up, and legacy systems cannot always be touched? Here is what I told every security leader I sat with: 𝟭. The next board meeting is where you own the table. Not because you survived another quarter. Because you walk in showing the organization is already ahead of the next model, the next disclosure, the next headline. Reachability is continuously monitored. The security posture is built to absorb whatever comes next. No new model or framework rattles a program built on that foundation. 𝟮. Patching the full backlog was never going to work. It works even less now. Sometimes there is no patch yet. Sometimes the system is legacy and cannot be touched. The only path forward is pinpointing the small fraction that is actually reachable in your environment, and eliminating them even when patching is off the table. 𝟯. The time to change the paradigm is now. The CISOs already running with us moved before they had to. Everyone else will be moving under pressure. I spent 15 years on the other side of this problem, leading Israel's National Red Team. I never thought the timing would line up like this. The problem I have been working on my entire career just became the number-one problem in security - not for the Head of VM, but for the CEO and the board. This is the moment to build the answer. That is what #Astelia is for. We pinpoint the handful of vulnerabilities that are genuinely reachable in your environment, and provide compensating controls for the exposures you cannot patch in time. If you are looking at your program right now and feeling that the old playbook will not survive what is coming, you’re right - we can help. I took this photo during my latest visit to South Florida. It captures the sense of calm and confidence we want CISOs to feel when discussing Mythos in board meetings.
- LINKEDIN · IMAGESince 7 Sept 2026
Mythos Didn't Just Change the Conversation. It Changed the Market. Last week, three Fortune 500 security teams opened POCs with Astelia. Their CISOs walked into Monday morning meetings and realized their vulnerability programs were built for a world where time to exploit was measured in years. It's now measured in hours, every patch ships as an exploit blueprint, and the 2.3-year window between disclosure and weaponization has collapsed to under 20 hours. They didn't come in asking how to patch faster. They came in with harder questions: 𝟭. Which of the millions of vulnerabilities in our environment can an attacker actually reach? 𝟮. When a patch isn't available or can't be deployed, what's our move? 𝟯. How do we walk into the next board meeting with specifics instead of severity charts? Those are the questions Astelia was built to answer. We pinpoint the small fraction of vulnerabilities that are genuinely reachable and exploitable in your specific environment. We show the full attack path. And when patching isn't on the table, we surface the compensating controls, segmentation changes, and network-level mitigations that close the exposure while the patch catches up. These teams aren't outliers. They're the leading edge of a shift happening in every CISO conversation right now. If you're sitting with the same questions, let's talk.
- LINKEDIN · IMAGESince 7 Sept 2026
100+ companies signed OpenAI's open letter warning that AI-enabled cyber attacks will become far more widespread and sophisticated in the coming months. Each cyber defense instruction in this letter leaves an open question: ▪️ Fix the highest-risk weaknesses at incident speed. What does "high-risk" mean in your network? ▪️ Verify results without disrupting services. Is the attacker's route closed, or did a patch just go out? ▪️ Use compensating controls where you can't patch. Which control breaks the path? You can't answer any of these without network reachability. 👉Here's the breakdown and what you can do about it: https://lnkd.in/ep7E-xKb
6 of 213 adsSign up to see every Astelia ad, filter by format and date, and get alerts on new ones.
See all 213 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.