LinkedIn thought leader ad examples
130 thought leader ads are live on LinkedIn right now, from 138 companies. Browse real ones, filtered by industry.
- Base OperationsRecorded 10 Sept 2026
Security teams have been stuck with three bad options when it comes to assessing risk across their company operations. 1. Do nothing and stay in permanent react mode. 2. Manually gather threat data that's inconsistent, slow, and impossible to scale beyond a handful of locations. 3. Or use black box risk scores that lack context, cover limited geographies, aren’t granular enough, and update once a year. None of those options help protect global operations at scale. That’s why forward-thinking security teams are moving from reactive crisis management to proactive threat intelligence.
- Beyond IdentityRecorded 10 Sept 2026
SAP Taulia faced a coordinated attack on over 200 Okta accounts. Not one was compromised. When attackers targeted Taulia’s identity provider, they hit a wall: identity defenses that verify both the user and the device with cryptographic proof — something attackers can't steal. Without passwords, OTPs, or push notifications existing, attackers had nothing to phish, social engineer, or bypass. Why does that matter? Because Taulia serves Fortune 500 clients that expect uncompromising security at every login. Security is often hard to quantify. This time, it wasn’t: - 1,800+ hours saved per month from password friction alone - Zero identity-related incidents since becoming a customer - The #1 cause of security incidents, credential compromise, now prevented every time We’re proud to work with forward-thinking leaders like Duke H. Le, Taulia’s Sr. Director of Corporate IT, who understand that identity is the first line of defense, and that security can be a competitive advantage. See how Taulia turned identity security into a measurable business advantage: https://lnkd.in/eKVkuNjw Beyond Identity
- Beyond IdentityRecorded 10 Sept 2026
CISOs facing the rise of deepfake threats need to understand one key distinction: probabilistic vs. deterministic security. Deterministic security ensures you can always prove: - the person is who they claim to be - they’re operating from the device you know and expect - with the security controls you require — and never a deepfake. Listen to the full conversation on the Cloud Security Podcast: https://lnkd.in/eSNzTA-b Beyond Identity
- AsteliaSince 7 Sept 2026
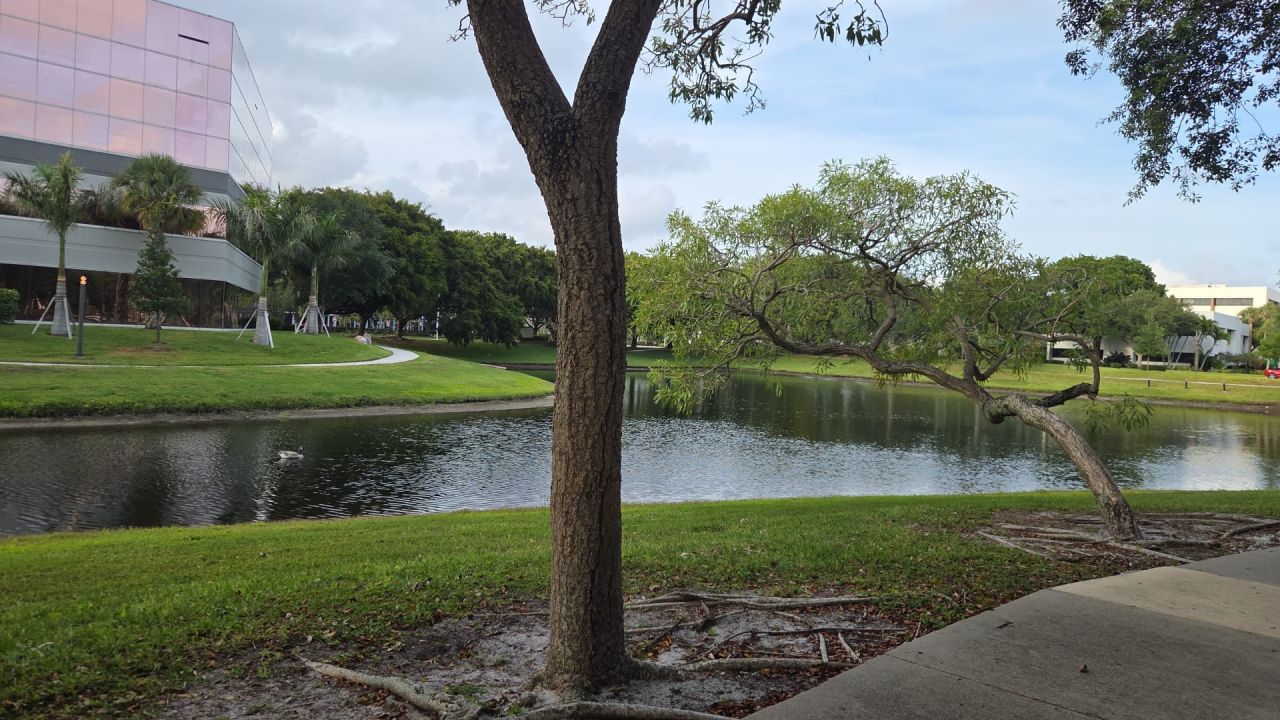
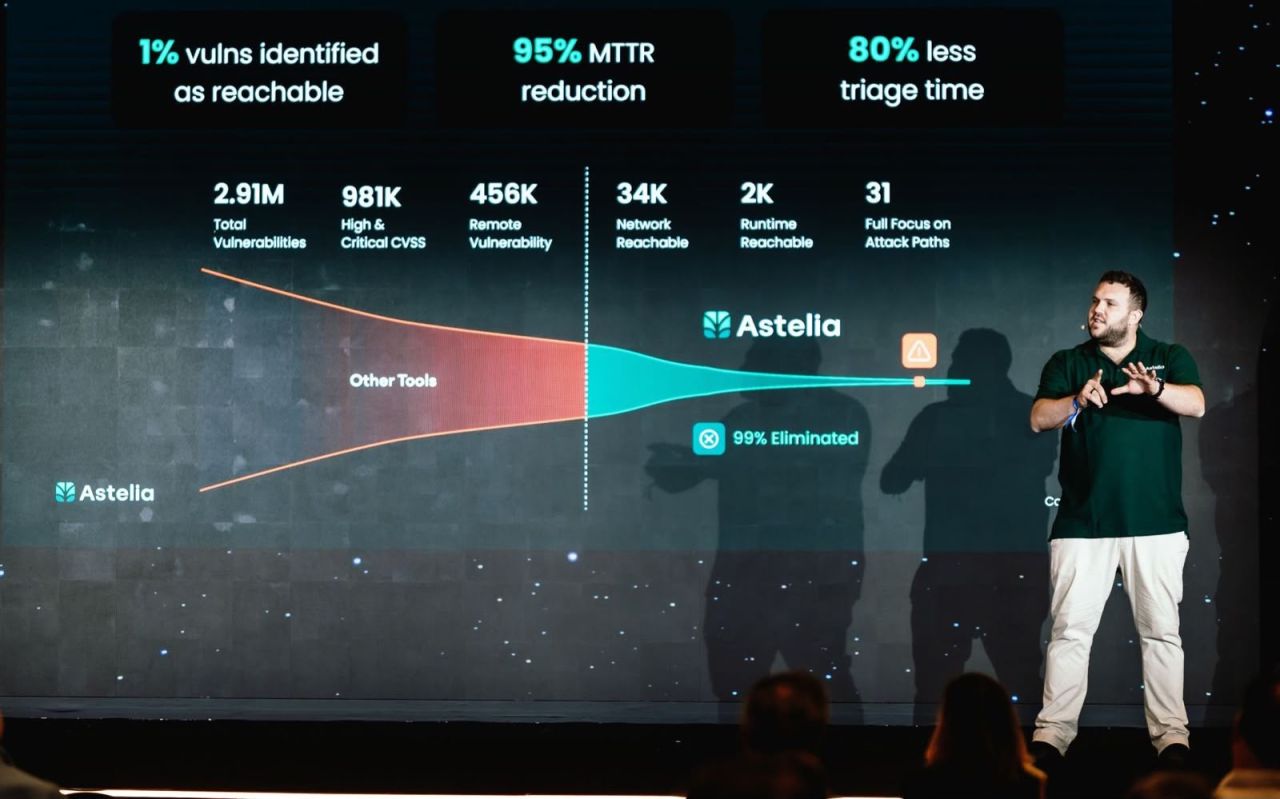
𝗠𝘆𝘁𝗵𝗼𝘀 𝗰𝗵𝗮𝗻𝗴𝗲𝗱 𝗲𝘃𝗲𝗿𝘆𝘁𝗵𝗶𝗻𝗴. The boards are not asking technical questions anymore. They are asking the question CISOs cannot answer in CVSS language: “How are you protecting the organization from Mythos attacks?” I just spent two weeks in face-to-face meetings with Fortune 500 and Fortune 2000 CISOs across Houston and Miami. Different industries, different stacks, same conversation in different words. The smartest CISOs in the room are not asking whether they are ready for Mythos. They already know Mythos is a symptom, not the disease. They are asking the bigger question: how do we run a security program when the time-to-exploit keeps collapsing, while security teams cannot scale fast enough to keep up, and legacy systems cannot always be touched? Here is what I told every security leader I sat with: 𝟭. The next board meeting is where you own the table. Not because you survived another quarter. Because you walk in showing the organization is already ahead of the next model, the next disclosure, the next headline. Reachability is continuously monitored. The security posture is built to absorb whatever comes next. No new model or framework rattles a program built on that foundation. 𝟮. Patching the full backlog was never going to work. It works even less now. Sometimes there is no patch yet. Sometimes the system is legacy and cannot be touched. The only path forward is pinpointing the small fraction that is actually reachable in your environment, and eliminating them even when patching is off the table. 𝟯. The time to change the paradigm is now. The CISOs already running with us moved before they had to. Everyone else will be moving under pressure. I spent 15 years on the other side of this problem, leading Israel's National Red Team. I never thought the timing would line up like this. The problem I have been working on my entire career just became the number-one problem in security - not for the Head of VM, but for the CEO and the board. This is the moment to build the answer. That is what #Astelia is for. We pinpoint the handful of vulnerabilities that are genuinely reachable in your environment, and provide compensating controls for the exposures you cannot patch in time. If you are looking at your program right now and feeling that the old playbook will not survive what is coming, you’re right - we can help. I took this photo during my latest visit to South Florida. It captures the sense of calm and confidence we want CISOs to feel when discussing Mythos in board meetings.
- AsteliaSince 7 Sept 2026
I watched a CISO at a Fortune 500 company go quiet in the middle of our demo. He was going through our funnel, following one attack path, port by port, all the way down to the single asset it reached. He looked at it for a while and then said something like, "I've looked at a lot of these dashboards. This is the first time I can actually see why a vulnerability is critical, instead of relying on a score telling me it is." That's the part that matters to me. Not the deal, not the signature. The moment reachability clicks as the thing that actually matters. Most of this market sells risk management, which is really just a smarter guess at what might matter. We don't rank guesses. We show the actual network path an attacker would have to take, and whether it's open. It's a binary question: reachable or not. That's usually what gets us the next conversation with large enterprises like his, because a team that's already seen every tool on the market is looking at real evidence instead of another score.
- AnvilogicRecorded 7 Sept 2026
Today, we launch Anvilogic’s 𝗔𝗜 𝗦𝗢𝗖, an adaptive platform that meets you where you are, and finally lets you run detection and triage across all your data, in a single platform. We have always envisioned being a complete SOC platform and started building our foundation in detection engineering, which we knew would power the rest of the journey. And now, we are ready to launch into the next phase of our journey by extending our platform beyond detection engineering to an 𝗔𝗜 𝗦𝗢𝗖 𝗽𝗹𝗮𝘁𝗳𝗼𝗿𝗺, that extends into triage, investigation and automated response, powered by the principles that got us here: solid cybersecurity domain expertise, persona-specific workflows, context-rich transparency and a high bar for customer satisfaction. Our platform uses large language models (LLMs) in conjunction with your context via domain-infused prompts and rich enrichment feeds to search across data sources, build relevant/custom detections, raise actionable alerts, disposition them accurately, explain our reasoning, and move them downstream for resolution/action. All of this is accomplished using 𝗔𝗜 𝗮𝗴𝗲𝗻𝘁𝘀 𝘁𝗵𝗮𝘁 𝗮𝘂𝘁𝗼𝗺𝗮𝘁𝗲 𝘀𝗽𝗲𝗰𝗶𝗳𝗶𝗰 𝗽𝗲𝗿𝘀𝗼𝗻𝗮 𝘄𝗼𝗿𝗸𝗳𝗹𝗼𝘄𝘀 𝗳𝗼𝗿 𝘀𝗲𝗮𝗿𝗰𝗵, 𝗱𝗲𝘁𝗲𝗰𝘁, 𝘁𝘂𝗻𝗲 𝗮𝗻𝗱 𝘁𝗿𝗶𝗮𝗴𝗲. The results are high-precision and actionable, with full context because of our upstream detection engineering capabilities tailored to your environment – with better data management and detection strategy comes highly effective triage and investigation. No more human L1, L2. Agents with human oversight can up the game. Elevate human analysts to richer tasks higher up the SOC stack. Summary of AI agents and platform capabilities we’re announcing today: 1. Search: across data repos using natural language, schema-aware and optimized 2. Build: detection-as-code, auto-deployed to your SIEM or data lake or both 3. Tune: continuous environment-aware auto-tuning of detections, with allow-listing 4. Triage: auto-triage alerts with rich context, high precision, guidance and explainability 5. Manage: simple data onboarding and auto-ETL/normalization across supported repos This isn’t just alert scoring using LLMs. An AI SOC platform means much more than that: its 𝗲𝗻𝗱-𝘁𝗼-𝗲𝗻𝗱 𝗦𝗢𝗖 𝗼𝗽𝗲𝗿𝗮𝘁𝗶𝗼𝗻𝘀 𝘁𝗵𝗮𝘁 𝗯𝗿𝗶𝗻𝗴 𝘁𝗵𝗲 𝗱𝗲𝘁𝗲𝗰𝘁 & 𝗿𝗲𝘀𝗽𝗼𝗻𝗱 𝘁𝗲𝗮𝗺𝘀 𝘁𝗼𝗴𝗲𝘁𝗵𝗲𝗿, 𝘄𝗶𝘁𝗵𝗼𝘂𝘁 𝘀𝗶𝗹𝗼𝘀 𝗮𝗻𝗱 𝗰𝗼𝗻𝗳𝗹𝗶𝗰𝘁, 𝗳𝗶𝗻𝗮𝗹𝗹𝘆. This is detections that work, and triage you can trust, because it’s grounded in the detection strategy that we designed for you, proven in enterprise environments across our customers worldwide. Read more on our new website: www.anvilogic.com. And see what our customers are saying.
- AnvilogicRecorded 7 Sept 2026
New episode with returning guest & favorite CON partner Scott Rodgers has dropped🔥 Scotty and I talk highlights from the Mandiant (part of Google Cloud) M-Trends.... We cover: Stolen Creds leapfrogging 🐸 phishing The infostealer industrial complex The quiet death of BEACON (and what that means) F5’s nation-state saga (that happened post-M-Trends) Plus: scream therapy. I promise, it tracks. Register to be notified of every episode drop on 🔗 https://lnkd.in/gP3HJUQ7
- AlcatrazRecorded 4 Sept 2026
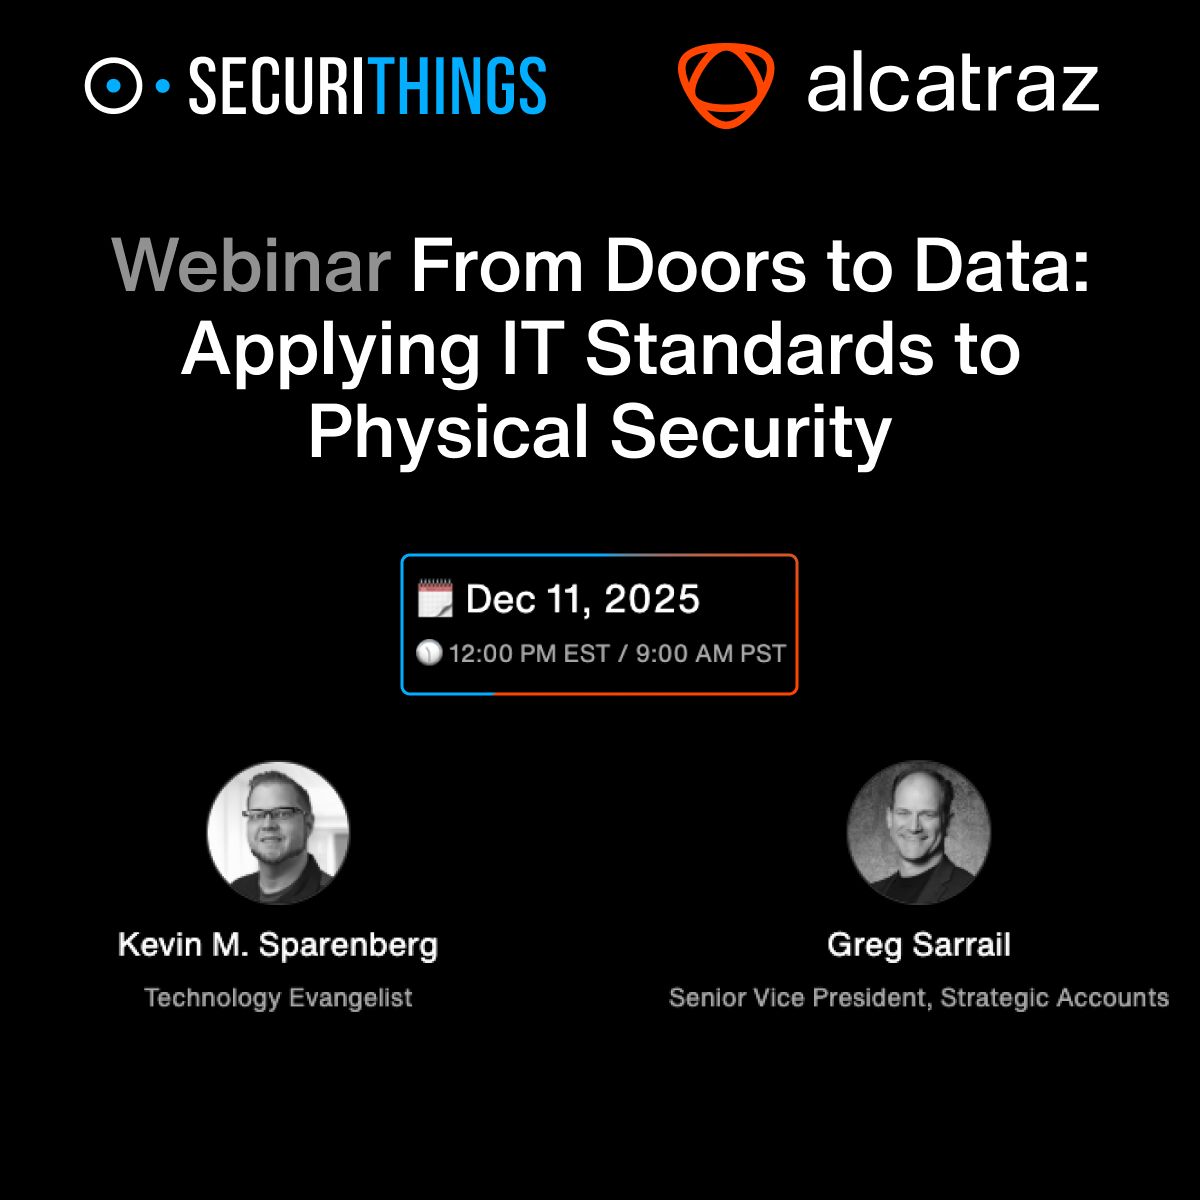
Enterprise security leaders are tasked with protecting data and employees from every vulnerability, elevating physical security to IT-level standards. On Dec 11, I’m joining @Kevin M. Sparenberg from SecuriThings for a live webinar on how we’re helping enterprises modernize physical access with visibility, automation, and IT-grade control without ripping and replacing legacy infrastructure. If you're looking to do more with less and to simplify compliance and device management at scale, this one's for you: 👉 Register here: https://lnkd.in/gsnqhjZ9 #facialauthentication, #alcatrazai, #securithings, #nomoretailgating, #zerotrust, #accesscontrol,
- AlcatrazRecorded 4 Sept 2026
We took a quick pulse check with Physical Security peers during our latest Webinar, and the results confirmed what we’re seeing across the industry: facial authentication is on the rise: 46% of attendees were already using biometrics for access control and 84% were most interested in facial authentication as their preferred biometric modality. At a recent event, I recorded this video below to show how frictionless facial biometric access control is with Alcatraz. You can just walk in like you belong; no badging, no holdups. It’s fast, hands-free, and built to get you where you’re going without thinking twice. 🚨 In terms of security? Alcatraz helps detect and prevent tailgating or piggybacking incidents instantly. When someone follows too closely behind an authorized person, the system detects it and triggers an alert in real time. 🪪 Concerned about privacy? Alcatraz never stores personal images or PII. It’s encrypted, opt-in, and designed to meet the strictest privacy standards. Interested in seeing a quick personalized demo? Book a time on my calendar or reach out to me at any time: https://lnkd.in/gDXswV4g #AccessControl #PhysicalSecurity #Biometric #BiometricAccessControl
- advact AGRecorded 3 Sept 2026
Unser Ziel ist es, dass deine Mitarbeitenden den Umgang mit unserem Outlook-Add-in üben können und wissen, dass es diesen Knopf gibt. Das erreichen wir durch Kommunikation via Intranet oder Infomail und durch simulierte Angriffe. Wir bauen echte Angriffe als Simulation nach und verschicken sie das ganze Jahr über zufällig. Wer schon gut sensibilisiert ist, bekommt weniger Simulationen. Wer noch Mühe hat, bekommt mehr Chancen zum Üben. Die Auflösung erfolgt sofort im Outlook ... “Das war eine Simulation. Melde echte Mails bitte genauso weiter.“ So lernen deine Mitarbeitenden, im Ernstfall richtig zu handeln und den Knopf konsequent zu nutzen. Wissen deine Mitarbeitenden bei einer verdächtigen Mail, was zu tun ist?
- advact AGRecorded 3 Sept 2026
Maximal zwei Stunden, nachdem eine Meldung oder eine neue Phishing-Welle hereinkommt, geben wir Bescheid. Der Schnitt liegt bei 53 Minuten. Ein Kunde von uns hat das ausgerechnet. Wenn 300 Leute innerhalb weniger Minuten das gleiche Mail bekommen, melden die ersten das sofort. Mit dieser Geschwindigkeit kann man extrem viel erreichen. Wir erkennen das Phishing-Mail und lassen es bei den restlichen 299 Leuten direkt aus dem Postfach löschen. Bevor sie das gefährliche Mail überhaupt gelesen haben. Könnt ihr euch darauf verlassen, dass bei 300 gefährlichen Mails wirklich niemand den falschen Link anklickt?
- CyberdaySince 24 Mar 2026
AI is starting to reshape how ISMS work actually gets done. Not in a “replace everything” way - but with important, practical things that usually take the most time: - drafting controls - interpreting requirements - keeping things up to date - answering “what should we focus on next?” - helping with hard but important things, like risk management or internal audits These are the areas where teams tend to get stuck - not because they lack intent, but because the work is repetitive, unclear, or hard to prioritize. That’s where AI agents can start to make a real difference. In our next webinar on Thursday, April 2nd, we’ll look at how AI agents can support ISMS work in practice: - where they actually help (and what's left for you) - how to use them without overcomplicating things - what this looks like in an ISO 27001 / NIS2 context You can join us here: https://lnkd.in/dhqrb_FY If you’ve been thinking about AI in security or compliance - or wondering if it’s just hype - this one’s for you. #ISO27001 #AI #cybersecurity #infosec #compliance
- 1KosmosRecorded 29 Aug 2026
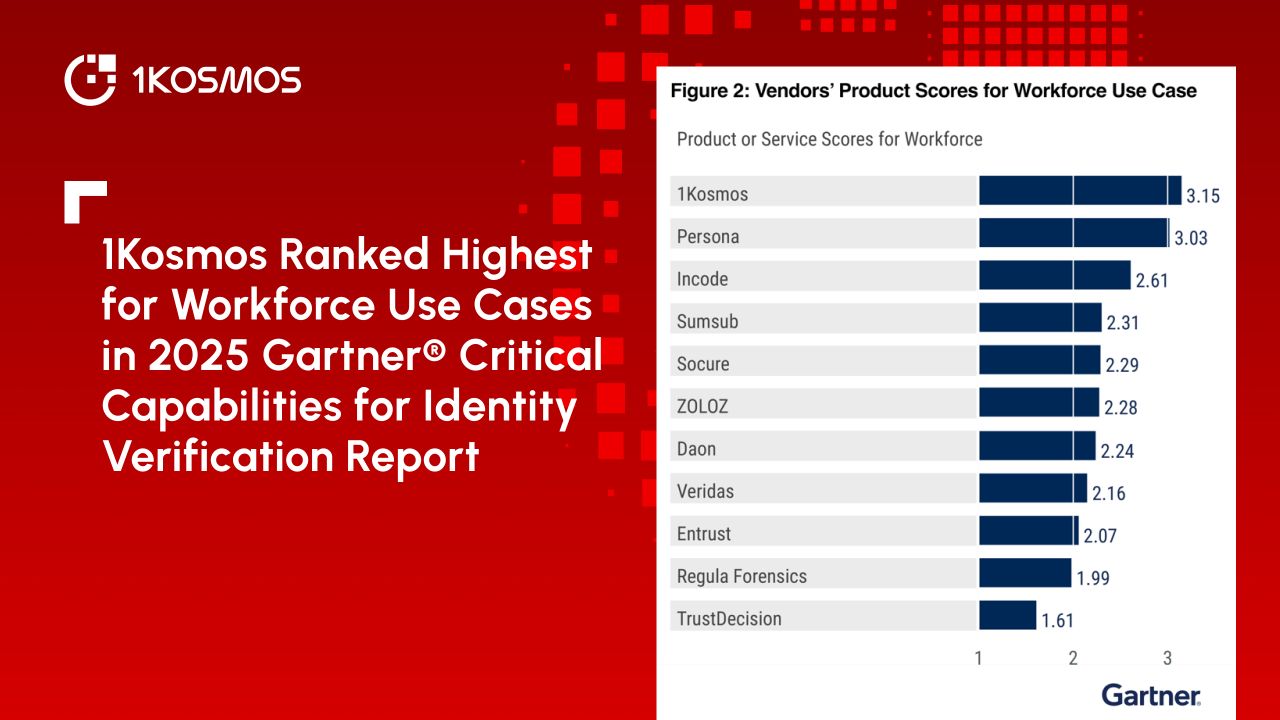
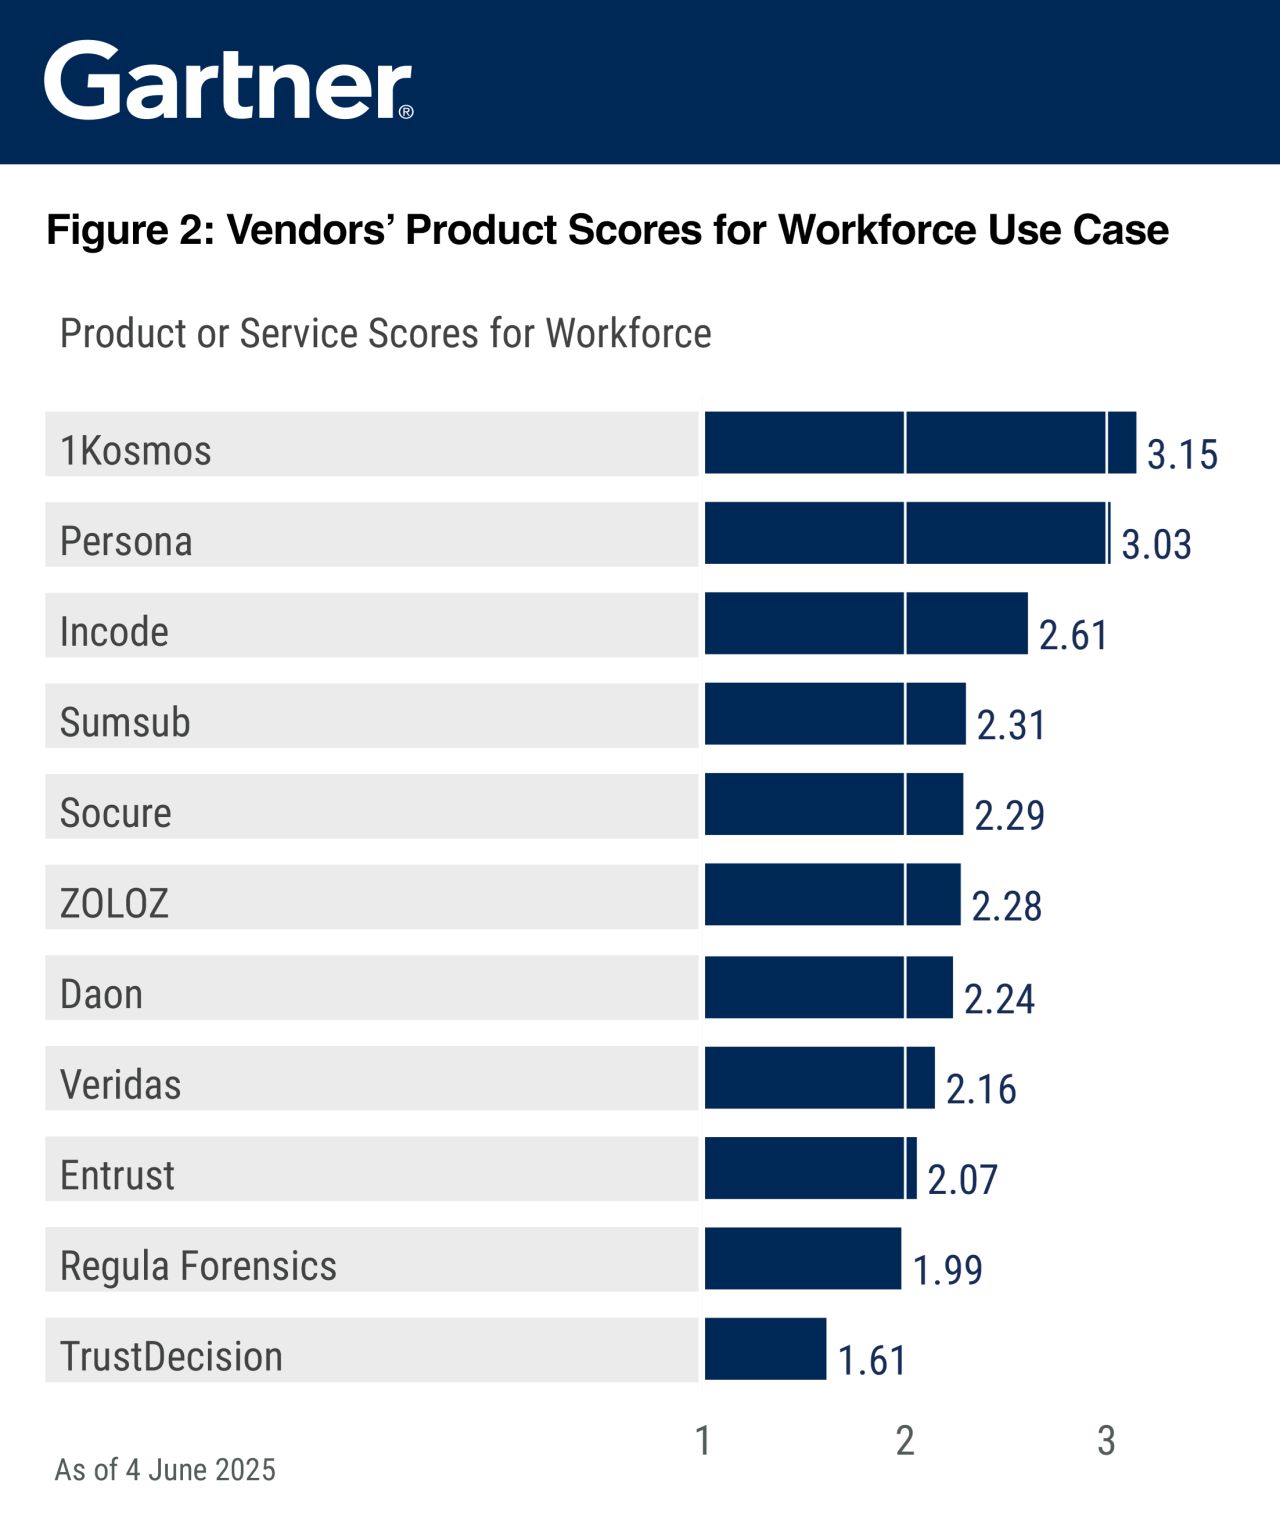
EXCITING NEWS: I am so proud of our team 1Kosmos..... Identity verification is no longer a nice-to-have — it’s foundational. At 1Kosmos, we’re proud to be leading the charge. 2025 Gartner® Magic Quadrant for Identity Verification, 1Kosmos has not only tripled annual recurring revenue in the past year and secured $57 million in new funding, Even more meaningful: in Gartner’s Critical Capabilities for Identity Verification report, we ranked #1 in IDV among all vendors for workforce use cases Read my blog: https://lnkd.in/enPj9t4q Michael Engle Huzefa Olia Jens Hinrichsen Michael Cichon Ashwin Achar Vikram Subramanian Sheetal Elangovan Abigail McKenney Erica West Jennifer Boulay
- 1KosmosRecorded 29 Aug 2026
No doubt Gartner reports help call out the winners in the industry – and I saw my buddies at 1Kosmos land the top spot for Workforce Identity Verification this year 😎 Identity verification is a wild topic because it’s not just KYC… it’s part of onboarding, account recovery, and your whole security posture. It’s a core part of cybersecurity across the workforce! 1Kosmos has been crushing it with high marks for integrations across Identity Governance and Administration, Access Management, and IT Service Management (IGA/AM/ITSM acronym soup, but all the right stuff 😁) with risk signals like device profiling and privacy controls for regulated industries. Take a quick peek through the Gartner report and see how 1Kosmos keeps winning: https://jh.live/1kosmos (oh, and give them a big congrats on their Series B raise, too!)
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.