LinkedIn image ad examples
3 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- CleafySince 17 Sept 2026
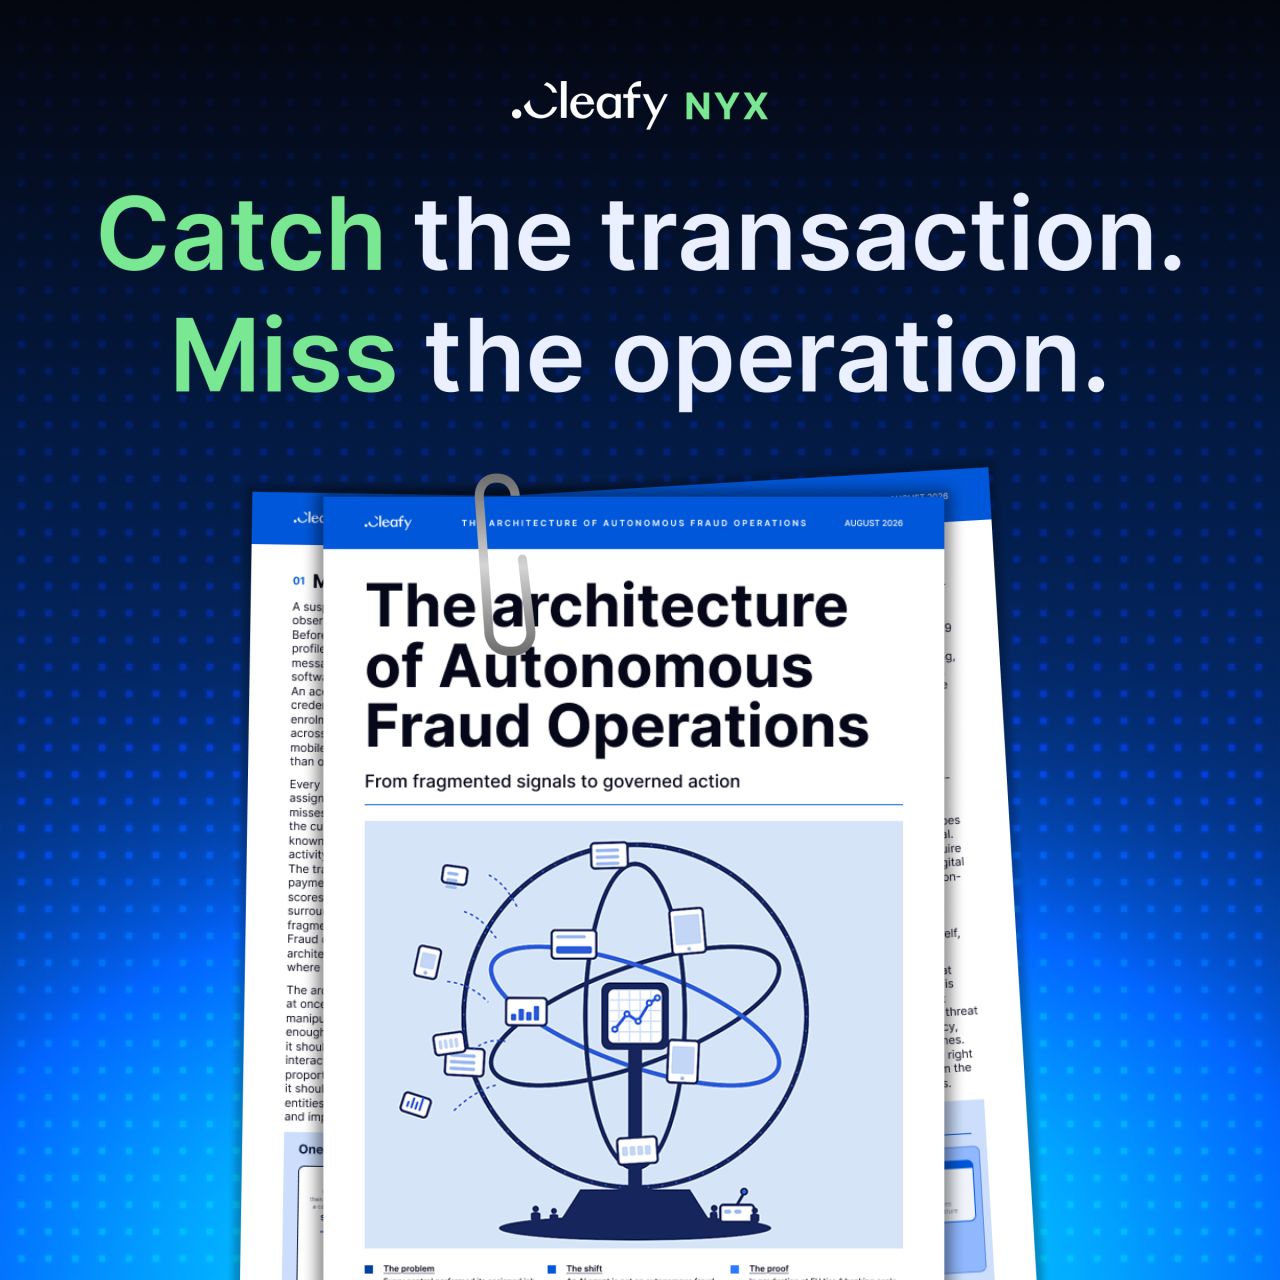
Catch the transaction. Miss the operation. That's what happens when detection stops at the signal instead of the pattern. This whitepaper shows how fraud teams can get from fragmented signals to governed action.
- CleafySince 17 Sept 2026
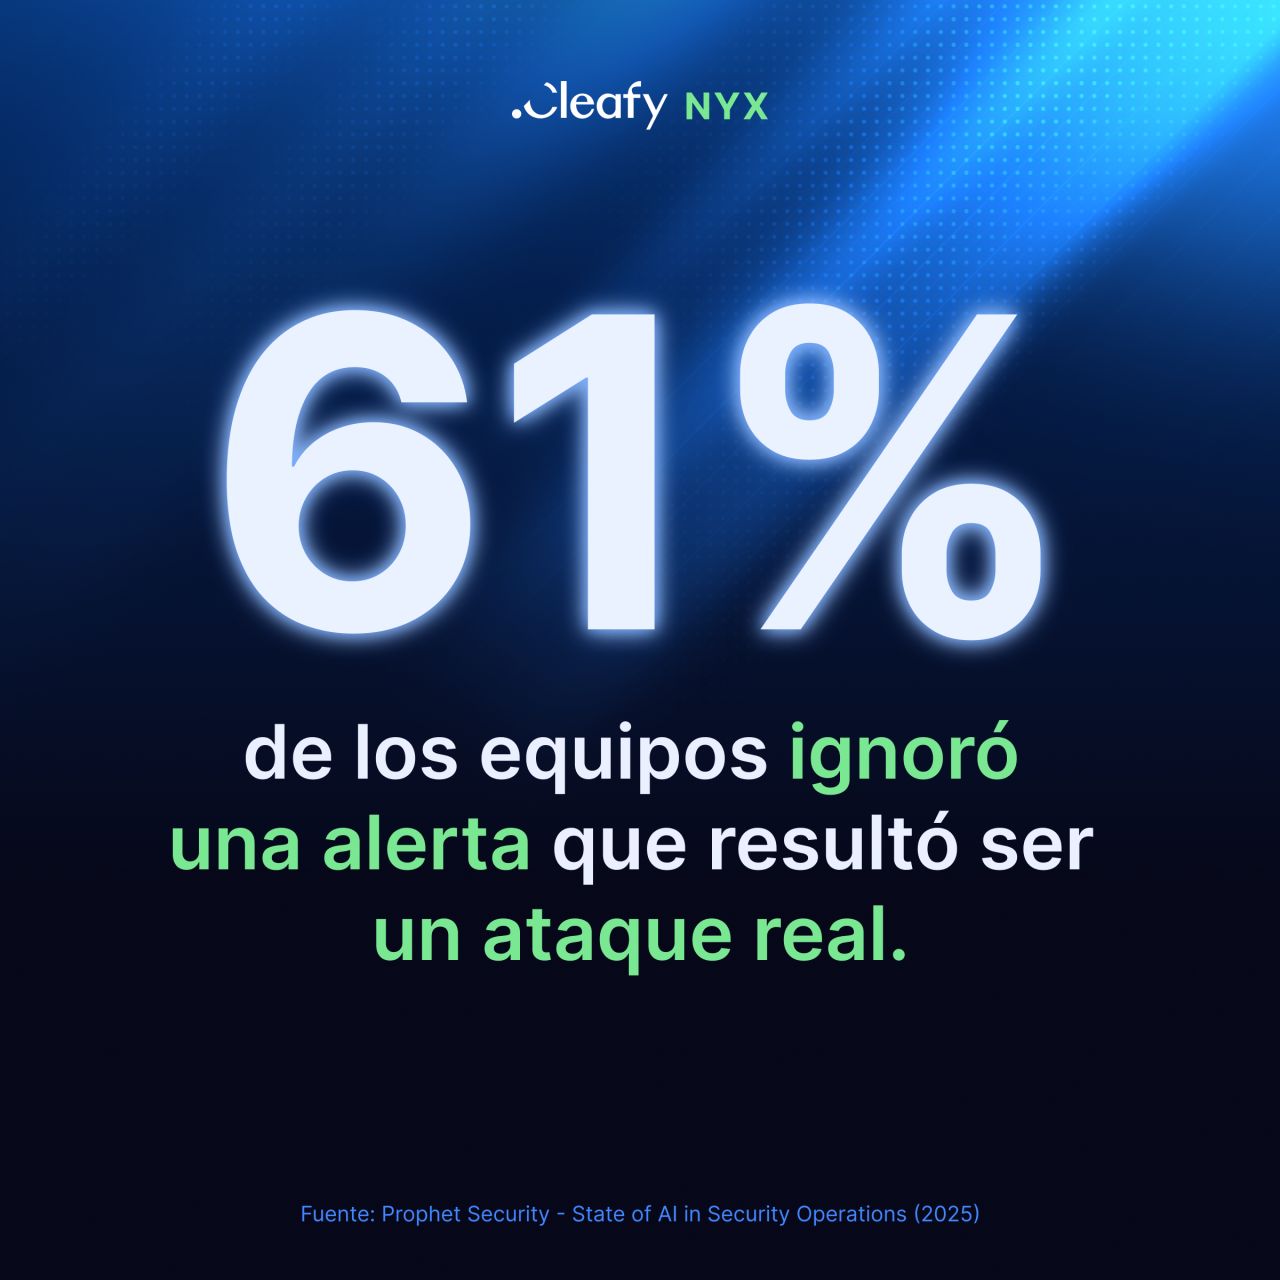
El 61% de los equipos ha ignorado una alerta que resultó ser un ataque real. No por descuido, sino por trabajar con fragmentos mientras el atacante ve toda la operación. Nuestro nuevo informe explica por qué las señales fragmentadas dejan escapar el fraude coordinado, y qué cambia con una visión conectada.
- BugHuntRecorded 8 Oct 2026
Uma das primeiras perguntas que aparece quando o programa de bug bounty chega no jurídico é se ele cria um novo risco para a empresa. A resposta técnica é não. Qualquer sistema com ativos expostos na internet já está sujeito a tentativas de teste por terceiros, com ou sem autorização. Isso acontece independentemente de haver um programa de bug bounty. O que o programa muda é o controle sobre esse processo. Vulnerabilidades que antes poderiam chegar sem identificação, sem regras e sem um canal definido passam a ser reportadas por pesquisadores identificados, seguindo a política, o escopo e os limites estipulados pela própria empresa. Sob a ótica da LGPD, um programa de identificação de vulnerabilidades pode fazer parte do conjunto de medidas técnicas e administrativas adotadas pela empresa para proteger seus dados e sistemas. Ou seja: o programa não cria a exposição. Ele estabelece regras, identifica quem participa e cria um canal para que vulnerabilidades sejam reportadas e tratadas de forma organizada.
- BugHuntRecorded 8 Oct 2026
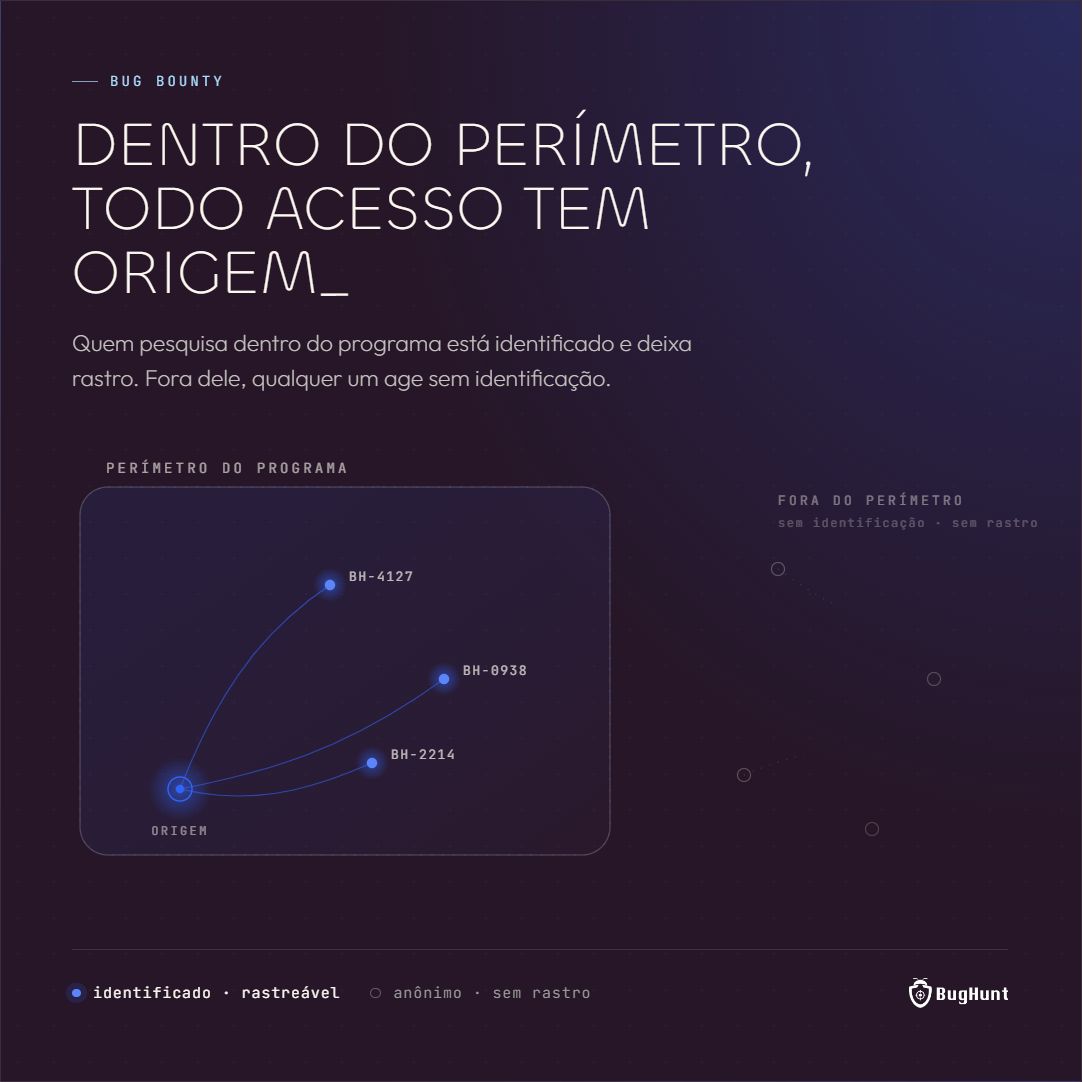
O que impede um pesquisador de explorar o que encontrou em vez de reportar? A resposta começa pelo perfil de quem participa de um programa de bug bounty. Quem participa do programa está identificado na plataforma, aceita previamente termos de conduta e precisa seguir as regras definidas por cada empresa. Isso muda bastante a dinâmica. O pesquisador constrói uma reputação ao longo do tempo, e sua participação em novos programas depende de agir dentro das regras e reportar corretamente as vulnerabilidades encontradas. É um modelo em que os incentivos apontam na direção certa. Isso não significa que um programa elimina completamente o risco de alguém agir de forma maliciosa. Significa que, diferente de um cenário sem programa, existe identidade, regras de atuação, histórico de participação e consequências para quem ultrapassa os limites estabelecidos. Sem um programa, uma vulnerabilidade pode ser descoberta por alguém que a empresa não conhece, sem escopo definido, regras de atuação ou um canal formal para o reporte. Dentro de um programa de bug bounty, o cenário é diferente. O pesquisador sabe exatamente o que pode testar, quais são os limites e como deve reportar o que encontrou. Para o jurídico, esse é um ponto importante: não é apenas uma questão de autorização para testar. É também sobre criar regras, identificar quem participa e estabelecer um canal formal para lidar com vulnerabilidades. É isso que transforma uma interação que já poderia acontecer de maneira desestruturada em um processo com mais controle e previsibilidade.
- GarancySince 22 Sept 2026
Kompromisslose Sicherheit aus Deutschland. Steuern Sie Identitäten, Rollen und Berechtigungen mit der Identity-Management-Software von Garancy.
- GarancySince 22 Sept 2026
Identity-Management-Software aus Deutschland. Steuern Sie Identitäten, Rollen und Berechtigungen souverän – für Sicherheit ohne Hintertüren.
- Fort CyberSince 19 Sept 2026
45% dintre organizațiile care au răspuns studiului nostru se încadrează în segmentul cu cel mai ridicat nivel de maturitate cibernetică. Când verificăm însă trei măsuri concrete, precum monitorizare permanentă, plan de răspuns testat și exerciții regulate de securitate, procentul scade la 27%. 39 de organizații considerate „mature" nu îndeplinesc simultan aceste trei criterii. Diferența dintre cele două cifre e toată povestea: a instala soluții de securitate și a scrie proceduri nu e același lucru cu a ști că funcționează. Asta se află doar înainte de un incident real, nu în timpul lui. Radiografia securității cibernetice în România 2026: 200+ respondenți, 32 de întrebări. Descarcă raportul complet👇
- ControlMonkeySince 21 Sept 2026
Recovery is not something enterprise teams can leave to assumptions. ControlMonkey helps organizations make critical cloud and SaaS configurations recoverable - with visibility into what’s protected, what can be restored, and where gaps remain. Trusted by teams at Block, Veolia, Comcast, Intel, and more.
- CyberVadisSince 22 Sept 2026
Vos fournisseurs utilisent l'IA générative. La question n'est plus "si", mais "comment" et surtout, "en avez-vous pleinement conscience ?" 💡 Chez CyberVadis, j'échange quotidiennement avec les grands groupes français sur la sécurisation de leur chaîne de valeur. Aujourd'hui, nous dévoilons avec le CESIN notre dernière étude exclusive sur la prise en compte de l'IA dans le risque cyber tiers (TPCRM). Le constat est sans appel : si les processus TPRM se consolident, la couche IA n'y est pas encore intégrée de manière structurée. Vous gérez probablement un risque IA tiers sans les outils pour le mesurer. Voici 4 "Key Takeaways" de notre étude qui méritent toute votre attention : ✔️ L'angle mort IA : 83 % des RSSI n'ont pas couvert le risque IA de leurs tiers dans leur dispositif. ✔️ Le déclaratif ne suffit plus : 65 % des tiers affirment tenir un inventaire de leurs outils IA, 4 % le prouvent. ✔️ Des contrôles à ajouter, pas un dispositif à refondre : les contrôles IA à vérifier dès votre prochaine évaluation. ✔️ Trois priorités pour agir : cartographie, clauses contractuelles et gouvernance du risque IA tiers. La bonne nouvelle ? Intégrer le risque IA ne demande pas une refonte totale de vos dispositifs, mais des mises à jour ciblées. Pour décrypter ensemble ces résultats et partager les leviers d'action concrets pour sécuriser vos écosystèmes, nous organisons un webinar de présentation exclusif : 📅 Rendez-vous le 2 octobre à 11h15 👉 Lien d'inscription : https://lnkd.in/en6wq22w Vous souhaitez recevoir l'étude complète en amont ou échanger sur la maturité TPRM de votre organisation ? Laissez un commentaire ou contactez-moi directement en message privé 📩 #CyberSecurity #TPRM #IntelligenceArtificielle #CyberVadis #CESIN #RiskManagement
- Beazley SecuritySince 23 Sept 2026
EM Protect continuously discovers and monitors your external attack surface, helping you uncover risks before attackers do. Available to eligible Beazley cyber policyholders at no cost.
- Beazley SecuritySince 23 Sept 2026
Activate EM Protect to identify exposed assets, prioritize critical vulnerabilities, and remediate what matters most. Available to eligible Beazley cyber policyholders at no cost.
- CyberVadisSince 22 Sept 2026
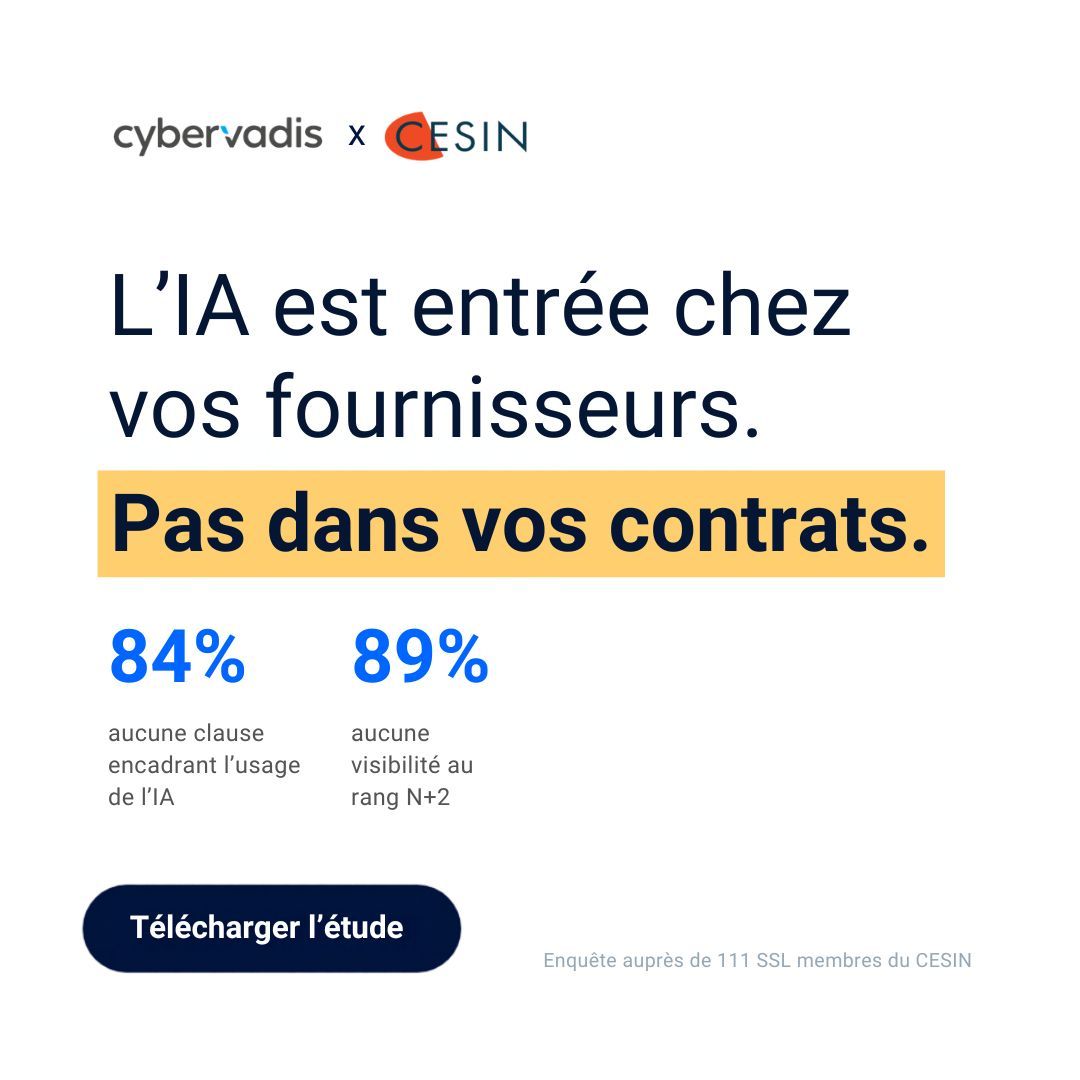
65 % de vos fournisseurs déclarent tenir un inventaire de leurs outils IA. 4 % peuvent le prouver. C'est le premier chiffre de l'étude que nous publions avec le CESIN. Il ne sort pas d'un sondage : 111 RSSI membres du CESIN d'un côté, 652 évaluations de fournisseurs vérifiées sur preuves documentaires dans 49 pays de l'autre. L'écart entre ce qui est déclaré et ce qui est démontrable, vous le connaissez déjà sur la sécurité classique. Sur l'IA il est bien pire, parce que personne n'a encore mis à jour ses questionnaires. Dans le détail : 83 % des RSSI n'ont pas couvert le risque IA de leurs tiers, 84 % n'ont aucune clause encadrant son usage, 89 % n'ont aucune visibilité au rang N+2. Le guide détaille les contrôles IA à ajouter à votre prochaine évaluation, les clauses à inscrire dans vos contrats, et par où commencer quand on part de zéro. Sans refondre votre dispositif. Téléchargez l'étude complète.
- CR GroupSince 22 Sept 2026
You might not have heard of CR Group . We build certified encryption and secure communications infrastructure for defense organisations, government agencies and critical infrastructure operators across Europe. Not a crowded cocktail party topic. The market we are working in are evolving. Europe is now looking much closer at the question: who controls the technology our security depends on? The answer we are arriving at is: it needs to be Europe. In my role as CEO of CR Group I bring a view on how to build an ecosystem of focused European tech leaders that are collectively stronger than they’d be alone. Tutus Data in Sweden and Sentyron in the Netherlands – certified, mission driven, and building the sovereign security infrastructure Europe needs. Over the coming months I’ll share how I think about this market and what I’m seeing from the inside. Not as an expert, but as a company builder paying close attention to current developments. Worth following if this space interests you.
- FiligranSince 23 Sept 2026
4 years ago, Julien and I founded Filigran to give a home to #OpenCTI, the open-source platform born inside a threat intelligence team, for other threat intelligence teams. The name comes from filigree, the craft of assembling fine threads into something precise and strong, and it still describes what this community does every day: pulling on a signal, patiently, until the structure appears. Today, what we build reaches far beyond threat intelligence, and the name has never fit better, as more and more threads come together around a single conviction: defense has to be proactive, and informed by the threat. None of it would exist without the analysts, engineers and contributors who have been building it with us, in open source, since before Filigran even existed. On October 15 in Paris, THREAD, our first conference, will bring this community together for a full day. I wanted it deeply rooted in our DNA: a day made for practitioners and for the leaders who rely on them, where the people who do the work are the ones on stage. Most of it happens in labs, workshops and roundtables, and part of our roadmap will be put to a vote, with a commitment on our side to build what comes out on top. Security leaders and practitioners from Accenture, Thales, Richemont, Dassault Systèmes, Centrica and many others will be with us, and more will be revealed in the coming days. THREAD takes place as Filigran turns 4. I have been looking forward to this day for a long time, and I cannot think of a better way to mark these four years than a day with the community, the customers and the partners who made them possible. It is the first edition of what we intend to make an annual gathering and, as always, only the beginning. So far, most of this community has met in threads, on Slack and GitHub. This time, we will be in the same room, and I hope you will be part of it. Come pull the thread with us! https://lnkd.in/esqa-wwx See you in Paris. #PullTheThread
- Code Blue CyberRecorded 8 Oct 2026
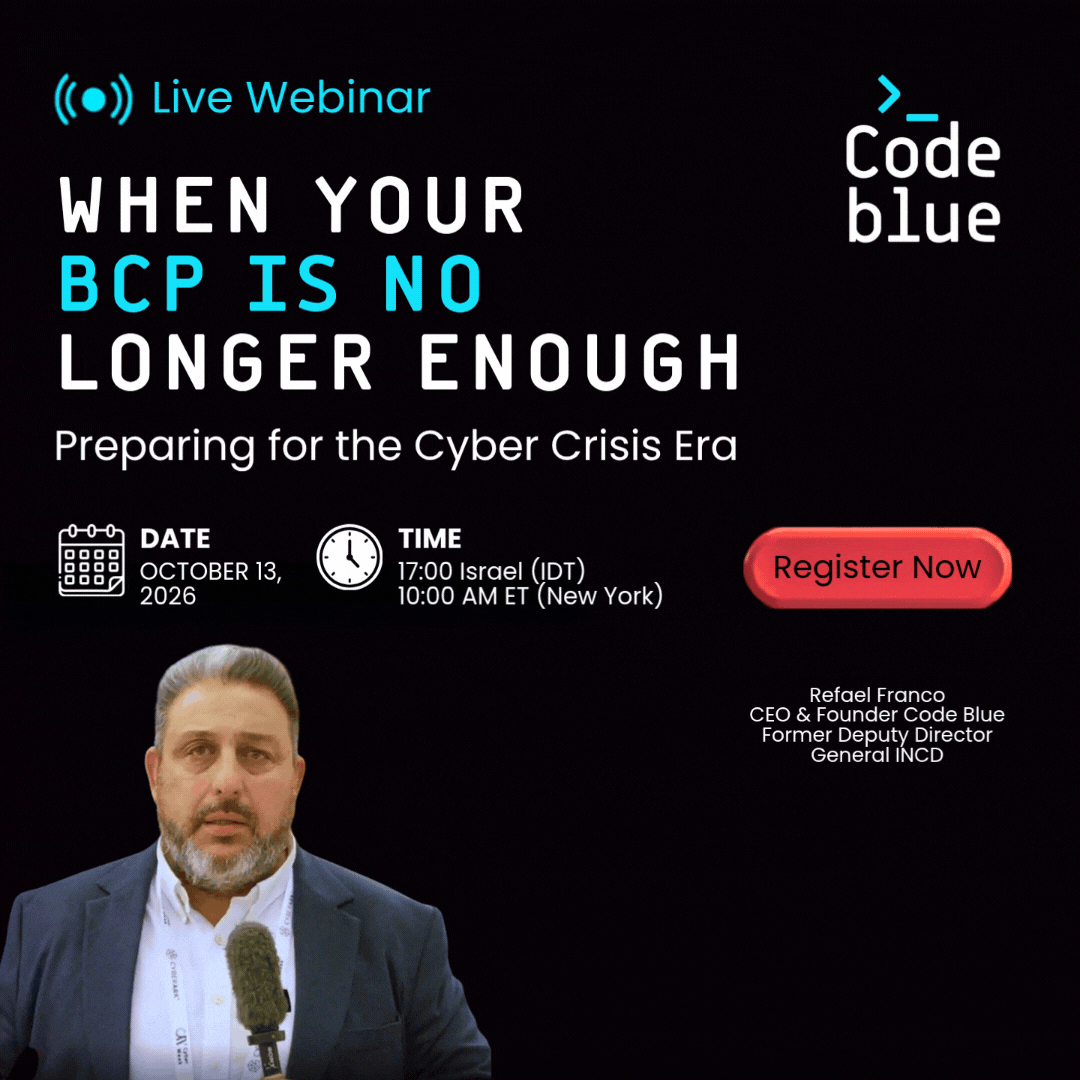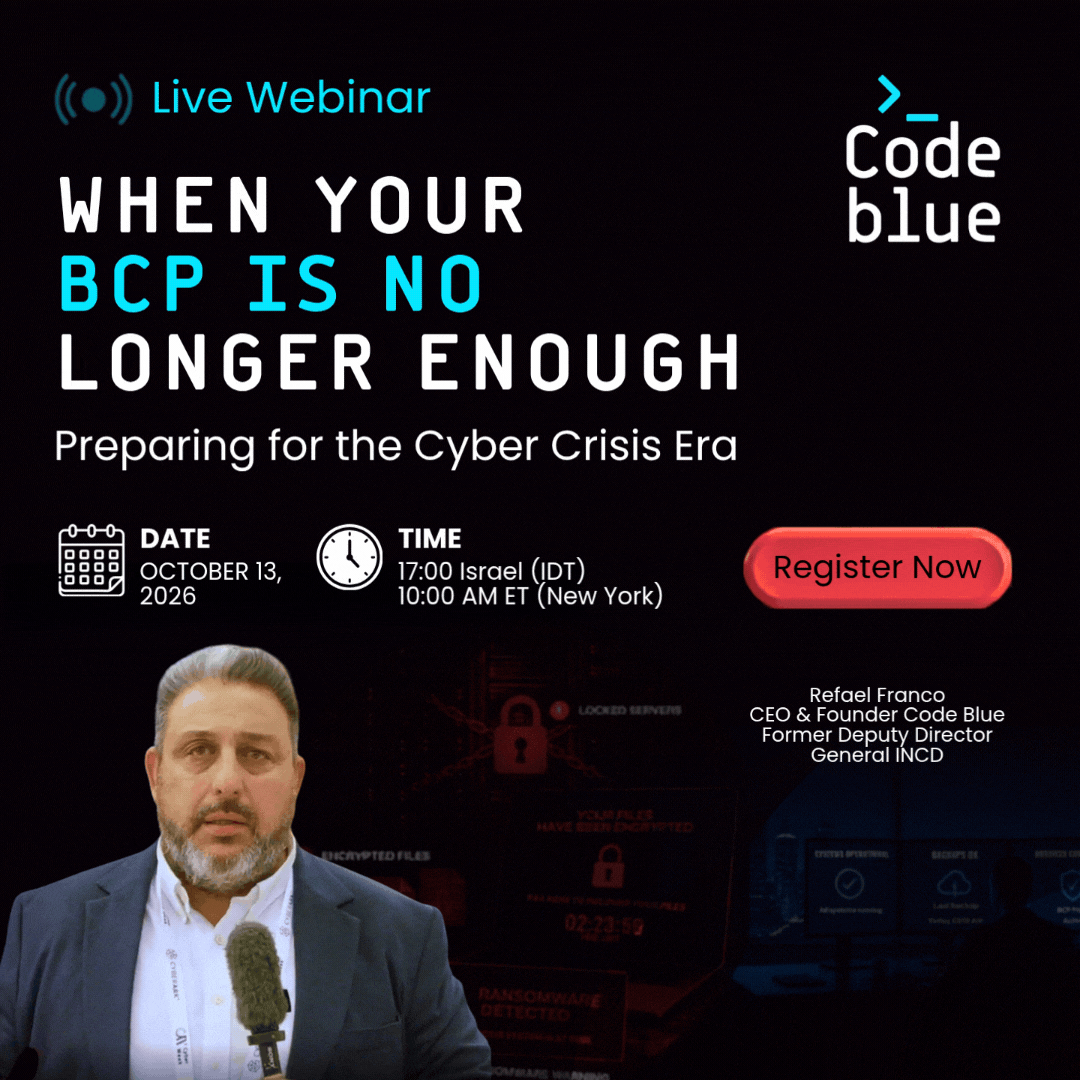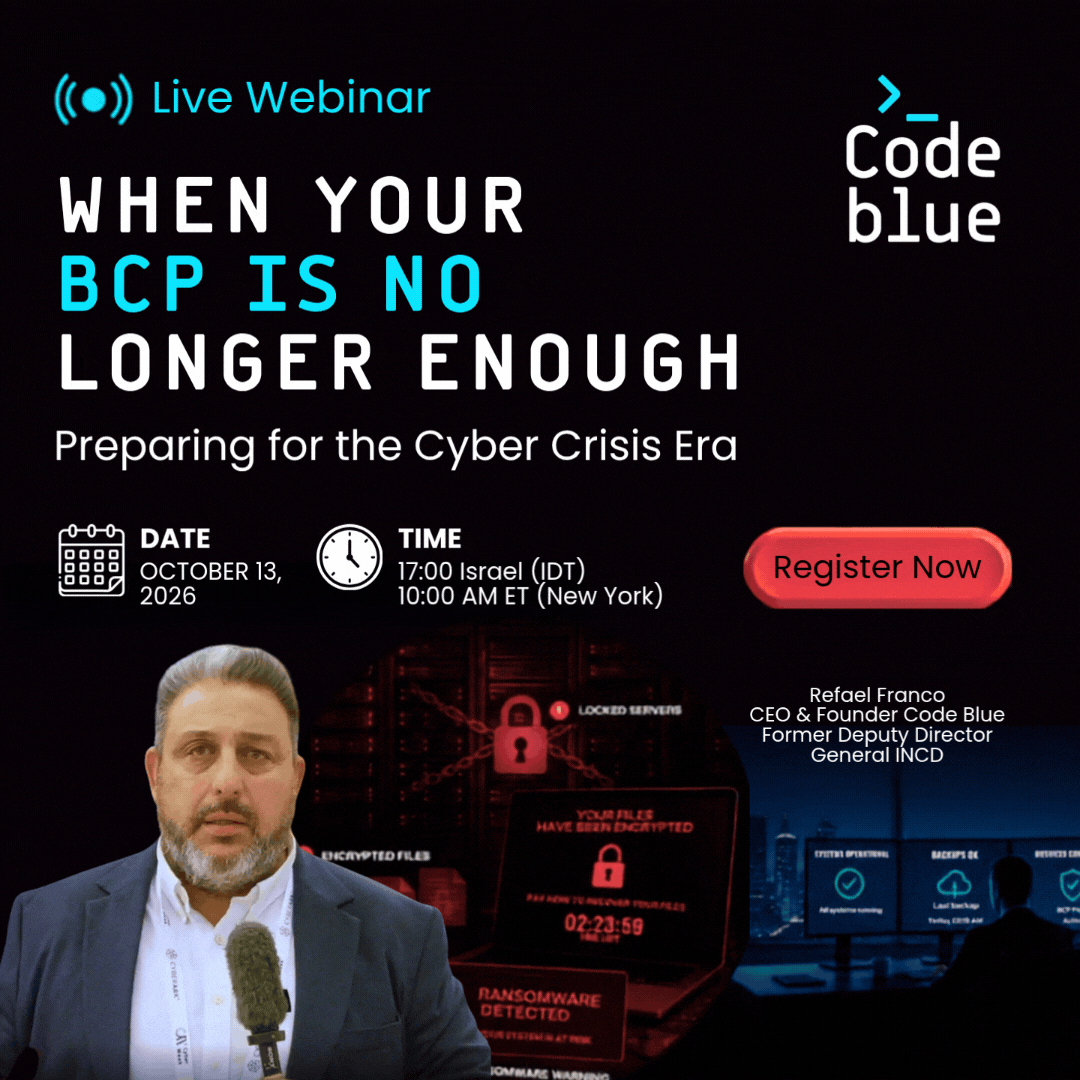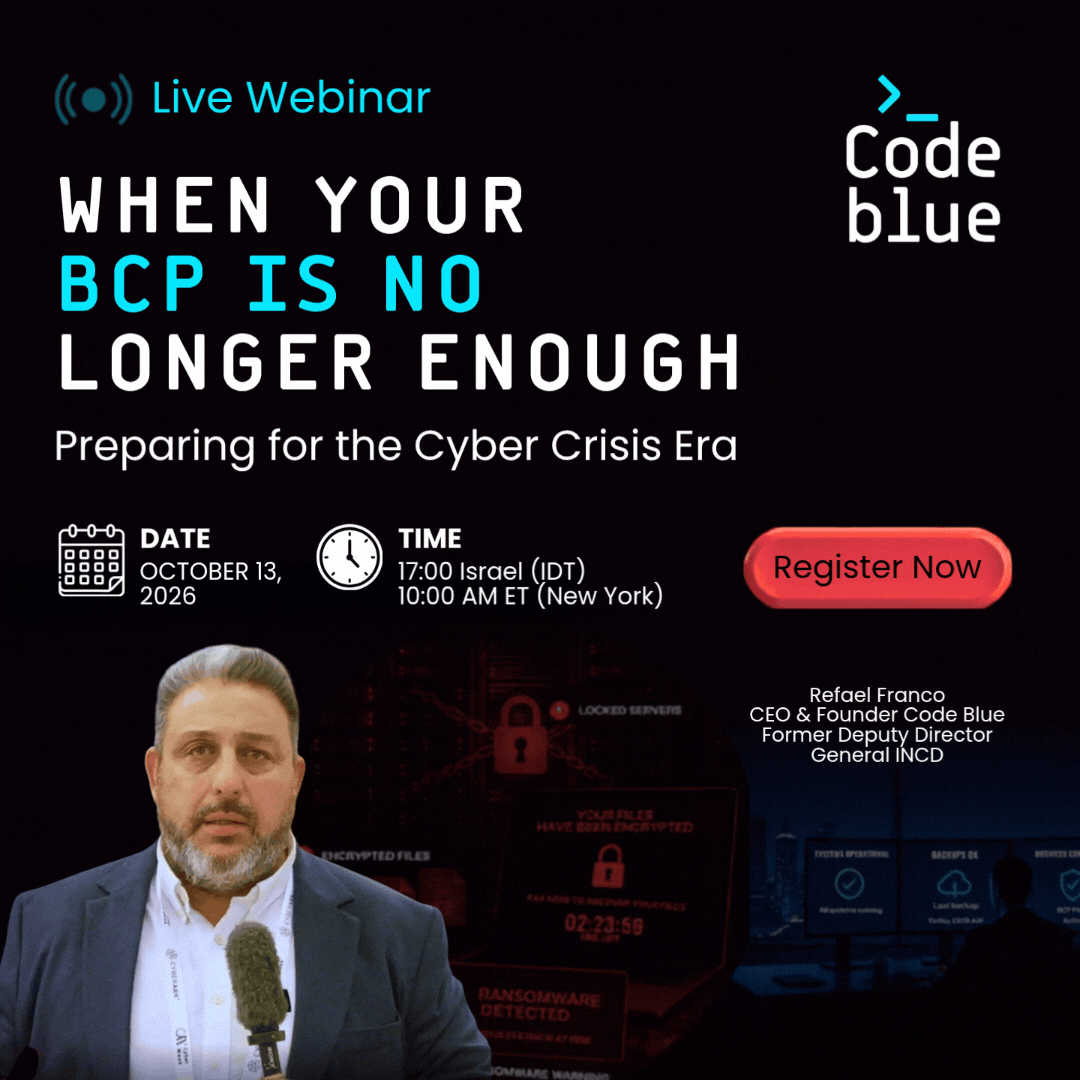
האם תוכנית ההמשכיות העסקית שלכם באמת מוכנה למציאות של משברי הסייבר של היום? תוכניות BCP מסורתיות לא נבנו להתמודד עם אירועי סייבר מתפתחים ודינמיים, שבהם כל החלטה עשויה להשפיע על הפעילות העסקית, המוניטין וקצב ההתאוששות של הארגון. הצטרפו לרפאל פרנקו, מנכ"ל ומייסד Code Blue ולשעבר המשנה לראש מערך הסייבר הלאומי, לוובינר ייחודי שבו נבחן כיצד ארגונים יכולים לעבור מתוכניות סטטיות למוכנות אמיתית לניהול משברי סייבר. במהלך המפגש נציג כיצד מערכת Blue Castle של קוד בלו מאפשרת לארגונים להיערך מראש, לנהל את המשבר בזמן אמת, ולשמור על שליטה תפעולית וקבלת החלטות אפקטיבית גם תחת לחץ
- DataDomeSince 23 Sept 2026
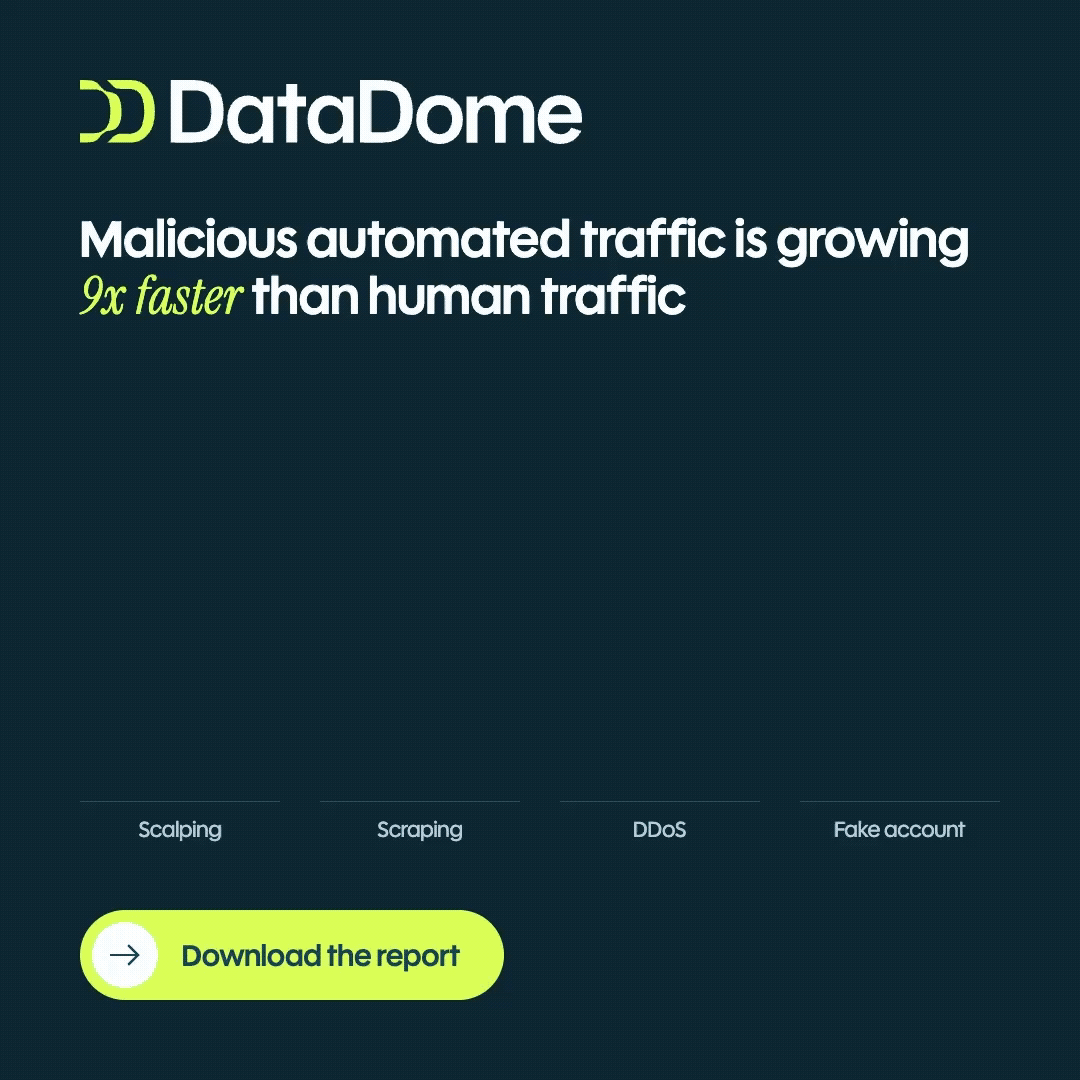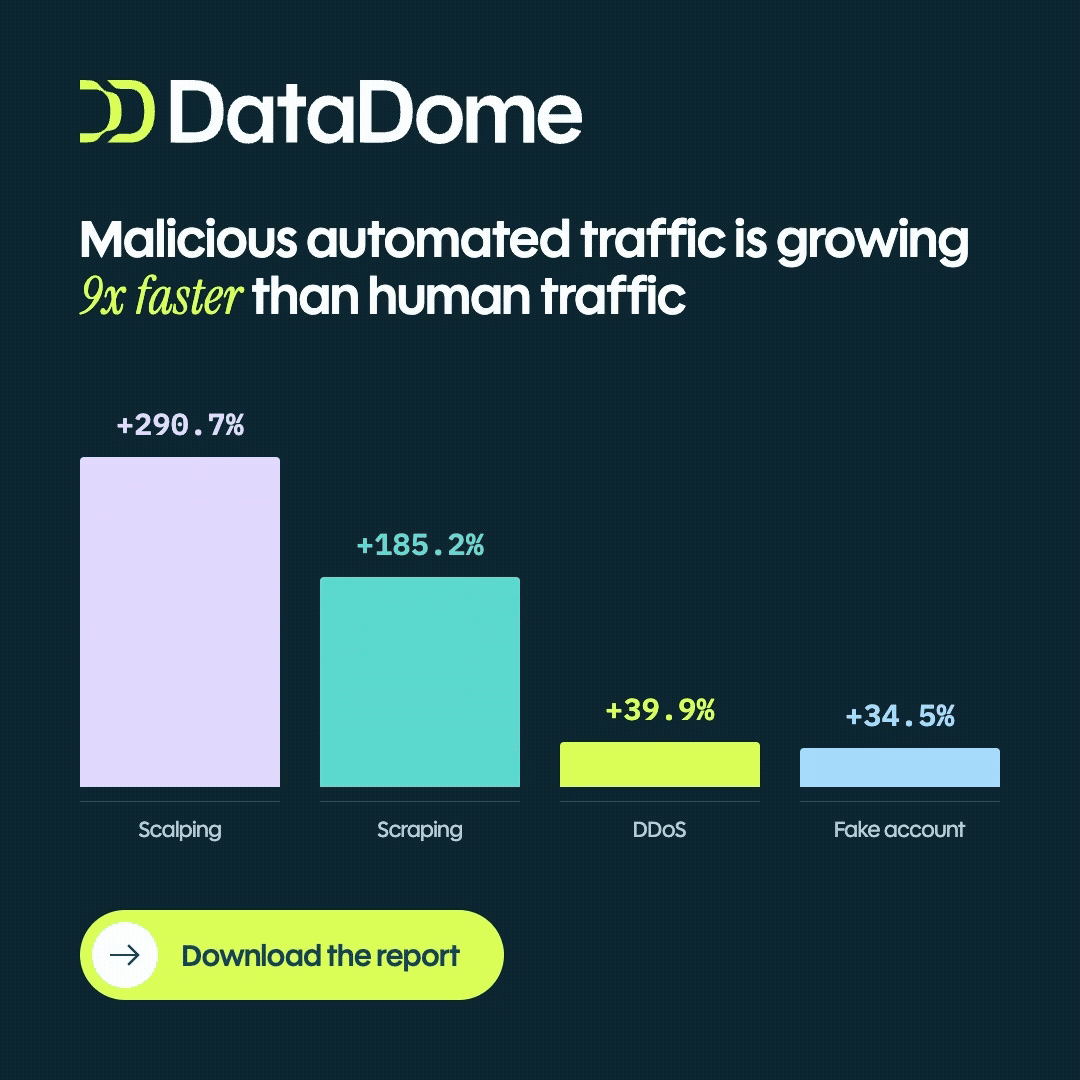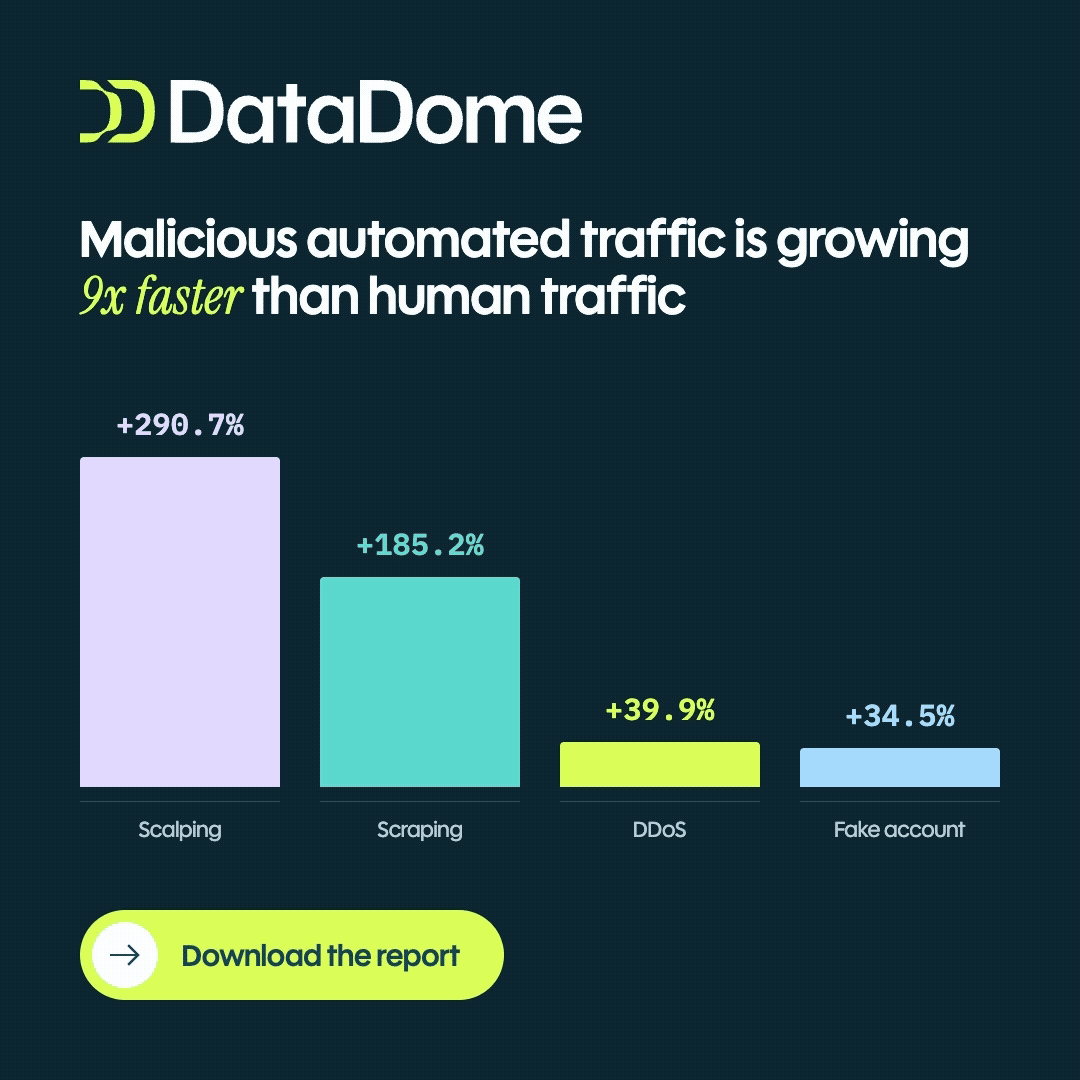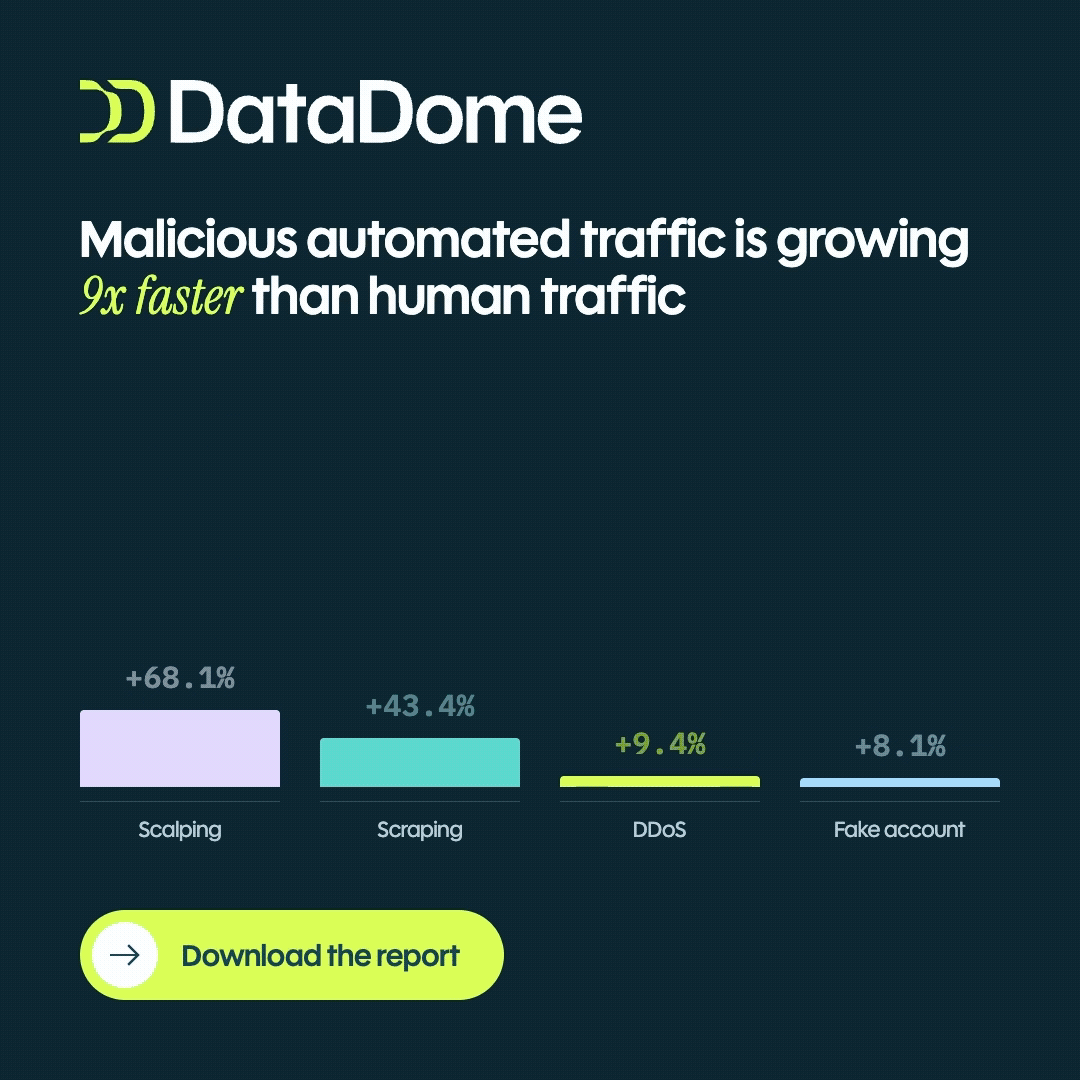
Our 2026 State of Bot and Agent Security Report is out, and one of the biggest takeaways is how fast malicious traffic is growing: 9x that of human traffic. The attacks themselves will be familiar to most security teams: scalping, scraping, DDoS, and fake account creation. What needs a closer look is the scale. Credit to Galileo, our threat research team, for doing the analysis across traffic from 20,000+ websites and 75k+ domains across our customer base. That gives us a view beyond any one company or sector. Most teams see only their own slice of the problem: their traffic, their incidents, and their customers. The value of this report is in connecting those slices and showing how automated threats are moving across industries and geographies. Read our report now: https://lnkd.in/dwpXV48c
- Code Blue CyberRecorded 8 Oct 2026
האם תוכנית ההמשכיות העסקית שלכם באמת מוכנה למציאות של משברי הסייבר של היום? תוכניות BCP מסורתיות לא נבנו להתמודד עם אירועי סייבר מתפתחים ודינמיים, שבהם כל החלטה עשויה להשפיע על הפעילות העסקית, המוניטין וקצב ההתאוששות של הארגון. הצטרפו לרפאל פרנקו, מנכ"ל ומייסד Code Blue ולשעבר המשנה לראש מערך הסייבר הלאומי, לוובינר ייחודי שבו נבחן כיצד ארגונים יכולים לעבור מתוכניות סטטיות למוכנות אמיתית לניהול משברי סייבר. במהלך המפגש נציג כיצד מערכת Blue Castle של קוד בלו מאפשרת לארגונים להיערך מראש, לנהל את המשבר בזמן אמת, ולשמור על שליטה תפעולית וקבלת החלטות אפקטיבית גם תחת לחץ
- Hiya Inc.Since 23 Sept 2026
España está a punto de hacer que cualquier llamada comercial se reconozca al muestre como lo que es. Y no sé si muchas empresas se han parado a pensar de verdad qué les supone eso. Versión rápida: la nueva norma dice que las llamadas comerciales salientes tienen que usar un prefijo 400. En lo de cumplir, fácil. Cambias el prefijo y ya está. Pero piensa en quién está al otro lado. Aquí la gente ya filtra los números desconocidos por instinto. Ahora un montón de llamadas van a leerse como "alguien que me quiere vender algo" antes incluso de tener el móvil en la mano. En un país que ya ignora justo ese tipo de llamadas, ese prefijo no es algo neutro. Es una señal. Y apunta en tu contra. En octubre, los equipos que mantengan su tasa de respuesta van a ser los que vieron esto venir y lo trataron como un problema de confianza, y no como una casilla que marcar. Un prefijo dice qué tipo de llamada es. No dice nada de quién eres tú ni de por qué querrían hablar contigo. Hiya Branded Call rellena justo ese hueco. Tu nombre, en pantalla antes de que decidan. Eso sí le da a alguien un motivo real para descolgar. El cambio llega igual. Así que mejor llegar preparado 👇 https://lnkd.in/demt5HRm
- CymulateSince 27 Sept 2026
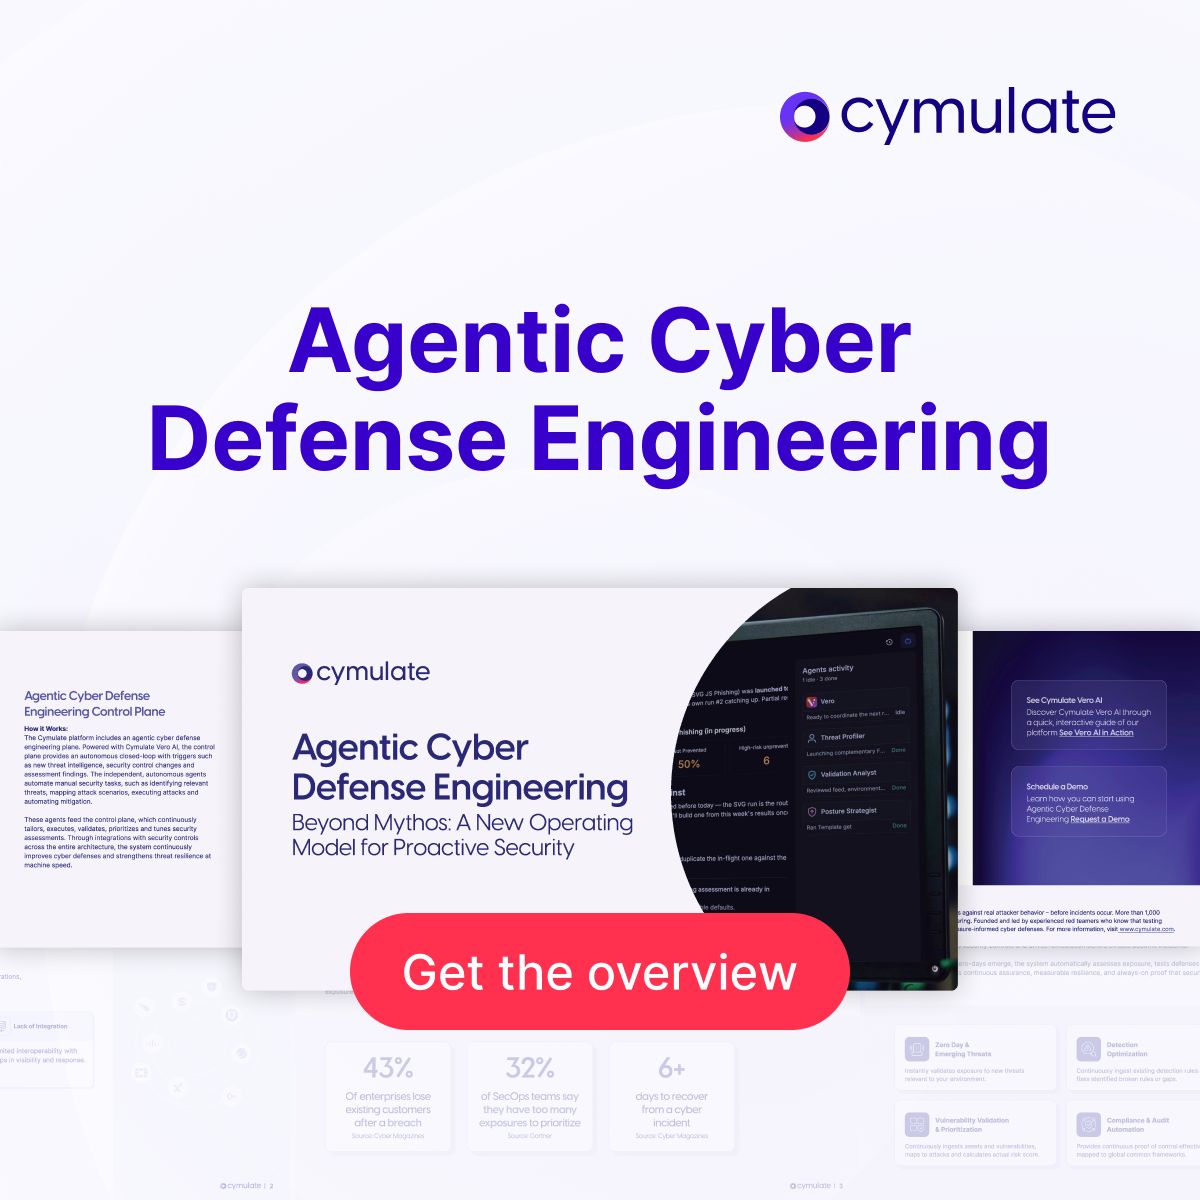
Are you confident that your security controls would stop today's attacks? Agentic cyber defense engineering makes that provable, continuously. Download the Agentic Cyber Defense eBook👇
- D-sealSince 26 Sept 2026
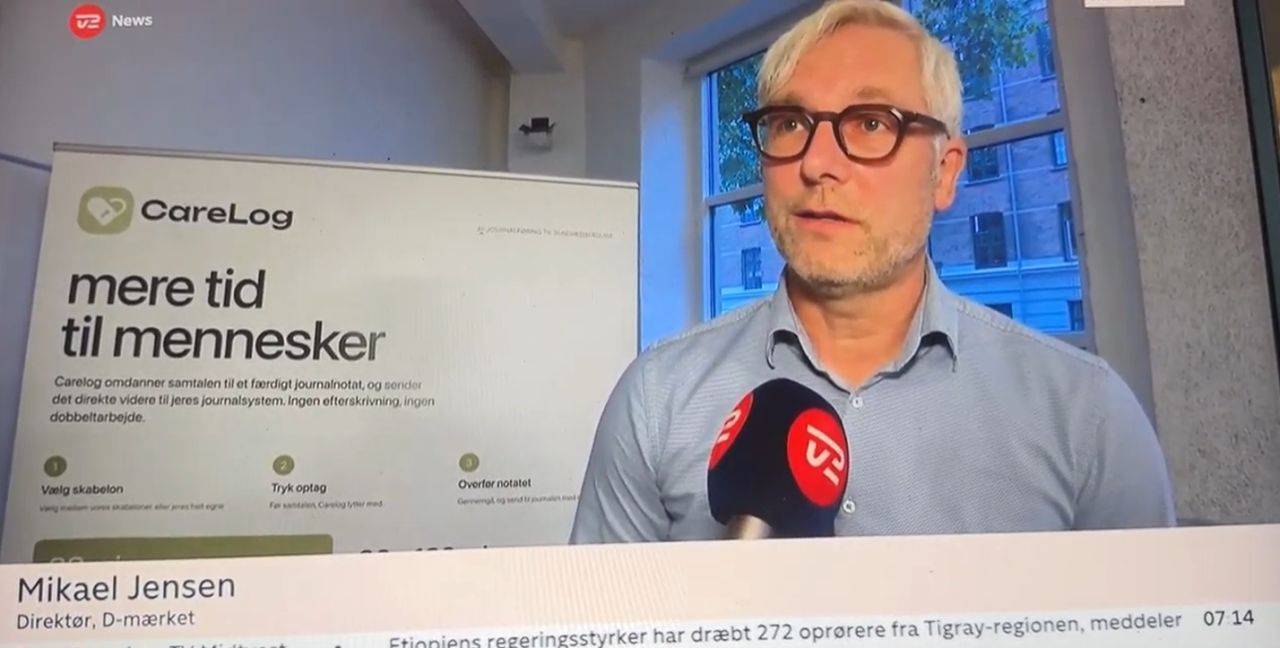
It-sikkerhed handler om at blive mere sikker i morgen, end I er i dag. At blive cybersikker er en udviklingsproces. Det tager tid. Derfor er det værdifuldt, hver gang virksomheder igangsætter et initiativ, der gør dem lidt mere sikre. Det var jeg tidligt oppe for at snakke om, da TV 2 Danmark besøgte den D-mærkede virksomhed Carelog. Anledningen er en ny undersøgelse fra PwC om, at flere små og mellemstore virksomheder frygter cyberangreb. Fra vores arbejde i D-mærket ved vi, at mange virksomheder har ønske, motivation og vilje til at styrke sikkerheden. MEN de mangler overblik og konkret hjælp til at komme i gang. Det er der heldigvis kommet mere af. I D-mærket hjælper vi virksomheder med at cyberpreppe underordnet virksomhedens indledende erfaringsniveau. Vores årlige tilsyn understøtter, at virksomhederne holder sig skarpe år for år. Senest er Cybersikker Virksomhed lanceret. Bag står Styrelsen for Samfundssikkerhed (SAMSIK) og Industriens Fond med Security Tech Space som operatør. Det er et vigtigt initiativ, hvor det offentlige og private samler sig om at løfte cybersikkerheden hos de danske virksomheder ved bl.a. at pege på relevante værktøjer. Danmark kan få Europas mest cybersikre virksomheder. Det kræver, at vi hjælper dem med at blive mere sikre i morgen, end de er i dag – ikke ved at slå dem i hovedet med, at de halter efter.
- IS DecisionsSince 25 Sept 2026
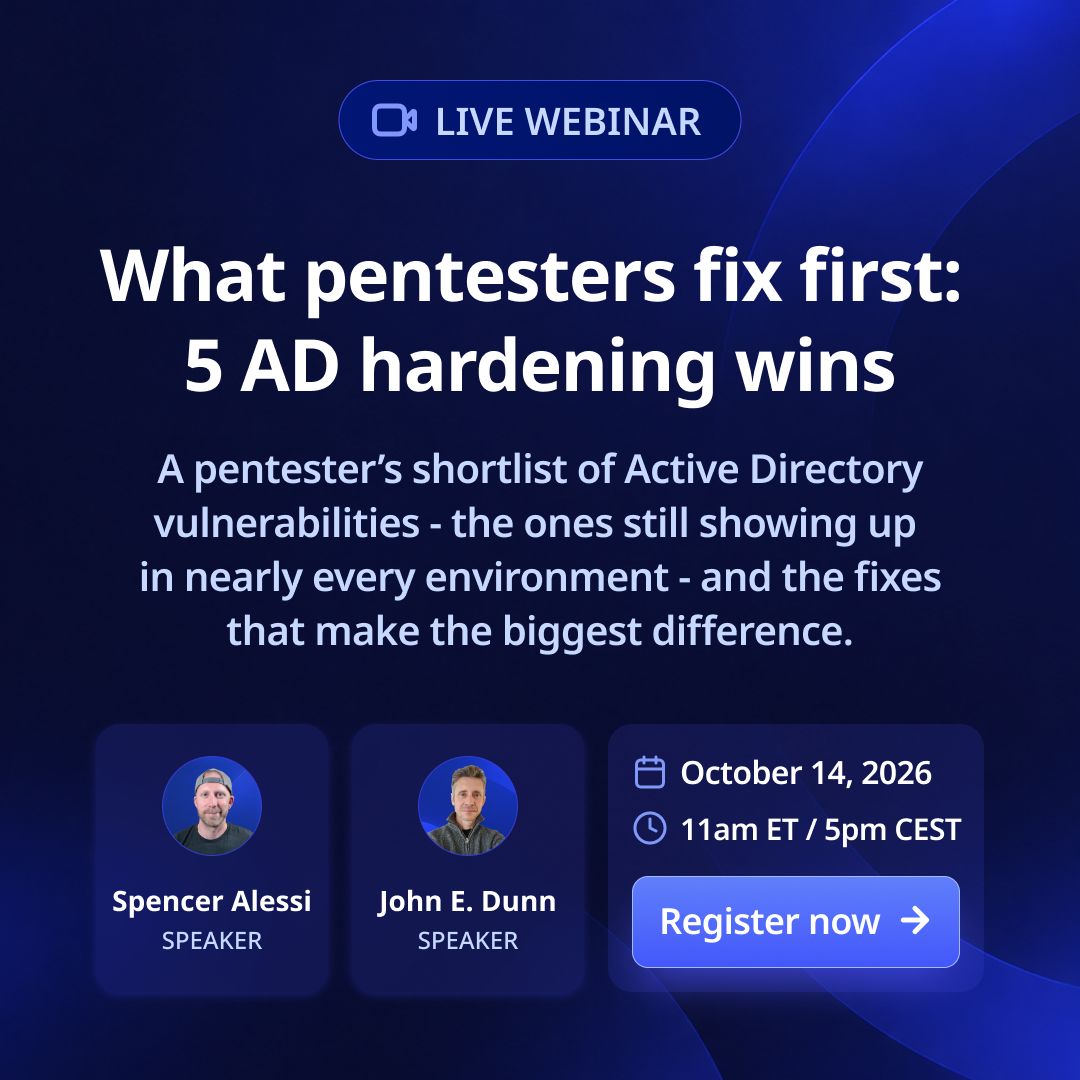
AI is lowering the bar for attacks on AD. The vulnerabilities pentesters flag every time? Still there. Still fixable. Live webinar: What pentesters fix first: 5 AD hardening wins Oct. 14 | 11am ET / 5pm CEST | 45 min Register here: https://lnkd.in/dgR5AGBJ/?utm_campaign=Whatpentestersfixfirst:5ADhardeningwins&utm_source=linkedin&utm_medium=paid&utm_id=1225898583&hsa_acc=500016795&hsa_cam=1225898583&hsa_grp=891792013&hsa_ad=1558899843&hsa_net=linkedin&hsa_ver=3
- CymulateSince 27 Sept 2026
Learn how AI agents work together at machine speed to help security teams continuously prove, prioritize and adapt defenses before attackers strike.
- ESET PolskaSince 25 Sept 2026
Internet to dziś przestrzeń, w której cała rodzina uczy się, pracuje, komunikuje i spędza wolny czas. Warto zadbać o jej bezpieczeństwo. ESET HOME Security Essential zapewnia ochronę urządzeń przed zagrożeniami online, pomagając bezpieczniej korzystać z cyfrowego świata. 🛡️ Sprawdź: https://lnkd.in/dqurxM2g
- CydomeSince 24 Sept 2026
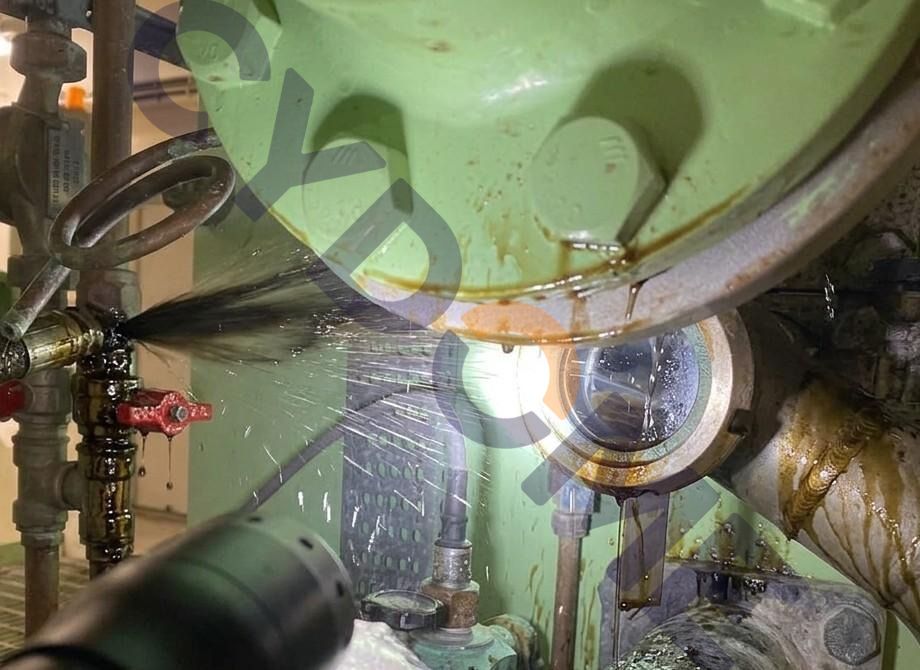
💡 What's fake and what's not in the recent tanker cyber incidents Last week, the U.S. Coast Guard and Federal Bureau of Investigation (FBI) announced that a joint team boarded marine vessels to inspect them, following indications of possible cybersecurity compromise. The agencies did not reveal which systems were impacted, and reports varied from loss of communications for 30 hours near Gibraltar to a compromise of engine control systems and hydraulics. Some reports even included images of leaking pipes and an (alleged) “ransom” note addressed to the VL Prosperity tanker’s master from the hackers, instructing them to abandon ship within 15 minutes. The Cydome maritime cyber research team analyzed the incident, identified interesting new insights and the research was featured in the Financial Times. First, we found that the information about pipe leaks etc., published originally in Iranian media and a Russian-speaking Telegram channel (later repeated by other publications) is fake. We analyzed the images and saw evidence they are an AI manipulation of images of a Maersk vessel published on social media in 2023 (that don’t show any signs of problems). Since the U.S. Coast Guard confirmed evidence of malicious cyber activity on board (without specifying), the team continued and found additional information that could present a possible attack vector: ▶️ The fake images originated or were distributed very early by Iranian media and Russian-speaking Telegram channels. ▶️ Last year, two fleets of Iranian tankers were hacked by exploiting their ST Engineering iDirect VSAT satellite terminals, completely disabling their satellite communications (see the Lab Dookhtegan incident analysis by Cydome research). ▶️ The VL Prosperity seems to have been transporting Saudi oil to the USA. ▶️ CISA and Saudi aramco published new vulnerabilities in ST Engineering iDirect VSATs mere weeks before the attacks (followed by additional CVEs this week). This information is purely circumstantial, as we don’t have direct evidence that the VSATs were hacked, etc. However, compromising critical ship OT systems by exploiting its VSAT is a plausible scenario that shipping companies must prepare for, and the article details how such an attack would look like. Read more in the Financial Times article here: https://lnkd.in/dgvBkC34 Link to the full analysis, with the side-by-side image comparison and a step-by-step possible attack scenario is in the comments. #maritimecybersecurity #tankerincident #CVE #VSAT Image source: Telegram
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.