LinkedIn image ad examples
1,339 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- Fischer IdentityRecorded 19 Sept 2026
Smaller colleges and universities face growing cybersecurity and operational challenges while trying to do more with less. Many think enterprise-grade Identity and Access Management (IAM) is out of reach, but it’s not. Our latest blog, “Right-Sized Identity Management: Why Fischer Identity Is the Smart Choice for Smaller Schools,” shows how institutions can: ✅ Cut costs and reduce IT workload with automation ✅ Improve student satisfaction from day one ✅ Strengthen cybersecurity and compliance ✅ Guard against emerging threats like AI-generated “ghost students” With 20+ years in higher education, Fischer Identity delivers affordable, no-code IAM solutions that modernize institutions securely without custom code or enterprise-level costs. 👉 Read the full blog: https://buff.ly/tZRlxGX #HigherEd #IAM #IGA #Cybersecurity #AI #DigitalIdentity #ZeroTrust #StudentExperience #EducationIT #FischerIdentity
- FocaldataRecorded 19 Sept 2026
Um cibercriminoso identificado como ResearcherX publicou em um marketplace da dark web o que afirma ser uma vulnerabilidade zero-day no iOS 26, capaz de causar corrupção de memória e permitir o controle total de dispositivos Apple. Caso seja confirmada, a falha representaria uma ameaça crítica à arquitetura de segurança mais recente da empresa, já que estaria localizada no parser do iOS Message e permitiria acesso root sem qualquer interação do usuário. De acordo com a postagem, a brecha seria uma “full chain solution”, indicando que o ponto inicial de infecção bastaria para dominar todo o sistema. O ataque se daria por meio do processamento de mensagens malformadas, caracterizando um zero-click: o usuário não precisaria abrir arquivos nem clicar em nada, bastando receber um pacote de dados comprometido. Especialistas destacam que o bug estaria relacionado à corrupção de memória, uma categoria recorrente em motores de análise, mesmo com tecnologias modernas de defesa. O ponto mais preocupante seria a alegação de que o exploit consegue contornar a chamada “Proteção Multi Camadas”, que envolve mecanismos do kernel e proteções do espaço de usuário introduzidas no iOS 26 para fortalecer a segurança. Se funcional, o exploit daria acesso direto aos dados mais sensíveis armazenados nos aparelhos, incluindo mensagens e fotos, localização em tempo real e informações do keychain, como senhas e chaves de criptografia. A notícia surge poucos meses após o lançamento do iOS 26, divulgado pela Apple como uma das maiores evoluções em segurança já produzidas pela empresa. Embora o sistema operacional de smartphones da maçã tenha reforçado seus mecanismos de defesa, corrigindo falhas anteriores de memória, o anúncio indica que hackers podem já ter encontrado caminhos para burlá-los. Na dark web, vulnerabilidades zero-day completas para o iOS costumam alcançar valores muito altos, variando entre US$ 2 milhões e US$ 5 milhões, dependendo do nível de aplicação práticsa e da exclusividade do exploit oferecido. Focaldata. Tudo Está Conectado. www.focaldata.com.br #cibersegurança #fortinet #infoblox #trendmicro #gigamon #crowdstrike #segura #transmitsecurity #vigilant #zadara #paloalto #f5 #cloud4wi #acronis #culturadeprevenção #posturadeprevenção
- FrenosRecorded 19 Sept 2026
We’re on the ground at Black Hat MEA. From December 2–4, the Frenos team will be in Riyadh meeting with OT security leaders, operators, and engineers who are pushing critical infrastructure resilience forward. If you’re attending, stop by Booth H1.T80 to see how adversary modeling, digital twin analysis, and agentic AI are helping organizations understand operational risk with clarity and speed. Vivek Ponnada will be available throughout the event to walk through real-world use cases and discuss what’s top-of-mind for OT defenders today. 📍 Booth H1.T80 🗓 02–04 December 2025 📌 Riyadh, Saudi Arabia – RECC Will we see you there?
- FocaldataRecorded 19 Sept 2026
A WatchGuard Technologies divulgou seu relatório de previsões para a segurança digital em 2026, destacando o papel central da inteligência artificial, a intensificação das regulamentações e as mudanças profundas na cadeia de suprimentos de software. O cenário aponta para empresas cada vez mais pressionadas a aprimorar suas políticas de proteção de dados, diante de um ecossistema tecnológico mais dinâmico e vulnerável. Entre as tendências identificadas, a companhia prevê a quase extinção dos crypto-ransomwares tradicionais, já que práticas corporativas de backup e recuperação têm reduzido drasticamente a eficácia desses ataques. Com o pagamento de resgates se tornando raro, hackers devem migrar para táticas baseadas no roubo e exposição pública de dados. Em contrapartida, repositórios de código aberto como NPM e PyPI devem enfrentar aumento significativo de ameaças, impulsionando o desenvolvimento de defesas automatizadas por IA integradas aos próprios ecossistemas. O relatório também enfatiza a chegada do Cyber Resilience Act, que, a partir de setembro de 2026, exigirá que empresas que atuam na União Europeia reportem vulnerabilidades exploradas em até 24 horas. Embora essa norma deva estimular uma adoção mais séria de práticas de segurança, sua coexistência com regulamentações globais tende a tornar a conformidade mais complexa e desafiadora para organizações multinacionais. No campo da inteligência artificial, os especialistas projetam que 2026 poderá testemunhar o primeiro ataque realizado inteiramente por sistemas de IA autônoma, sem intervenção humana. Esse marco deve evidenciar o ritmo acelerado da evolução tecnológica e reforçar a urgência de defesas igualmente automatizadas. Ao mesmo tempo, configurações incorretas, falta de autenticação multifator e ataques a VPNs continuarão sendo vetores comuns, com estimativas de que até um terço dos incidentes envolverá acesso remoto inadequado. Diante desse cenário, é preciso entender que a segurança corporativa precisará se apoiar cada vez mais em plataformas unificadas, com defesas automatizadas por IA e proteção integrada de endpoints, redes e identidades. A simplificação e centralização das estratégias de segurança serão fundamentais para permitir respostas em tempo real, garantindo maior resiliência em um ambiente digital cada vez mais desafiador. Focaldata. Tudo Está Conectado. www.focaldata.com.br #cibersegurança #fortinet #infoblox #trendmicro #gigamon #crowdstrike #segura #transmitsecurity #vigilant #zadara #paloalto #f5 #cloud4wi #acronis #culturadeprevenção #posturadeprevenção
- Field EffectRecorded 19 Sept 2026
EDR creates more work than value for MSPs. Alert noise, limited visibility, and manual cleanup drain your team. See why MSPs are replacing EDR with holistic detection built to scale.
- Field EffectRecorded 19 Sept 2026
XDR promises end-to-end protection, but the reality rarely matches the marketing. Learn where XDR falls short for MSPs and why MDR is the smarter, more reliable security choice.
- ExpelSince 10 Apr 2026
Is your SOC running as efficiently as it should? Our SOC KPIs template helps you measure key security metrics like incident response times, analyst workload, and detection accuracy—so you can track performance, identify gaps, and optimize your security operations. Download the free SOC KPIs template today.
- ExpelSince 10 Apr 2026
Your SOC team is buried in alerts, stretched thin, and constantly reacting. But do you know where the real bottlenecks are? Our SOC KPIs template helps you track essential metrics like incident response time, analyst workload, and detection accuracy, so you can make data-driven decisions that improve efficiency, and reduce operational costs. Get the template today and start optimizing your SOC.
- EvinaSince 8 Apr 2026
Are your payment systems ready to face the evolving threats of 2026? The DCB market is set to reach $100 billion, drawing advanced malware like Joker and Autolycos. Equip yourself with actionable insights to shield your transactions and ensure seamless customer experiences.
- EvinaSince 8 Apr 2026
What will it take for you to outsmart tomorrow's cybercriminals? As toll fraud evolves alongside a thriving $100B DCB market, understanding its mechanics has never been more crucial. Explore our expert-driven report for clear steps towards fortified security.
- ExeinSince 17 Jul 2026
Exein is now the Official Physical AI Security Partner of TGR Haas F1 Team, starting this weekend at the Belgian GP! On track, a millisecond decides the race. In cybersecurity, a millisecond decides the breach. Sensors, actuators, software: F1 runs on the same Physical AI logic Exein is built to protect. From the track to real life, the mission stays the same. As connected devices and autonomous systems take on more of the decision-making — on track and off it — runtime security is essential in high-performance environments. Our technology will protect the physical AI systems and devices behind Haas F1 Team's operations, bringing Exein's security expertise into one of the most demanding technical environments in the world. With Haas, we'll be together on the biggest stage, a partnership we'll be highlighting throughout this season and beyond, with initiatives spotlighting the growing importance of cybersecurity, innovation, and technological excellence. We wish Ollie, Esteban, and the entire Haas team a great weekend at Spa, and a strong rest of the season! 🏎️
- F9C SecurityRecorded 18 Sept 2026
Cada falso positivo custa mais do que alguns minutos de análise. Ele consome tempo da equipe, reduz a produtividade e pode desviar a atenção de ameaças que realmente exigem uma resposta imediata. No setor financeiro, reduzir o excesso de alertas significa aumentar a eficiência operacional e fortalecer a prevenção a fraudes. Conheça como a F9C ajuda instituições financeiras a identificar o que realmente importa.
- Exeon AnalyticsSince 18 Jun 2026
Threat Detection & Response with Exeon.NDR Detect threats earlier. Respond faster. Exeon.NDR uses machine learning to identify malicious behavior in real time, helping security teams focus on what truly matters.
- EthiackSince 28 Aug 2026
"AI pentesting can't find business logic vulnerabilities." Hackian just found two in n8n and SonarQube. No scanner would catch these. 80%+ of pentesters would not catch these. Because they're not signature-based vulnerabilities. And they're not the typical checklist vulnerabilities. They're business design flaws. And complex ones in complex targets. n8n example: Hackian exploited how the workflow automation was architected, bypassing intended access controls through legitimate-looking API calls. SonarQube example: Hackian accessed projects it wasn't supposed to by understanding and exploiting the permission model itself, not by breaking authentication. These are the "ghosts" everyone says AI can't find. Here's the difference: Traditional tools look for patterns. Known signatures. Predictable exploit chains. Hackian doesn't scan. It reasons. → It explores applications like a human hacker would → It tests assumptions about how things should work → It experiments with edge cases and logical inconsistencies → It validates real exploitation, not theoretical risk This is Agentic AI pentesting. Not a scanner with better marketing. To everyone who says AI can't find business logic vulnerabilities. Here you go. Two real exploits. And if Hackian can find them, criminals can too. Full technical breakdown: https://lnkd.in/eZENHg82 Still think AI pentesting is just hype? Try Ethiack and you will see
- EthiackSince 24 Aug 2026
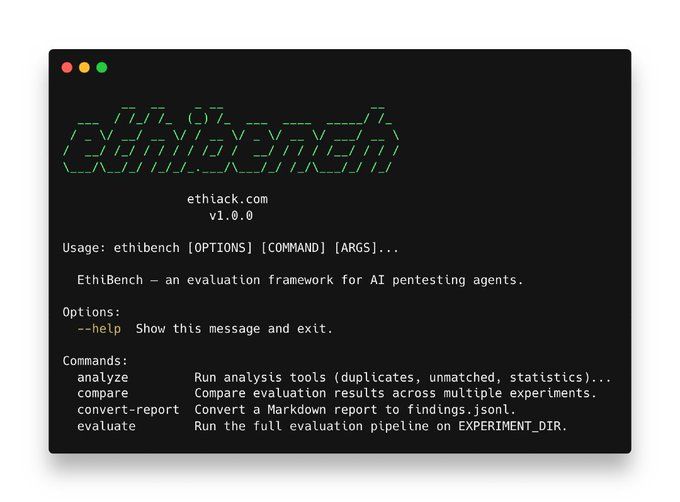
We just open-sourced EthiBench: a new evaluation protocol for AI pentesting agents. Read more:
- F9C SecurityRecorded 18 Sept 2026
A prevenção a fraudes precisa proteger as operações sem gerar impactos para clientes e equipes. Conheça uma abordagem inteligente para identificar diferentes tipos de fraude, reduzir falsos positivos e fortalecer a segurança das operações de pagamento. Saiba mais e solicite um contato inicial com nosso time de especialistas.
- FencerSince 23 Jun 2026
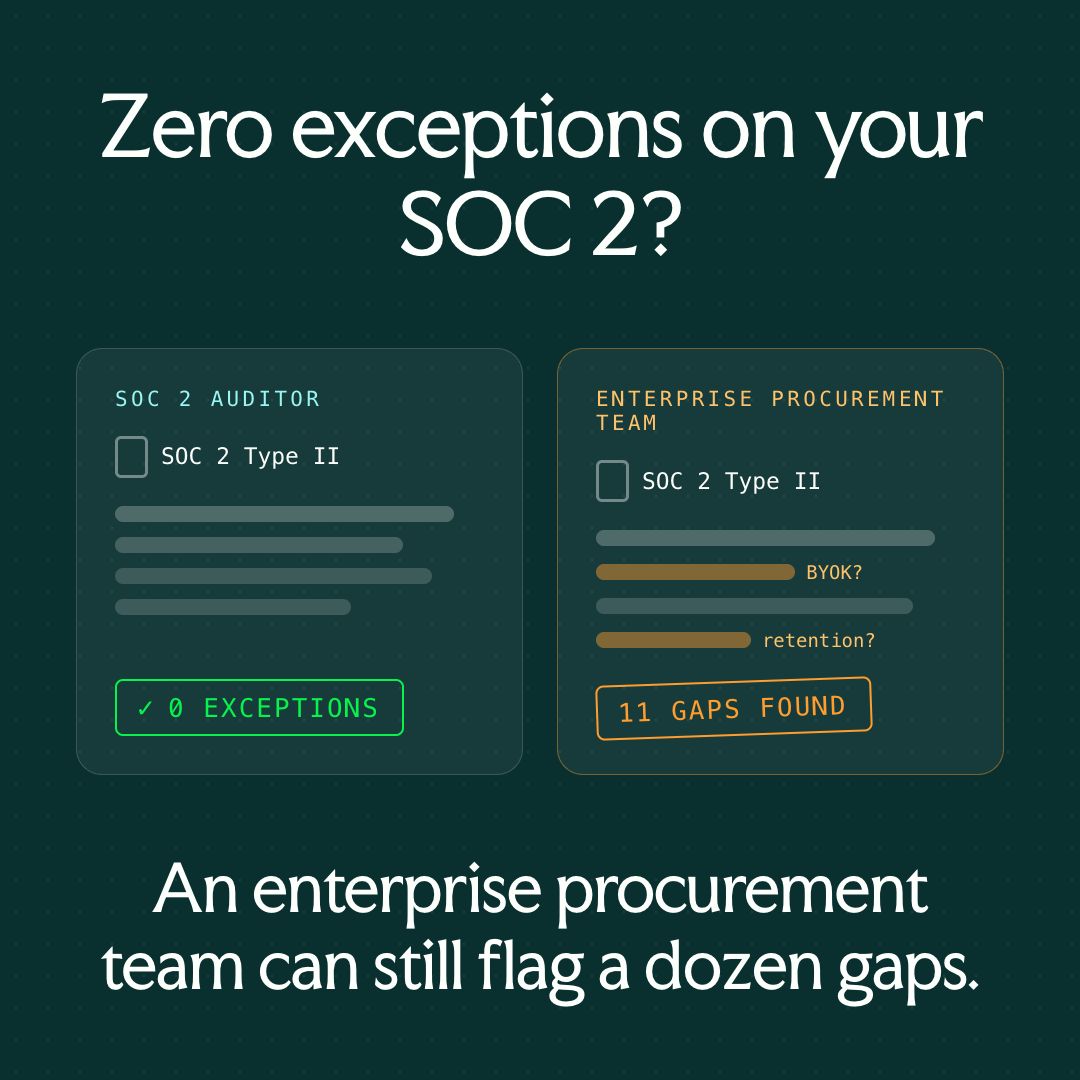
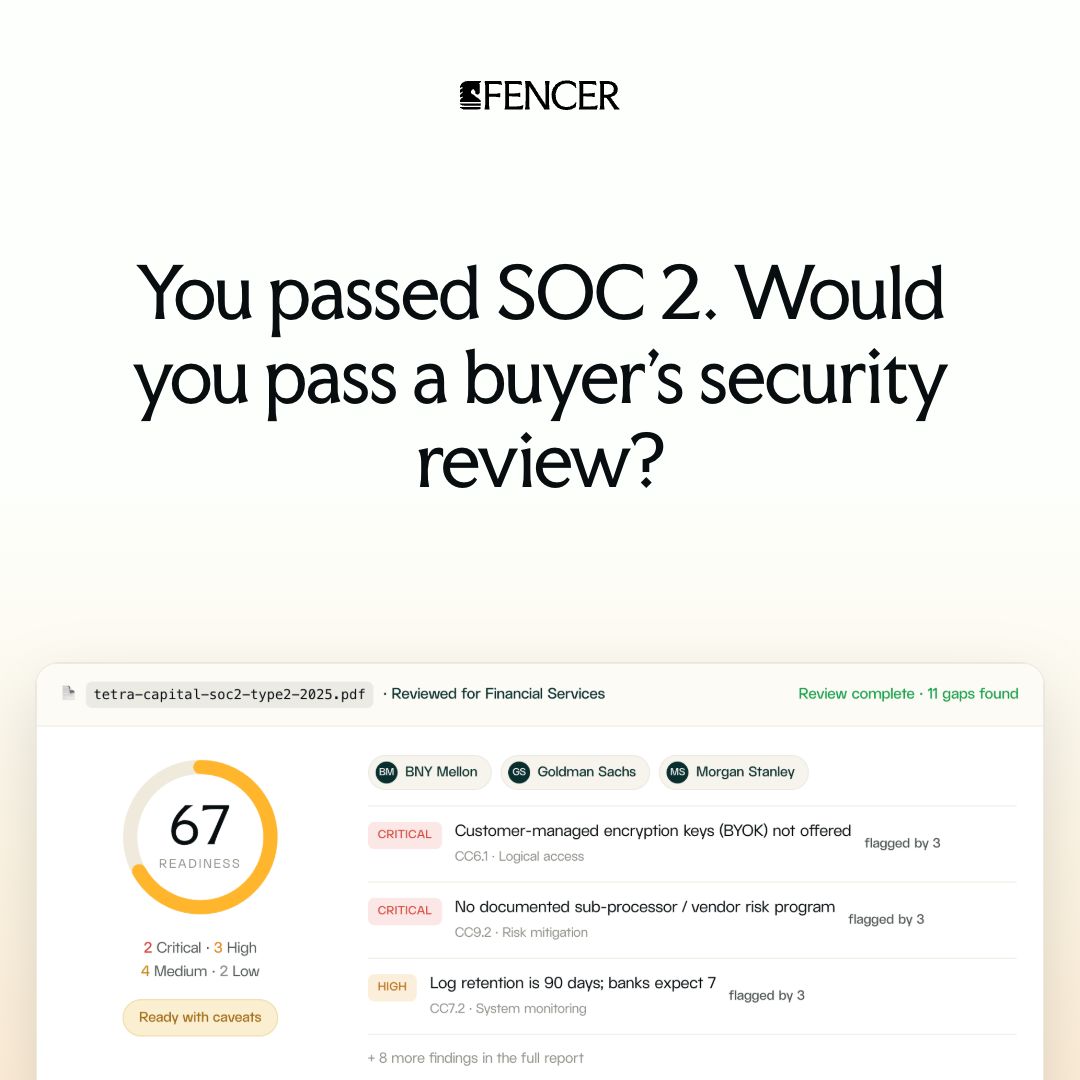
Passing your SOC 2 audit and clearing an enterprise buyer's security review are two different bars. A free, 90-second check shows where your report falls short.
- FencerSince 23 Jun 2026
One enterprise security review can add a month to a deal. A free, 90-second check shows what a buyer's security team would flag in your SOC 2 before it stalls a deal.
- EvidencySince 29 Jun 2026
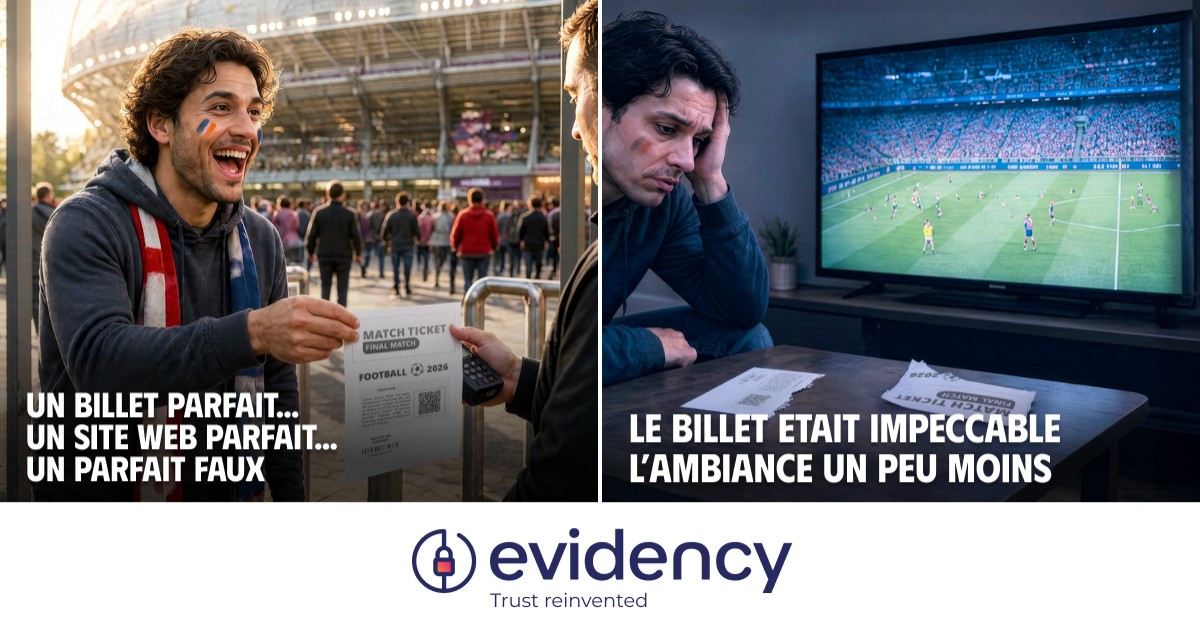
Un document peut paraître parfait. Et être parfaitement faux. Evidency intègre une preuve d'authenticité dès la création du document. Pour vous permettre de vérifier la source et de vous fier à ce que vous voyez.
- EvidencySince 14 Jul 2026
Près de 2 entreprises sur 3 sont victimes de fraude documentaire chaque année. Evidency intègre une preuve d'authenticité dès la création du document. Pour vous permettre de vérifier la source et de vous fier à ce que vous voyez.
- ESET Česká republikaSince 14 Aug 2026
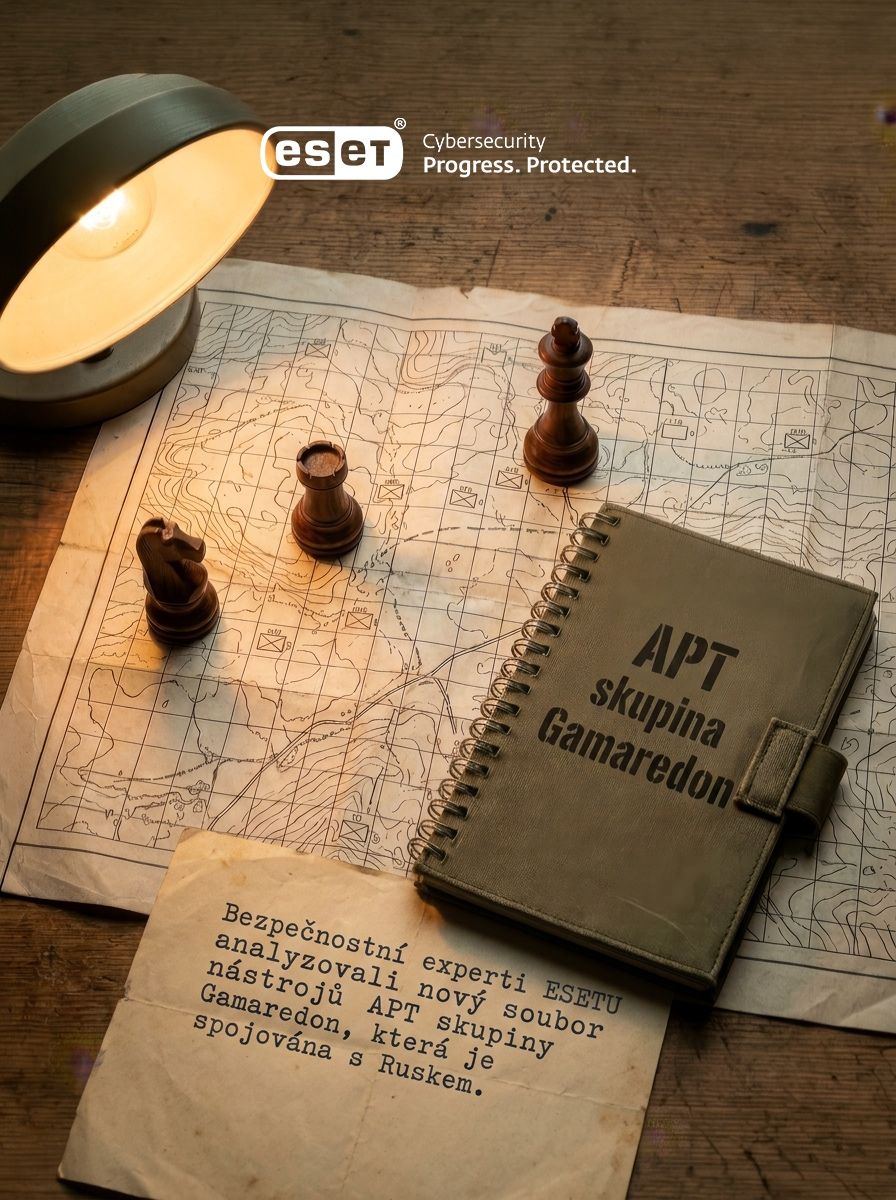
Analytici ze společnosti ESET vydali novou zprávu o APT skupině Gamaredon, která je spojována s Ruskem. Během roku 2025 se skupina zaměřovala výhradně na ukrajinské vládní a vojenské instituce. Nasadila šest nových nástrojů založených na PowerShellu (PteroDee, PteroCache, PteroDum, PteroOdd, PteroPaste, PteroEffigy) a hlavně změnila způsob, jakým krade data: odcizené soubory nahrává do běžných cloudových úložišť kompatibilních s Amazon S3 (Wasabi, Tebi, Intercolo). Škodlivá činnost tak splyne s legitimním provozem. „Mnoho aktualizací skupina provedla před významnými svátky v Rusku a na Krymu. Je pozoruhodné, že během těchto svátků ani bezprostředně po nich nebyly pozorovány žádné aktualizace, což dále naznačuje, že operátoři skupiny Gamaredon jsou pravděpodobně zaměstnanci napojení na státní správu,“ uvádí Zoltán Rusnák z ESETu. Celý rozbor najdete v článku: https://lnkd.in/g9_gbCNB
- ESET Česká republikaSince 14 Aug 2026
Ransomware není začátek útoku. Je to až jeho finále. To je možná největší omyl, se kterým se stále setkáváme. Ve většině případů útočníci nejdříve týdny připravují půdu. Nenápadně získávají přístup do firemních systémů a čekají na správný okamžik. Nejčastěji využívají: * infostealery ke krádeži přihlašovacích údajů, * nezáplatované zranitelnosti, * phishing a sociální inženýrství. Teprve když mají jistotu, že dopad bude co největší, nasadí ransomware. Proto dnes nestačí myslet jen na prevenci. Stejně důležité je být připraven na rychlou detekci, reakci i obnovu provozu. Právě schopnost vrátit firmu co nejrychleji zpět do provozu často rozhoduje o tom, jestli útok skončí nepříjemností, nebo existenčním problémem. Jak dnes ransomware funguje, proč útočníci mění své taktiky a jak nastavit účinnou obranu? Více v novém článku Digital Security Guide: https://lnkd.in/gDQTswdN
- ExaforceSince 1 Jul 2026
Book your SOC checkup for Black Hat 2026. Visit the Exaforce SOCtors' Office and get the treatment for your SecOps symptoms. Booth 4144. Book your checkup: https://lnkd.in/gBRDcw9k
- ExaforceSince 1 Jul 2026
The SOCtors are en route to Vegas. At Black Hat 2026, Exaforce is running a full SOC Health Clinic at Booth 4144. Four Exabot specialists - Detect, Triage, Investigate, Respond - each purpose-built for a different part of the attack lifecycle. Bring your biggest SOC headache. See AI agents handle it live. Leave with a prescription you can take back to your team. Book your consultation: https://lnkd.in/gBRDcw9k
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.