On air · 1 of 3 networks
Ethiack
- ethiack.com
- Cybersecurity
- PT
- 56 employees
Ethiack’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 147. Watch Ethiack with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| None recorded | 0 | Checked 28 Oct 2026 | See all 147 ads → | ||
| Meta | Not checked | — | |||
| Running | 1 | Ads on the Google Ads Transparency Center | Checked 28 Oct 2026 | Collect them with the API → |
Ethiack has no live LinkedIn ads. We recorded 1 Google ad on 28 Oct 2026.
Latest ads
- LINKEDIN · IMAGESince 28 Oct 2026
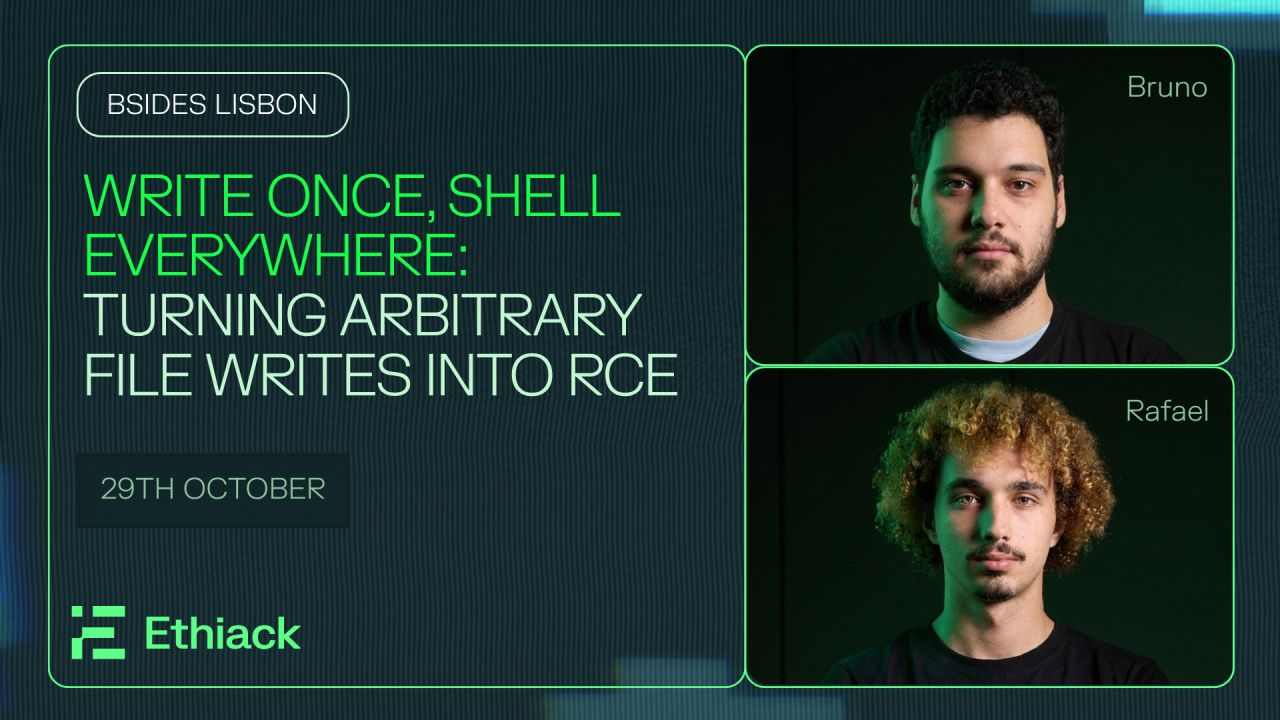
Arbitrary file write is often treated as an "almost critical" bug class in web security: interesting and dangerous, but hard to prove impact when you can't drop a web shell in an obvious location. On October 29th at BSidesLisbon, our researchers Bruno Mendes and Rafael Castilho will present a novel methodology for popping shells across the most popular languages and frameworks, working with minimal information about the target application. It's especially relevant for bug bounty engagements, where you rarely get full source access. Catch the talk if you're at Bsides Lisbon
- LINKEDIN · IMAGESince 28 Oct 2026
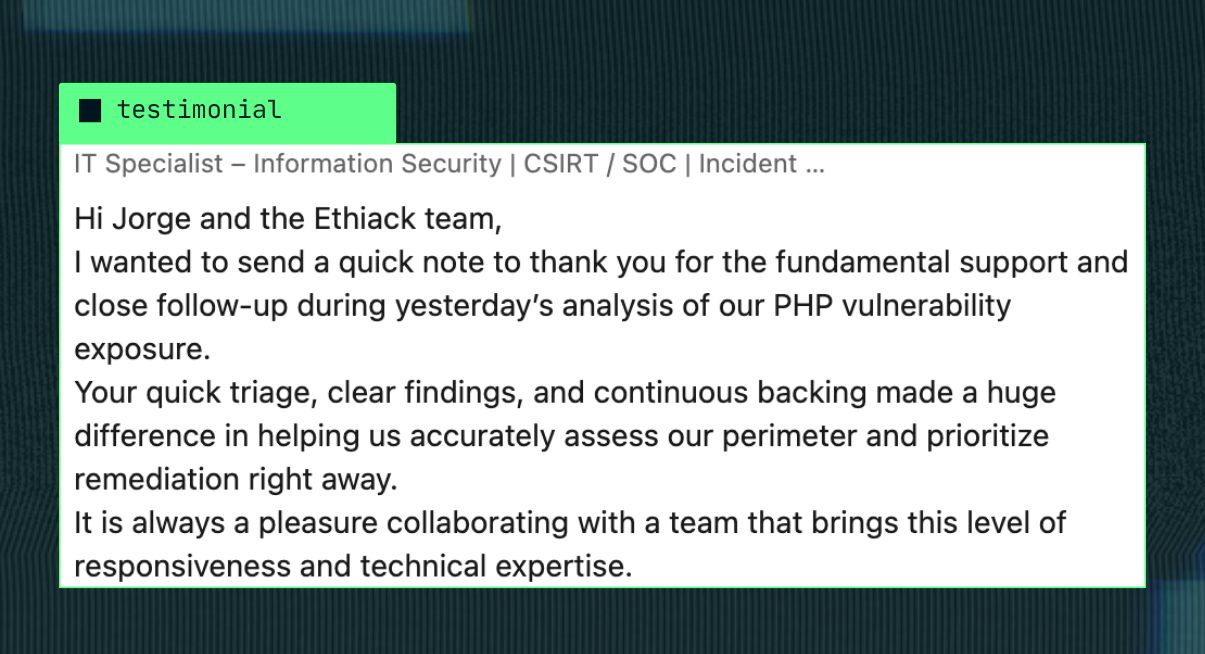
When the PHP vulnerability (CVE-2026-109618 / CVE-2026-109619) surfaced, Ethiack Zero flagged it early, and our team reached out to customers to check their exposure and apply precautions right away. A security team told us what that made possible: quick triage, clear findings, continuous support. Explore Ethiack Zero↓
- LINKEDIN · IMAGESince 27 Sept 2026
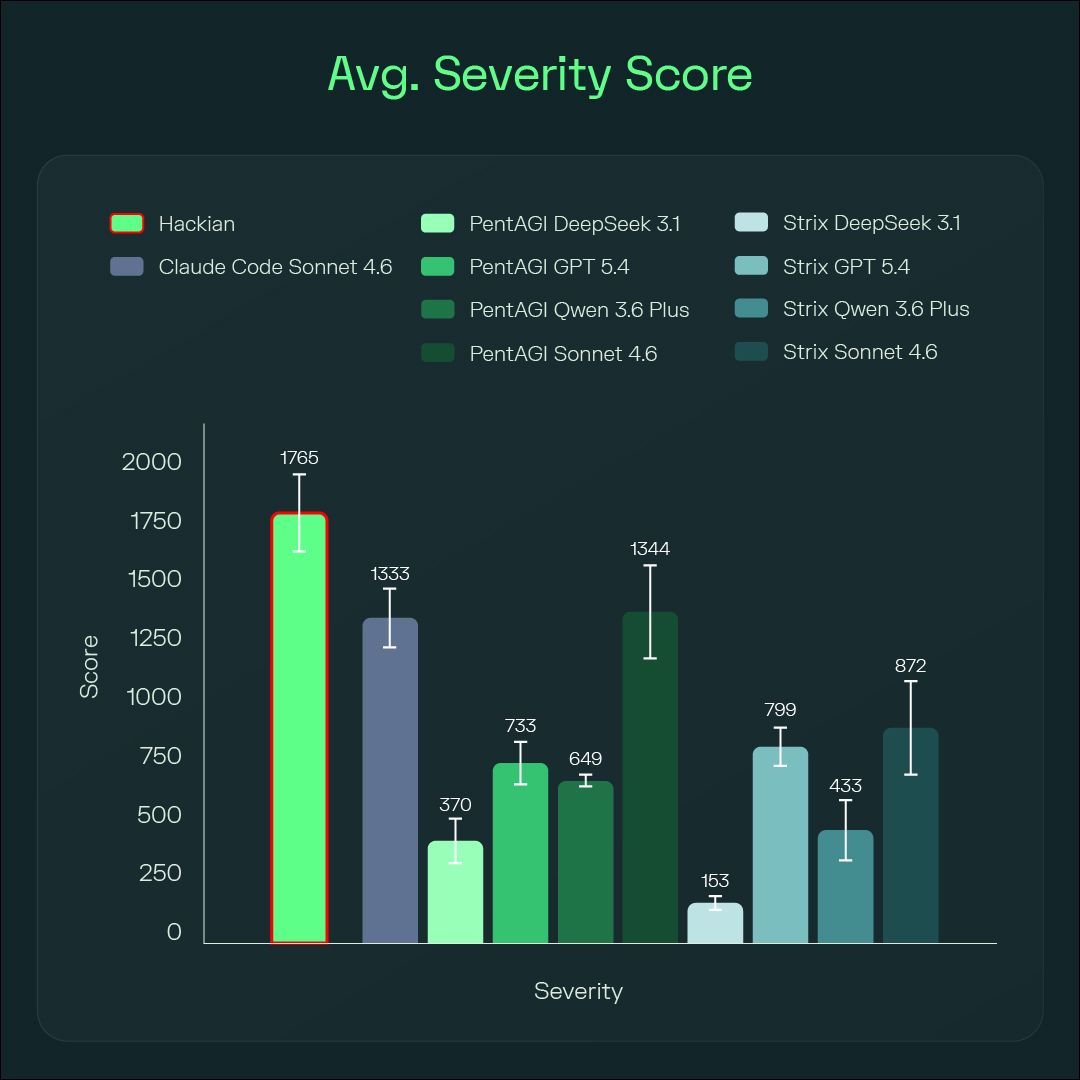
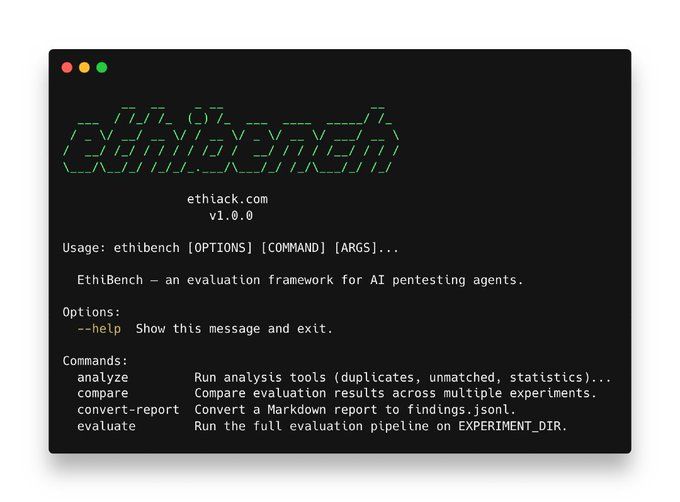
We just open-sourced EthiBench: a new evaluation protocol for AI pentesting agents. The existing benchmarking methods aren't good because they work like a CTF, which doesn't resemble real-world vulns. An agent that is terrible at finding real-world vulns can ace a CTF-style benchmark, and an agent that's great at finding real-world vulns could be underscored. In our own work, gains on controlled benchmarks didn't reliably carry over to real engagements, which is exactly what pushed us to build this. So we designed a whole new benchmarking methodology (along with a research paper) that works by assessing the agent's ability to find bugs in real-world applications. We think this is a stronger foundation for testing the efficacy and accuracy of pentesting agents. We made the benchmark methodology open source and we ranked existing agents. Read more 👇
- LINKEDIN · IMAGESince 28 Aug 2026
"AI pentesting can't find business logic vulnerabilities." Hackian just found two in n8n and SonarQube. No scanner would catch these. 80%+ of pentesters would not catch these. Because they're not signature-based vulnerabilities. And they're not the typical checklist vulnerabilities. They're business design flaws. And complex ones in complex targets. n8n example: Hackian exploited how the workflow automation was architected, bypassing intended access controls through legitimate-looking API calls. SonarQube example: Hackian accessed projects it wasn't supposed to by understanding and exploiting the permission model itself, not by breaking authentication. These are the "ghosts" everyone says AI can't find. Here's the difference: Traditional tools look for patterns. Known signatures. Predictable exploit chains. Hackian doesn't scan. It reasons. → It explores applications like a human hacker would → It tests assumptions about how things should work → It experiments with edge cases and logical inconsistencies → It validates real exploitation, not theoretical risk This is Agentic AI pentesting. Not a scanner with better marketing. To everyone who says AI can't find business logic vulnerabilities. Here you go. Two real exploits. And if Hackian can find them, criminals can too. Full technical breakdown: https://lnkd.in/eZENHg82 Still think AI pentesting is just hype? Try Ethiack and you will see
- LINKEDIN · IMAGESince 24 Aug 2026
We just open-sourced EthiBench: a new evaluation protocol for AI pentesting agents. Read more:
- LINKEDIN · IMAGESince 20 Aug 2026
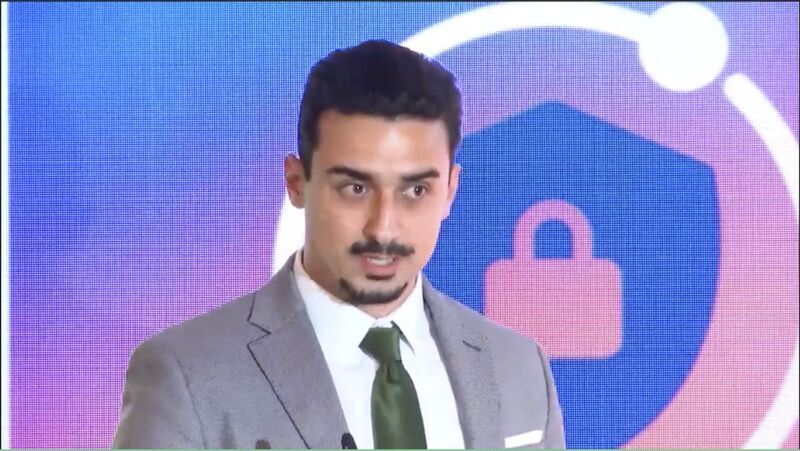
European CISOs, stop pretending it's about quality "We don't buy European cyber because the quality isn't there." How convenient. In many categories, European vendors are: - Cheaper - More responsive - More flexible - Closer to your regulatory reality - More aligned with NIS2, DORA, EU frameworks - With a similar or superior product quality Yet they still lose. Why? Because: - You default to American/Israeli brands - You trust marketing more than results - You outsource thinking to analysts - You confuse market share with technical superiority And in cyber, that's dangerous. When your entire security stack is non-European, you are not sovereign. And neither is your country. You are dependent. Vulnerable. Exposed. Dependency is not neutral. It affects: - Pricing power - Strategic leverage - Data exposure - Political pressure - Long-term innovation capacity This is not anti-American or Israeli. This is pro-European responsibility. If you are an European CISO and you never consider European vendors, you're part of the problem. Digital sovereignty will not be solved by politicians and bureaucrats. It will be solved by procurement decisions. It will be solved by you. Do you actually benchmark European tech? Or do you just assume it's inferior? Be honest. *Here is a pic of me talking at ENISA, so that my point stands stronger.
6 of 147 adsSign up to see every Ethiack ad, filter by format and date, and get alerts on new ones.
See all 147 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.