LinkedIn image ad examples
1,342 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- CorpiaRecorded 21 Sept 2026
Conteúdo, conexões e prática. Participe do CyberID RoadTrip Blumenau e viva a Governança de Acessos.
- Gray AnalyticsRecorded 21 Sept 2026
Starting November 10, 2025, the Department of War requires CMMC compliance for all contracts. Cyber threats are growing. Don’t let your business fall behind. ✅ Protect Sensitive Information (CUI) ✅ Stay Ahead of Competitors in the race to win Contracts Be first to market. Get assessed today.
- Goliath Cyber Security GroupRecorded 21 Sept 2026
Goliath Cyber Security Group - The 3 R's for Cybersecurity Investment Decisions... ✅ Risk Reduction Does this meaningfully lower business-impacting risk? ✅ Replacement Does this eliminate redundant tools, complexity, or manual processes? ✅ Return on Risk Reduction How much financial and operational value do we gain from the lowered risk? At Goliath Cyber Security Group, our team has over 30+ years of executive leadership in the Cybersecurity industry. We have put together industry leading services and solutions for the SMB to the Enterprise that can answer to the 3 R's and more. Schedule a call with our team and see what a TRUE partnership in Cybersecurity actually means... https://lnkd.in/dxeZN3iD #riskmanagement #cybersecurity #riskreduction #replacement #ROI #GoliathCyber #Goliath360 #AI
- Future Fibre TechnologiesSince 3 Feb 2026
Nuisance alarms waste time and erode trust in your security systems. Aura Ai-X from Future Fibre Technologies delivers near-zero nuisance alarms across airports, transport hubs, energy sites, and critical infrastructure worldwide. Stop reacting to noise. Start responding to real threats.
- Future Fibre TechnologiesSince 3 Feb 2026
Every perimeter has a signature. Aura Ai-X learns it. Aura Ai-X distinguishes real threats from environmental noise using deep learning trained on real-world conditions, not just static thresholds. The result: security you can trust.
- FuseLogicSince 10 Feb 2026
A large retailer needed IAM across 80,000 users and hundreds of stores. The traditional approach would have taken months. By starting from existing HR data and automating the lifecycle from day one, the first phase went live within 30 days.
- FuseLogicSince 10 Mar 2026
Case study: FuseLogic heeft, samen met Intergamma, binnen budget in recordtijd een perfect werkende Okta-omgeving neergezet. "De Okta-implementatie bij Intergamma zorgt voor blije gezichten. " Lees de volledige case: https://lnkd.in/exChhn64 #Okta #snelheid
- FronteggSince 8 May 2026
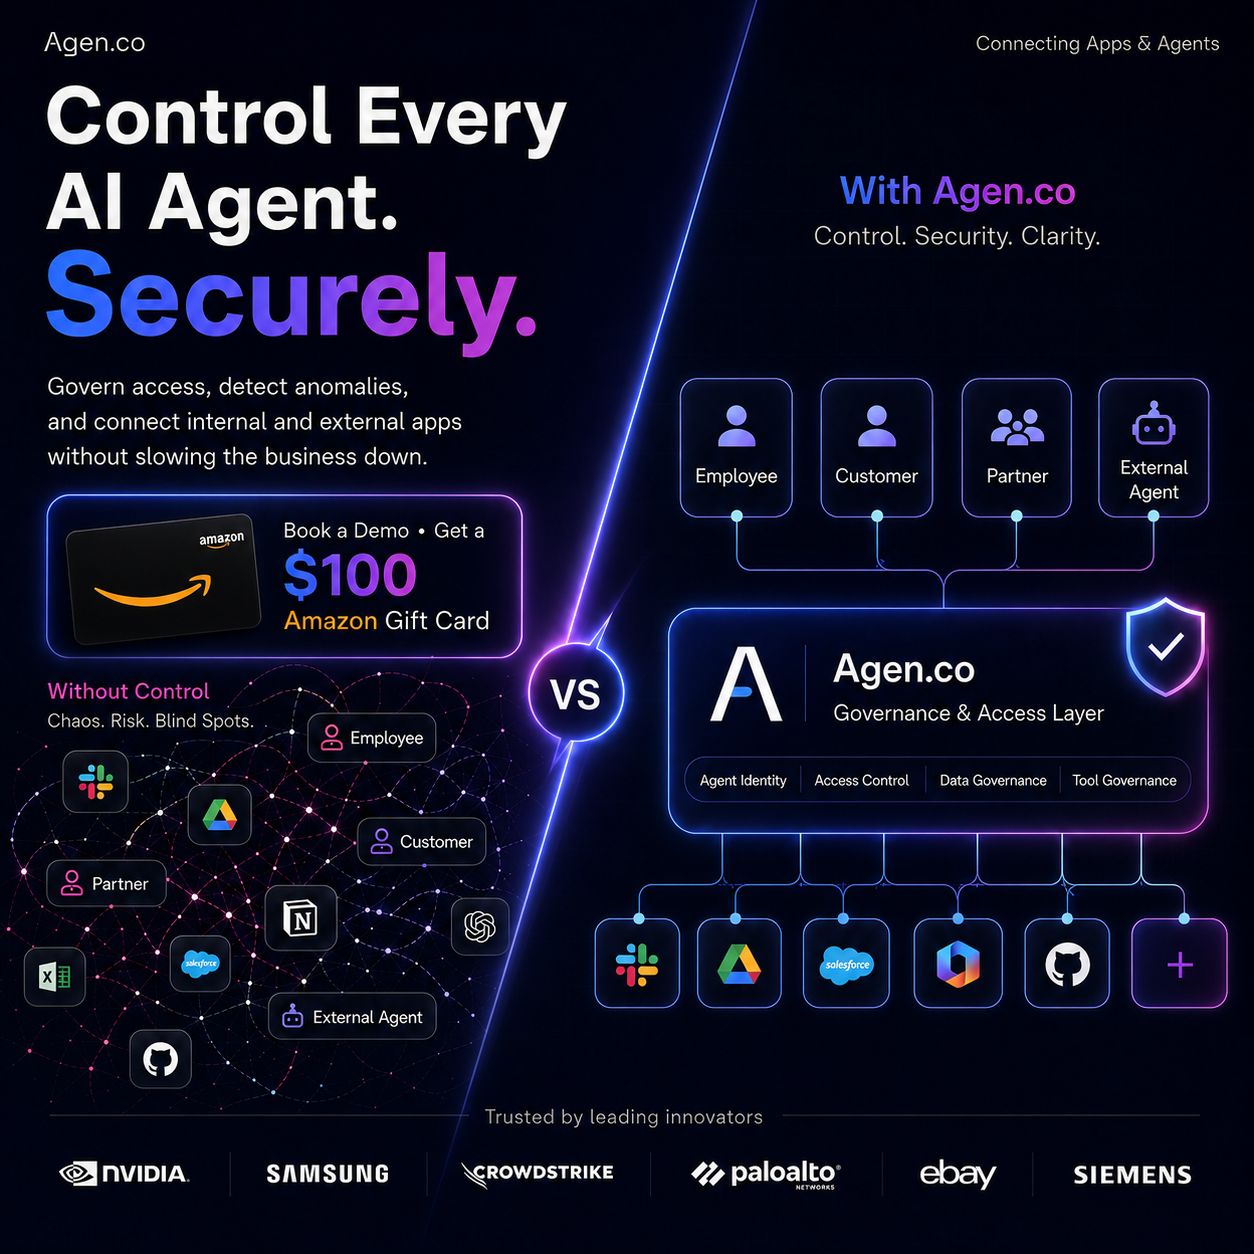
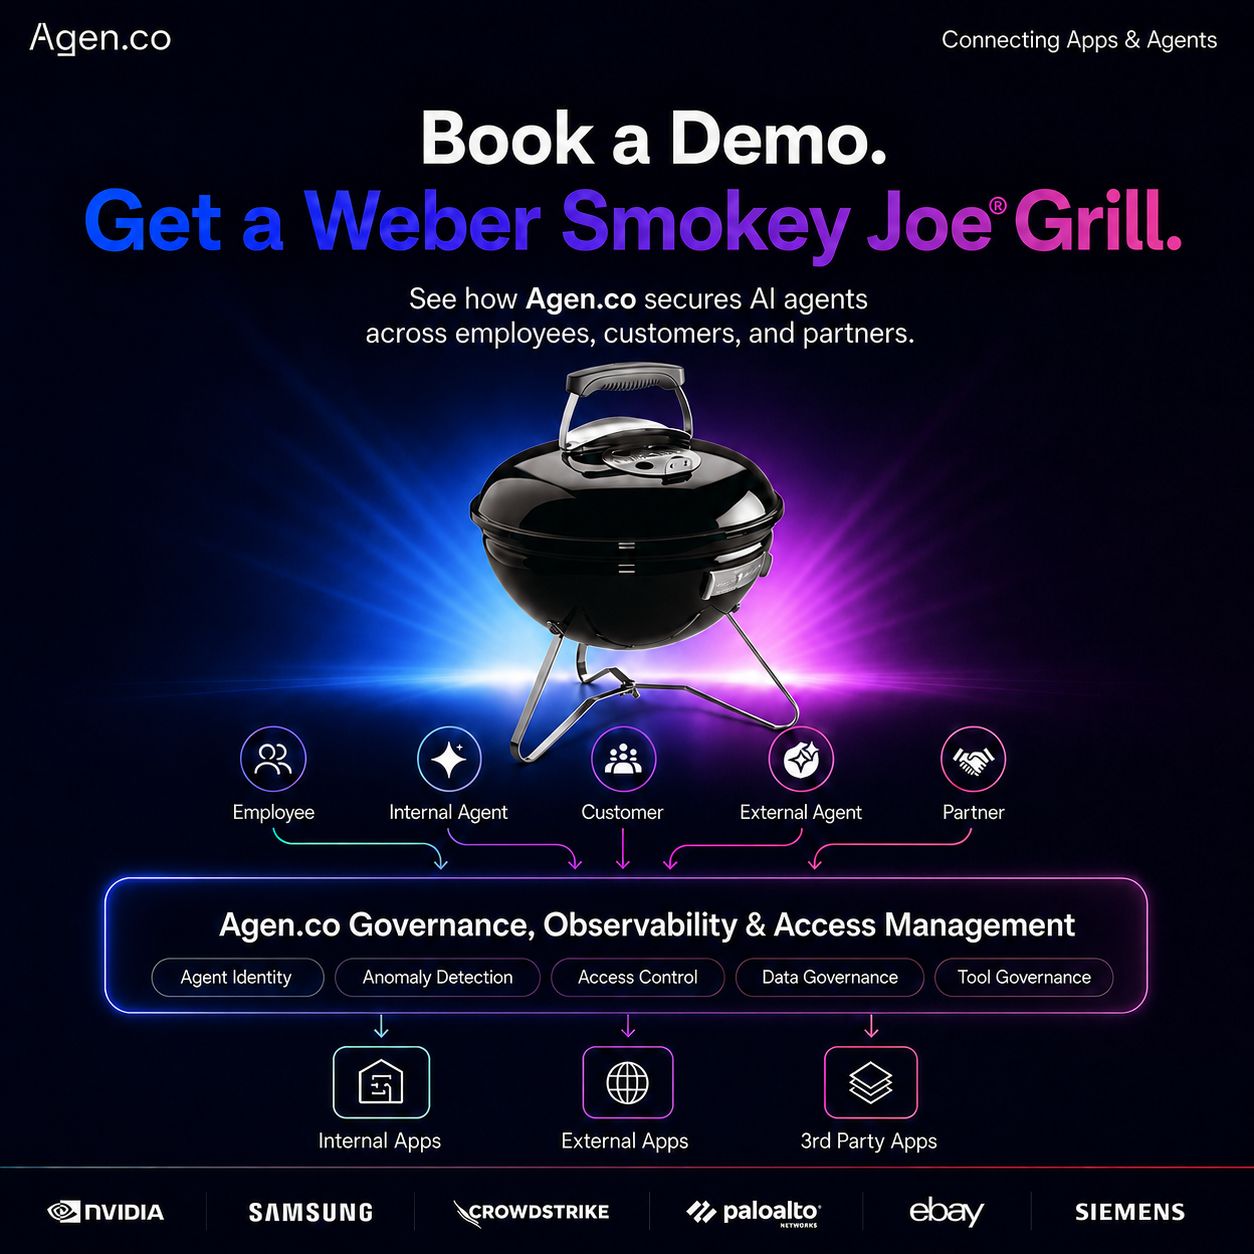
Your engineers won't stop using AI coding agents, and they shouldn't. Agen.co adds identity, access control, and audit trails so you can say yes.
- DelveSince 14 Mar 2026
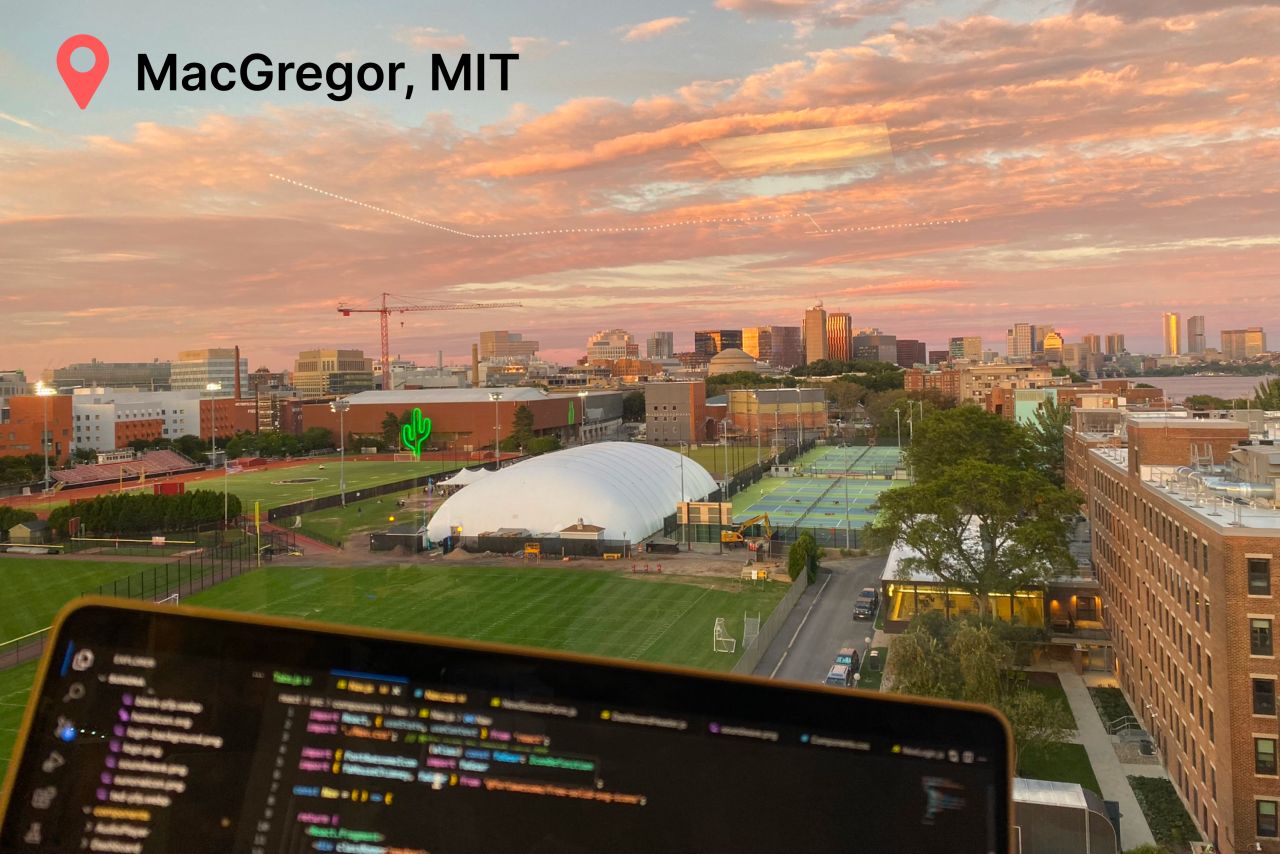
Since a lot of people have been asking, here's how we got our first customer at Delve: — At the time, Karun and I were building an AI medical scribe in between classes at MIT. Along the way, we met the founders of Bland. They had just pivoted out of healthcare and had lots of insight. We kept in touch. As we continued building, we hit the point where we needed to get HIPAA compliant for our scribe. That’s when we went down the rabbit hole of compliance requirements for 6 weeks straight. By the end of it, we had gotten so many ideas for low hanging fruit automations that would've made the process less painful. So we pivoted to automate compliance itself. — Right around that time, the Bland founders reached out. They needed to go through HIPAA too. They had a deadline they needed to hit, so we essentially became consultants for them in that time window. We spun up cloud infrastructure, revised policies, and helped their entire team go through security training. A few months later, they came back to us because they needed SOC 2. This time we just went directly to their office. — We hit the whiteboards and mapped out their entire data flow: what tools touched which data, where sensitive information flowed, and what technical architecture looked like. Then we made a plan of attack to divide and conquer the work. That day turned into a compliance super-day. By the end of it, they were done with major compliance requirements and had made significant security improvements across the board. (Plus, we had gotten a much better understanding of the process and knew even better how to streamline the process). Later, we managed the entire SOC 2 audit process for them from start to finish. We stayed in their Slack channel answering questions with 5min response time throughout the audit. — In that week alone, Bland unlocked $500k ARR with their SOC 2 report. To date, they've powered 50M+ phone calls and are used daily by 100+ enterprises. Meanwhile at Delve, we've scaled a lot of what we did for Bland. Now, every Delve customer gets a 1:1 Slack channel, end-to-end audit support, and a TurboTax-like platform that lays out compliance requirements very clearly. After Bland, we continued to do "compliance Collison installations" for many other customers and further automated everything that we did manually behind the scenes. — So to everyone who's been asking: your first customer doesn't come from cold outreach or paid ads. It comes from solving a problem you understand for someone you already know. Don't be afraid to consult or get your hands dirty. Those learnings help you build an even better experience and product compared to alternative solutions.
- DelveSince 13 Mar 2026
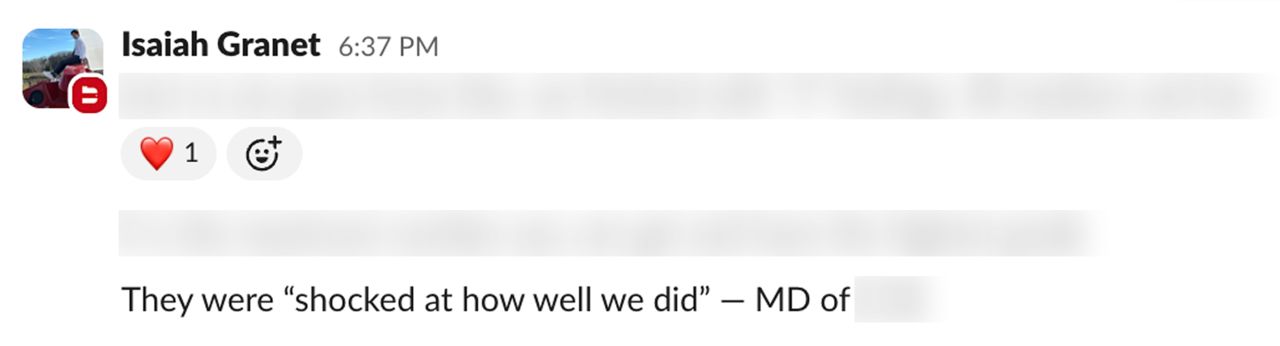
Last month, Bland completed a 24-hour in-person audit for a F100 enterprise with the help of Delve (spoiler: they passed with flying colors). Here's the story: Bland is an AI voice provider with over 100 enterprise customers that’s powered 50M phone calls to date. After a 9-month sales process with a F100 (which involved many security questionnaires), they made it to one of the final stages: an in-person audit. That meant an auditor would come to their office and spend 24 hours reviewing compliance policies, automated infrastructure tests, and past audit reports. — After a long 2 days and even more review, Bland ended up passing with flying colors. They scored the highest grade possible on the security review. Even the division’s managing director was “shocked at how well [they] did.” — At Delve, we know that compliance isn’t just about completing a checklist of to-dos or getting a PDF report. It’s about closing larger deals, reducing risks to your company, and scaling faster. For us, that means going the extra mile to help companies build strong security that won’t just get them to pass an audit, but also meet enterprise expectations. — So happy for Bland. They’re just 1 example of all the incredible things Delve customers accomplish.
- FronteggSince 8 Jul 2026
When an AI agent acts on behalf of your employee, who's accountable? Agen.co gives every agent an identity you control. Book a demo. Get a Weber Smokey Joe.
- Constella IntelligenceSince 16 Jun 2026
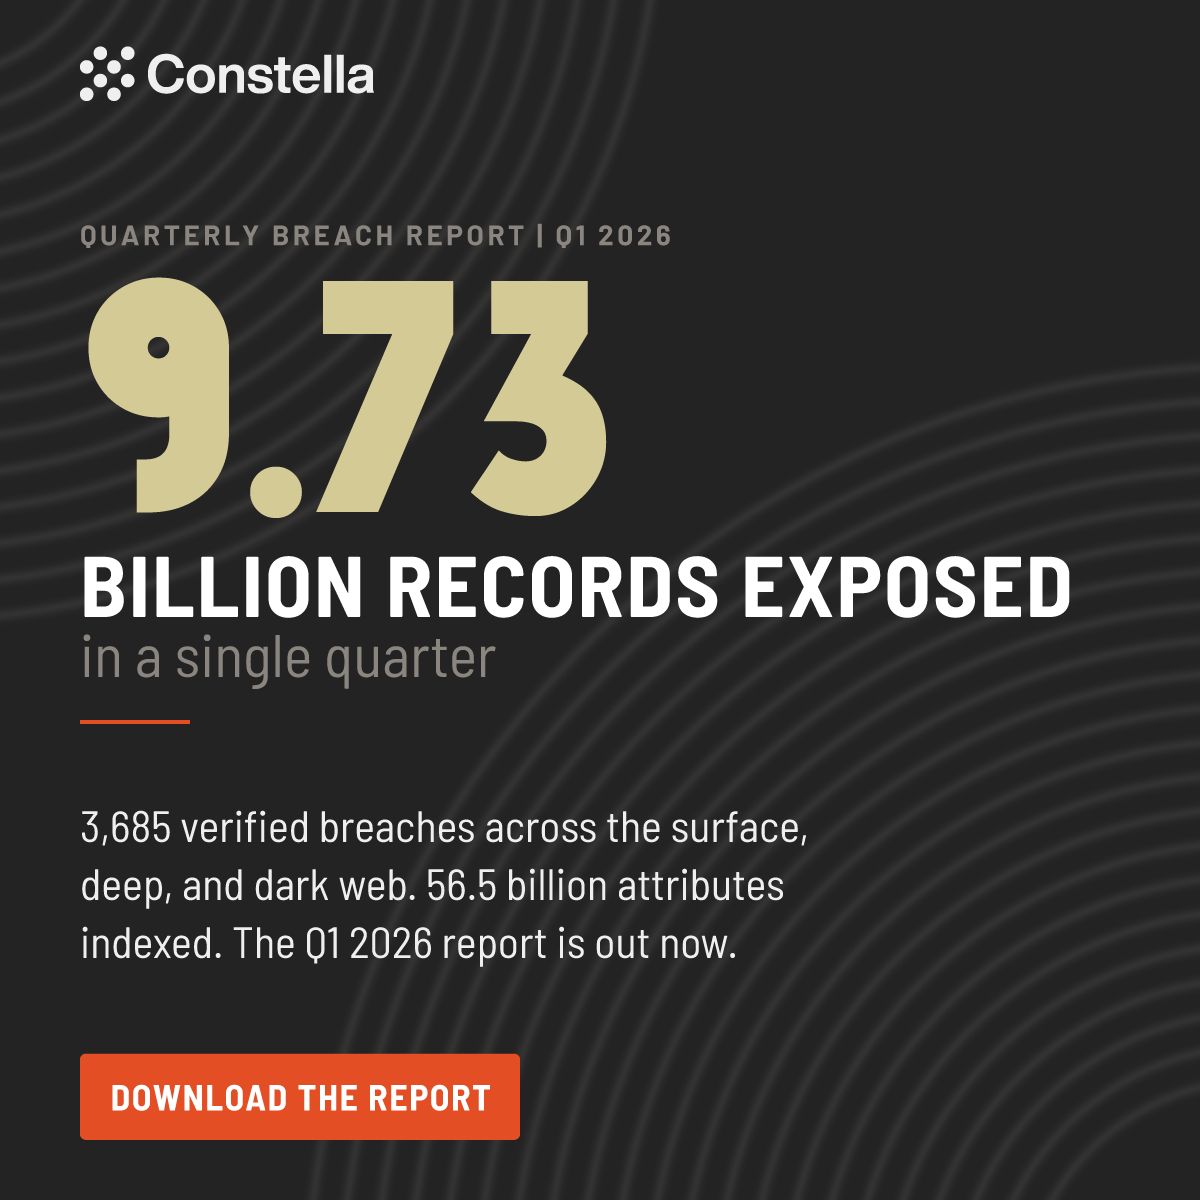
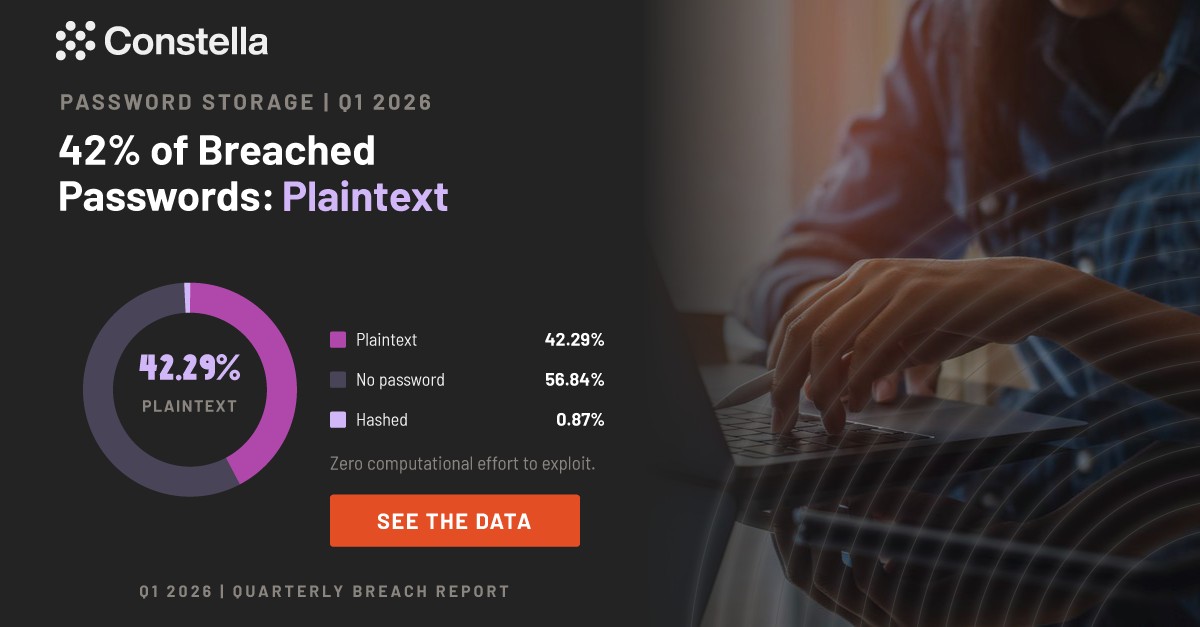
9,730,000,000. That is how many curated records entered the Constella Intelligence Data Lake in the first quarter of 2026, drawn from 3,685 verified breaches across the surface, deep, and dark web. The Q1 2026 Quarterly Breach Report is out, and the headline shift is this: 72% of verified breaches were direct compromises of live systems. Threat actors are not recycling old credential dumps. They are going after government registries, telecom databases, and financial platforms to harvest fresh, complete identity profiles. Inside the report: - 42.29% of breached passwords stored in plaintext - 31.6M infostealer packages from 2.77M infected devices - The 167.8M record SudamericaData incident, the quarter's largest - Sector, geographic, and attribute-level breakdowns Download your copy of the report here: https://lnkd.in/esVWqd9J #IdentityRisk #ThreatIntelligence #DataBreach #Infostealer #CyberSecurity
- Constella IntelligenceSince 18 Jun 2026
42% of Breached Passwords: Plaintext 42.29% of breached passwords in Q1 were stored in plaintext, usable with zero effort. The chart shows how little stood between attackers and the credentials they collected. Read the full password storage analysis. See the data in our new report: https://lnkd.in/efVSZwTX
- GDPRLocalRecorded 20 Sept 2026
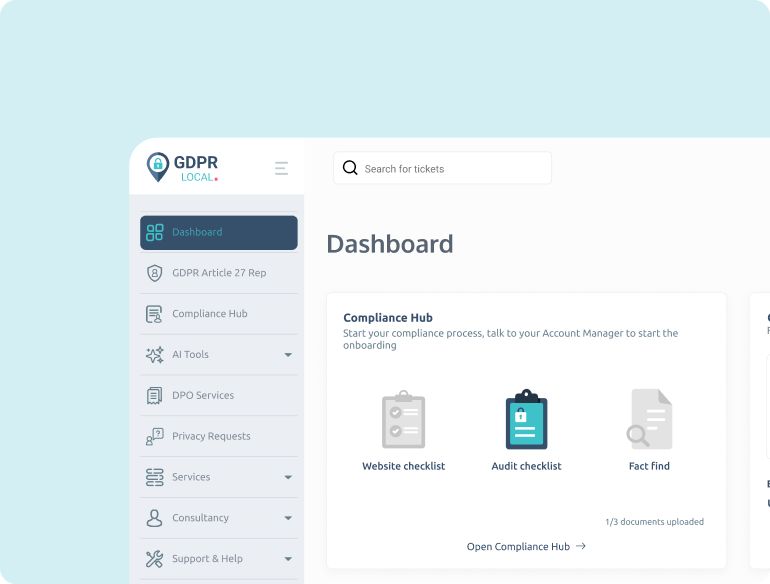
GDPR compliance comes down to knowing your data. What data do you collect and have a lawful basis for processing it? Data compliance should solve business problems, not create them. A startup that knows its data flows is better positioned than an enterprise with perfect documentation but no clear processes. Some companies have privacy policies but no idea what triggered Article 27 requirements - the obligation to appoint a local EU representative when you're based outside the EU. That’s why you should map your data flows first. Document your lawful basis second. Build from there. GDPR compliance is operational work that keeps you in business. For practical guidance on each of these steps: gdprlocal.com
- GDPRLocalRecorded 20 Sept 2026
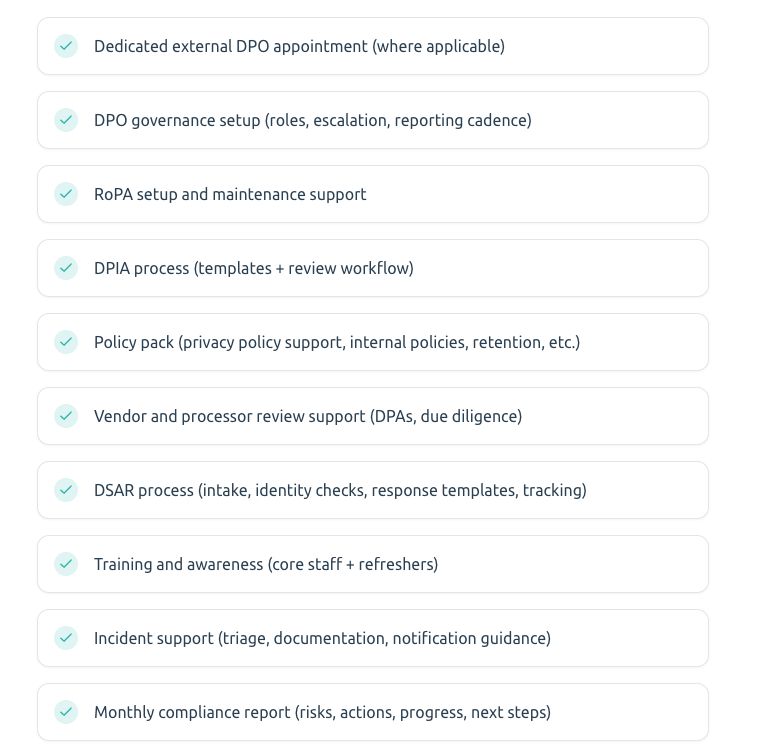
Do you know what a DPO does? It's a structured function that covers every layer of your company's data processing. Here's what a DPO does in practice: Advice & Guidance → Informs and advises management and staff on their obligations under the GDPR. Monitoring & Audits → Does internal audits and compliance checks, and reviews data protection policies, procedures, and documentation. Liaison & Contact Point → Acts as the primary contact point for Supervisory Authority and DSARs. Breach Management → Advises and assists the Controller in the event of a Personal Data Breach, including notifications. Training & Awareness → Advises on and provides a data protection awareness training plan. That's a lot of distinct functions. Each one has its own process, its own documentation, its own challenges. Understanding the full scope of what a DPO manages is the first step to knowing whether a company has the right coverage. See the full framework → dpo.gdprlocal.com
- i-doit groupSince 13 Jul 2026
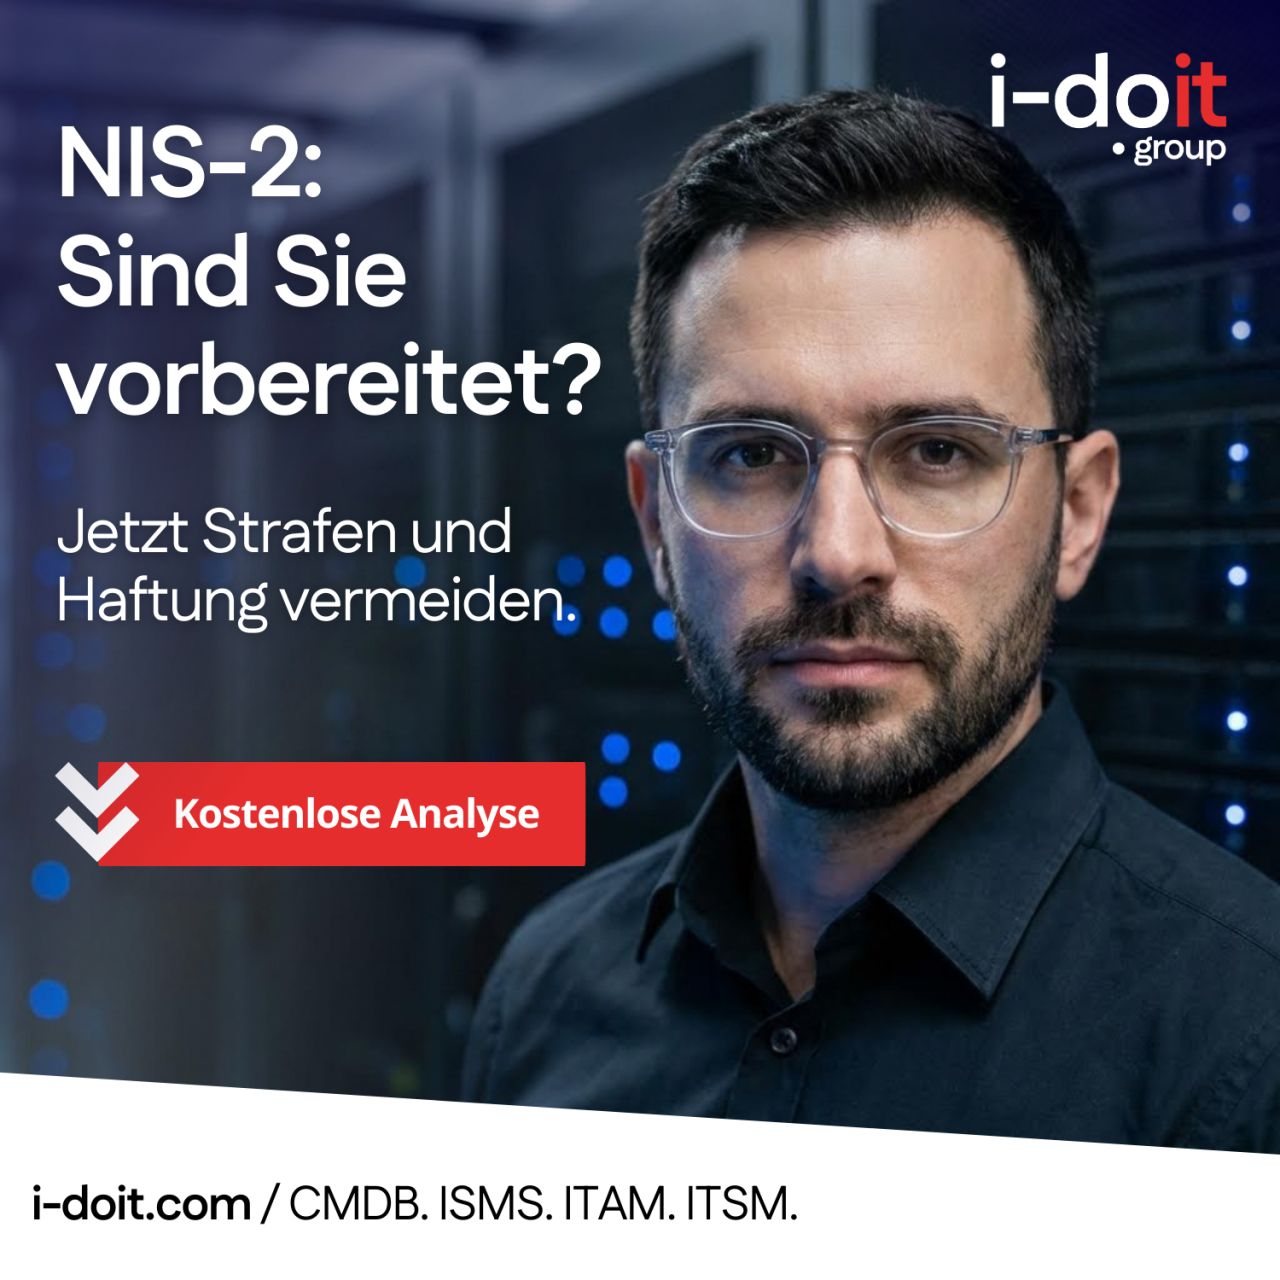
Achtung: NIS-2 ist verpflichtend. Es drohen Bußgelder von bis zu 10 Mio. € und eine persönliche Haftung der Geschäftsführung. Viele Unternehmen sind betroffen, ohne es zu wissen. Vereinbaren Sie jetzt Ihr kostenloses NIS-2 Analysegespräch – mit einem einzigen Klick. Teilen Sie Ihre Kontaktdaten mit uns. Das war's. Wir melden uns und klären gemeinsam Ihre individuelle Situation. Kostenlos und unverbindlich. Unser NIS-2 Analysegespräch zeigt Ihnen: ✅ Ob Ihr Unternehmen betroffen ist ✅ Welche Risiken und Fristen jetzt gelten ✅ Wie man NIS-2 strukturiert umsetzen kann Sanktionen vermeiden und Verantwortung übernehmen! 👉🏻 Jetzt Gutschein sichern.
- GarancySince 3 Aug 2026
IT-Schutz für KRITIS, Versorger und Kommunen: Identity-Management-Software aus Deutschland – für Sicherheit ohne Backdoors. Gerade für KRITIS-Betreiber, Versorger und Kommunen reicht es nicht aus, dass eine Lösung technisch sicher ist. Sie muss auch rechtlich belastbar sein. Wer digitale Identitäten verwaltet, bewegt sich im Spannungsfeld von Datenschutz, Compliance, Informationssicherheit und zunehmenden regulatorischen Anforderungen wie NIS-2 oder DORA. Deshalb wird die Frage, wo Software entwickelt wird, welchen Rechtsräumen sie unterliegt und wer im Ernstfall Verantwortung übernimmt, zu einem wichtigen Kriterium. Bei Garancy entwickeln und supporten wir unsere Software bewusst in Deutschland. Wir glauben an europäische Lösungen, weil das für unsere Kunden einen echten Unterschied macht: 🔐 Mehr digitale Souveränität: Unsere IDM-Software unterliegt den strengen europäischen Datenschutz- und Sicherheitsstandards. Das schafft Transparenz und reduziert rechtliche und geopolitische Abhängigkeiten. 🛡️ Sicherheit trifft Compliance: Gerade KRITIS-Betreiber, Versorger und Kommunen müssen nachvollziehen und belegen können, wer Zugriff auf ihre Systeme hat. Bei Garancy kennen wir die regulatorischen Rahmenbedingungen unserer Kunden aus der Praxis – von DSGVO, NIS-2, DORA und KRITIS bis hin zu individuellen Betriebsratsregelungen. Und helfen Unternehmen, sie rechtssicher umzusetzen. 🤝 Direkte Ansprechpartner statt anonymer Eskalationsketten: Kurze Wege, schnelle Abstimmungen und Teams, die erreichbar bleiben, zeichnen uns bei Garancy aus. Das gilt auch dann, wenn es kritisch wird. Kurz: Made in Germany ist für uns kein Herkunftssiegel. Es ist ein Beitrag zu mehr digitaler Souveränität, Sicherheit und Verlässlichkeit. Finden Sie jetzt heraus, wie Identity Management von Garancy Ihre IT-Landschaft sicherer und effizienter machen kann – auf garancy.com!
- Garantir CybersecuritySince 22 Jun 2026
Your code signing shouldn't be the reason your release is late. Compliance says signing keys must live in an HSM. Most teams read that as "upload every binary to a central server and wait" - a bottleneck that scales with artifact size. GaraTrust - the most trusted cryptographic services platform - never touches your binaries. The client hashes locally and sends only a small, fixed-length hash over the network. The signature comes back fast, whether the artifact is 10 MB or 10 GB. Same HSM-grade security. Millisecond signing. Every build, every release. Your security solution should protect the pipeline, not slow it down. Learn more. https://lnkd.in/gwwS4Smj//?utm_source=linkedin&utm_medium=paid&utm_id=1184340296&utm_campaign=CodeSigning-Consideration-WebVisits&hsa_acc=509002179&hsa_cam=1184340296&hsa_grp=858150176&hsa_ad=1472690456&hsa_net=linkedin&hsa_ver=3
- Garantir CybersecuritySince 22 Jun 2026
A valid signature doesn't mean the code is safe. It just means someone had the key. In a compromised build environment, traditional signing tools will sign malicious code without hesitation and ship it with your name on it. That's how the worst supply chain attacks happen: not a cracked key, but a trusted pipeline signing the wrong thing. GaraTrust, the cryptographic services platform from Garantir, verifies every binary against its source before a signature is ever generated. Reproducible builds, automated hash validation, and keys that stay non-exportable in an HSM. Built for NIST SSDF, SLSA, and EO 14028. This isn't code signing. It's supply chain defense. Learn More → https://lnkd.in/g8yKuHzB//?utm_source=linkedin&utm_medium=paid&utm_id=1184340296&utm_campaign=CodeSigning-Consideration-WebVisits&hsa_acc=509002179&hsa_cam=1184340296&hsa_grp=858150176&hsa_ad=1472710316&hsa_net=linkedin&hsa_ver=3
- SharetruRecorded 20 Sept 2026
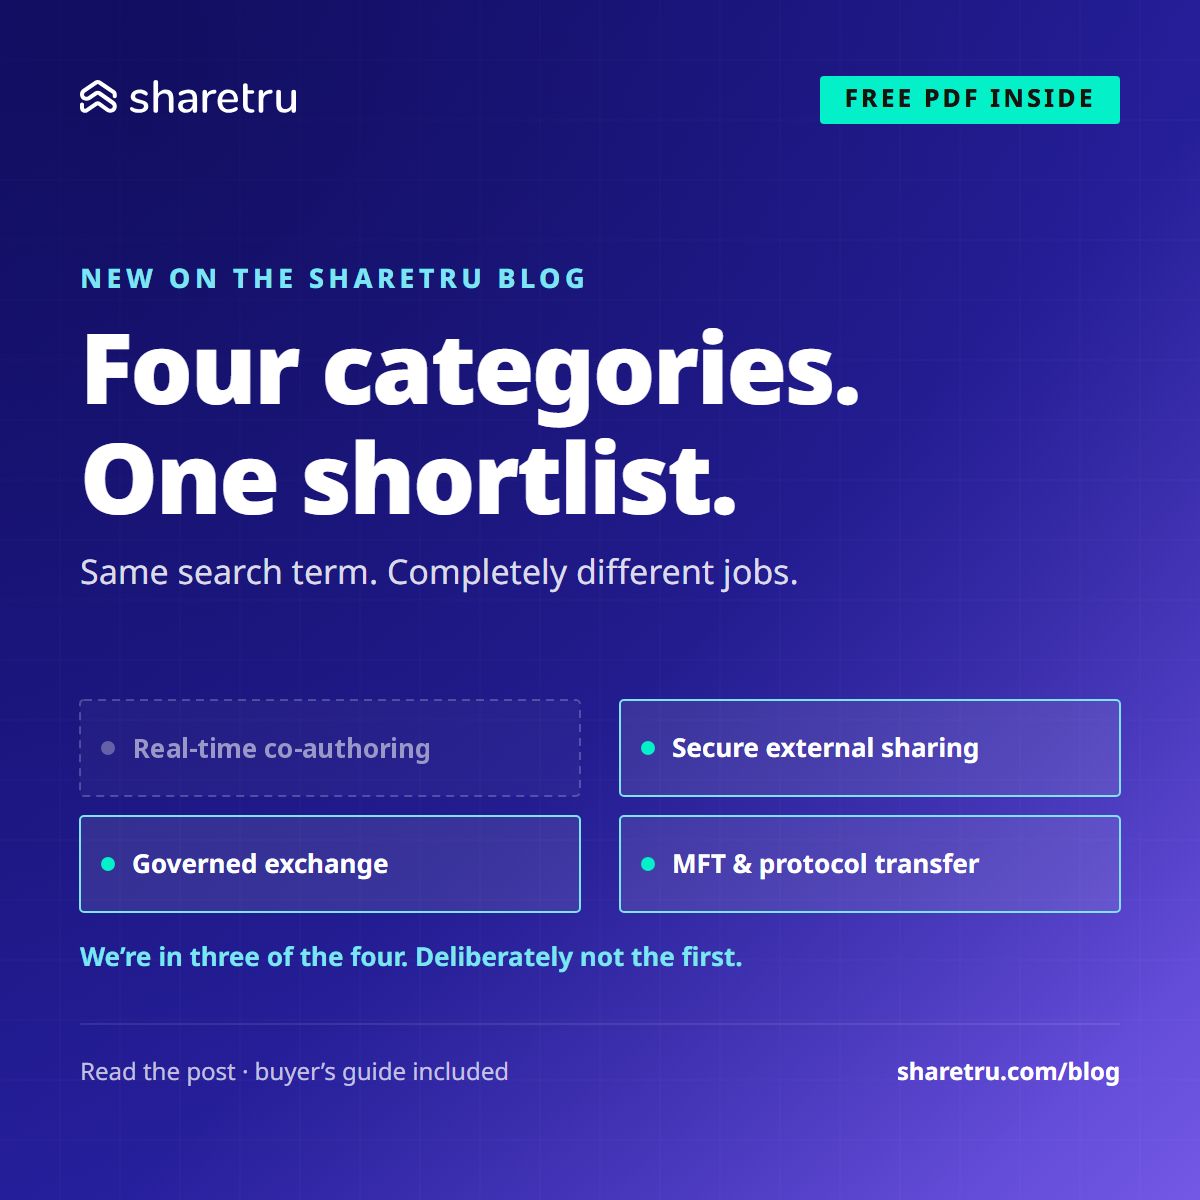
Half the platforms on a government file transfer shortlist aren't competing with each other. They're four different categories that happen to share a search term. Collaboration platforms are built for internal teamwork. Secure external sharing gets files to outside recipients without pushing people back to email. Governed exchange handles regulated data crossing an organizational boundary. MFT and protocol transfer handles automation, counterparties, legacy systems, scheduled jobs. We're in three of those four. Secure external sharing, governed exchange, protocol transfer — that overlap is the whole product. We are not a collaboration platform. Our own buying guide scores us None for internal co-authoring, and if that's the center of your decision, buy from the first column. We'll lose that evaluation and we should. Then there's the FedRAMP column, which every roundup flattens into a checkmark. A vendor can be FedRAMP authorized and still sell you something that isn't. The authorization attaches to one specific service inside one specific boundary. It doesn't attach to the company, and it doesn't travel with the logo. Buy the self-hosted version of an authorized vendor's product and you inherit nothing — not the boundary, not the continuous monitoring, not the evidence package. You own all of it, during an assessment, when someone asks you to prove it. That applies to us too, so I put it in writing. Sharetru sells three products. Only Sharetru Federal carries the FedRAMP Moderate authorization. If you need FedRAMP, the paperwork has to say Sharetru Federal. Our logo doesn't cover everything. Nobody's does. Sort the categories first. Then ask every vendor which deployment you'd be buying and what it actually inherits. Full breakdown, including where we're the wrong answer: https://lnkd.in/ezt7aVTf/?utm_campaign=Mid-funnelAdsforDemoRequest&utm_source=linkedin&utm_medium=paid&utm_id=820695156&hsa_acc=510106551&hsa_cam=820695156&hsa_grp=559627736&hsa_ad=1581823046&hsa_net=linkedin&hsa_ver=3 #fedramp #securefilesharing
- GBG PlcSince 9 Sept 2026
Verification, UBO discovery, screening and monitoring, together in one place, so your team isn't stitching it together.
- GBG PlcSince 9 Sept 2026
Multi-owner racing syndicates, onboarded fast, without compromising compliance. See how Weatherbys did it with GBG Detected.
- Gambit SecurityRecorded 20 Sept 2026
You can't really prepare to turn 40. It just happens. It happened to me last week. Incidents can't be prepared for either...I've had my share & the rudely fail to ever warn you before they hit! In a previous role, we took resilience testing seriously. Twice a year we'd break down the environment and actually stand it back up again, from infrastructure through to applications and data. We recorded it. Documented everything. We actually proved we could meet our RTOs and RPOs. I'd argue this was better than what most organisations were doing. But we'd spend the preceding 30 days getting ready. Practising recovery. Finding issues. Fixing things. Updating documentation. Trying again. And that's the bit I've thought about a lot since...We proved we could recover after preparing to recover. Real incidents don't work like that. You don't get 30 days to make sure everything works before the ransomware hits. Nobody freezes your environment while you prepare. And something you successfully recovered six months ago may have changed hundreds of times since. That's why I've changed how I think about resilience. I'm less interested in whether you passed your last DR test. I want to know whether you could recover your Minimum Viable Business today, tomorrow, next week... No rehearsal. No warning. Just the environment as it exists right now. That means understanding recovery continuously as code, infrastructure and dependencies change, rather than proving it at two carefully prepared points in the year. That's a big part of what we're focused on at Gambit. Continuously proving whether the systems your business actually depends on are recoverable. Turning 40 was inevitable (& surprisingly pleasant) Realizing a 4 hour RTO actually takes 30+ hours (& is ver unpleasant) doesn't have to be inevitable! Book a resilience assessment: hhttps://lnkd.in/eE8JJy-W
- G DATA CyberDefenseSince 10 Sept 2026
Cybersicherheit ist Teamwork. 🤝 Machen Sie alle Mitarbeitenden mit unseren Awareness Trainings zu Verbündeten.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.