On air · 1 of 3 networks
Gambit Security
- gambit.security
- Cybersecurity
- US
- 91 employees
Gambit Security’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 337. Watch Gambit Security with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 337 | Checked 28 Oct 2026 | See all 337 ads → | ||
| Meta | Not checked | — | |||
| None recorded | 0 | No ads found on the Google Ads Transparency Center | Checked 30 Oct 2026 | Collect them with the API → |
Gambit Security has 337 live LinkedIn ads. We recorded no Google ads on 30 Oct 2026.
Latest ads
- LINKEDIN · IMAGERecorded 20 Sept 2026
You can't really prepare to turn 40. It just happens. It happened to me last week. Incidents can't be prepared for either...I've had my share & the rudely fail to ever warn you before they hit! In a previous role, we took resilience testing seriously. Twice a year we'd break down the environment and actually stand it back up again, from infrastructure through to applications and data. We recorded it. Documented everything. We actually proved we could meet our RTOs and RPOs. I'd argue this was better than what most organisations were doing. But we'd spend the preceding 30 days getting ready. Practising recovery. Finding issues. Fixing things. Updating documentation. Trying again. And that's the bit I've thought about a lot since...We proved we could recover after preparing to recover. Real incidents don't work like that. You don't get 30 days to make sure everything works before the ransomware hits. Nobody freezes your environment while you prepare. And something you successfully recovered six months ago may have changed hundreds of times since. That's why I've changed how I think about resilience. I'm less interested in whether you passed your last DR test. I want to know whether you could recover your Minimum Viable Business today, tomorrow, next week... No rehearsal. No warning. Just the environment as it exists right now. That means understanding recovery continuously as code, infrastructure and dependencies change, rather than proving it at two carefully prepared points in the year. That's a big part of what we're focused on at Gambit. Continuously proving whether the systems your business actually depends on are recoverable. Turning 40 was inevitable (& surprisingly pleasant) Realizing a 4 hour RTO actually takes 30+ hours (& is ver unpleasant) doesn't have to be inevitable! Book a resilience assessment: hhttps://lnkd.in/eE8JJy-W
- LINKEDIN · IMAGERecorded 23 Oct 2026
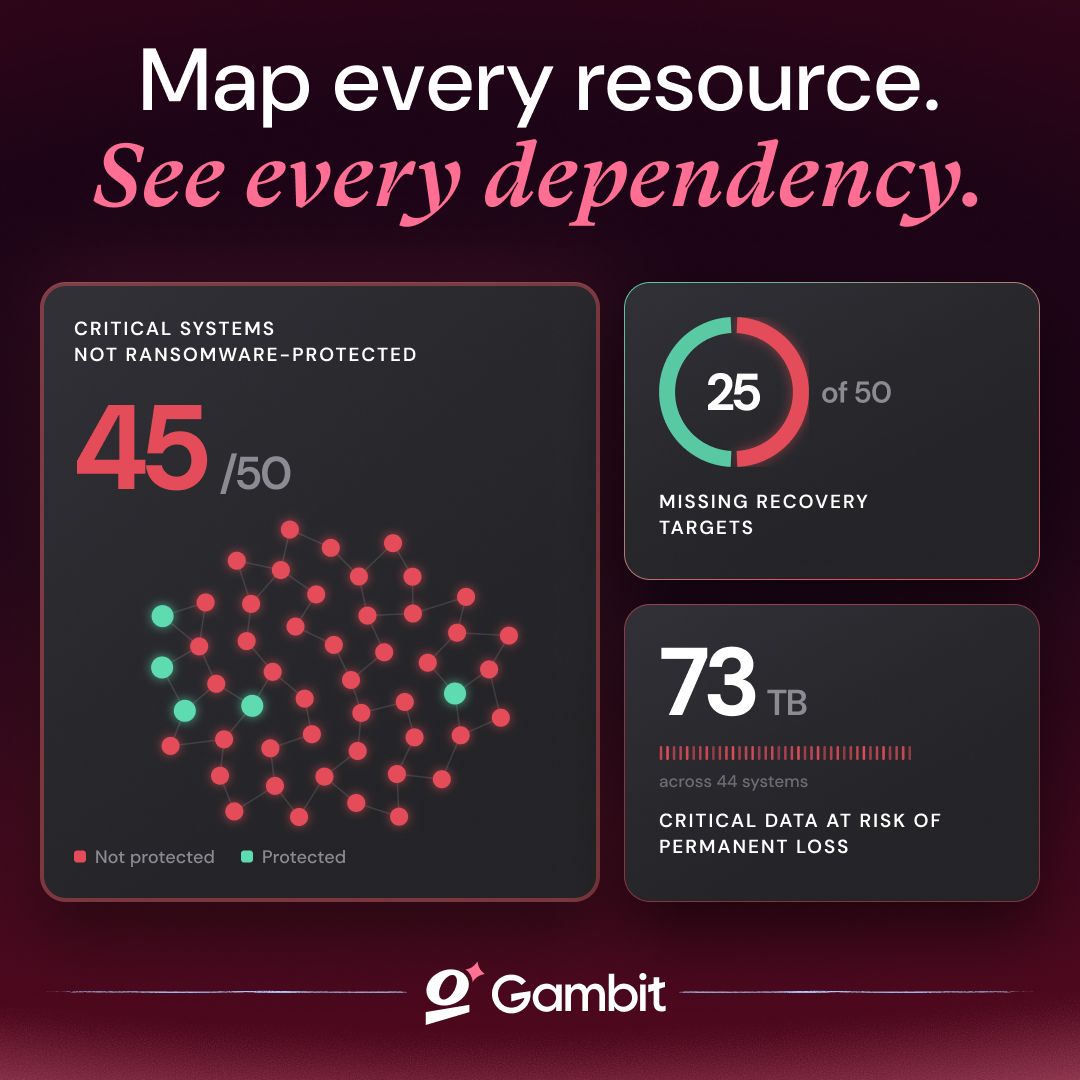
Map every dependency. Expose every recovery gap. Know what actually comes back - before disruption answers the question for you.
- LINKEDIN · IMAGERecorded 17 Oct 2026
MONDAY MOAN Resilience is hard to understand in cyber right now...We at Gambit Security are working hard to define it but there is so many different version out there right now. Let's start on things we agree on... 🔴 The current approach is BROKEN! Tabletop tests are like dungeons & dragons for executives & as a CISO I can tell you I will never run a tabletop I'm going to fail. Then we move on to simulations...We spend weeks prepping for them, assign people to the time period required, ensure they have the necessary skills & build a perfect environment...One I am not going to fail! The way we test resilience right now is based on DR & IR...𝗜𝗧 𝗗𝗢𝗘𝗦 𝗡𝗢𝗧 𝗪𝗢𝗥𝗞! 🔴 SOC 2, ISO 27001, FedRAMP, HIPAA, PCI DSS and DORA all touch resilience through recovery, continuity, availability and testing. But in practice, we still audit plans, backups, RTOs and annual exercises. In an AI age where attacks adapt and infrastructure changes constantly, that is weak evidence. If you cannot prove the business can still operate today, you are not auditing resilience. You are auditing paperwork...𝗜𝗧 𝗗𝗢𝗘𝗦 𝗡𝗢𝗧 𝗪𝗢𝗥𝗞! Resilience is the ability for your MVB to survive in any circumstances. You need to be able to 𝗽𝗿𝗼𝘃𝗲 𝘁𝗵𝗮𝘁 in your current environment 𝗮𝗹𝗹 𝘁𝗵𝗲 𝘁𝗶𝗺𝗲 and in 𝗿𝗲𝗮𝗹 𝗱𝗮𝘁𝗮 even when 𝘆𝗼𝘂𝗿 𝗲𝗻𝘃𝗶𝗿𝗼𝗻𝗺𝗲𝗻𝘁 𝗮𝗻𝗱 𝗮𝗽𝗽𝗹𝗶𝗰𝗮𝘁𝗶𝗼𝗻𝘀 𝗮𝗿𝗲 𝗰𝗼𝗻𝘀𝘁𝗮𝗻𝘁𝗹𝘆 𝗰𝗵𝗮𝗻𝗴𝗶𝗻𝗴. Find out how resilient you are...https://lnkd.in/etKYtXk3 𝘠𝘦𝘴 𝘐 𝘥𝘰 𝘭𝘰𝘷𝘦 𝘚𝘵𝘳𝘢𝘯𝘨𝘦𝘳 𝘛𝘩𝘪𝘯𝘨𝘴 𝘢𝘯𝘥 𝘵𝘩𝘦 𝘴𝘩𝘰𝘸 𝘪𝘯 𝘵𝘩𝘦 𝘞𝘦𝘴𝘵 𝘌𝘯𝘥 𝘪𝘴 𝘈𝘔𝘈𝘡𝘐𝘕𝘎!
- LINKEDIN · IMAGERecorded 16 Oct 2026
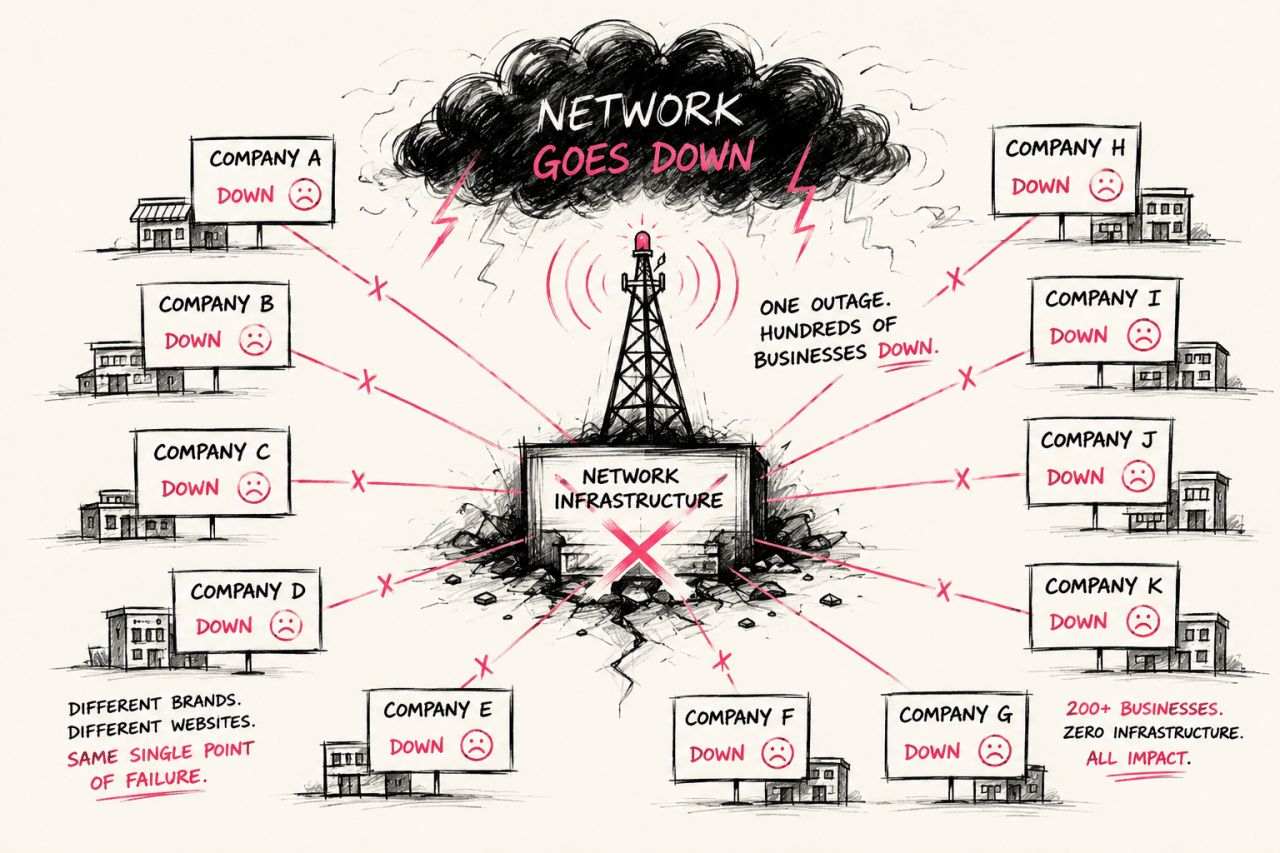
I had a conversation with a customer this week that changed how I think about resilience. We were talking about a telecoms provider. It serves millions of customers, but that's only half the story. Hundreds of other phone companies sell services on top of its network. Different brands. Different websites. Different customers. But no infrastructure. If the network goes down, every one of those businesses loses its product at exactly the same moment. It made me realise something. As CISOs, we're obsessed with mapping who can take us down... 🧨 Third parties. 🧨 Fourth parties. 🧨 Supply chain risk. We rarely ask the opposite...Who can't operate until we come back? That's the real dependency chain. Your resilience plan shouldn't stop at your front door. It should include every customer, partner and reseller whose business depends on yours. 𝗕𝗲𝗰𝗮𝘂𝘀𝗲 𝗿𝗲𝘀𝗶𝗹𝗶𝗲𝗻𝗰𝗲 𝗶𝘀𝗻'𝘁 𝗷𝘂𝘀𝘁 𝗮𝗯𝗼𝘂𝘁 𝗵𝗼𝘄 𝗾𝘂𝗶𝗰𝗸𝗹𝘆 𝘆𝗼𝘂 𝗿𝗲𝗰𝗼𝘃𝗲𝗿. 𝗜𝘁'𝘀 𝗮𝗯𝗼𝘂𝘁 𝗵𝗼𝘄 𝗺𝗮𝗻𝘆 𝗼𝘁𝗵𝗲𝗿 𝗯𝘂𝘀𝗶𝗻𝗲𝘀𝘀𝗲𝘀 𝗮𝗿𝗲 𝘄𝗮𝗶𝘁𝗶𝗻𝗴 𝗳𝗼𝗿 𝘆𝗼𝘂 𝘁𝗼. Book your Resilience Assessment: https://lnkd.in/ejrFmQDb
- LINKEDIN · IMAGERecorded 13 Oct 2026
Wandering through the woods on a firday random thought... One of the last items left in a trust center that's purely a PDF...recovery testing! People can have a crasy amount of audits per year! DORA. NIST. SOC 2. ISO 42001. Cyber insurance. Customer assurance. Different acronyms. Same question...Can you prove you can recover? And somehow the answer is still screenshots, spreadsheets and chasing engineers...At best a PDF done once a year. Every. Single. Time...That's insane! Your resilience evidence should already exist. Did recovery work? How long did it take? What broke? Can you prove it? If you do this once a year then one week later it's all irrelevant because something changed in the application or company. If you're rebuilding the evidence every time an auditor asks, you don't have evidence...You have an arts & crafts project. Book your Resilience Assessment: https://lnkd.in/e4fF2maj
- LINKEDIN · IMAGERecorded 13 Oct 2026
Sometime when we think about resilience we only see what's immediately in front of us and not the wider landscape so before you spend another $1 on resilience, tell me what actually matters that isn't right in front of your face. All of it?! A company recently told me they had to temporarily halt US production following a ransomware attack. Think about what “restart production” actually means in a business like that. Applications have to work. Infrastructure has to work. Identity and data have to be available. Operational technology matters. So do the third parties sitting somewhere in that chain. Miss one critical dependency and your recovery plan can look great while the business is still standing still. This is where I think we're spending resilience budgets in the wrong order. Cyber spending grew 12% last year according to Boston Consulting Group (BCG), with more than 80% of the security leaders they surveyed continuing to increase budgets into 2027. More money is coming. I'd spend the first part of it on understanding the business. Pick the process that absolutely has to restart after an attack. Map every application, identity, dataset, piece of infrastructure and external service it needs to function. Then decide where the resilience investment goes. That's how I think about Minimum Viable Business at Gambit Security. Start with what makes the business run, understand everything underneath it, then use that evidence to decide what deserves your time and money. Otherwise we risk spending more on resilience without actually knowing what we're trying to keep alive. Book your Resilience Assessment: https://lnkd.in/eiMCnq9b
6 of 337 adsSign up to see every Gambit Security ad, filter by format and date, and get alerts on new ones.
See all 337 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.