On air · 2 of 3 networks
Delve
- delve.co
- Cybersecurity
- US
- 23 employees
Delve’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 191. Watch Delve with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 147 | Checked 28 Oct 2026 | See all 191 ads → | ||
| Meta | Not checked | — | |||
| Running | 100+ | Ads on the Google Ads Transparency Center | Checked 30 Oct 2026 | Collect them with the API → |
Delve has 147 live LinkedIn ads. We recorded 100+ Google ads on 30 Oct 2026.
Latest ads
- LINKEDIN · IMAGESince 19 Mar 2026
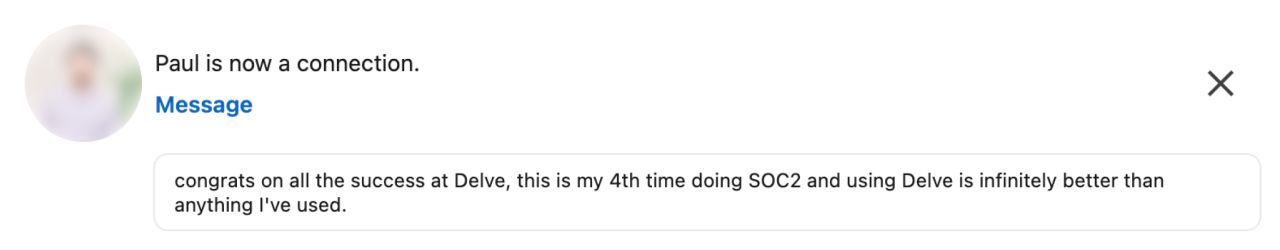
“This is my 4th time doing SOC 2 and using Delve is infinitely better than anything I’ve used.” Makes my day to get LinkedIn connection requests from customers like this. -- At Delve, we are re-thinking compliance from the ground up. Making compliance 10x easier for first-time complyers. And 10x more effective & proactive for enterprise teams at scale. We’ve built a different product from the ground up that doesn’t resemble what the compliance industry has had before. And it always makes our day to receive messages like this! -- The features that our fastest-growing customers use the most include: → AI Copilot that has full company context and can help complete any compliance task → AI to automate security questionnaires, helping fill out questionnaires that would’ve otherwise taken hours → Automated integration tests to monitor compliance and resolve any issues with step-by-step instructions custom to you -- A lot of our earliest customers have seen how fast the Delve product evolves every week. Our product looked very different just a quarter ago. Excited to keep iterating for all our customers!
- LINKEDIN · IMAGESince 16 Mar 2026
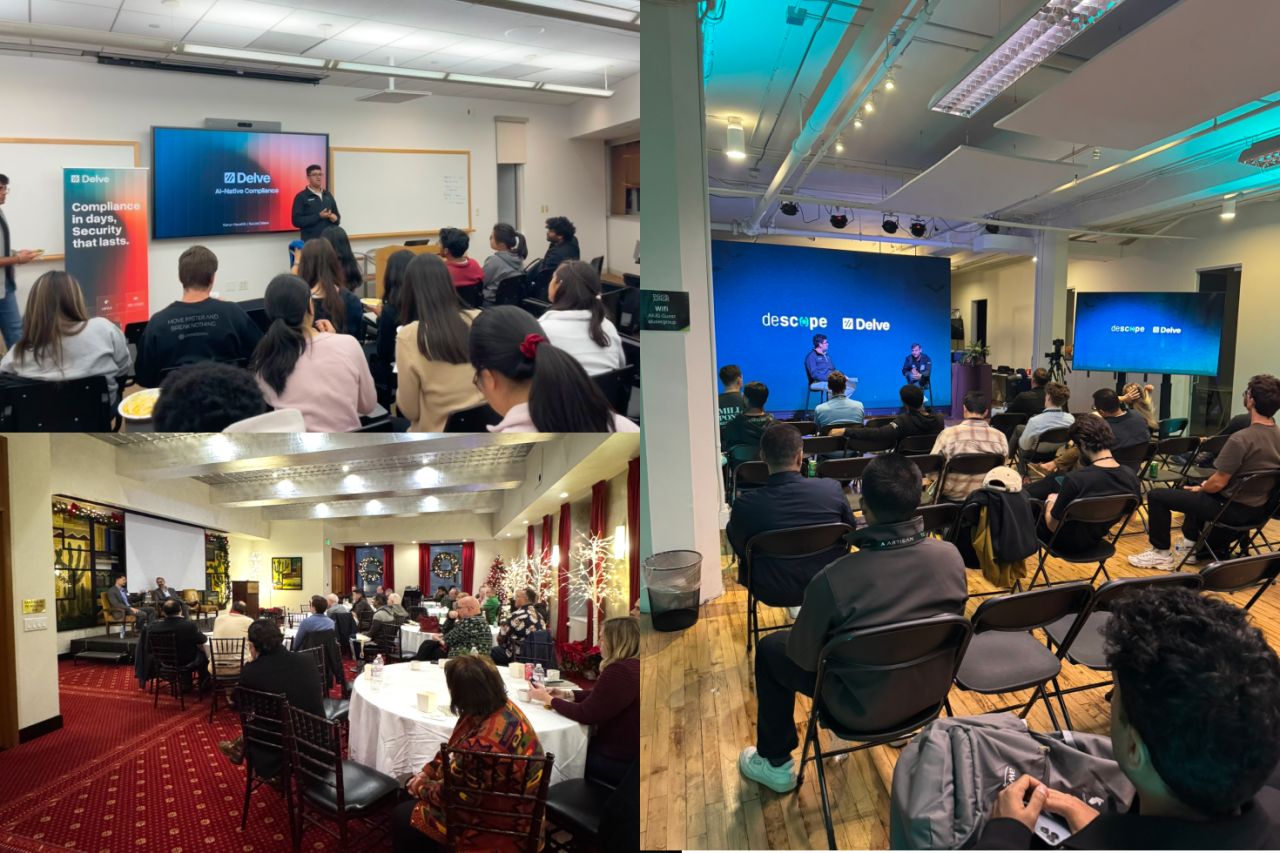
We’ve learned a lot over the last year scaling to 1,000+ compliance teams. Here’s how we see AI changing GRC in 2026. -- For the longest time, compliance has been reactive. Built on screenshots, point in time audits, and manual evidence pulled after the fact. That approach worked when systems changed slowly. But cloud and AI infrastructure now evolves faster than humans can reasonably track. From our experience, most compliance failures today do not come from missing controls. They happen in the gap between when something changes and when someone notices. -- We believe that in 2026, AI will significantly narrow that gap. Instead of manually pulling screenshots and evidence, AI will help collect compliance signals continuously, including from tools that do not expose APIs. When IAM policies change, cloud configurations shift, or new vendors are added, automations will increasingly support work that still depends on manual effort today. Compliance starts to reflect how systems behave in reality, not just how they looked during an audit window. -- This enables a bigger shift. In 2026, we believe risk will be forecasted, not reported after the fact. Controls will be monitored continuously instead of validated quarterly with screenshots. Remediation will be tailored to your environment and risk tolerance rather than generic to an industry checklist. Even frameworks will evolve, moving away from pass-or-fail and toward more contextual risk scoring. -- Regulation is already pushing in this direction. The EU AI Act, ISO 42001, and the NIST AI RMF all require ongoing risk management, documentation, and governance, not static reports. -- AI turns compliance from a reactive obligation into a source of continuous insights. Compliance is not about eliminating risk. It is about managing it. It shapes how much trust customers place in you and how clearly you understand risk inside your own organization. When controls are monitored over time, you gain visibility into how your systems actually operate. That visibility helps you build trust with customers, make better internal decisions, and run the business with fewer blind spots. That is how AI turns compliance into proactive insight in 2026.
- LINKEDIN · IMAGESince 16 Mar 2026
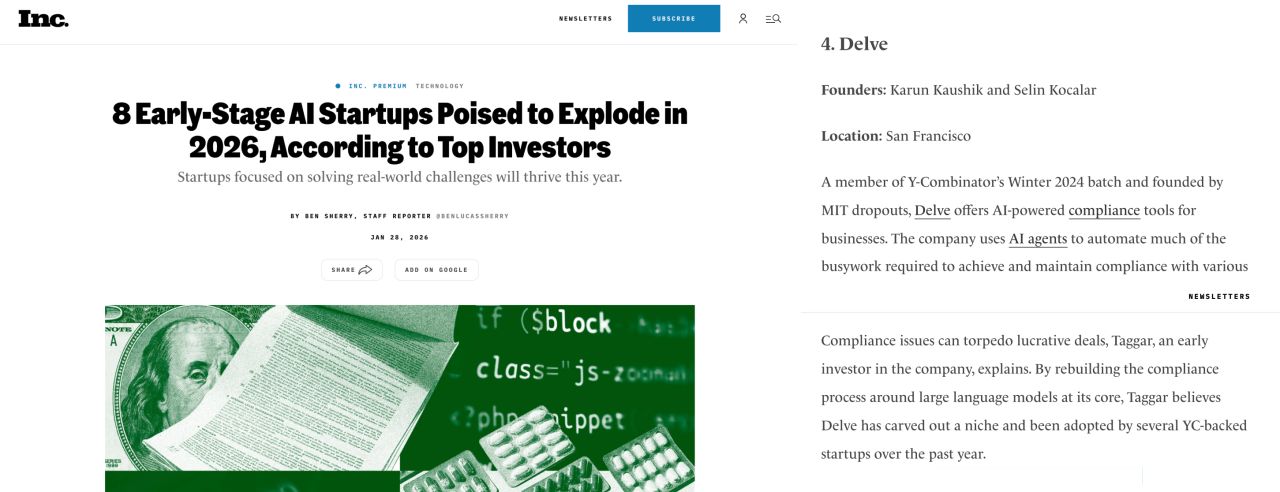
Last week, Inc. Magazine named Delve as one of the 8 Early-Stage AI Companies to Watch this year! A year ago, we had a handful of customers. Today, we support 1,000+ teams across 50+ countries. Huge congrats to the rest of the list, OpenEvidence, AMI Labs by Yann LeCun, Eureka Labs by Andrej Karpathy, Listen Labs, cubic (YC X25), Axiom, and Reducto. Onward 🚀
- LINKEDIN · IMAGESince 16 Mar 2026
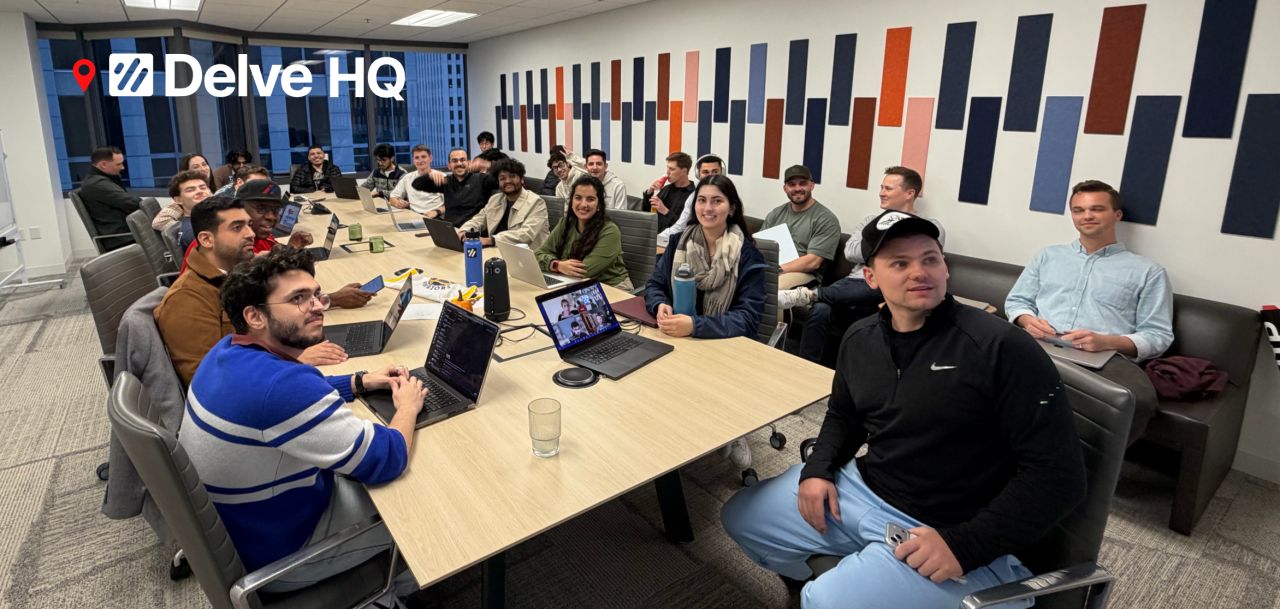
At Delve, we’re 3% the team size of our competitors doing 30% of their monthly revenue. A lot of people ask how we do it. Here’s the key: -- The operational structure of companies built in the last 2 years looks nothing like the ones built before thanks to AI. Our org chart looks different. Our codebase looks different. Our customer support functions differently. The way we manage emails, ramp sales reps, and set team milestones looks different. -- It’s not just smaller team = less red tape = faster execution. The core makeup of the company is different. And to reach the same ARR milestones, we simply need fewer heads. -- Here’s what that means for each team member at Delve. Every action they take creates 10x more leverage than someone at any other company. 1 sales call is worth 10 sales calls at another company. 1 customer ticket response is worth 10 responses at another company. 1 Linkedin post is worth 10 posts at another company. This is word-for-word what I tell the team. And it's why we bet on people at Delve. We bring on highly capable, mission-aligned people. We give everyone high ownership and accountability. Because what "AI-native" really means to us isn't just that our product incorporates AI. It means that by using AI cleverly across the company, we can build for leverage and hire for ownership. Headcount is so irrelevant to us.
- LINKEDIN · IMAGESince 14 Mar 2026
Since a lot of people have been asking, here's how we got our first customer at Delve: — At the time, Karun and I were building an AI medical scribe in between classes at MIT. Along the way, we met the founders of Bland. They had just pivoted out of healthcare and had lots of insight. We kept in touch. As we continued building, we hit the point where we needed to get HIPAA compliant for our scribe. That’s when we went down the rabbit hole of compliance requirements for 6 weeks straight. By the end of it, we had gotten so many ideas for low hanging fruit automations that would've made the process less painful. So we pivoted to automate compliance itself. — Right around that time, the Bland founders reached out. They needed to go through HIPAA too. They had a deadline they needed to hit, so we essentially became consultants for them in that time window. We spun up cloud infrastructure, revised policies, and helped their entire team go through security training. A few months later, they came back to us because they needed SOC 2. This time we just went directly to their office. — We hit the whiteboards and mapped out their entire data flow: what tools touched which data, where sensitive information flowed, and what technical architecture looked like. Then we made a plan of attack to divide and conquer the work. That day turned into a compliance super-day. By the end of it, they were done with major compliance requirements and had made significant security improvements across the board. (Plus, we had gotten a much better understanding of the process and knew even better how to streamline the process). Later, we managed the entire SOC 2 audit process for them from start to finish. We stayed in their Slack channel answering questions with 5min response time throughout the audit. — In that week alone, Bland unlocked $500k ARR with their SOC 2 report. To date, they've powered 50M+ phone calls and are used daily by 100+ enterprises. Meanwhile at Delve, we've scaled a lot of what we did for Bland. Now, every Delve customer gets a 1:1 Slack channel, end-to-end audit support, and a TurboTax-like platform that lays out compliance requirements very clearly. After Bland, we continued to do "compliance Collison installations" for many other customers and further automated everything that we did manually behind the scenes. — So to everyone who's been asking: your first customer doesn't come from cold outreach or paid ads. It comes from solving a problem you understand for someone you already know. Don't be afraid to consult or get your hands dirty. Those learnings help you build an even better experience and product compared to alternative solutions.
- LINKEDIN · IMAGESince 13 Mar 2026
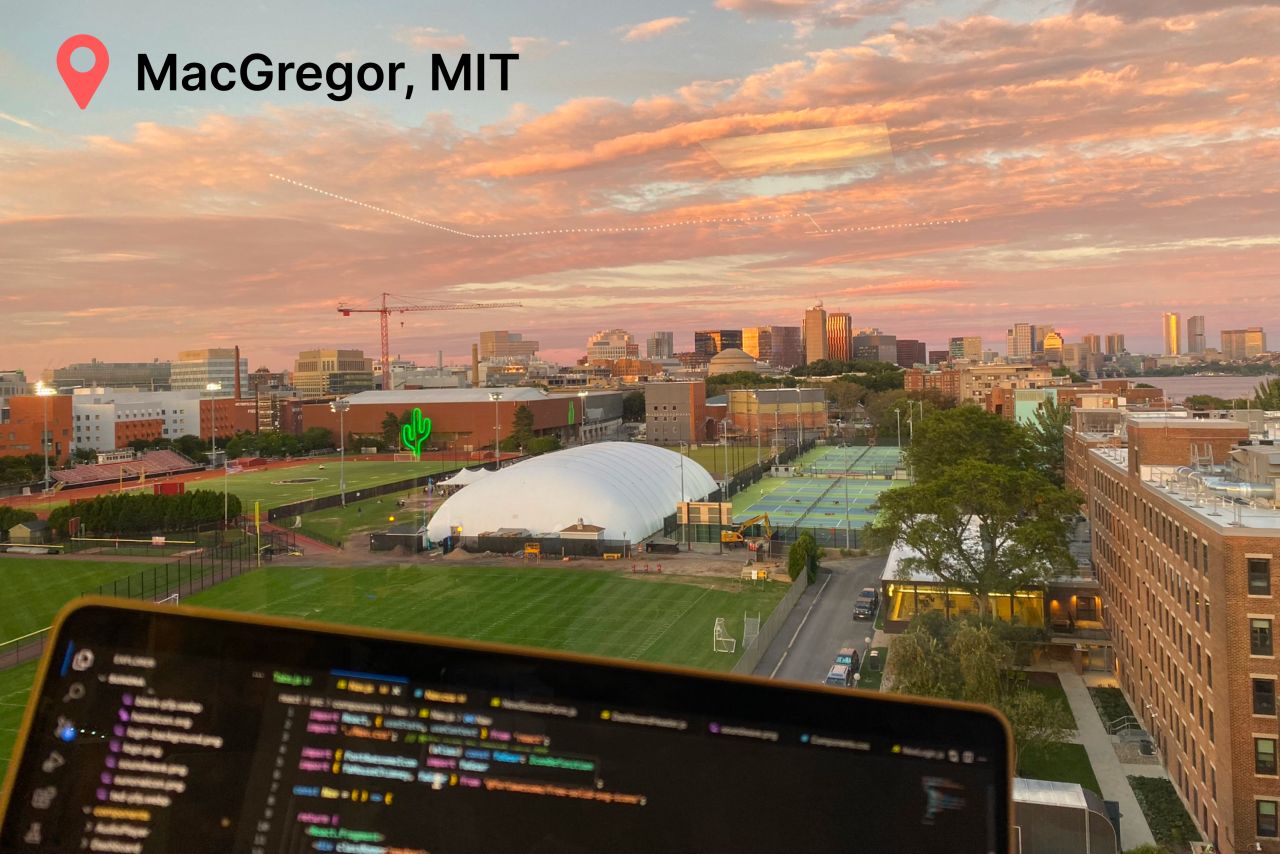
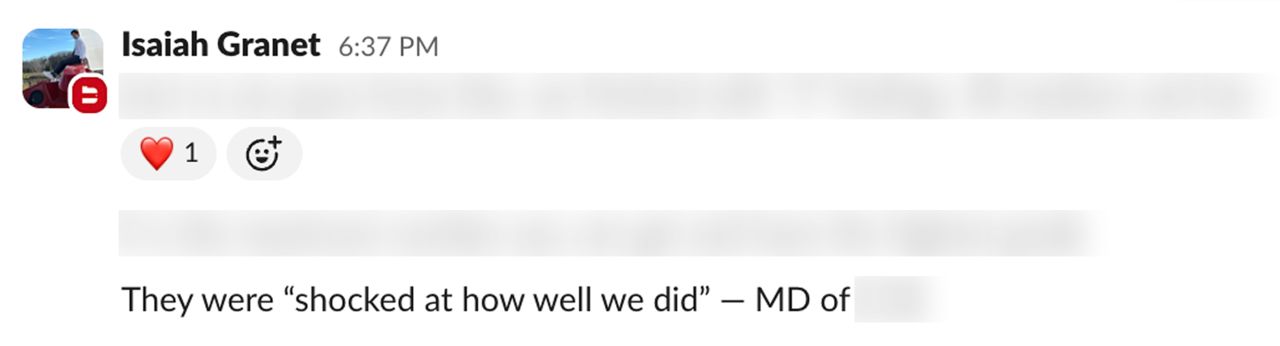
Last month, Bland completed a 24-hour in-person audit for a F100 enterprise with the help of Delve (spoiler: they passed with flying colors). Here's the story: Bland is an AI voice provider with over 100 enterprise customers that’s powered 50M phone calls to date. After a 9-month sales process with a F100 (which involved many security questionnaires), they made it to one of the final stages: an in-person audit. That meant an auditor would come to their office and spend 24 hours reviewing compliance policies, automated infrastructure tests, and past audit reports. — After a long 2 days and even more review, Bland ended up passing with flying colors. They scored the highest grade possible on the security review. Even the division’s managing director was “shocked at how well [they] did.” — At Delve, we know that compliance isn’t just about completing a checklist of to-dos or getting a PDF report. It’s about closing larger deals, reducing risks to your company, and scaling faster. For us, that means going the extra mile to help companies build strong security that won’t just get them to pass an audit, but also meet enterprise expectations. — So happy for Bland. They’re just 1 example of all the incredible things Delve customers accomplish.
6 of 191 adsSign up to see every Delve ad, filter by format and date, and get alerts on new ones.
See all 191 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.