On air · 2 of 3 networks
Garantir Cybersecurity
- garantir.io
- Cybersecurity
- US
- 19 employees
Garantir Cybersecurity’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 35. Watch Garantir Cybersecurity with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 28 | Checked 28 Oct 2026 | See all 35 ads → | ||
| Meta | Not checked | — | |||
| Running | 5 | Ads on the Google Ads Transparency Center | Checked 30 Oct 2026 | Collect them with the API → |
Garantir Cybersecurity has 28 live LinkedIn ads. We recorded 5 Google ads on 30 Oct 2026.
Latest ads
- LINKEDIN · IMAGESince 27 Jun 2026
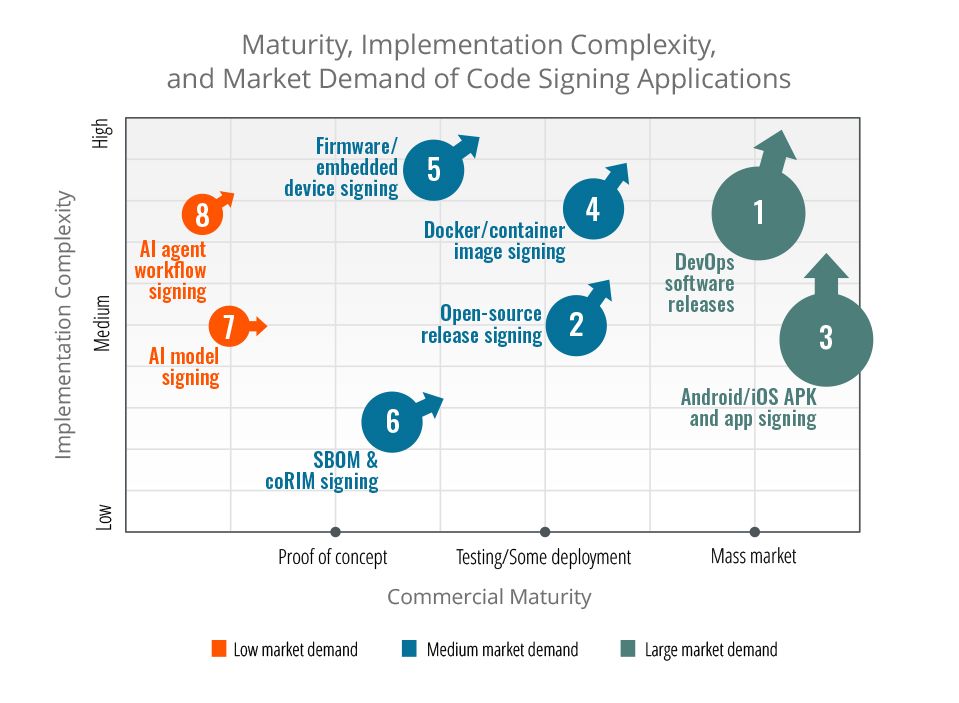
Code signing is an increasingly sought-after addition to existing cryptographic services and Public Key Infrastructure (PKI) offerings, with bolstered demand driven by fears surrounding supply chain attacks and AI security. Three buckets of use cases are of particular note as the code signing market continues to evolve: 1) AI use cases: Provenance concerns alongside IP and proprietary data protection interests are currently concentrating demand around model signing, however the proliferation of AI agents into enterprise environments is contributing to growing demand for workflow signing despite runtime context introducing some obstacles for deployment here. The status and projected trajectory of emergent AI-orientated use cases is a progressively important development to watch in this space. 2) IoT use cases: Despite the increasingly widespread nature of code signing applications such as embedded device and firmware signing, device heterogeneity and the resultant interoperability challenges, long device lifecycles, and limited compute capacity or memory all continue to complicate deployment. 3) DevOps use cases: Code signing is also an established part of DevOps and the CI/CD pipeline, however, macro challenges impacting the broader PKI market are beginning to impact DevOps signing processes. Increasing supply chain attacks, demands for quantum migration, and costs are all points of friction here. Our thoughts on the opportunities and challenges presented by the code signing market as well as some of the key vendors operating in this space such as Garantir Cybersecurity, Encryption Consulting LLC, SEALSQ, Entrust, Keyfactor, HID, AppViewX, and DigiCert are covered in our recent reports, linked in the comments below.
- LINKEDIN · IMAGESince 22 Jun 2026
Post-quantum cryptography isn't a future problem. It's a code signing problem you have right now. Most signing platforms aren't built for cryptographic agility. When PQC standards land, switching algorithms means a costly rip-and-replace — because keys, trust chains, and workflows are hard-wired to legacy crypto. GaraTrust was built differently. It supports quantum-safe algorithms and multi-vendor HSMs, so you can change algorithms without disrupting a single CI/CD pipeline. Cloud, on-prem, or air-gapped, your signing architecture holds as standards evolve. Future-proof your code signing before the mandate forces your hand.
- LINKEDIN · IMAGESince 22 Jun 2026
How many vendors does it take to cover your cryptographic operations? One for code signing. Another for certificate lifecycle management. A few for PKI. A different process for SSH. Maybe another for S/MIME - managed separately, or frankensteined together. GaraTrust is one platform for all of it. Start where the pressure is – code signing – and expand into CLM, private PKI, SSH, S/MIME, and document signing from the same deployment, the same control plane, the same investment. One platform. One vendor. Multiple security initiatives solved. Learn more. https://lnkd.in/gkNPhHuR//?utm_source=linkedin&utm_medium=paid&utm_id=1184340296&utm_campaign=CodeSigning-Consideration-WebVisits&hsa_acc=509002179&hsa_cam=1184340296&hsa_grp=858150176&hsa_ad=1472800356&hsa_net=linkedin&hsa_ver=3
- LINKEDIN · IMAGESince 22 Jun 2026
As of March 1, 2026, publicly trusted code signing certificates max out at 460 days. The multi-year cert is dead. That means more renewals, more room for human error, and more chances for an expired certificate to take down your signing pipeline at the worst possible moment. And it's not a future mandate - it's in effect now. GaraTrust automates the entire certificate lifecycle for code signing. Renewals happen seamlessly in the background, and every signing request is authenticated against your trusted certificates automatically. No manual tracking. No surprise expirations. No signing outages. See why its trusted by global entrerprises! https://lnkd.in/gSrh4Gth//?utm_source=linkedin&utm_medium=paid&utm_id=1184340296&utm_campaign=CodeSigning-Consideration-WebVisits&hsa_acc=509002179&hsa_cam=1184340296&hsa_grp=858150176&hsa_ad=1472730336&hsa_net=linkedin&hsa_ver=3
- LINKEDIN · IMAGESince 22 Jun 2026
A valid signature doesn't mean the code is safe. It just means someone had the key. In a compromised build environment, traditional signing tools will sign malicious code without hesitation and ship it with your name on it. That's how the worst supply chain attacks happen: not a cracked key, but a trusted pipeline signing the wrong thing. GaraTrust, the cryptographic services platform from Garantir, verifies every binary against its source before a signature is ever generated. Reproducible builds, automated hash validation, and keys that stay non-exportable in an HSM. Built for NIST SSDF, SLSA, and EO 14028. This isn't code signing. It's supply chain defense. Learn More → https://lnkd.in/g8yKuHzB//?utm_source=linkedin&utm_medium=paid&utm_id=1184340296&utm_campaign=CodeSigning-Consideration-WebVisits&hsa_acc=509002179&hsa_cam=1184340296&hsa_grp=858150176&hsa_ad=1472710316&hsa_net=linkedin&hsa_ver=3
- LINKEDIN · IMAGESince 22 Jun 2026
Your code signing shouldn't be the reason your release is late. Compliance says signing keys must live in an HSM. Most teams read that as "upload every binary to a central server and wait" - a bottleneck that scales with artifact size. GaraTrust - the most trusted cryptographic services platform - never touches your binaries. The client hashes locally and sends only a small, fixed-length hash over the network. The signature comes back fast, whether the artifact is 10 MB or 10 GB. Same HSM-grade security. Millisecond signing. Every build, every release. Your security solution should protect the pipeline, not slow it down. Learn more. https://lnkd.in/gwwS4Smj//?utm_source=linkedin&utm_medium=paid&utm_id=1184340296&utm_campaign=CodeSigning-Consideration-WebVisits&hsa_acc=509002179&hsa_cam=1184340296&hsa_grp=858150176&hsa_ad=1472690456&hsa_net=linkedin&hsa_ver=3
6 of 35 adsSign up to see every Garantir Cybersecurity ad, filter by format and date, and get alerts on new ones.
See all 35 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.