LinkedIn image ad examples
1,342 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- DH2iSince 7 Oct 2026
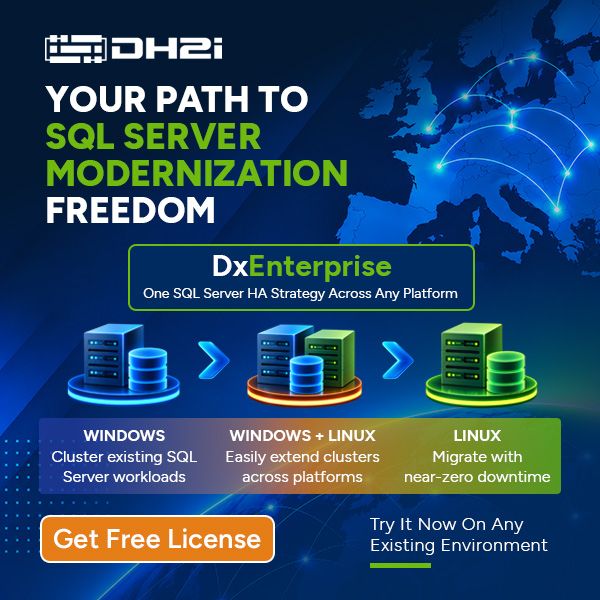
Building a more sovereign IT strategy doesn’t mean you have to migrate every SQL Server workload at once. DxEnterprise lets you move from Windows to Linux at your own pace while maintaining consistent high availability across both environments.
- DH2iSince 7 Oct 2026
Taking greater control of where your SQL Server workloads run? DxEnterprise provides one consistent HA approach across Windows, Linux, and containers—without tying your HA strategy to a specific platform.
- AftraSince 8 Oct 2026
Cybersecurity shouldn’t be scary, but sometimes what you find when you go looking is. Since October is #Cybersecurityawarenessmonth and Halloween, we’re offering a 30 day free trial of Aftra to help you uncover the digital skeletons in your closet. Do you dare to give it a try? Link in comments.
- AftraSince 8 Oct 2026
In October the leaves start to fall, the mornings are frigid cold, and in Iceland it starts to get noticeably darker. A preview into the long, dark, cold winter to come. It's also Halloween month. A time to put on costumes and scare away the bad spirits before the autumn harvest. Which makes it quite fitting that it's also been adopted as #cybersecurityawareness month. It's a time to think about what we can do better and educate others on how to stay secure. To cleanse your digital environment of risks. And that's why over at Aftra we're offering a free month trial right now. If you sign up in October, you'll get 30 days for free to uncover your digital exposure and can even try out our new security training to raise awareness amongst your team. Go check it out. Link in comments.
- Cimento AIRecorded 10 Oct 2026
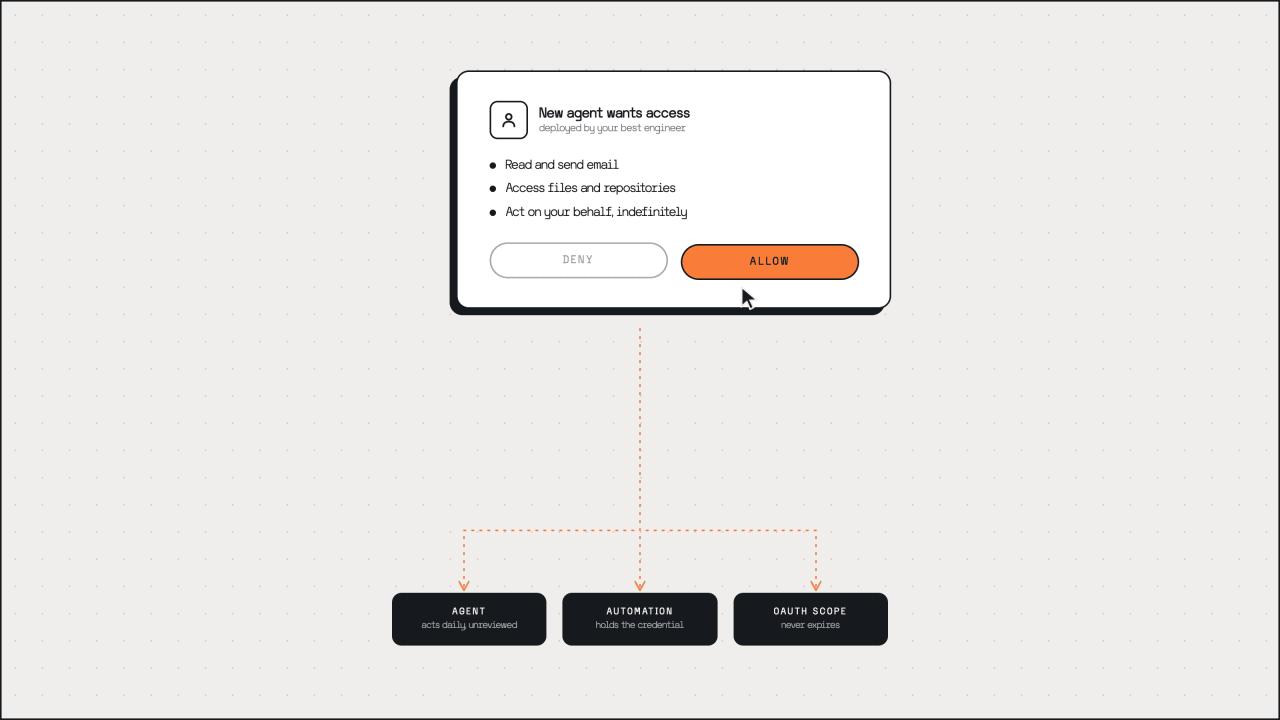
Every security awareness program is built around the same person: the employee who's behind on training and clicks whatever lands in the inbox. That picture is out of date. The riskiest people in most companies now are the most forward-thinking ones. The engineers adopting agents, approving OAuth scopes, handing automation credentials. Not maliciously. Enthusiastically. A click is discrete and trainable. An allow is continuous; it compounds, and it delegates. Most measurement programs are still pointed at the click. New post on where to point the instrument instead, starting with your strongest people rather than your weakest: https://lnkd.in/g-ue7qbZ
- Autonomous SecuritySince 5 Oct 2026
AI agents are becoming part of the enterprise stack. Security teams need visibility and control across the entire agentic ecosystem. Autonomous Security helps you discover AI agents, understand their access and risk, and enforce security policies in real time. See how it works.
- Autonomous SecuritySince 5 Oct 2026
Let AI run wherever it needs to. The agentic surface is evolving fast. New agents, features, and cloud based execution create new paths for risk. Secure your entire agentic environment with Autonomous Security.
- CyberVadisSince 15 Sept 2026
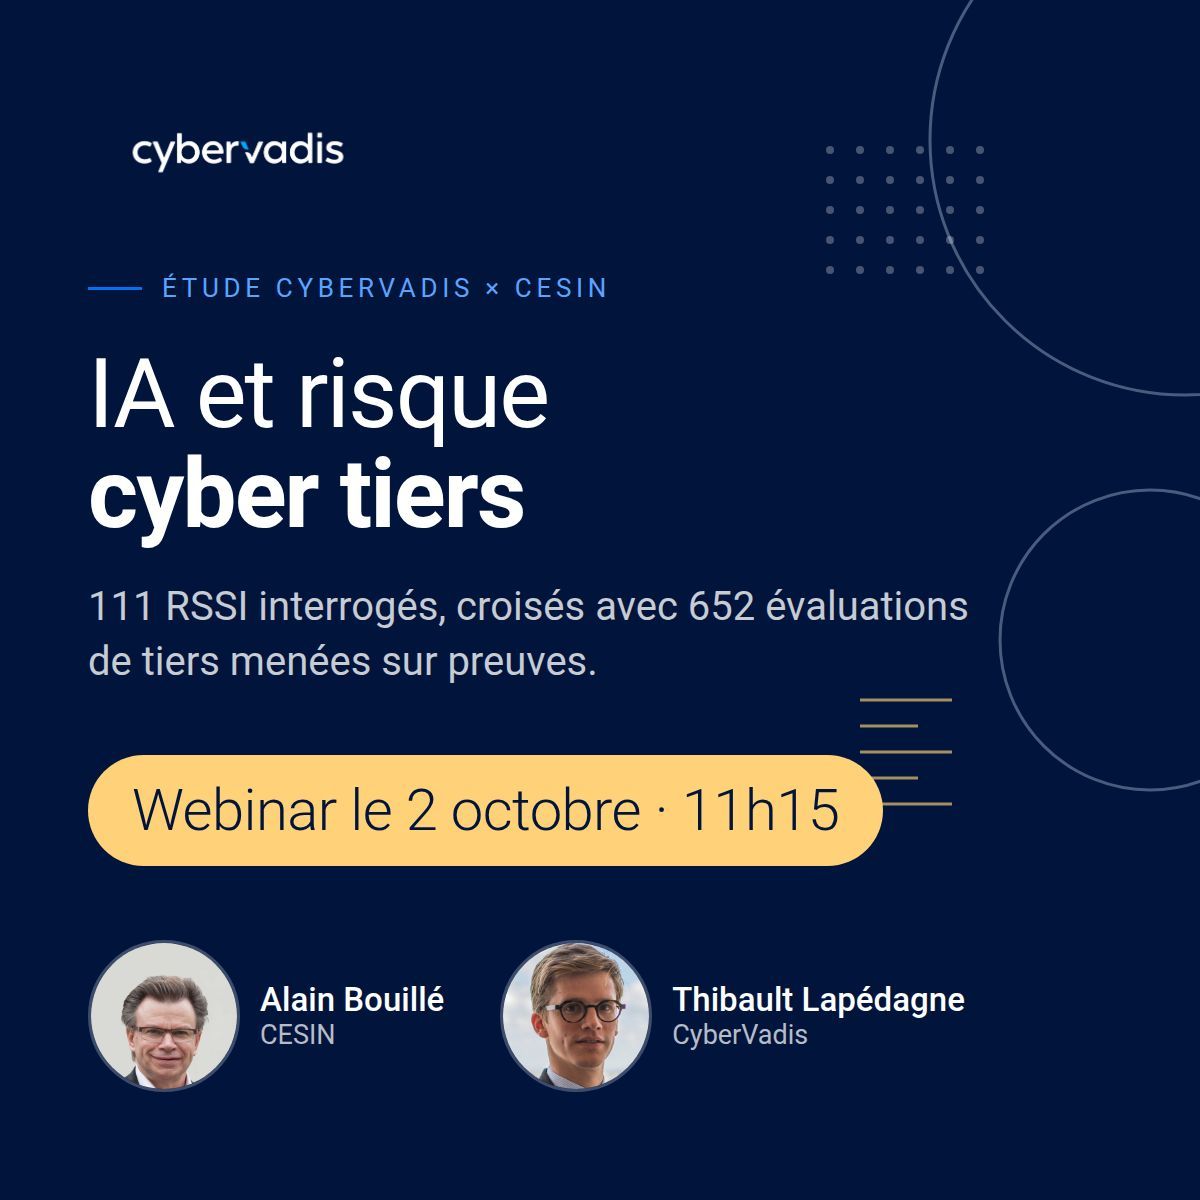
83 % des RSSI n’ont pas encore couvert le risque IA de leurs tiers. Et vous ? CyberVadis et le CESIN ont croisé les réponses de 111 RSSI avec 652 évaluations de tiers menées sur preuves. 📅 Le 2 octobre à 11h15, découvrez les écarts entre perception et réalité — et 3 priorités concrètes pour agir. 👉 Inscrivez-vous au webinar.
- Centro Nacional de Cibersegurança (CNCS) - Portuguese National Cybersecurity CentreSince 15 Sept 2026
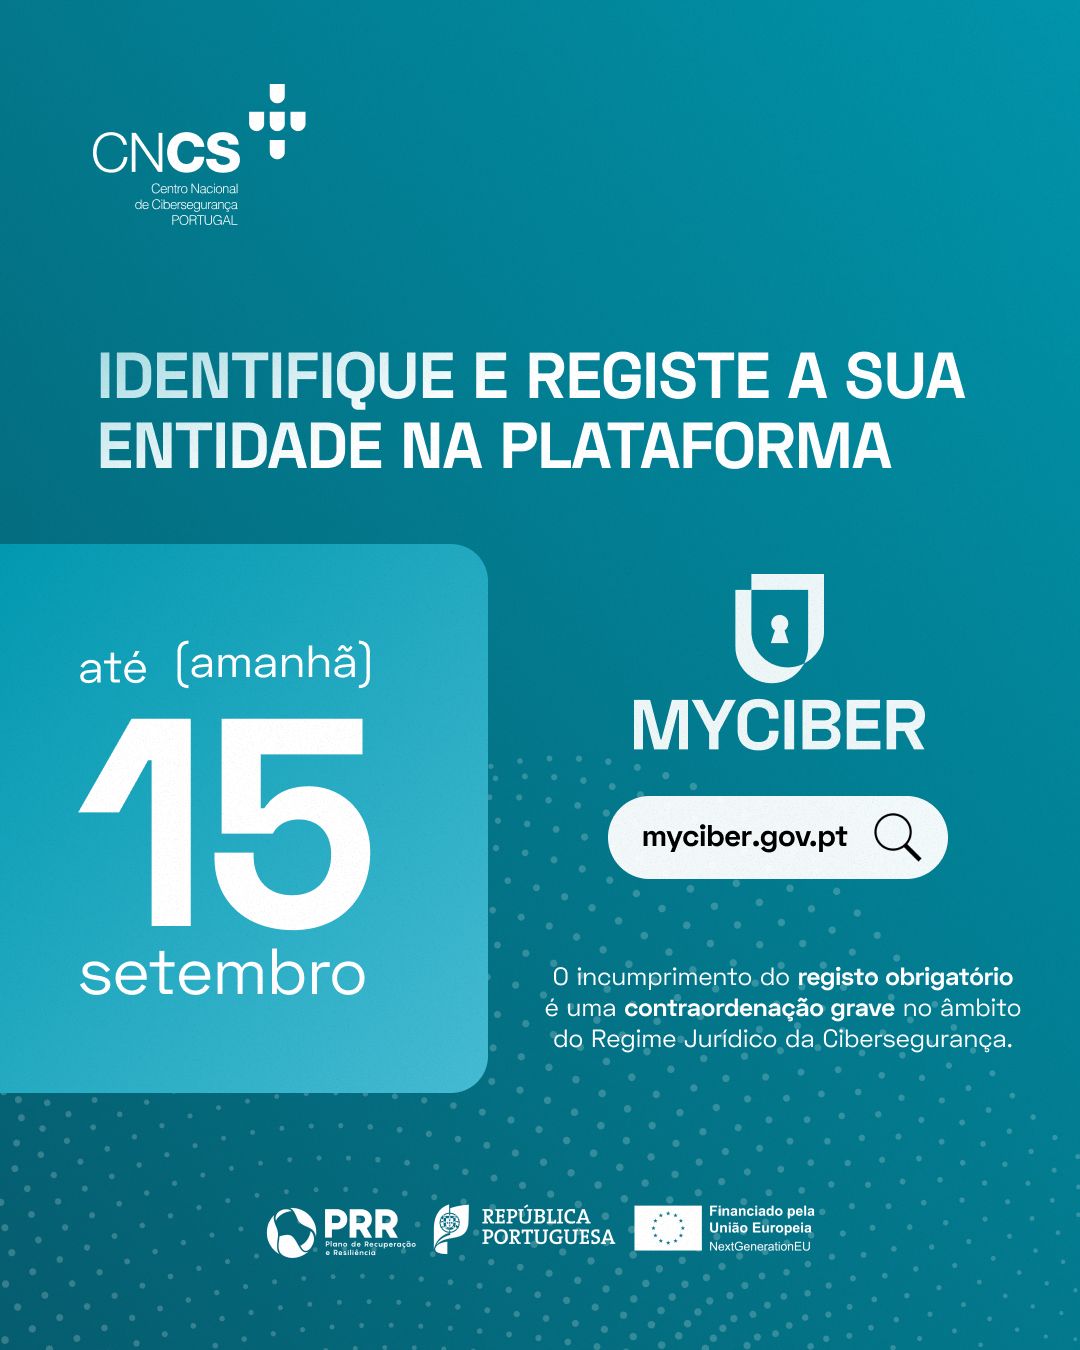
🚨 Termina amanhã o prazo final a que estão obrigadas as entidades abrangidas no artigo 3.º do Regime Jurídico da Cibersegurança, para cumprirem a sua obrigação de autoidentificação e registo na Plataforma MyCiber. Este é o primeiro passo para garantir o processo de qualificação das entidades e evitar o seu incumprimento, punível com coima. Para além dos setores já abrangidos pelo anterior regime, o novo enquadramento legal passou também a abranger setores como a gestão de serviços de tecnologias da informação ou comunicação, águas residuais, espaço, indústria transformadora, serviços postais e de estafeta, gestão de resíduos, produção, fabrico e distribuição de produtos químicos, produção, transformação e distribuição de produtos alimentares, prestação de serviços digitais e investigação. ⚠️ O processo de registo não constitui uma tarefa técnica exclusiva dos serviços de informática. O registo apenas pode ser realizado pelo representante legal da entidade ou uma pessoa a quem tenham sido atribuídos poderes específicos para o efeito, que deve autenticar-se na plataforma através da Chave Móvel Digital ou do Cartão de Cidadão. 📌 A utilização do Sistema de Certificação de Atributos Profissionais (SCAP), quando disponível, pode simplificar o processo de validação dos poderes de representação. Antes de concluir o processo: ✅ Verifique se a sua entidade está abrangida ✅ Identifique corretamente o setor de atividade da entidade para efeitos de enquadramento nos Anexos I e II do Regime Jurídico da Cibersegurança ✅ Complete o registo e a autoidentificação ✅ Conheça as obrigações que lhe são aplicáveis 👉 https://myciber.gov.pt 🔗 Saiba mais: https://lnkd.in/dtEhu_fd A conformidade começa pela identificação. Não deixe esta obrigação legal para depois do prazo. 🔐 Mais do que uma obrigação legal, a cibersegurança é um investimento na resiliência, na confiança e na continuidade da atividade das organizações. #MyCiber #NIS2 #RecuperarPortugal #ConstruirOFuturo #PRR
- CoplaSince 15 Sept 2026
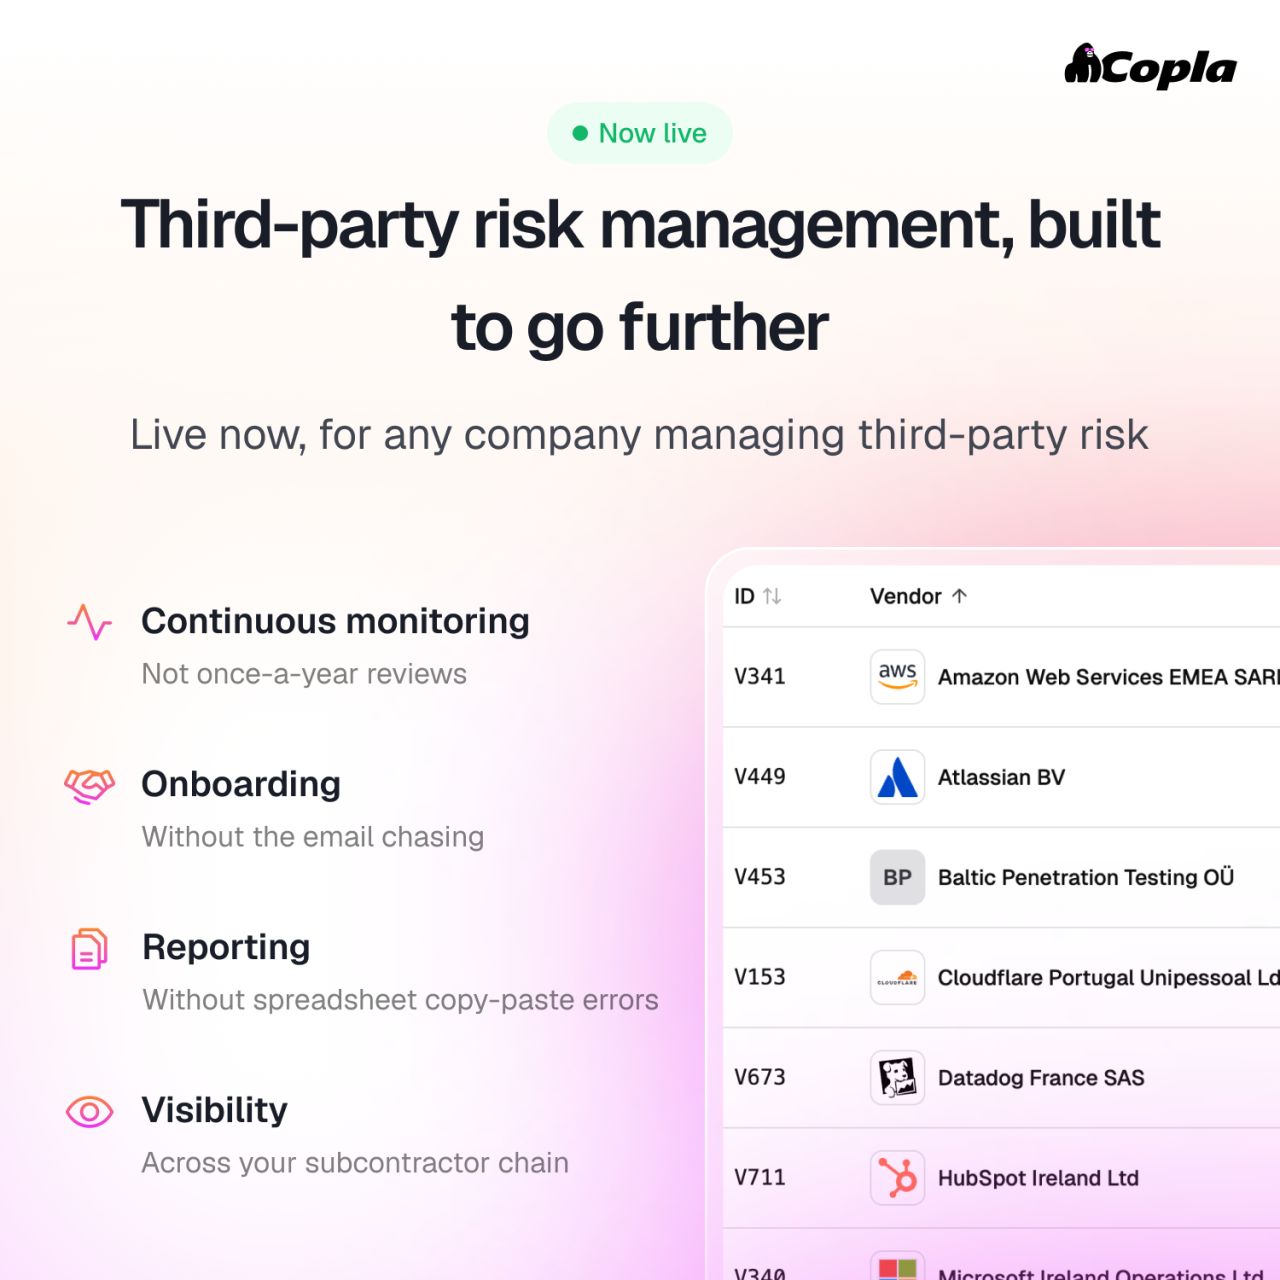
Today we're launching our third-party risk management software at Copla, and it's one of the products I'm proudest of this year. It covers ICT third-party risk under DORA, and goes further. It's live now, for any company managing vendor relationships. If your process still runs on spreadsheets, book a meeting with me and let’s talk about how Copla’s TPRM software can improve your processes: https://lnkd.in/dHF9SeEr
- CyCognitoSince 15 Sept 2026
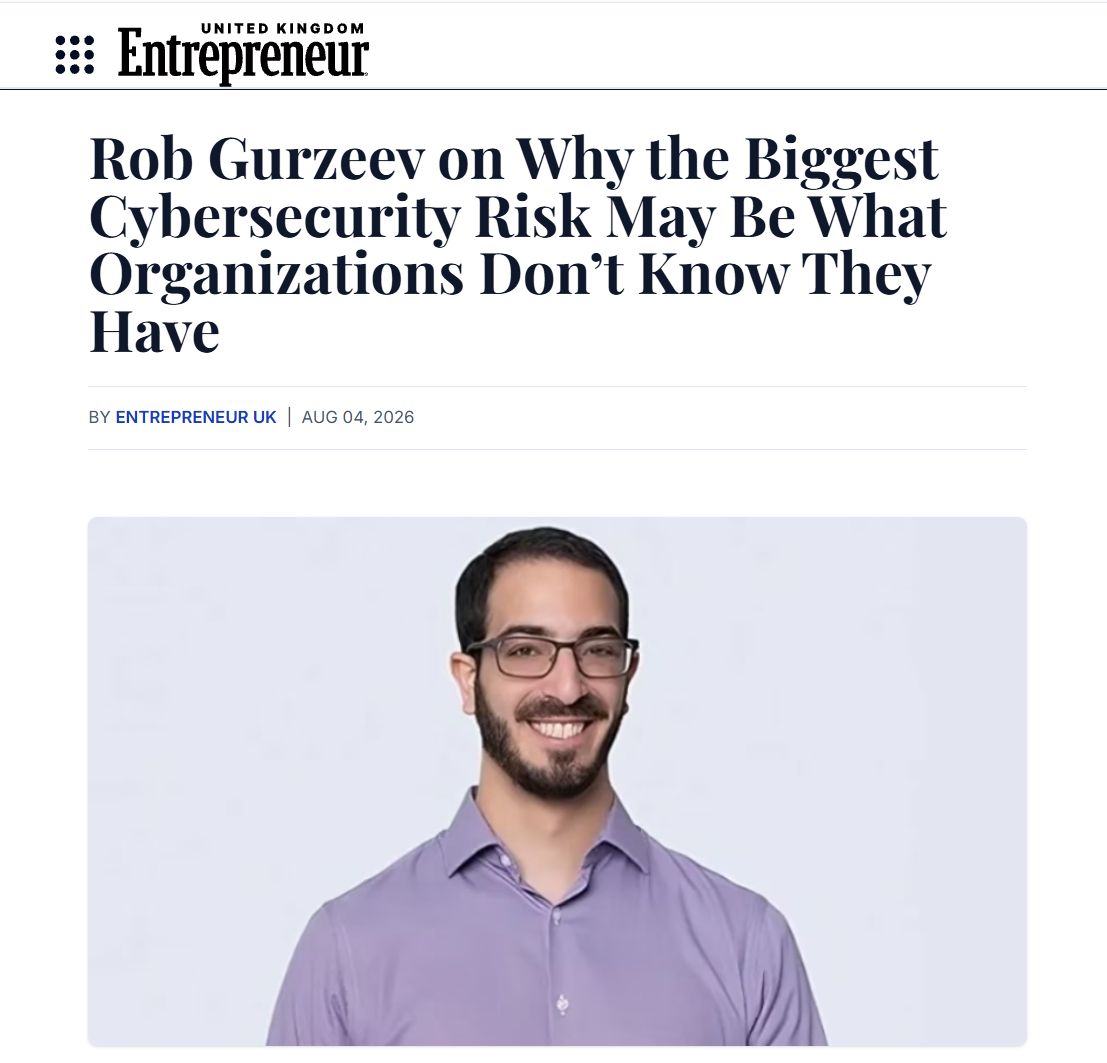
Big thanks to Entrepreneur Magazine for this conversation with our CEO Rob N. Gurzeev, about dark corners in which risk accumulates. Bottom line: the assets that were never on your list are the ones attackers get in through, and AI is creating more of them every day. Someone in finance can build an app with a prompt and put it on the internet. AI-written code reaches production without passing the secure pipelines built for human developers. Neither one arrives looking like a vulnerability with a patch, so neither one gets flagged. As Rob put it: "Guarding the front door while you leave the windows open is not a strategy." Read here to learn more: https://lnkd.in/dRhwqiz5
- Centro Nacional de Cibersegurança (CNCS) - Portuguese National Cybersecurity CentreSince 15 Sept 2026
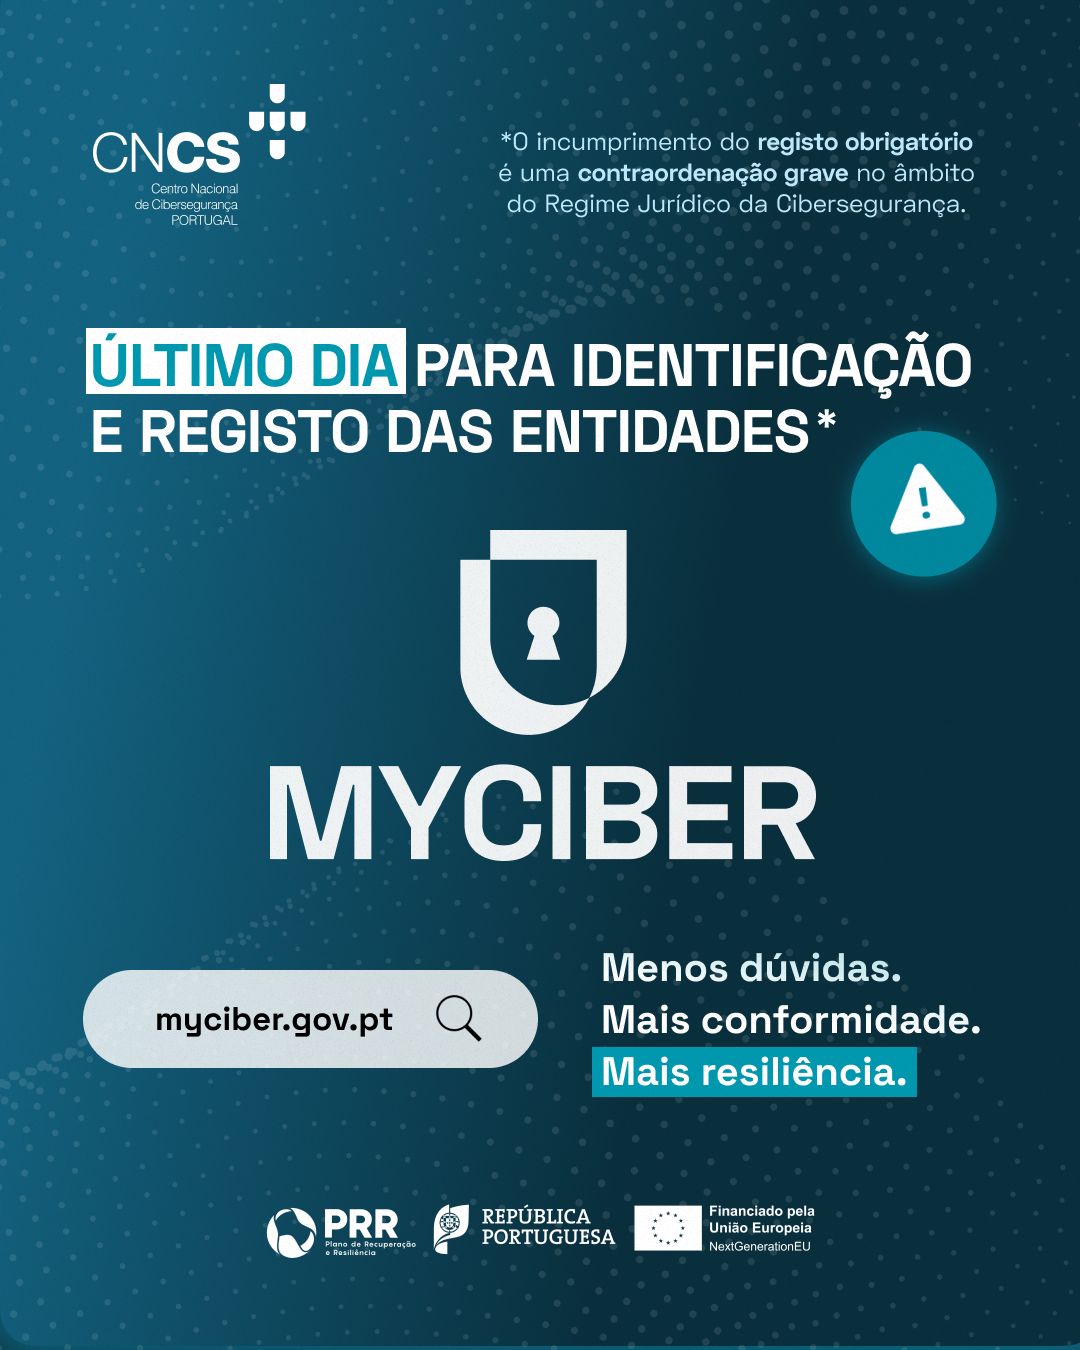
⏳ Termina hoje o prazo para autoidentificação e registo na plataforma MyCiber As entidades abrangidas pelo artigo 3.º do Regime Jurídico da Cibersegurança devem cumprir a obrigação de autoidentificação e registo na plataforma MyCiber até ao final do dia de hoje, 15 de setembro. Antes de concluir o processo: ✅ Verifique se a sua entidade está abrangida ✅ Identifique corretamente o setor de atividade da entidade para efeitos de enquadramento nos Anexos I e II do Regime Jurídico da Cibersegurança ✅ Complete o registo e a autoidentificação ✅ Conheça as obrigações que lhe são aplicáveis 👉 https://myciber.gov.pt/ ⚠️ A autoidentificação e o registo constituem uma obrigação legal das entidades abrangidas pelo Regime Jurídico da Cibersegurança. 📌 Recorde-se igualmente que, com a publicação do Regulamento do Regime Jurídico da Cibersegurança, iniciou-se a contagem do prazo legal de 24 meses para a implementação das medidas de cibersegurança aplicáveis e para a produção de efeitos das obrigações associadas às entidades abrangidas. 🔗 Saiba mais: https://lnkd.in/eusgte24 Cumprir começa pela identificação. 🔐 A identificação e o registo são apenas o início de um caminho para uma maior resiliência e maturidade em cibersegurança. #MyCiber #NIS2 #RecuperarPortugal #ConstruirOFuturo #PRR
- CleafySince 17 Sept 2026
76% of teams say AI-enabled fraud is outrunning their ability to respond. Yours doesn't have to. Our new report maps the architecture that takes fraud operations from fragmented signals to governed, autonomous action.
- CleafySince 17 Sept 2026
El 76% de los equipos afirma que el fraude impulsado por IA está superando su capacidad de respuesta. El tuyo no tiene por qué. Nuestro nuevo informe traza la arquitectura que lleva las operaciones de fraude de señales fragmentadas a una acción autónoma y gobernada.
- ESET Česká republikaSince 17 Sept 2026
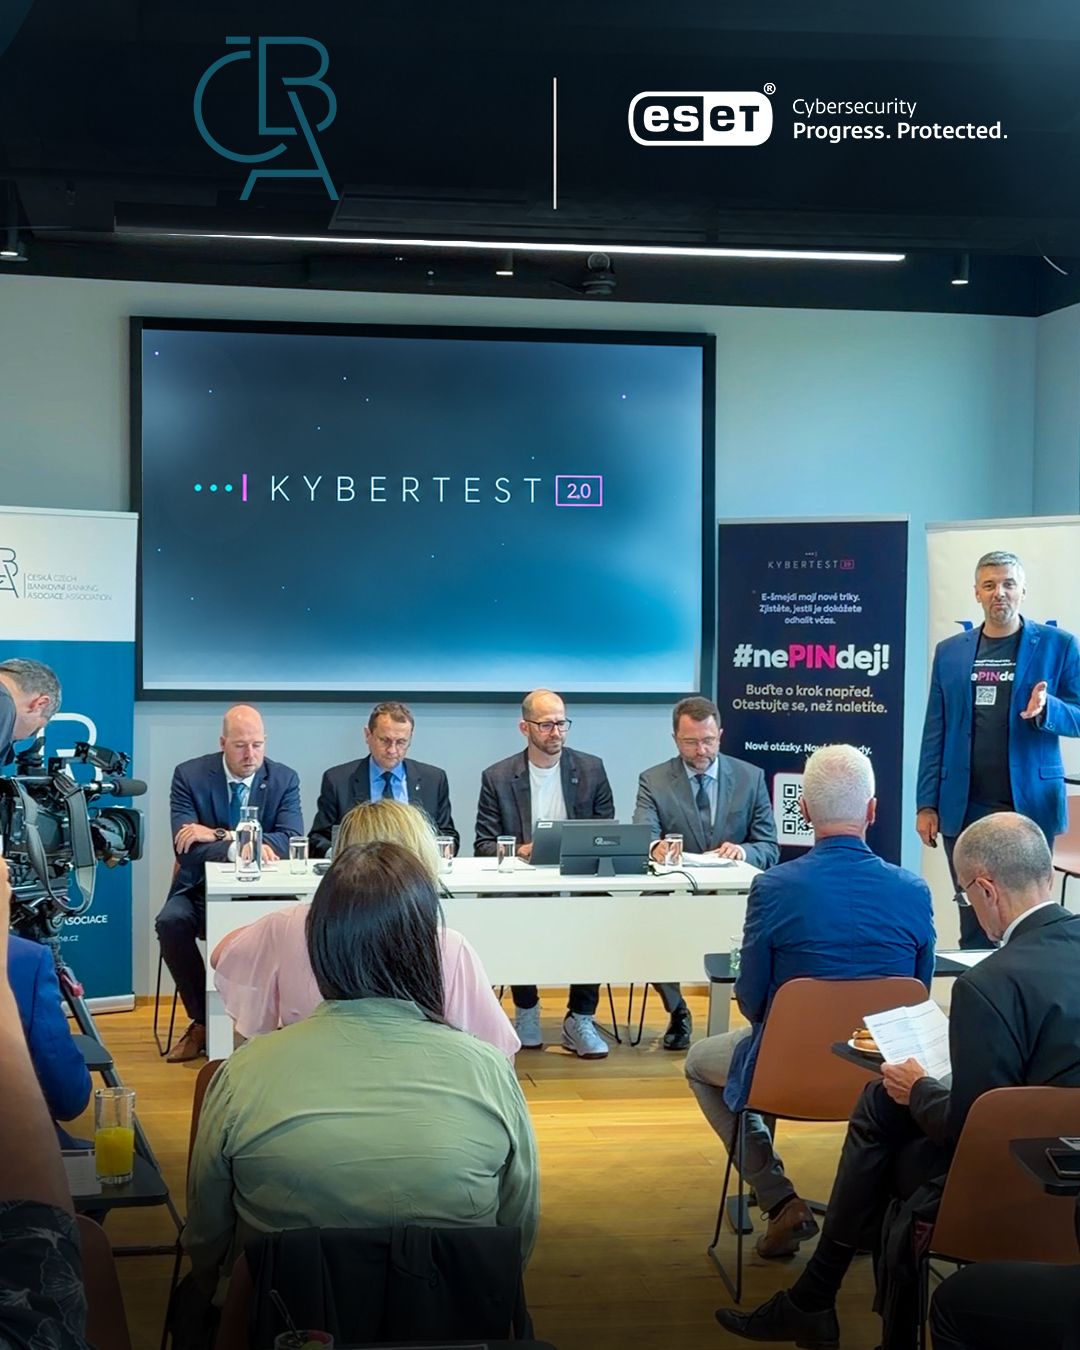
🤝 Spojujeme síly s Českou bankovní asociací. Stali jsme se technologickým partnerem České bankovní asociace a součástí kyberkampaně #nePINdej!. Společně chceme pomáhat lidem lépe rozpoznat online podvody a posilovat důvěru v digitální svět. Naši odborníci se zapojí do vzdělávacích aktivit, sdílení zkušeností i tvorby obsahu založeného na reálných hrozbách. Protože bezpečnější internet začíná informovanými uživateli. #ESET #nePINdej #Kyberbezpecnost
- Dragos, Inc.Since 26 Sept 2026
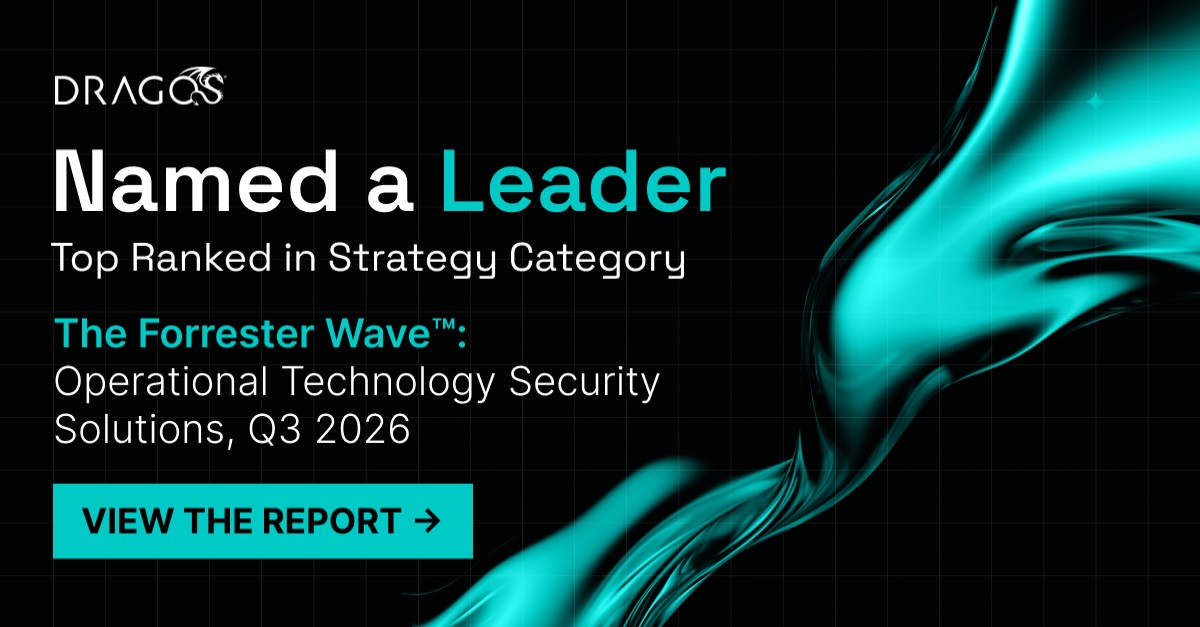
Your equipment will run for decades. Your OT security strategy should too. That means protecting what's running today while preparing for how your OT environment will evolve. Forrester ranked Dragos highest in Strategy, and Dragos was the only vendor to score a 5/5 in Vision. See Forrester's full assessment.
- BugHuntRecorded 8 Oct 2026
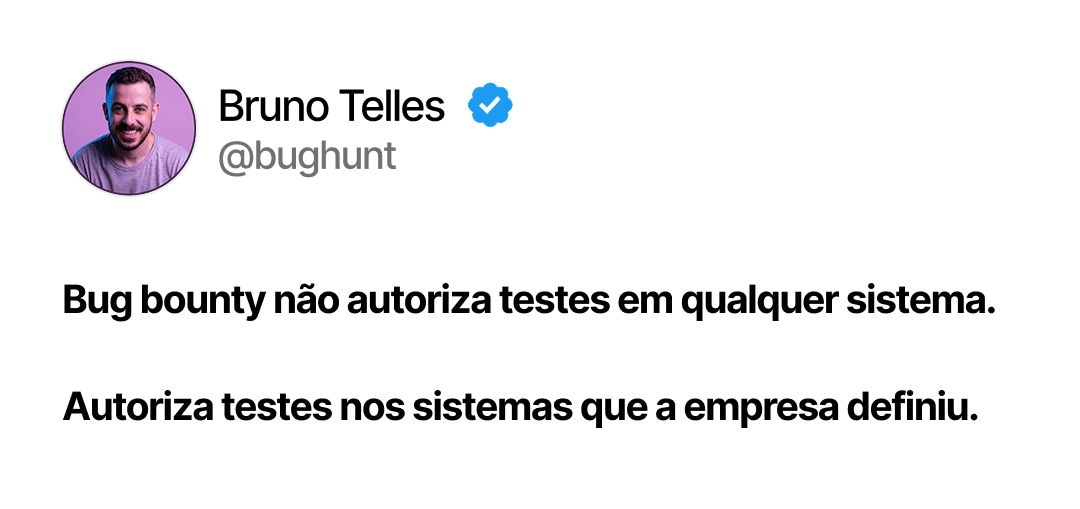
Uma das primeiras perguntas feitas durante a análise de um programa de bug bounty é: “Estamos autorizando terceiros a testar os sistemas da empresa?” A resposta é: não de forma ampla ou irrestrita. Um programa bem estruturado estabelece uma autorização específica e delimitada. Ele define: > Quais sistemas podem ser testados; > Quais atividades são permitidas; > Quais técnicas são proibidas; > Durante qual período as regras são válidas; > Como uma vulnerabilidade deve ser reportada. O pesquisador que segue essas regras atua dentro dos limites expressamente definidos pelo programa. Já qualquer atividade fora desse escopo não está autorizada e deve ser tratada conforme as regras do programa, os instrumentos contratuais e a legislação aplicável. Essa distinção é essencial. O programa não elimina limites. Ele os torna mais claros. Quando isso fica bem compreendido, a conversa deixa de ser sobre uma autorização genérica e passa a tratar de uma questão mais concreta: > Como definir um escopo seguro, controlado e adequado à realidade da empresa? É justamente essa clareza que transforma uma iniciativa de segurança em um processo de governança.
- ESET Česká republikaSince 17 Sept 2026
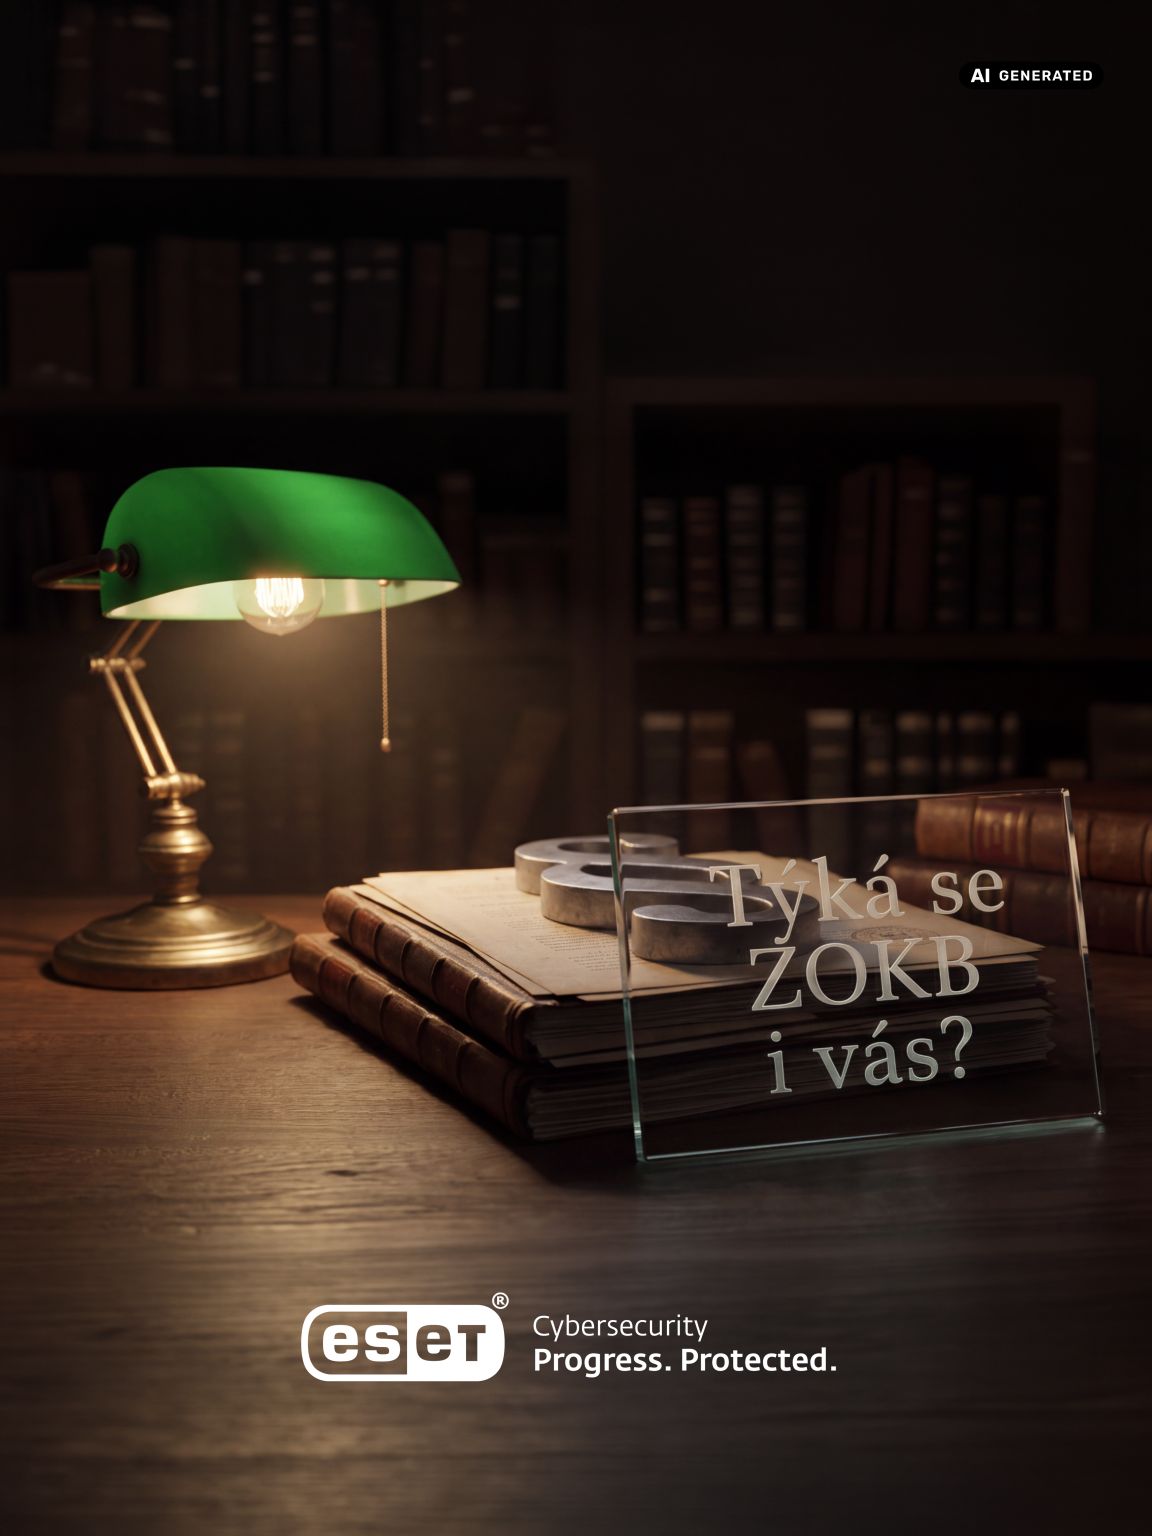
„To je pro velké korporáty, ne pro nás.“ Přesně tahle věta stojí za tím, proč řada českých firem zjistí, že spadá pod ZoKB, až na poslední chvíli. 🧐 Nový zákon o kybernetické bezpečnosti se může týkat i středních firem z oborů, které regulaci dosud neřešily. Příprava navíc není otázkou týdne – je potřeba zjistit, zda pod zákon spadáte, zmapovat povinnosti a připravit potřebná opatření. 🛡️ Dobrá zpráva? Máme pro vás praktického průvodce novým ZoKB, který si můžete zdarma stáhnout. Zjistíte v něm, koho se zákon týká, jaké povinnosti přináší a co budete muset řešit. 📘 Stáhněte si příručku zdarma: https://lnkd.in/dMgyT-iz
- BugHuntRecorded 8 Oct 2026
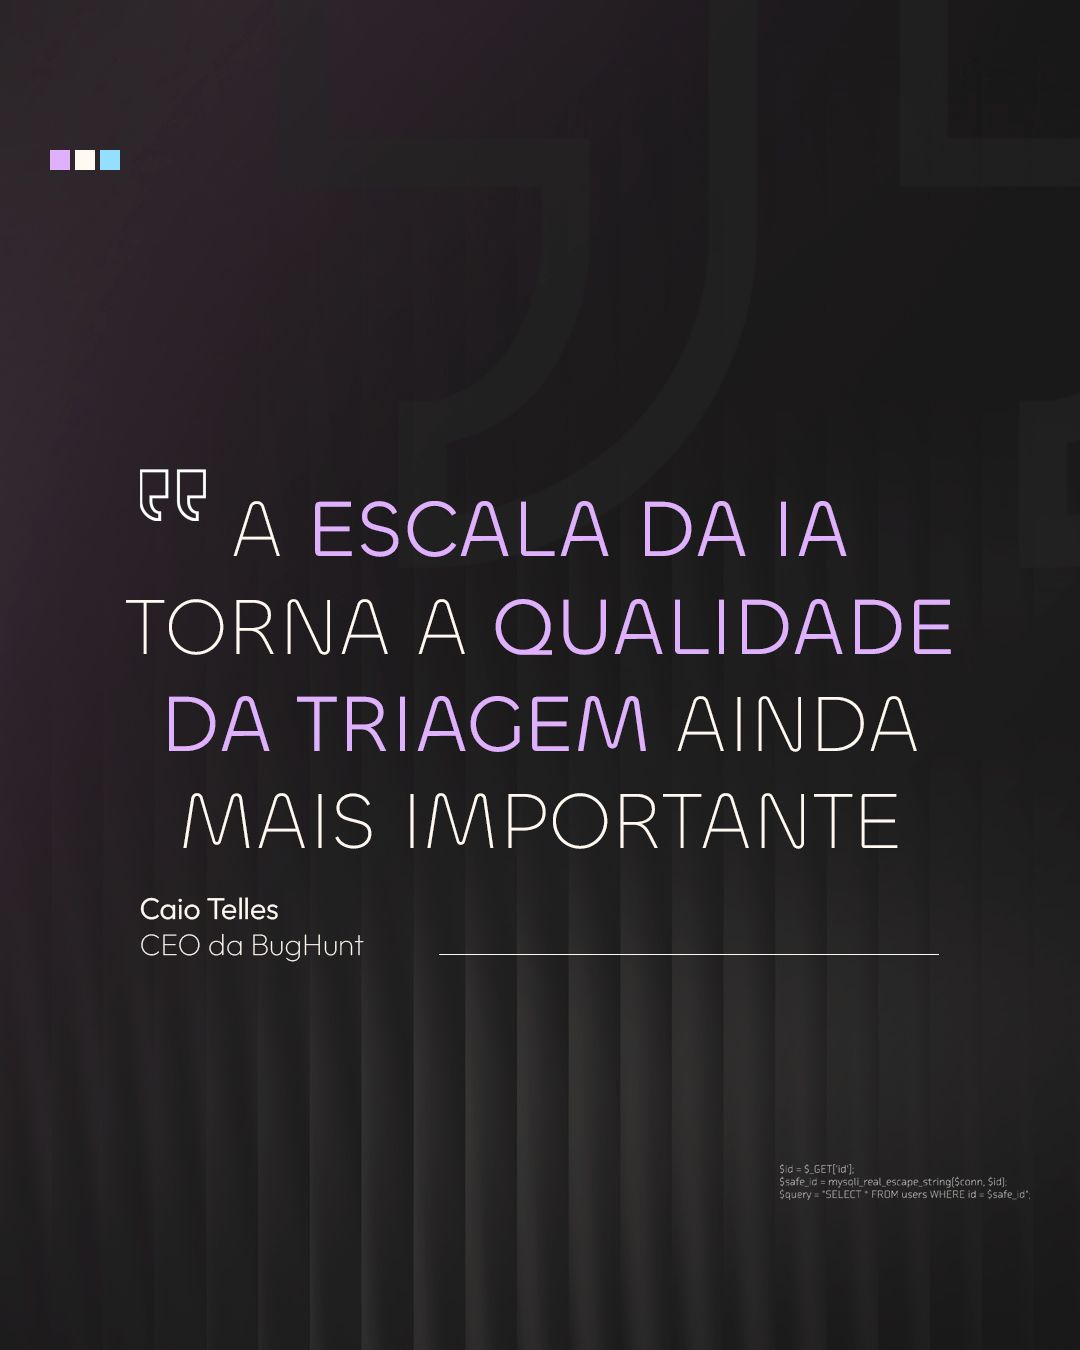
A IA aumentou muito a capacidade de identificar possíveis vulnerabilidades. E isso já está aparecendo nos programas de bug bounty. O problema é que identificar um comportamento suspeito não significa necessariamente ter encontrado uma vulnerabilidade. Tenho visto reports construídos a partir do output de uma ferramenta, mas sem validação suficiente do pesquisador. A ferramenta aponta um comportamento, gera uma hipótese e, às vezes, até ajuda a estruturar o report. Mas alguém ainda precisa entender o que está acontecendo, reproduzir o cenário, validar o impacto e explicar o problema com clareza. Quando essa etapa não acontece, o volume aumenta, mas a qualidade não acompanha. E isso fica evidente na triagem. Para mim, esse será um dos efeitos mais importantes da IA no bug bounty: quanto mais fácil ficar identificar possíveis falhas, mais importante será saber separar sinal de ruído. Não vejo a IA como um problema. Pelo contrário, ela já é uma ferramenta muito poderosa para pesquisa. Mas a validação continua sendo papel do pesquisador. A IA pode acelerar a descoberta. Entender se aquilo realmente é uma vulnerabilidade ainda exige conhecimento.
- CryptomathicSince 17 Sept 2026
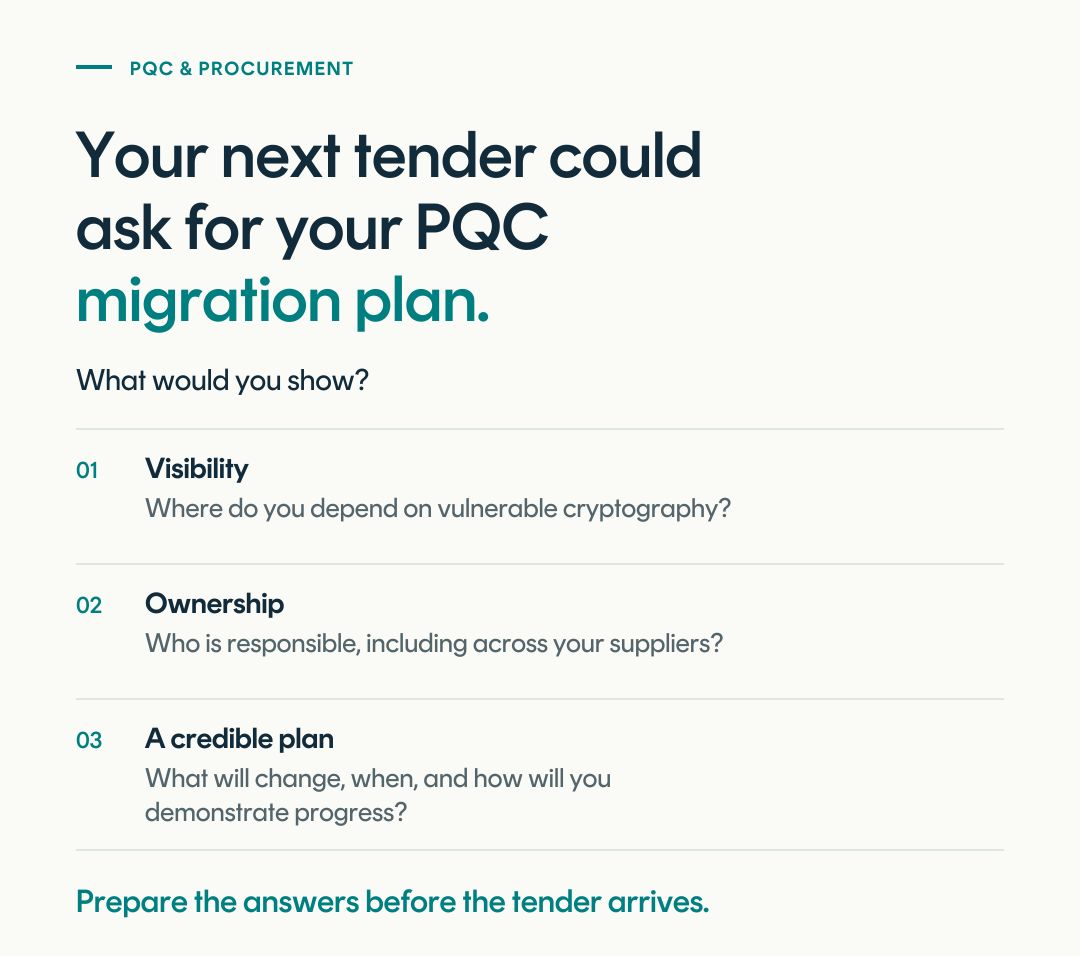
Your next customer security assessment could ask for your post-quantum migration plan. What would you show them? The G7 Cybersecurity Working Group has called for organisations across sectors to begin their transition to post-quantum cryptography as soon as possible. Its recommendations include incorporating PQC requirements into public procurement. This is policy guidance, not a binding mandate. But it gives suppliers a reason to prepare: customer requirements could arrive before a direct regulatory obligation does. As buyers assess their own readiness, they will need answers from the companies they depend on: • Where does your product or service rely on vulnerable cryptography? • Which changes depend on your suppliers? • Who owns the migration, and what is the plan? • What evidence of progress can you provide? Those answers take time to assemble, particularly when cryptography is spread across applications, infrastructure and third-party services. For anyone building the internal case to get started, procurement adds a commercial consideration. A credible migration plan could become part of what customers expect when deciding who to buy from. Read the G7 call to action in the comments.
- CyberVadisSince 18 Sept 2026
Do you need to cost-reduce and improve your due diligence on your third-parties? Let us, CyberVadis, help you to better manage your risk of your evolving third-party environment, comply with regulatory requirements and remove your supplier due-diligence burden. https://lnkd.in/eB8wfr3t (Contact CyberVadis, request a demo) https://lnkd.in/e8zfYh8r (AWS Security Blog)
- GarancySince 22 Sept 2026
Kompromisslose Sicherheit – made in Europe. Steuern Sie Identitäten, Rollen und Berechtigungen souverän mit Identity Management von Garancy.
- GarancySince 22 Sept 2026
Wie lückenlos ist Ihre IT geschützt? Steuern Sie Identitäten, Rollen und Berechtigungen mit Identity Management nach strengen EU-Richtlinien!
- Dragos, Inc.Since 26 Sept 2026
Comparing OT security vendors? Forrester just named Dragos a Leader, ranked highest in Strategy, the only vendor to score a 5/5 in Vision. Dragos earned the highest possible score across all eight Forrester criteria, from product capabilities to services and community, so you're not betting on a platform that plateaus. Read Forrester's full assessment of Dragos.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.