On air · 2 of 3 networks
Cryptomathic
- cryptomathic.com
- Cybersecurity
- DK
- 101 employees
Cryptomathic’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 183. Watch Cryptomathic with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 5 | Checked 30 Oct 2026 | See all 183 ads → | ||
| Meta | Not checked | — | |||
| Running | 4 | Ads on the Google Ads Transparency Center | Checked 26 Oct 2026 | Collect them with the API → |
Cryptomathic has 5 live LinkedIn ads. We recorded 4 Google ads on 26 Oct 2026.
Latest ads
- LINKEDIN · VIDEOSince 6 Oct 2026
You can’t migrate cryptography you can’t see. Without visibility and ownership, every cryptographic change becomes slower, harder and riskier. In this clip, Glen Leonhard explains why crypto-agility starts with bringing unmanaged cryptography under control. Watch the full Cryptomathic and Solid8 Technologies Pty Ltd - South Africa webinar: https://lnkd.in/eMXbSTpi #cryptoagility #cryptography #PQC
- LINKEDIN · VIDEOSince 30 Sept 2026
A question for my network: is AI alone enough to create a CBOM you can actually trust? I'm interested to hear how others are approaching it. Where does AI add real value, and where is human oversight still essential?
- LINKEDIN · VIDEOSince 29 Sept 2026
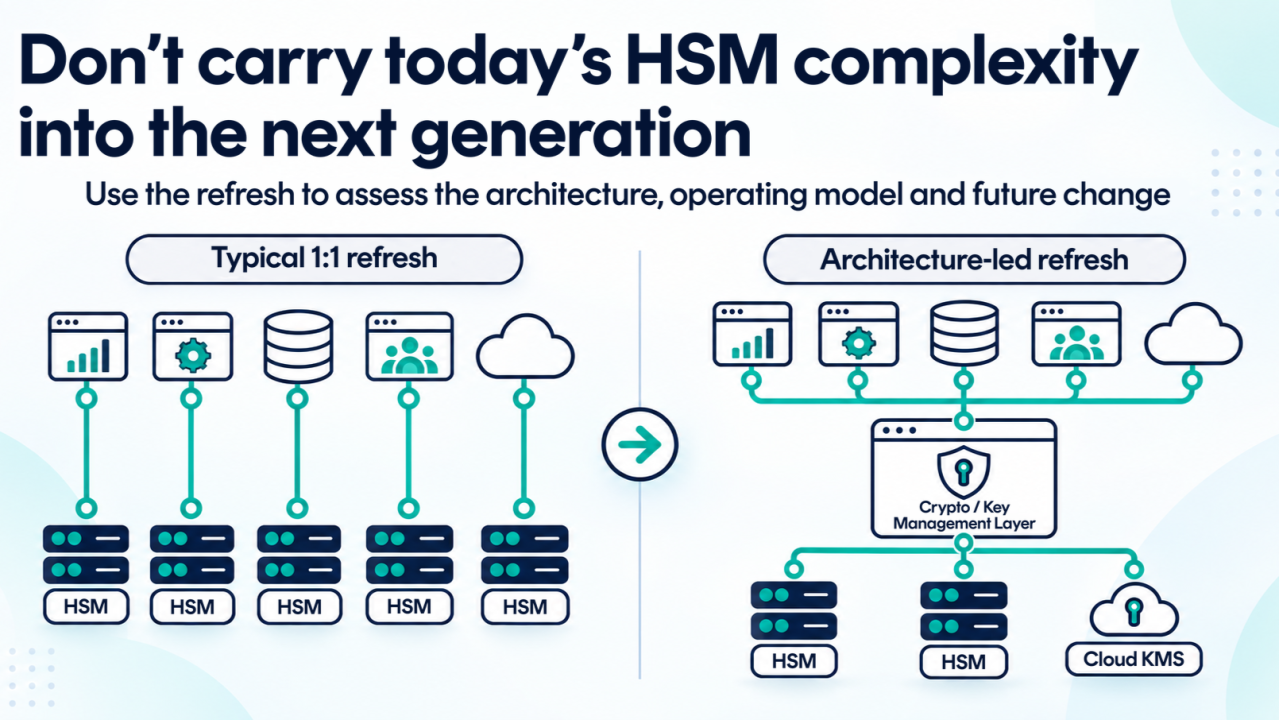
Before you replace your HSM estate one-for-one, ask whether you want to carry the same architecture into the next generation. A like-for-like replacement may be right. But before the plan is fixed, I’d ask three questions. 1. What genuinely needs dedicated HSM infrastructure? 2. Which cryptographic services could be shared? 3. And how much application work will the next hardware change require? Some separation is essential for resilience, isolation or performance. That needs to stay. The opportunity is to identify duplication and repeated integration work that could be reduced through shared cryptographic services. That’s the comparison I’d make before committing to the next hardware investment. I’ve written an article on what to assess, and where CK360 could fit. You’ll find it alongside this video in the comments.
- LINKEDIN · ARTICLESince 23 Sept 2026
An HSM refresh is usually treated as a hardware decision. But before replacing the current estate 1:1, it is worth asking a broader question: How much of the current cryptographic architecture should we actually carry into the next generation? For banks with complex hardware security module estates, the refresh can be an opportunity to review infrastructure, integration patterns and the operating model around cryptographic services, not just the next appliance. I wrote a short article on what I think is worth assessing before the replacement plan is fixed, and where a shared cryptographic control layer should fit into that discussion. #Cryptography #HSM #KeyManagement #BankingSecurity #CryptoAgility
- LINKEDIN · IMAGESince 17 Sept 2026
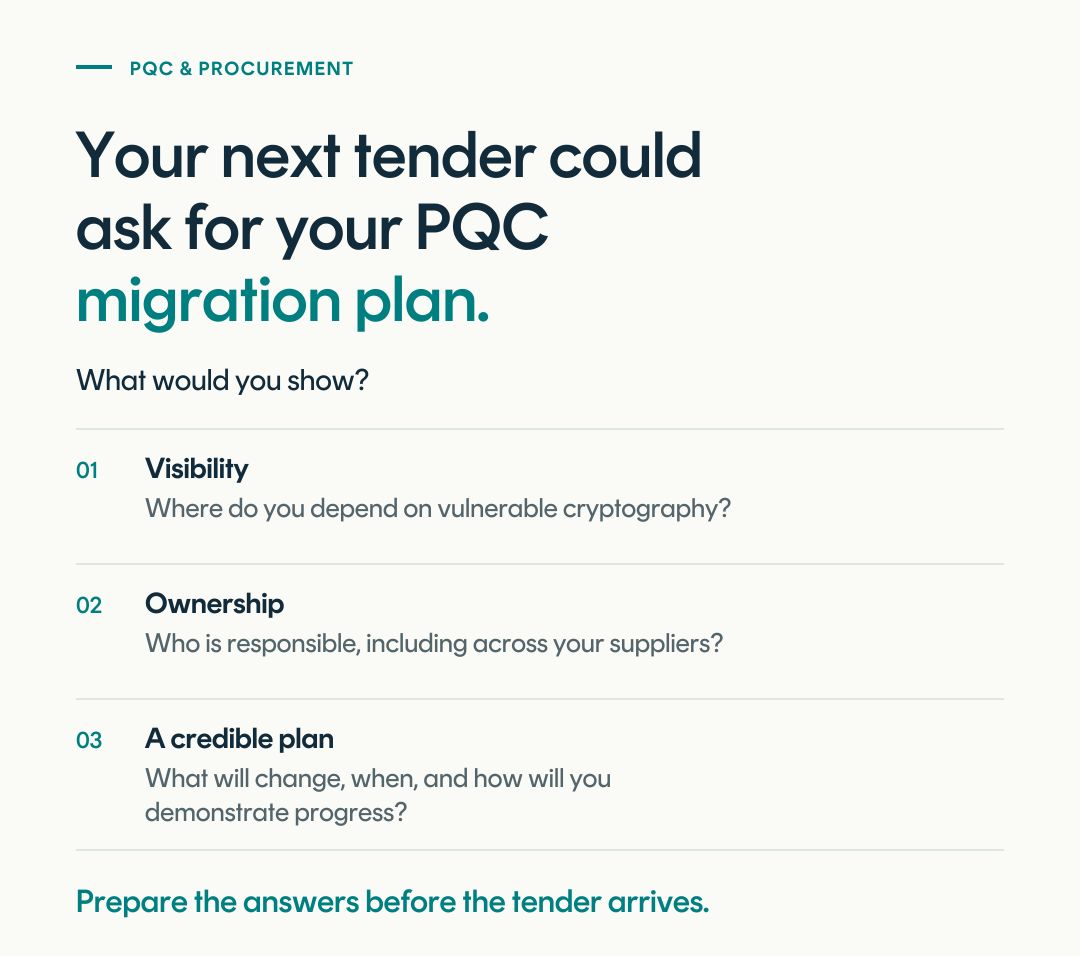
Your next customer security assessment could ask for your post-quantum migration plan. What would you show them? The G7 Cybersecurity Working Group has called for organisations across sectors to begin their transition to post-quantum cryptography as soon as possible. Its recommendations include incorporating PQC requirements into public procurement. This is policy guidance, not a binding mandate. But it gives suppliers a reason to prepare: customer requirements could arrive before a direct regulatory obligation does. As buyers assess their own readiness, they will need answers from the companies they depend on: • Where does your product or service rely on vulnerable cryptography? • Which changes depend on your suppliers? • Who owns the migration, and what is the plan? • What evidence of progress can you provide? Those answers take time to assemble, particularly when cryptography is spread across applications, infrastructure and third-party services. For anyone building the internal case to get started, procurement adds a commercial consideration. A credible migration plan could become part of what customers expect when deciding who to buy from. Read the G7 call to action in the comments.
- LINKEDIN · ARTICLESince 17 Sept 2026
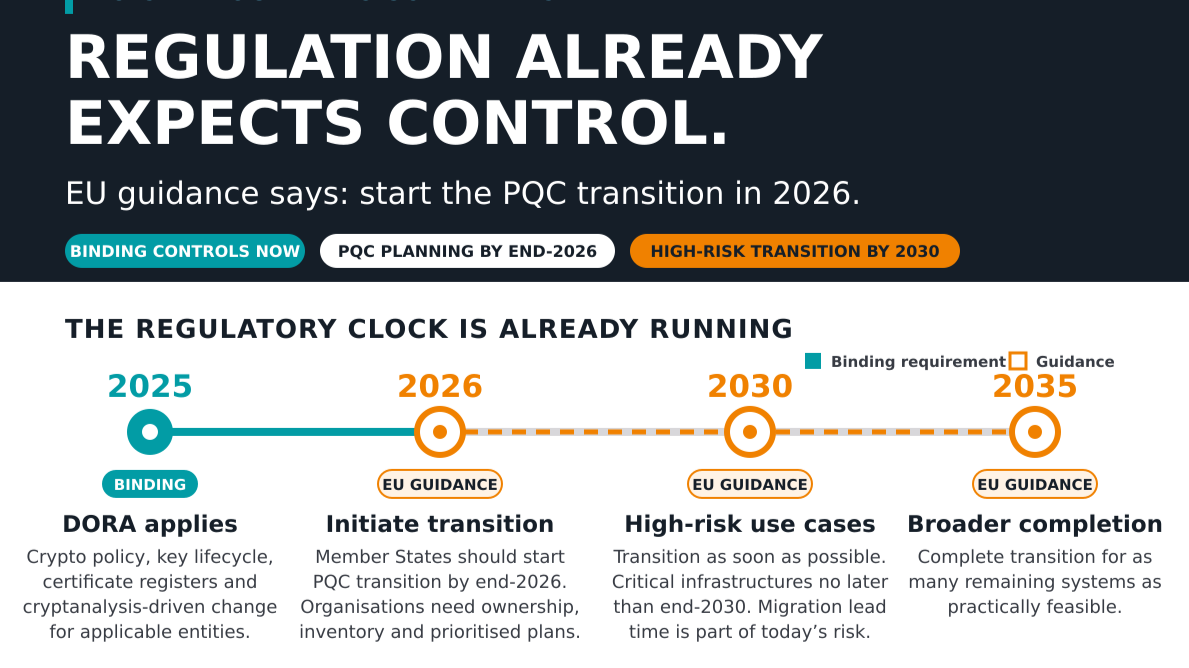
In this article https://lnkd.in/epmFkHTH I navigate the implicit and explicit cryptography and PQC requirements derived from EU regulation, DORA and NIS2 DORA and NIS2 do not mandate a particular PQC algorithm or technology platform. But they establish clear expectations around cryptographic policy, key lifecycle management, asset visibility, accountability, periodic review and the ability to respond to technological change. That means organisations should already be able to show: → where cryptography is used → who owns it → which critical services depend on it → how keys and certificates are controlled → how vulnerable technology can be replaced safely Cryptographic control (and PQC migration) is a present governance, evidence and operational-control challenge. Cryptomathic is fully positionned to address the cryptographic control challenge. #DORA #NIS2 #PQC #CryptoAgility #Cryptography #RiskManagement #Compliance Sudeep Venkatesh Anthony Da Ponte Laurent Leloup René Martin Guillaume Petipas Rob Purcell Herve M.
6 of 183 adsSign up to see every Cryptomathic ad, filter by format and date, and get alerts on new ones.
See all 183 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.