B2B ad examples
2 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- CleafySince 17 Sept 2026
61% of teams have ignored an alert that turned out to be a real attack. This happened not from carelessness, but from working with fragments while the attacker sees the whole operation. Our new report breaks down why fragmented signals miss coordinated fraud, and what a connected view changes.
- CleafySince 17 Sept 2026
Una campaña de fraude ataca hoy miles de cuentas. Las operaciones antifraude siguen caso a caso. Nyx cierra esa brecha: lleva las operaciones antifraude de la investigación, caso por caso, a la respuesta a nivel de campaña. Operaciones antifraude autónomas: ya en producción en bancos Tier 1 europeos.
- BugHuntRecorded 8 Oct 2026
Uma vulnerabilidade pode ser encontrada antes de a empresa estar preparada para receber esse tipo de report. O pesquisador tenta avisar, mas não encontra um canal claro. A mensagem chega por e-mail, formulário, LinkedIn ou até por alguém de outra área. A partir daí, começa uma corrida interna para entender quem deve assumir, quem valida a falha, quando o jurídico entra e como manter a comunicação com quem fez o report. Recentemente, olhando como o Google estrutura esse processo, um ponto me chamou atenção: os reports de segurança passam por um canal próprio e seguem para triagem e avaliação técnica. Parece simples, mas ajuda a organizar justamente o que costuma virar improviso em muitas empresas. Ou seja, muitas vezes existe disposição para colaborar. O que falta é a empresa ter um processo capaz de receber essa colaboração e conduzir o que vem depois. Não ter um fluxo estruturado não impede que alguém encontre uma falha. Só deixa a empresa mais exposta à improvisação justamente no momento em que precisa responder com mais rapidez e segurança. Se um pesquisador tentasse reportar uma vulnerabilidade crítica para a sua empresa hoje, ele saberia por onde começar?
- GarancySince 22 Sept 2026
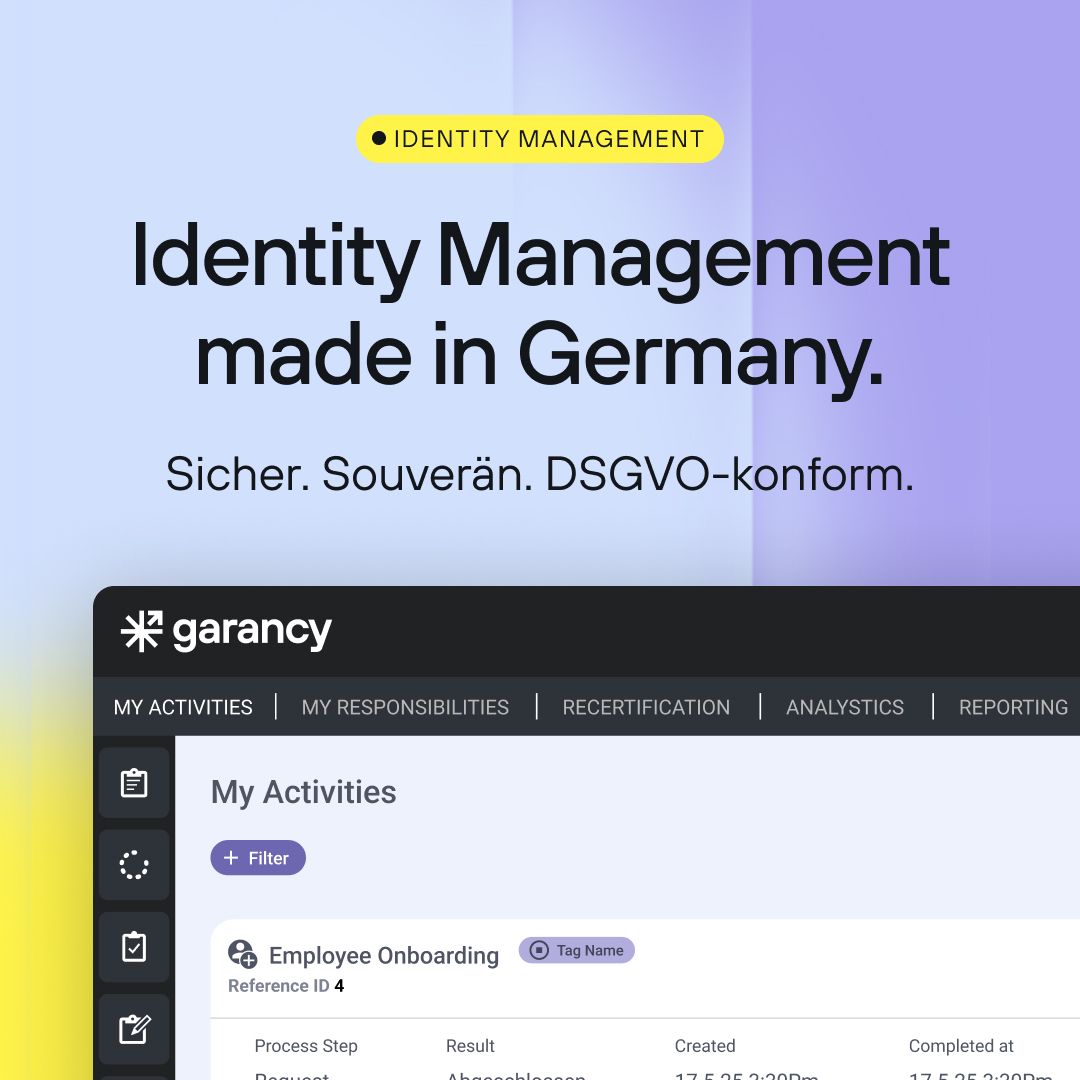
Kompromisslose Sicherheit aus Deutschland. Steuern Sie Identitäten, Rollen und Berechtigungen mit der Identity-Management-Software von Garancy.
- GarancySince 22 Sept 2026
Identity-Management-Software aus Deutschland. Steuern Sie Identitäten, Rollen und Berechtigungen souverän – für Sicherheit ohne Hintertüren.
- Beazley SecuritySince 23 Sept 2026
EM Protect continuously uncovers and tracks changes across your attack surface, including external-facing assets, cloud, third-party, and digital ecosystems, providing visibility into vulnerabilities in near-real time. Activate today to start maximizing your benefit.
- Beazley SecuritySince 23 Sept 2026
Beazley policyholders, activating EM Protect is as easy as 1, 2, 3... Get started now to gain continous visbility into your external attack surface, helping you uncover risks before attackers do. This benefit is part of your cyber coverage. Activate now
- CyberVadisSince 22 Sept 2026
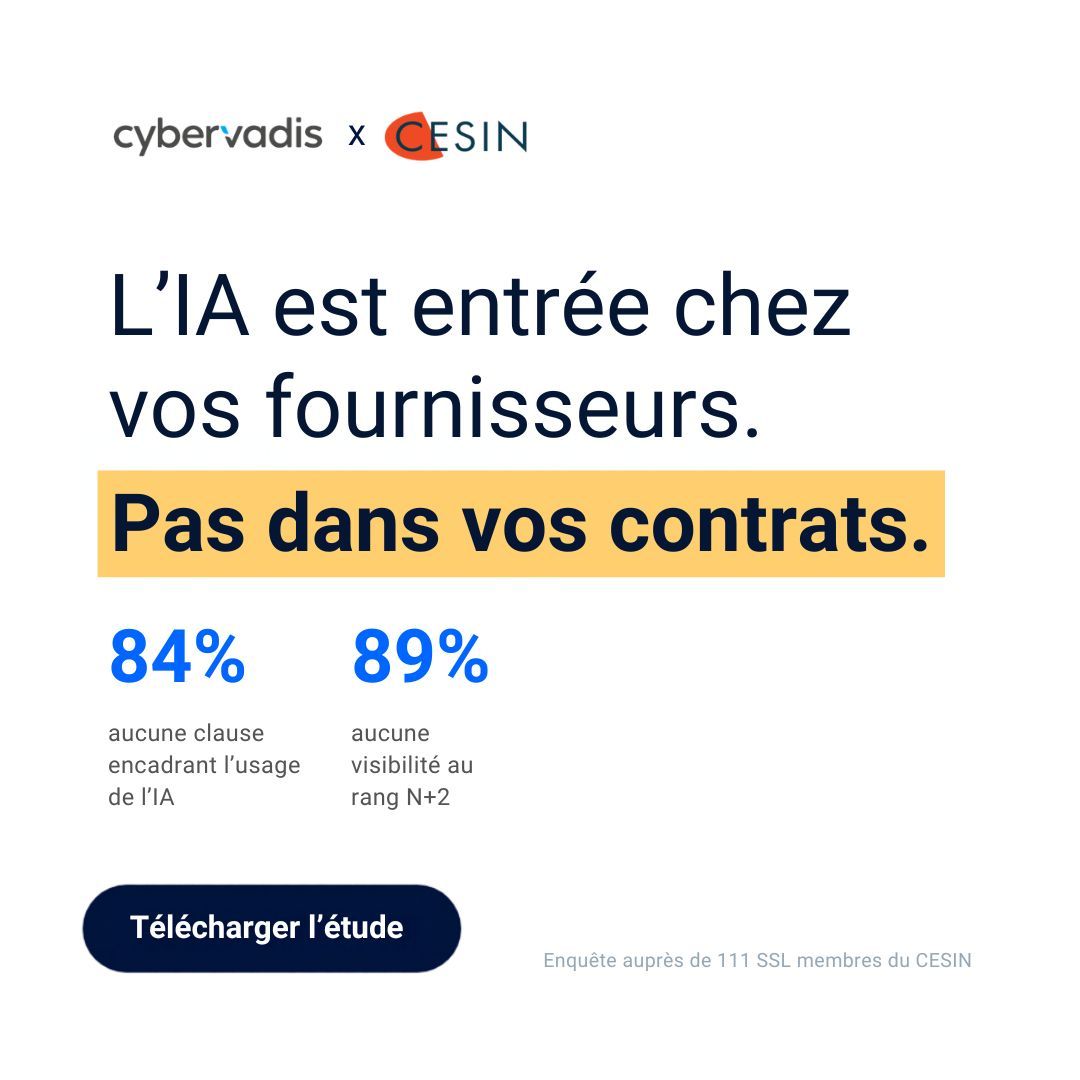
65 % de vos fournisseurs déclarent tenir un inventaire de leurs outils IA. 4 % peuvent le prouver. C'est le premier chiffre de l'étude que nous publions avec le CESIN. Il ne sort pas d'un sondage : 111 RSSI membres du CESIN d'un côté, 652 évaluations de fournisseurs vérifiées sur preuves documentaires dans 49 pays de l'autre. L'écart entre ce qui est déclaré et ce qui est démontrable, vous le connaissez déjà sur la sécurité classique. Sur l'IA il est bien pire, parce que personne n'a encore mis à jour ses questionnaires. Dans le détail : 83 % des RSSI n'ont pas couvert le risque IA de leurs tiers, 84 % n'ont aucune clause encadrant son usage, 89 % n'ont aucune visibilité au rang N+2. Le guide détaille les contrôles IA à ajouter à votre prochaine évaluation, les clauses à inscrire dans vos contrats, et par où commencer quand on part de zéro. Sans refondre votre dispositif. Téléchargez l'étude complète.
- Code Blue CyberRecorded 8 Oct 2026
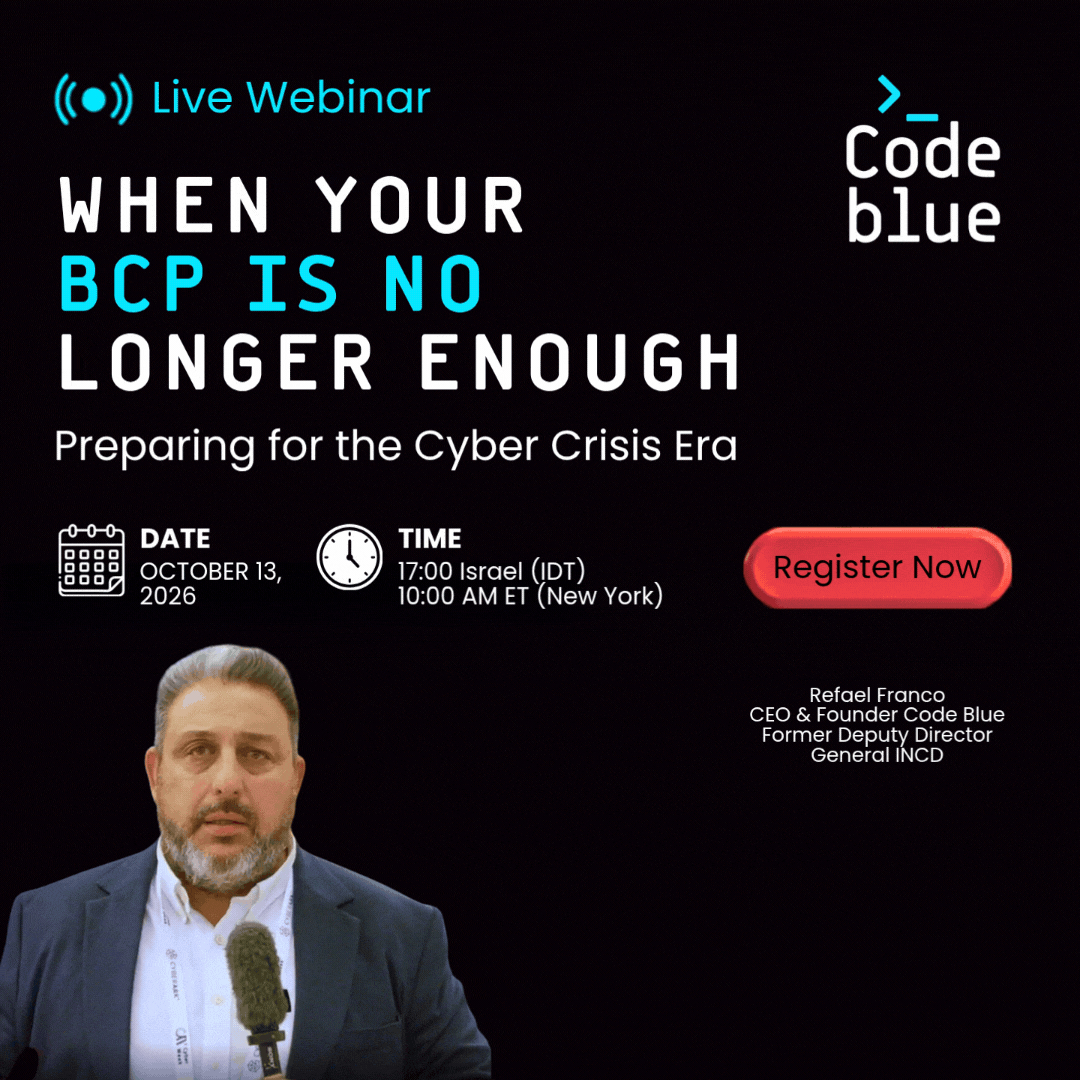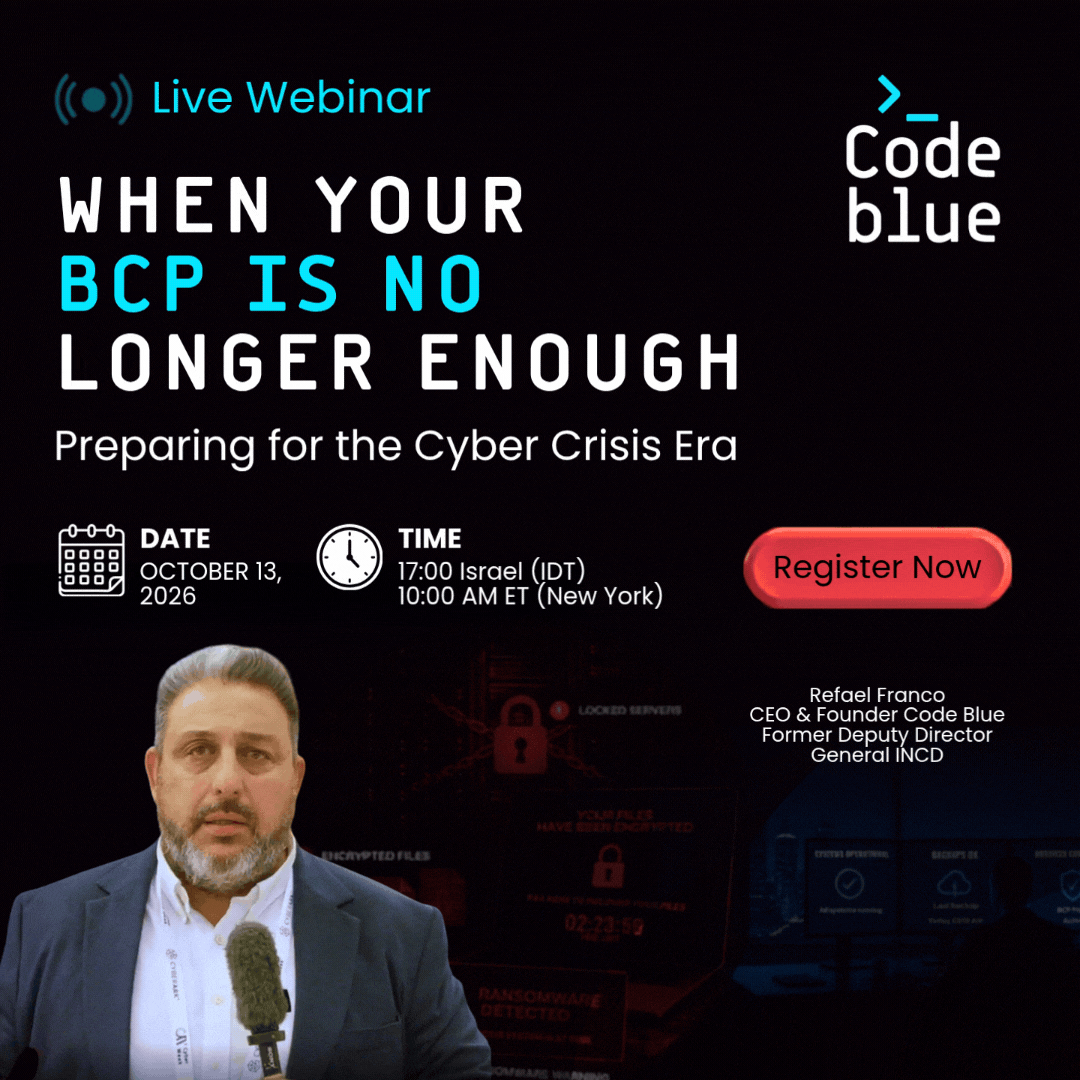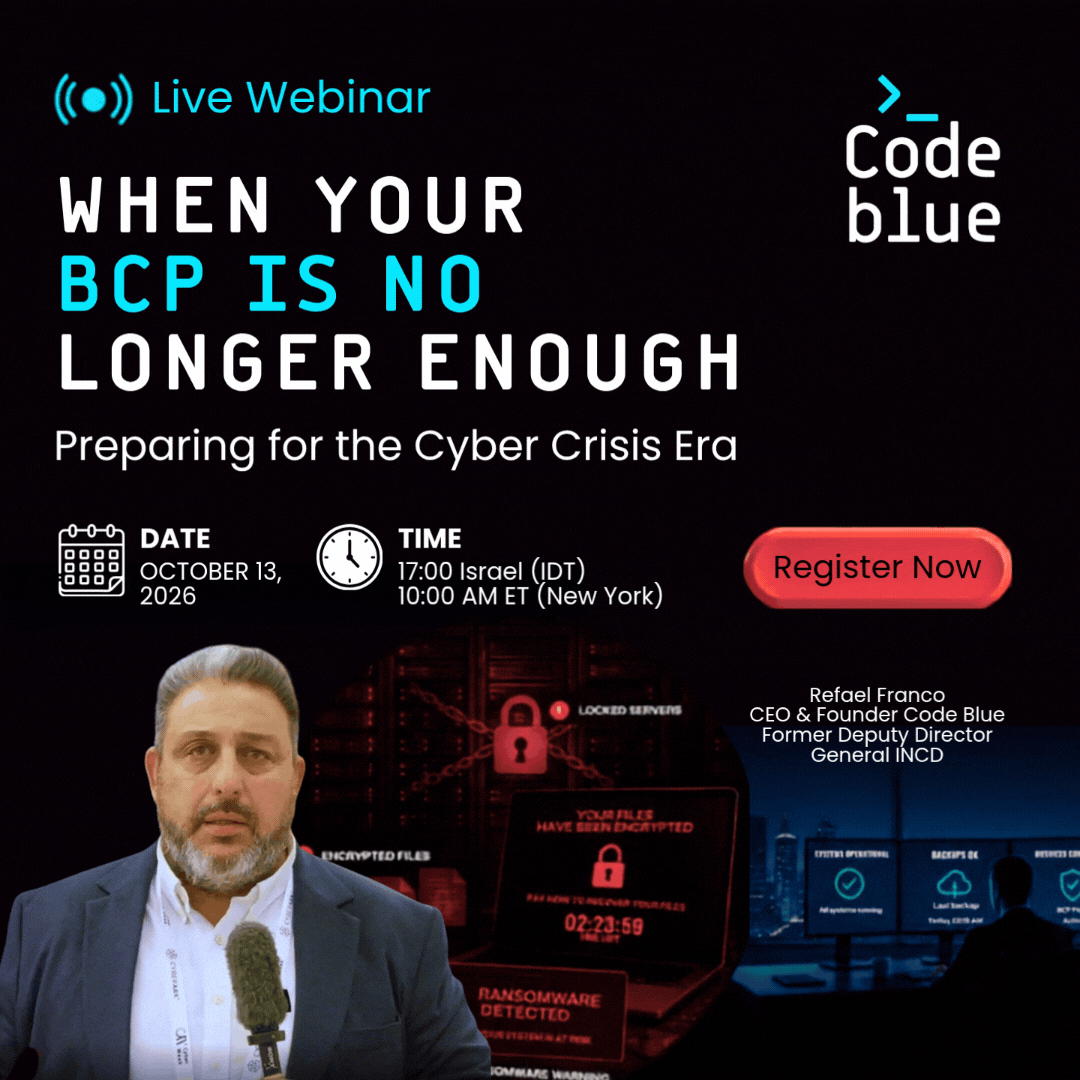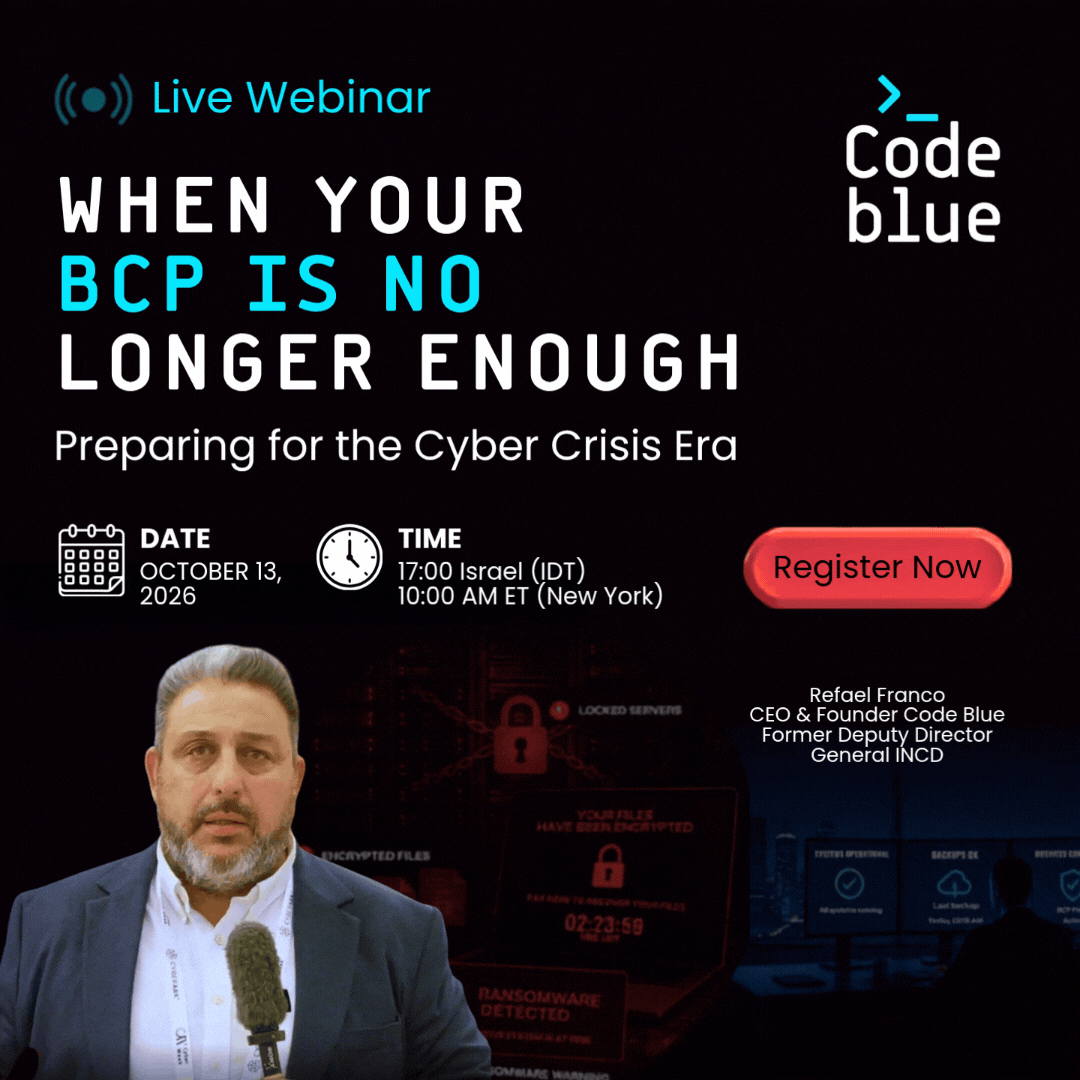
האם תוכנית ההמשכיות העסקית שלכם באמת מוכנה למציאות של משברי הסייבר של היום? תוכניות BCP מסורתיות לא נבנו להתמודד עם אירועי סייבר מתפתחים ודינמיים, שבהם כל החלטה עשויה להשפיע על הפעילות העסקית, המוניטין וקצב ההתאוששות של הארגון. הצטרפו לרפאל פרנקו, מנכ"ל ומייסד Code Blue ולשעבר המשנה לראש מערך הסייבר הלאומי, לוובינר ייחודי שבו נבחן כיצד ארגונים יכולים לעבור מתוכניות סטטיות למוכנות אמיתית לניהול משברי סייבר. במהלך המפגש נציג כיצד מערכת Blue Castle של קוד בלו מאפשרת לארגונים להיערך מראש, לנהל את המשבר בזמן אמת, ולשמור על שליטה תפעולית וקבלת החלטות אפקטיבית גם תחת לחץ
- CryptomathicSince 23 Sept 2026
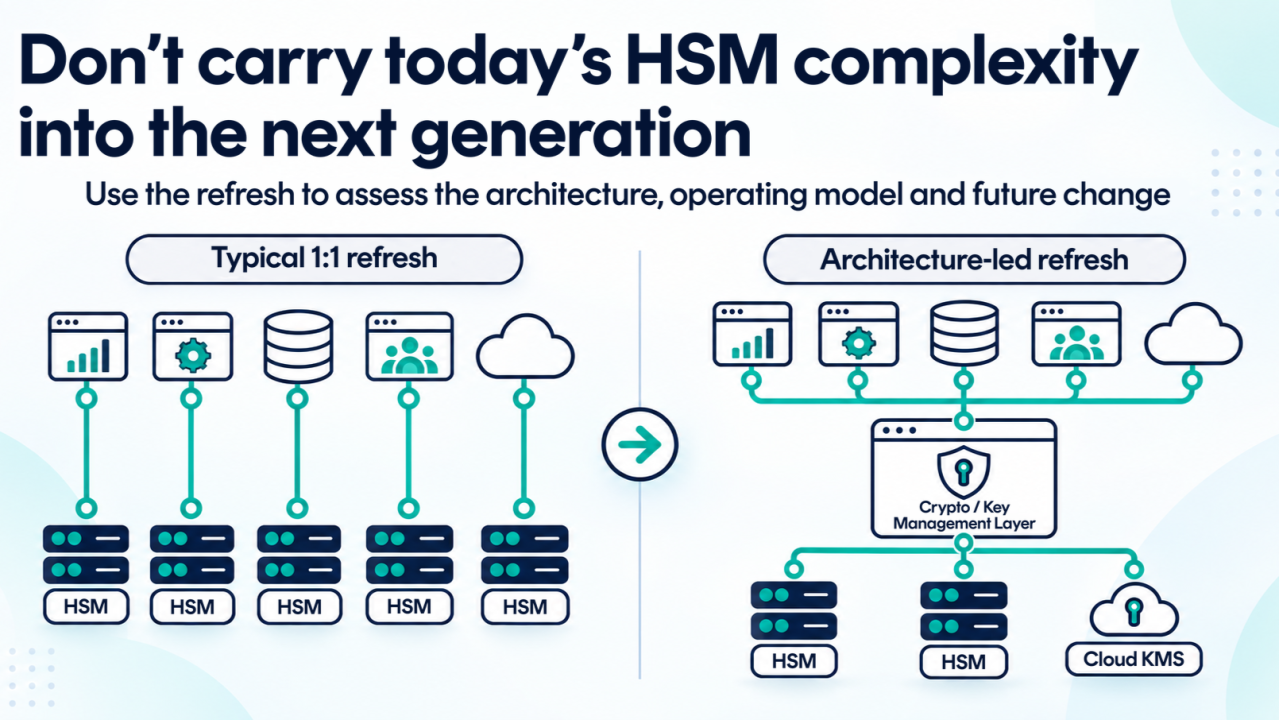
An HSM refresh is usually treated as a hardware decision. But before replacing the current estate 1:1, it is worth asking a broader question: How much of the current cryptographic architecture should we actually carry into the next generation? For banks with complex hardware security module estates, the refresh can be an opportunity to review infrastructure, integration patterns and the operating model around cryptographic services, not just the next appliance. I wrote a short article on what I think is worth assessing before the replacement plan is fixed, and where a shared cryptographic control layer should fit into that discussion. #Cryptography #HSM #KeyManagement #BankingSecurity #CryptoAgility
- Hiya Inc.Since 23 Sept 2026
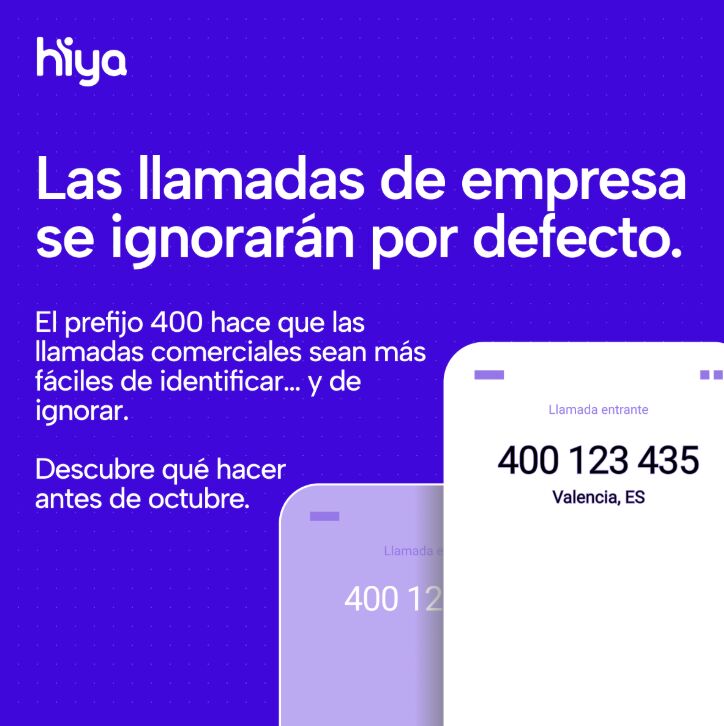
España está a punto de hacer que cualquier llamada comercial se reconozca al muestre como lo que es. Y no sé si muchas empresas se han parado a pensar de verdad qué les supone eso. Versión rápida: la nueva norma dice que las llamadas comerciales salientes tienen que usar un prefijo 400. En lo de cumplir, fácil. Cambias el prefijo y ya está. Pero piensa en quién está al otro lado. Aquí la gente ya filtra los números desconocidos por instinto. Ahora un montón de llamadas van a leerse como "alguien que me quiere vender algo" antes incluso de tener el móvil en la mano. En un país que ya ignora justo ese tipo de llamadas, ese prefijo no es algo neutro. Es una señal. Y apunta en tu contra. En octubre, los equipos que mantengan su tasa de respuesta van a ser los que vieron esto venir y lo trataron como un problema de confianza, y no como una casilla que marcar. Un prefijo dice qué tipo de llamada es. No dice nada de quién eres tú ni de por qué querrían hablar contigo. Hiya Branded Call rellena justo ese hueco. Tu nombre, en pantalla antes de que decidan. Eso sí le da a alguien un motivo real para descolgar. El cambio llega igual. Así que mejor llegar preparado 👇 https://lnkd.in/demt5HRm
- Code Blue CyberRecorded 8 Oct 2026
At Ready for Tomorrow, Eitan Platok, CTO of Code Blue, will talk about "Fight AI Threats with Resilience AI": how attackers are using AI, and how organizations can use AI to detect, respond and recover faster. Ready for Tomorrow: Cyber, AI & Organizational Resilience A unique event by Howden and Code Blue on the future of organizational resilience, cyber crisis management and AI-driven innovation. 📅 19.10.2026 | 09:00-13:30 📍 Tosca, Petah Tikva
- CyberVadisSince 24 Sept 2026
Il y a quatre ans, j'ai reçu un mail d'extorsion. Mon nom, mon adresse, le prénom de mon fils, et une référence à un vin rouge que je n'avais jamais mentionné nulle part en ligne. Ce jour-là, j'ai eu peur, vraiment. Puis j'ai compris : ce n'était pas moi qui avais été piratée. C'était probablement un petit fournisseur (le vigneron) à qui j'avais fait confiance, quelque part dans ma vie personnelle. Ce qui m'avait marquée à l'époque, c'est le temps que ça avait dû prendre à quelqu'un pour assembler ces détails et construire un message aussi ciblé. Aujourd'hui, ce travail de profilage, une IA générative le fait en quelques minutes, à partir de n'importe quelle fuite de données chez n'importe lequel de nos fournisseurs. On vient de le confirmer dans une étude réalisée par Thibault Lapédagne, créateur de la méthodologie d'évaluation CyberVadis et Alain Bouillé, Délégué Général du CESIN : la plupart des entreprises n'ont aujourd'hui ni clause contractuelle sur l'usage de l'IA chez leurs fournisseurs, ni visibilité sur ce qui se passe au rang d'après. Je le vis à double titre. Comme professionnelle du risque tiers, ça change l'échelle du problème. Comme personne qui a reçu ce genre de mail, ça me rappelle que derrière chaque fournisseur mal maîtrisé, il y a un individu réel qui encaisse les conséquences. Chez vous, l'IA côté fournisseurs, c'est déjà un sujet qu'on adresse ou un angle mort qu'on n'a pas encore ouvert ? Commentez Etude et je vous l'envoie.
- CymulateSince 27 Sept 2026
Are you confident that your security controls would stop today's attacks? Agentic cyber defense engineering makes that provable, continuously. Download the Agentic Cyber Defense eBook👇
- D-sealSince 26 Sept 2026
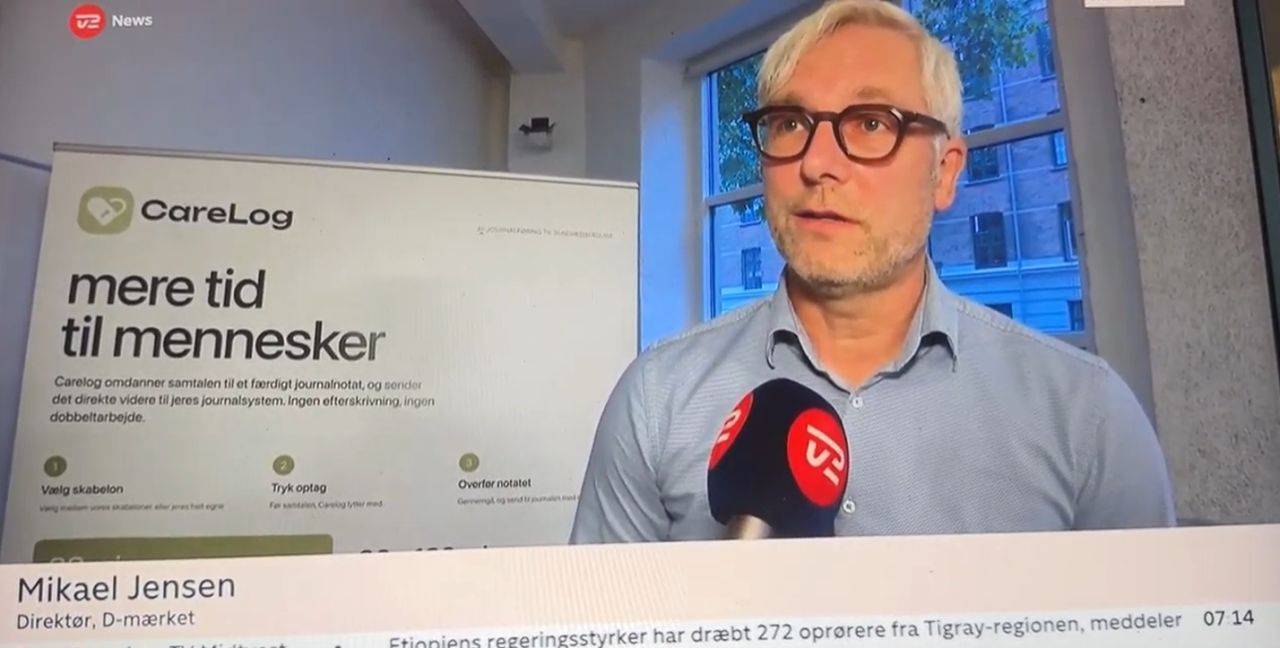
It-sikkerhed handler om at blive mere sikker i morgen, end I er i dag. At blive cybersikker er en udviklingsproces. Det tager tid. Derfor er det værdifuldt, hver gang virksomheder igangsætter et initiativ, der gør dem lidt mere sikre. Det var jeg tidligt oppe for at snakke om, da TV 2 Danmark besøgte den D-mærkede virksomhed Carelog. Anledningen er en ny undersøgelse fra PwC om, at flere små og mellemstore virksomheder frygter cyberangreb. Fra vores arbejde i D-mærket ved vi, at mange virksomheder har ønske, motivation og vilje til at styrke sikkerheden. MEN de mangler overblik og konkret hjælp til at komme i gang. Det er der heldigvis kommet mere af. I D-mærket hjælper vi virksomheder med at cyberpreppe underordnet virksomhedens indledende erfaringsniveau. Vores årlige tilsyn understøtter, at virksomhederne holder sig skarpe år for år. Senest er Cybersikker Virksomhed lanceret. Bag står Styrelsen for Samfundssikkerhed (SAMSIK) og Industriens Fond med Security Tech Space som operatør. Det er et vigtigt initiativ, hvor det offentlige og private samler sig om at løfte cybersikkerheden hos de danske virksomheder ved bl.a. at pege på relevante værktøjer. Danmark kan få Europas mest cybersikre virksomheder. Det kræver, at vi hjælper dem med at blive mere sikre i morgen, end de er i dag – ikke ved at slå dem i hovedet med, at de halter efter.
- IS DecisionsSince 25 Sept 2026
AI is lowering the bar for attacks on AD. The vulnerabilities pentesters flag every time? Still there. Still fixable. Live webinar: What pentesters fix first: 5 AD hardening wins Oct. 14 | 11am ET / 5pm CEST | 45 min Register here: https://lnkd.in/dgR5AGBJ/?utm_campaign=Whatpentestersfixfirst:5ADhardeningwins&utm_source=linkedin&utm_medium=paid&utm_id=1225898583&hsa_acc=500016795&hsa_cam=1225898583&hsa_grp=891792013&hsa_ad=1558899843&hsa_net=linkedin&hsa_ver=3
- CymulateSince 27 Sept 2026
Learn how AI agents work together at machine speed to help security teams continuously prove, prioritize and adapt defenses before attackers strike.
- ESET PolskaSince 25 Sept 2026
Internet to dziś przestrzeń, w której cała rodzina uczy się, pracuje, komunikuje i spędza wolny czas. Warto zadbać o jej bezpieczeństwo. ESET HOME Security Essential zapewnia ochronę urządzeń przed zagrożeniami online, pomagając bezpieczniej korzystać z cyfrowego świata. 🛡️ Sprawdź: https://lnkd.in/dqurxM2g
- CydomeSince 24 Sept 2026
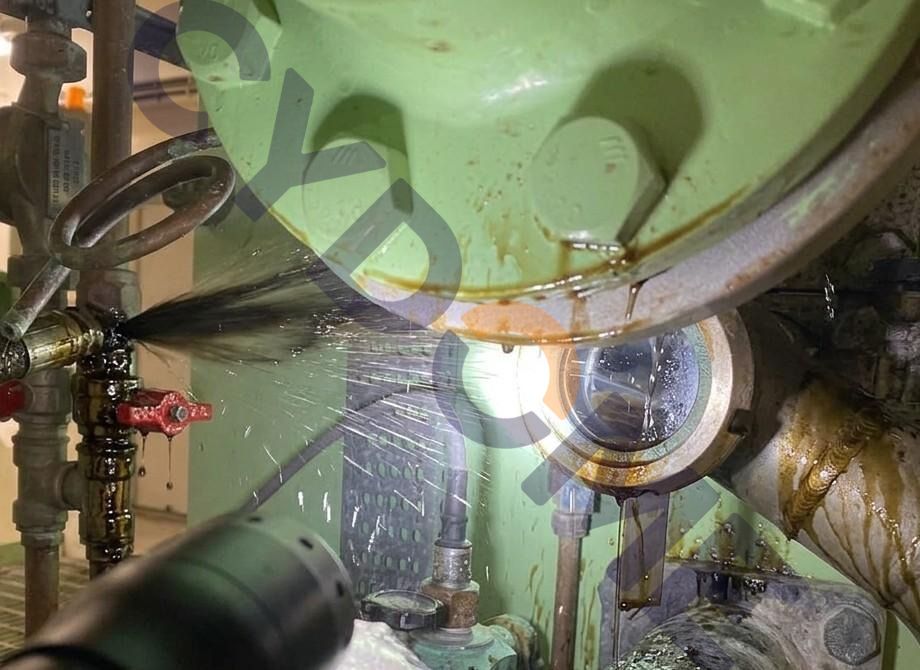
💡 What's fake and what's not in the recent tanker cyber incidents Last week, the U.S. Coast Guard and Federal Bureau of Investigation (FBI) announced that a joint team boarded marine vessels to inspect them, following indications of possible cybersecurity compromise. The agencies did not reveal which systems were impacted, and reports varied from loss of communications for 30 hours near Gibraltar to a compromise of engine control systems and hydraulics. Some reports even included images of leaking pipes and an (alleged) “ransom” note addressed to the VL Prosperity tanker’s master from the hackers, instructing them to abandon ship within 15 minutes. The Cydome maritime cyber research team analyzed the incident, identified interesting new insights and the research was featured in the Financial Times. First, we found that the information about pipe leaks etc., published originally in Iranian media and a Russian-speaking Telegram channel (later repeated by other publications) is fake. We analyzed the images and saw evidence they are an AI manipulation of images of a Maersk vessel published on social media in 2023 (that don’t show any signs of problems). Since the U.S. Coast Guard confirmed evidence of malicious cyber activity on board (without specifying), the team continued and found additional information that could present a possible attack vector: ▶️ The fake images originated or were distributed very early by Iranian media and Russian-speaking Telegram channels. ▶️ Last year, two fleets of Iranian tankers were hacked by exploiting their ST Engineering iDirect VSAT satellite terminals, completely disabling their satellite communications (see the Lab Dookhtegan incident analysis by Cydome research). ▶️ The VL Prosperity seems to have been transporting Saudi oil to the USA. ▶️ CISA and Saudi aramco published new vulnerabilities in ST Engineering iDirect VSATs mere weeks before the attacks (followed by additional CVEs this week). This information is purely circumstantial, as we don’t have direct evidence that the VSATs were hacked, etc. However, compromising critical ship OT systems by exploiting its VSAT is a plausible scenario that shipping companies must prepare for, and the article details how such an attack would look like. Read more in the Financial Times article here: https://lnkd.in/dgvBkC34 Link to the full analysis, with the side-by-side image comparison and a step-by-step possible attack scenario is in the comments. #maritimecybersecurity #tankerincident #CVE #VSAT Image source: Telegram
- Dragos, Inc.Since 25 Sept 2026
Defining xOT was the easy part: the full range of technologies that can influence or impact physical operations. Most OT security programs were built around a narrower view of the operational environment, and for a long time that made sense. But what operations depend on has changed. More of what keeps production running now sits outside traditional OT boundaries, and whether we call those systems OT doesn't change the consequence when they're disrupted. The harder (and much more important) question to answer is what changes when you use that definition to build a security program. It changes what you need visibility into, how you think about vulnerabilities, what activity you need to detect, what belongs in an investigation, and what you need to be prepared to respond to. That's really the point of xOT. I wrote a bit more about what changes when you define the environment this way, and why getting the definition right matters. https://lnkd.in/gcha8XcF Every xOT environment will draw these lines a little bit differently. The important part is making sure your cybersecurity program reflects what operations actually depend on. #cybersecurity #otcybersecurity #OTthreats #icssecurity #xot
- IS DecisionsSince 25 Sept 2026
Join the first Authentication Insights live webinar on Oct 14. Spencer Alessi (Sr. Pentester at SecurIT360, Microsoft MVP) and John E. Dunn (IT Journalist) walk through 5 AD hardening wins you can fix fast. Register here: https://lnkd.in/dyvW3u_r/?utm_campaign=Whatpentestersfixfirst:5ADhardeningwins&utm_source=linkedin&utm_medium=paid&utm_id=1225898583&hsa_acc=500016795&hsa_cam=1225898583&hsa_grp=891792013&hsa_ad=1559037833&hsa_net=linkedin&hsa_ver=3
- Dragos, Inc.Since 26 Sept 2026
Ten years ago we started Dragos, Inc. with one mission: safeguard civilization by protecting the operational technology that runs our world and is critical to our local communities. Today marks a major milestone. The Accenture majority investment in Dragos has cleared government approvals and is now official. Which means Dragos can and has now officially acquired NetRise and runZero! With our previous acquisitions of Network Perception and Phosphorus Cybersecurity Inc. we're building the industry's first end-to-end xOT Cybersecurity platform, from the software supply chain and connected devices to the operational core. In addition to my role as CEO I've also been elevated to the role of Chairman of the Board of Directors. The new investment has also brought significant job growth to include over 100 positions opened over the past few months and hundreds more in the future; mostly focused in R&D as well as investments across Dragos. Our commitment is to make sure the Dragos Platform doesn't just meet where you are in your journey today but is where you will need to be in the future as we navigate a growingly complex world. I'm grateful to welcome HD Moore Thomas Pace Michael Scott and their teams to Dragos. What you've built extends our mission in exactly the way defenders need. I share more on what all this means, and link to our upcoming webinar with me on the topic, in my recent blog. Read more at: https://lnkd.in/eUJssa-u
- ESET PolskaSince 25 Sept 2026
🛡️ Masz wszystko pod kontrolą? A co z tym, czego nie widzisz? Nie każdą próbę ataku da się zauważyć na pierwszy rzut oka. Podejrzany plik, złośliwa strona czy aplikacja mogą wyglądać zupełnie niewinnie. Dlatego oprócz ostrożności warto mieć dodatkową warstwę ochrony. 🔎 ESET HOME Security Essential pomaga chronić urządzenie przed złośliwym oprogramowaniem i innymi zagrożeniami, które mogą pojawić się podczas codziennego korzystania z internetu. Bo bezpieczeństwo nie kończy się na świadomości zagrożeń. Wymaga ochrony, która stale czuwa w tle, kiedy Ty po prostu korzystasz z sieci. 🔐 👉 Sprawdź ESET HOME Security Essential i zadbaj o ochronę swoich urządzeń. https://lnkd.in/dqurxM2g
- ESET Southern AfricaRecorded 8 Oct 2026
Partner with ESET to deliver proactive, prevention- first cybersecurity while giving your customers simple, centralised security management. As an ESET MSP partner, you can: 👉 Deliver proven cybersecurity to customers 👉 Simplify security management with ESET PROTECT 👉 Strengthen your service with a trusted partner 👉 Grow your business and keep customers protected Ready to explore what an ESET partnership could look like for your MSP? Fill in the form to speak to our team and find out more.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.