B2B ad examples
1,800 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- Adversa AISince 18 Oct 2026
Vibe coding is now an enterprise problem. Employees are building internal dashboards, HR tools, and live CRM integrations. Security teams often don't have visibility into these apps and their build processes. The major conceptual mistake here is to treat "AI coding" as one generic risk category. Vibe coding is a completely new enterprise governance surface. To secure it, you have to split the trend into two materially different architectures: ☁️ Hosted AI builders (SaaS, e.g., Lovable, v0, Base44) The building happens in a vendor's cloud. The main security risks are insecure application design and data exposure, which are often completely invisible to your endpoint security. 💻 Local coding agents (e.g., Claude Code, Cursor, Copilot) These run on employee machines. The additive risk here is an autonomous agent misusing employee privileges and corporate credentials to cause as much damage as a determined insider could. Treating these as the same problem means you're applying the wrong security boundaries. Outright bans don’t work. AppSec, IT, and SOC teams need realistic "paved roads" instead: tenant settings and data classification for SaaS builders, combined with credential scoping, runtime monitoring, AIDR, and identity-level guardrails for local agents. Read our full analysis on how to secure the vibe coding era without relying on "no": https://lnkd.in/eFGnjG3u #Vibecoding #AIsecurity #AIGRC #AgenticAI #AIDR
- GitGuardianSince 17 Oct 2026
For a long time at GitGuardian, we secured secrets where we assumed they lived: in the code. Attackers found a new target recently: developer laptops (and obviously vibe coder laptops) Every major supply-chain attack pushed them toward the place credentials actually pile up the developer laptop. Shell histories, .env files, CLI caches, and now AI agent configs from Cursor, Copilot and Claude Code. Our early-access data: ~40% of them are written there by the AI agents themselves, in terminal sessions, output logs and caches no repo scanner ever checks. So we built for the assumption every security team should make: These devices will be compromised. The only question is whether you'll know what was on it. Today we're shipping Developer Endpoint Protection, built into ggshield: → Limit the blast radius → Detect live attacks with honeytokens → Remediate at the source Find and remediate critical exposed credentials before attackers can steal them
- GitGuardianSince 17 Oct 2026
5x more secrets remediated year over year with the same team, and 80%+ lower MTTR (GitGuardian customer data). That’s what a dedicated function does.
- CyberhavenSince 18 Oct 2026
Legacy DLP tools inspect files at a single point and miss data with no recognizable pattern: source code, product designs, business plans, meeting recordings. Cyberhaven traces the full journey of every sensitive file, cutting false positives by 90% so security teams can act on real risk instead of sorting through false alarms.
- BigIDSince 18 Oct 2026
The University of Maryland faced a familiar yet daunting challenge: sprawling cloud data, scattered sensitive records, and increasing exposure to risk. Their solution? BigID.
- CyberhavenSince 18 Oct 2026
Employee use of GenAI applications stalled between December and June. Data moving through those same tools grew 80% year over year. Cyberhaven's mid-year report lays out what that shift means for enterprise security programs.
- Above SecurityRecorded 19 Oct 2026
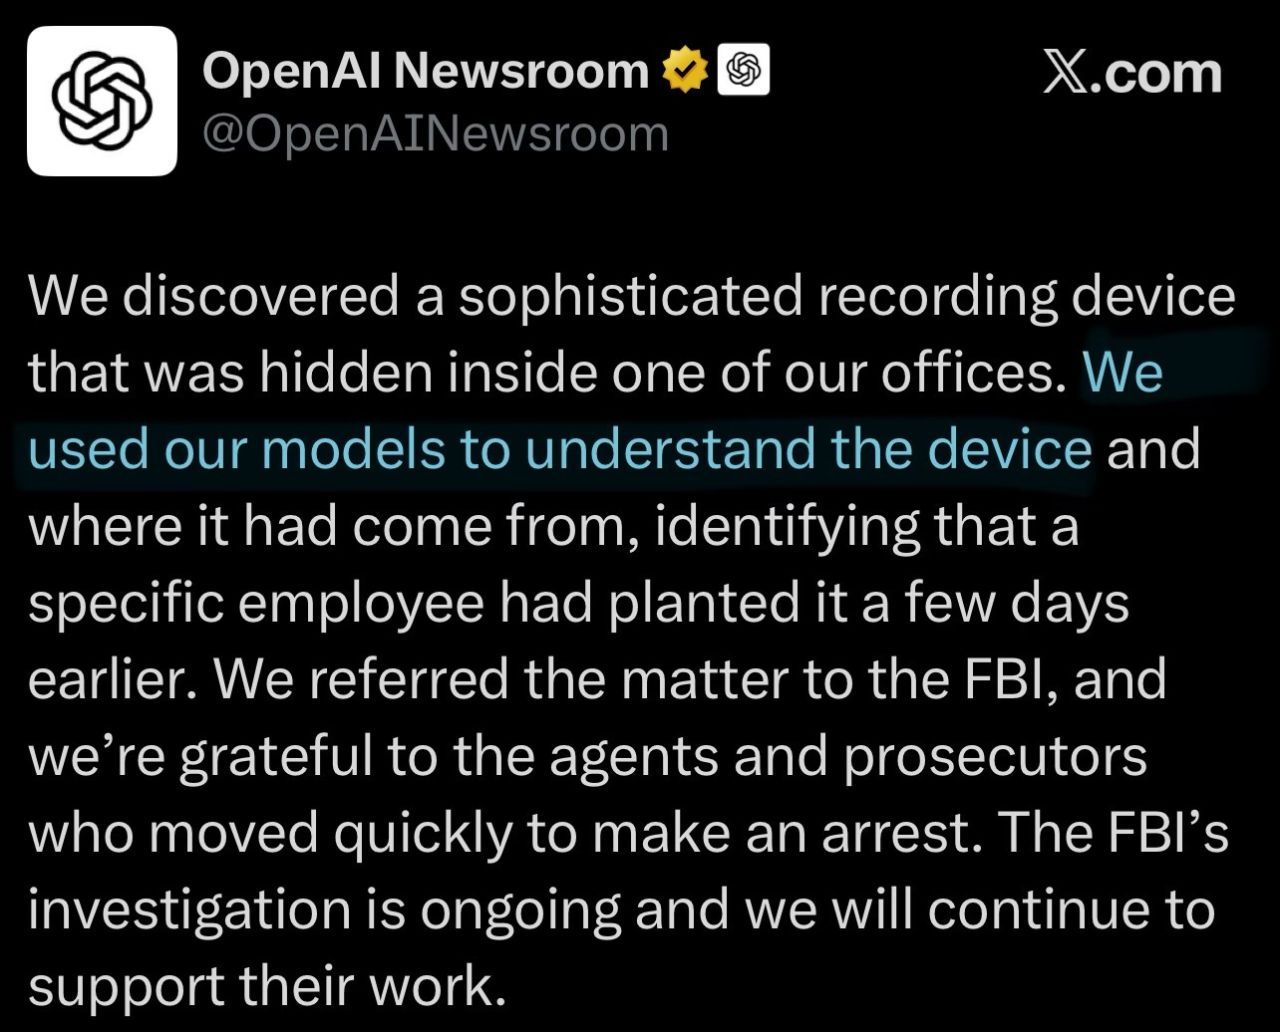
Insider risk should be managed left of boom. A pretty extreme case of malicious insider threat. Insider threats come in every color, from malicious espionage to simple negligence. But what interests me is what happened before they found the device. I'm sure there were earlier behavioral signals that, when connected, could have raised suspicion. Not when you discover the recording device, but when the risk starts developing.
- KasperskySince 16 Oct 2026
Grow your business, not your cyber risks. As your business grows, so do the cyber risks. But protecting your business doesn’t have to mean adding complexity or stretching your resources. Join our webinar on October 27 to discover practical ways to strengthen cybersecurity, protect customer trust, and keep your business running smoothly. 📅 Save your spot and learn how to make cybersecurity work for your business. 👉 Register now!
- A-LIGNSince 17 Oct 2026
Your path to AI governance starts with ISO 42001 certification. A-LIGN was among the first accredited certification bodies for the standard, with nearly 6,000 ISO assessments completed globally. See how we can help. Book a meeting with our team today.
- Fidelis SecurityRecorded 18 Oct 2026
AI is changing security operations - but what actually works today, and what is still hype? Join us for Beyond the Hype: Building an AI-Ready Security Operations Center, featuring John Pirc, CPTO, and Paul Girardi, EVP of Strategy & Partnerships, with Maria Glendinning, Director of Strategic Growth Initiatives and Partner Experience at Fidelis Security, moderating the conversation. They’ll explore practical AI use cases, the importance of data quality and governance, where human expertise remains essential, and how security teams can prepare for increasingly autonomous workflows. 📅 Tuesday, November 10, 2026 ⏰ 11:00 a.m. ET Register now: https://lnkd.in/dhNUdTh6 #Cybersecurity #AI #SecurityOperations #FidelisSecurity
- ESET ItaliaSince 15 Oct 2026
☕ La Colazione da ESET arriva a Bologna! Il 20 ottobre ti aspettiamo a Palazzo Gnudi, in Via Riva di Reno 77/a, per una mattinata di confronto, idee e cybersecurity. 🤝 Ci vediamo a partire dalle 10:00! Prenota il tuo posto 👉 https://bit.ly/4hNshbd
- E-GÜVENSince 16 Oct 2026
Şirketlerin e-imzaya geçişi tesadüf değil. İş dünyasında hız, verimlilik ve esneklik her geçen gün daha fazla önem kazanırken; e-imza çözümleri de süreçlerin daha pratik şekilde yönetilmesine yardımcı oluyor. İmza ve onay adımlarını hızlandıran, operasyonel yükü azaltan ve dijital iş yapış biçimine uyumu destekleyen e-imza, kurumlar için güçlü bir dönüşüm aracı haline geliyor. E-Güven ile siz de iş süreçlerinizi daha güvenli, daha düzenli ve daha verimli bir yapıya taşıyabilirsiniz. E-imzaya geçin, iş süreçlerinizi ileri taşıyın. #egüven #dijitalçözümuzmanınız #elektronikimza #eimza
- E-GÜVENSince 16 Oct 2026
Yapılacaklar listeniz uzadıkça süreçlerinizin de yavaşlaması gerekmez. E-Güven ile belgelerinizi saniyeler içinde dijital ortamda imzalayabilir; işlerinizi güvenli, hızlı ve yasal geçerliliğe sahip şekilde tamamlayabilirsiniz. Listenizdeki son maddeyi de kolayca tamamlamak için elektronik imzanın avantajlarını keşfedin. #egüven #dijitalçözümuzmanınız
- Hiya Inc.Since 15 Oct 2026
📞 Este sábado 17 de octubre cambia la forma de hacer llamadas comerciales en España. Como recuerda el ministro Óscar López en este vídeo de Europa Press, las llamadas comerciales destinadas a captar nuevos clientes deberán utilizar el prefijo 400. Una medida que busca proteger al consumidor, pero que plantea un nuevo reto para las empresas: ¿cómo conseguir que los clientes sigan respondiendo al teléfono? Aquí es donde Hiya y nuestra solución Branded Calls cobran todavía más sentido. Permitimos que las empresas identifiquen sus llamadas salientes mostrando su nombre generando confianza desde el primer segundo. Porque una cosa es identificar que una llamada es comercial y otra muy distinta es saber quién te está llamando. Si quieres conocer cómo Hiya puede ayudar a tu empresa a proteger sus tasas de respuesta ante este nuevo escenario, aquí tienes toda la información: https://lnkd.in/eE2A-WdB #BrandedCalls #Contactabilidad #CustomerExperience
- Fox-ITSince 16 Oct 2026
AI is changing the pace of cyber risk - and vulnerability management needs to keep up. The ECB’s recent letter to financial institutions highlights a growing challenge: as AI improves attackers’ ability to identify vulnerabilities, develop exploits and map attack paths, organisations have less time to assess and respond. The issue is not just the volume of vulnerabilities. It’s understanding: ✅ What is exploitable ✅ What assets are exposed ✅ How weaknesses could be combined ✅ Where business impact could occur ✅ Which actions reduce risk fastest Read our article for insights on the ECB’s 6 focus areas, why this matters beyond financial services, and how organisations can respond with greater clarity across visibility, prioritisation, remediation and resilience. Read the full article 👇 https://lnkd.in/dJQXJup7 #CyberResilience #RiskManagement #BankingFinancialServices #AIGovernance #EUFinance #ECB
- IDECSISince 16 Oct 2026
La plupart des environnements M365 ont des failles actives. Pas par manque de budget. Par manque de méthode. 30 contrôles. Une grille d'évaluation. Une méthodologie claire. Téléchargez la checklist et sachez où vous en êtes avant vendredi.
- EnclaveSince 16 Oct 2026
Western open-weight models are starting to show up for offensive security. Meta just released Muse Spark Open, which they call the most capable US open-weight model, built for coding and agentic work. We put it through the AI Hacking Race, our benchmark where a model only scores when it gets verified command execution inside an isolated target and proves it from the inside. Muse Spark Open verified 1 of 11 vulnerable runs. The one solve was a clean Jenkins exploit chain: it found a leaked controller token, authenticated as the controller, and ran code through the script console, in about 4 minutes for 82 cents. On most of the other challenges it read the right vulnerable code and could not finish the exploit inside the time budget. It never claimed a flag it could not prove, and none of the four patched controls verified. One of eleven is a modest score, but the direction is what stands out. An open-weight model with published weights, that works offensive security tasks without refusing and reads the planted vulnerable code across Grafana, Jenkins, and Nextcloud, is a genuine step forward for Western open models in this space. Full writeup: https://lnkd.in/eNnB-P53
- Cyber360 | Specjaliści od cyberbezpieczeństwaSince 16 Oct 2026
Kolejny samorząd na celowniku cyberprzestępców: Urząd Miejski w zachodniopomorskim potwierdza nieautoryzowany dostęp do swoich systemów. Jak poinformował portal CyberDefence24, w Urzędzie Miejskim w Darłowie doszło do przełamania zabezpieczeń. Atakujący wykorzystali niezałataną podatność w oprogramowaniu, uzyskując dostęp do infrastruktury informatycznej oraz części danych petentów. To kolejny polski samorząd w tym roku – po Myszkowie, Nowej Rudzie, Lewinie Kłodzkim czy Gminie Obrazów – który musi mierzyć się z paraliżem operacyjnym oraz potencjalnym wyciekiem danych mieszkańców. 🏛️ Co jest DZIŚ kluczowe dla administracji publicznej? Samorządy i urzędy nie są już dla hakerów celem „przy okazji” – stały się celem numer jeden ze względu na wrażliwość przetwarzanych danych i często przestarzałą infrastrukturę IT. Dyrektorzy, Włodarze i Szefowie IT w samorządach muszą szybko spełnić 3 kluczowe warunki: 1️⃣ Natychmiastowe zarządzanie podatnościami (Vulnerability Management): Atak w Darłowie powiódł się przez niewyłapaną na czas lukę w oprogramowaniu. Urzędy muszą wdrożyć ciągłe skanowanie podatności oraz procedurę natychmiastowego łatania systemów wystawionych do internetu (Patch Management). 2️⃣ Czas na spełnienie wymogów NIS2 / uKSC drastycznie się kurczy: Nadchodzące zmiany w prawie jednoznacznie włączają samorządy (urzędy miast, starostwa, spółki komunalne) do reżimu KSC. Oznacza to osobistą odpowiedzialność kierowników jednostek za brak wdrożonych procedur i audytów bezpieczeństwa. 3️⃣ Monitorowanie sieci 24/7 (SOC) i ciągłość działania: Brak całodobowego monitoringu sprawia, że przestępcy poruszają się po sieci urzędu przez wiele dni niezauważeni. Samorządy muszą przestawić się z modelu „reagujemy po fakcie” na stałą stałą ochronę. Jak Wasza jednostka radzi sobie z audytem podatności zewnętrznych oraz przygotowaniem do wymogów NIS2? W Cyber360 przygotowaliśmy dedykowaną ofertę stworzoną z myślą o gminach, powiatach i jednostkach samorządowych. Umów się na krótkie spotkanie (link w komentarzu) i sprawdź specjalne warunki wsparcia.
- Fox-ITSince 16 Oct 2026
As AI accelerates vulnerability discovery and exploitation, security teams are under increasing pressure to make faster, better informed decisions. But speed alone is not enough. Organisations need to understand which vulnerabilities are most exploitable, how they connect across environments, and which remediation actions will reduce risk most effectively. Natalie Walker’s latest article looks at the ECB’s recent call to action for financial institutions but it’s also a message that will resonate far beyond financial services. Read now 👇 https://lnkd.in/dJQXJup7 #CyberResilience #RiskManagement #Banking #FinancialServices #Industry #AIGovernance #EUFinance #ECB
- ESET DACHSince 16 Oct 2026
Wie im Spitzensport entscheidet Prävention über den Erfolg. ESET MDR stoppt Angriffe, bevor sie Auswirkungen haben.
- ESET DACHSince 16 Oct 2026
Wenn Systeme ausfallen, steht oft mehr als nur die IT still. Schützen Sie Ihr Unternehmen mit ESET.
- FortinetSince 15 Oct 2026
From ransomware to nation-state threats, discover how organizations are strengthening #OTSecurity
- FortinetSince 15 Oct 2026
▶ Watch: 71% of organizations experienced OT intrusions. See the trends, risks, and priorities shaping #OTSecurity
- InfusionPoints, LLCRecorded 18 Oct 2026
FedRAMP CR26 is changing the way Cloud Service Providers approach security, compliance, and continuous authorization readiness. Whether you're already on the FedRAMP Marketplace or preparing for what's next, understanding these changes is critical. Download InfusionPoints' FedRAMP CR26 CSP Playbook for practical guidance to help your team navigate evolving requirements and prepare for the future of FedRAMP.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.