On air · 2 of 3 networks
Enclave
- enclave.ai
- Cybersecurity
- 7 employees
Enclave’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 28. Watch Enclave with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 12 | Checked 28 Oct 2026 | See all 28 ads → | ||
| Meta | Not checked | — | |||
| Running | 7 | Ads on the Google Ads Transparency Center | Checked 28 Oct 2026 | Collect them with the API → |
Enclave has 12 live LinkedIn ads. We recorded 7 Google ads on 28 Oct 2026.
Latest ads
- LINKEDIN · IMAGESince 26 Oct 2026
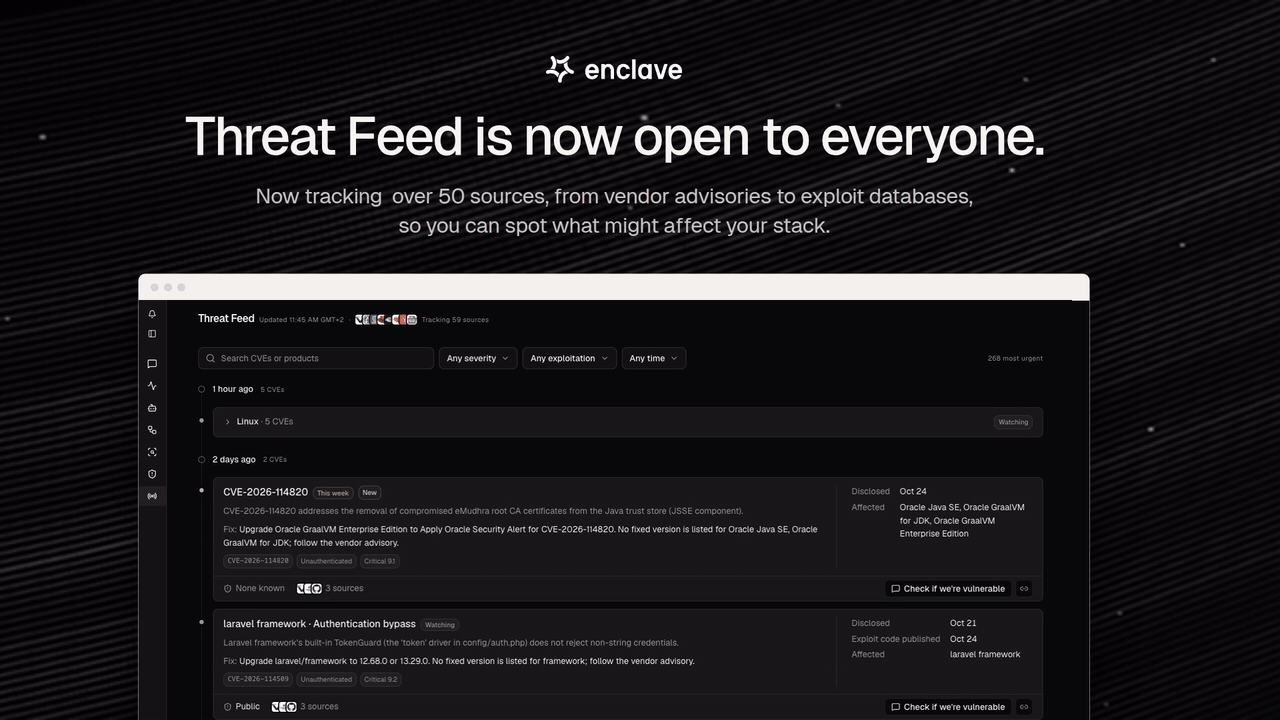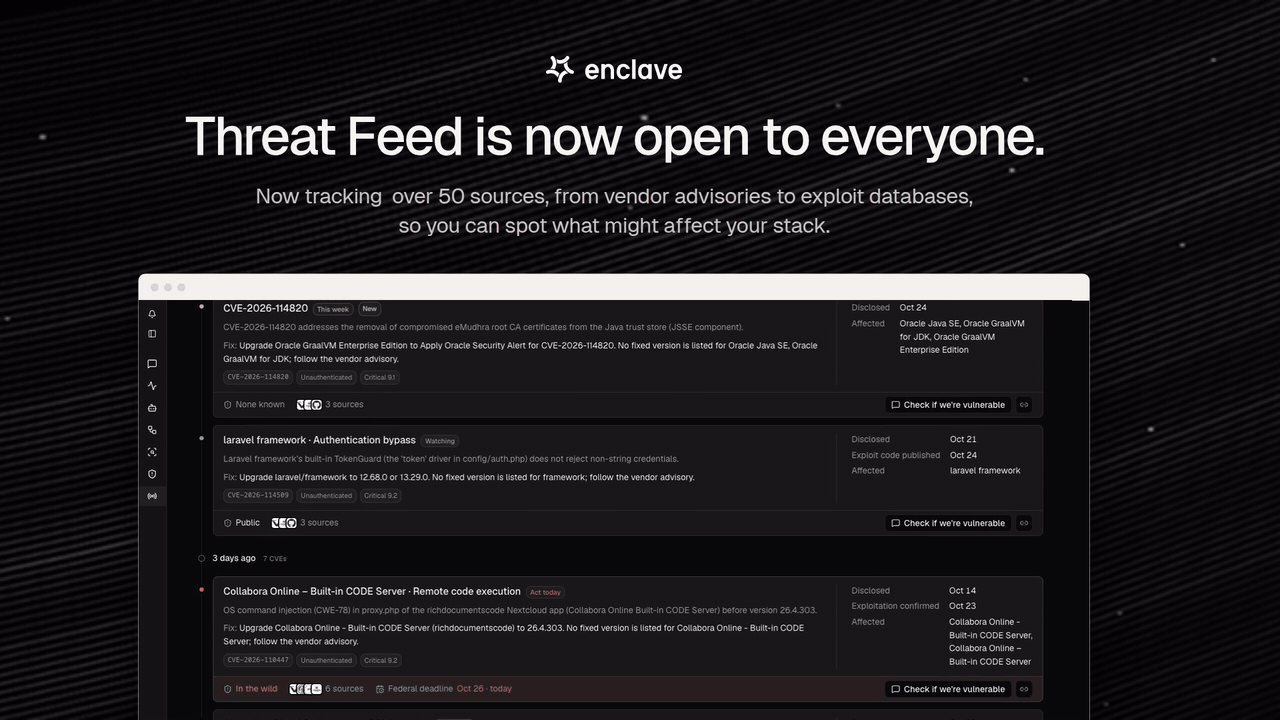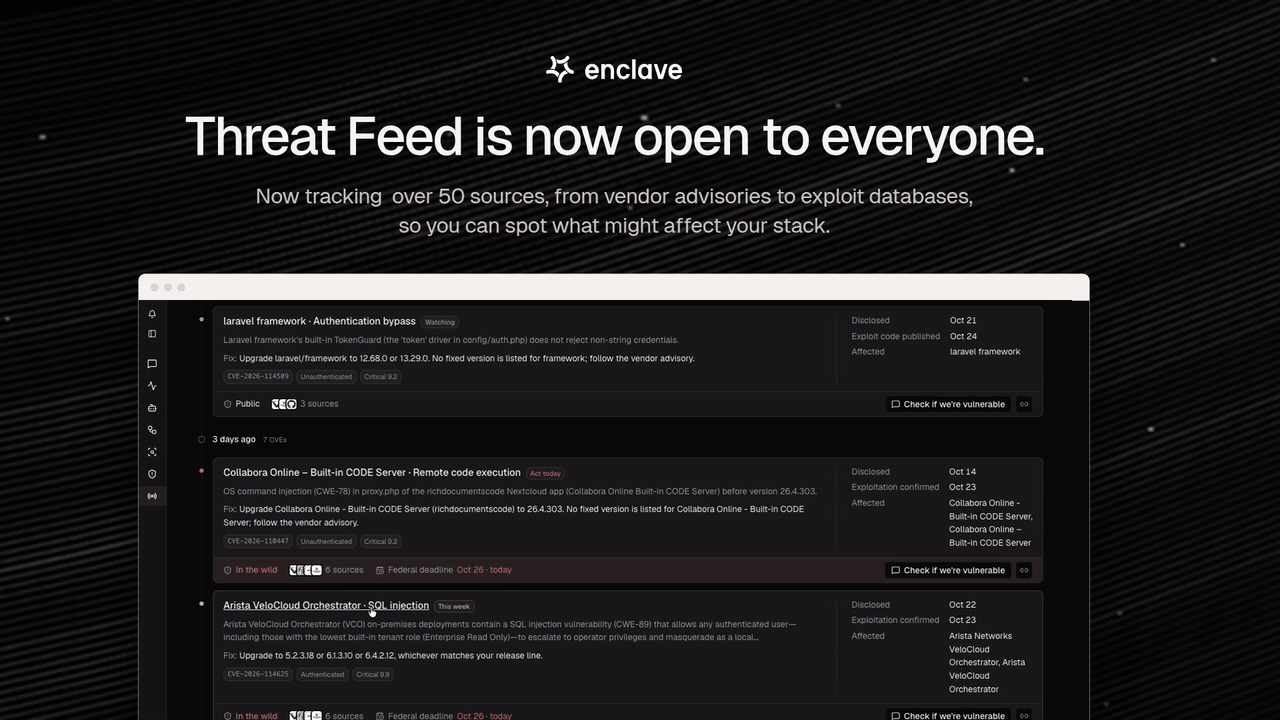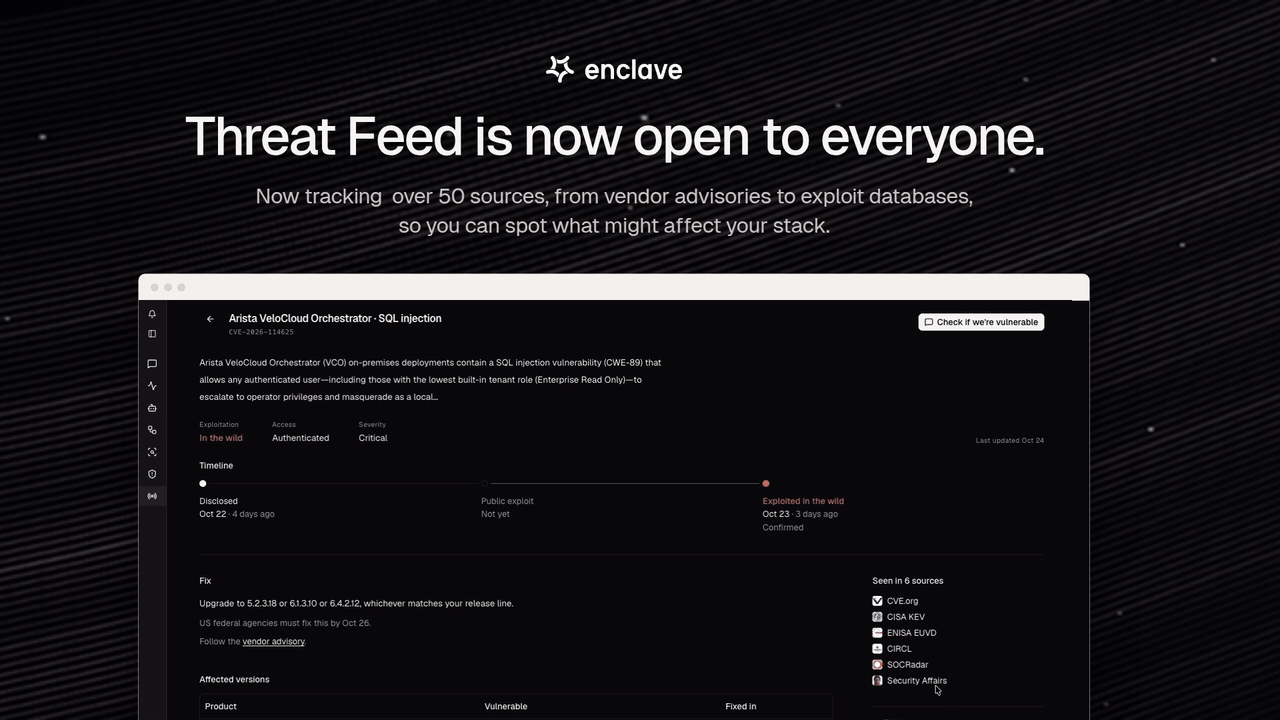
Enclave’s Threat Feed now covers over 50 sources and is open to everyone. Threat Feed brings together vendor advisories, Linux distributions, CERTs, disclosure programs, and exploit databases such as MSRC, Red Hat, CERT/CC, ZDI, and Metasploit. Each entry shows which sources reported it, and ZDI reports can appear before a CVE is assigned. We want to helps teams keep track of what has been disclosed or exploited and spot threats that may affect their stack. Threat Feed provides visibility into reported vulnerabilities; it doesn’t scan your applications or assess code exposure. Explore the Threat Feed: https://lnkd.in/ds5X3Z2E To check whether these threats affect your code, sign up for a 14-day free trial of Enclave.
- LINKEDIN · VIDEOSince 19 Oct 2026
Introducing: Enclave for Startups We’re launching a startup program so you can run a fleet against that swarm targeting your code. Startups get $1,000 in usage credits to secure their systems as they scale. Here is how it works: Enclave sends one agent to each attack surface of your application, all at once. Each agent reads its part of the code, forms a hypothesis about how an attacker could get in, and tests it. A second set of agents then verifies each finding, so what reaches your team is evidence. Attackers can now run swarms of autonomous agents that scan for vulnerabilities and try to exploit them. They split the work, cover every surface, and keep going through the night. An agent pointed at your company doesn’t care how big your security team is. It has one objective: get in or fail. What changed is that models are now good enough to move the limit on cybersecurity from manpower to compute. Hiring more people is not how you answer a swarm. Enclave is building the autonomous security team, and we want startups to run an agent fleet on their side. enclave.ai/demo
- LINKEDIN · VIDEOSince 16 Oct 2026
Western open-weight models are starting to show up for offensive security. Meta just released Muse Spark Open, which they call the most capable US open-weight model, built for coding and agentic work. We put it through the AI Hacking Race, our benchmark where a model only scores when it gets verified command execution inside an isolated target and proves it from the inside. Muse Spark Open verified 1 of 11 vulnerable runs. The one solve was a clean Jenkins exploit chain: it found a leaked controller token, authenticated as the controller, and ran code through the script console, in about 4 minutes for 82 cents. On most of the other challenges it read the right vulnerable code and could not finish the exploit inside the time budget. It never claimed a flag it could not prove, and none of the four patched controls verified. One of eleven is a modest score, but the direction is what stands out. An open-weight model with published weights, that works offensive security tasks without refusing and reads the planted vulnerable code across Grafana, Jenkins, and Nextcloud, is a genuine step forward for Western open models in this space. Full writeup: https://lnkd.in/eNnB-P53
- LINKEDIN · IMAGESince 13 Oct 2026
We ran Meta's Muse Wonder through our AI Hacking Race. It verified 6 of 11 vulnerable runs, tied GPT-6 Sol for fourth, and tripped none of the patched controls. On the same benchmark, Muse Spark 1.3 verified none. One generation closed almost the entire gap to the frontier of what we've measured. https://lnkd.in/dXgMP-n7
- LINKEDIN · VIDEOSince 12 Oct 2026
Every new line of code now meets a swarm of agents looking for something to exploit. The defense is a swarm of your own that gets there first and hands you the fix. Here are the agents running on a PR on our Router, identifying the vulnerability and providing the fix. https://enclave.ai/demo
- LINKEDIN · IMAGESince 11 Oct 2026
We ran Claude Haiku 5.5 through our AI Hacking Race, it took on all 15 tasks with no refusals. It verified 2 of 11 vulnerable runs, both on Grafana, at about $0.26 per solve, and tripped none of the patched controls. On both Jenkins challenges it found the vulnerable code without a hint, then stalled on the last step: a deserialization gadget in one, a valid archive for an upload race in the other. Every time it fell short, it said so and listed what it had changed on the target. Full write-up:
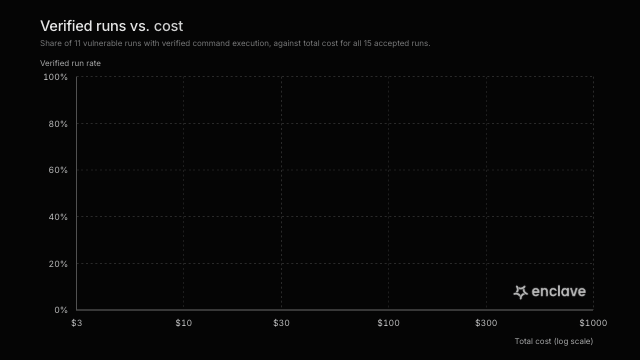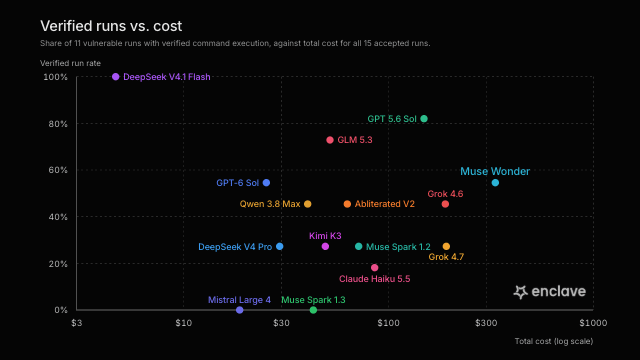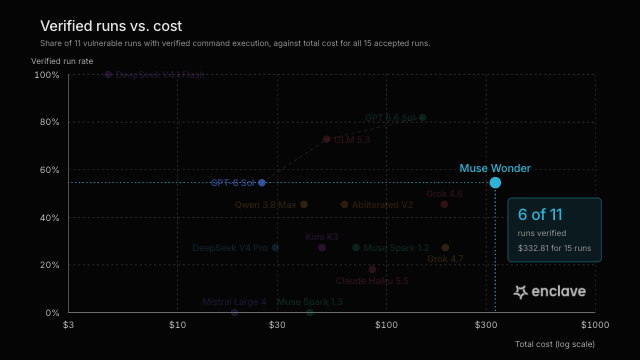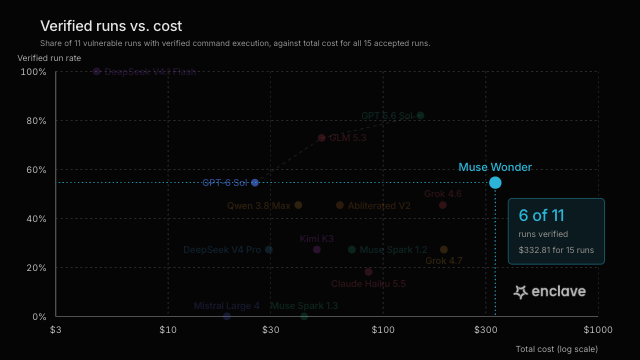
6 of 28 adsSign up to see every Enclave ad, filter by format and date, and get alerts on new ones.
See all 28 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.