LinkedIn image ad examples
1,352 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- ESET North AmericaRecorded 18 Sept 2026
Ransomware drives 35% of breaches in manufacturing, with costs averaging $5.56M per incident. ESET MDR delivers expert threat hunting, AI-powered detection, and ICS/OT integration—so you stay secure without overloading your team.
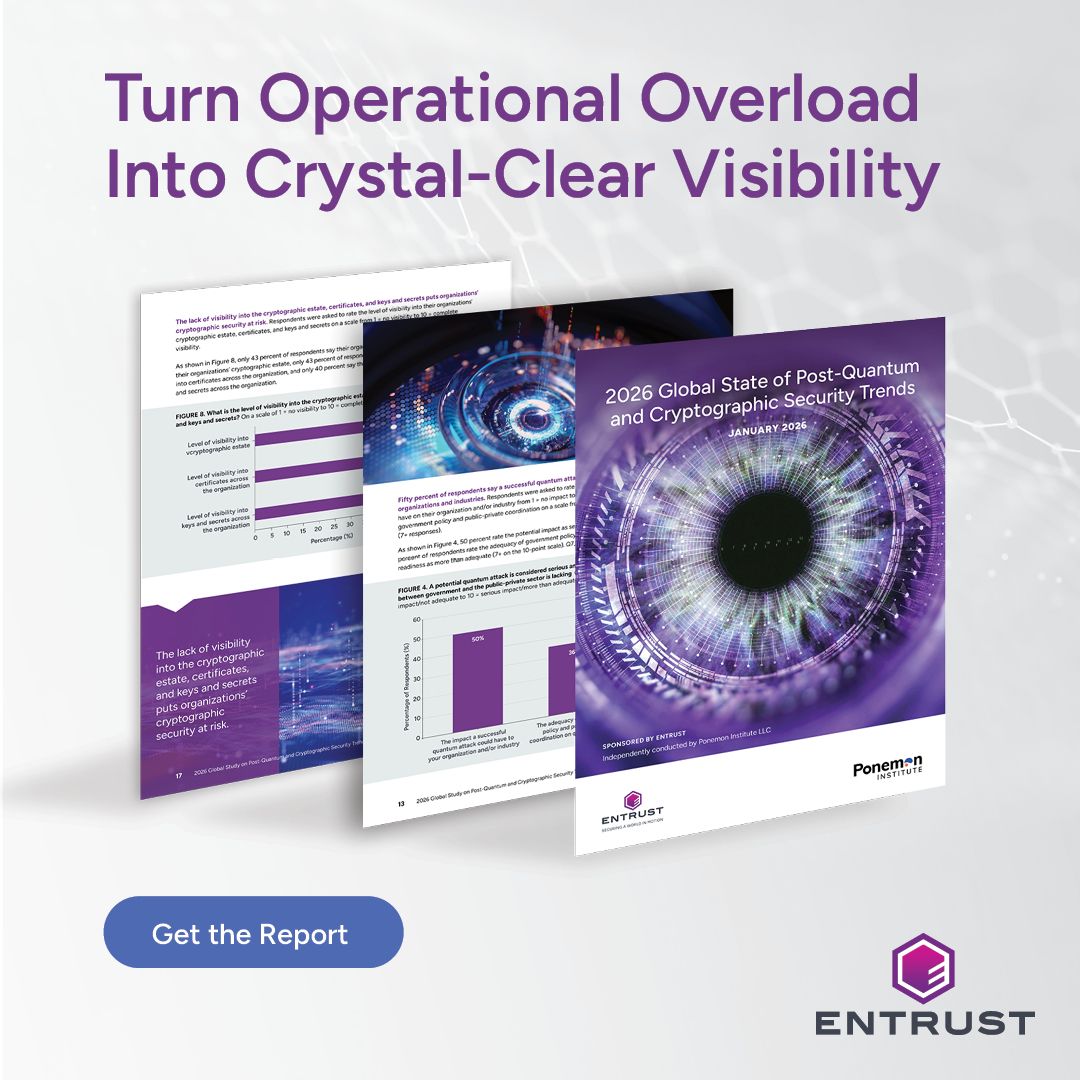
- EntrustSince 3 Mar 2026
Is your company ready for post-quantum security? Learn how top enterprises are preparing and benchmark your strategy with the 2026 Global State of Post-Quantum and Cryptographic Security Trends report.
- EntrustSince 3 Mar 2026
Download now to see how 4,000 global IT, security, and risk leaders compare on post-quantum readiness and crypto security trends.
- EmpowerIDSince 31 Mar 2026
Your team pulls from 30+ systems to answer one question. 80% of identity operations is manual stitching, not governance. --> Download Access Certification Maturity Whitepaper
- EmpowerIDSince 16 Apr 2026
Couldn't make our April 9 session with Deloitte? The replay and whitepaper are now available. 60 minutes: current state, target state, how to get from SAP IdM to a governed future state without disruption. Available through April 30.
- EscapeSince 2 May 2026
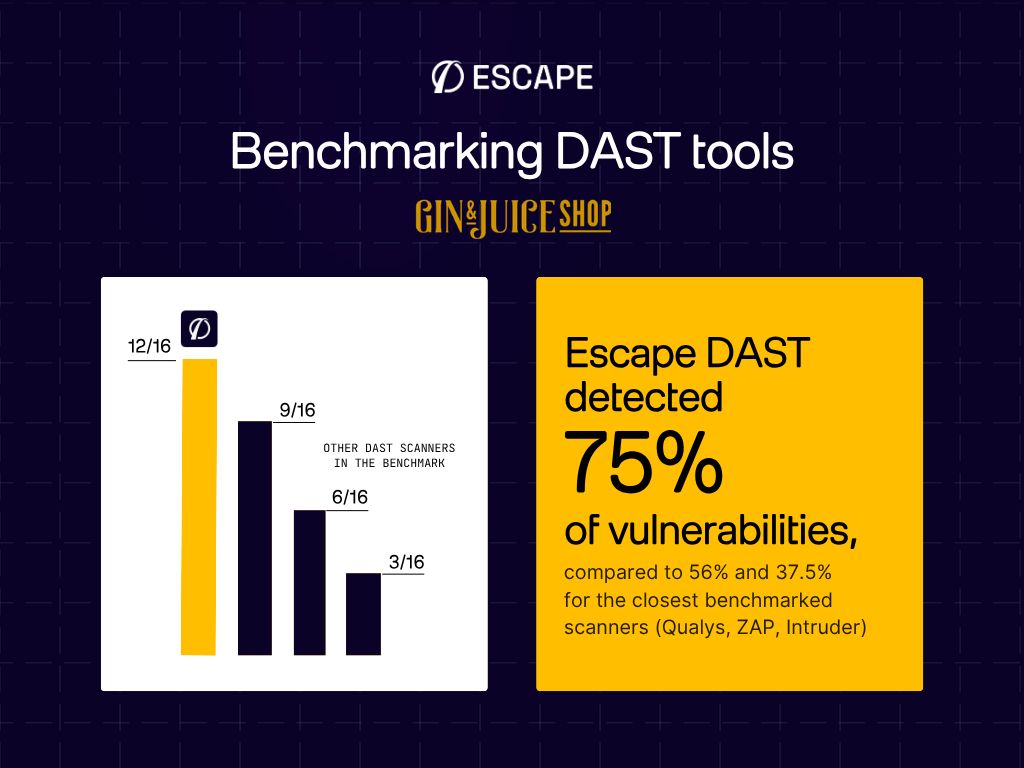
Tired of "DAST" scanners that just run generic payloads? We benchmarked Escape against industry-standard scanners (Qualys, ZAP, Intruder) on the Gin & Juice Shop. See how we stacked up on vulnerability detection, coverage, and noise.
- EscapeSince 1 May 2026
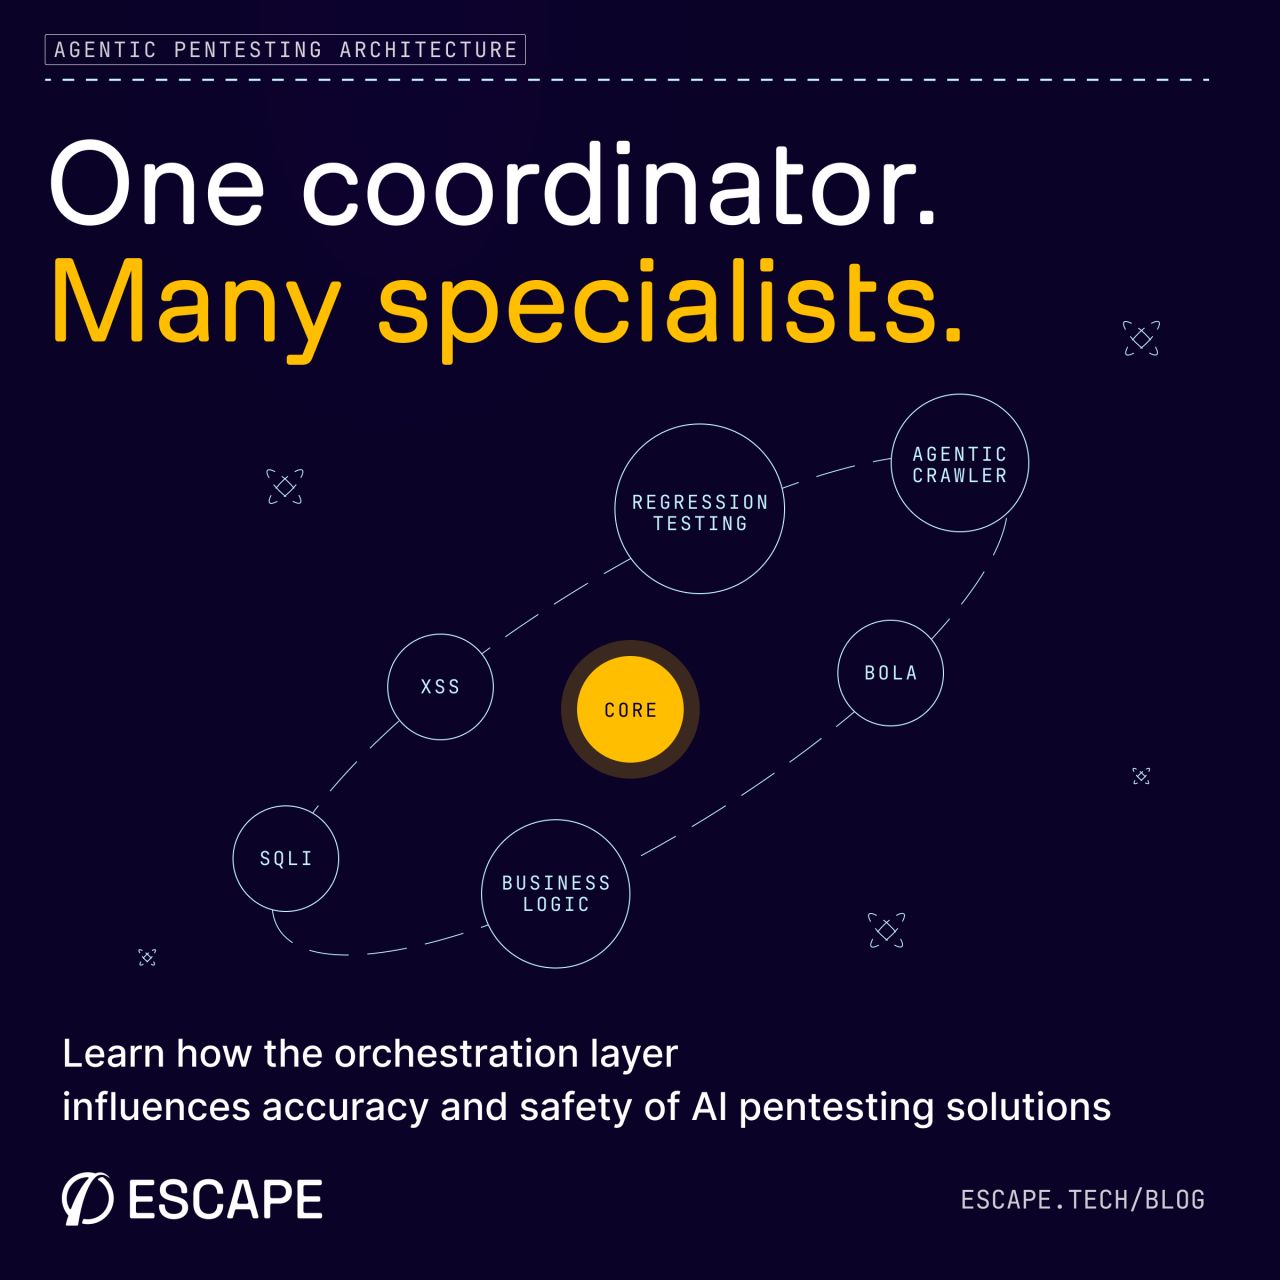
When evaluating AI pentesting tools, most people start with the model. We'd argue that shouldn't be the only point. In our recent benchmark, three different AI pentesting tools, all built on the same underlying model (DeepSeek v3.2), produced wildly different results on the same target: 6/20, 9/20, and 1/20 vulnerabilities found. Same model. Same target. A 9x gap in detection. The variable was orchestration: how each tool structures the agent's action loop, manages tool calls, and handles authentication. This is why we've spent so much time on the architecture behind our agents.. Starting with a coordinator that reasons about scope, specialized sub-agents that handle XSS, SQLi, BOLA, and business logic, and an intelligence layer that lets findings from one agent inform the next. We broke down how our multi-agent architecture works, what each specialist agent actually does, and where we still see limitations in the field in this article: https://lnkd.in/eSjzhF9b
- EquixlySince 23 Jul 2026
We don’t use frontier models to find vulnerabilities. XBOW does. That’s the core difference, and it’s on purpose. XBOW routes its reasoning to third-party frontier models in the cloud. Generalist models, built to do a bit of everything, that bill per token and are free to refuse an offensive request mid-scan when a safety filter kicks in. We run our own model, and the orchestration around it, on our own hardware. No generalist prompted into playing attacker. From the outset, it was trained to do one and only one job: AI pentesting. Your data is never shipped off to an outside model provider, and it doesn’t cost more the more you use it. Scan exactly when you need or on every commit. The invoice is the same. Identical goal as XBOW. Opposite bet on where the AI runs, and what it was built for. And that choice decides your cost, your speed, and where your data ends up. Think we’re wrong? Read the full Equixly vs. XBOW comparison in the comments and tell us. #AIPentesting #OffensiveSecurity #PenetrationTesting
- Endor LabsSince 18 Aug 2026
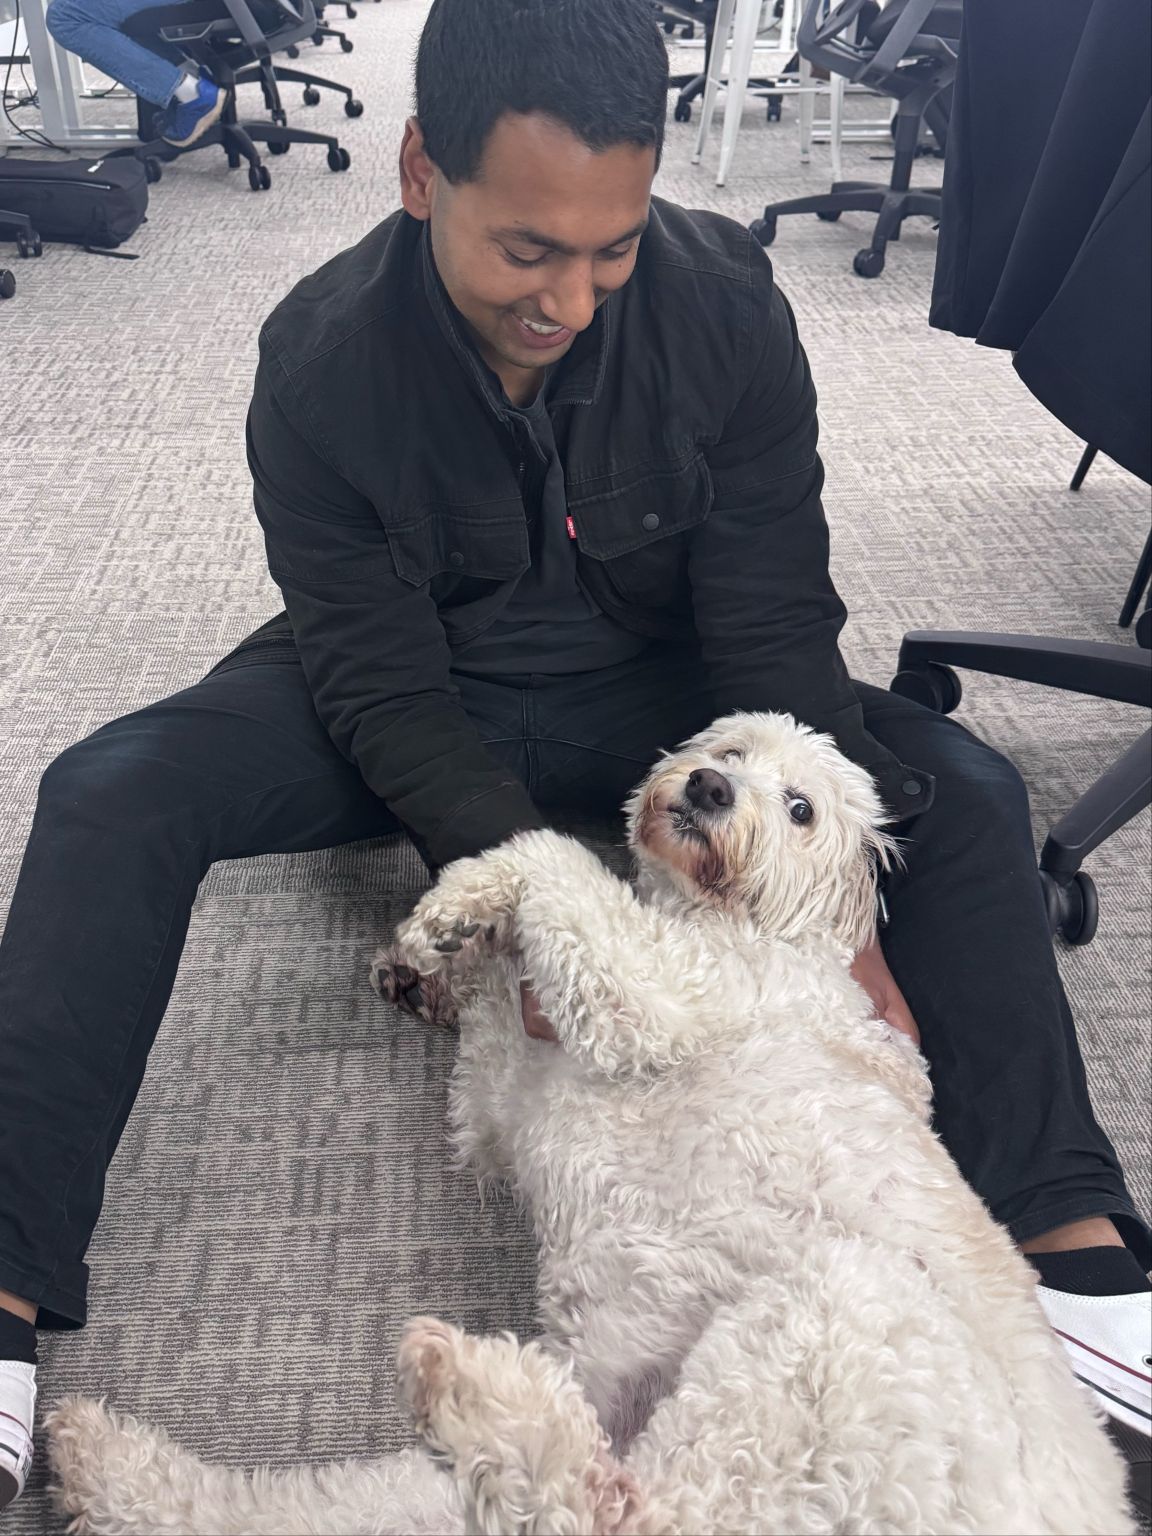
If mid-day puppy cuddles are your thing, we’re hiring across Engineering, Sales, and Marketing at our Palo Alto HQ. 🐶 Simba can never get enough belly rubs, so frankly, we need more hands. https://lnkd.in/gjccUH2Q
- EfficientIPSince 19 Aug 2026
Choosing your next DNS, DHCP, and IPAM (DDI) platform is a decision you'll live with for years. This checklist ensures you're making the right decision.
- Endor LabsSince 20 Aug 2026
Running untrusted JavaScript safely is one of the hardest problems in Node.js, and now a mainstream one, since AI agents and automation platforms run model- and user-generated code all day. isolated-vm is the library most of them reach for: 1M+ weekly downloads, relied on by n8n, Activepieces, Mastra, and Rocket.Chat to contain code they don't trust. Endor Labs researcher Cristian-Alexandru Staicu found a critical type confusion in it (GHSA-864f-rcv7-6rh4), a guest-to-host sandbox escape. From a single shared reference, the exploit goes from a controlled crash to hijacking the host's control flow. The interesting part is what didn't break. isolated-vm is built on a V8 Isolate, the same isolation Chrome uses between browser tabs, and that held. What failed was the C++ glue carrying data across the boundary. "The primitive is sound" isn't the same as "the library is safe", and the glue code is increasingly where sandbox escapes live. Maintainer shipped a fix fast; upgrade to 7.0.1 or 6.2.0. Full write-up: https://lnkd.in/eug6Fzi5 https://lnkd.in/eug6Fzi5 #AppSec #AISecurity
- EfficientIPSince 1 Sept 2026
DDI modernization is not about replacing one set of DNS and DHCP servers with another. It is about creating a more unified operating model for the network.
- Enginsight GmbHSince 11 Aug 2026
Nach einem Vorfall zählt, was dokumentiert ist. Wer hat wann was bemerkt, und wer hat reagiert? Enginsight Managed Detection and Response (MDR) beantwortet diese Frage mit Protokollen statt mit Vermutungen. Ein Cyber Defence Center in Deutschland überwacht Ihre Systeme rund um die Uhr. Bei kritischen Vorfällen erhalten Sie innerhalb von 15 Minuten eine Rückmeldung, zugesichert im Service Level Agreement. Seit Dezember 2025 gilt NIS2 in Deutschland verbindlich. Die Verantwortung dafür liegt bei der Geschäftsführung und lässt sich nicht delegieren.
- Enginsight GmbHSince 11 Aug 2026
Angriffe halten sich nicht an Ihre Geschäftszeiten. Unser Cyber Defence Center arbeitet 24 Stunden am Tag, 365 Tage im Jahr, mit deutschsprachigen Analysten. Bei kritischen Vorfällen steht die erste Rückmeldung nach 15 Minuten, die Validierung in der Regel innerhalb einer Stunde. Entwicklung und Betrieb liegen vollständig in Deutschland, wahlweise on-premises oder in der Cloud. Ihre Daten bleiben in Ihrem Rechtsrahmen. In sechs bis acht Wochen ist der Service produktiv.
- EnStream LPRecorded 17 Sept 2026
Fraudsters can pass screens, forms, and passwords. @EnStream checks what they can’t easily fake: the mobile network itself.
- EquixlySince 2 Oct 2025
🚀 Discover the Future of Equixly API Security at Cybertech Europe 2025 What to Expect: - Live Demos - Exclusive Gadgets - Expert Insights 📍 La Nuvola Convention Center, Rome, Italy 🗓 October 21–22 Join Us – We can't wait to see you there! #CybertechEurope2025 #APIsecurity #Cybersecurity #AI
- EndaceSince 18 Sept 2025
Threats evolve. Blind spots grow. Join Endace + Keysight on 24-Sep and discover how top SOCs gain visibility, speed, and certainty. For SOC teams who can't afford to guess. Wednesday 24 September 4 PM (Saudi Time), 5 PM (UAE Time)
- EndaceRecorded 17 Sept 2026
Bring clarity to every network incident, alert or issue with a full packet capture platform that integrates with all your commercial, open-source or custom-built tools. Our always-on packet capture solutions are used by some of the world's largest public and private organizations to defend and protect some of the biggest, fastest, and most critical networks on the planet.
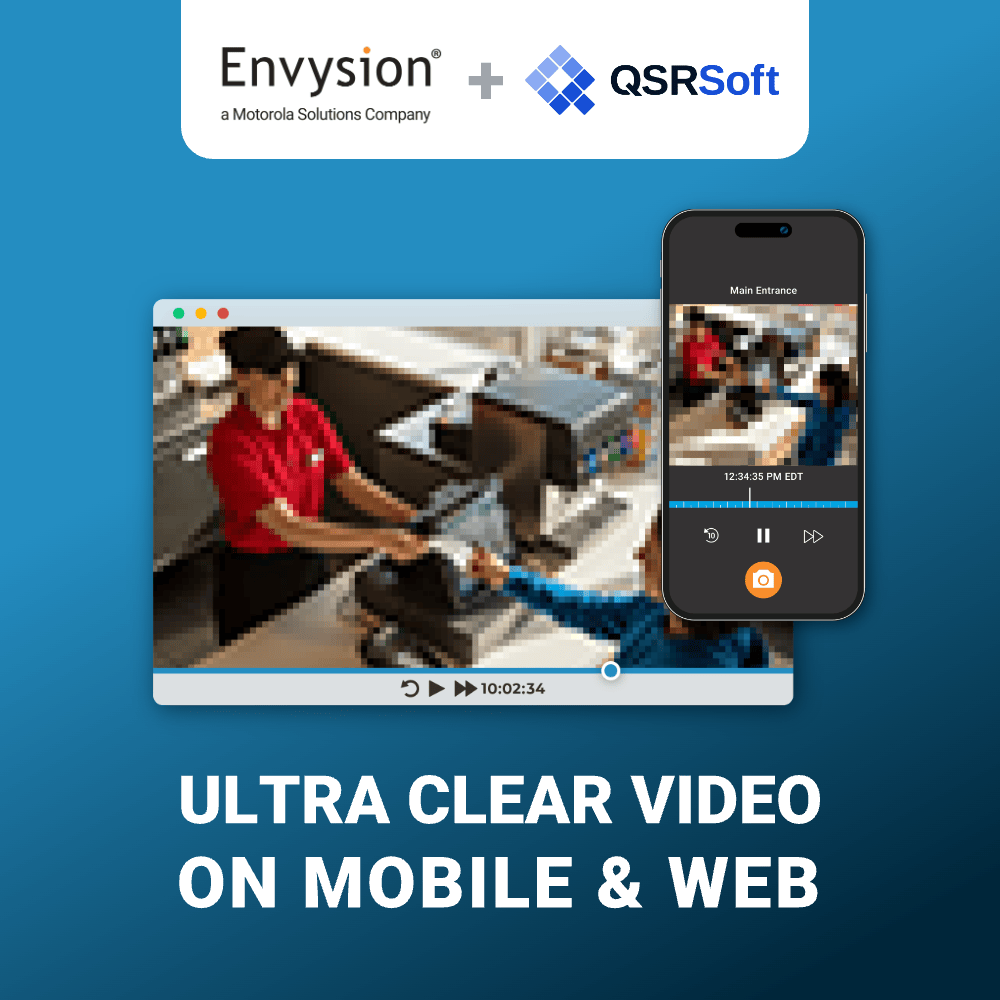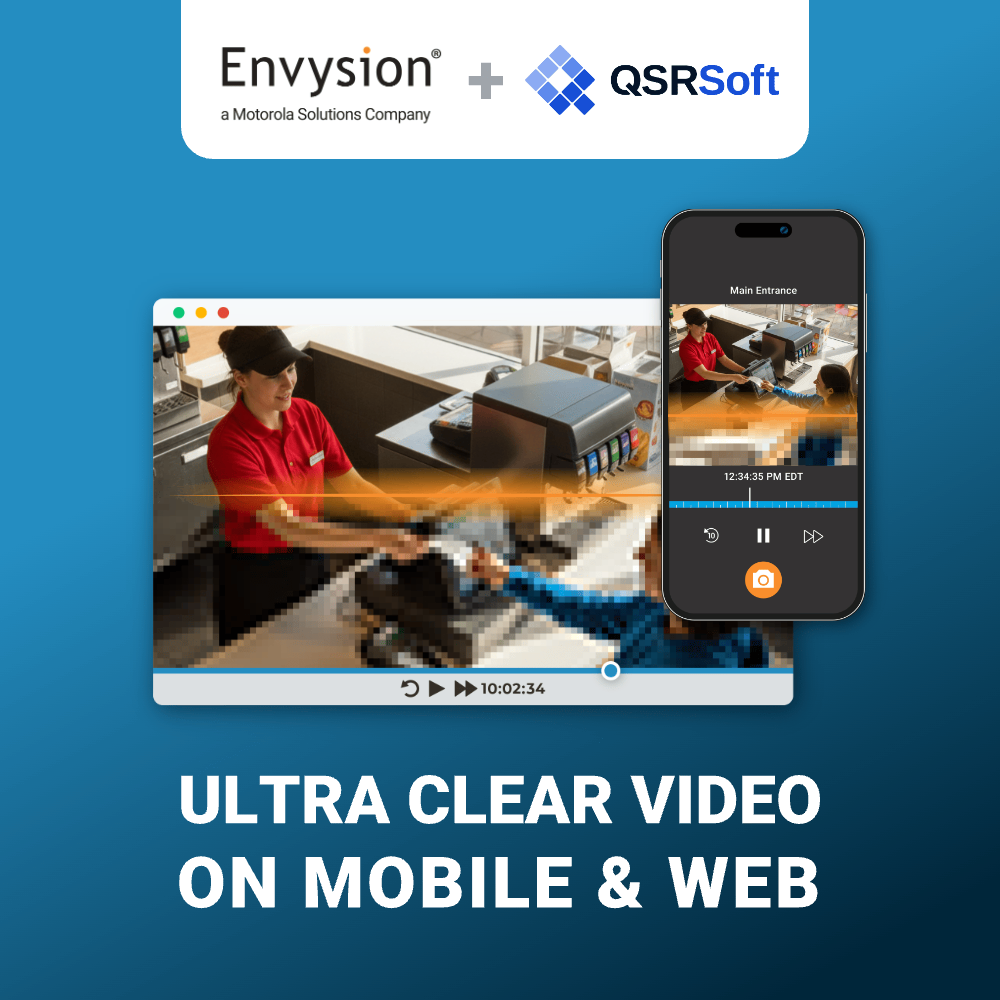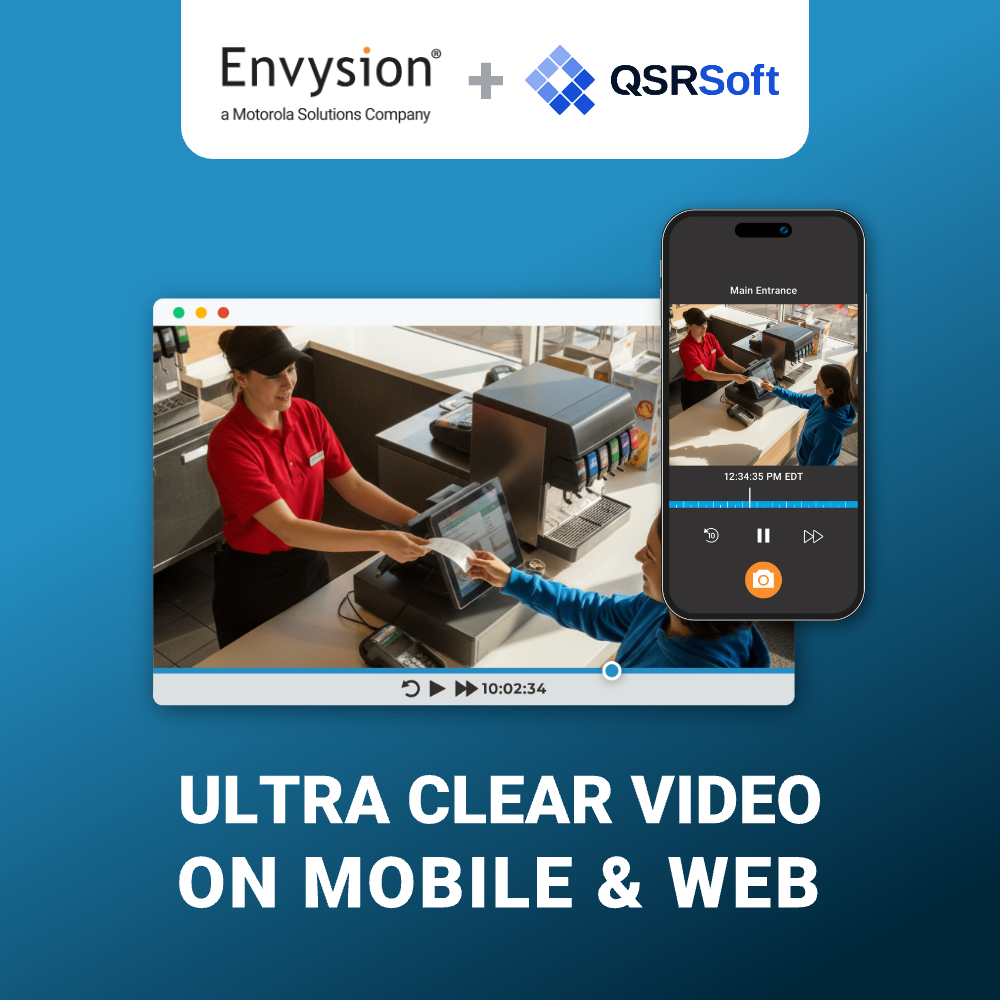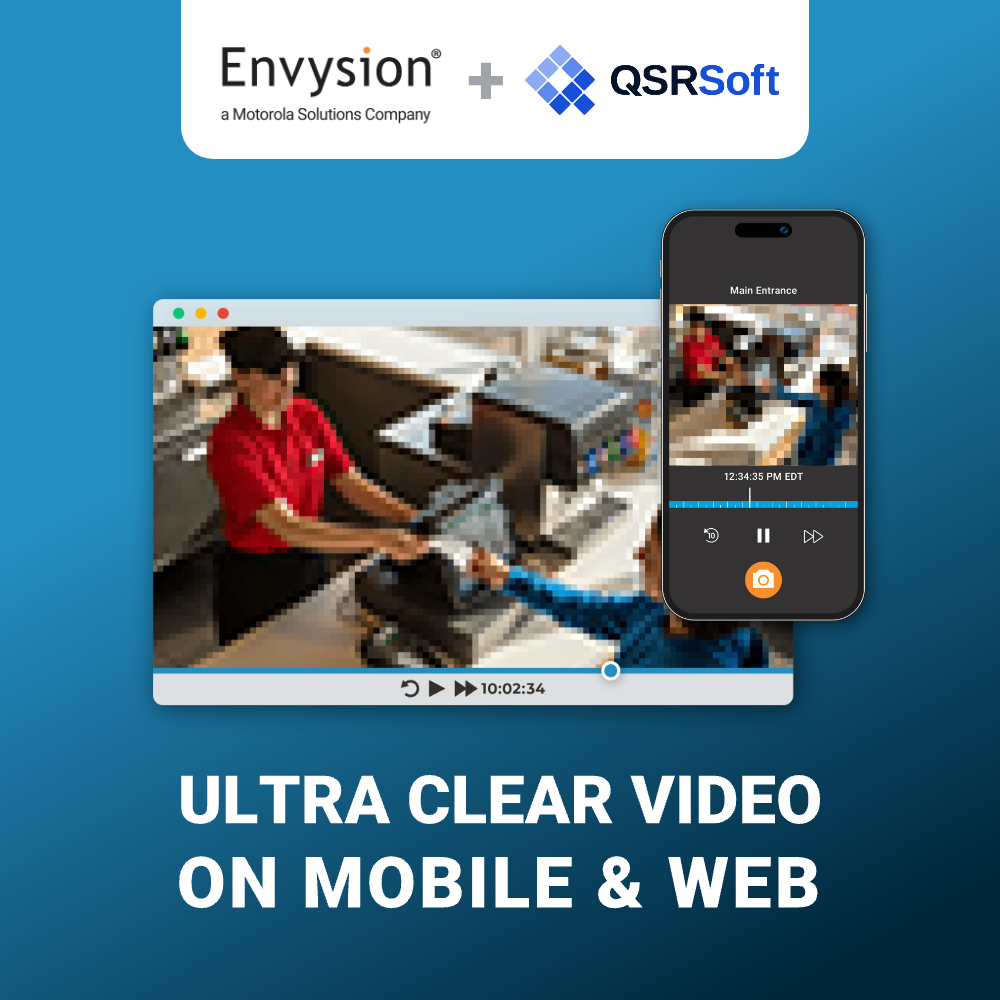
- Envysion, a Motorola Solutions CompanyRecorded 17 Sept 2026
Tired of blurry or hard-to-use security video?
- Envysion, a Motorola Solutions CompanyRecorded 17 Sept 2026
Upgrade your restaurant to meet National Restaurant Building and Equipment Standards with Envysion.
- LogpressoRecorded 17 Sept 2026
🚩로그프레소 CTI 신규 위협 분석 사례 - ‘법원 등기 수신’ 사칭 스캠 주의 최근 “법원등기 발송 예정인데 직접 수령 가능하신가요?”라며 접근한 뒤, 한글 도메인 접속을 유도해 피싱 페이지로 넘기는 음성 통화 기반의 사용자 응답 유도형 공격 (소셜 엔지니어링)이 빈번하게 관찰되고 있습니다. 사용자가 해당 링크에 접속 시 검찰청 사칭 화면으로 리디렉션되어 자격증명 등 민감정보 탈취로 이어지거나, 추가 악성코드 감염의 우려가 있어 각별히 주의를 요합니다. 링크에서 자세한 분석 내용을 확인해보시기 바랍니다. ✅ 전체 분석 보기: https://lnkd.in/g6XbTftv #로그프레소 #CTI #위협분석 #스캠 #피싱 #보이스피싱 #사이버보안 #SecOps
- LogpressoRecorded 17 Sept 2026
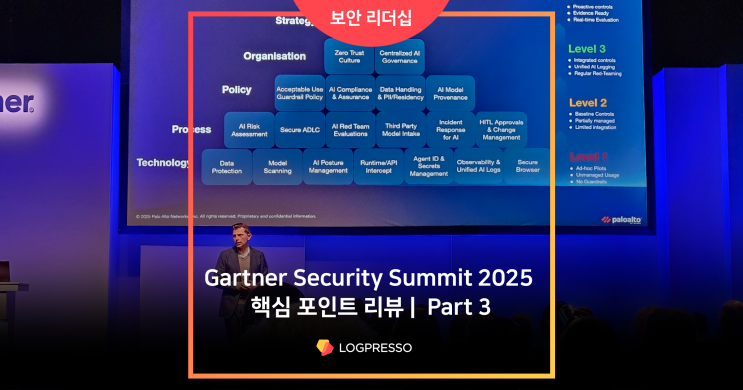
🧑🏻🏫 로그프레소의 Gartner Security & Risk Management Summit 2025 UK 참관기 3부에서는 ‘사이버보안과 AI’에 대해 다룹니다. 이번 서밋을 관통한 키워드는 단연 AI 였는데요. AI는 더 이상 보조가 아니라 핵심 도구가 되었고, 공격자도 방어자도 AI를 적극 활용하는 국면에 들어섰습니다. 이번 글에서는 아래 내용을 자세히 확인해보실 수 있으며, 다음 편부터는 AI 에이전트 도입, AI가 내재화된 보안 아키텍처, 방어·거버넌스 재설계, Human-in-the-loop와 AI 리스크 관리까지 이어갑니다. ✅ 생성형 AI가 바꾼 고도화된 공격 지형의 변화 ✅ 즉각적인 조치, 전략적 접근 각각의 관점에서 생성형 AI로 인한 위험을 줄이는 방법 ✅ 성공적인 AI 기반 자동화 SOC 전환 전략 📌 3부 전문 읽기: https://lnkd.in/gnF_z2Sb #로그프레소 #Gartner #AI보안 #SecOps #자율형SOC #거버넌스 #보안운영
- ElisityRecorded 17 Sept 2026
Elisity’s platform transforms existing network infrastructure into intelligent policy enforcement nodes, helping organizations accelerate Zero Trust maturity in weeks, not years.
- Ensign InfoSecurityRecorded 17 Sept 2026
Cloud threats evolve fast—your defences should evolve faster. Our latest eGuide breaks down how Zero Trust, threat-informed defence, and cloud-native controls can help you stay ahead. Learn how to integrate real-time detection, automation, and business-aligned strategies to secure today’s cloud—and tomorrow’s. Download the eGuide now to build securely, scale confidently, and respond intelligently.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.