On air · 2 of 3 networks
Escape
- escape.tech
- Cybersecurity
- US
- 77 employees
Escape’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 27. Watch Escape with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 6 | Checked 30 Oct 2026 | See all 27 ads → | ||
| Meta | Not checked | — | |||
| Running | 10 | Ads on the Google Ads Transparency Center | Checked 28 Oct 2026 | Collect them with the API → |
Escape has 6 live LinkedIn ads. We recorded 10 Google ads on 28 Oct 2026.
Latest ads
- LINKEDIN · IMAGESince 19 May 2026
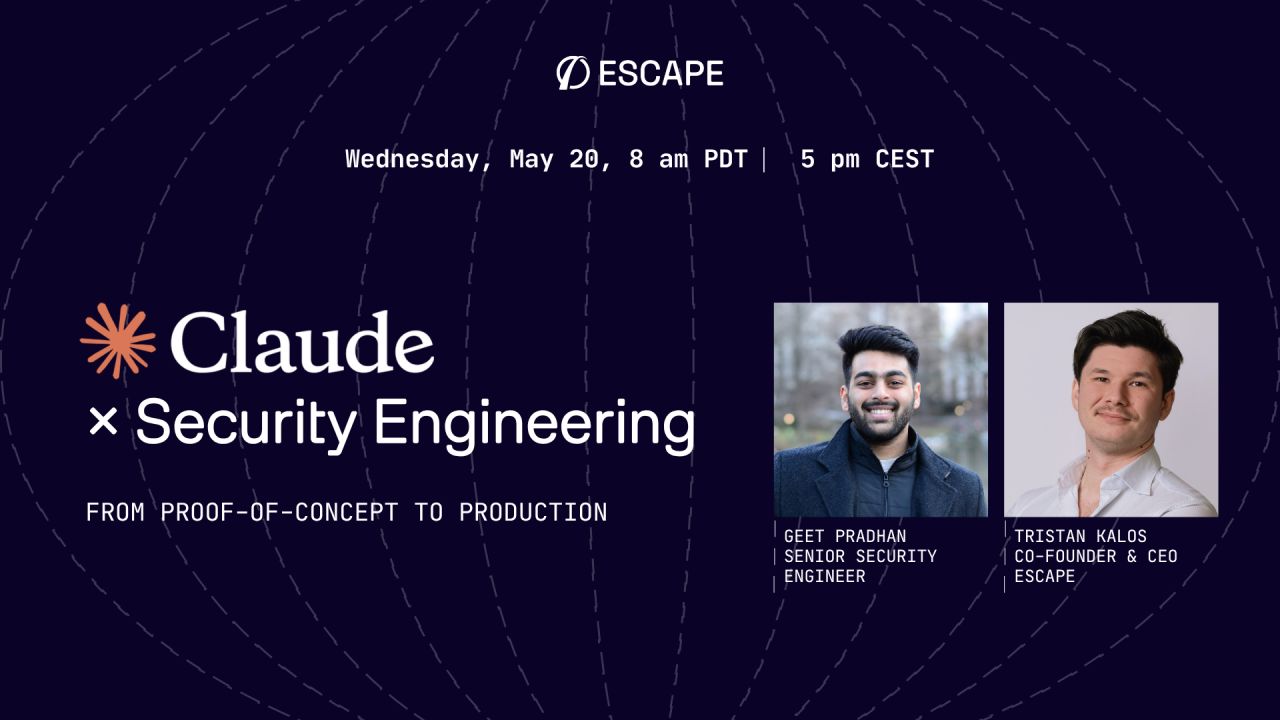
Everyone's talking about Claude in security. But how can we integrate it into Security Engineering workflows without token bankruptcy? Claude can do amazing things. But implementation can get real messy, real quick. Token economics matter. Workflow integration matters. Context management matters. Geet Pradhan has spent the last year watching how Claude fits into his organization’s security program. He’s built significant security automation internally and learned hard lessons about where AI actually helps vs. where it's hype. Join us for a live conversation as Geet breaks down the pragmatic path from proof-of-concept to production security. In Part 1: Building 0→1 Security Functions with Claude, Geet will cover: - What actually works in real ProdSec workflows - Where Claude genuinely changes how teams operate (and where it's just noise) - What Claude model to choose and when - Scaling security without proportional headcount, including examples of real operational workflows In Part 2, see directly from Escape’s CEO, Tristan Kalos, new Claude × Escape integration in action. We’ll show - How to connect Escape to Claude Desktop, Claude.ai, and Claude Code over a one-click OAuth 2.1. No API key copy-paste. - Discover your crown-jewel assets with ASM through simple prompting - Run human-grade pentests against them - Triage findings by adding your org’s context - And hand developers a clean remediation, all without leaving the assistant. If you want to move from "cool proof-of-concept" to "this is part of how we enable small security teams to scale security testing efficiently ", this webinar is for you. Don't miss this opportunity to learn from your peers and ask your questions live!
- LINKEDIN · IMAGESince 7 May 2026
"Claude Code is just hype" they said... Every model drop floods LinkedIn and Reddit with the same takes. I've been skeptical too. "We have created a monster" narrative has been used by AI labs at every major model release since GPT-2. Yet, I've watched security teams start shipping real workflows with Claude. Just keep in mind that there is a gap between the marketing and what actually works in production. So we're bringing in someone who's lived it. On May 20, Geet Pradhan, sr. Security Engineer, is joining me live to break it down: → Where Claude genuinely changes how security engineers operate → Which models are worth using and for what → Real practical examples (threat modeling, detection & response...) Then I'll show the new Escape × Claude integration live: One-click OAuth into Claude Desktop, Claude.ai, and Claude Code → discover crown-jewel assets via ASM → run human-grade pentests → triage with your org context → hand developers a clean remediation If you're trying to do more with a small team, link in the comments 👇
- LINKEDIN · IMAGESince 2 May 2026
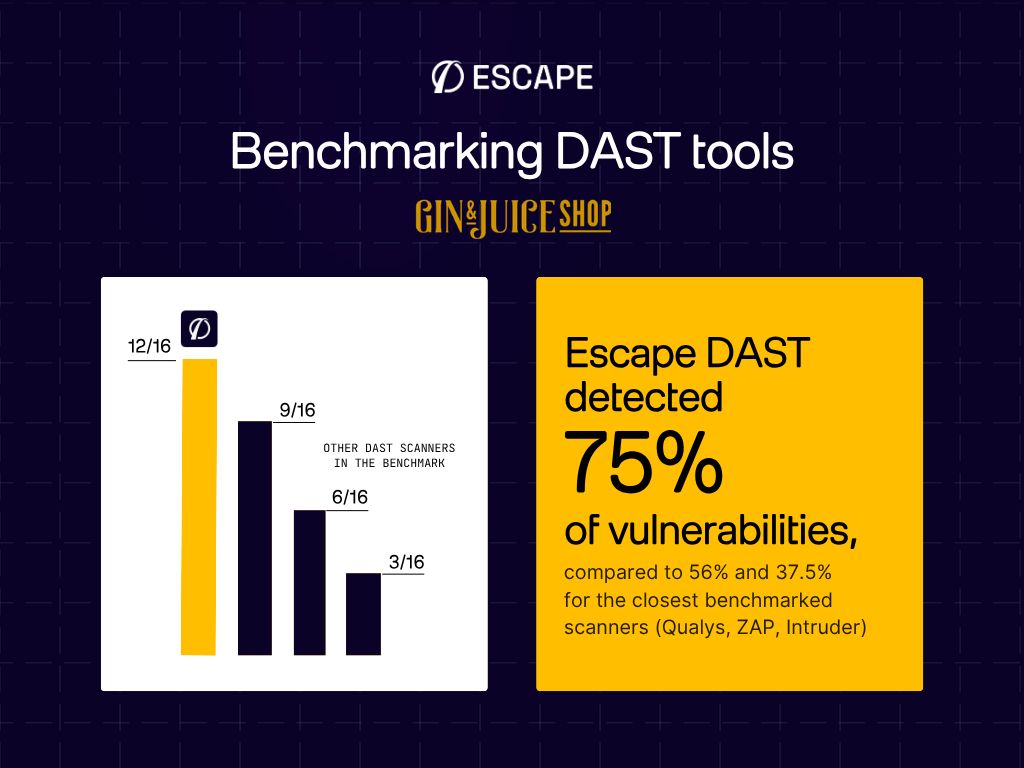
Tired of "DAST" scanners that just run generic payloads? We benchmarked Escape against industry-standard scanners (Qualys, ZAP, Intruder) on the Gin & Juice Shop. See how we stacked up on vulnerability detection, coverage, and noise.
- LINKEDIN · IMAGESince 1 May 2026
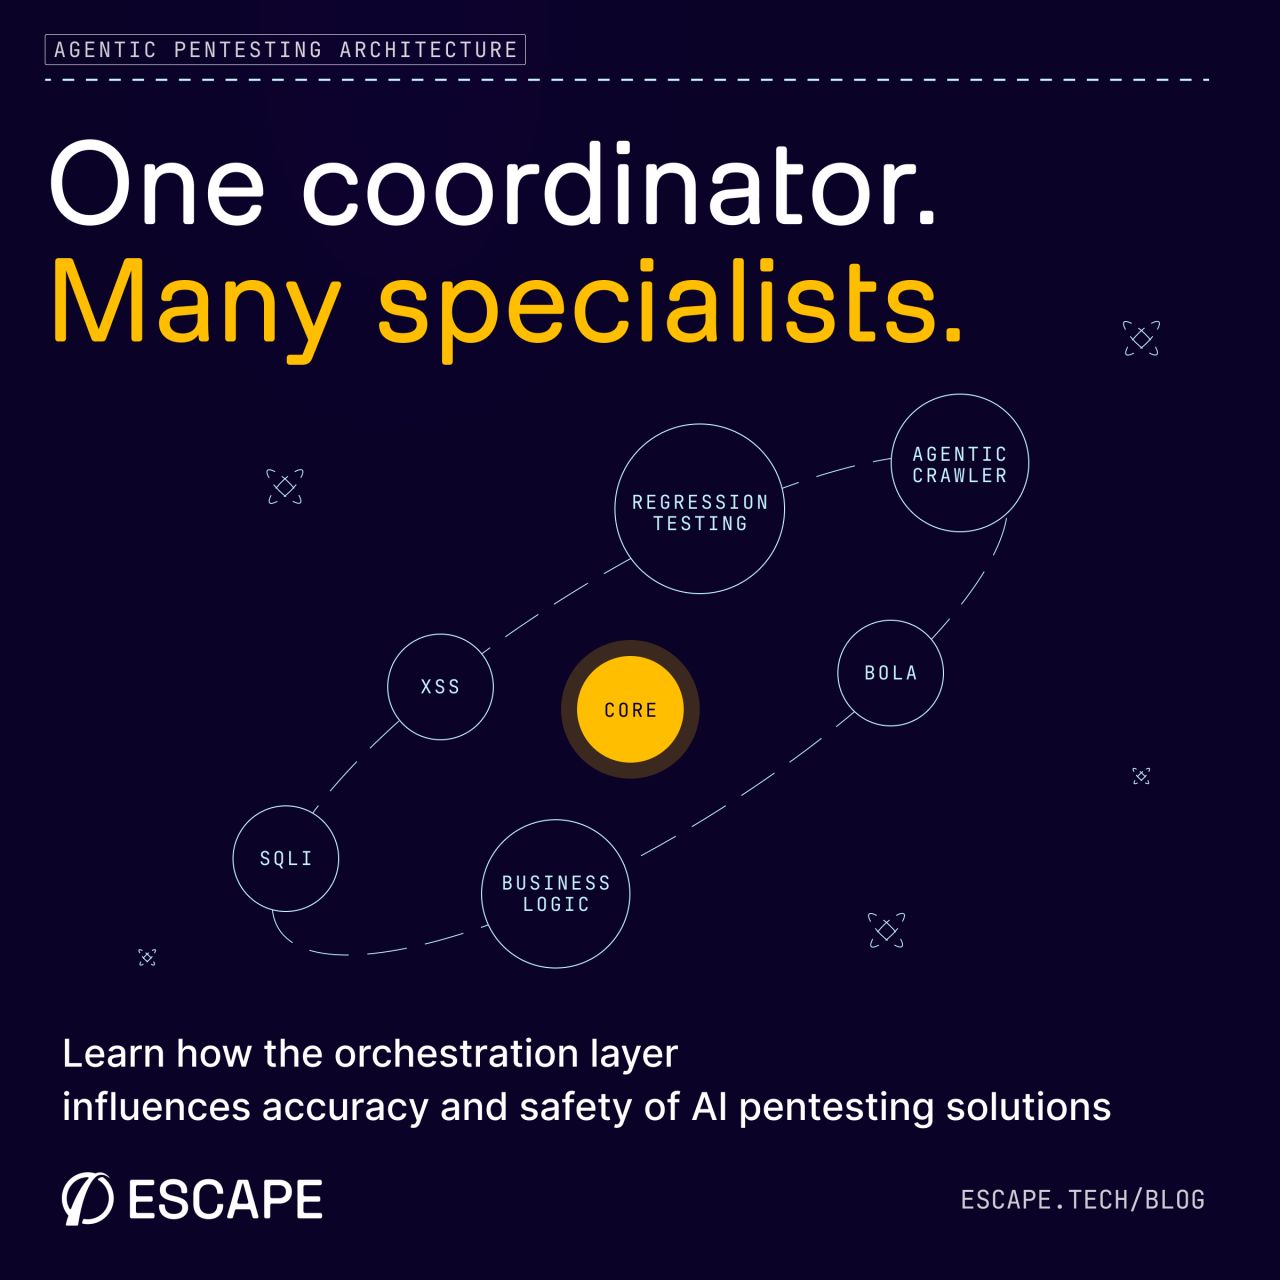
When evaluating AI pentesting tools, most people start with the model. We'd argue that shouldn't be the only point. In our recent benchmark, three different AI pentesting tools, all built on the same underlying model (DeepSeek v3.2), produced wildly different results on the same target: 6/20, 9/20, and 1/20 vulnerabilities found. Same model. Same target. A 9x gap in detection. The variable was orchestration: how each tool structures the agent's action loop, manages tool calls, and handles authentication. This is why we've spent so much time on the architecture behind our agents.. Starting with a coordinator that reasons about scope, specialized sub-agents that handle XSS, SQLi, BOLA, and business logic, and an intelligence layer that lets findings from one agent inform the next. We broke down how our multi-agent architecture works, what each specialist agent actually does, and where we still see limitations in the field in this article: https://lnkd.in/eSjzhF9b
- LINKEDIN · IMAGESince 1 May 2026
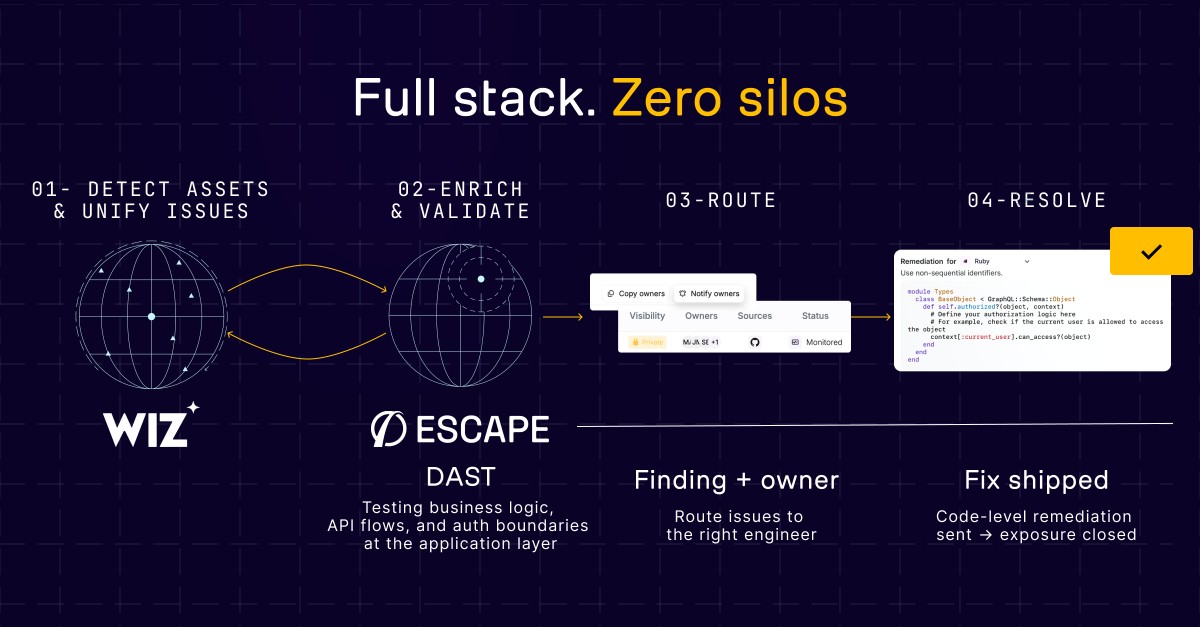
Escape integrates natively with Wiz to unify cloud and application findings in a single interface. Every API, SPA, and microservice Wiz exposes gets tested by Escape, with remediations assigned to the right team automatically.
- LINKEDIN · IMAGESince 1 May 2026
API security in silos creates blind spots. See how DoubleVerify unified their cloud-to-code security by integrating Escape with the Wiz Security Graph to discover, inventory, and secure thousands of APIs daily.
6 of 27 adsSign up to see every Escape ad, filter by format and date, and get alerts on new ones.
See all 27 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.