On air · 2 of 3 networks
Endor Labs
- endorlabs.com
- Cybersecurity
- US
- 215 employees
Endor Labs’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 946. Watch Endor Labs with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 151 | Checked 28 Oct 2026 | See all 946 ads → | ||
| Meta | Not checked | — | |||
| Running | 21 | Ads on the Google Ads Transparency Center | Checked 28 Oct 2026 | Collect them with the API → |
Endor Labs has 151 live LinkedIn ads. We recorded 21 Google ads on 28 Oct 2026.
Latest ads
- LINKEDIN · VIDEOSince 25 Sept 2026
I promised an end-of-week #Bali #offsite recap, so here we go. Tl;dr - 💯 worth the investment. 1. We came as colleagues across 8 countries, but left as 1 team: After my last post, lots of folks asked me how we could afford to take the whole team offline for a week. My answer: 1 week together makes the other 51 far more productive. We locked in clarity on the roadmap, team breakouts settled key technical decisions in hours instead of weeks of Slack threads, communication friction dropped, and trust got built face to face. Most importantly everyone left the offsite motivated to keep winning. 2. The Hackathon We periodically host Hackathons, but this was the shortest compared to our typical 2 day Hackathons. In 3 hours, empowered with any and all AI tools, teams built: • UI telemetry and feature flagging in-house, eliminating the need for a SaaS tool. • Creative new ways to prioritize a vulnerability backlog by real business and application impact. • A new dimension to how we attribute SCA reachability across private packages. Every project had one focus: making our customers' lives easier as they scale. Here's the recap 🎥
- LINKEDIN · IMAGESince 20 Aug 2026
Running untrusted JavaScript safely is one of the hardest problems in Node.js, and now a mainstream one, since AI agents and automation platforms run model- and user-generated code all day. isolated-vm is the library most of them reach for: 1M+ weekly downloads, relied on by n8n, Activepieces, Mastra, and Rocket.Chat to contain code they don't trust. Endor Labs researcher Cristian-Alexandru Staicu found a critical type confusion in it (GHSA-864f-rcv7-6rh4), a guest-to-host sandbox escape. From a single shared reference, the exploit goes from a controlled crash to hijacking the host's control flow. The interesting part is what didn't break. isolated-vm is built on a V8 Isolate, the same isolation Chrome uses between browser tabs, and that held. What failed was the C++ glue carrying data across the boundary. "The primitive is sound" isn't the same as "the library is safe", and the glue code is increasingly where sandbox escapes live. Maintainer shipped a fix fast; upgrade to 7.0.1 or 6.2.0. Full write-up: https://lnkd.in/eug6Fzi5 https://lnkd.in/eug6Fzi5 #AppSec #AISecurity
- LINKEDIN · VIDEOSince 19 Aug 2026
Endor Labs security researcher Peyton Kennedy audited seven of the most popular AI orchestration platforms: #NocoBase, #Flowise, #Langflow, #Dify, #Activepieces, #Kestra, and Apache #Airflow. He found 14 Critical and High severity vulnerabilities, including multiple instances where an unauthenticated user could trigger a prompt injection and remote code execution (RCE), resulting in data exfiltration. Every finding traces back to the same assumption: "anyone who can touch a workflow is trusted to run code on the host." Peyton presented the full research at DEF CON 34. Read more here: https://lnkd.in/eg8-U7JD #AISecurity #LLMSecurity
- LINKEDIN · IMAGESince 18 Aug 2026
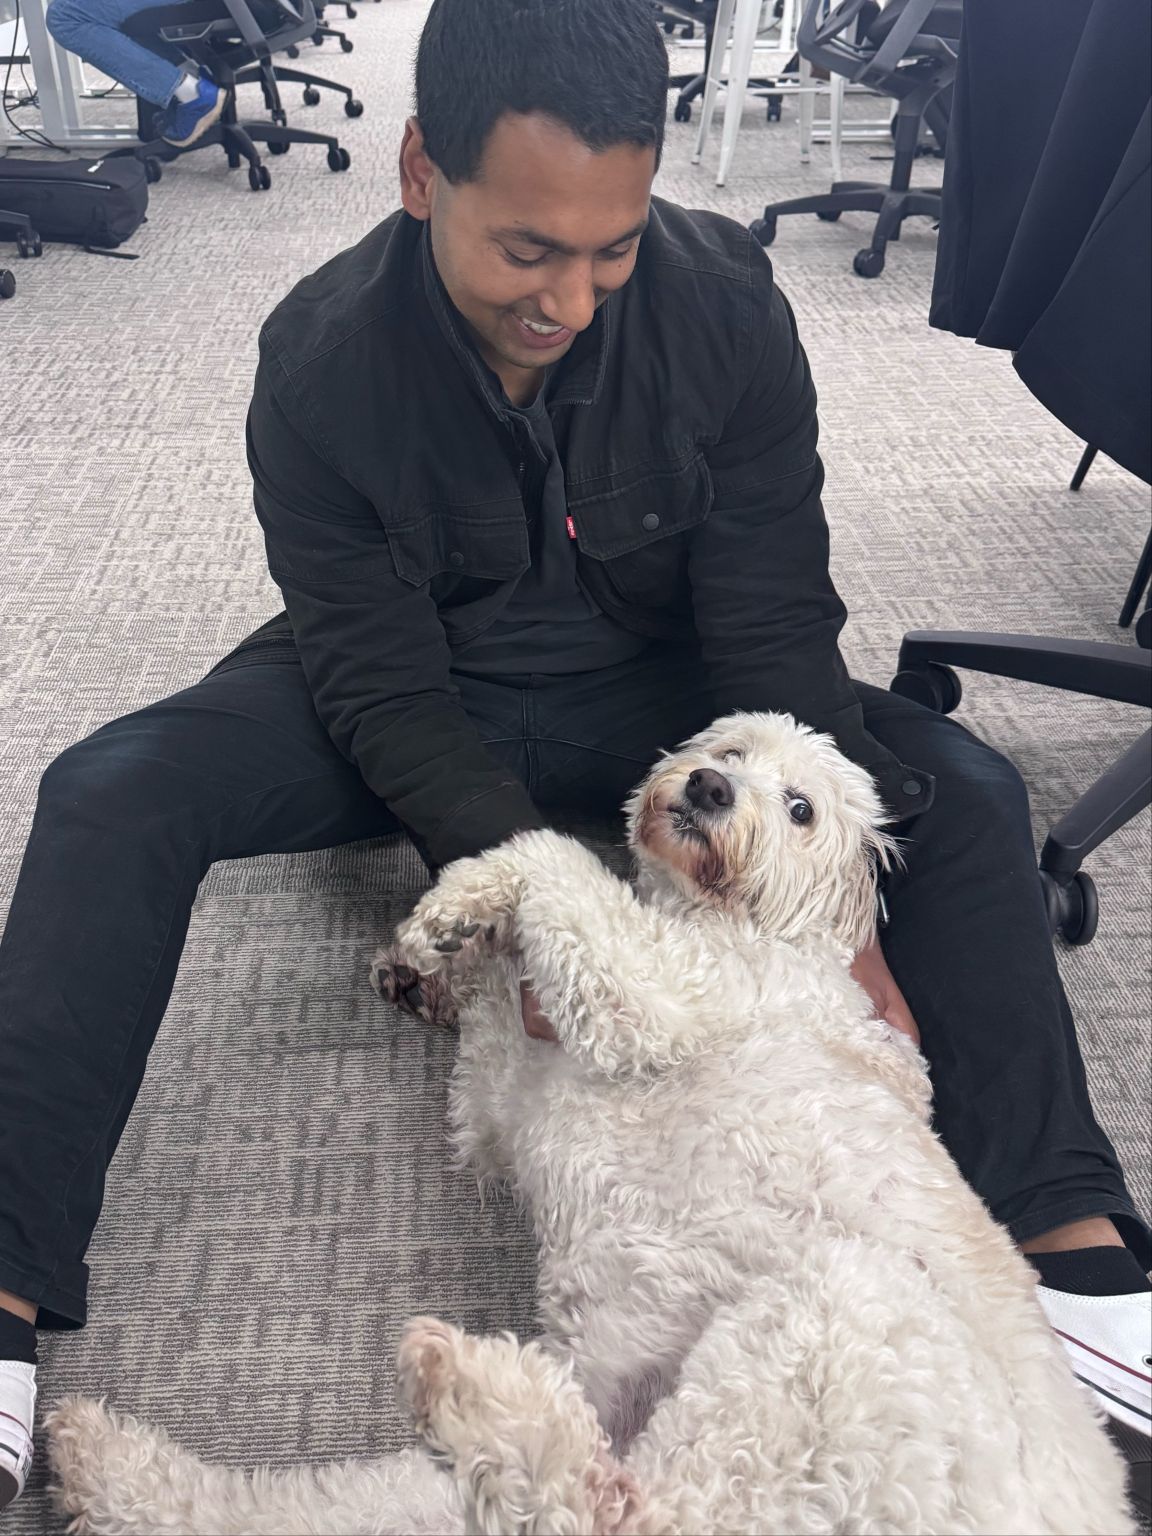
If mid-day puppy cuddles are your thing, we’re hiring across Engineering, Sales, and Marketing at our Palo Alto HQ. 🐶 Simba can never get enough belly rubs, so frankly, we need more hands. https://lnkd.in/gjccUH2Q
- LINKEDIN · IMAGESince 17 Aug 2026
‼️796 npm packages. 1,092 versions. ~20M weekly downloads compromised in one campaign. Shai-Hulud 2.0 and its 2026 successors all use the same opening move: a preinstall script that quietly downloads the Bun JavaScript runtime, then uses it to steal credentials. However, Bun isn't the villain here. It's fast, self-contained, and increasingly common in production stacks, Stripe, Notion, Linear, and now Anthropic all run it. That's exactly why attackers like it too: a different process name, and none of the hooks your Node monitoring relies on. 👀 Bun has legitimate uses, so blocking it outright may not be realistic. ✍ Blocking the install mechanism itself, the thing malware relies on to get onto the system, is more effective. Our latest breakdown covers the 5 controls that actually move the needle, starting with: - A minimum release age on dependency updates - An auditable allowlist for lifecycle scripts - Blocking known-malicious versions at install time Read the full breakdown 👉 https://lnkd.in/gB2vXmsa #SupplyChainSecurity #AppSec
- LINKEDIN · IMAGESince 4 Aug 2026
Endor Labs identified all 303+ packages and 500 versions in an active npm worm hitting the Cacheable/keyv ecosystem, infrastructure pulling 500M+ downloads a week. Median detection time: about 6 minutes. The payload runs through a malicious preinstall hook that downloads the Bun runtime and executes a Bun-compiled stealer. First detection: [email protected], flagged 8 minutes after publication. What it does: — Steals npm, GitHub, AWS, Kubernetes, and Vault credentials — Persists in developer tooling — Uses stolen npm tokens to publish the next wave of packages It spread by injecting tarballs into large npm orgs while preserving the original gitHead, so infected versions looked like normal publishes. Affected scopes include @servicetitan (100+ packages), @ornikar, @onereach, @hubsync, @picsart, and @qlik. If these packages are in your dependency tree: → Rotate npm, GitHub, and cloud credentials → Audit for unexpected package publishes → Pin to the last known clean versions Endor Labs mapped the full campaign across every affected org's npm scope. This is an active investigation and will be updated as we learn more, follow along at the blog link below. https://lnkd.in/e89kYEai
6 of 946 adsSign up to see every Endor Labs ad, filter by format and date, and get alerts on new ones.
See all 946 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.