LinkedIn image ad examples
1,339 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- ESET AustraliaRecorded 18 Sept 2026
Train employees to recognize cyber threats and keep your data safe with ESET.
- ESET North AmericaRecorded 18 Sept 2026
AI-driven attacks and zero-day exploits are targeting manufacturers. Learn why balancing prevention with detection is critical - and how MDR makes it possible.
- ESET North AmericaRecorded 18 Sept 2026
Did you know the average cost of a ransomware attack in 2024 was $4.91 million? Is your organization prepared to handle such a financial impact? What current security measures do you have in place to defend against these threats? See how to navigate ransomware in 2025 and learn more about effective strategies and solutions. Act now to protect your business with our fully automated ransomware prevention and remediation technology. Stay vigilant!
- NovaRed BrasilRecorded 18 Sept 2026
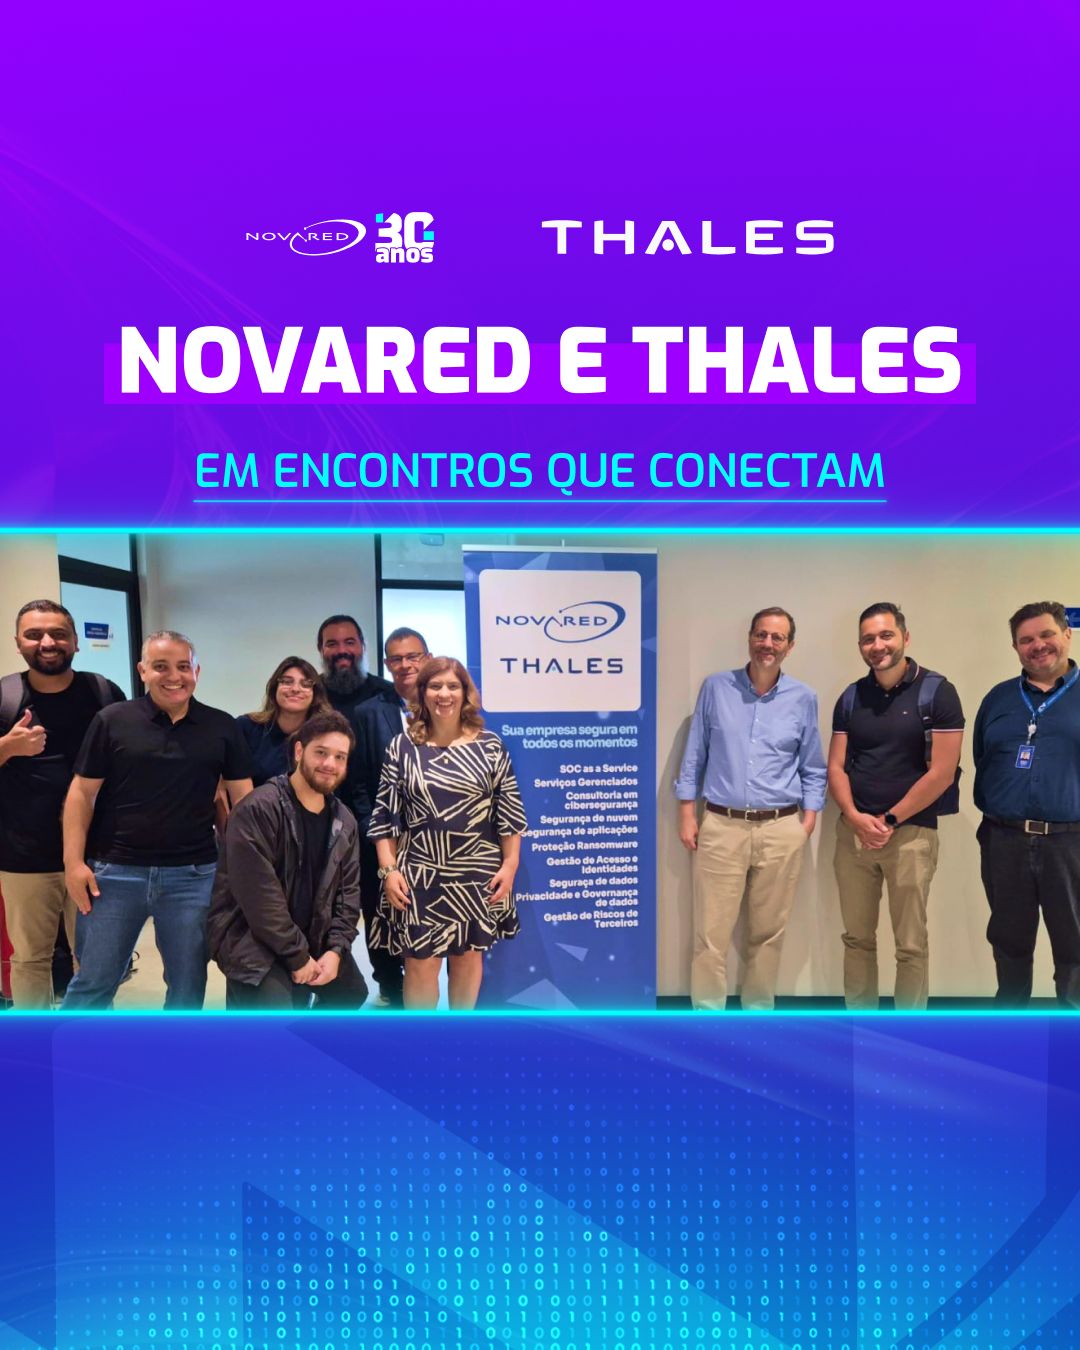
Na semana passada, abrimos nossas portas para conversas no nosso encontro exclusivo entre clientes e fornecedores. Um momento para aproximar quem constrói soluções e quem transforma essas soluções em resultado diariamente. Desta vez, contamos com a presença da Thales, representada por Jaqueline Lima e Bryan Rivera, que apresentaram soluções, compartilharam insights e participaram das conversas que tornaram o encontro ainda mais rico. Nada de palestras longas ou formalidade demais. Aqui, a proposta é justamente uma troca verdadeira para entender de perto desafios, mostrar tecnologias, ouvir dores reais e criar caminhos que façam sentido para o negócio. Obrigada a todos que estiveram com a gente. E que venham os próximos encontros, sempre com mais diálogo, mais inovação e, claro, mais colaboração. 🌟👥
- Entro SecuritySince 17 Mar 2026
Follow Entro Security for expert insights on the future of Agentic AI, NHI, and secrets security.
- ElasticitoSince 10 Apr 2026
Are you wondering how your Microsoft 365 environment stacks up against these new standards? 📅 Date: 15th April 2026 🕙 Time: 10:00 AM (London) 📍 Location: Live Webinar Save your seat: https://lnkd.in/d6kptaqC
- ElasticitoSince 10 Apr 2026
Webinar: Are you wondering how your Microsoft 365 environment stacks up against these new standards? 📅 Date: 15th April 2026 🕙 Time: 10:00 AM (London) 📍 Location: Live Webinar Save your seat: https://lnkd.in/d6kptaqC
- EquixlySince 21 Apr 2026
For complete application security, bring continuous penetration testing into your Checkmarx One environment. Join this webinar to discover how Equixly provides enhanced continuous offensive validation of your APIs and application logic. This joint solution strengthens your ability to identify exploitable risk and maintain confidence as your applications evolve. Secure your spot today.
- EquixlySince 21 Apr 2026
With Equixly, Checkmarx customers gain greater assurance across the full application lifecycle. You can correlate findings from source code to live exploitation paths, enabling more accurate prioritization and faster remediation. See how we do it.
- Entro SecuritySince 20 Apr 2026
Did you know? Every AI agent in your ecosystem relies on at least one Non-Human Identity (NHI) to access your data, tools, and cloud infrastructure. If you're only governing the agent's output, you're missing the engine driving it. Follow Entro Security for expert insights on Agentic AI, NHI, and secrets security. 👇
- EntrustSince 3 Mar 2026
Get the free Ponemon trends study to benchmark post-quantum readiness against global peers and identify the gaps to prioritize first.
- EntrustSince 3 Mar 2026
See what 4,000 global IT, security, and risk leaders report about PQ preparedness, crypto visibility, and rising operational pressure.
- EmpowerIDSince 30 Mar 2026
One week until our SAP IdM EOL session with Deloitte. If you're planning a migration from SAP Identity Manager, this is the session to attend. Learn what Deloitte recommends - current state, target state, and how to get there. 📗Whitepaper for attendees. Space is limited.
- EmpowerIDSince 31 Mar 2026
Privileged account compromised - can you tell the board who had access within SEC's 4-day window? Most teams need weeks. -->Download SEC cyber disclosure readiness checklist for identity governance
- EscapeSince 1 May 2026
API security in silos creates blind spots. See how DoubleVerify unified their cloud-to-code security by integrating Escape with the Wiz Security Graph to discover, inventory, and secure thousands of APIs daily.
- EscapeSince 1 May 2026
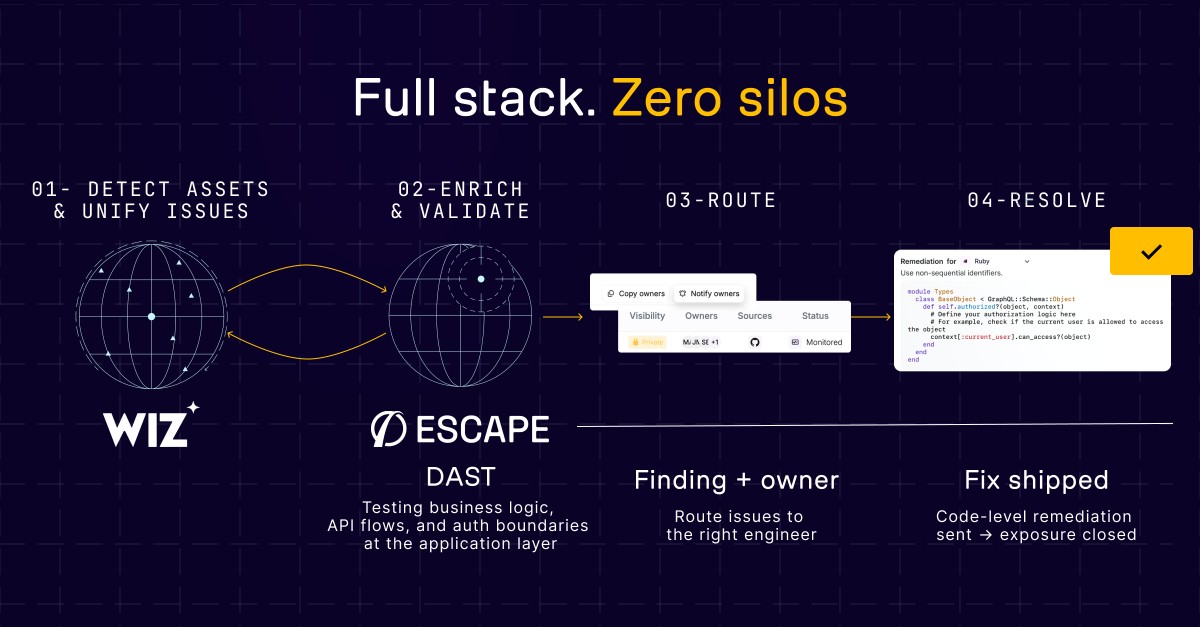
Escape integrates natively with Wiz to unify cloud and application findings in a single interface. Every API, SPA, and microservice Wiz exposes gets tested by Escape, with remediations assigned to the right team automatically.
- EfficientIPSince 2 Jun 2026
It's the time to conquer multi-cloud complexity and regain control of your infrastructure. Unlock actionable strategies from IDC in collaboration with EfficientIP to modernize your DNS, ensuring guaranteed operational efficiency and resilience. Download the IDC Spotlight.
- Endor LabsSince 4 Aug 2026
Endor Labs identified all 303+ packages and 500 versions in an active npm worm hitting the Cacheable/keyv ecosystem, infrastructure pulling 500M+ downloads a week. Median detection time: about 6 minutes. The payload runs through a malicious preinstall hook that downloads the Bun runtime and executes a Bun-compiled stealer. First detection: [email protected], flagged 8 minutes after publication. What it does: — Steals npm, GitHub, AWS, Kubernetes, and Vault credentials — Persists in developer tooling — Uses stolen npm tokens to publish the next wave of packages It spread by injecting tarballs into large npm orgs while preserving the original gitHead, so infected versions looked like normal publishes. Affected scopes include @servicetitan (100+ packages), @ornikar, @onereach, @hubsync, @picsart, and @qlik. If these packages are in your dependency tree: → Rotate npm, GitHub, and cloud credentials → Audit for unexpected package publishes → Pin to the last known clean versions Endor Labs mapped the full campaign across every affected org's npm scope. This is an active investigation and will be updated as we learn more, follow along at the blog link below. https://lnkd.in/e89kYEai
- Endor LabsSince 17 Aug 2026
‼️796 npm packages. 1,092 versions. ~20M weekly downloads compromised in one campaign. Shai-Hulud 2.0 and its 2026 successors all use the same opening move: a preinstall script that quietly downloads the Bun JavaScript runtime, then uses it to steal credentials. However, Bun isn't the villain here. It's fast, self-contained, and increasingly common in production stacks, Stripe, Notion, Linear, and now Anthropic all run it. That's exactly why attackers like it too: a different process name, and none of the hooks your Node monitoring relies on. 👀 Bun has legitimate uses, so blocking it outright may not be realistic. ✍ Blocking the install mechanism itself, the thing malware relies on to get onto the system, is more effective. Our latest breakdown covers the 5 controls that actually move the needle, starting with: - A minimum release age on dependency updates - An auditable allowlist for lifecycle scripts - Blocking known-malicious versions at install time Read the full breakdown 👉 https://lnkd.in/gB2vXmsa #SupplyChainSecurity #AppSec
- EfficientIPSince 19 Aug 2026
Download this checklist for 25 questions to ask before choosing your next DNS, DHCP and IPAM platform.
- Embed SecurityRecorded 17 Sept 2026
There’s no shared benchmark for alert investigation, and getting the right verdict is only part of the equation. A system can reach the right answer for entirely the wrong reasons. So we built our own evaluation system. Jeffrey Johns breaks down how we grade AI SOC analysts on three things: accuracy, consistency, and whether a senior analyst would endorse the reasoning. If you’re evaluating AI for your SOC, are you asking vendors how they measure all three? Read the blog: https://lnkd.in/gqYjZSHW #Cybersecurity #AI #SecOps
- Enginsight GmbHSince 11 Aug 2026
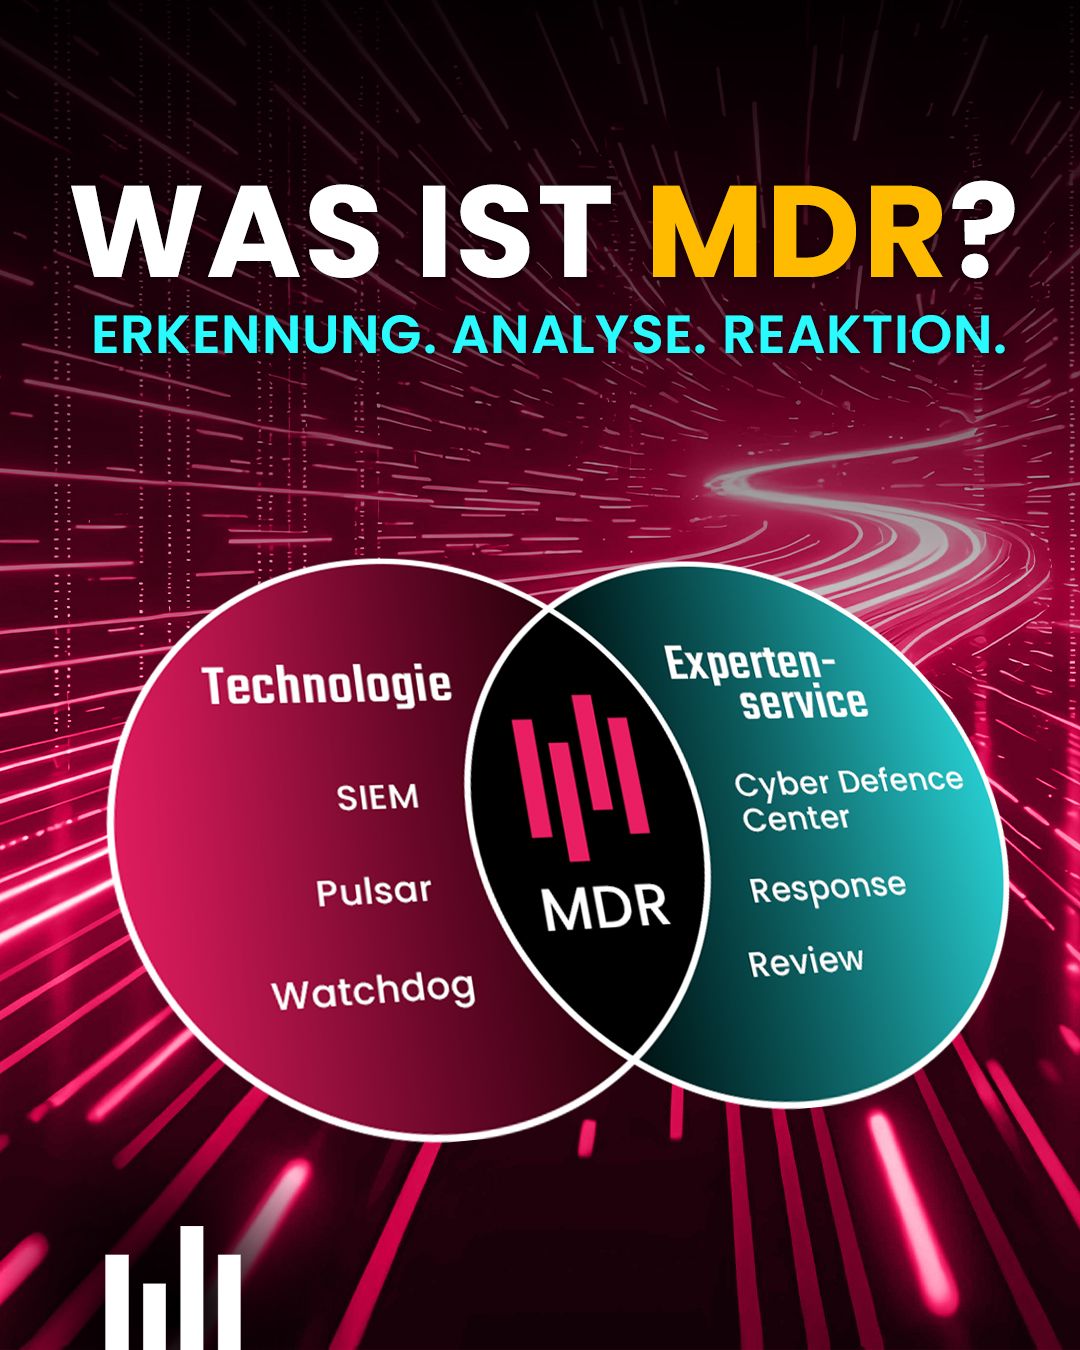
Ein SIEM sammelt und korreliert Logs. Die Bewertung bleibt bei Ihnen. Managed Detection and Response (MDR) setzt an dieser Stelle an: Technologie und ein Analystenteam, das die Alarme prüft, priorisiert und bei Bedarf eingreift. Bei Enginsight sind das Pulsar Agent, Watchdog und das eigene SIEM auf der technischen Seite und ein Cyber Defence Center in Deutschland auf der Serviceseite. Reaktion erfolgt automatisiert oder manuell, dazu kommen Reporting und regelmäßige Service Reviews. Der Vergleich, wann ein SIEM allein genügt und wann ein Service sinnvoller ist, steht auf unserer Übersichtsseite.
- Enginsight GmbHSince 11 Aug 2026
Zwei Nachtschichten pro Woche kann ein Team von drei Leuten nicht abdecken. Das ist keine Frage der Motivation. Unser Cyber Defence Center übernimmt die Überwachung außerhalb Ihrer Arbeitszeit. Wir arbeiten dabei mit Use Cases statt mit tausenden isoliert feuernden Einzelregeln: Ein Use Case bündelt mehrere Erkennungsregeln, Korrelationslogik und eine definierte Reaktion, abgestimmt auf Ihre tatsächliche Infrastruktur. Ein nächtlicher Zugriff aus einer anderen Zeitzone wird vorab als normal eingestuft und alarmiert nicht. Ein Admin-Konto, das angelegt und Minuten später gelöscht wird, alarmiert sofort. Je nach Paket etwa 50 oder etwa 150 kuratierte Use Cases über Endpunkte und Identitäten. Das SIEM (Security Information and Event Management) bleibt offen, Sie schließen eigene Datenquellen an und behalten vollen Einblick in Ihre Daten.
- EnStream LPRecorded 17 Sept 2026
When identities are blurred, fraud can slip through. @EnStream helps bring your real customers into focus with real-time mobile intelligence.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.