LinkedIn image ad examples
1,339 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- FocaldataRecorded 19 Sept 2026
Uma falha crítica de segurança foi descoberta em dispositivos que utilizam as VPNs da série AG da Array Networks, permitindo ataques baseados em injeção de comandos. Os invasores exploram essa vulnerabilidade para instalar web shells e criar usuários não autorizados, abrindo caminho para o controle remoto dos sistemas afetados. Embora a Array Networks tenha lançado uma correção em maio, o problema continuou difícil de rastrear porque a empresa não atribuiu um identificador oficial à falha no momento da atualização. Isso prejudicou a visibilidade sobre o alcance real da vulnerabilidade e a capacidade de monitorar sua exploração ao longo do tempo. A situação ganhou gravidade após o alerta emitido pela JPCERT, agência de resposta a emergências cibernéticas do Japão, que identificou ataques direcionados a organizações japonesas desde agosto. Os cibercriminosos estavam executando comandos para inserir web shells escritos em PHP nos dispositivos vulneráveis, obtendo assim controle total dos servidores comprometidos. As investigações mostraram ainda que a falha afeta modelos AG 9.4.5.8 e anteriores e está ligada ao recurso “DesktopDirect”, que oferece acesso remoto — funcionalidade muito usada no meio corporativo. Essa facilidade amplia o risco, já que empresas podem ter grande quantidade de dados sensíveis expostos. Por isso, o JPCERT recomendou desativar o DesktopDirect e aplicar filtros de URL até que novas atualizações sejam disponibilizadas. Até o momento, a Array Networks não se pronunciou oficialmente sobre os ataques nem confirmou se uma nova correção será lançada, deixando usuários e empresas em alerta enquanto aguardam orientações mais claras sobre como mitigar o problema de forma definitiva. Focaldata. Tudo Está Conectado. www.focaldata.com.br #cibersegurança #fortinet #infoblox #trendmicro #gigamon #crowdstrike #segura #transmitsecurity #vigilant #zadara #paloalto #f5 #cloud4wi #acronis #culturadeprevenção #posturadeprevenção
- Field EffectRecorded 19 Sept 2026
MSPs need threat response that’s fast and business-friendly. Explore how configurable active response levels let MSPs defend faster while avoiding dreaded shutdowns.
- ExpelSince 10 Apr 2026
Your SOC is only as strong as the data behind it. Our SOC KPIs template helps you track incident response times, workload efficiency, and detection accuracy—giving you the visibility needed to improve security operations and reduce risk. Get the insights you need to measure, track, and optimize SOC performance. Download the free template now.
- ExpelSince 12 Apr 2026
Security tools generate alerts. Expel turns them into action. Get 24×7 monitoring, AI-powered investigation, and actual remediation with a 14-minute MTTR on critical and high incidents.
- EthiackSince 20 Aug 2026
European CISOs, stop pretending it's about quality "We don't buy European cyber because the quality isn't there." How convenient. In many categories, European vendors are: - Cheaper - More responsive - More flexible - Closer to your regulatory reality - More aligned with NIS2, DORA, EU frameworks - With a similar or superior product quality Yet they still lose. Why? Because: - You default to American/Israeli brands - You trust marketing more than results - You outsource thinking to analysts - You confuse market share with technical superiority And in cyber, that's dangerous. When your entire security stack is non-European, you are not sovereign. And neither is your country. You are dependent. Vulnerable. Exposed. Dependency is not neutral. It affects: - Pricing power - Strategic leverage - Data exposure - Political pressure - Long-term innovation capacity This is not anti-American or Israeli. This is pro-European responsibility. If you are an European CISO and you never consider European vendors, you're part of the problem. Digital sovereignty will not be solved by politicians and bureaucrats. It will be solved by procurement decisions. It will be solved by you. Do you actually benchmark European tech? Or do you just assume it's inferior? Be honest. *Here is a pic of me talking at ENISA, so that my point stands stronger.
- F9C SecurityRecorded 18 Sept 2026
Da apropriação de contas (ATO) a golpes em Pix, cartões e engenharia social, proteger as operações exige visibilidade, inteligência e capacidade de resposta em tempo real. Conheça como a F9C Security ajuda instituições financeiras e empresas de meios de pagamento a fortalecerem sua prevenção a fraudes.
- F9C SecurityRecorded 18 Sept 2026
A prevenção a fraudes precisa proteger as operações sem gerar impactos para clientes e equipes. Conheça uma abordagem inteligente para identificar diferentes tipos de fraude, reduzir falsos positivos e fortalecer a segurança das operações de pagamento. Saiba mais abaixo e receba um contato inicial do nosso Time!
- FencerSince 23 Jun 2026
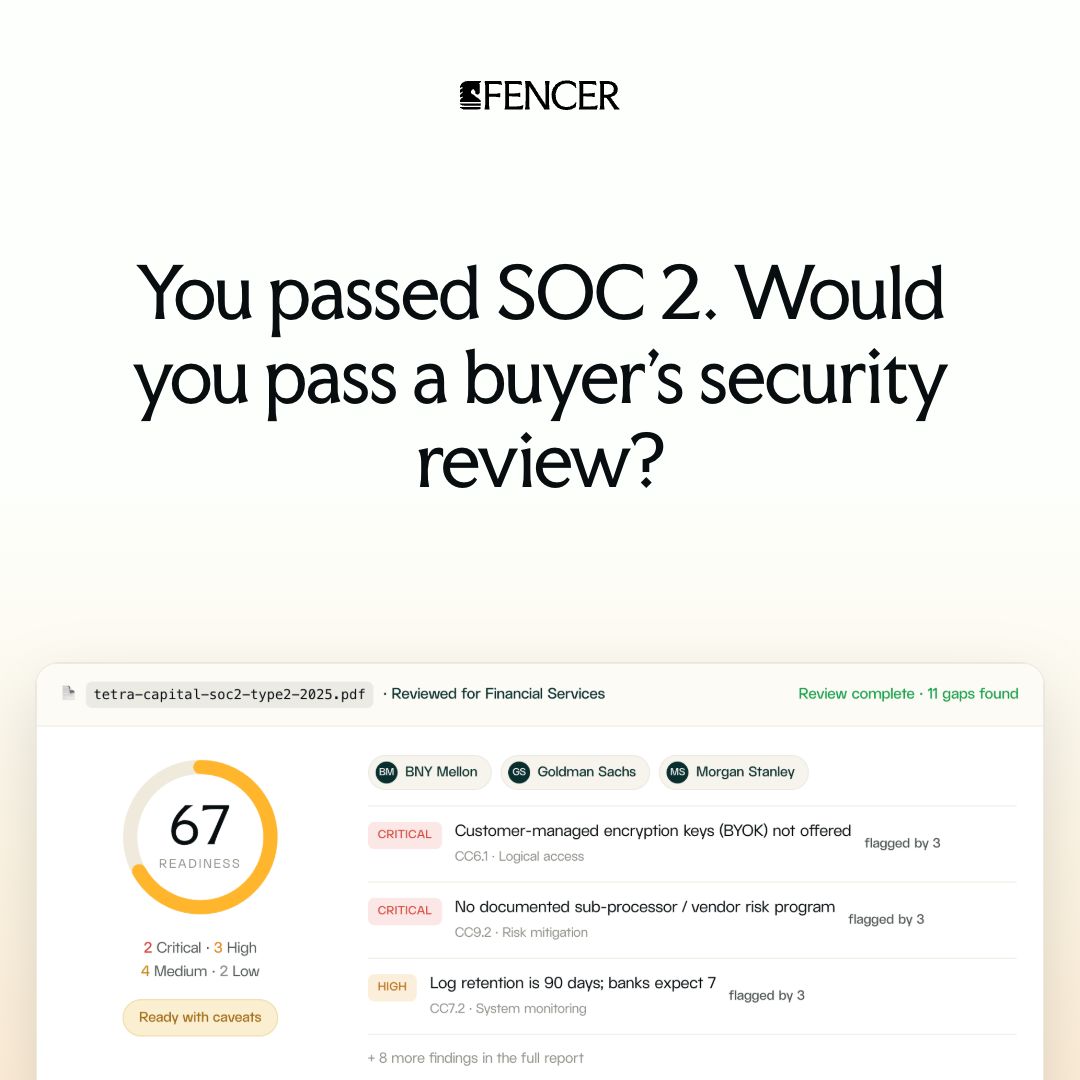
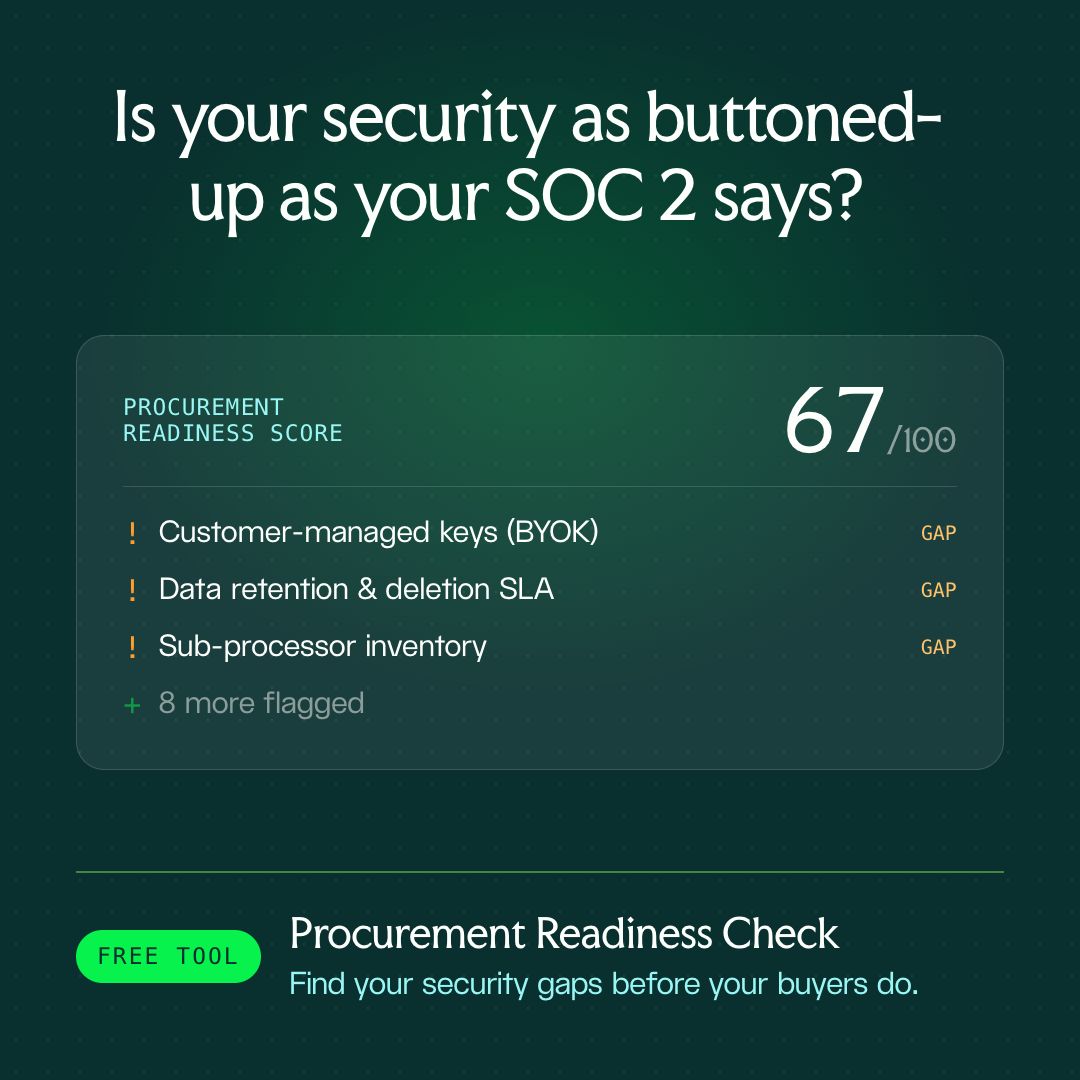
One enterprise security review can add a month to a deal. A free, 90-second check shows what a buyer's security team would flag in your SOC 2 before it stalls a deal.
- FencerSince 23 Jun 2026
One enterprise security review can add a month to a deal. A free, 90-second check shows what a buyer's security team would flag in your SOC 2 before it stalls a deal.
- ExaforceSince 1 Jul 2026
The SOCtors are officially in practice. Exaforce is coming to Black Hat 2026 with something the show floor has never seen: a full SOCtors' Office where AI agents detect, triage, investigate, and respond - live, on real scenarios. Walk in with your biggest SOC headache. Leave with a prescription. Booth 4144. Book your appointment at the link.
- ExaforceSince 1 Jul 2026
Your SOC needs a second opinion. Intake notes: overwhelmed analysts, unresolved alerts, 3am pages for threats that weren't. Prognosis: fixable. The Exaforce SOCtors are coming to Black Hat 2026 with a full team: four AI specialist Exabots, live demos, and a personalized prescription for a healthier SOC. Booth 4144. Reserve your spot: https://lnkd.in/gBRDcw9k
- ESET FranceSince 3 Jul 2026
Et si votre équipe IT ne pouvait plus tout gérer seule ? Dans CTRL+S, retour d'expérience sur le passage à une cybersécurité managée.
- ESET FranceSince 3 Jul 2026
EDR, MDR et XDR : derrière les acronymes cyber, des choix qui impactent directement votre sécurité. CTRL+S vous aide à y voir clair.
- FalkorSince 12 Aug 2026
You have the data. But do you have the full story? 🧩 📱 In digital forensics, getting the data is not the hardest part anymore. Understanding it is. AI helps analysts turn large amounts of data into clear timelines, faster insights, and stronger case stories. From too much data to clear action. See how AI supports forensic analysis. https://lnkd.in/gQszcA3D
- FalkorSince 12 Aug 2026
🍞 + 🍓 Some things work better together. The same is true in investigations. When forensic data, OSINT, internal case data, and external intelligence remain in separate systems, critical signals are easier to miss and investigations slow down. Our latest article explores why combining data sources matters — and how data fusion helps investigators uncover hidden relationships, enrich forensic artifacts, and turn fragmented evidence into actionable intelligence. Read the full article: https://lnkd.in/gDAXwEXz
- ESET Česká republikaSince 25 Aug 2026
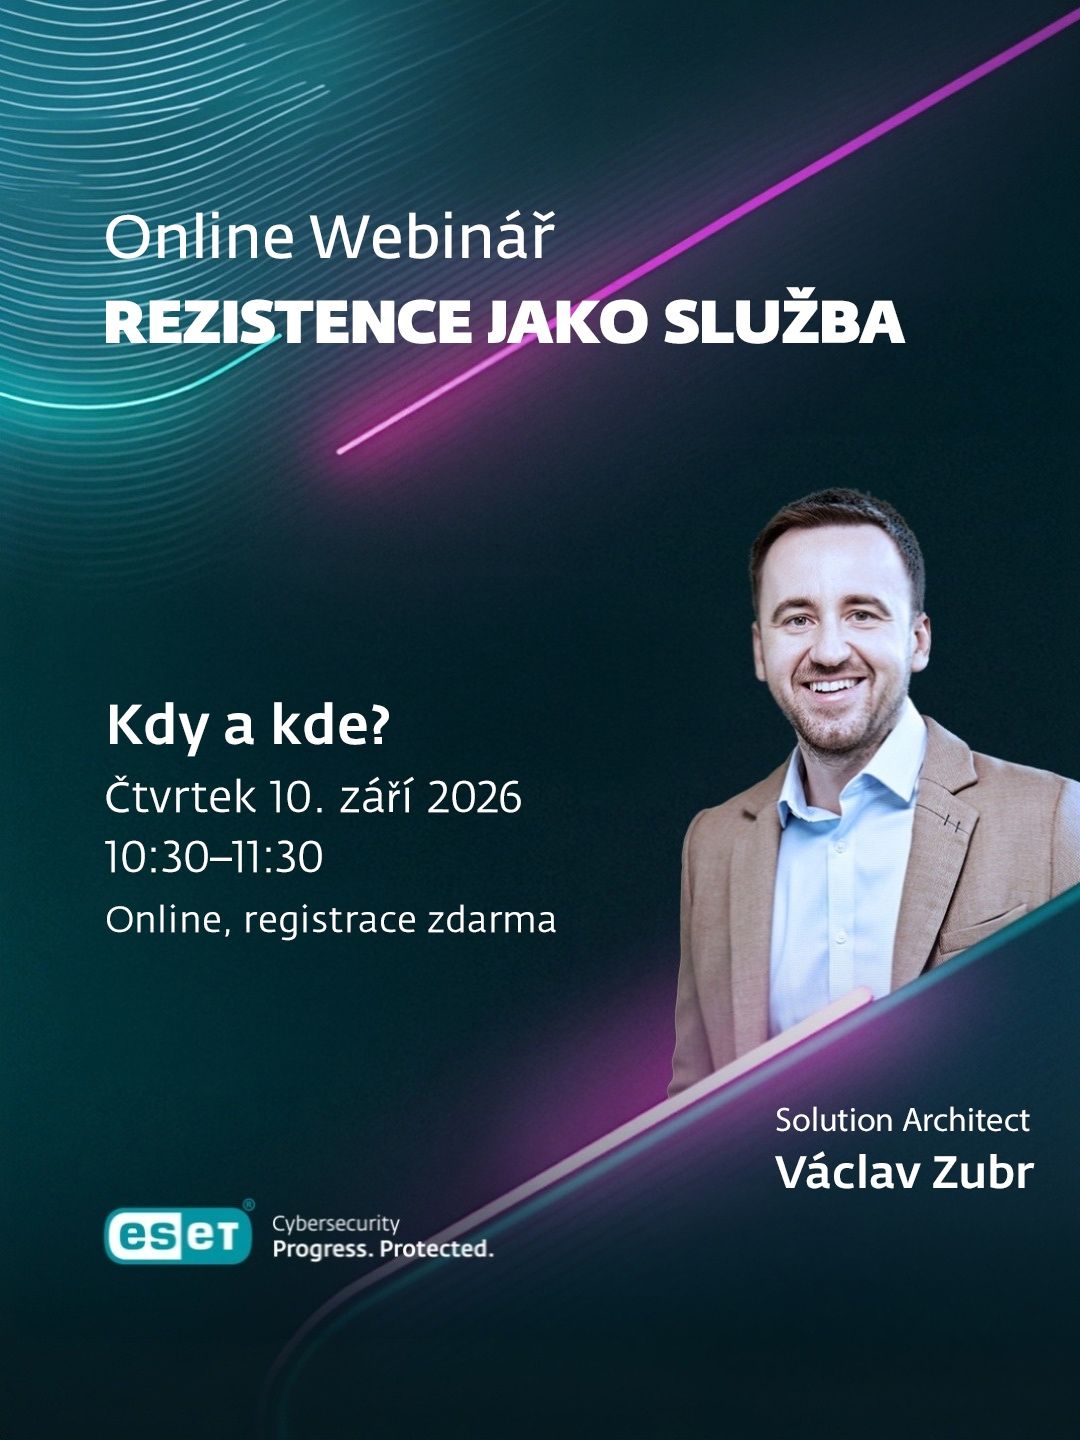
Kdo hlídá vaši firmu, když váš IT tým spí? 🌙 Zjistěte na našem bezplatném webináři, jak funguje nepřetržitý kybernetický dohled MDR. 🛡️ Připojte se 10. 9. 2026 v 10:30 a registrujte se zdarma zde: https://lnkd.in/d-2egMCw
- ESET East AfricaRecorded 18 Sept 2026
Overwhelmed by cyberthreats? ESET defends against real threats and flags the false ones so you can grow your business. ESET security experts are here to help you. Request a demo.
- ExeinSince 9 Sept 2026
AI’s latest models have everyone talking. But when AI operates inside machines and infrastructure, its attack surface also becomes physical. That changes what security teams need to protect and where they need to look for risk. We break down the Physical AI threat model at the link.
- ExeinSince 9 Sept 2026
An attacker skipped password verification, gained Administrator privilege and tried to replace /etc/shadow. One Photon rule blocked the atomic rename before it landed. The password never changed, and the attacker received no signal that runtime protection had intervened.
- ESET East AfricaRecorded 18 Sept 2026
Your enterprise customers need trusted cybersecurity and your business needs the right partner to help you deliver it. Partner with ESET to expand your security portfolio with enterprise-grade solutions, global expertise and dedicated local support. Grow your enterprise business with a cybersecurity partner invested in your success. Become an ESET Partner: https://lnkd.in/eCjUsNZZ #ESET #Cybersecurity #ProgressProtected #BecomeAPartner
- ESET PolskaSince 15 Sept 2026
🧹 Kiedy ostatnio zrobiłeś cyfrowe porządki? Stare aplikacje, nieużywane konta, zapomniane dostępy… Z czasem może ich uzbierać się naprawdę sporo. A każde niepotrzebne konto czy aplikacja to kolejny potencjalny punkt wejścia dla cyberprzestępcy. Dlatego warto co jakiś czas zrobić szybki przegląd: 🔐 usuń nieużywane aplikacje, 🔐 zamknij stare konta, 🔐 odbierz niepotrzebne uprawnienia, 🔐 sprawdź, gdzie nadal jesteś zalogowany. Kiedy ostatnio zrobiłeś taki przegląd? Zareaguj 👇 👍 Regularnie robię porządki ❤️ Nie pamiętam…
- Evalian®Since 17 Sept 2025
I often hear from organisations that they assume they are secure simply because they have not experienced a known cyber incident. In reality, once we begin onboarding and conducting proactive threat hunting and continuous monitoring, it is common to uncover indicators of attacker persistence or potential insider activity. Having the right security tools and baseline configurations in place does not guarantee protection. Without continuous monitoring, tailored detection logic, and proactive investigation, malicious activity often goes unnoticed. To help organisations evaluate SOC providers, we have created a checklist designed to prompt the right questions, such as: • Do they provide continuous 24/7 monitoring and response across your environment? • Can they deliver custom integrations to support unique and complex environments? • How frequently are detections and rules tuned to your specific environment? • Do they proactively hunt for threats, or do they rely solely on automated alerts? Download our SOC provider checklist and use it to benchmark potential providers: https://lnkd.in/dVDwRt2B #SOC #CyberSecurity #SOCaaS #MDRsolutions #Security #Infosec #Cyber #SecurityOperations #ManagedSecurity #DefensiveSecurity
- EvinaSince 7 Oct 2025
2025 is a pivotal year for iGaming. Between evolving regulations and rapid innovation, the ecosystem is being redefined. For payment aggregators, these forces are setting new benchmarks for growth and responsibility. To help you lead the market, we've created a guide to the 10 crucial trends that will make the difference. This guide covers: - How to anticipate new regulatory requirements to protect players. - How to manage the risks of instant payments to gain a competitive advantage. - Why legacy testing methods are now obsolete and must be replaced by AI. 👉 Download the guide and build your strategy to lead the market in 2026.
- FacephiSince 2 Oct 2025
📣 Facephi will be at Money20/20 Las Vegas. Want to see how our technology stops digital fraud before it happens? Book a 1:1 meeting with our team and discover our solutions in action. 👉 Reserve your spot today and meet us at Booth 17055. https://lnkd.in/dFTwZ_S8
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.