LinkedIn image ad examples
3 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- Grupo NTSecSince 21 Aug 2025
Nuestra experiencia protegiendo a grandes empresas brasileñas está ahora al servicio de su negocio en España. Consultoría, monitorización y respuesta a incidentes con tecnología de vanguardia y un equipo altamente especializado. Conozca nuestro porfolio y descubra cómo podemos proteger su empresa: https://lnkd.in/d_6BABeV
- Grupo NTSecSince 21 Aug 2025
Somos el Grupo NTSec: referencia en soluciones de ciberseguridad que combinan tecnología avanzada con un soporte especializado. Llegamos a España para ofrecer protección total frente a las amenazas digitales. Conozca nuestro porfolio completo: https://lnkd.in/d_6BABeV
- GuidePoint SecurityRecorded 22 Sept 2026
With 80% of breaches involving identity takeovers, can your IAM program withstand today's threats?
- GuidePoint SecurityRecorded 22 Sept 2026
Identity is not just about access—it's about securing your entire business." Discover the identity-first approach.
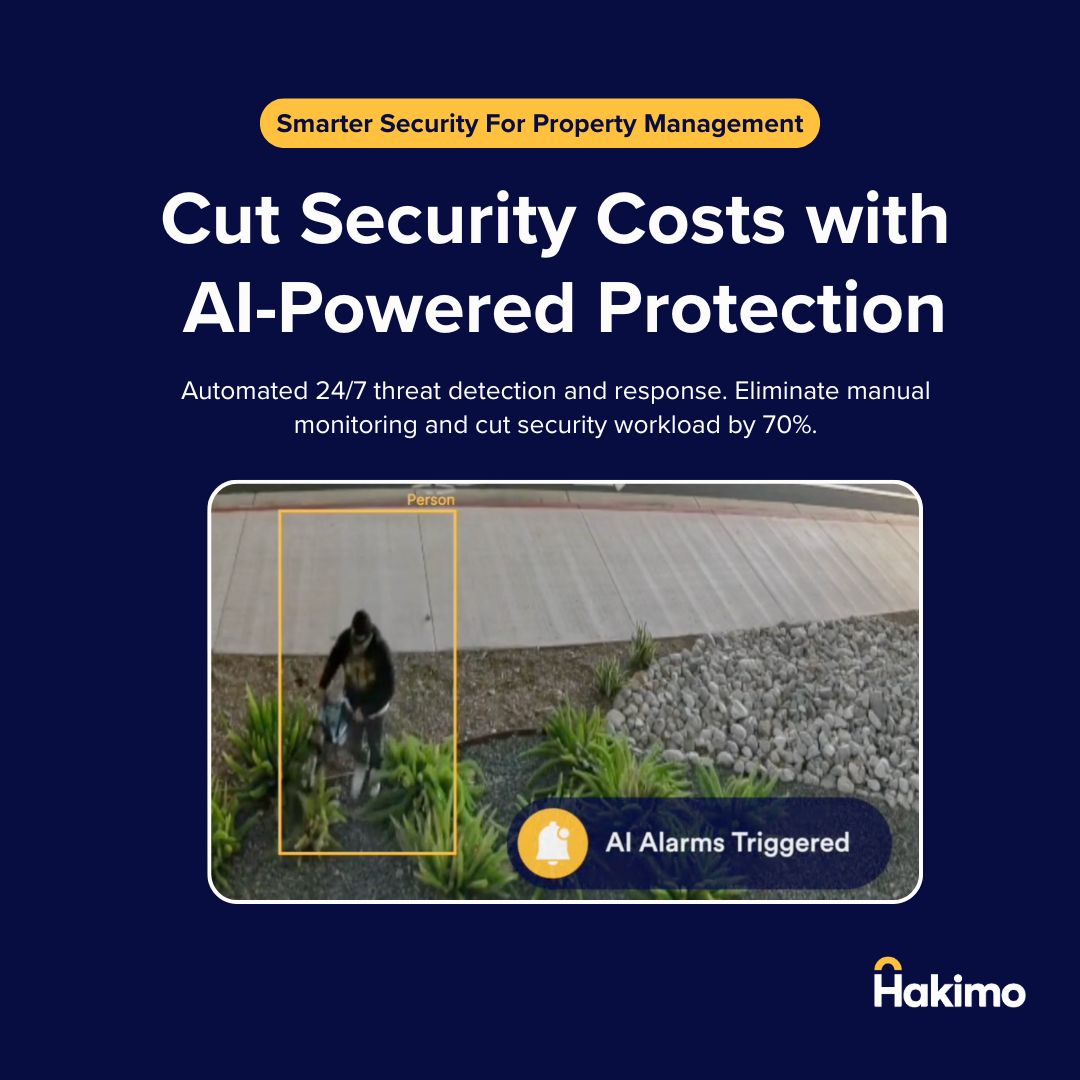
- HakimoRecorded 22 Sept 2026
Boost physical security while reducing workload. Hakimo monitors every camera in real time and alerts your team only when it matters, helping affordable housing communities stay safer without adding staff or stretching budgets. With automated threat detection and fewer false alarms, your team can focus on residents while Hakimo handles the heavy lifting 24/7.
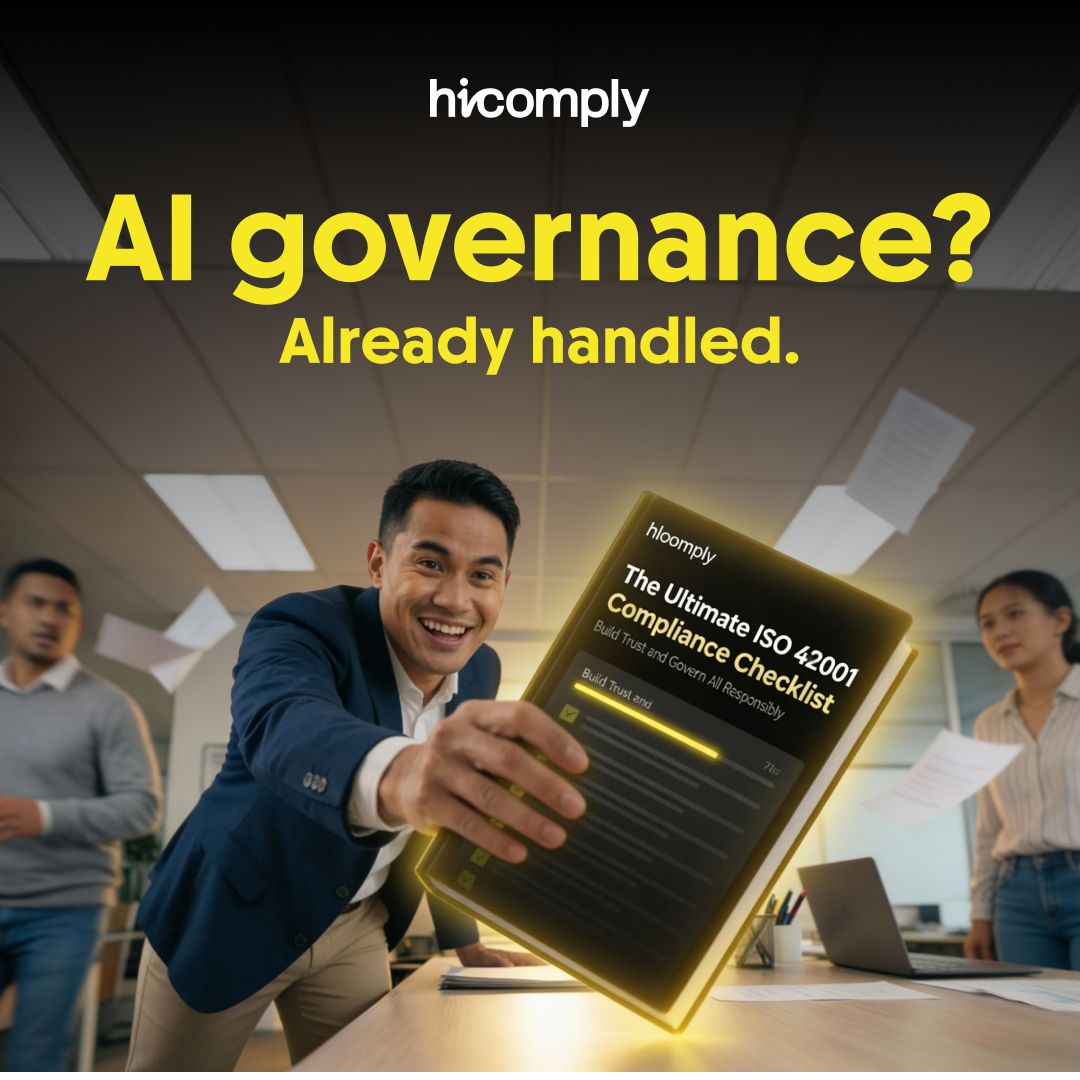
- HicomplyRecorded 22 Sept 2026
Your competitors are still Googling "what is ISO 42001." You? You've got the checklist. 6 steps covering everything from AI risk management to audit-ready documentation. Built for teams who'd rather get certified than stress about it.
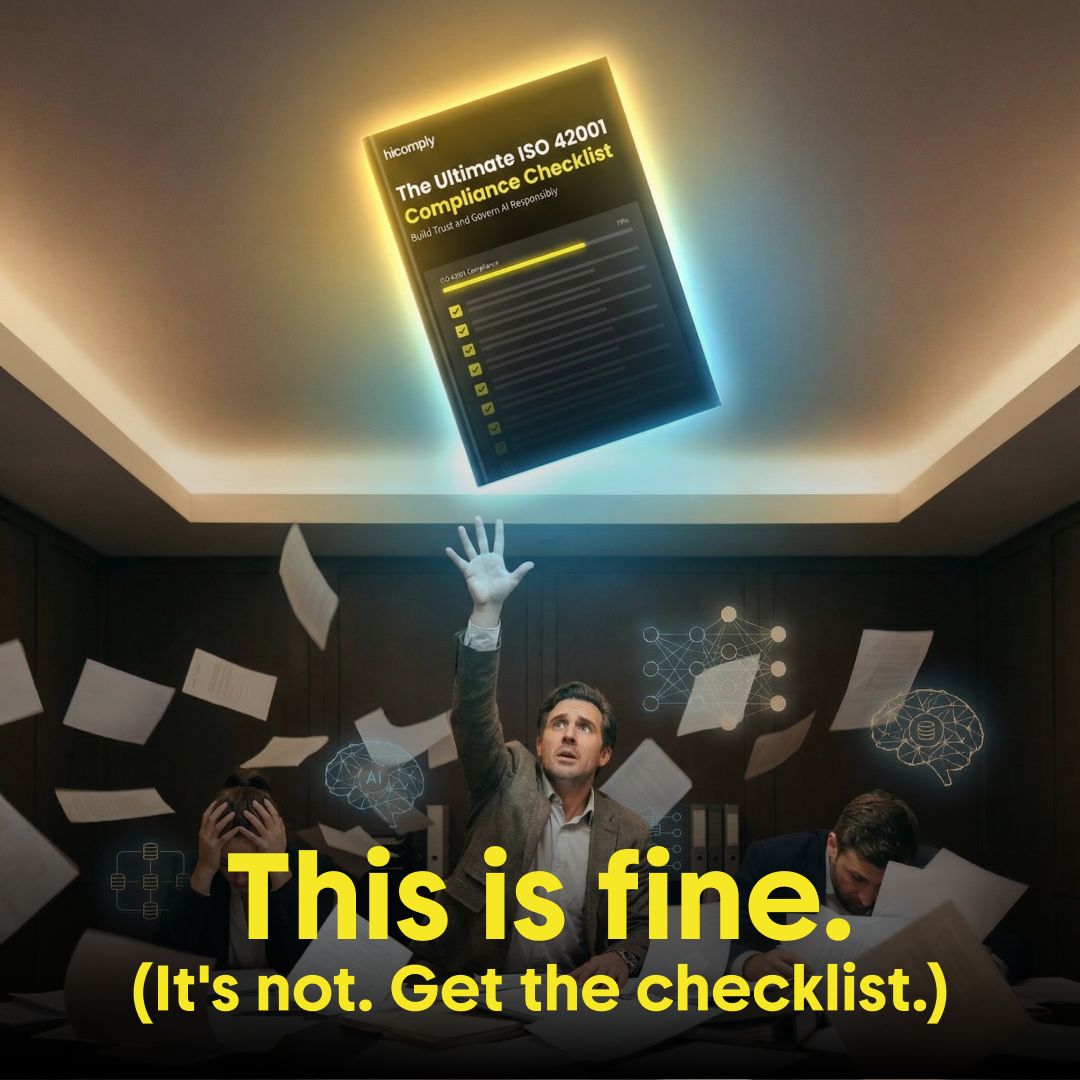
- HicomplyRecorded 22 Sept 2026
AI governance feels manageable until someone says the word "audit." Then it's papers flying, policies missing, and everyone asking who owns what. Sound familiar? This checklist exists so you never have to live that moment. 6 steps. Clear structure. Actual calm.
- HITRUSTRecorded 22 Sept 2026
HITRUST simplifies RFP and procurement processes. Stop friction between risk and business units by leveraging standardized, reusable assurances. See how incorporating validated assessments improves throughput and minimizes rework.
- HITRUSTRecorded 22 Sept 2026
Your TPRM process is slower and more manual than it should be. Inefficiency costs 8-20 hours of low-value work per vendor. Get the executive insights to replace manual systems with a scalable assurance program.
- CorelliumSince 12 Feb 2026
A single mobile security gap can trigger fines, audits, and reputational damage. Most financial services teams miss mobile vulnerabilities because outdated devices, unsupported OS versions, and the inability to prove data security. The result? Rework, delayed releases, and costly audit remediation. Corellium helps financial institutions eliminate technical debt with virtual iOS devices that provide root-level access, version-accurate testing, and compliance-ready visibility—without maintaining expensive device labs. Modernize your mobile testing before it costs more than your testing budget. Schedule a meeting to learn how.
- CorelliumSince 12 Feb 2026
No more iPhone jailbreaks. 🚫📱 With iOS 26 blocking physical access, many financial app teams are left testing at the surface—right where fraud, data leakage, and compliance gaps hide. Corellium gives banks and fintechs full root-level visibility, OS version coverage, and automation—without the risk, overhead, or policy issues of physical devices. See how financial institutions are upgrading mobile security testing (and retiring device labs for good). Book a meeting 👇
- GreyNoise IntelligenceSince 28 Feb 2026
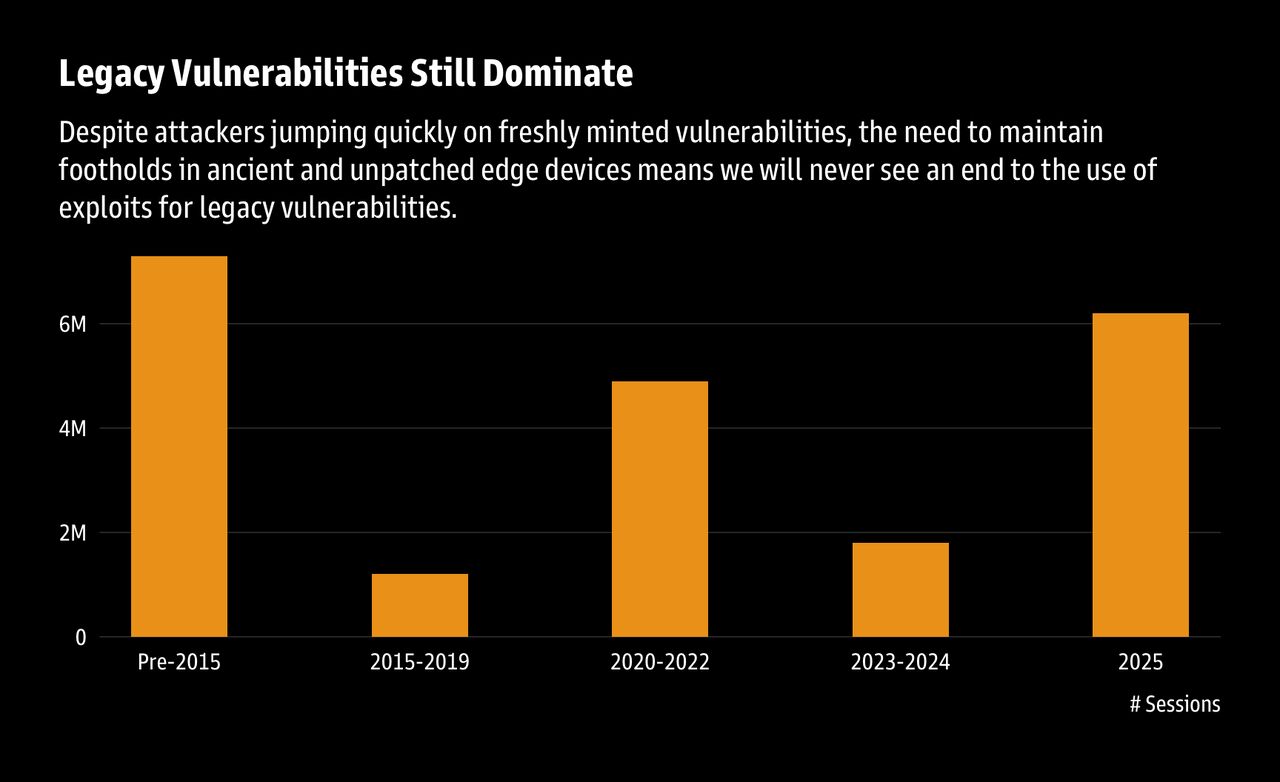
Our latest GreyNoise research is out — the 2026 GreyNoise State of the Edge Report, covering H2 2025. The finding that keeps coming up in every conversation: 52% of remote code execution attempts came from IPs with no prior history in GreyNoise data 😮. More than half of the most dangerous exploitation hitting internet-facing infrastructure came from IPs with no prior history in GreyNoise data — infrastructure that may not appear on reputation feeds until after the exploitation attempt. But one chart 📊 in particular stopped us \(attached\). It shows CVE exploitation volume broken down by vulnerability age. The pattern is hard to ignore: pre-2015 CVEs — vulnerabilities over a decade old — generated 7.3 million exploitation sessions. That's 4x more than 2023-2024 CVEs combined, though one 26-year-old vulnerability \(CVE-1999-0526, X Server\) accounts for the majority. Even excluding it, Shellshock and PHP-CGI continue generating measurable traffic a decade later. The conventional wisdom is that patching programs should focus on the newest vulnerabilities first. The data tells a different story. Public exploit code for these vulnerabilities has been available for years, and the sustained traffic suggests they remain effective against systems that have quietly accumulated outside the patch cycle. Three other findings from the report that warrant attention: 👀 A residential botnet grew from 2,000 to 300,000 IPs in 72 days — a 150x increase, 73% residential. IP-based blocking, reputation scoring, and per-source rate limiting have limited effectiveness against this model. ‼️ Palo Alto GlobalProtect absorbed 16.7 million sessions — more than 3.5x Cisco and Fortinet combined. That notable concentration warrants investigation — whether it reflects available tooling, exposed attack surface, or targeted campaigns. 👿 A single hosting provider \(UCLOUD\) accounted for more malicious sessions than AWS and Azure combined — 14% of all observed sessions from one ASN. The full report 📓 covers edge infrastructure targeting, infrastructure concentration patterns, AI/LLM attack surface emergence, and actionable recommendations for security leadership and operations teams. Read the full research report here: https://lnkd.in/e8dueWPT Always happy to discuss or answer questions about the data — drop a line at [email protected].
- GlasswallSince 17 Jul 2026
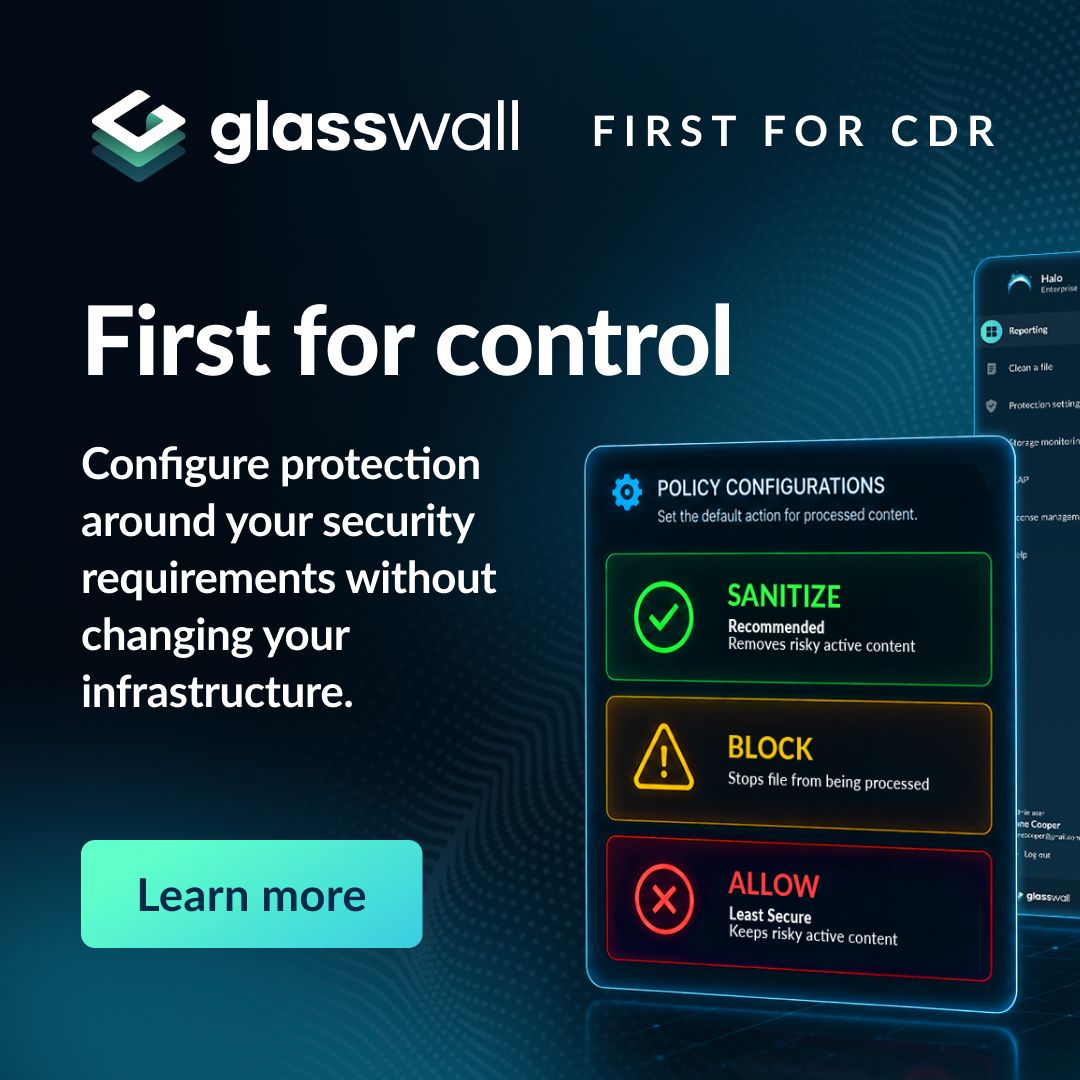
Security tools that can't adapt to your environment tend to create one of two outcomes: teams work around them, or they get replaced. A file handling policy that's appropriate for a classified government network is far too restrictive for a financial services firm processing thousands of customer documents a day. A configuration built for a cloud-native SaaS platform doesn't translate cleanly to an air-gapped operational network. When a tool forces a choice between the protection it can offer and the operational reality of your environment, that tension doesn't go away — it just gets resolved informally, usually in favor of keeping workflows moving. The problem with one-size-fits-all security isn't that it's wrong for every organization. It's that it's precise for none of them. And the gaps it creates are often invisible until something goes wrong. Glasswall CDR is built around granular policy management. Security teams configure exactly how file components are handled during the CDR process — what gets removed, what gets repaired, what the acceptable output looks like for that specific environment. Those policies can be set to match compliance requirements, operational constraints and risk tolerance without overhauling what's already in place. That level of control is particularly important in high-assurance environments where compliance mandates are specific and documented. But it matters in any environment where the right level of protection differs by workflow, by user group or by the sensitivity of the data involved. Protection that fits your environment is protection that actually gets used.
- GlasswallSince 15 Jul 2026
Security tools that don't connect to your existing stack create new gaps to manage. With 300+ native connections, Glasswall CDR extends protection across the infrastructure you already have.
- PathlockSince 26 Jun 2026
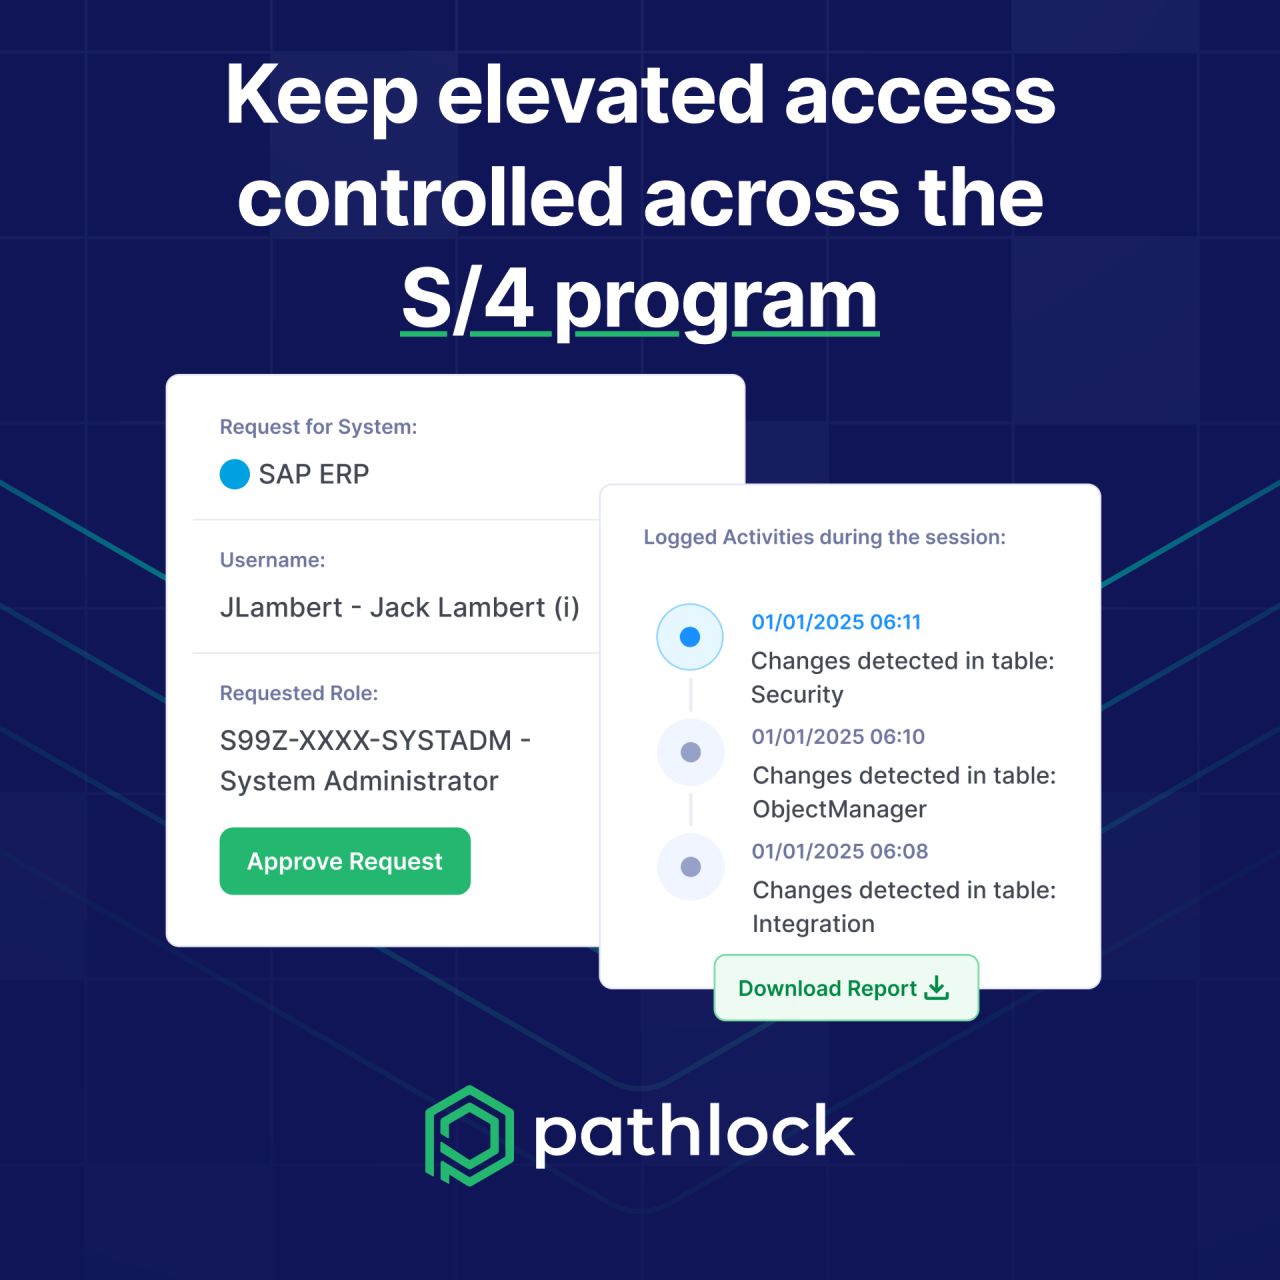
An S/4 program runs on elevated access — the migration work itself needs broad permissions, and cutover and hypercare push emergency access higher still. That's a long stretch where privileged activity is heavy and easy to lose track of. Firefighter access that's time-boxed and monitored, with the audit trail written automatically, keeps the program moving without leaving a gap to reconstruct later.
- PathlockSince 26 Jun 2026
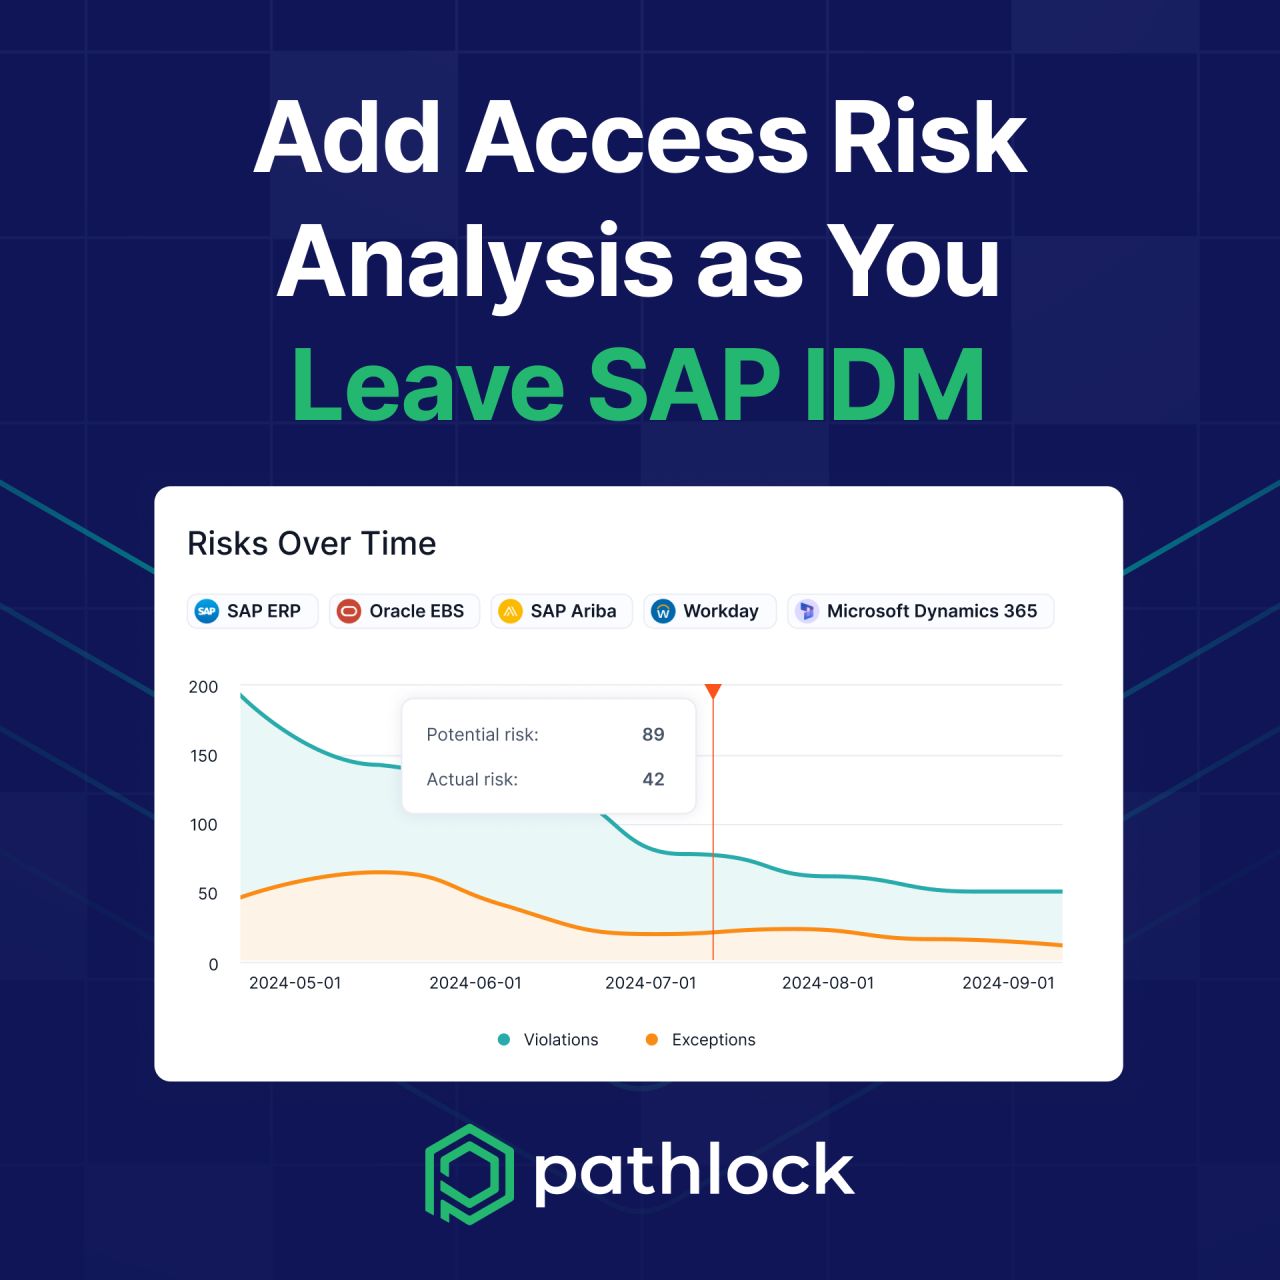
SAP IDM handled provisioning and lifecycle — not segregation of duties. The access risk and SoD analysis you need has always lived in a separate GRC tool. A move off SAP IDM is the moment to bring identity lifecycle and access risk analysis onto one platform, so conflicts are quantified and remediated where access is managed, instead of adding yet another tool to the stack.
- Core ImpactSince 13 Jun 2026
Upskill team capabilities by building on existing expertise. Give your pen testers the tools and training to go further. https://lnkd.in/eUd4DDwd
- Group 2000Since 16 Jul 2026
You do not grow by solving the same problem over and over again. At Group 2000, you work on complex technical challenges alongside experienced software engineers and architects. You get the room to deepen your expertise, contribute your own ideas and gradually take ownership of increasingly important components. Discover a place where you can genuinely grow as an engineer.
- Group 2000Since 16 Jul 2026
Innovation does not have to mean uncertainty. Since 1978, Group 2000 has developed specialist technology for customers around the world. Today, we combine that stability with complex technical challenges, international projects and plenty of room for individual responsibility. Build your future with a company that is here for the long term.
- CorbadoSince 27 Aug 2026
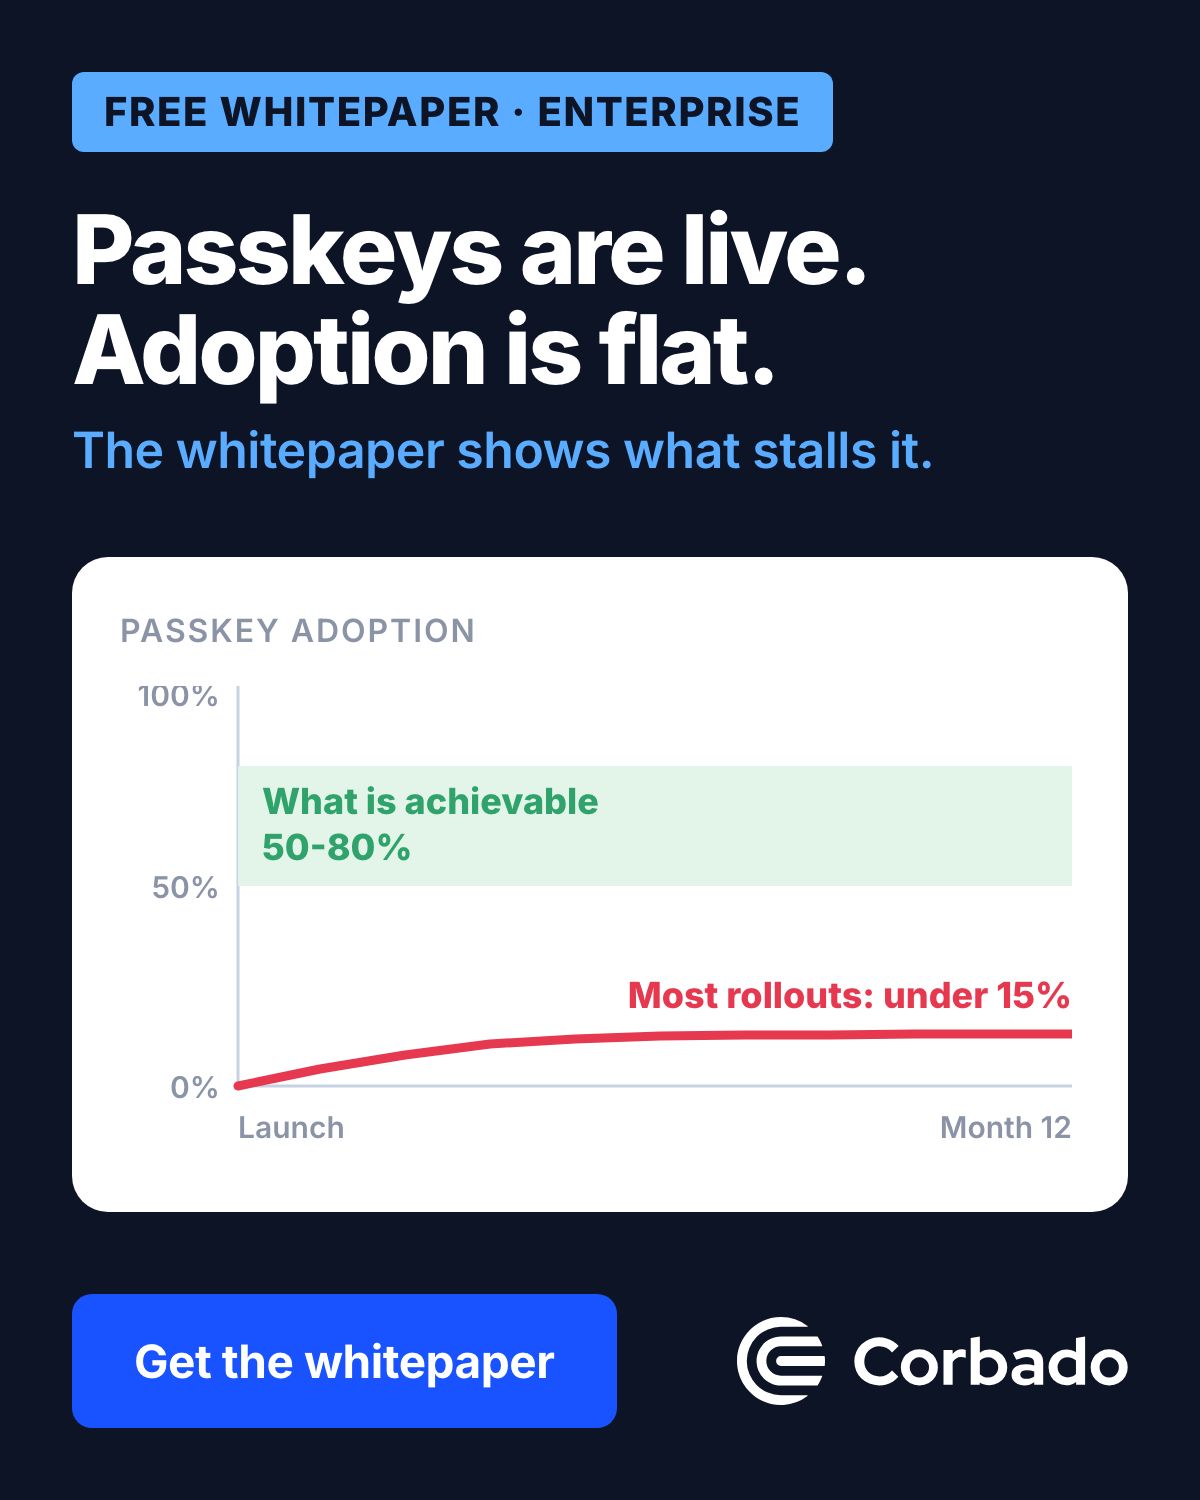
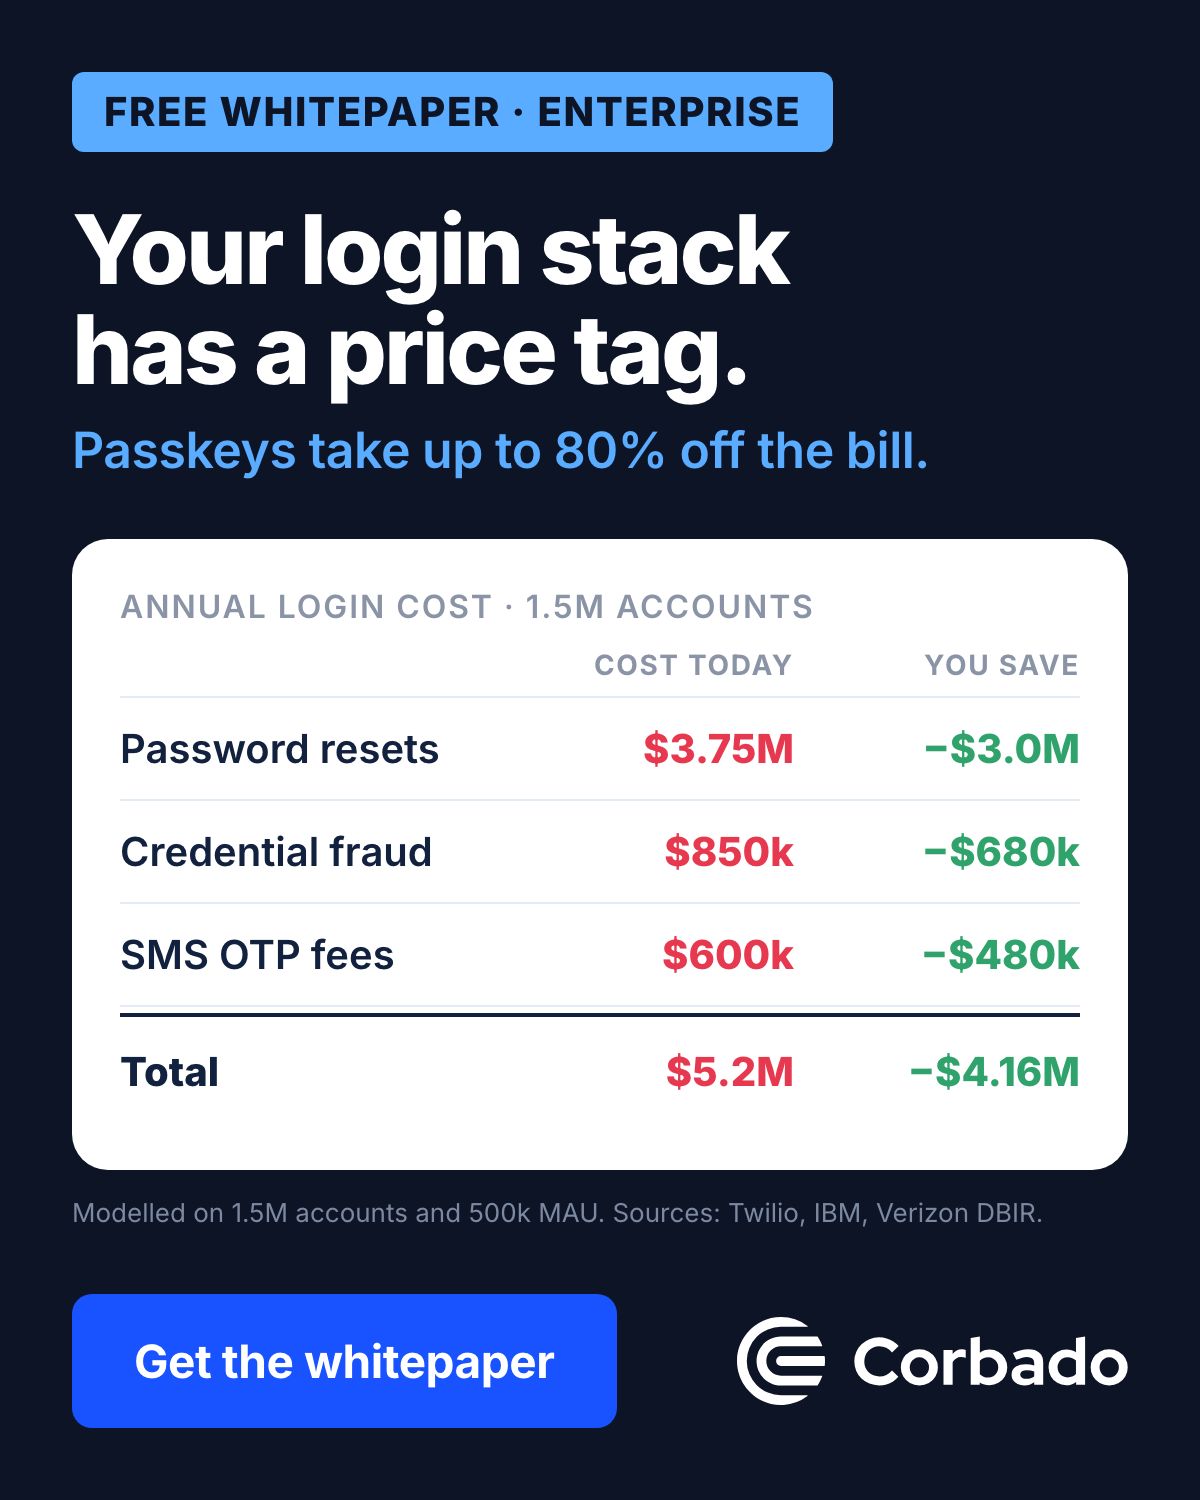
Passkeys are usually live long before anyone actually uses them. The whitepaper covers what stalls adoption and how the rollouts that worked got past it.
- CorbadoSince 27 Aug 2026
Most teams treat authentication as a cost line they cannot avoid. Passkeys can flip that. The whitepaper has the full ROI model behind these numbers and the rollout plan that goes with it.
- Group-IBSince 8 Sept 2026
⚡ A reorganization triggers internal power struggles nobody wants. A new platform purchase demands an ROI business case nobody can yet prove. So institutions stay siloed, and adversaries win by default. You don’t need a new budget, extra headcount, or a massive software overhaul to fix this. You just need 90 days and the team you already have. Your staff can: 🔹 Unify language: Adopt MITRE F3 across both functions. 🔹 Audit the gap: Walk one live incident end-to-end to map where intelligence died. 🔹 Track what matters: Measure one shared metric—signal-to-action time. 📖 Read the full 90-day plan
- Group-IBSince 8 Sept 2026
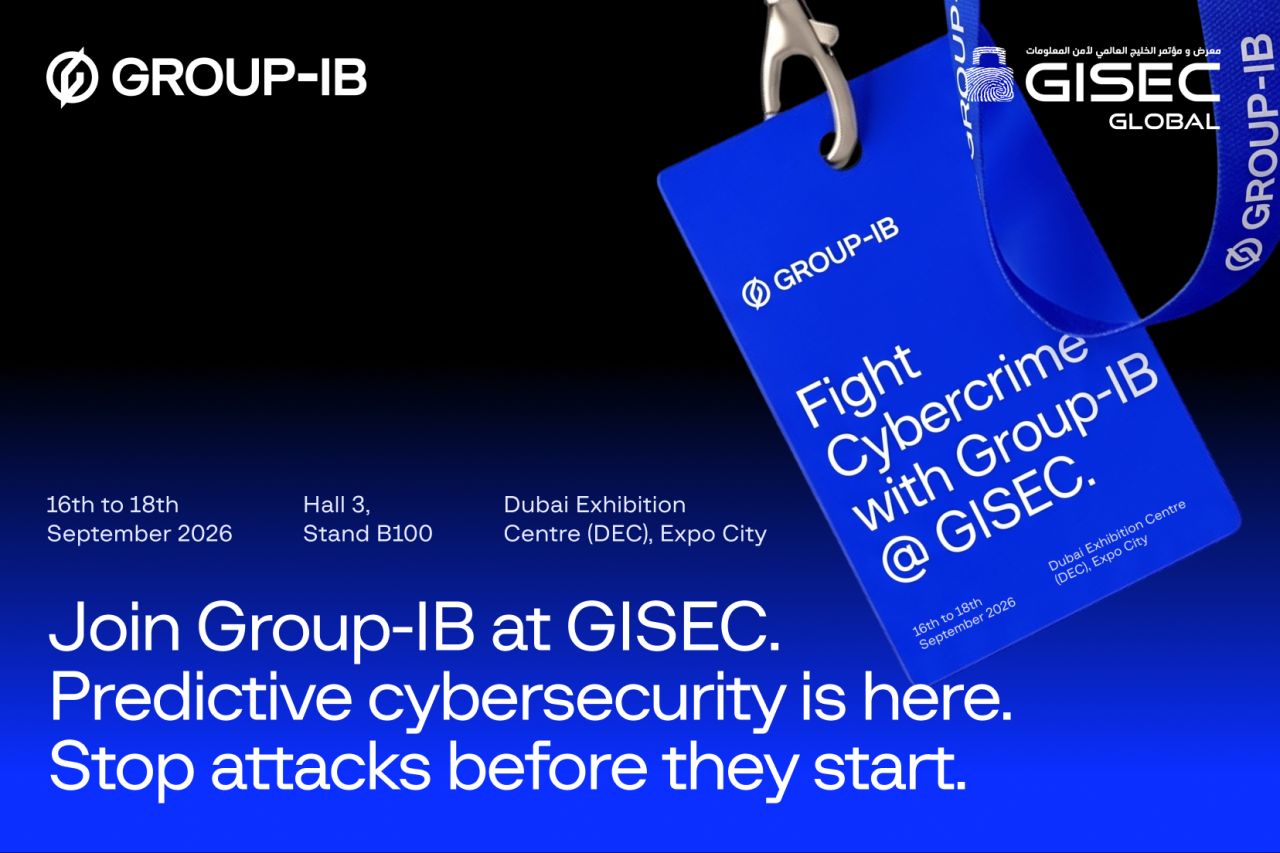
✨ If you make it to one cybersecurity event this year, make it this one. GISEC Global is where the region's security community gathers. And this year, Group-IB isn't there to make a bold claim about the future of cybersecurity. We're there to prove it. Prediction isn't a direction we're pointing at. It's already running. Book twenty minutes with our team at the stand, and we'll show you what that looks like: 🔹 Cyber and fraud signals, fused into one defence. 🔹 Every major release of our year, in the Innovation Hub. 🔹 A Threat Exposure Assessment that maps your blind spots, live. No pitch. A working session on what your defence could catch before the first alert with the team behind two decades of operations alongside INTERPOL, EUROPOL, and AFRIPOL. 📍 Dubai Exhibition Centre (DEC), Expo City, Hall 5, Stand B100 📅 16th – 18th September 2026. Book your slot: https://lnkd.in/eh9Ayr-y/?utm_campaign=NewCampaignGroup&utm_source=linkedin&utm_medium=paid&utm_id=626082903&hsa_acc=509945487&hsa_cam=626082903&hsa_grp=889361033&hsa_ad=1531642593&hsa_net=linkedin&hsa_ver=3 #Cybersecurity #GISECGlobal #ThreatDetection #FraudPrevention #CyberDefense #GISEC2026 #FightAgainstCybercrime
- Core6Since 9 Sept 2026
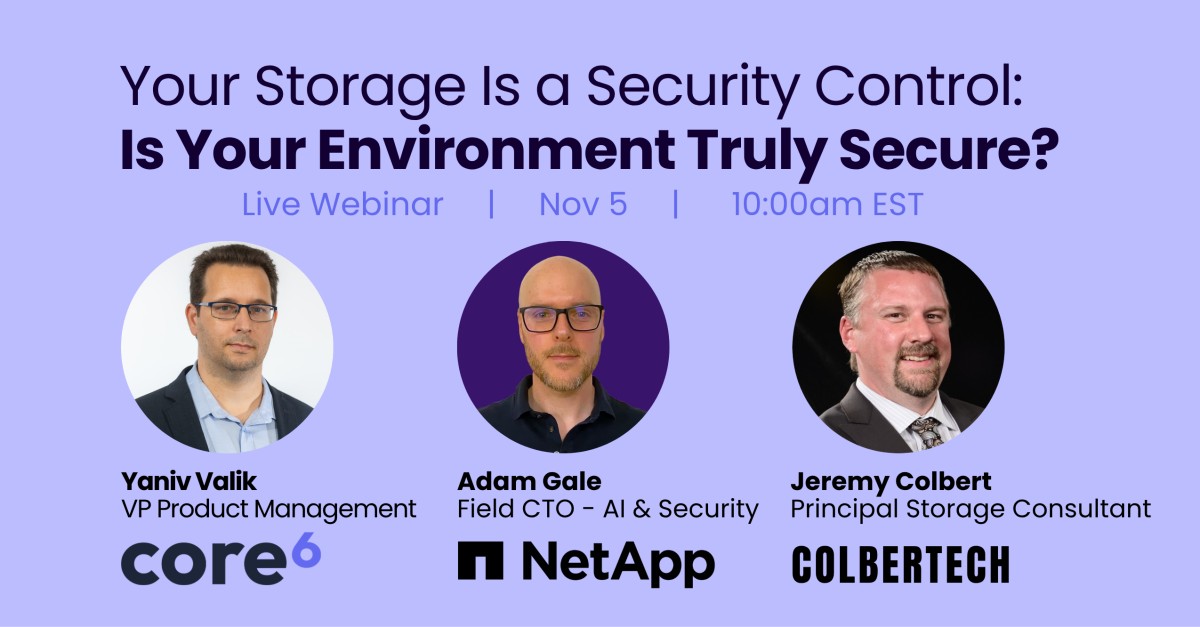
On November 5, join NetApp and Core6 to see how storage and infrastructure teams are turning primary storage into a frontline defense against modern threats. This webinar also features the former Storage Director at Royal Bank of Canada.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.