On air · 1 of 3 networks
GreyNoise Intelligence
- greynoise.io
- Cybersecurity
- US
- 68 employees
GreyNoise Intelligence’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 97. Watch GreyNoise Intelligence with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 71 | Checked 29 Oct 2026 | See all 97 ads → | ||
| Meta | Not checked | — | |||
| Not checked | — |
GreyNoise Intelligence has 71 live LinkedIn ads.
Latest ads
- LINKEDIN · IMAGESince 27 Oct 2026
We’re bringing NoiseFest to Barcelona! 🎉 If you’re in town for Fal.Con or BCC’26, we’d love for you to join GreyNoise, Vega, and Noma Security for an evening of cocktails, Nobu’s signature canapés, and great conversation with fellow security leaders. 📅 Tuesday, November 3 | 20:00–23:00 📍 Nobu Restaurant Barcelona Take a break from the conference floor, connect with peers, and swap stories about what’s really happening on the threat landscape. It’s an intimate evening and space is limited. We hope to see you there! ➡️ Request your invite: https://lnkd.in/gzMSAyHF #NoiseFest #GreyNoise #ThreatIntelligence
- LINKEDIN · IMAGESince 15 Oct 2026
A GreyNoise product demonstration led to the initiation of a intrusion investigation and some follow-up research into a malicious cyber actor conducting proxyjacking operations against network edge devices turning them into commercially available residential proxies. https://lnkd.in/eRftmJYY
- LINKEDIN · IMAGESince 11 Sept 2026
Artificial intelligence is insanely powerful and super duper good at lots of stuff that we mere human mortals are so meek at. But AI is, in fact, not human. And, as a result, AI's current capacity for good opsec and good tradecraft is limited. A model cannot go to jail, nor can it understand and appreciate the pain and helplessness of having its agency or livelihood clobbered, or being removed from its family, or having its assets frozen. Finding bugs and writing exploits is one skillset, but operating on other folks' computers and networks is a very different one. Anyways, we at GreyNoise Intelligence found a particularly forward-leaning actor compromising organizations (using the codex harness with the DeepSeek models) that were running vulnerable PaperCut Software. We yoinked the attacker's target list, their tools, their progress spreadsheets where they notated how many of the orgs they'd gotten domain admin on, and even their rank-ordered exclusion list of countries not to target. Couldn't tell you why, but their first three target geographies to exclude were Russia, China, and Hong Kong. At GreyNoise, we have no incident response business. We've also historically not been in the business of unprompted victim notification or ambulance chasing. That said, having come across the entirety of this campaign as it was happening, with some pretty meaty targets, we're in the process of working through victim notification now. https://lnkd.in/e29aaZCH
- LINKEDIN · IMAGESince 11 Sept 2026
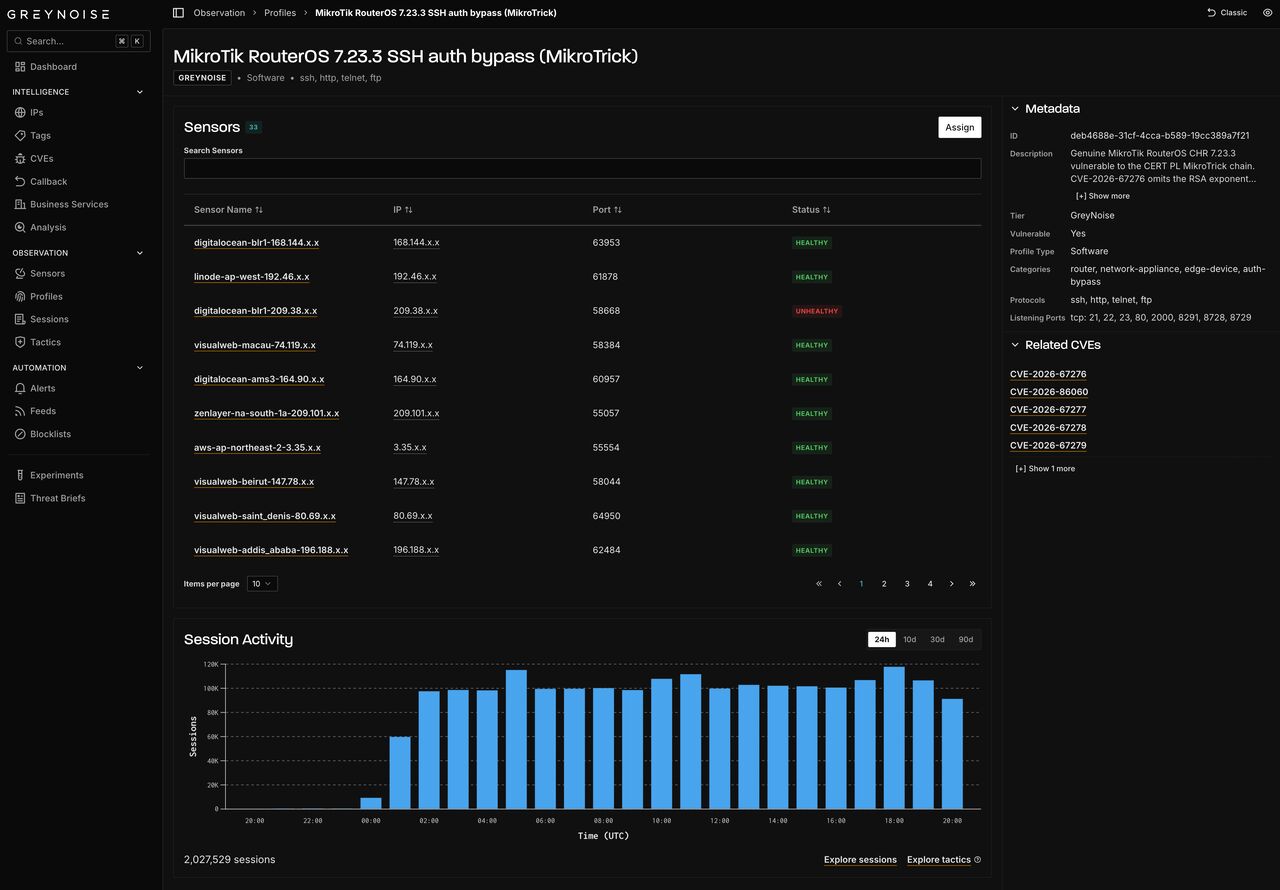
GreyNoise Intelligence is positioned to detect in-the-wild exploitation of the recent MikroTik "Mikrotrick" bug. A big-enough saturation of these profiles are up and running on our grid. All GreyNoise Swarm customers can deploy this profile right now as well. Exploitation has been publicly reported, but I do not believe mass, automated exploitation has begun yet. Last week CERT Polska shared their observation that six RouterOS vulnerabilities that are being chained in the wild. MikroTik patched on 2026-09-03 - 7.25beta3, 7.24.2, 7.23.4, and 6.49.21. If you're on 7.x below 7.23.4, or 7.24.x below 7.24.2, or 6.x below 6.49.21, you're in range. A public POC has been posted. The attack chain is complex and wraps together the following CVEs: CVE-2026-67276 - SSH publickey forgery <---- this is the banger CVE-2026-86060 - SSH argument injection CVE-2026-67279 - unauthenticated command execution via rekey CVE-2026-67277 - btest pre-auth uninitialized buffer CVE-2026-67278 - X.509 signature forgery CVE-2026-67281 - WebFig /jsproxy unauthenticated root file read This is one of those attacks that's nightmarish to track from internet-watchers' perspectives. The network portion of the attack is over SSH-encrypted channels, post-keypair exchange, which means you can't use out-of-the-box network comms to detect the attack (unless you've got some kind of black magic to extract key material from running devices and decrypt communications 👀) Worse yet, the bugs target an embedded system, which presents lots of challenges WRT collecting host artifacts. Unfortunately we still can't run Microsoft Defender on Mikroktik routers, because neither Mikrotik routers, nor any routers, run Microsoft Windows. This is going to end up being one of those bugs where the majority of defenders will initially have to rely on the fingerprints of the known public POCs, which we will report as throughly as we are able to. Regardless, I'm pretty confident GreyNoise is in a good position to observe mass-exploitation of these vulnerabilities as soon as it starts.
- LINKEDIN · IMAGESince 29 Aug 2026
Check out Mark Mager's inaugural blog post published 0.032 seconds after joining GreyNoise Intelligence. He wrote about how we're thinking about detecting everything, everywhere, all the time when the slope of vulnerabilities disclosed approaches a vertical line. https://lnkd.in/eiGyRJ-e
- LINKEDIN · IMAGESince 28 Feb 2026
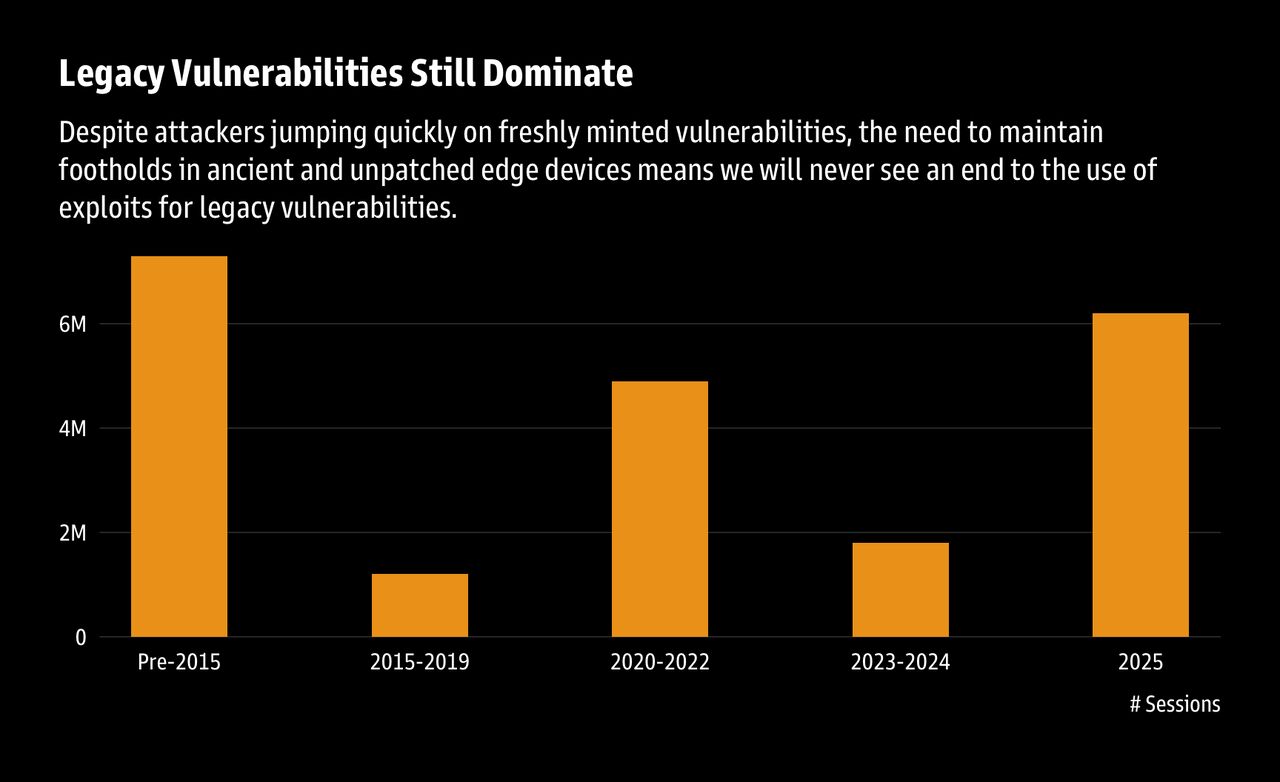
Our latest GreyNoise research is out — the 2026 GreyNoise State of the Edge Report, covering H2 2025. The finding that keeps coming up in every conversation: 52% of remote code execution attempts came from IPs with no prior history in GreyNoise data 😮. More than half of the most dangerous exploitation hitting internet-facing infrastructure came from IPs with no prior history in GreyNoise data — infrastructure that may not appear on reputation feeds until after the exploitation attempt. But one chart 📊 in particular stopped us \(attached\). It shows CVE exploitation volume broken down by vulnerability age. The pattern is hard to ignore: pre-2015 CVEs — vulnerabilities over a decade old — generated 7.3 million exploitation sessions. That's 4x more than 2023-2024 CVEs combined, though one 26-year-old vulnerability \(CVE-1999-0526, X Server\) accounts for the majority. Even excluding it, Shellshock and PHP-CGI continue generating measurable traffic a decade later. The conventional wisdom is that patching programs should focus on the newest vulnerabilities first. The data tells a different story. Public exploit code for these vulnerabilities has been available for years, and the sustained traffic suggests they remain effective against systems that have quietly accumulated outside the patch cycle. Three other findings from the report that warrant attention: 👀 A residential botnet grew from 2,000 to 300,000 IPs in 72 days — a 150x increase, 73% residential. IP-based blocking, reputation scoring, and per-source rate limiting have limited effectiveness against this model. ‼️ Palo Alto GlobalProtect absorbed 16.7 million sessions — more than 3.5x Cisco and Fortinet combined. That notable concentration warrants investigation — whether it reflects available tooling, exposed attack surface, or targeted campaigns. 👿 A single hosting provider \(UCLOUD\) accounted for more malicious sessions than AWS and Azure combined — 14% of all observed sessions from one ASN. The full report 📓 covers edge infrastructure targeting, infrastructure concentration patterns, AI/LLM attack surface emergence, and actionable recommendations for security leadership and operations teams. Read the full research report here: https://lnkd.in/e8dueWPT Always happy to discuss or answer questions about the data — drop a line at [email protected].
6 of 97 adsSign up to see every GreyNoise Intelligence ad, filter by format and date, and get alerts on new ones.
See all 97 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.