LinkedIn image ad examples
3 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- CleafySince 17 Sept 2026
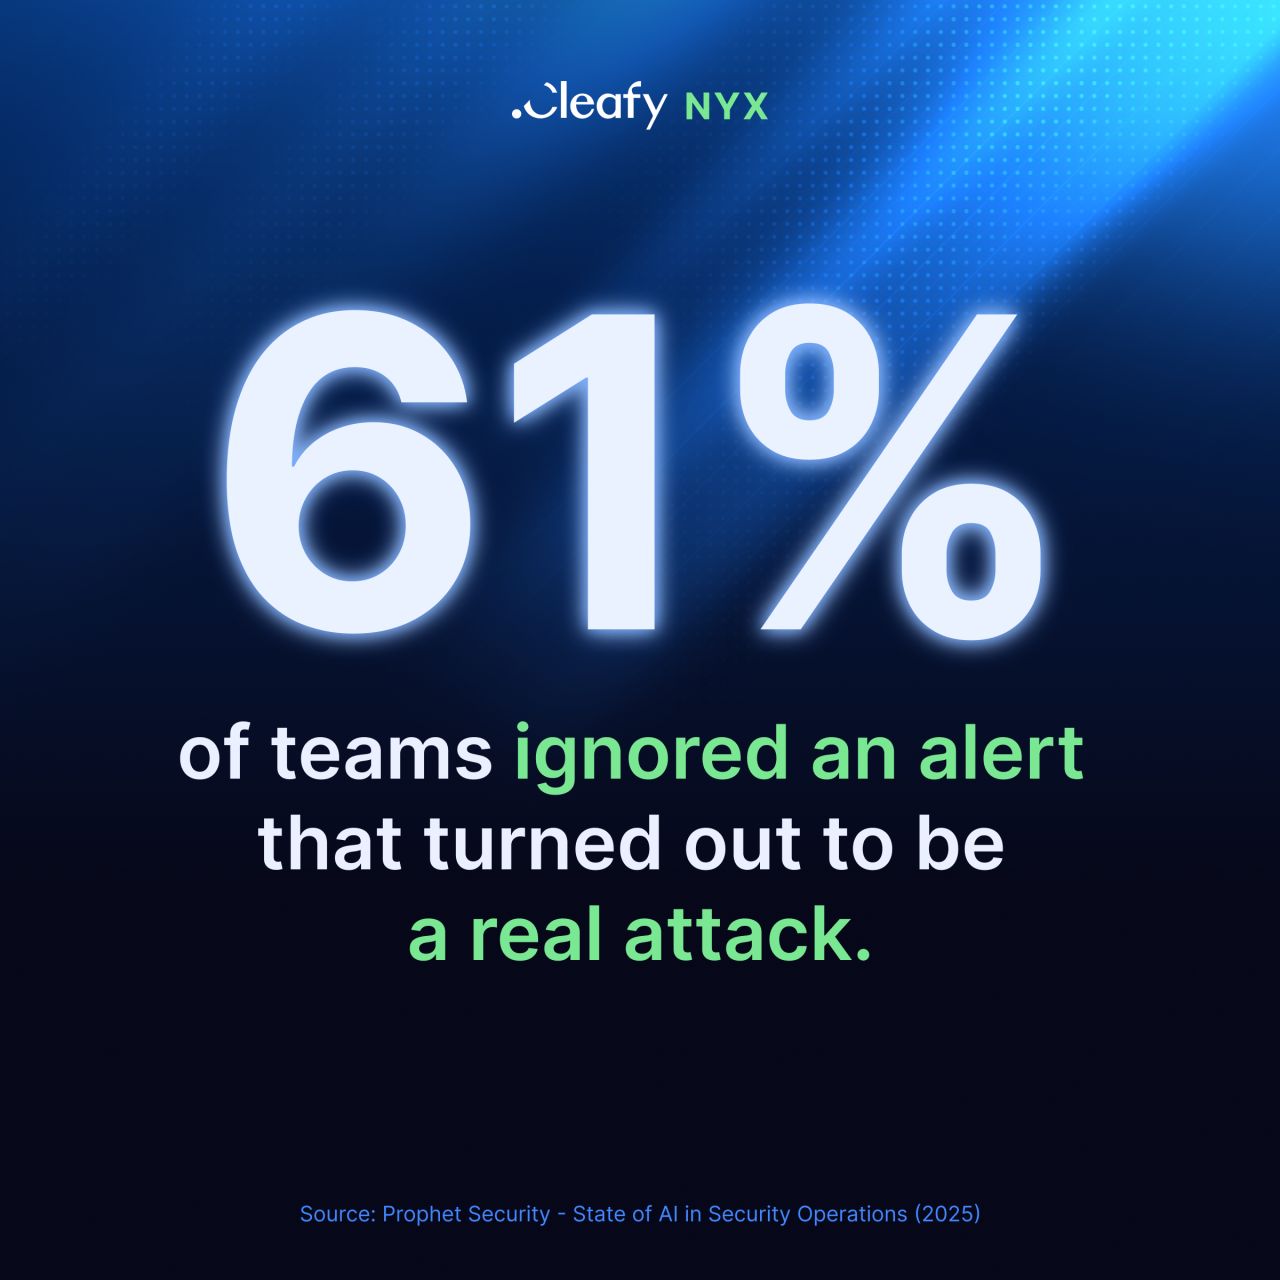
61% of teams have ignored an alert that turned out to be a real attack. This happened not from carelessness, but from working with fragments while the attacker sees the whole operation. Our new report breaks down why fragmented signals miss coordinated fraud, and what a connected view changes.
- BugHuntRecorded 8 Oct 2026
Uma vulnerabilidade pode ser encontrada antes de a empresa estar preparada para receber esse tipo de report. O pesquisador tenta avisar, mas não encontra um canal claro. A mensagem chega por e-mail, formulário, LinkedIn ou até por alguém de outra área. A partir daí, começa uma corrida interna para entender quem deve assumir, quem valida a falha, quando o jurídico entra e como manter a comunicação com quem fez o report. Recentemente, olhando como o Google estrutura esse processo, um ponto me chamou atenção: os reports de segurança passam por um canal próprio e seguem para triagem e avaliação técnica. Parece simples, mas ajuda a organizar justamente o que costuma virar improviso em muitas empresas. Ou seja, muitas vezes existe disposição para colaborar. O que falta é a empresa ter um processo capaz de receber essa colaboração e conduzir o que vem depois. Não ter um fluxo estruturado não impede que alguém encontre uma falha. Só deixa a empresa mais exposta à improvisação justamente no momento em que precisa responder com mais rapidez e segurança. Se um pesquisador tentasse reportar uma vulnerabilidade crítica para a sua empresa hoje, ele saberia por onde começar?
- GarancySince 22 Sept 2026
Wie lückenlos ist Ihre IT geschützt? Steuern Sie Identitäten, Rollen und Berechtigungen mit Identity Management nach strengen EU-Richtlinien!
- Beazley SecuritySince 23 Sept 2026
EM Protect continuously uncovers and tracks changes across your attack surface, including external-facing assets, cloud, third-party, and digital ecosystems, providing visibility into vulnerabilities in near-real time. Activate today to start maximizing your benefit.
- Beazley SecuritySince 23 Sept 2026
Beazley policyholders, activating EM Protect is as easy as 1, 2, 3... Get started now to gain continous visbility into your external attack surface, helping you uncover risks before attackers do. This benefit is part of your cyber coverage. Activate now
- Code Blue CyberRecorded 8 Oct 2026
At Ready for Tomorrow, Eitan Platok, CTO of Code Blue, will talk about "Fight AI Threats with Resilience AI": how attackers are using AI, and how organizations can use AI to detect, respond and recover faster. Ready for Tomorrow: Cyber, AI & Organizational Resilience A unique event by Howden and Code Blue on the future of organizational resilience, cyber crisis management and AI-driven innovation. 📅 19.10.2026 | 09:00-13:30 📍 Tosca, Petah Tikva
- CyberVadisSince 24 Sept 2026
Il y a quatre ans, j'ai reçu un mail d'extorsion. Mon nom, mon adresse, le prénom de mon fils, et une référence à un vin rouge que je n'avais jamais mentionné nulle part en ligne. Ce jour-là, j'ai eu peur, vraiment. Puis j'ai compris : ce n'était pas moi qui avais été piratée. C'était probablement un petit fournisseur (le vigneron) à qui j'avais fait confiance, quelque part dans ma vie personnelle. Ce qui m'avait marquée à l'époque, c'est le temps que ça avait dû prendre à quelqu'un pour assembler ces détails et construire un message aussi ciblé. Aujourd'hui, ce travail de profilage, une IA générative le fait en quelques minutes, à partir de n'importe quelle fuite de données chez n'importe lequel de nos fournisseurs. On vient de le confirmer dans une étude réalisée par Thibault Lapédagne, créateur de la méthodologie d'évaluation CyberVadis et Alain Bouillé, Délégué Général du CESIN : la plupart des entreprises n'ont aujourd'hui ni clause contractuelle sur l'usage de l'IA chez leurs fournisseurs, ni visibilité sur ce qui se passe au rang d'après. Je le vis à double titre. Comme professionnelle du risque tiers, ça change l'échelle du problème. Comme personne qui a reçu ce genre de mail, ça me rappelle que derrière chaque fournisseur mal maîtrisé, il y a un individu réel qui encaisse les conséquences. Chez vous, l'IA côté fournisseurs, c'est déjà un sujet qu'on adresse ou un angle mort qu'on n'a pas encore ouvert ? Commentez Etude et je vous l'envoie.
- Code Blue CyberRecorded 8 Oct 2026
העולם לא מאט. גם איומי הסייבר לא. הצטרפו ל־Ready for Tomorrow Cyber, AI & Organizational Resilience אירוע ייחודי של Howden ו-Code Blue שיעסוק בעתיד החוסן הארגוני, ניהול משברי סייבר ויישומי AI בעולם שמשתנה במהירות. 📅 19.10.2026 | 09:00-13:30 📍 טוסקה, פתח תקווה
- Dragos, Inc.Since 25 Sept 2026
Defining xOT was the easy part: the full range of technologies that can influence or impact physical operations. Most OT security programs were built around a narrower view of the operational environment, and for a long time that made sense. But what operations depend on has changed. More of what keeps production running now sits outside traditional OT boundaries, and whether we call those systems OT doesn't change the consequence when they're disrupted. The harder (and much more important) question to answer is what changes when you use that definition to build a security program. It changes what you need visibility into, how you think about vulnerabilities, what activity you need to detect, what belongs in an investigation, and what you need to be prepared to respond to. That's really the point of xOT. I wrote a bit more about what changes when you define the environment this way, and why getting the definition right matters. https://lnkd.in/gcha8XcF Every xOT environment will draw these lines a little bit differently. The important part is making sure your cybersecurity program reflects what operations actually depend on. #cybersecurity #otcybersecurity #OTthreats #icssecurity #xot
- IS DecisionsSince 25 Sept 2026
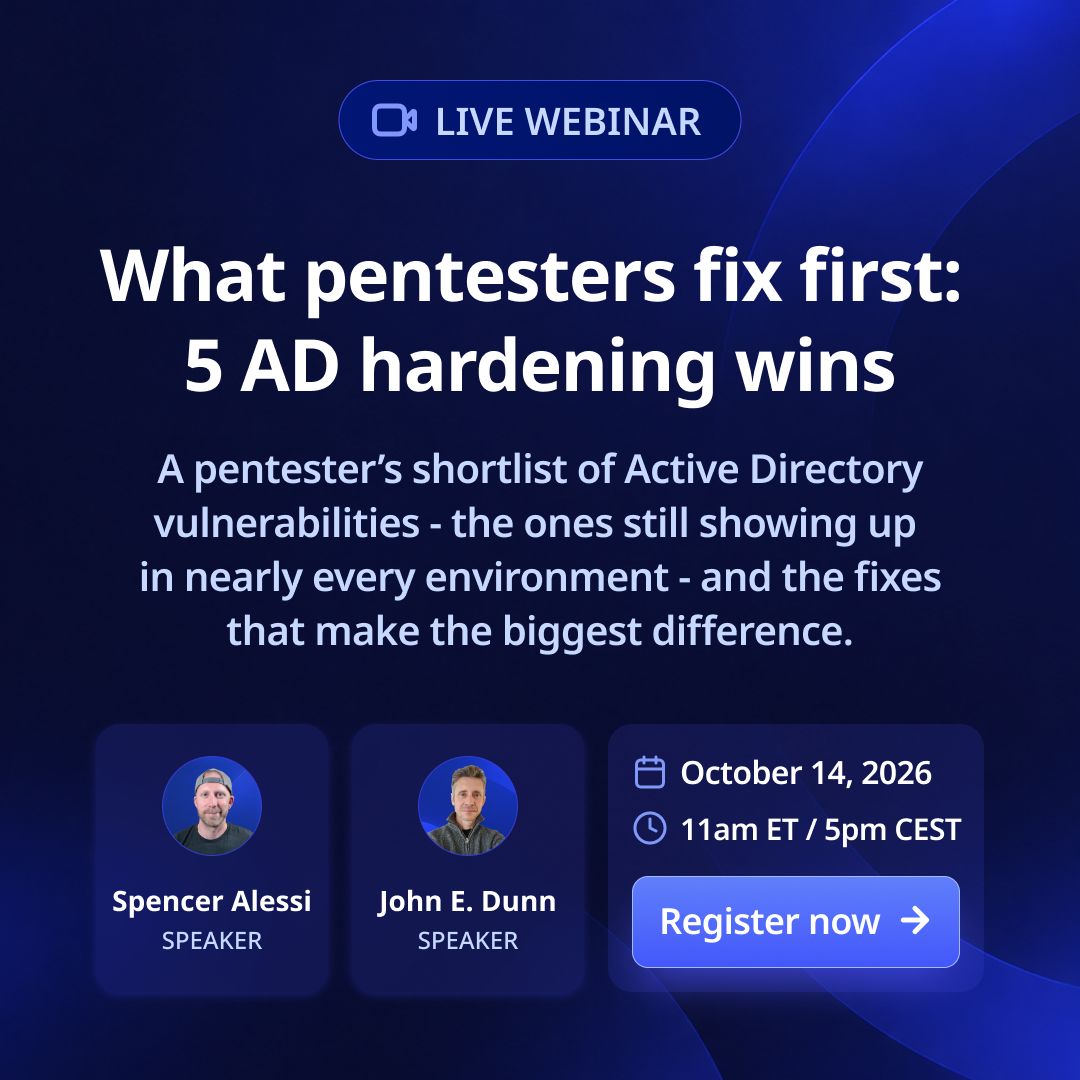
Join the first Authentication Insights live webinar on Oct 14. Spencer Alessi (Sr. Pentester at SecurIT360, Microsoft MVP) and John E. Dunn (IT Journalist) walk through 5 AD hardening wins you can fix fast. Register here: https://lnkd.in/dyvW3u_r/?utm_campaign=Whatpentestersfixfirst:5ADhardeningwins&utm_source=linkedin&utm_medium=paid&utm_id=1225898583&hsa_acc=500016795&hsa_cam=1225898583&hsa_grp=891792013&hsa_ad=1559037833&hsa_net=linkedin&hsa_ver=3
- Dragos, Inc.Since 26 Sept 2026
Ten years ago we started Dragos, Inc. with one mission: safeguard civilization by protecting the operational technology that runs our world and is critical to our local communities. Today marks a major milestone. The Accenture majority investment in Dragos has cleared government approvals and is now official. Which means Dragos can and has now officially acquired NetRise and runZero! With our previous acquisitions of Network Perception and Phosphorus Cybersecurity Inc. we're building the industry's first end-to-end xOT Cybersecurity platform, from the software supply chain and connected devices to the operational core. In addition to my role as CEO I've also been elevated to the role of Chairman of the Board of Directors. The new investment has also brought significant job growth to include over 100 positions opened over the past few months and hundreds more in the future; mostly focused in R&D as well as investments across Dragos. Our commitment is to make sure the Dragos Platform doesn't just meet where you are in your journey today but is where you will need to be in the future as we navigate a growingly complex world. I'm grateful to welcome HD Moore Thomas Pace Michael Scott and their teams to Dragos. What you've built extends our mission in exactly the way defenders need. I share more on what all this means, and link to our upcoming webinar with me on the topic, in my recent blog. Read more at: https://lnkd.in/eUJssa-u
- ESET PolskaSince 25 Sept 2026
🛡️ Masz wszystko pod kontrolą? A co z tym, czego nie widzisz? Nie każdą próbę ataku da się zauważyć na pierwszy rzut oka. Podejrzany plik, złośliwa strona czy aplikacja mogą wyglądać zupełnie niewinnie. Dlatego oprócz ostrożności warto mieć dodatkową warstwę ochrony. 🔎 ESET HOME Security Essential pomaga chronić urządzenie przed złośliwym oprogramowaniem i innymi zagrożeniami, które mogą pojawić się podczas codziennego korzystania z internetu. Bo bezpieczeństwo nie kończy się na świadomości zagrożeń. Wymaga ochrony, która stale czuwa w tle, kiedy Ty po prostu korzystasz z sieci. 🔐 👉 Sprawdź ESET HOME Security Essential i zadbaj o ochronę swoich urządzeń. https://lnkd.in/dqurxM2g
- IS DecisionsSince 25 Sept 2026
Pentesters walk into AD environments and flag the same misconfigurations every time. Most of them are still unfixed. Live webinar Oct 14 What pentesters fix first:5 AD hardening wins with Spencer Alessi (Sr. Pentester at SecurIT360, Microsoft MVP) and John E. Dunn (IT Journalist). 45 min. Free. Register here: https://lnkd.in/dSKUSvYW/?utm_campaign=Whatpentestersfixfirst:5ADhardeningwins&utm_source=linkedin&utm_medium=paid&utm_id=1225898583&hsa_acc=500016795&hsa_cam=1225898583&hsa_grp=891792013&hsa_ad=1559067673&hsa_net=linkedin&hsa_ver=3
- Board of CyberSince 12 Sept 2026
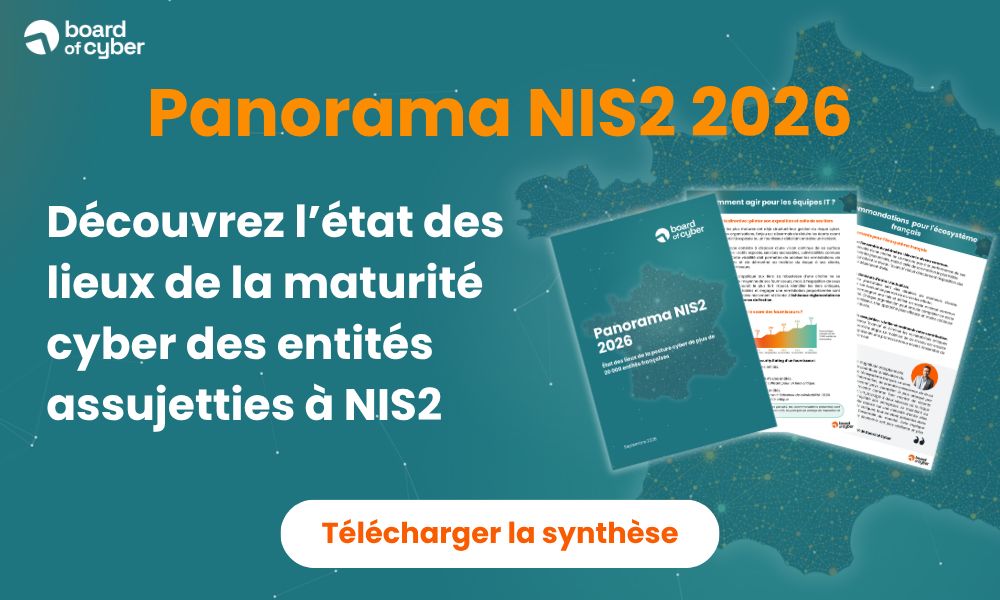
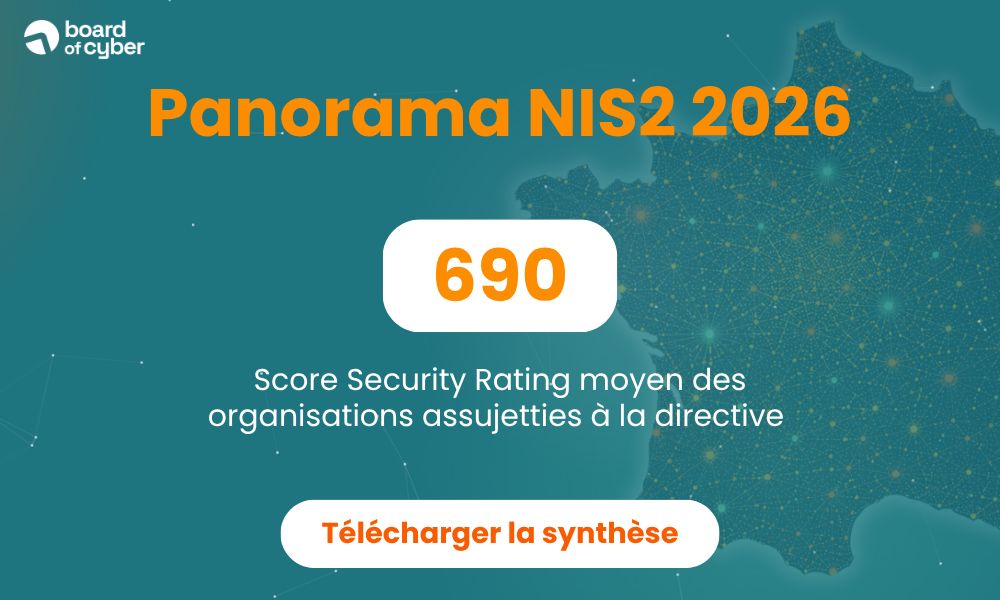
La résilience d’une organisation ne dépend pas uniquement de ses propres défenses. Une vulnérabilité exposée ou la défaillance d’un fournisseur critique peut interrompre l’activité, affecter les clients et fragiliser durablement la confiance. NIS2 place cette réalité au cœur de la gouvernance des organisations concernées. Découvrez les tendances issues de l’analyse de 2,8 millions d’actifs exposés appartenant à 21 800 entités françaises.
- Board of CyberSince 11 Sept 2026
La résilience d’une organisation ne dépend pas uniquement de ses propres défenses. Une vulnérabilité exposée ou la défaillance d’un fournisseur critique peut interrompre l’activité, affecter les clients et fragiliser durablement la confiance. NIS2 place cette réalité au cœur de la gouvernance des organisations concernées. Découvrez les tendances issues de l’analyse de 2,8 millions d’actifs exposés appartenant à 21 800 entités françaises.
- BioID GmbHSince 12 Sept 2026
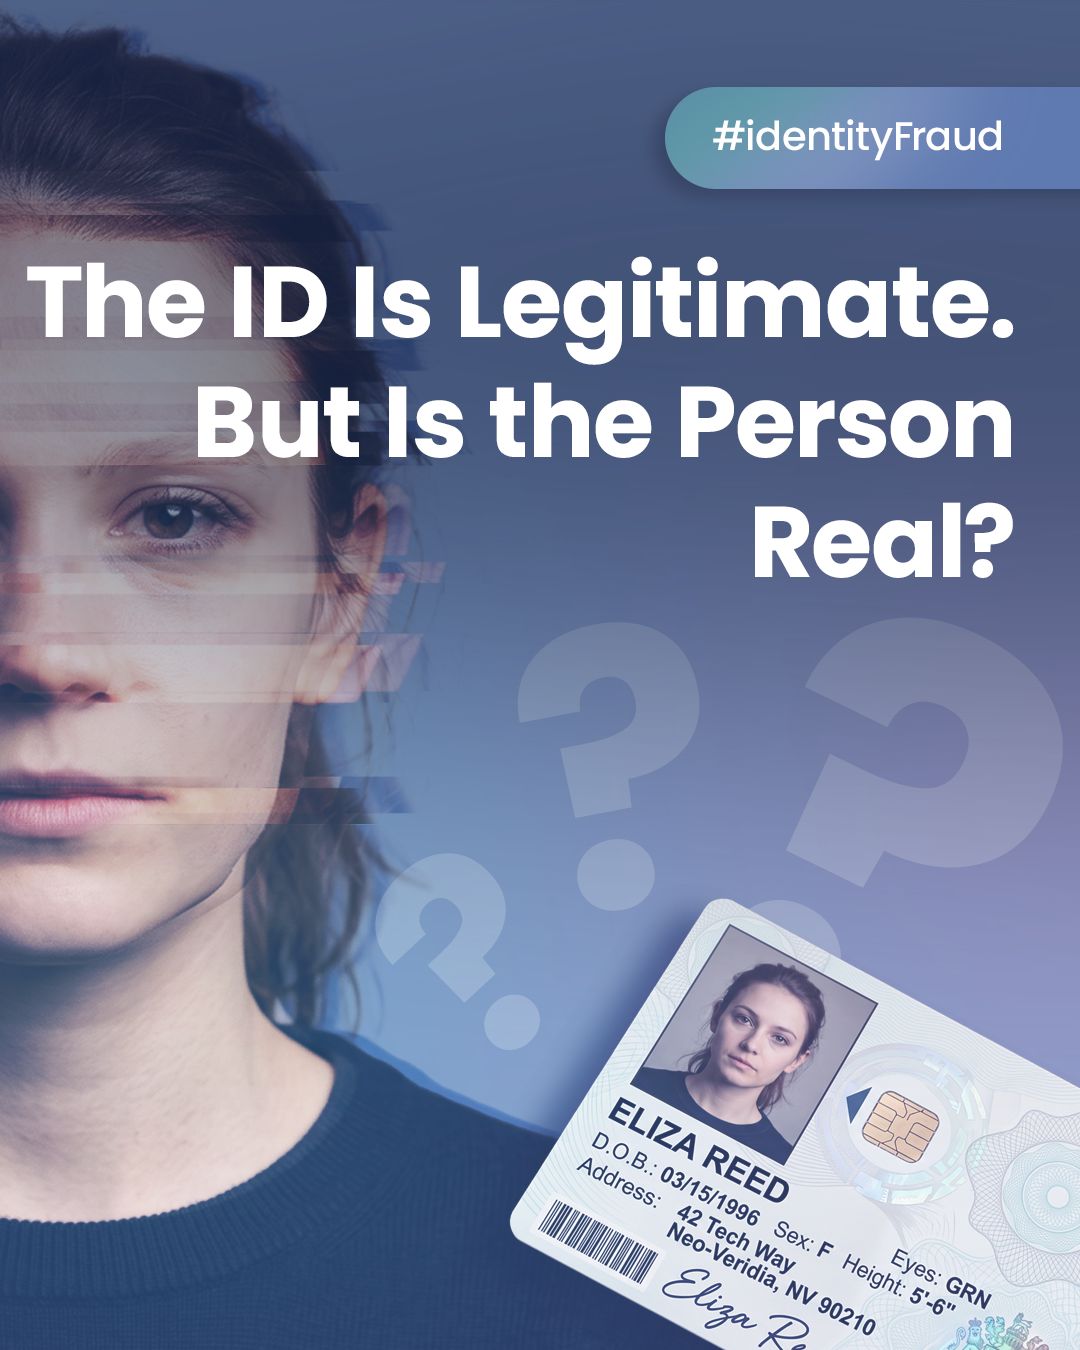
The ID Is Legitimate. But Is the Person Real? A deepfake is the content. An injection attack is the delivery method. Did you know that an attacker can potentially inject synthetic media directly into the processing pipeline without presenting it to a physical camera at all? Presentation Attack ↓ Fake content is presented to the camera. vs. Injection Attack ↓ Fake content is inserted in the biometric process, skipping/manipulating the real camera signal. BioID helps protect across these attack surfaces. 1️⃣ BioID's Face Liveness Detection is independently tested to ISO/IEC 30107-3 Level 3 / Level C for sophisticated presentation attacks. 2️⃣ BioID's injection attack detection (#IAD) helps, if a process is attacked differently - by injecting media directly, suggesting the photo or video is being captured live by the camera but instead using prerecorded or manipulated material. 3️⃣ Complementary AI-powered #deepfake detection helps identify synthetic or manipulated facial content - no matter if presentedto the camera or injected in the process. Interested? Test our tech at the BioID Playground! #bioid #identityfraud #deepfakedetection #injectionattack #deepfakes #biometrics #liveness
- DataKryptoSince 14 Sept 2026
How do you maintain confidentiality when an agentic workload crosses infrastructure boundaries? Telecom networks are becoming more autonomous, with AI workloads moving across models, agents, tools, and infrastructure. An agentic workload may extend across data centers, edge environments, cloud platforms, and other infrastructure. Trusted execution environments remain valuable for establishing trust in specific infrastructure, protecting cryptographic material, and verifying an execution environment. The challenge is keeping data and models confidential as the workload moves between those environments. In our new blog, SVP & Chief Growth Officer Paolo Campoli explains why the enclave is the wrong shape for an agentic workload and why confidentiality must move with the workload. Read the blog: https://ow.ly/EYwl50ZLHMJ
- CloberSince 15 Sept 2026
Spoiler: la renovación de tu hipervisor va a doler. Antes de que llegue la factura, puedes saber el número real. Sin sorpresas ni letra pequeña. Te ayudamos a ver cuánto vas a pagar si sigues como estás, y cuánto podrías ahorrar si cambias de enfoque. En menos de un minuto. Rellena el formulario y te lo calculamos.
- CloberSince 15 Sept 2026
Antes era un "y si cambiamos de proveedor...". Ahora es un hecho. Seguir dependiendo de un único fabricante ya tiene un coste real, y cada vez más empresas lo están revisando. Descubre en menos de un minuto cuánto podrías ahorrar con una infraestructura más independiente y flexible. Rellena el formulario y te lo calculamos.
- CCRCSince 15 Sept 2026
Hou je crisisteam klein, maar zorg dat communicatie vanaf minuut één aan tafel zit. Het klinkt als een detail. Maar mijn ervaring is dat het één van de belangrijkste succesfactoren is tijdens een crisis. Na honderden crisisoefeningen in verschillende sectoren zie ik telkens hetzelfde patroon. Zodra de druk toeneemt, groeit het crisisteam vanzelf. Er schuiven steeds meer mensen aan, omdat iedereen iets belangrijks wil inbrengen. Logisch. Maar niet verstandig. 👉 Een crisisteam is er niet om ieder inhoudelijk probleem op te lossen. Een crisisteam is er om besluiten te nemen. Daarom geloof ik in een klein, slagvaardig crisisteam. De inhoud organiseer je eromheen. Laat experts onderzoeken, analyseren en scenario's uitwerken. Maar houd de groep die de knopen doorhakt zo compact mogelijk. Er is echter één uitzondering: communicatie. Die moet vanaf het eerste moment aan tafel zitten. Nog te vaak zie ik dat communicatie pas wordt aangehaakt als er een persbericht, e-mail of klantupdate moet worden geschreven. Daarmee maak je de communicatieprofessional uitvoerder, terwijl die juist een strategische rol heeft. 💡 Een goede communicatieadviseur denkt niet alleen na over *wat* je communiceert, maar vooral over *wanneer*, *naar wie* en *welke impact* een boodschap heeft op klanten, medewerkers, leveranciers en de buitenwereld. Dat perspectief wil je niet pas achteraf toevoegen. Mijn stelling is daarom simpel: houd je crisisteam klein. Maar zorg dat communicatie vanaf minuut één een vaste stoel aan tafel heeft. Hoe is dat binnen jouw organisatie geregeld? Schuift communicatie direct aan bij een crisis, of pas wanneer de eerste boodschap de deur uit moet?
- CCRCSince 15 Sept 2026
We trainen elk jaar honderden bestuurders, CISO's en crisisteams. Van ziekenhuizen tot woningcorporaties, van brancheverenigingen tot universiteiten. ◾ Wat is het grootste probleem? Iemand moet beslissen, iemand moet bellen, iemand moet het naar buiten brengen. En precies dan kijkt iedereen aan tafel naar dezelfde drie mensen, en die drie mensen kijken naar elkaar. Dat is geen kennisprobleem en ook geen toolprobleem. Het is een rolprobleem en het lost zich niet op door er nóg een document aan toe te voegen. ✔️ Wat het wel doet: oefenen. Niet één keer, maar tot je team onder druk weet wat het moet doen zonder eerst rond te kijken. Daar zijn wij voor.
- BioID GmbHSince 16 Sept 2026
Biometrics Made in Germany – discussed this week at the annual Darmstadt Biometrics Week, hosted by Fraunhofer IGD. With an agenda full of #injection attack and #deepfake detection, this is just the right place to be for our team. Attending, presenting, demonstrating – as every year for decades, we are excited to support and learn. Biometrics is no longer only about what happens in front of the camera – this is our takeaway from the German @IT Security Association Germany (TeleTrusT) Biometrics Working Group workshop, organised in cooperation with the European Association of Biometrics (EAB) at Fraunhofer IGD. One of the highlights was the discussion around injection attacks, deepfakes and, particularly, how the attack surface is evolving. For years, much of the conversation around biometric attacks focused on what could be presented to the sensor: a photograph, mask or other physical artefacts. Injection attacks change the picture. An attack can take place after the biometric sensor and before signal processing, where biometric data or signals can potentially be manipulated or injected digitally. And this has an important consequence: Scalability. Unlike many physical presentation attacks, digital injection attacks can potentially be automated and repeated at scale across applications, devices and environments. The deepfake landscape makes this even more relevant. From face swaps and facial attribute editing to synthetic identities, face morphing and generated video, the ability to create increasingly convincing biometric content continues to evolve. We appreciated observing the evolution of terminology, standards, and threat models surrounding attack vectors that, from a technological standpoint, intersect with challenges the biometrics industry has been tackling for years under various names. The takeaway is simple: Biometric security cannot stop at asking whether the face looks real. We increasingly need to ask whether the entire biometric signal and processing pipeline can be trusted. This is where liveness detection, injection attack detection and deepfake detection increasingly come together. A very worthwhile day in Darmstadt, and another reminder that in digital identity, the attack surface keeps moving. #Biometrics #InjectionAttacks #Deepfakes #DigitalIdentity #LivenessDetection #CyberSecurity #Identity #TeleTrusT #EAB #Fraunhofer"
- CuebidSince 16 Sept 2026
När nätverket fungerar tänker få på det. När det inte fungerar kan medarbetare inte arbeta, system blir otillgängliga och verksamheten tappar fart. Nätverkskommunikation är inte bara en IT-fråga. Det är en förutsättning för en fungerande verksamhet.
- CuebidSince 16 Sept 2026
Nytt kontor. Fler medarbetare. Ett förvärv. Nya molntjänster. När verksamheten förändras behöver nätverket kunna följa med. Rätt nätverkskommunikation skapar förutsättningar för att växa och förändras utan att säkerhet, kontroll eller tillgänglighet blir en bromskloss.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.