LinkedIn image ad examples
1,339 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- D-Fend SolutionsSince 19 Oct 2026
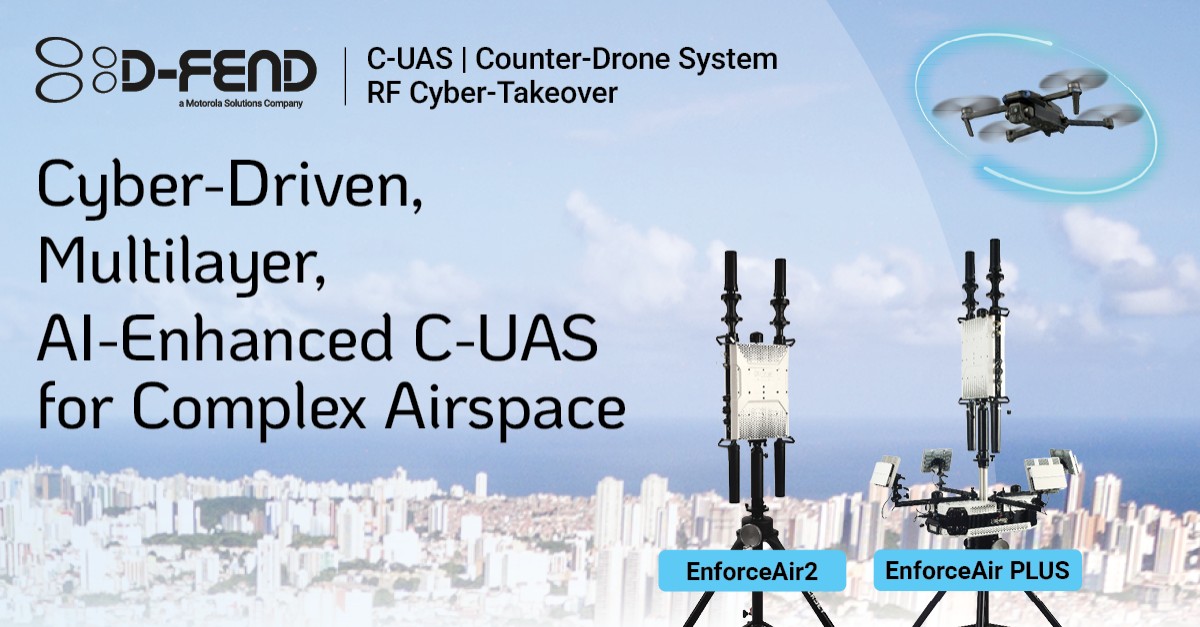
Protect complex airspace, without compromising operational continuity. Detect, identify, and mitigate drone threats with precise, controlled outcomes.
- CybleSince 19 Oct 2026
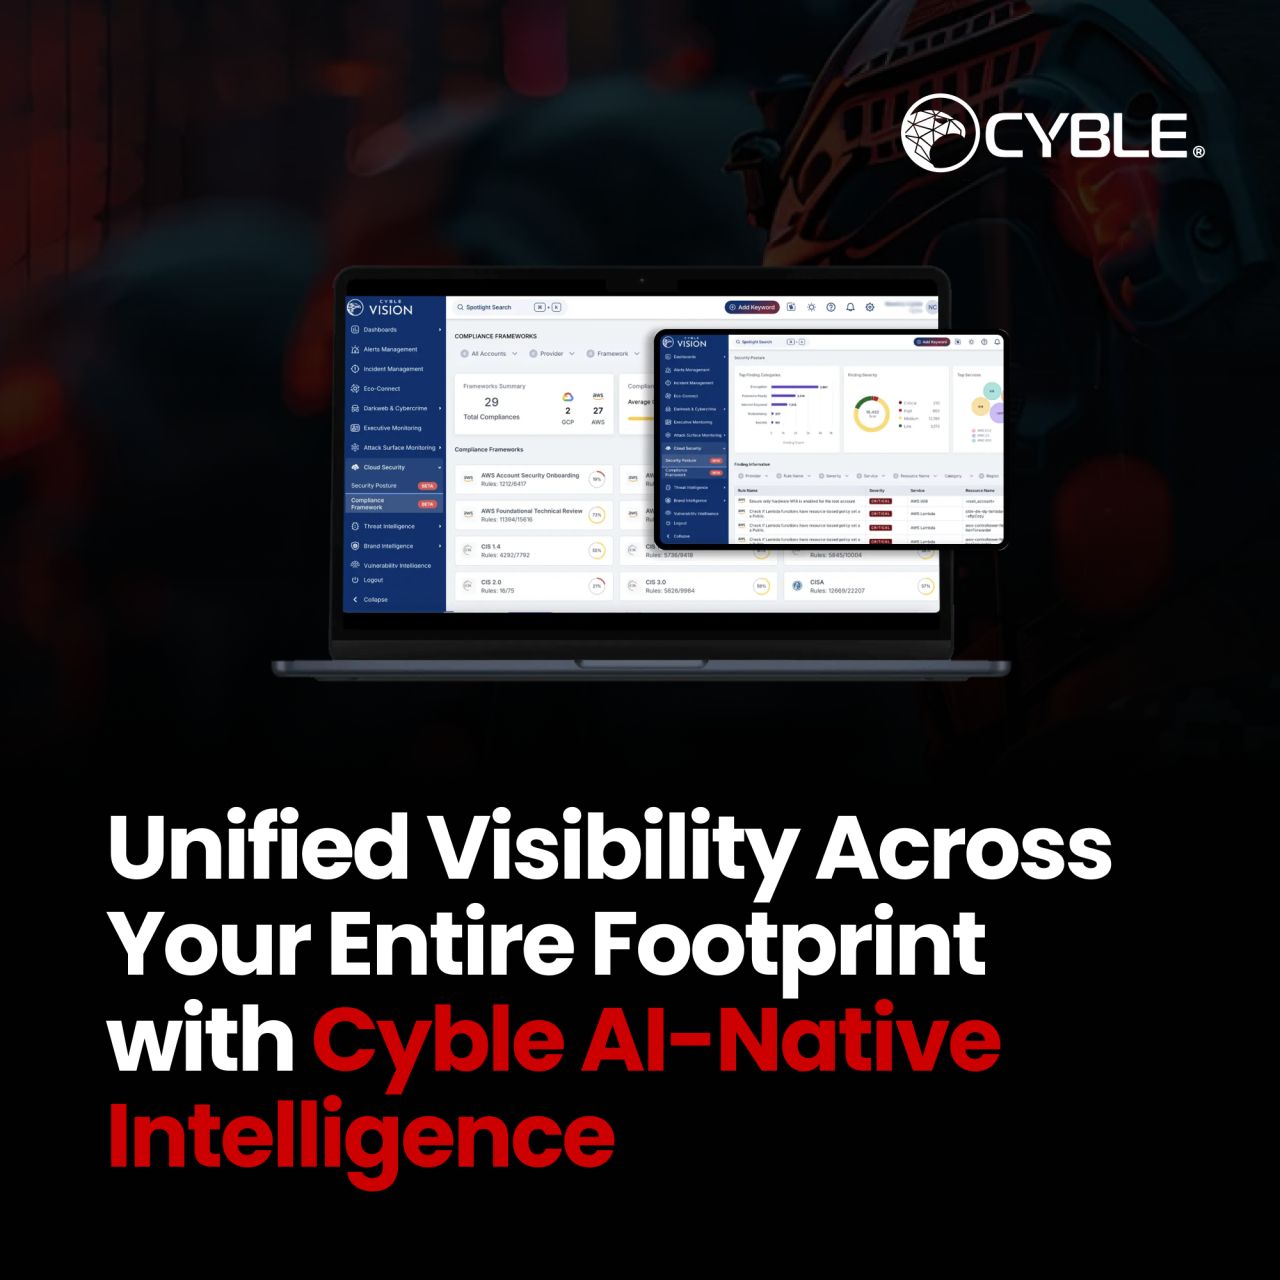
Digital transformation keeps expanding your attack surface. Every new cloud service, integration and vendor connection adds another asset that's hard to fully see. Cyble Vision unifies visibility across your entire footprint, cloud, on-prem and third-party. Blaze AI correlates it all, so nothing sits outside your control.
- CybleSince 19 Oct 2026
Not a login and a docs link. A Cyble analyst walks you through the platform across 14 days, on your schedule, against live threat data. Ask the awkward questions while someone who works the intelligence daily is on the call.
- Adversa AISince 18 Oct 2026
Vibe coding is now an enterprise problem. Employees are building internal dashboards, HR tools, and live CRM integrations. Security teams often don't have visibility into these apps and their build processes. The major conceptual mistake here is to treat "AI coding" as one generic risk category. Vibe coding is a completely new enterprise governance surface. To secure it, you have to split the trend into two materially different architectures: ☁️ Hosted AI builders (SaaS, e.g., Lovable, v0, Base44) The building happens in a vendor's cloud. The main security risks are insecure application design and data exposure, which are often completely invisible to your endpoint security. 💻 Local coding agents (e.g., Claude Code, Cursor, Copilot) These run on employee machines. The additive risk here is an autonomous agent misusing employee privileges and corporate credentials to cause as much damage as a determined insider could. Treating these as the same problem means you're applying the wrong security boundaries. Outright bans don’t work. AppSec, IT, and SOC teams need realistic "paved roads" instead: tenant settings and data classification for SaaS builders, combined with credential scoping, runtime monitoring, AIDR, and identity-level guardrails for local agents. Read our full analysis on how to secure the vibe coding era without relying on "no": https://lnkd.in/eFGnjG3u #Vibecoding #AIsecurity #AIGRC #AgenticAI #AIDR
- CyeraSince 17 Oct 2026
Data security is getting harder. Cyera makes it simpler. Identify exposure, reduce risk, and take action fast. Get a custom demo today.
- InfobloxSince 18 Oct 2026
Edge.Cloud. Zero Trust. Nichts davon funktioniert ohne sichere, skalierbare DDI. Lesen Sie jetzt den Leitfaden zur Modernisierung Ihres Netzwerkkerns.
- GitGuardianSince 17 Oct 2026
Your security stack is doing its job. It just wasn’t built to see the credential layer underneath it. ▪ Your vault protects the secrets registered with it. ▪ EDR watches the endpoint. ▪ Code scanning covers the repos it can reach. ▪ CNAPP maps the cloud. But credentials move across all of them: pipelines, laptops, Slack, Jira, container images, public GitHub, AI agent configs. There is no fixed inventory or single system of record. Each tool sees its slice. Nobody sees the whole layer, and that’s the gap attackers exploit. See how to secure yours at gitguardian.com/platform
- GitGuardianSince 17 Oct 2026
For a long time at GitGuardian, we secured secrets where we assumed they lived: in the code. Attackers found a new target recently: developer laptops (and obviously vibe coder laptops) Every major supply-chain attack pushed them toward the place credentials actually pile up the developer laptop. Shell histories, .env files, CLI caches, and now AI agent configs from Cursor, Copilot and Claude Code. Our early-access data: ~40% of them are written there by the AI agents themselves, in terminal sessions, output logs and caches no repo scanner ever checks. So we built for the assumption every security team should make: These devices will be compromised. The only question is whether you'll know what was on it. Today we're shipping Developer Endpoint Protection, built into ggshield: → Limit the blast radius → Detect live attacks with honeytokens → Remediate at the source Find and remediate critical exposed credentials before attackers can steal them
- CyberhavenSince 18 Oct 2026
Legacy DLP tools inspect files at a single point and miss data with no recognizable pattern: source code, product designs, business plans, meeting recordings. Cyberhaven traces the full journey of every sensitive file, cutting false positives by 90% so security teams can act on real risk instead of sorting through false alarms.
- BigIDSince 18 Oct 2026
The University of Maryland faced a familiar yet daunting challenge: sprawling cloud data, scattered sensitive records, and increasing exposure to risk. Their solution? BigID.
- CyberhavenSince 18 Oct 2026
Employee use of GenAI applications stalled between December and June. Data moving through those same tools grew 80% year over year. Cyberhaven's mid-year report lays out what that shift means for enterprise security programs.
- Above SecurityRecorded 19 Oct 2026
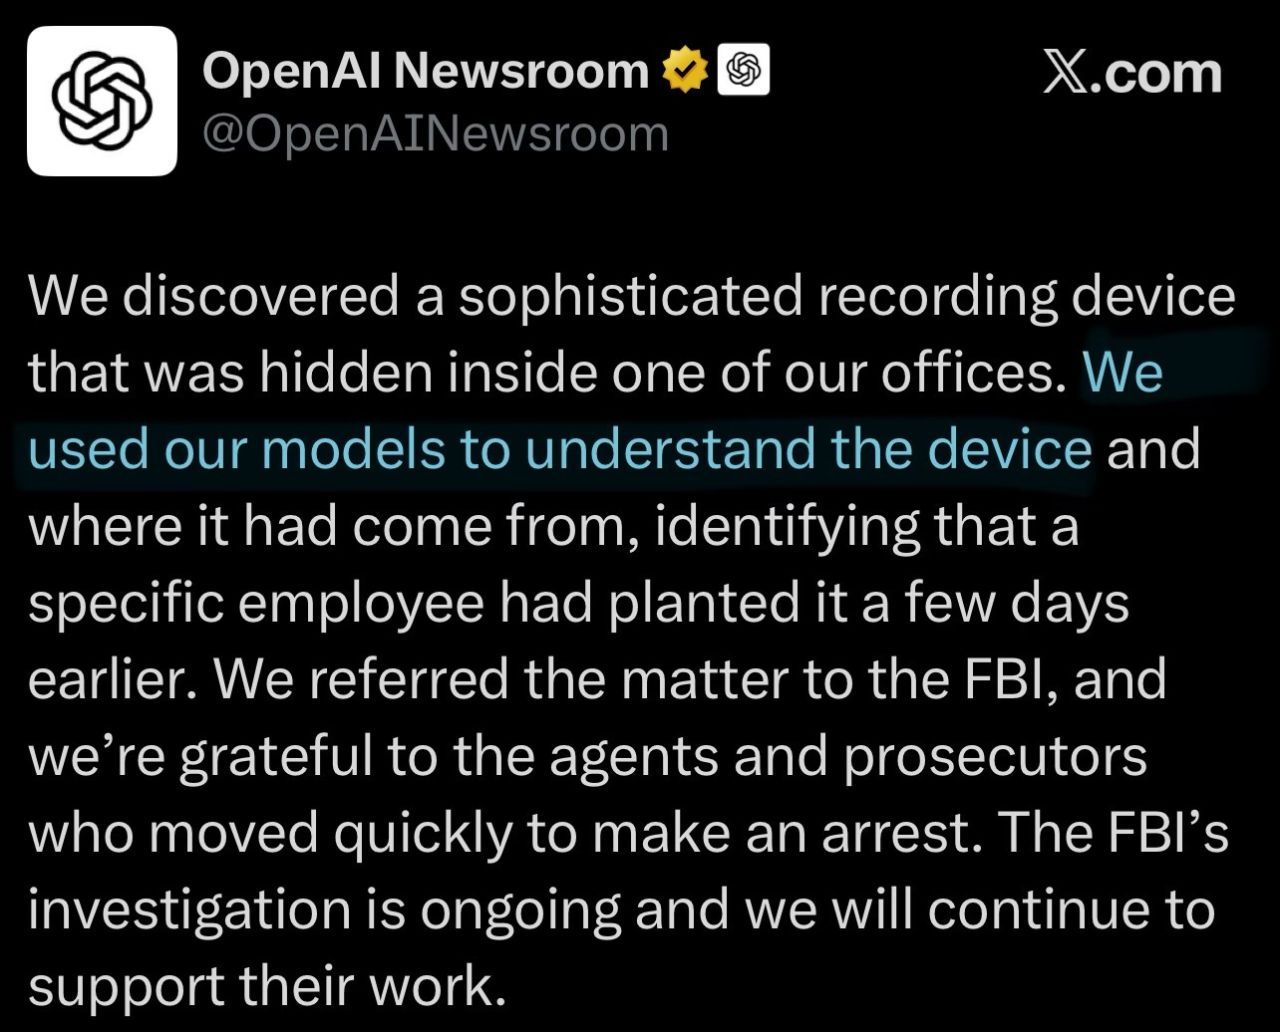
Insider risk should be managed left of boom. A pretty extreme case of malicious insider threat. Insider threats come in every color, from malicious espionage to simple negligence. But what interests me is what happened before they found the device. I'm sure there were earlier behavioral signals that, when connected, could have raised suspicion. Not when you discover the recording device, but when the risk starts developing.
- KasperskySince 16 Oct 2026
Grow your business, not your cyber risks. As your business grows, so do the cyber risks. But protecting your business doesn’t have to mean adding complexity or stretching your resources. Join our webinar on October 27 to discover practical ways to strengthen cybersecurity, protect customer trust, and keep your business running smoothly. 📅 Save your spot and learn how to make cybersecurity work for your business. 👉 Register now!
- A-LIGNSince 17 Oct 2026
Your path to AI governance starts with ISO 42001 certification. A-LIGN was among the first accredited certification bodies for the standard, with nearly 6,000 ISO assessments completed globally. See how we can help. Book a meeting with our team today.
- E-GÜVENSince 16 Oct 2026
Klasörlerle dolu arşiv odaları hem yüksek maliyet yaratır hem de aradığınız evraklarınıza erişiminizi zorlaştırır. E-Güven ile kağıt kullanımını sıfıra indirin; hızlıca imzalamanız gereken evraklarda zaman ve maliyetten tasarruf edin!
- IDECSISince 16 Oct 2026
La plupart des environnements M365 ont des failles actives. Pas par manque de budget. Par manque de méthode. 30 contrôles. Une grille d'évaluation. Une méthodologie claire. Téléchargez la checklist et sachez où vous en êtes avant vendredi.
- Cyber360 | Specjaliści od cyberbezpieczeństwaSince 16 Oct 2026
Kolejny samorząd na celowniku cyberprzestępców: Urząd Miejski w zachodniopomorskim potwierdza nieautoryzowany dostęp do swoich systemów. Jak poinformował portal CyberDefence24, w Urzędzie Miejskim w Darłowie doszło do przełamania zabezpieczeń. Atakujący wykorzystali niezałataną podatność w oprogramowaniu, uzyskując dostęp do infrastruktury informatycznej oraz części danych petentów. To kolejny polski samorząd w tym roku – po Myszkowie, Nowej Rudzie, Lewinie Kłodzkim czy Gminie Obrazów – który musi mierzyć się z paraliżem operacyjnym oraz potencjalnym wyciekiem danych mieszkańców. 🏛️ Co jest DZIŚ kluczowe dla administracji publicznej? Samorządy i urzędy nie są już dla hakerów celem „przy okazji” – stały się celem numer jeden ze względu na wrażliwość przetwarzanych danych i często przestarzałą infrastrukturę IT. Dyrektorzy, Włodarze i Szefowie IT w samorządach muszą szybko spełnić 3 kluczowe warunki: 1️⃣ Natychmiastowe zarządzanie podatnościami (Vulnerability Management): Atak w Darłowie powiódł się przez niewyłapaną na czas lukę w oprogramowaniu. Urzędy muszą wdrożyć ciągłe skanowanie podatności oraz procedurę natychmiastowego łatania systemów wystawionych do internetu (Patch Management). 2️⃣ Czas na spełnienie wymogów NIS2 / uKSC drastycznie się kurczy: Nadchodzące zmiany w prawie jednoznacznie włączają samorządy (urzędy miast, starostwa, spółki komunalne) do reżimu KSC. Oznacza to osobistą odpowiedzialność kierowników jednostek za brak wdrożonych procedur i audytów bezpieczeństwa. 3️⃣ Monitorowanie sieci 24/7 (SOC) i ciągłość działania: Brak całodobowego monitoringu sprawia, że przestępcy poruszają się po sieci urzędu przez wiele dni niezauważeni. Samorządy muszą przestawić się z modelu „reagujemy po fakcie” na stałą stałą ochronę. Jak Wasza jednostka radzi sobie z audytem podatności zewnętrznych oraz przygotowaniem do wymogów NIS2? W Cyber360 przygotowaliśmy dedykowaną ofertę stworzoną z myślą o gminach, powiatach i jednostkach samorządowych. Umów się na krótkie spotkanie (link w komentarzu) i sprawdź specjalne warunki wsparcia.
- Fox-ITSince 16 Oct 2026
As AI accelerates vulnerability discovery and exploitation, security teams are under increasing pressure to make faster, better informed decisions. But speed alone is not enough. Organisations need to understand which vulnerabilities are most exploitable, how they connect across environments, and which remediation actions will reduce risk most effectively. Natalie Walker’s latest article looks at the ECB’s recent call to action for financial institutions but it’s also a message that will resonate far beyond financial services. Read now 👇 https://lnkd.in/dJQXJup7 #CyberResilience #RiskManagement #Banking #FinancialServices #Industry #AIGovernance #EUFinance #ECB
- Fox-ITSince 16 Oct 2026
The ECB’s recent letter to significant financial institutions is a clear signal: organisations can no longer rely on vulnerability volume alone to understand exposure. As AI accelerates vulnerability discovery, exploit development and attack-path analysis, the real question becomes: Which weaknesses are genuinely exploitable, how could they be combined, and what action will reduce risk fastest? Natalie Walker’s latest article explores what the ECB is asking banks to address, why the issue extends beyond financial services, and how organisations can respond with greater clarity across visibility, prioritisation, remediation and resilience. Read now 👇 https://lnkd.in/dJQXJup7 #CyberResilience #RiskManagement #BankingFinancialServices #AIGovernance #EUFinance #ECB
- ESET DACHSince 16 Oct 2026
Wie im Spitzensport entscheidet Prävention über den Erfolg. ESET MDR stoppt Angriffe, bevor sie Auswirkungen haben.
- ESET DACHSince 16 Oct 2026
Wenn Systeme ausfallen, steht oft mehr als nur die IT still. Schützen Sie Ihr Unternehmen mit ESET.
- InfusionPoints, LLCRecorded 18 Oct 2026
FedRAMP CR26 is changing the way Cloud Service Providers approach security, compliance, and continuous authorization readiness. Whether you're already on the FedRAMP Marketplace or preparing for what's next, understanding these changes is critical. Download InfusionPoints' FedRAMP CR26 CSP Playbook for practical guidance to help your team navigate evolving requirements and prepare for the future of FedRAMP.
- IncodeSince 15 Oct 2026
Verify licence and identity before pickup, so customers go straight to the car. - Internal Audience Notice: This content has been specifically tailored for employees of Europcar. It is not intended for public distribution. -
- InfusionPoints, LLCRecorded 18 Oct 2026
The clock is ticking for FedRAMP Rev. 5 providers. Beginning December 7, 2026, FedRAMP's new Vulnerability Detection and Response (VDR) and Vulnerability Evaluation and Reporting (VER) requirements take effect under CR26 and CISA BOD 26-04. For Cloud Service Providers (CSPs), this means rethinking how vulnerabilities are detected, prioritized, managed, and reported. Maintaining your FedRAMP certification requires more than keeping up with yesterday's compliance processes. Is your organization prepared for what's next? Download InfusionPoints' FedRAMP CR26 CSP Playbook to understand the evolving requirements and take the next steps toward continuous compliance readiness.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.