LinkedIn image ad examples
1,352 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- Encryption Consulting LLCSince 23 Oct 2026
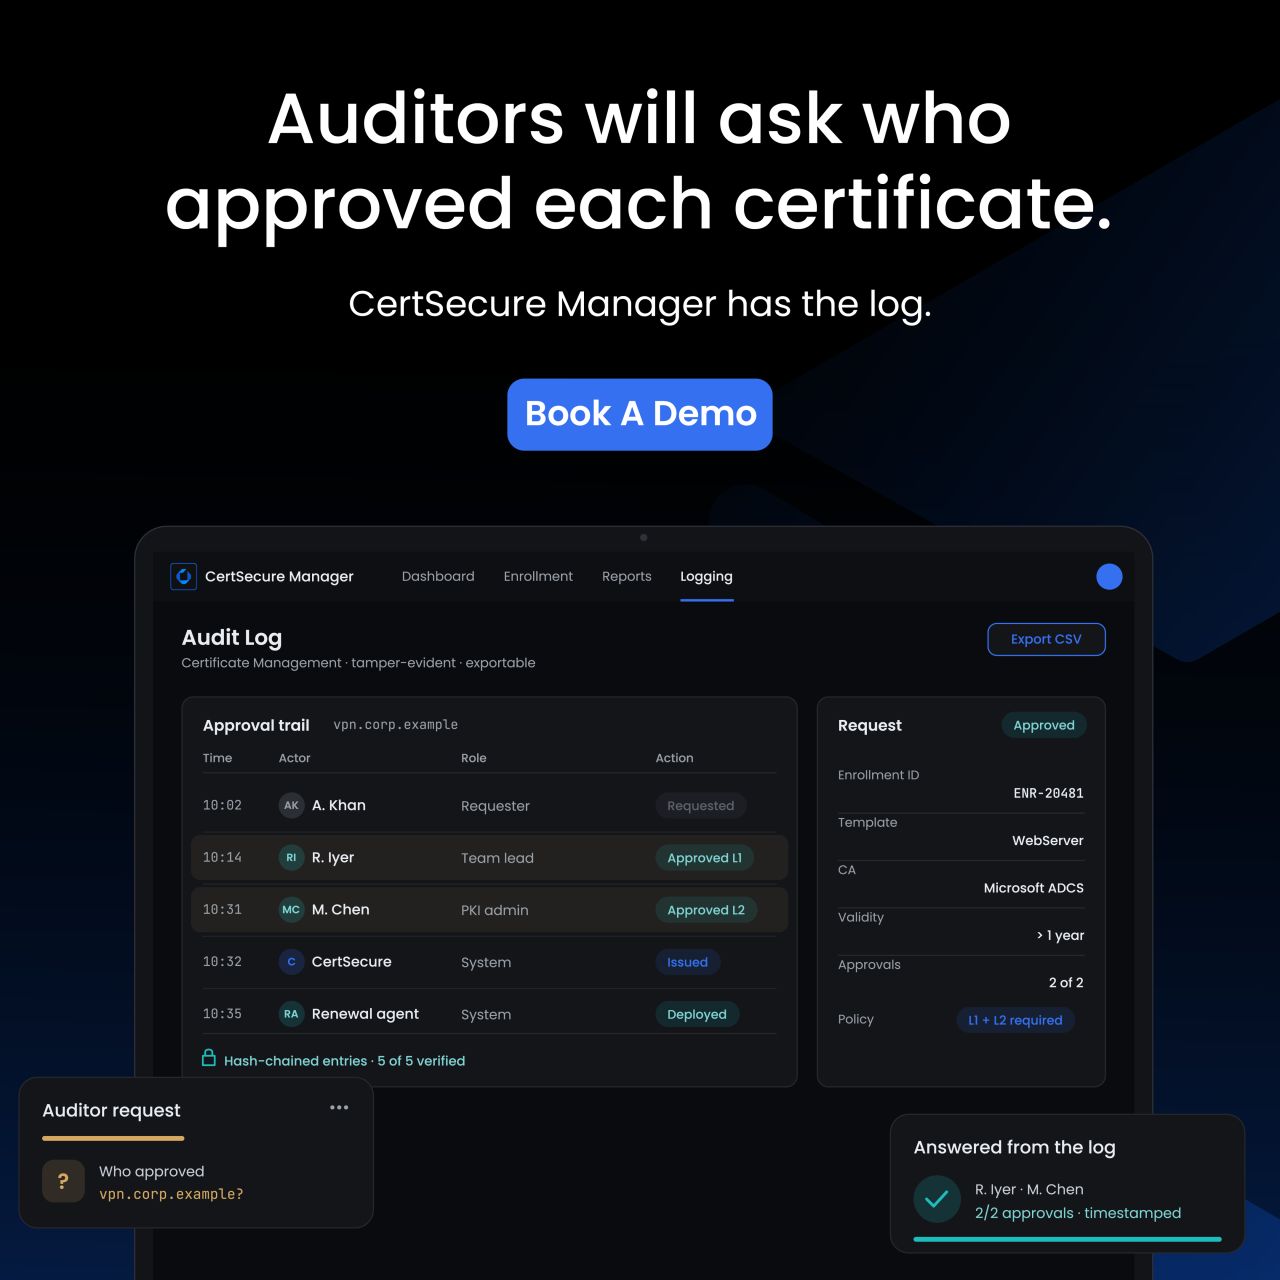
Who approved this certificate? With CertSecure Manager, the answer is 1 click, with a full tamper-evident trail auditors accept. Book a demo.
- GEUTEBRÜCK GmbHSince 21 Oct 2026
Der Vorfall dauert wenige Minuten. Die Folgen für die Wasserversorgung können weit länger anhalten. Entscheidend ist, was in diesen Minuten passiert. Wie Wasserver- und Abwasserentsorger Vorfälle erkennen, während sie geschehen – und handlungsfähig bleiben.
- GEUTEBRÜCK GmbHSince 21 Oct 2026
Mehr Bedrohungen. Mehr Anforderungen. Mehr Verantwortung. Aber nicht mehr Ressourcen. Resilienz in der Wasserversorgung entsteht dort, wo Risiken früh erkannt und Reaktionen vorbereitet sind.
- ArnicaRecorded 24 Oct 2026
Most AppSec tools are judged on what they find. The better test is what happens after a PR merges. Use this checklist to pressure-test any vendor across your whole development cycle.
- Abnormal AISince 22 Oct 2026
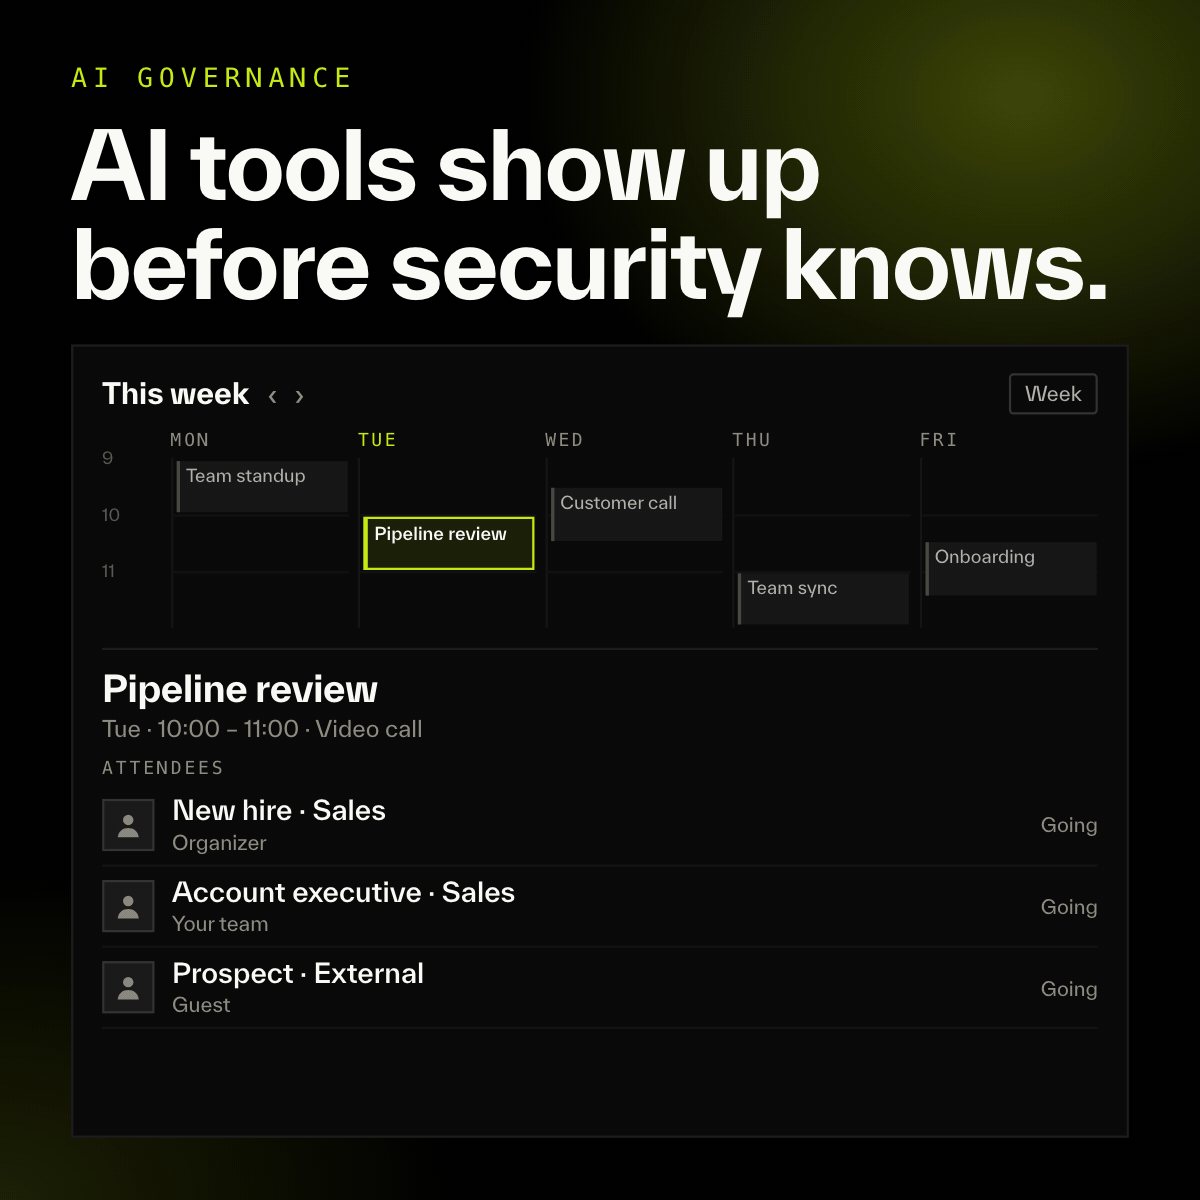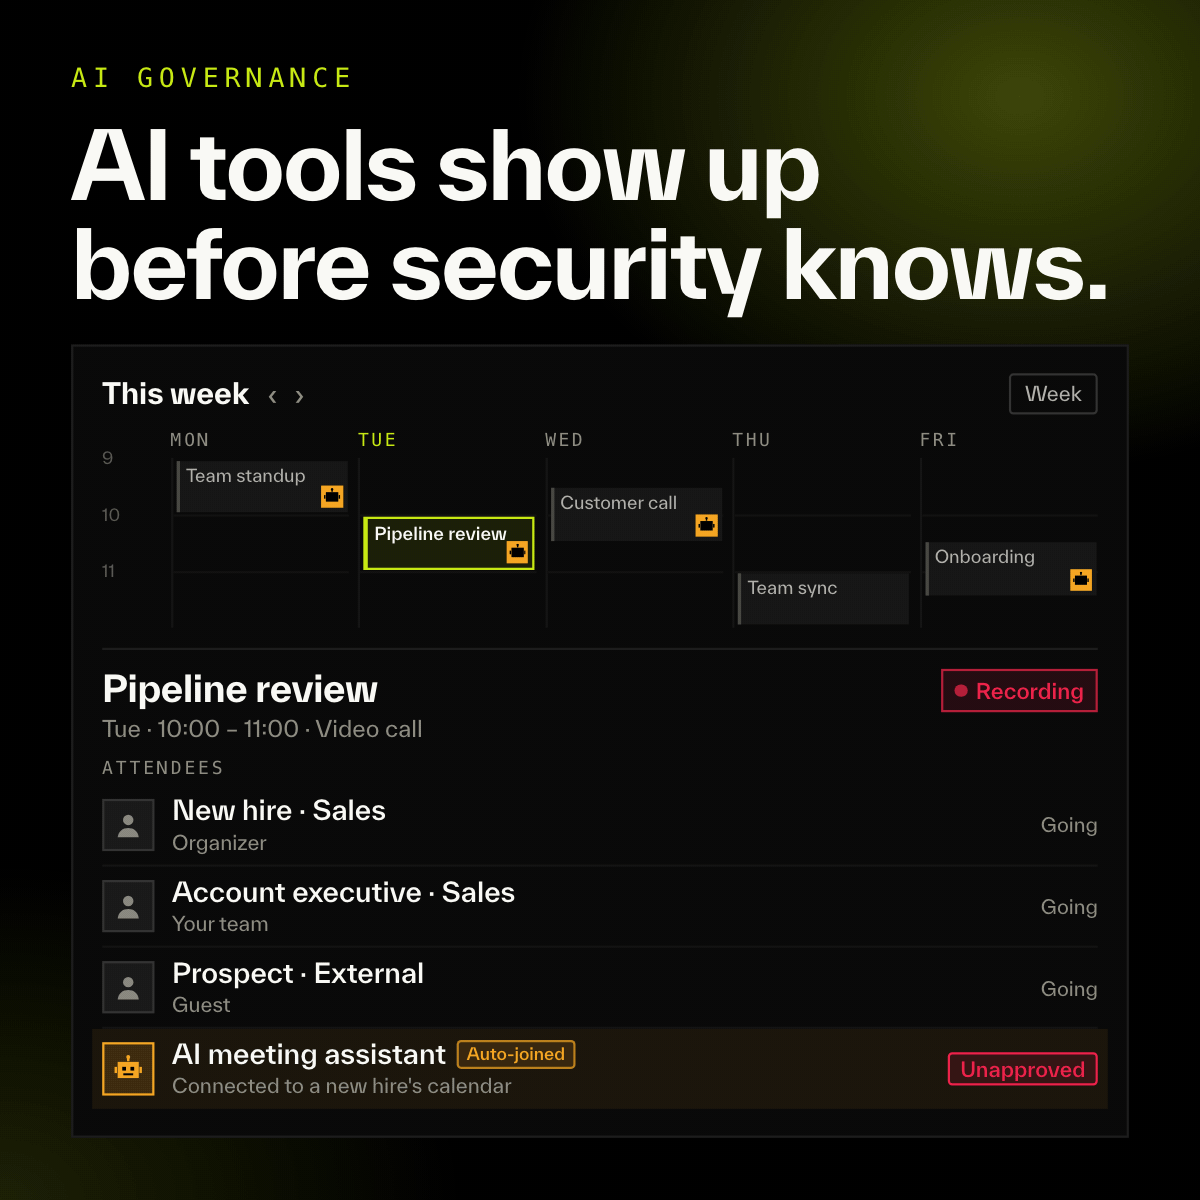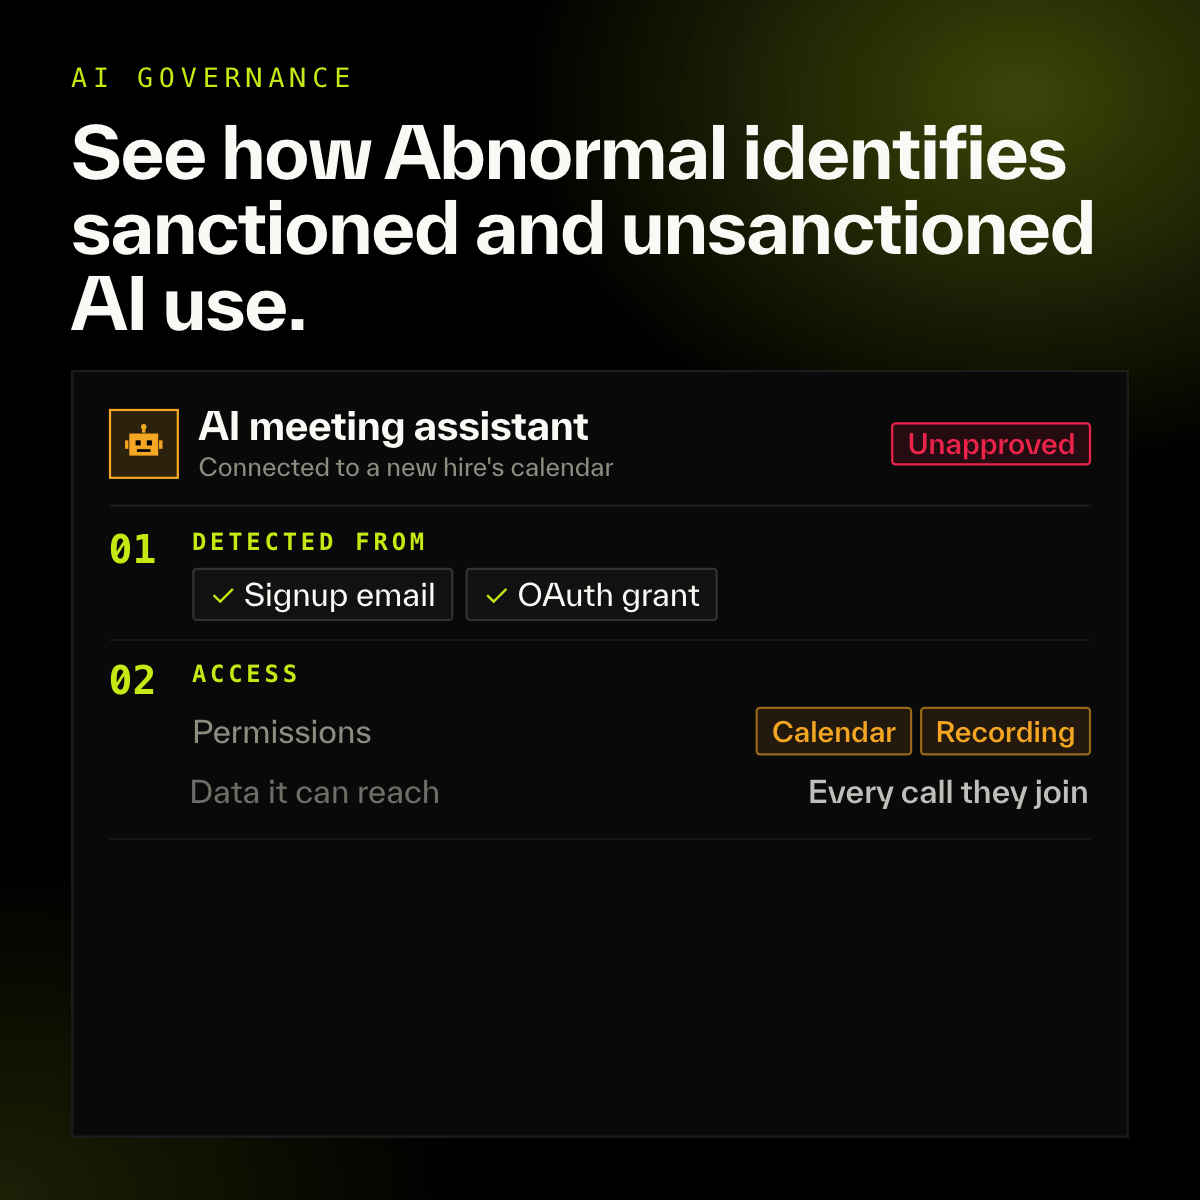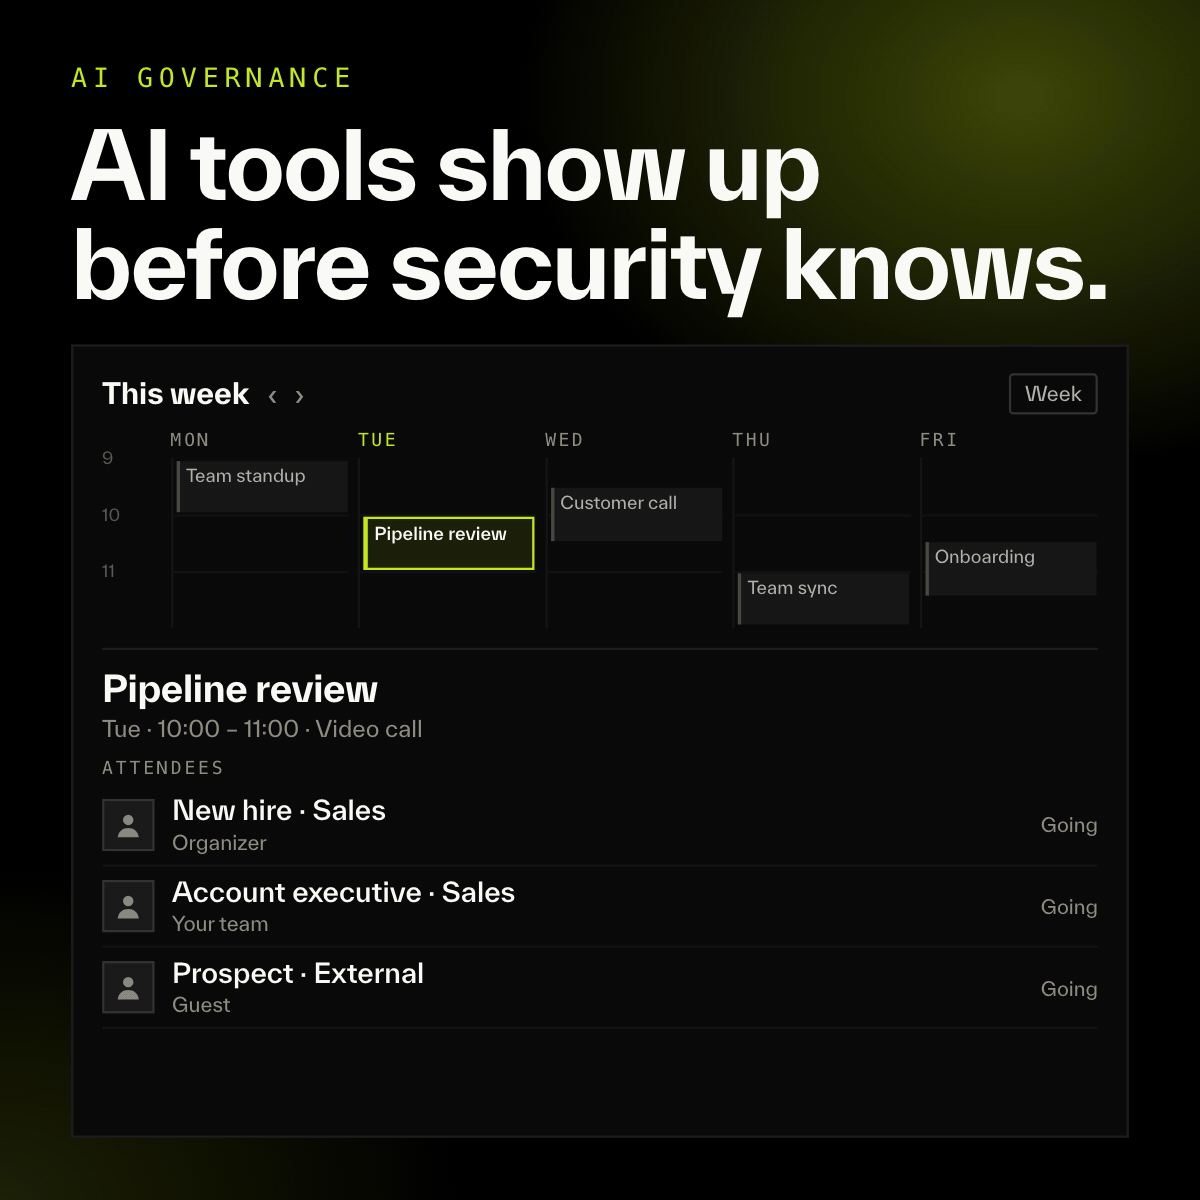
An unapproved AI meeting assistant can reach every call a new hire joins. Request a demo to see Abnormal route it for an approval decision.
- Abnormal AISince 22 Oct 2026
AI use is spreading across your business faster than manual reviews can keep up. Abnormal helps security teams see AI activity across email, identity, SaaS, browser activity, and AI provider APIs.
- CYBEROOSince 20 Oct 2026
I rischi informatici non sono (solo) un problema tecnico: sono un tema di cultura organizzativa. Quando la formazione è generica, l'attenzione cala, e con lei la protezione. Per difendere reputazione e continuità serve un apprendimento continuo: guidato dall'AI adattiva, personalizzato per ruolo, capace di trasformare un rischio diffuso in una competenza diffusa. 👉 Scarica il whitepaper e scopri come ripensare la formazione aziendale come leva di change management.
- CyoloSince 20 Oct 2026
Every third-party session, tied to an identity, fully auditable. Cyolo deploys in a day, no hardware, no disruption. See it live.
- CINI Cybersecurity National LabSince 20 Oct 2026
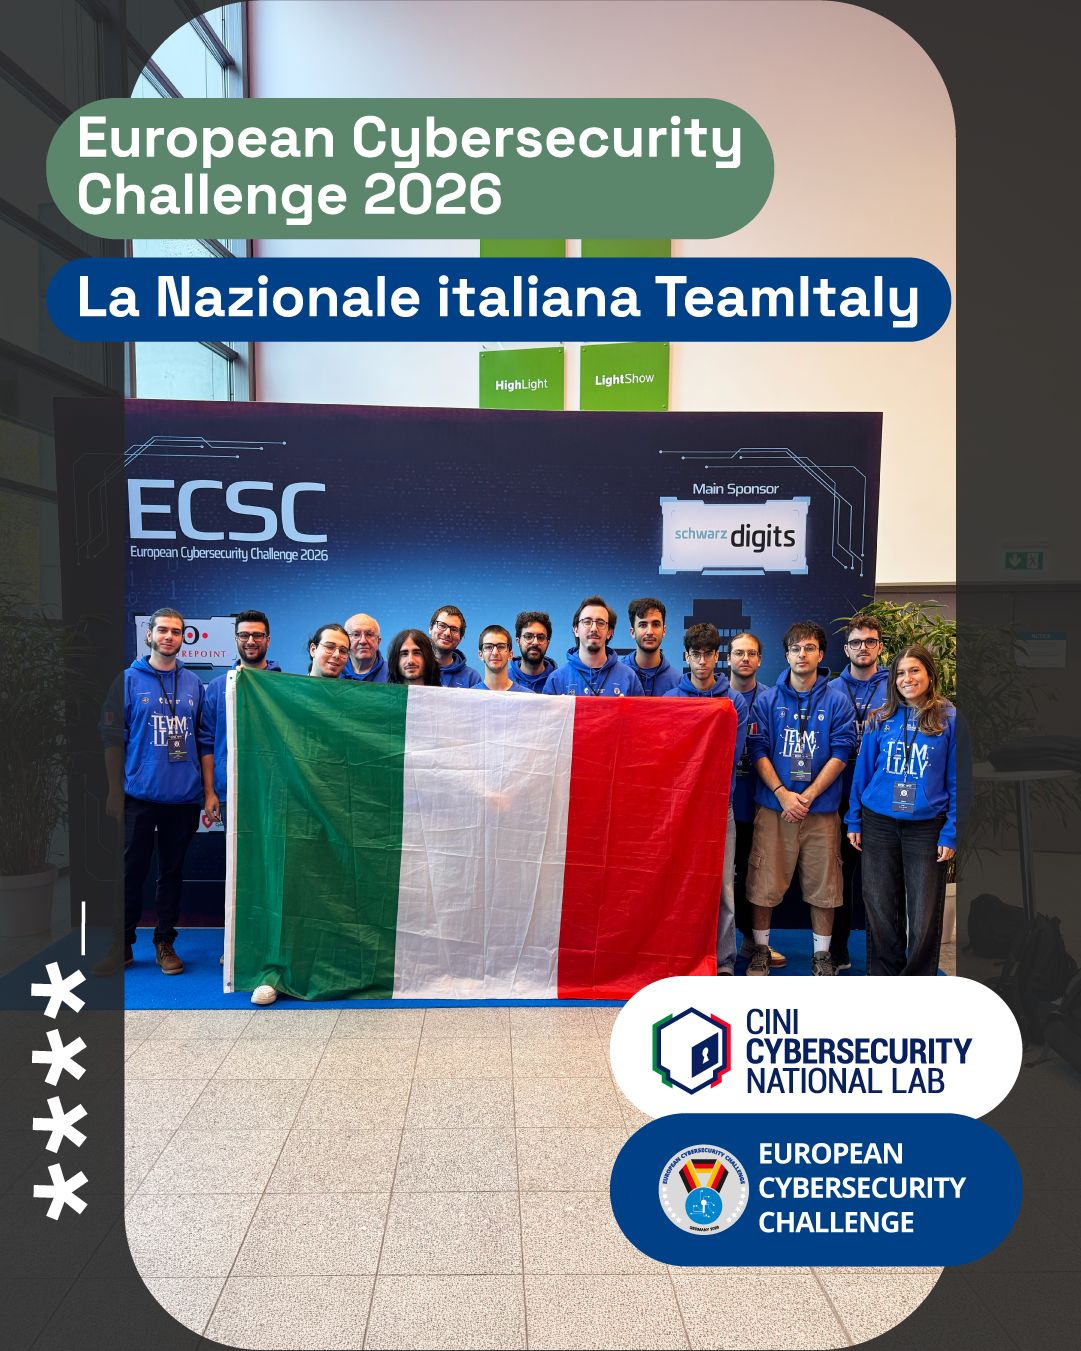
🇮🇹👕 Ecco il TeamItaly che ha portato i colori dell’Italia alla 12ª edizione dell’European Cybersecurity Challenge (ECSC) 2026. A Bochum, il team azzurro di giovani cyber talenti si è confrontato con le migliori squadre nazionali d’Europa e dei Paesi ospiti invitati, conquistando il 10° posto nella classifica ufficiale e vivendo giorni di prove in cui la cooperazione e la rapidità decisionale del gruppo hanno fatto la differenza. Un’esperienza che va oltre il risultato finale: restano nuovi incontri, nuove consapevolezze e ricordi da portare con sé. 👏 Grazie ai nostri ragazzi per aver vissuto fino in fondo questa sfida e a tutte le persone che li hanno accompagnati lungo il percorso. #CybersecurityNationalLab #TeamItaly #ECSC2026 #cybersecurity
- CloudworksSince 21 Oct 2026
"Over 35% of organizations align to existing maturity models, yet these frameworks lack AI-specific controls, limiting effectiveness against emerging threats." – Gartner® If your Zero Trust model predates your AI rollout, this report is worth a read. It covers three concrete use cases for securing AI, including how to handle AI agents and LLMs. Download the report here 👇
- CyoloSince 20 Oct 2026
Air-gapped, on-prem, or cloud-connected: Cyolo secures OT access everywhere, no infrastructure changes, no downtime. Speak to an expert.
- CYBEROOSince 20 Oct 2026
Le tue persone sono il tuo rischio informatico più grande. O la tua difesa più forte. La differenza la fa un solo fattore: quanto li hai preparati davvero. Regole e slide non bastano. Serve allenamento reale, che entri nei gesti di ogni giorno e resista anche nei momenti di pressione. 👉 Leggi il whitepaper e scopri come trasformare ogni persona in un presidio di sicurezza.
- ANSSI - Côte d'IvoireRecorded 23 Oct 2026
𝗖𝗬𝗕𝗘𝗥.𝗘𝗫 𝟮𝟬𝟮𝟲 𝗽𝗿𝗲́𝘀𝗲𝗻𝘁𝗲 𝘀𝗼𝗻 𝗽𝗮𝗿𝘁𝗲𝗻𝗮𝗶𝗿𝗲 𝗼𝗳𝗳𝗶𝗰𝗶𝗲𝗹 𝗱𝗲 𝗹𝗮 𝗰𝗮𝘁𝗲́𝗴𝗼𝗿𝗶𝗲 𝗣𝗔𝗦𝗦𝗜 L'Agence Nationale de la Sécurité des Systèmes d'Information de Côte d'Ivoire (ANSSI-CI) a le plaisir d'annoncer que 𝗞𝗔𝗬𝗗𝗔𝗡 𝗧𝗘𝗖𝗛𝗡𝗢𝗟𝗢𝗚𝗬 rejoint le CYBER.EX 2026 en qualité de Partenaire Officiel de la catégorie 𝗣𝗿𝗲𝘀𝘁𝗮𝘁𝗮𝗶𝗿𝗲 𝗱'𝗔𝘂𝗱𝗶𝘁 𝗱𝗲 𝗦𝗲́𝗰𝘂𝗿𝗶𝘁𝗲́ 𝗱𝗲𝘀 𝗦𝗜 (𝗣𝗔𝗦𝗦𝗜) 𝗮𝗴𝗿𝗲́𝗲 Avant qu'une attaque ne survienne, il faut savoir où elle pourrait frapper. C'est précisément le métier de Kaydan Technology : évaluer, tester et renforcer la sécurité des organisations. Son regard d'auditeur viendra enrichir l'exercice et les enseignements que chaque participant en retirera. 𝗕𝗶𝗲𝗻𝘃𝗲𝗻𝘂𝗲 𝗮̀ 𝗞𝗮𝘆𝗱𝗮𝗻 𝗧𝗲𝗰𝗵𝗻𝗼𝗹𝗼𝗴𝘆 𝗱𝗮𝗻𝘀 𝗹'𝗮𝘃𝗲𝗻𝘁𝘂𝗿𝗲 𝗖𝗬𝗕𝗘𝗥.𝗘𝗫. 28 et 29 octobre 2026 Hôtel Radisson, Abidjan [email protected] (225) 07 78 00 54 00 #anssici #KaydanTechnology #CYBEREX2026 #Audit #Cybersécurité #CôteDIvoire
- ChainguardSince 21 Oct 2026
If your supply chain defense only checks public sources, it can't see the malware nobody has reported yet, and that blind spot is bigger than most people assume. Resilient Cyber partner Chainguard just shared data from their Go and .NET beta. Their scanner returned malware verdicts on more than 5,000 packages, and over 10% of those had no match in any public source when they were caught. I've been saying for a while that we can't keep treating the software supply chain as a reactive problem. Attackers are using AI to scale their campaigns and make them more convincing, and if you only learn about a malicious package after it's been pulled into a build, you're always going to be a step behind. The control belongs earlier, stopping the bad package before anything pulls it in. That's the direction Chainguard is taking as Chainguard Libraries expands into Go and .NET in early access, scanning endpoints for malware and greyware and adding a configurable cooldown so brand new packages don't land in your environment the minute they're published. Check it out if Go or .NET are part of your stack https://lnkd.in/e5eF9jgD
- CloudworksSince 21 Oct 2026
AI agents act on their own, access data, and call other systems. That makes them identities, and they need the same control as everyone else. This Gartner® report looks at how to extend Zero Trust to AI, with practical steps for visibility, governance, and agent-level controls. Get your copy below.
- ANSSI - Côte d'IvoireRecorded 23 Oct 2026
𝗖𝗬𝗕𝗘𝗥.𝗘𝗫 𝟮𝟬𝟮𝟲 𝗣𝗥𝗘́𝗦𝗘𝗡𝗧𝗘 𝗦𝗢𝗡 𝗣𝗔𝗥𝗧𝗘𝗡𝗔𝗜𝗥𝗘 𝗢𝗙𝗙𝗜𝗖𝗜𝗘𝗟 𝗗𝗘 𝗟𝗔 𝗖𝗔𝗧𝗘́𝗚𝗢𝗥𝗜𝗘 𝗢𝗣𝗘́𝗥𝗔𝗧𝗘𝗨𝗥 L’Agence Nationale de la Sécurité des Systèmes d’Information de Côte d’Ivoire (ANSSI-CI) a le plaisir d’annoncer que 𝗢𝗥𝗔𝗡𝗚𝗘 𝗖𝗢̂𝗧𝗘 𝗗’𝗜𝗩𝗢𝗜𝗥𝗘 rejoint le CYBER.EX 2026 en qualité de Partenaire Officiel de la catégorie Opérateur. Un opérateur au service de millions d’abonnés. Des infrastructures au cœur de la vie quotidienne des Ivoiriens. Un engagement concret pour la résilience numérique nationale. Lorsque la crise frappe, la continuité des communications devient une priorité absolue. Avec Orange à nos côtés, le CYBER.EX gagne un acteur clé pour éprouver cette continuité en conditions réelles. 28 et 29 octobre 2026 Hôtel Radisson, Abidjan [email protected] (+225) 07 78 00 54 00 𝗩𝗶𝘃𝗿𝗲 𝗹𝗮 𝗰𝗿𝗶𝘀𝗲 𝗽𝗼𝘂𝗿 𝗺𝗶𝗲𝘂𝘅 𝘀𝗲 𝗽𝗿𝗲́𝗽𝗮𝗿𝗲𝗿 𝗮̀ 𝗹𝗮 𝘃𝗿𝗮𝗶𝗲. #CYBEREX2026 #ANSSICI #OrangeCotedIvoire #Cybersecurite #ResilienceNumerique #CotedIvoire
- ChainguardSince 21 Oct 2026
ICYMI this week - Chainguard can now run our frontier model harness on your first party apps. Connect a repo and let it hunt. We've tuned this for deep searches and all findings are validated with real exploit chains in our sandbox environment. No false positives, a true deep scan on your code. Powered by Mythos 5.1 and available through the Anthropic Marketplace. It'll find issues in your code, your third-party code, and chains between all of it. We'll tell you how to remediate, deal with any upstream disclosures, and can run again after to be sure you've remediated. https://lnkd.in/g2Nx3xY6
- IST AMERICASRecorded 23 Oct 2026
La adopción de Inteligencia Artificial avanza rápido. El reto ahora es hacerlo sin perder visibilidad, seguridad ni control. Te invitamos a nuestro After Office: AI Governance & Control, un espacio ejecutivo para conversar sobre cómo las organizaciones pueden incorporar IA con mayor gobierno, control y una estrategia de ciberseguridad alineada al nuevo entorno. 📍 Quito 📅 28 de octubre de 2026 🕖 19:00 Invitan: IST AMERICAS - CrowdStrike - NEXYS.
- AuthZedSince 20 Oct 2026
Simple access rules don't stay simple for long. Calendly's Engineering Leader for Platforms on why it adopted a proven model early.
- AuthZedSince 20 Oct 2026
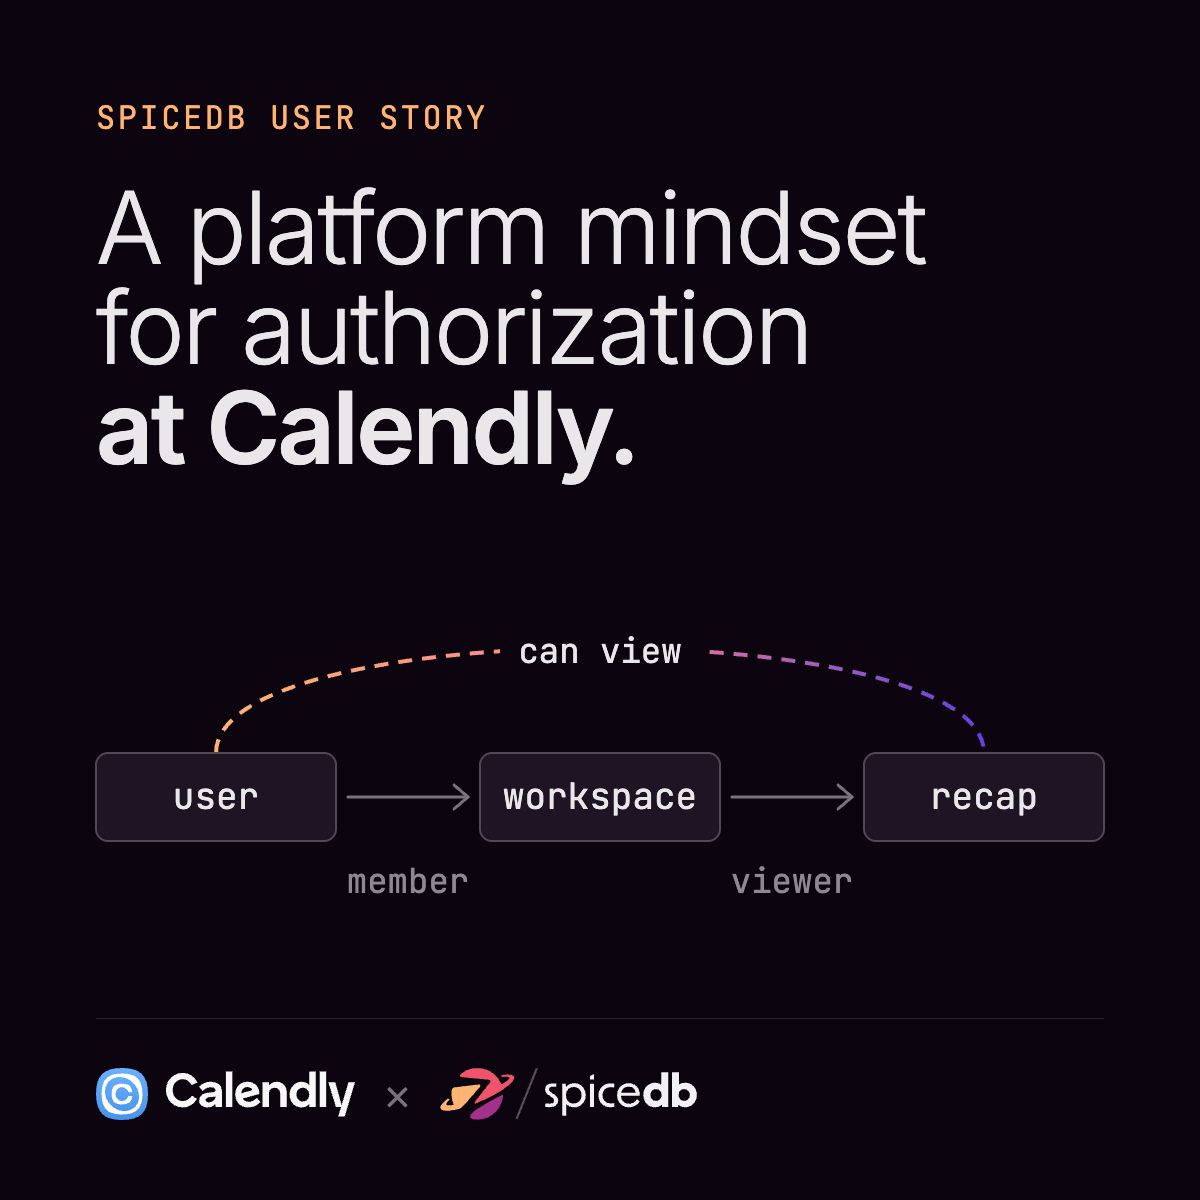
Beyond the Notetaker pilot, SpiceDB changed how Calendly's engineers approach authorization as a discipline. Here's what changed.
- BitdefenderSince 21 Oct 2026
Always-on protection. Faster response. More time for your team. Bitdefender MDR delivers 24/7/365 monitoring, investigation, and response through AI-augmented, human-led SOC operations. Read the Gartner® Market Guide for Managed Detection and Response 2026 to help assess your options.
- Gambit SecurityRecorded 23 Oct 2026
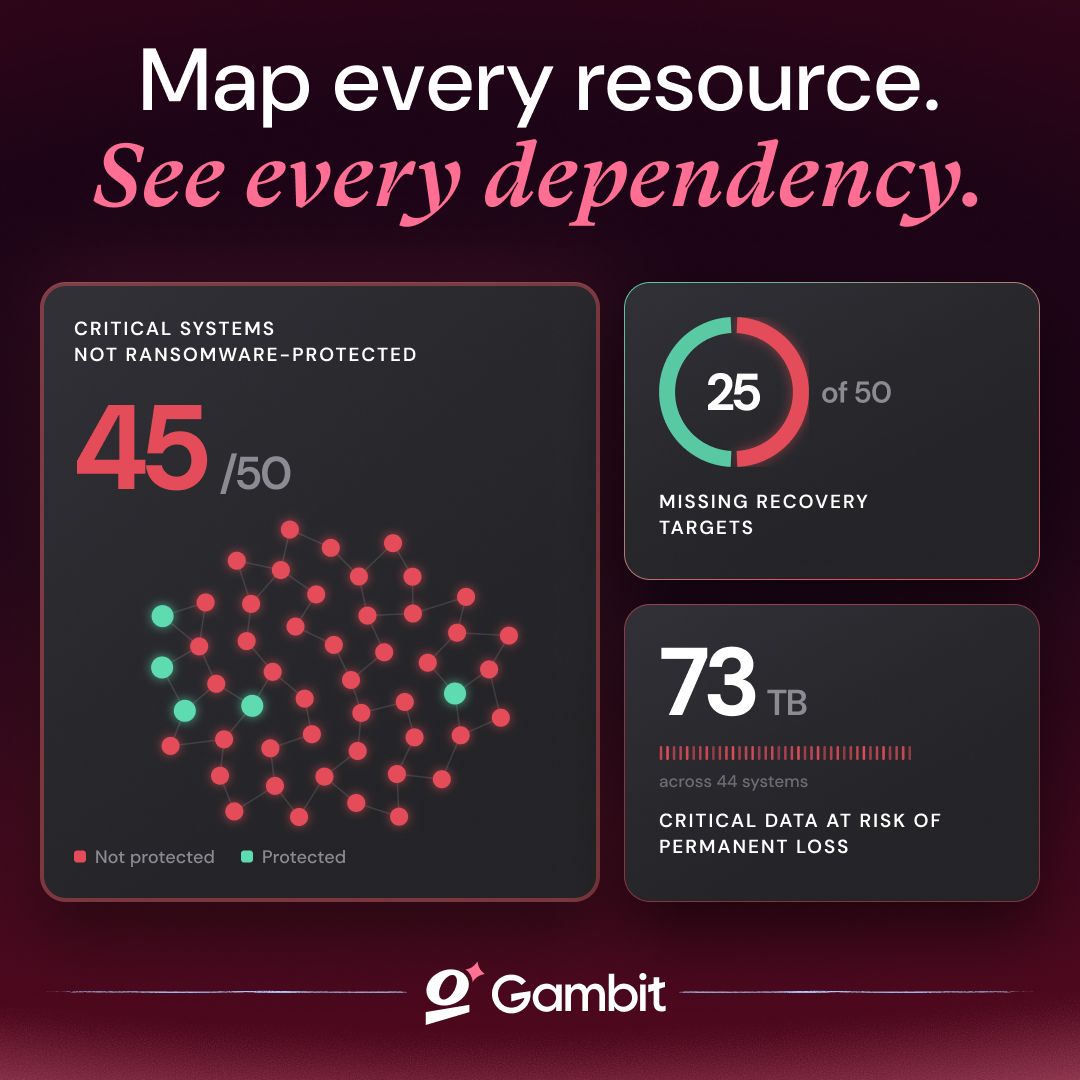
Map every dependency. Expose every recovery gap. Know what actually comes back - before disruption answers the question for you.
- BugHuntRecorded 23 Oct 2026
Como você tem lidado com os desafios do cargo? Nós queremos abrir essa discussão no mercado e estamos dando o primeiro passo. Responda à pesquisa e ajude a mostrar como é o dia a dia de quem lidera segurança no Brasil. São poucos minutos, sem login e sem coleta de e-mail. https://lnkd.in/dvmwcT-g
- Core ImpactSince 20 Oct 2026
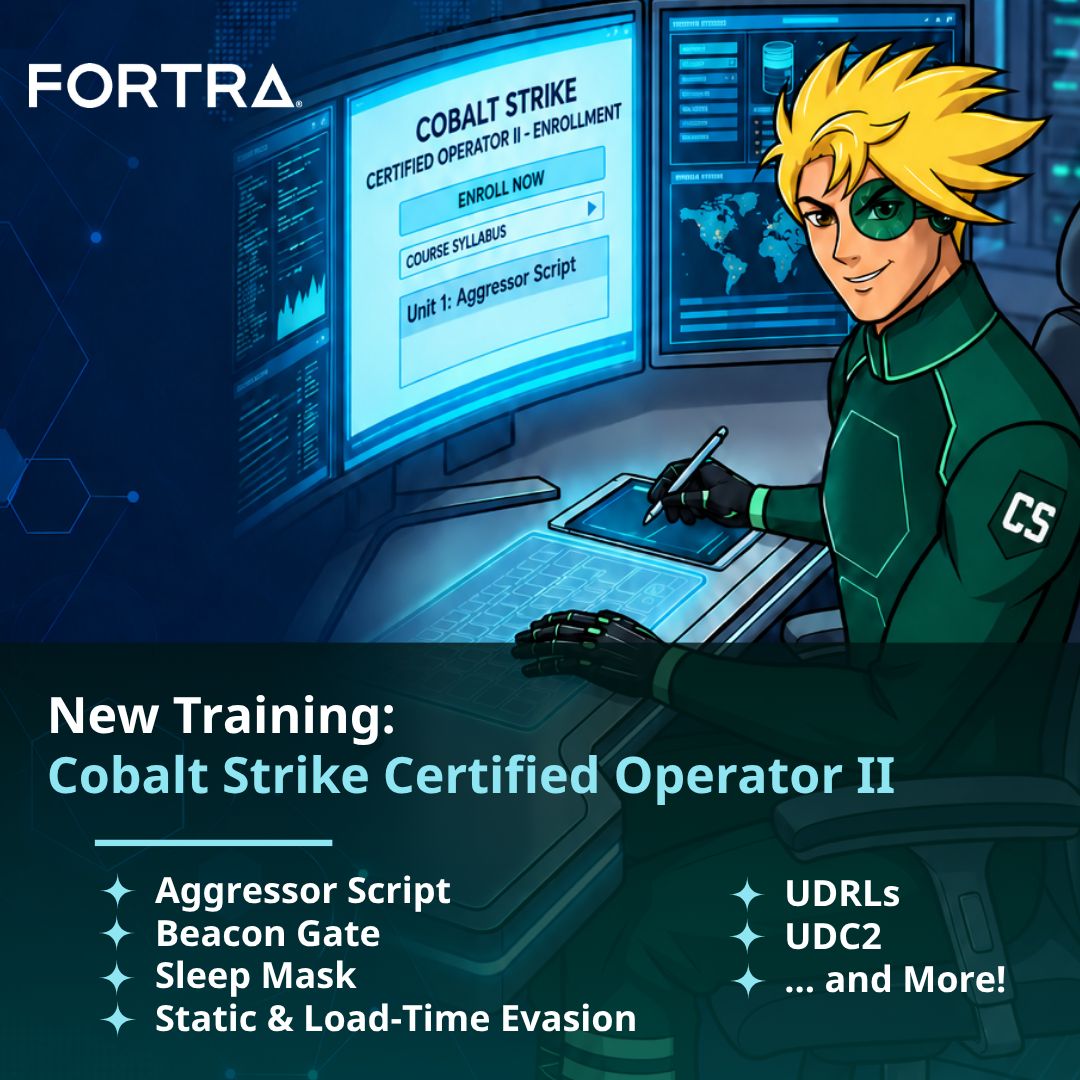
Explore the newly released CSCO II curriculum for advanced Cobalt Strike Operators.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.