LinkedIn image ad examples
1,352 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- EvidenSince 26 Oct 2026
From public safety to traffic management, authorities need greater visibility across increasingly complex environments. Eviden Vision AI, powered by Ipsotek VISuite, transforms video data into actionable intelligence to support faster, more coordinated responses.
- EvidenSince 26 Oct 2026
Modern investigations require more than video retrieval. Eviden Vision AI, powered by Ipsotek VISuite, helps security and forensic teams connect events across multiple cameras, accelerate investigations, and uncover critical insights faster.
- Dioss Smart SolutionsSince 26 Oct 2026
Hoe sterk staat een handtekening die als scan per mail terugkwam, als een klant ze later betwist? Met Dioss Sign tekenen je klanten met itsme® of eID: een gekwalificeerde handtekening, wettelijk gelijk aan pen op papier.
- Dioss Smart SolutionsSince 26 Oct 2026
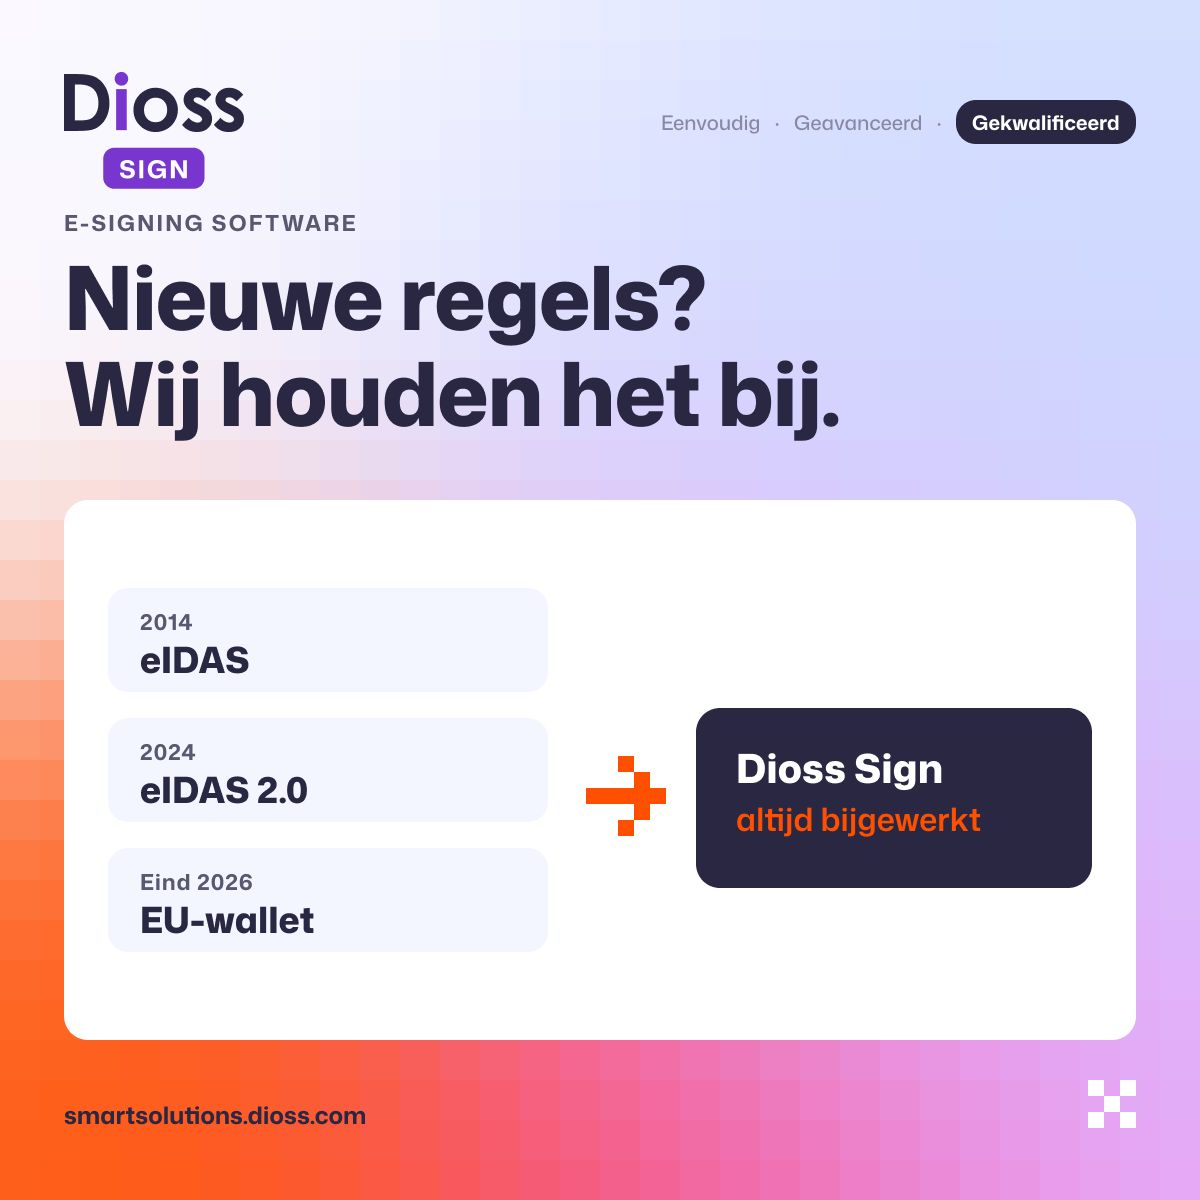
eIDAS, eIDAS 2.0, de EU-wallet: de regels rond digitaal ondertekenen blijven veranderen. Niemand heeft tijd om dat allemaal op te volgen. Dat hoeft ook niet. Komt er een nieuwe manier om je te identificeren, dan zet Dioss die in Dioss Sign. Zo hoef jij je werkwijze niet telkens te herzien.
- ZenitySince 25 Oct 2026
DSPM calls it a data problem. IAM calls it an identity problem. Neither sees what the agent intended to do. Zenity's Surface, Enforce, and Protect model closes that gap end-to-end.
- CyberProofSince 25 Oct 2026
Boost your security posture! Discover the 7 key benefits of Managed SIEM for Google SecOps to enhance threat detection & response. Read the datasheet!
- CyberProofSince 26 Oct 2026
Ingest & analyze data at scale while reducing storage costs and maintaining flexibility
- dope.securityRecorded 28 Oct 2026
Nobody budgets for the day the security stack gets slow instead of down. Down is loud, and it gets fixed. Everyone knows, there's a status page, there's a war room. Slow is quiet, and nobody owns it. Pages crawl, calls stutter, and people start turning off the VPN or the agent to get work done. That's where the real exposure starts. Nobody files a ticket that says "security made me slower." They just route around it. In a shared cloud-proxy design, the headroom is set by someone else's capacity plan, and AI-heavy traffic is growing faster than most plans assumed. At dope.security, enforcement runs on the device and traffic flies direct. Growth in AI usage lands on endpoints you already own, not on a shared queue you can't see. Security leaders: when did a "slow" security tool last cause more damage than a "down" one? #SSE #Endpointsecurity #Cybersecurity
- ZenitySince 24 Oct 2026
The agent is the new perimeter, and most security programs don't have a governance model for it. Zenity gives CISOs one built for agent behavior, not just human identity.
- ZscalerSince 23 Oct 2026
Patching the critical PHP2Shell vulnerabilities is an urgent priority in this era of AI-assisted attacks, but it also reinforces the need for a more sustainable approach. Join Deepen Desai, EVP Cybersecurity at Zscaler for a rapid response briefing. Register today
- ZscalerSince 23 Oct 2026
Two critical PHP2Shell vulnerabilities are raising the stakes for security teams worldwide. As AI helps adversaries move faster, organizations need more than emergency patching alone. Join Deepen Desai, EVP Cybersecurity for a practical briefing on the vulnerabilities, the evolving threat landscape, and Zero Trust approaches to help contain risk.
- BlinkOpsSince 24 Oct 2026
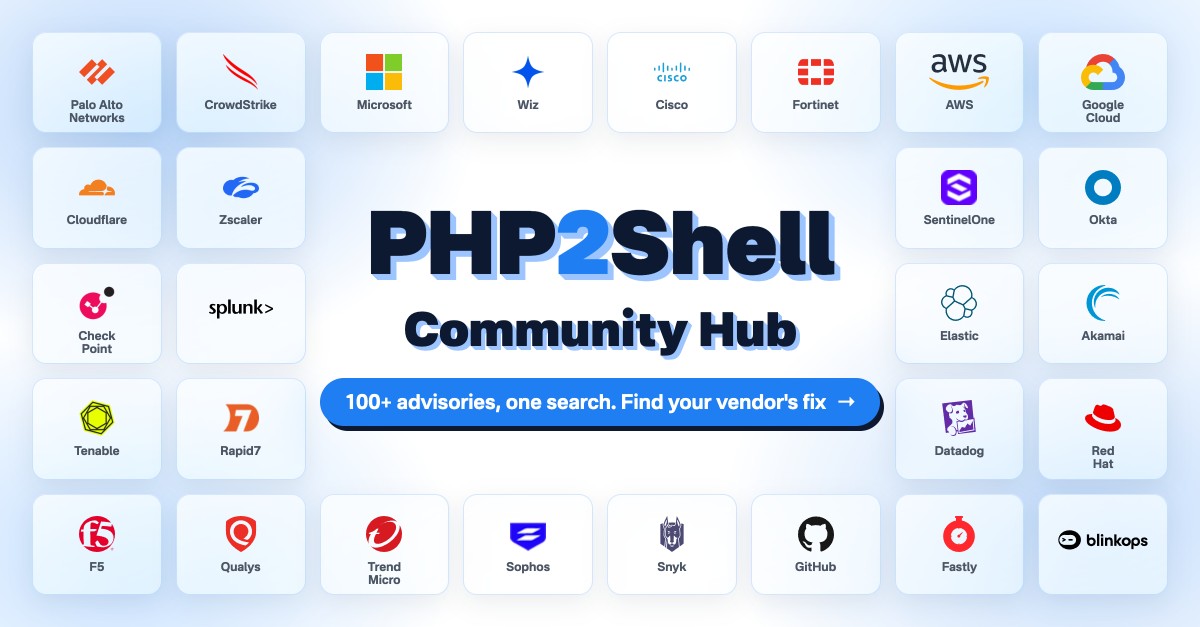
There's been a flood of PHP2Shell guidance this week. Every vendor has published something, and it's spread across dozens of blogs, advisories, and KB articles. → So we pulled it all into one place: https://lnkd.in/e2KRUJFZ The PHP2Shell Community Hub has 100+ articles from across the industry. You can filter by what you need to do (am I affected, patch, block, detect) and by the tools you already run, so your vendors' guidance shows up first. It includes work from CrowdStrike, Wiz, Palo Alto Networks Unit 42, Tenable, Google Cloud Security, Amazon Web Services (AWS), Elastic, Rapid7, Akamai Technologies, and plenty more. → If you're still working through your exposure, take a look this weekend: https://lnkd.in/e2KRUJFZ Published guidance we missed? Email [email protected] and we'll add it.
- CerbySince 26 Oct 2026
Your IAM program governs employee access. But what about paid social accounts, DSPs, and agency permissions? Uncover the gaps.
- CerbySince 26 Oct 2026
Employee offboarding doesn't guarantee access removal from ad accounts, business portfolios, or DSPs. Here's what IAM teams should check.
- Duo SecuritySince 26 Oct 2026
MFA alone won't stop modern phishing. Learn what tools and strategies can push your org toward real, end-to-end phishing resistance.
- Duo SecuritySince 26 Oct 2026
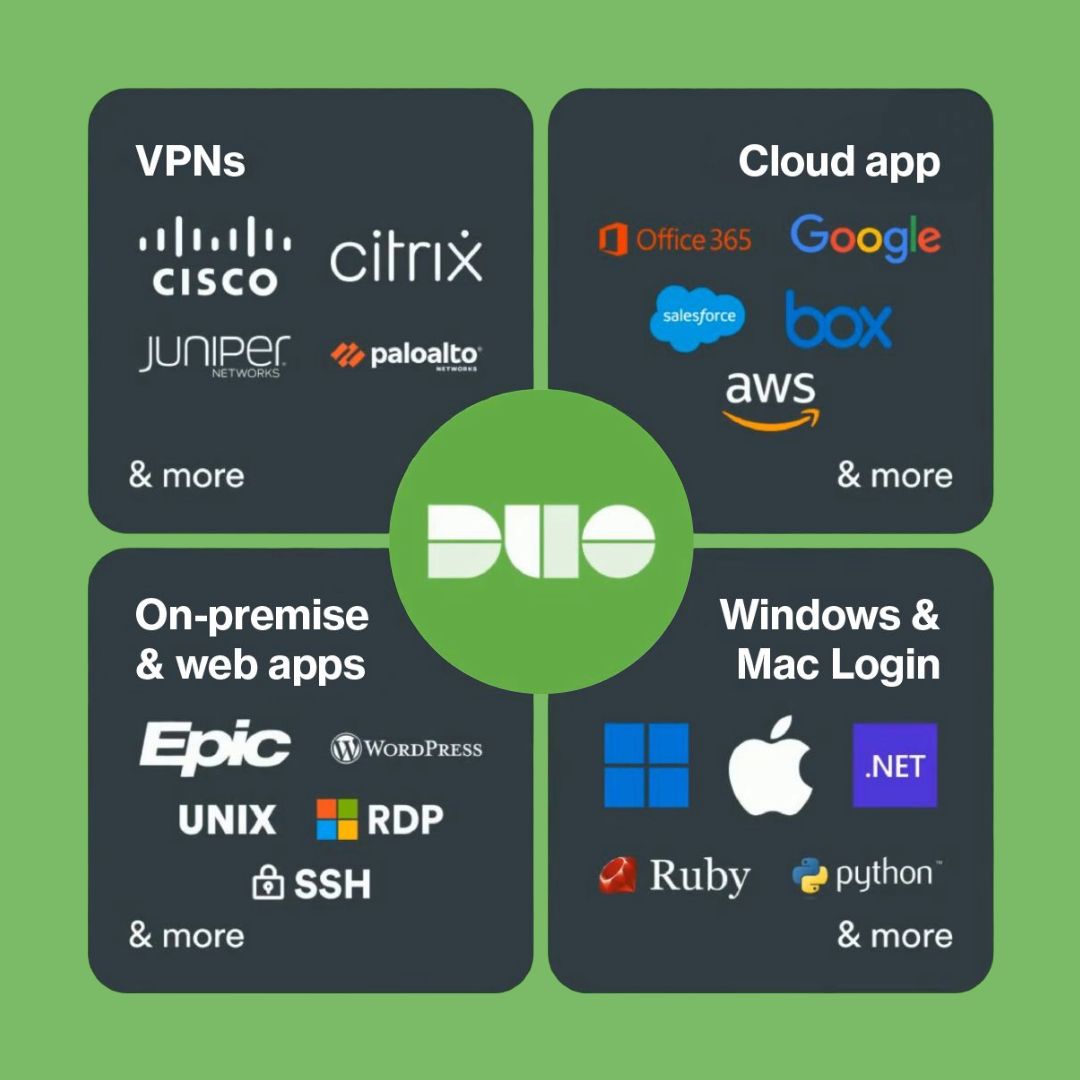
One roof. Complete coverage. From cloud to on-premises, Duo brings all your applications together under a single, secure access strategy.
- TenableSince 26 Oct 2026
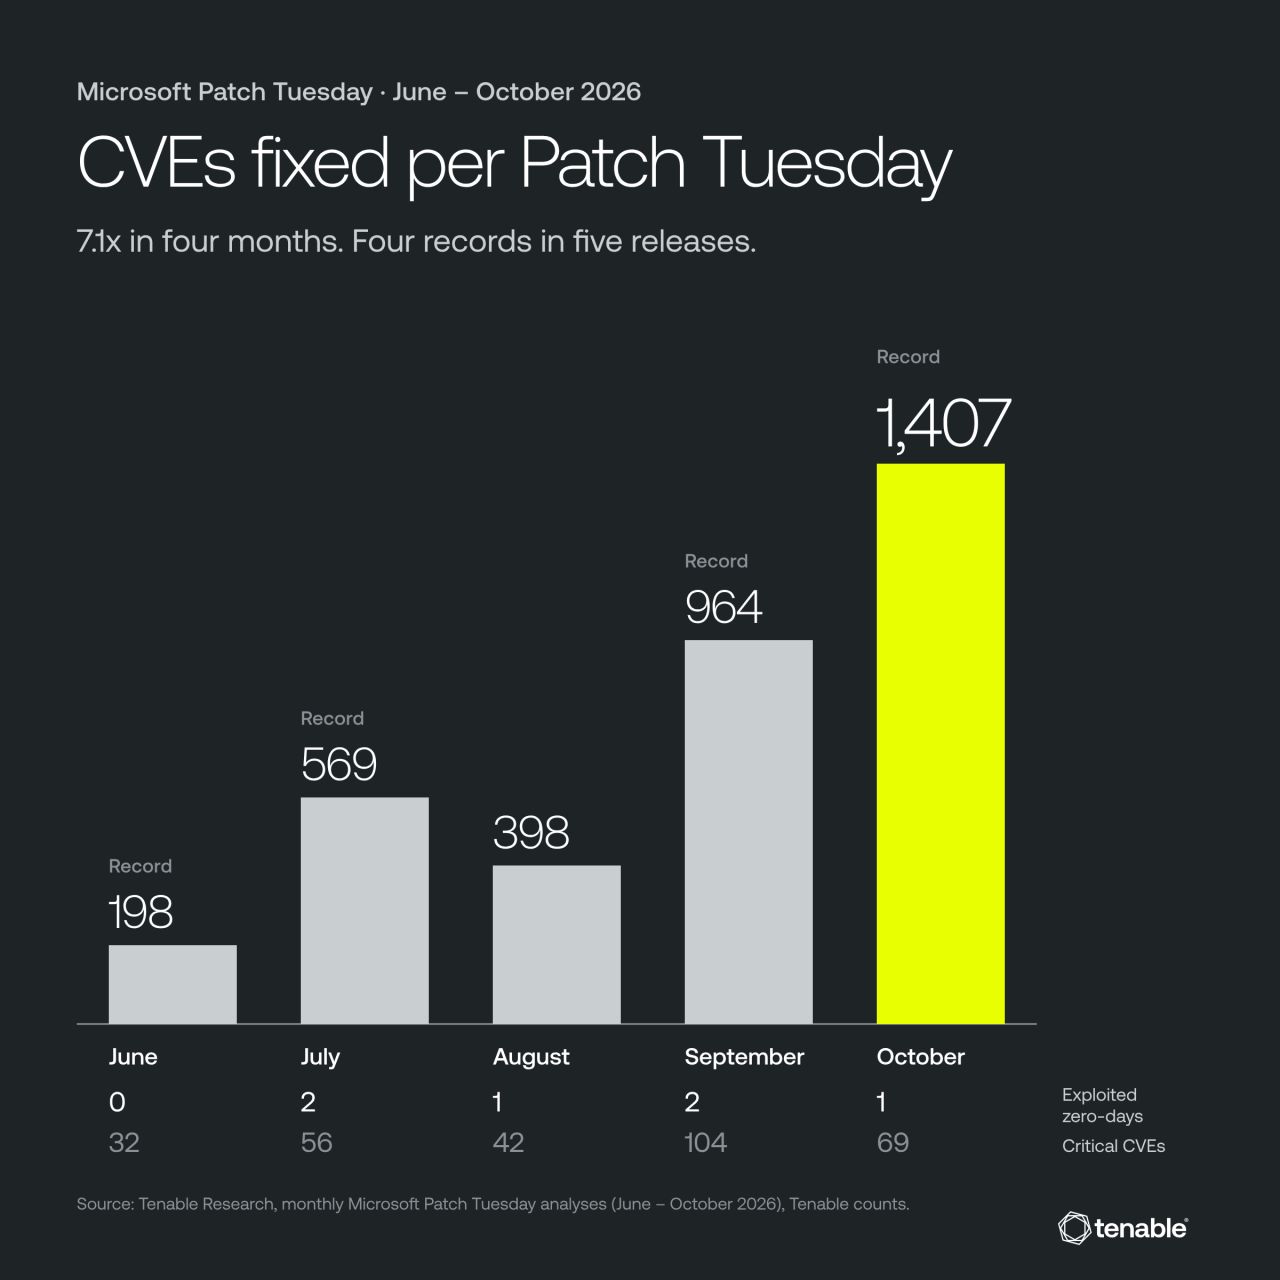
🚨 1,407 CVEs fixed by Microsoft yesterday: a new Patch Tuesday record, for the second month in a row. 📈 198 in June, 569 in July, 398 in August, 964 in September, 1,407 in October (Tenable Research counts). That is 7.1x in four months, with four records in five releases. Before June, the record stood at 167 CVEs. Three takeaways 👇 1️⃣ Volume is no longer a proxy for risk: critical CVEs now account for just 4.9% of the total, versus 16.2% in June. Triaging on CVSS alone is no longer enough. 2️⃣ Elevation of privilege dominates: 47.9% of Octobers CVEs, up from 31.8% in June. 3️⃣ Exploitation remains concentrated: six exploited zero-days in five months. In October, CVE-2026-96951 (Mark of the Web bypass in Windows Shell) was exploited in the wild, the third exploited Windows Shell flaw of 2026. CVE-2026-108398 (.NET, WDAC bypass) was publicly disclosed before a patch was available. With agentic AI now driving vulnerability discovery, these volumes are not coming down. 🎯 The question is no longer how many CVEs?, but which ones are exploitable in my environment, on which exposed assets?. That is the shift from vulnerability management to exposure management. 🔗 Full Tenable Research analysis: https://lnkd.in/etS5dNwS #ExposureManagement #VulnerabilityManagement #CyberSecurity #ZeroDay #Tenable
- ESETSince 26 Oct 2026
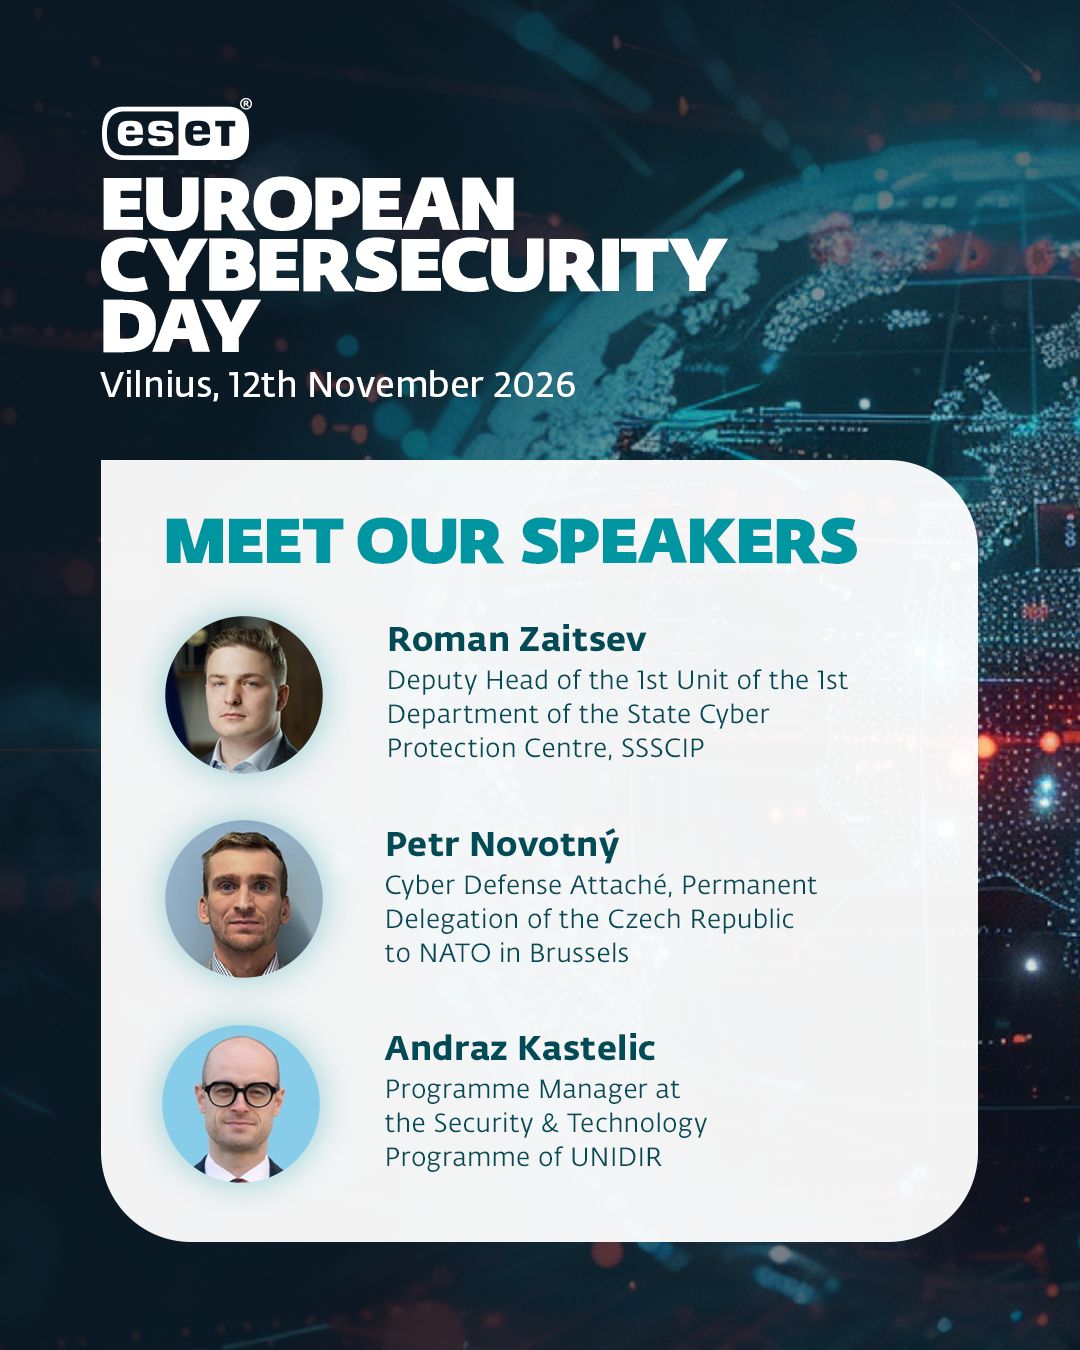
From destructive attacks targeting critical infrastructure to long-running cyberespionage campaigns against governments, telecommunications providers, and strategic industries, Europe is facing an increasingly complex threat landscape. At the same time, AI is changing cybersecurity, with new tools helping security teams while also creating new risks. 📍 At the 10th ESET European Cybersecurity Day in Vilnius on 12th November 2026, we’ll bring together researchers, cybersecurity practitioners and policy experts to discuss what this means for Europe and NATO's security, as well as for those protecting critical infrastructure. Register on our website, where you can also find the full agenda and speakers. We look forward to welcoming you in Vilnius, whether you’re joining us in person or online. 👉 https://lnkd.in/dsYmWCFu #EECD #ESET #CybersecurityDay
- TenableSince 26 Oct 2026
Fix it or shut it down. That’s been the reality for security teams worldwide over the last four days. PHP2Shell is shaping up to be one of the most significant vulnerability events of 2026. Two flaws in PHP’s core memory allocator (CVE-2026-109618, CVE-2026-109619) enable unauthenticated remote code execution. Each is unreliable on its own. Chained, they’re reliable enough against default configurations that any PHP endpoint accepting file uploads becomes a target. At Tenable’s EXPOSURE event in May, I shared Mandiant’s time-to-exploit data: 63 days in 2018, 5 days in 2023, and 𝑚𝑖𝑛𝑢𝑠-7 days this year. The line has crossed zero. PHP2Shell is what that looks like in practice: ✴️ Amazon’s MadPot honeypots recorded active exploitation on Oct 17, four days before public disclosure. ✴️ The embargo leaked 18 hours early via a Hacker News post. ✴️ Cloudflare saw “thousands” of exploitation attempts within hours of the advisory, rising to “millions” after publication. ✴️ Nine government agencies across seven countries issued advisories or directives. Six ordered preemptive shutdowns of PHP-dependent services. The exposure is immense. More than 22M PHP server headers are visible online, and patch adoption is 2.8%. About 59% of exposed hosts run end-of-life versions with no official patch. For most of this surface, the patch cycle isn’t slow. 𝐈𝐭 𝐝𝐨𝐞𝐬𝐧’𝐭 𝐞𝐱𝐢𝐬𝐭. This is structurally different from past web vulnerabilities. The flaws were found with the help of frontier AI, and AI is compressing exploit development from weeks to days. Ironically, major cybercriminal forums (more here: https://lnkd.in/d_yUAxPs) took themselves offline within hours, because their own PHP infrastructure was at risk. Many organizations didn’t even know they ran PHP. Let alone how to patch or mitigate it. 𝐘𝐨𝐮 𝐜𝐚𝐧’𝐭 𝐬𝐞𝐜𝐮𝐫𝐞 𝐰𝐡𝐚𝐭 𝐲𝐨𝐮 𝐜𝐚𝐧’𝐭 𝐬𝐞𝐞. In 2026 that principle has a second half: 𝐲𝐨𝐮 𝐜𝐚𝐧’𝐭 𝐝𝐞𝐟𝐞𝐧𝐝 𝐚𝐭 𝐡𝐮𝐦𝐚𝐧 𝐬𝐩𝐞𝐞𝐝 𝐚𝐥𝐨𝐧𝐞. To borrow an analogy from forest firefighting, the six government agencies who shut down their services cleared the fuel the hard way. The better way is to clear it before the fire arrives. That means continuous discovery, inventory, reachability, and business context - at AI speed combined with human judgment. The same AI that found these flaws is the best tool defenders have to get ahead of the next ones. Tenable Research’s FAQ, updated as this develops: https://lnkd.in/dUaVyNUq #ExposureManagement #AI #PHP2Shell
- DescopeSince 26 Oct 2026
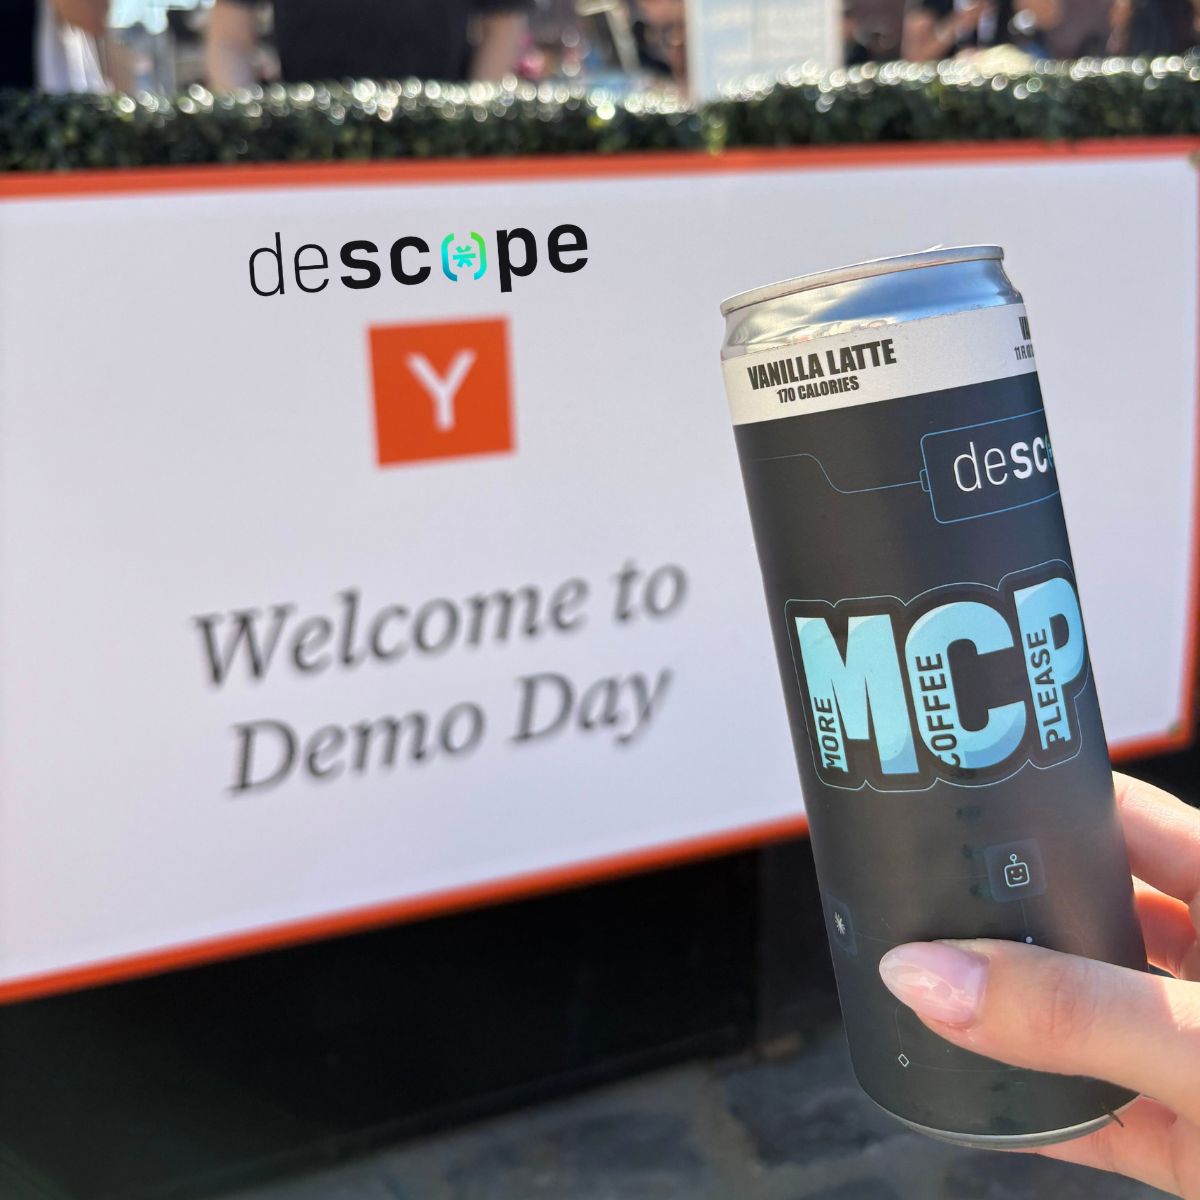
Eligible Y Combinator startups get two years of Descope Growth free, with SSO, SCIM, RBAC, and agent identity included. You.com shortened customer SSO onboarding from weeks to 15 minutes, and Vega's customers now cite SCIM support as a reason to buy. Apply for the YC offer and build on auth that scales past Demo Day.
- WizSince 26 Oct 2026
Developers shouldn't have to trade AI speed for code security. The Security for AI-Driven Development infographic helps engineering and security leaders implement a practical 4-stage scanning strategy built for the AI-SDLC.
- WizSince 26 Oct 2026
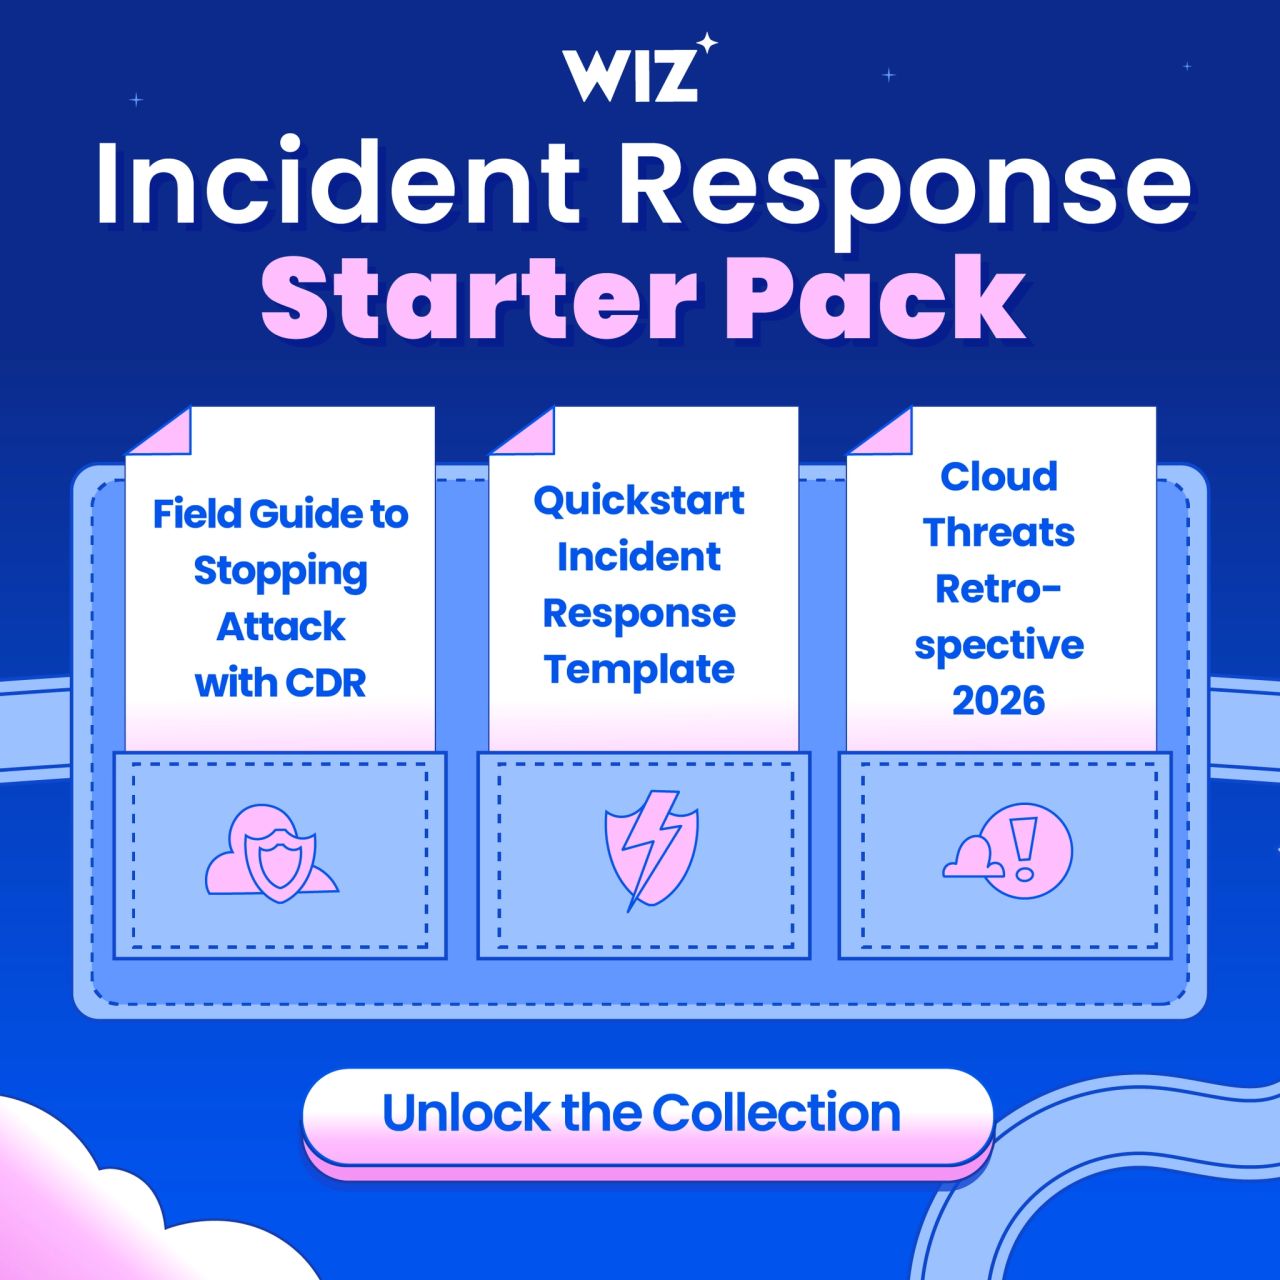
The Incident Response Starter Pack gives your team the practical frameworks and threat intelligence needed to isolate cloud threats at machine speed.
- ESET PolskaSince 22 Oct 2026
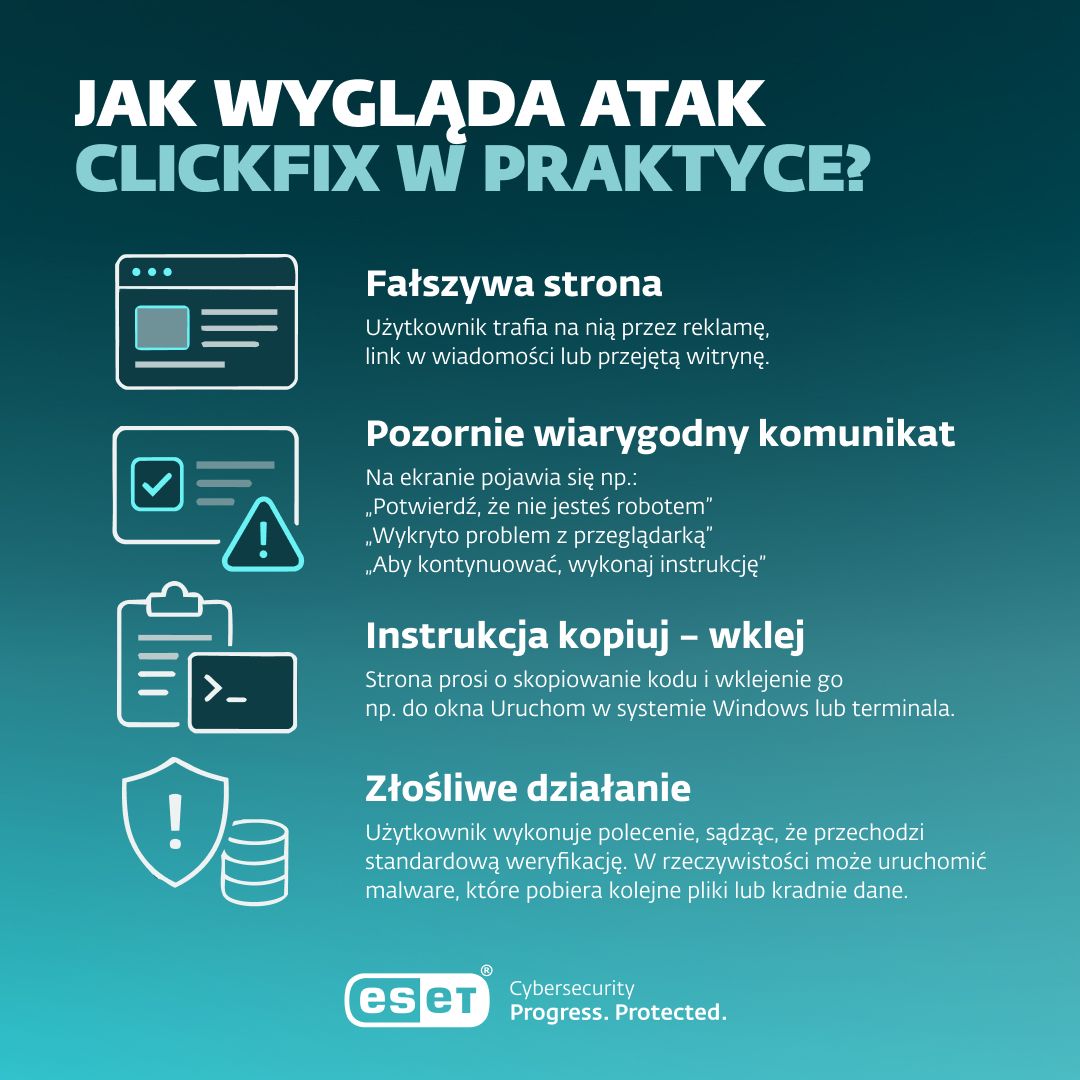
„Potwierdź, że nie jesteś robotem.” Klikasz. „Wykryto problem z przeglądarką.” Czytasz instrukcję. „Skopiuj polecenie i wklej je tutaj.” I właśnie w tym momencie zaczyna się problem. ClickFix wykorzystuje coś bardzo prostego: przekonuje Cię, żebyś sam uruchomił złośliwe polecenie. Nie wygląda jak klasyczny atak. Nie musi być podejrzanego załącznika. Nie musi być nawet pobierania pliku. Wystarczy chwila nieuwagi. Zobacz na grafice, jak wygląda taki atak krok po kroku.
- GuardeySince 22 Oct 2026
De IGJ houdt toezicht op cyberveiligheid in de zorg. Kun jij ook laten zien hoe jouw organisatie medewerkers bewust maakt van digitale risico's? Met Guardey wordt security awareness training een doorlopend onderdeel van de werkweek. Medewerkers oefenen met korte challenges over veilig digitaal werken, terwijl jij hun deelname en voortgang volgt. Zo heb je concrete resultaten om te laten zien wanneer er vragen komen over de training van medewerkers. Plan een demo en ontdek hoe Guardey deze voortgang inzichtelijk maakt.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.