On air · 1 of 3 networks
Tenable
- tenable.com
- Cybersecurity
- US
- 2,398 employees
Tenable’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 3,912. Watch Tenable with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 3,002 | Checked 30 Oct 2026 | See all 3,912 ads → | ||
| Meta | Not checked | — | |||
| Recently | 900+ | Ads on the Google Ads Transparency Center | Checked 11 Oct 2026 | Collect them with the API → |
Tenable has 3,002 live LinkedIn ads. We recorded 900+ Google ads on 11 Oct 2026.
Latest ads
- LINKEDIN · IMAGESince 28 Oct 2026
Last week it was PHP2Shell. This week it’s HTTP2Shell, a critical flaw in Google’s Brotli compression library. CVE-2026-111497 has already triggered emergency patches across Node.js, .NET, and Python. Last Friday, I mentioned the vulnerability is only the headline, but the real exposure runs much deeper. This proves it. Leaders should notice one detail. Updating the system’s Brotli library doesn’t fix it, because many applications carry their own bundled copies. Patching is crucial, but it assumes you know where to apply the patch. Most organizations don’t. That’s why proactive security matters. The advantage goes to teams that can see every path into their environment and close the dangerous ones before attackers find them. https://lnkd.in/eX-azm7k #PHP2Shell #ExposureManagement #AI #Cybersecurity
- LINKEDIN · IMAGESince 27 Oct 2026
Toda exposição que você não vê é uma janela para os invasores. O Tenable Hexa AI automatiza a resposta à exposição para manter você à frente
- LINKEDIN · IMAGESince 26 Oct 2026
Fix it or shut it down. That’s been the reality for security teams worldwide over the last four days. PHP2Shell is shaping up to be one of the most significant vulnerability events of 2026. Two flaws in PHP’s core memory allocator (CVE-2026-109618, CVE-2026-109619) enable unauthenticated remote code execution. Each is unreliable on its own. Chained, they’re reliable enough against default configurations that any PHP endpoint accepting file uploads becomes a target. At Tenable’s EXPOSURE event in May, I shared Mandiant’s time-to-exploit data: 63 days in 2018, 5 days in 2023, and 𝑚𝑖𝑛𝑢𝑠-7 days this year. The line has crossed zero. PHP2Shell is what that looks like in practice: ✴️ Amazon’s MadPot honeypots recorded active exploitation on Oct 17, four days before public disclosure. ✴️ The embargo leaked 18 hours early via a Hacker News post. ✴️ Cloudflare saw “thousands” of exploitation attempts within hours of the advisory, rising to “millions” after publication. ✴️ Nine government agencies across seven countries issued advisories or directives. Six ordered preemptive shutdowns of PHP-dependent services. The exposure is immense. More than 22M PHP server headers are visible online, and patch adoption is 2.8%. About 59% of exposed hosts run end-of-life versions with no official patch. For most of this surface, the patch cycle isn’t slow. 𝐈𝐭 𝐝𝐨𝐞𝐬𝐧’𝐭 𝐞𝐱𝐢𝐬𝐭. This is structurally different from past web vulnerabilities. The flaws were found with the help of frontier AI, and AI is compressing exploit development from weeks to days. Ironically, major cybercriminal forums (more here: https://lnkd.in/d_yUAxPs) took themselves offline within hours, because their own PHP infrastructure was at risk. Many organizations didn’t even know they ran PHP. Let alone how to patch or mitigate it. 𝐘𝐨𝐮 𝐜𝐚𝐧’𝐭 𝐬𝐞𝐜𝐮𝐫𝐞 𝐰𝐡𝐚𝐭 𝐲𝐨𝐮 𝐜𝐚𝐧’𝐭 𝐬𝐞𝐞. In 2026 that principle has a second half: 𝐲𝐨𝐮 𝐜𝐚𝐧’𝐭 𝐝𝐞𝐟𝐞𝐧𝐝 𝐚𝐭 𝐡𝐮𝐦𝐚𝐧 𝐬𝐩𝐞𝐞𝐝 𝐚𝐥𝐨𝐧𝐞. To borrow an analogy from forest firefighting, the six government agencies who shut down their services cleared the fuel the hard way. The better way is to clear it before the fire arrives. That means continuous discovery, inventory, reachability, and business context - at AI speed combined with human judgment. The same AI that found these flaws is the best tool defenders have to get ahead of the next ones. Tenable Research’s FAQ, updated as this develops: https://lnkd.in/dUaVyNUq #ExposureManagement #AI #PHP2Shell
- LINKEDIN · IMAGESince 26 Oct 2026
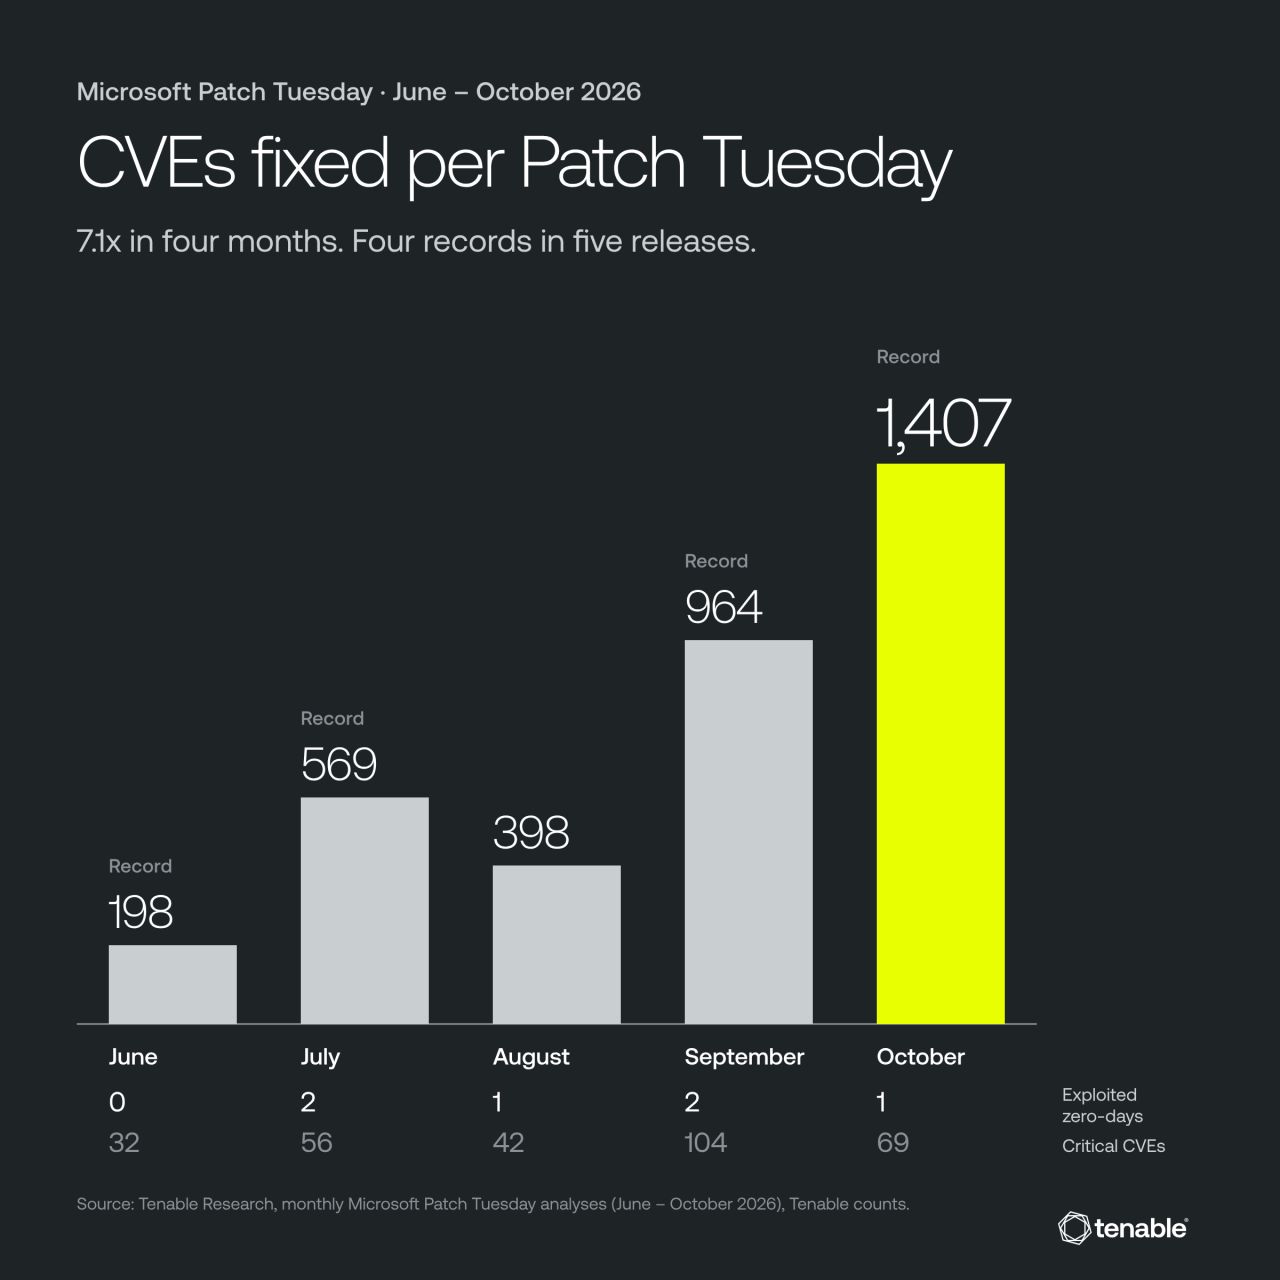
🚨 1,407 CVEs fixed by Microsoft yesterday: a new Patch Tuesday record, for the second month in a row. 📈 198 in June, 569 in July, 398 in August, 964 in September, 1,407 in October (Tenable Research counts). That is 7.1x in four months, with four records in five releases. Before June, the record stood at 167 CVEs. Three takeaways 👇 1️⃣ Volume is no longer a proxy for risk: critical CVEs now account for just 4.9% of the total, versus 16.2% in June. Triaging on CVSS alone is no longer enough. 2️⃣ Elevation of privilege dominates: 47.9% of Octobers CVEs, up from 31.8% in June. 3️⃣ Exploitation remains concentrated: six exploited zero-days in five months. In October, CVE-2026-96951 (Mark of the Web bypass in Windows Shell) was exploited in the wild, the third exploited Windows Shell flaw of 2026. CVE-2026-108398 (.NET, WDAC bypass) was publicly disclosed before a patch was available. With agentic AI now driving vulnerability discovery, these volumes are not coming down. 🎯 The question is no longer how many CVEs?, but which ones are exploitable in my environment, on which exposed assets?. That is the shift from vulnerability management to exposure management. 🔗 Full Tenable Research analysis: https://lnkd.in/etS5dNwS #ExposureManagement #VulnerabilityManagement #CyberSecurity #ZeroDay #Tenable
- LINKEDIN · VIDEOSince 26 Oct 2026
Calling all security practitioners: it’s time to build! #SWARMGlobal is a free-entry virtual event where you’ll build open-source AI agents, skills, and MCP servers for real workflows like alert triage, remediation orchestration, and executive reporting. Sponsored by Tenable with support from Anthropic, it runs November 2-6 with a hands-on tutorial, office hours, and a live pitch day for the top teams. Registration closes November 1st. Sign up today! https://lnkd.in/eKrQWKeq
- LINKEDIN · VIDEOSince 26 Oct 2026
On Sunday night, attackers turned the fridges in more than a hundred French supermarkets into very expensive heaters.They didn’t go for the data. They went for the stock. Nobody’s confirmed yet how they got in but my money’s on a known flaw in the fridge controllers. https://lnkd.in/eaS4wwYH #exposuremanagement
6 of 3,912 adsSign up to see every Tenable ad, filter by format and date, and get alerts on new ones.
See all 3,912 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.