B2B ad examples
1,812 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- GMS Information SecurityRecorded 21 Sept 2026
¿Sabes cuánto tarda tu SOC en actuar ante un incidente crítico? Segpun nuestros estudios, las simulaciones de ataques de ciberseguridad se redujeron de 120 a 15 minutos con Cortex XSOAR y workflows automatizados. Optimiza tu SOC y fortalece tu protección.
- GMS Information SecurityRecorded 21 Sept 2026
Sigue a GMS para estar al día con tendencias de IT.
- GlasswallSince 15 Jul 2026
Some tools earn trust. Glasswall CDR is mandated by the U.S. NSA NCDSMO for Cross Domain Solutions. In the highest-assurance environments, trust alone isn't enough.
- GlasswallSince 15 Jul 2026
Security tools that slow workflows down get turned off or worked around. At 812ms average processing time, Glasswall CDR doesn't give users a reason to bypass it.
- Group 2000Since 17 Jul 2026
Some engineering roles are about maintaining what already exists. At Group 2000, you help design and build technology for complex, mission-critical environments. You work on challenging software components, collaborate directly with experienced architects and take responsibility for solutions that need to perform reliably. Ready for a technical challenge that goes beyond the ordinary?
- Group 2000Since 16 Jul 2026
Your work can be technically challenging and meaningful at the same time. At Group 2000, you help develop secure technology for organizations operating in complex and highly regulated environments. The systems you work on need to be accurate, reliable and ready for real-world use. Build technology that matters.
- Group-IBSince 8 Sept 2026
🔗 A new platform purchase demands an ROI business case nobody can yet prove. So institutions stay siloed. You don’t need a new budget, extra headcount, or a massive software overhaul to fix this. You just need 90 days and the team you already have. In his latest playbook, Group-IB CEO, Dmitry Volkov, turns high-level strategy into an execution roadmap to collapse the gap between cybersecurity and fraud. 📖 Read the full playbook
- Group-IBSince 8 Sept 2026
🧭 In his latest playbook, Group-IB CEO, Dmitry Volkov, turns high-level strategy into an execution roadmap to collapse the gap between cybersecurity and fraud. A reorganization triggers internal power struggles nobody wants. A new platform purchase demands an ROI business case nobody can yet prove. So institutions stay siloed, and adversaries win by default. You don’t need a new budget, extra headcount, or a massive software overhaul to fix this. You just need 90 days and the team you already have. 📖 Read the full playbook
- QueryRecorded 21 Sept 2026
Centralize the insights, not your data. Security data is distributed by default. Your SIEM holds a fraction of it. The Query Security Data Mesh connects your data wherever it lives: cloud storage, data lakes, EDR, identity, network tools, 50+ sources in all. Lower costs. More coverage. No ingestion required.
- QueryRecorded 21 Sept 2026
Your SIEM bill keeps growing. Your coverage doesn't. There is a version of security operations where that trade-off doesn't exist. The data you couldn't afford to ingest becomes operational. Detections run on data wherever it lives. Your AI agents run across all of it. That is what the Query Security Data Mesh is for. Security operations beyond your SIEM. No migration required.
- ControlMonkeySince 18 Sept 2026
You protect users' data. But what about the configuration the business depends on? ControlMonkey makes it recoverable - extending recovery beyond data backup.
- CoroSince 19 Sept 2026
One in six breaches now involves AI. Learn how RHTP funding can help rural providers prepare for faster, more adaptive threats.
- CoroSince 19 Sept 2026
Rural communities face $155 billion in projected Medicaid cuts. Learn how RHTP funding can protect critical cybersecurity investments.
- PathlockSince 11 Sept 2026
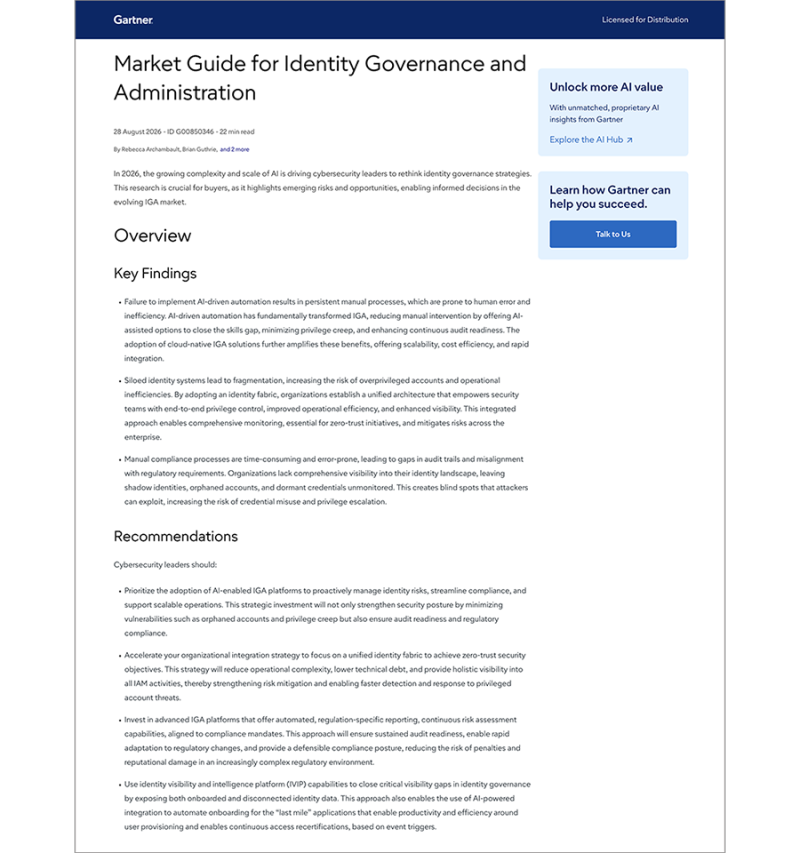
We are very excited to be recognized as a Representative Vendor in the 2026 Gartner® Market Guide for Identity Governance and Administration. According to Gartner, “in 2026, IGA is evolving from legacy, quarterly cycles of manual access reviews to an autonomous, continuous, and outcome-driven process that encompasses both access certification and provisioning.” Explore the risks, opportunities, and recommendations shaping the future of IGA. #IdentityGovernance #IGA #IdentitySecurity https://lnkd.in/gMP9vKdn
- PathlockSince 11 Sept 2026
Proud to see Pathlock named as a Representative Vendor in the 2026 Gartner Market Guide for Identity Governance and Administration (IGA)! Gartner puts it well: "in 2026, IGA is evolving from legacy, quarterly cycles of manual access reviews to an autonomous, continuous, and outcome-driven process that encompasses both access certification and provisioning." I lead Customer Engineering and Support at Pathlock, so I see that shift up close — customers moving off manual, periodic reviews toward continuous, outcome-driven governance. This recognition tracks with what I'm hearing from them every day. Read the full guide: https://lnkd.in/ezdAuu3f #IdentityGovernance #IGA #IdentitySecurity
- ConveyorSince 18 Sept 2026
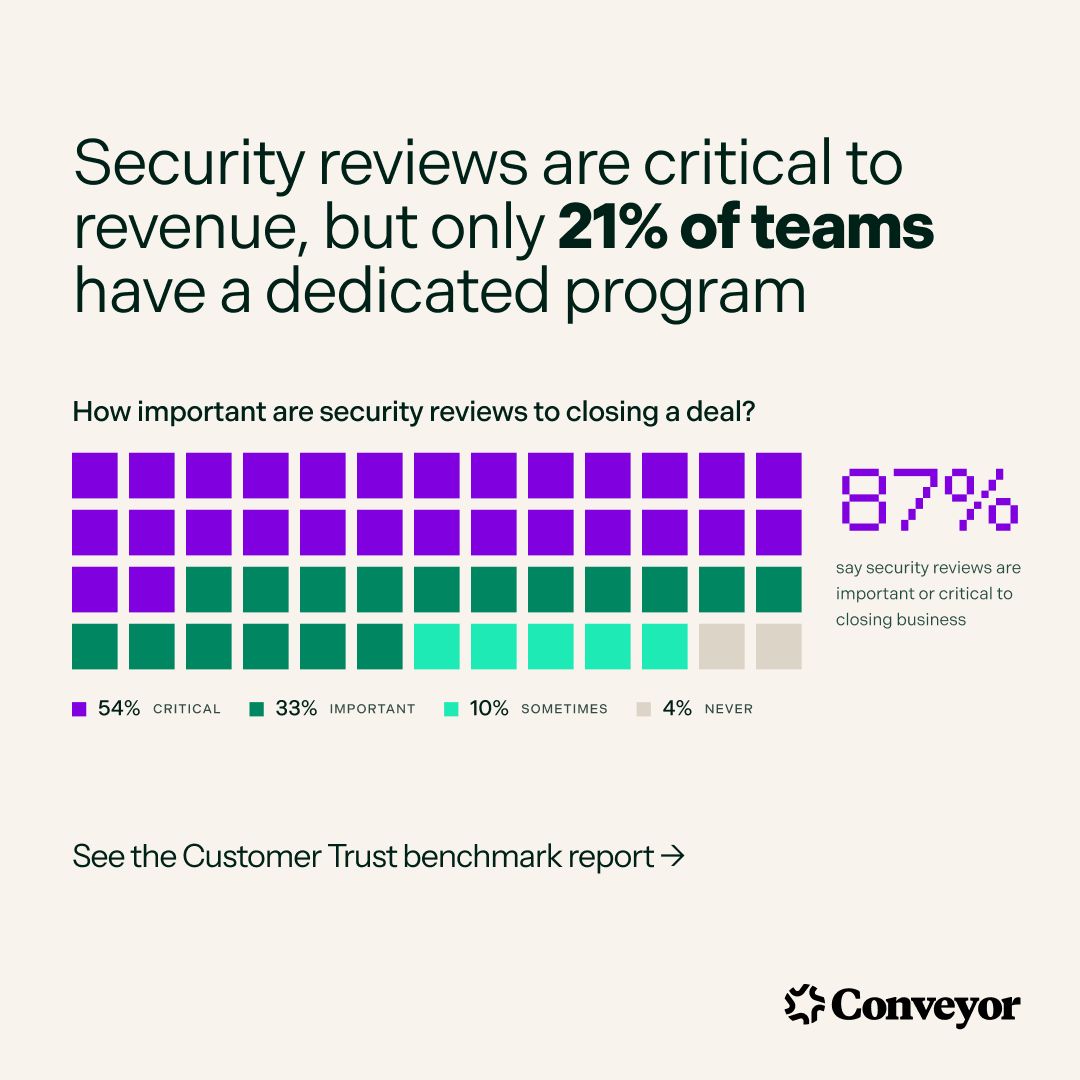
We surveyed 50+ B2B teams on questionnaire volume, sales support, and the operational challenges behind customer security reviews. One finding stood out: 87% say security reviews are critical to closing deals, but only 21% have a dedicated program to manage them. See what’s driving that gap in the 2026 Customer Trust Benchmark. 👇
- ConveyorSince 18 Sept 2026
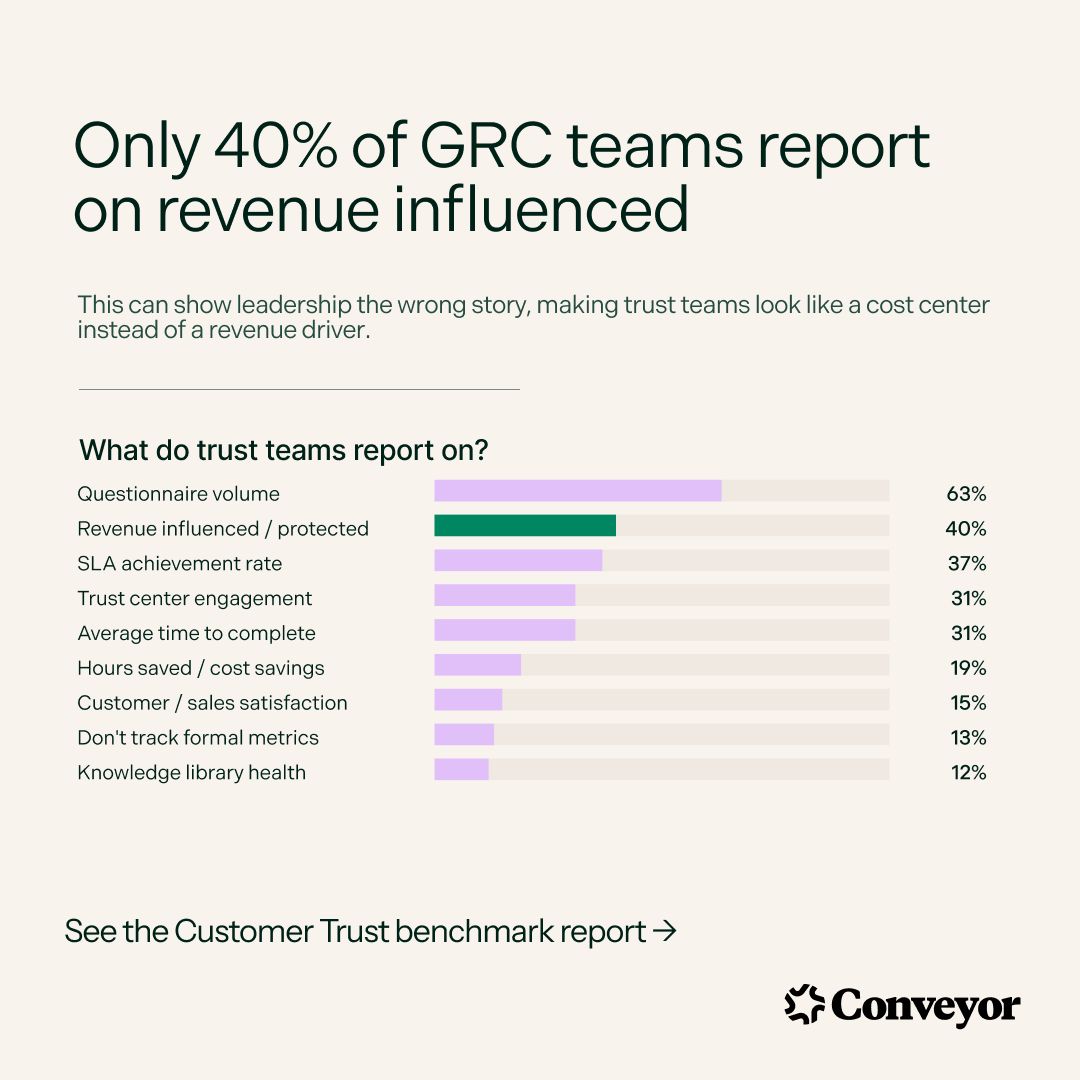
Most GRC teams report on questionnaire volume, but not revenue, and that’s costing them. That can make teams look like a cost center instead of a revenue driver, making it harder to justify more headcount, budget, or better tools. See what other trust teams are measuring in the Customer Trust Benchmark Report. 👇
- Artemis SecurityRecorded 21 Sept 2026
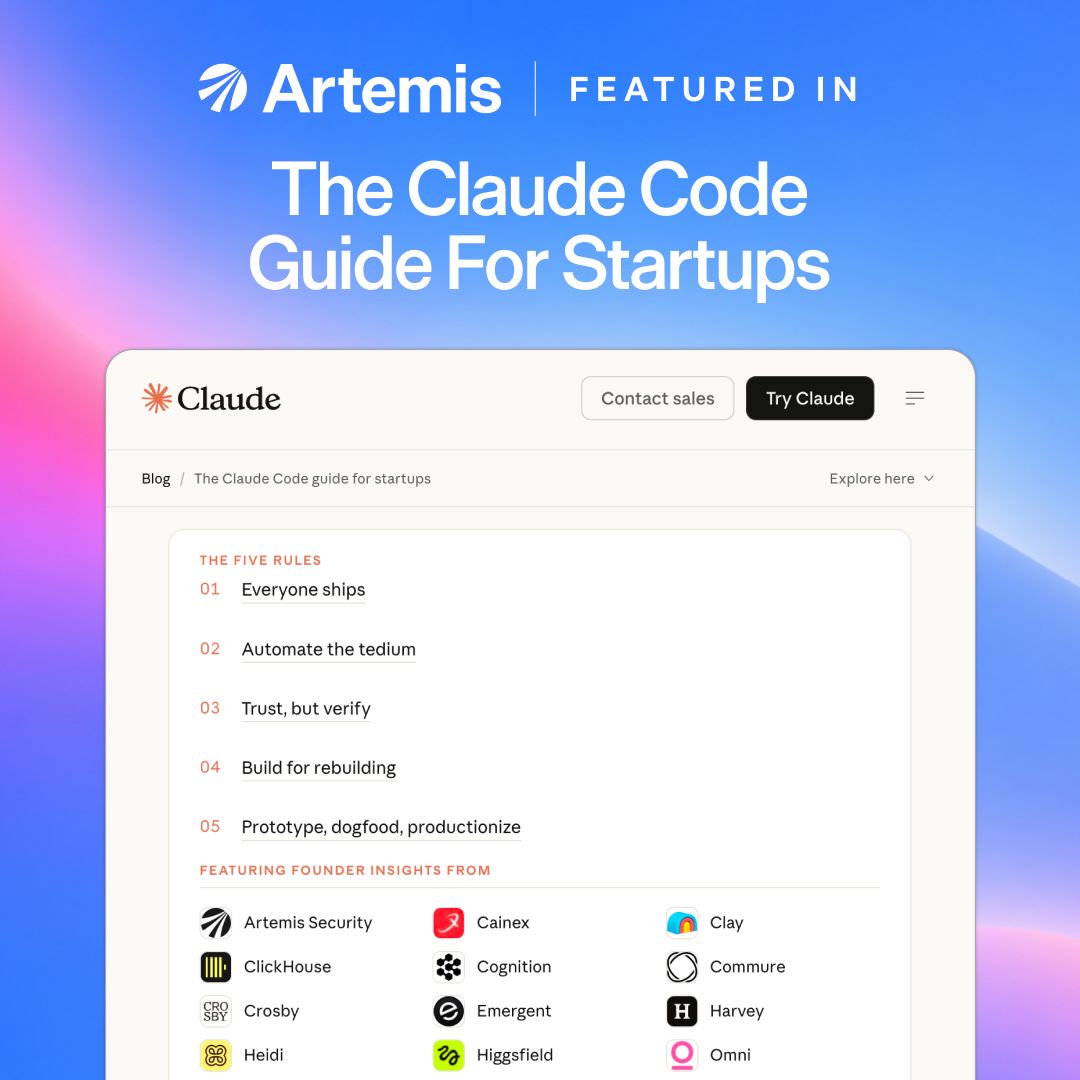
Excited to share that Anthropic just highlighted Artemis Security in their Claude Code Guide for Startups, a writeup on how the most AI-native companies operate. Artemis is the only cyber company featured in this list alongside a dozen of the world’s most AI-Native companies we admire including Cognition, Clay, ClickHouse, and Harvey. In the piece, we mention that everyone is racing to build AI products. Far fewer are rebuilding how their company actually runs. The second one is the much bigger unlock. Artemis runs as an AI-native company, not a company that happens to use AI. It's the reason we ship more than 5,000 PRs a week with a team a fraction the size of the incumbents. This allows us to deliver swiftly and reliably to protect F500 companies, Cursor, and many more enterprises, all to stop attacks at machine speed. Full guide in the comments.
- GreyNoise IntelligenceSince 29 Aug 2026
Check out Mark Mager's inaugural blog post published 0.032 seconds after joining GreyNoise Intelligence. He wrote about how we're thinking about detecting everything, everywhere, all the time when the slope of vulnerabilities disclosed approaches a vertical line. https://lnkd.in/eiGyRJ-e
- Artemis SecurityRecorded 21 Sept 2026
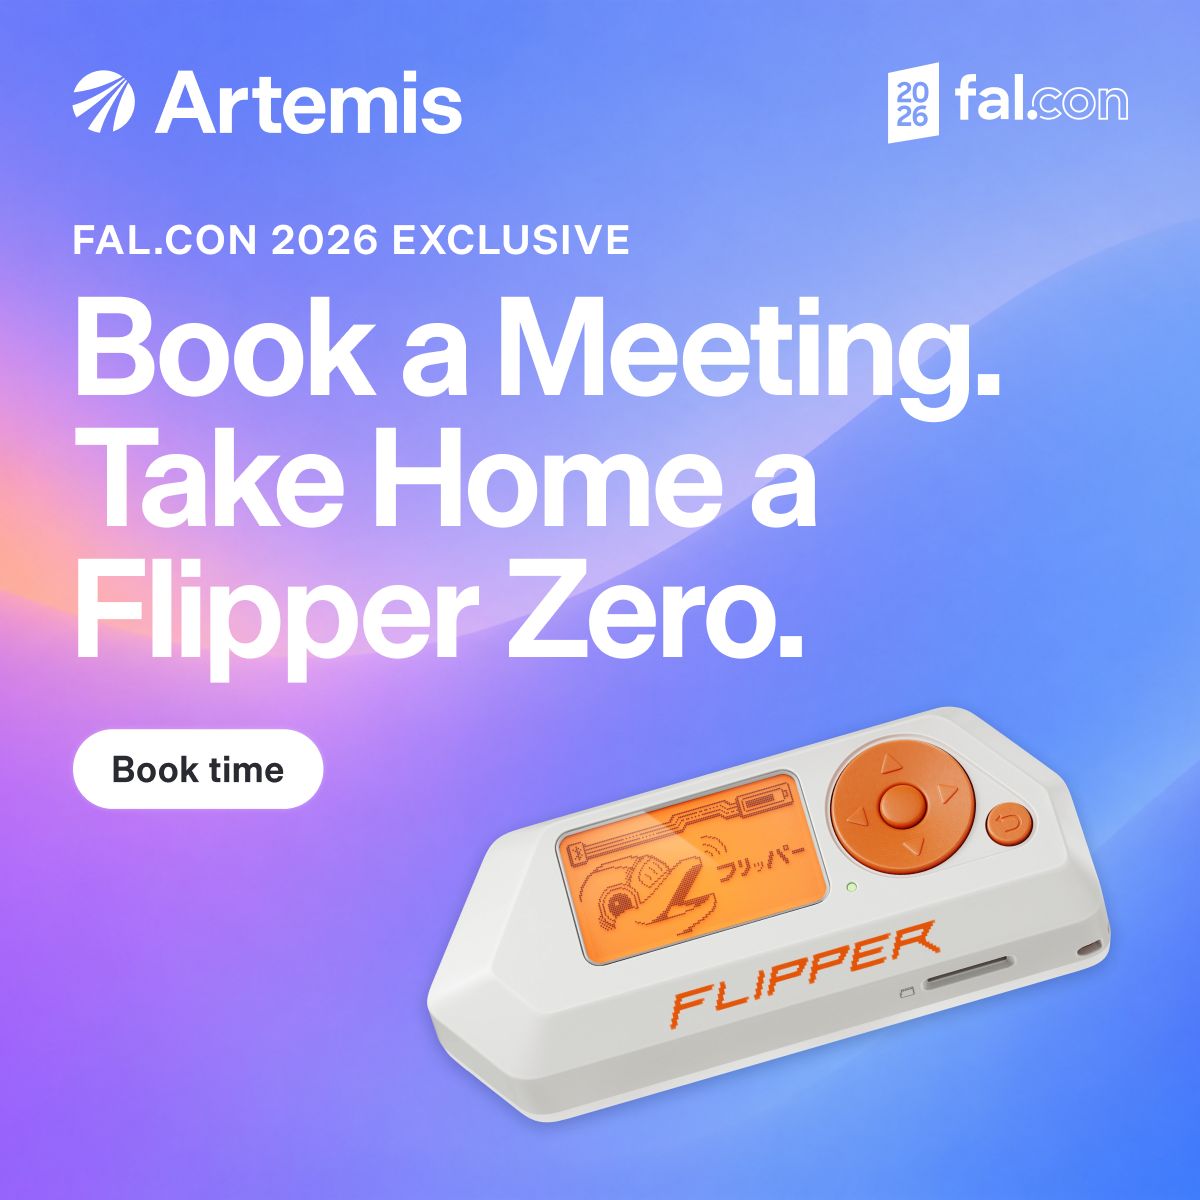
Attending Fal.Con? Book a meeting with our team, show up, and walk away with the internet's favorite hacking multi-tool, on us.
- GreyNoise IntelligenceSince 11 Sept 2026
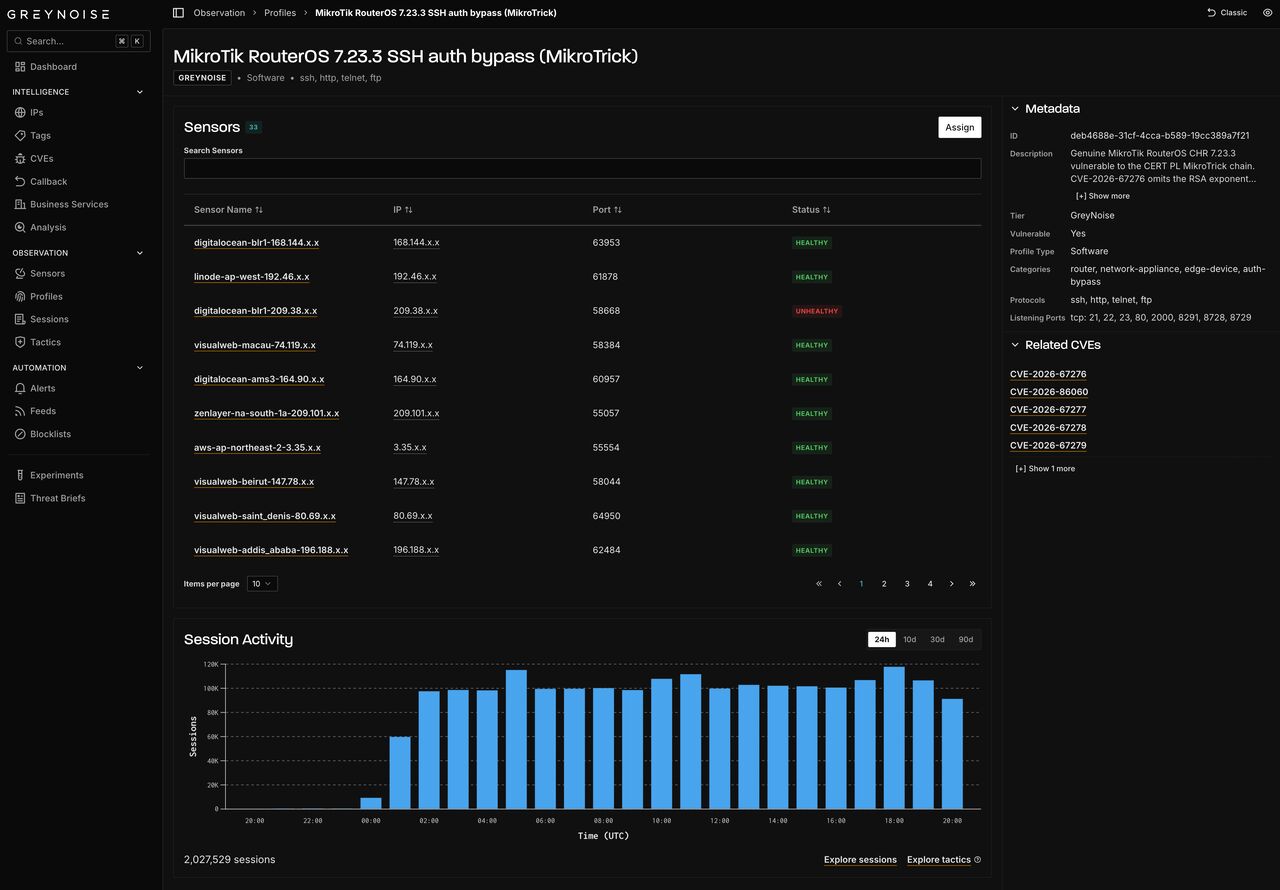
GreyNoise Intelligence is positioned to detect in-the-wild exploitation of the recent MikroTik "Mikrotrick" bug. A big-enough saturation of these profiles are up and running on our grid. All GreyNoise Swarm customers can deploy this profile right now as well. Exploitation has been publicly reported, but I do not believe mass, automated exploitation has begun yet. Last week CERT Polska shared their observation that six RouterOS vulnerabilities that are being chained in the wild. MikroTik patched on 2026-09-03 - 7.25beta3, 7.24.2, 7.23.4, and 6.49.21. If you're on 7.x below 7.23.4, or 7.24.x below 7.24.2, or 6.x below 6.49.21, you're in range. A public POC has been posted. The attack chain is complex and wraps together the following CVEs: CVE-2026-67276 - SSH publickey forgery <---- this is the banger CVE-2026-86060 - SSH argument injection CVE-2026-67279 - unauthenticated command execution via rekey CVE-2026-67277 - btest pre-auth uninitialized buffer CVE-2026-67278 - X.509 signature forgery CVE-2026-67281 - WebFig /jsproxy unauthenticated root file read This is one of those attacks that's nightmarish to track from internet-watchers' perspectives. The network portion of the attack is over SSH-encrypted channels, post-keypair exchange, which means you can't use out-of-the-box network comms to detect the attack (unless you've got some kind of black magic to extract key material from running devices and decrypt communications 👀) Worse yet, the bugs target an embedded system, which presents lots of challenges WRT collecting host artifacts. Unfortunately we still can't run Microsoft Defender on Mikroktik routers, because neither Mikrotik routers, nor any routers, run Microsoft Windows. This is going to end up being one of those bugs where the majority of defenders will initially have to rely on the fingerprints of the known public POCs, which we will report as throughly as we are able to. Regardless, I'm pretty confident GreyNoise is in a good position to observe mass-exploitation of these vulnerabilities as soon as it starts.
- CorpiaRecorded 21 Sept 2026
Gestão de acessos de TI com segurança e eficiência. Acompanhe a Corpia
- CorkRecorded 21 Sept 2026
Missing agents? MFA turned off? Cork finds it. You fix it. No more blind spots. Book a Demo Today!
- CorkRecorded 21 Sept 2026
Your tools aren’t talking to each other. That’s where your biggest security risks hide. Cork makes them talk — and closes the gaps. Book a Demo to learn more Today!
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.