On air · 1 of 3 networks
Query
- query.ai
- Cybersecurity
- US
- 41 employees
Query’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 28. Watch Query with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 28 | Checked 29 Oct 2026 | See all 28 ads → | ||
| Meta | Not checked | — | |||
| None recorded | 0 | No ads found on the Google Ads Transparency Center | Checked 30 Oct 2026 | Collect them with the API → |
Query has 28 live LinkedIn ads. We recorded no Google ads on 30 Oct 2026.
Latest ads
- LINKEDIN · IMAGERecorded 11 Oct 2026
There's probably more security data stored in Amazon S3 than anywhere else on earth. Most of it never sees the light of day in the average SOC. Security teams were wise to retain it, but using it takes a data engineer they often don't have, so we've built one into the Query product. Query Accelerated Connectors launched today. Point us at an S3 bucket, and that data joins everything else on the Query Security Data Mesh. Your analysts and agents can use all of it for the investigations, threat hunting, detections and incident response work they do every day. It's priced based on the data volume you choose to retain. Most of your data should still stay right where it lives, but sometimes you need a place to store it. Federate when possible. Accelerate when necessary. Built for the security data teams store in AWS. More details on the launch in the first comment below. AWS Partners
- LINKEDIN · IMAGERecorded 21 Sept 2026
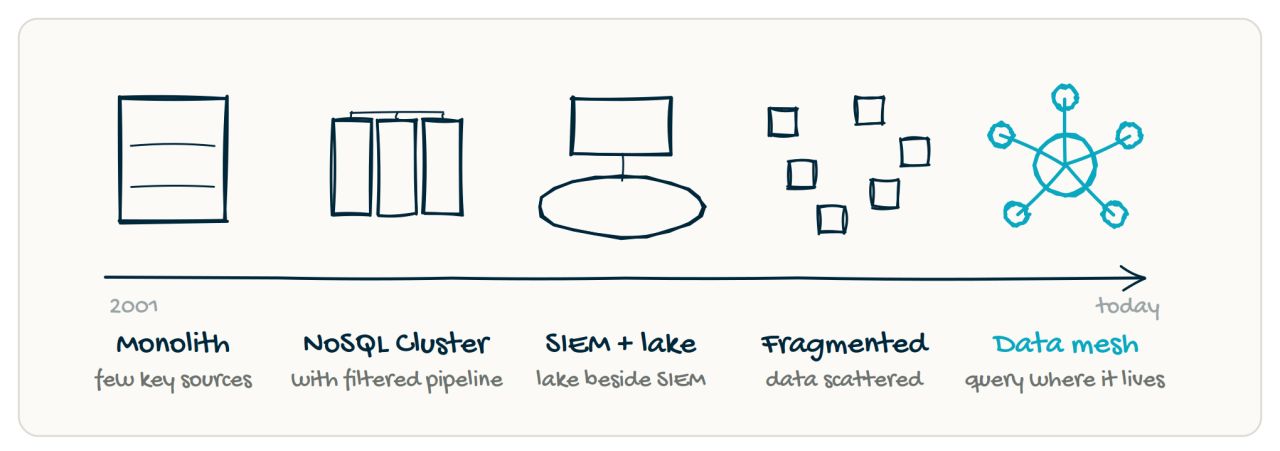
Last month I posted about my 25 years of building every SIEM architecture, and then seeing it lose to the same problem: the data outgrew the architecture. See that evolutionary journey in the diagram below. And then let’s talk about the new architecture I am proposing. It is something I have been building and refining over the last 5 years. The new architecture flips the problem. We start by accepting that distributed, heterogeneous data is the natural environment. Don't impulsively / habitually move big data to your SIEM vendor. Rather, we add a federation layer in our security stack to make the data discoverable and addressable. The federation layer creates the metadata that describes each source, its location, its data, its schema, and the APIs to reach it. It connects and joins the relevant pieces from across the environment and returns results in one unified data model. Storage, indexing, retention, and scaling get decided per source, based on what each kind of data actually needs, instead of one bill for everything. At that point the SIEM isn't a repository anymore. It becomes what it was truly meant to be – a security analytics brain running on top of the environment that already holds the data. At Query, we call this architecture a Security Data Mesh. The best part: your legacy SIEM folds into it. So does your security data lake project and so does your EDR. All without needing a major data migration. You investigate everything in place, you cut the cost of moving and duplicating data, and your AI finally performs on your whole environment instead of the fraction you could afford to centralize. Let’s stop fighting to centralize and own the data. Instead, let’s make it work for us from within its natural environment. Let me know if you agree/disagree. This has already been quite an evolutionary journey and I would love to learn from your experiences. #SIEM #cybersecurity #data #secdataops #AgenticSOC
- LINKEDIN · IMAGERecorded 21 Sept 2026
Your SIEM bill keeps growing. Your coverage doesn't. There is a version of security operations where that trade-off doesn't exist. The data you couldn't afford to ingest becomes operational. Detections run on data wherever it lives. Your AI agents run across all of it. That is what the Query Security Data Mesh is for. Security operations beyond your SIEM. No migration required.
- LINKEDIN · IMAGERecorded 21 Sept 2026
Centralize the insights, not your data. Security data is distributed by default. Your SIEM holds a fraction of it. The Query Security Data Mesh connects your data wherever it lives: cloud storage, data lakes, EDR, identity, network tools, 50+ sources in all. Lower costs. More coverage. No ingestion required.
- LINKEDIN · IMAGERecorded 21 Sept 2026
Detection coverage is constrained by your ingestion budget. Every source that never lands in your SIEM is a source your detections can't see. That blind spot isn't a tuning problem. It's an architecture decision, made by an opex budget. Federated Detections break the dependency. Write a rule once and run it across every connected source, wherever the data lives. No ETL, no duplication, no re-platforming required. Extend detection coverage across all your security data, including sources your SIEM will never ingest.
- LINKEDIN · IMAGERecorded 21 Sept 2026
Your security team, multiplied. Same analysts. Same shift. More alerts investigated, more hunts run, a backlog that finally gets worked. Query Workers run the cases your team never had time for: evidence assembled, every query logged, every gap flagged. Your analysts make every call. AI for the SOC that makes your job easier.
6 of 28 adsSign up to see every Query ad, filter by format and date, and get alerts on new ones.
See all 28 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.