B2B ad examples
2 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- Board of CyberSince 11 Sept 2026
690/1000. C’est le score moyen observé dans notre analyse de 21 700 entités françaises susceptibles d’être concernées par NIS2. Découvrez le Panorama NIS2 2026 de Board of Cyber : une lecture inédite de l’exposition cyber des organisations françaises et de leurs chaînes d’approvisionnement. Téléchargez la synthèse !
- Board of CyberSince 11 Sept 2026
690/1000. C’est le score moyen observé dans notre analyse de 21 700 entités françaises susceptibles d’être concernées par NIS2. Découvrez le Panorama NIS2 2026 de Board of Cyber : une lecture inédite de l’exposition cyber des organisations françaises et de leurs chaînes d’approvisionnement. Téléchargez la synthèse !
- CloberSince 15 Sept 2026
Antes era un "y si cambiamos de proveedor...". Ahora es un hecho. Seguir dependiendo de un único fabricante ya tiene un coste real, y cada vez más empresas lo están revisando. Descubre en menos de un minuto cuánto podrías ahorrar con una infraestructura más independiente y flexible. Rellena el formulario y te lo calculamos.
- CloberSince 15 Sept 2026
Antes de comprometer el presupuesto de IT del año que viene, mira cuánto te cuesta seguir como estás. Si tu renovación de licencias de virtualización se acerca, este es el momento de comparar antes de firmar. Te lleva menos de un minuto y puede ahorrarte una sorpresa en el presupuesto de 2027. Rellena el formulario y te lo calculamos.
- CCRCSince 15 Sept 2026
Bij de Rabobank zag ik hoe een uitstekend voorbereide crisisorganisatie ineens onzeker werd zodra het woord *cyber* viel. Die reactie bleek achteraf volledig onterecht. Toen ik destijds betrokken was bij cybercrisisoefeningen, merkte ik iets opvallends. De bestaande crisisorganisatie was uitstekend voorbereid op "klassieke" crises. Maar een cybercrisis? Dan veranderde de sfeer. Ineens leek alles anders: complexer, technischer, "iets voor de IT-afdeling". Terwijl de werkelijkheid veel eenvoudiger bleek. 👉 Een cybercrisis is op strategisch en tactisch niveau helemaal niet zo anders dan iedere andere crisis. Sterker nog: cybercrisismanagement is veel minder bijzonder dan we vaak denken. Natuurlijk heeft een cyberincident zijn eigen kenmerken. Maar de vragen waar een crisisteam mee worstelt, zijn heel vergelijkbaar met andere typen incidenten. ▪️Wat is er aan de hand? ▪️Welke impact heeft dit op onze organisatie? ▪️Wie informeren we? ▪️Welke keuzes moeten we nú maken? ▪️Hoe houden we de regie? Bij de Rabobank hebben we daarom niet een compleet nieuwe crisisorganisatie gebouwd. We hebben de bestaande crisisorganisatie geholpen om cyber beter te begrijpen. De reactie toen dat eenmaal gerealiseerd was: "Het valt eigenlijk best mee." Dat klinkt misschien wat ongenuanceerd, maar er zit een belangrijke les in. 👉 Veel organisaties denken dat ze voor cyber helemaal opnieuw moeten beginnen. Mijn ervaring is juist dat de basis er vaak al is. Je hoeft die basis alleen uit te breiden met de specifieke dilemma's die een cybercrisis met zich meebrengt. Dat inzicht is uiteindelijk ook één van de belangrijkste redenen geweest om CCRC op te richten. We willen organisaties laten ervaren dat de stap naar cyberweerbaarheid vaak veel kleiner is dan ze vooraf denken. Ik ben benieuwd hoe dat binnen jouw organisatie is. Wordt een cybercrisis nog gezien als iets fundamenteel anders dan een "gewone" crisis? Of zijn die twee werelden inmiddels samengebracht?
- CCRCSince 15 Sept 2026
In de eerste uren van een ransomware-aanval kijkt iedereen naar de CISO. Een paar uur later kijkt iedereen naar HR (waar zijn onze mensen?), naar communicatie (wat zeggen we naar buiten?), naar legal (welke meldplicht?), naar finance (wat kost dit per uur stilstand?) en naar logistiek (hoe leveren we vandaag uit?). ➡️ Het is dezelfde crisis. Maar de bottleneck verschuift elk uur. En wie dat niet weet, blijft hangen in de eerste fase totdat het te laat is voor de andere fases. De vraag is niet alleen of IT klaar is. De vraag is of al die andere afdelingen weten dat zij straks aan de beurt zijn en hoe ze de vragen op gaan vangen.
- CuebidSince 16 Sept 2026
Tillväxt. Produktivitet. Säkerhet. Kontinuitet. Fyra frågor som hör hemma på ledningens agenda. Och fyra frågor som är beroende av en digital infrastruktur som fungerar. Nätverket kanske är mer av en affärsfråga än det först verkar.
- Cynet SecuritySince 25 Sept 2026
Your team sees thousands of alerts a week. Cynet handles 90%+ of remediation on its own, so your analysts can focus on the attacks that matter.
- DataDomeSince 29 Sept 2026
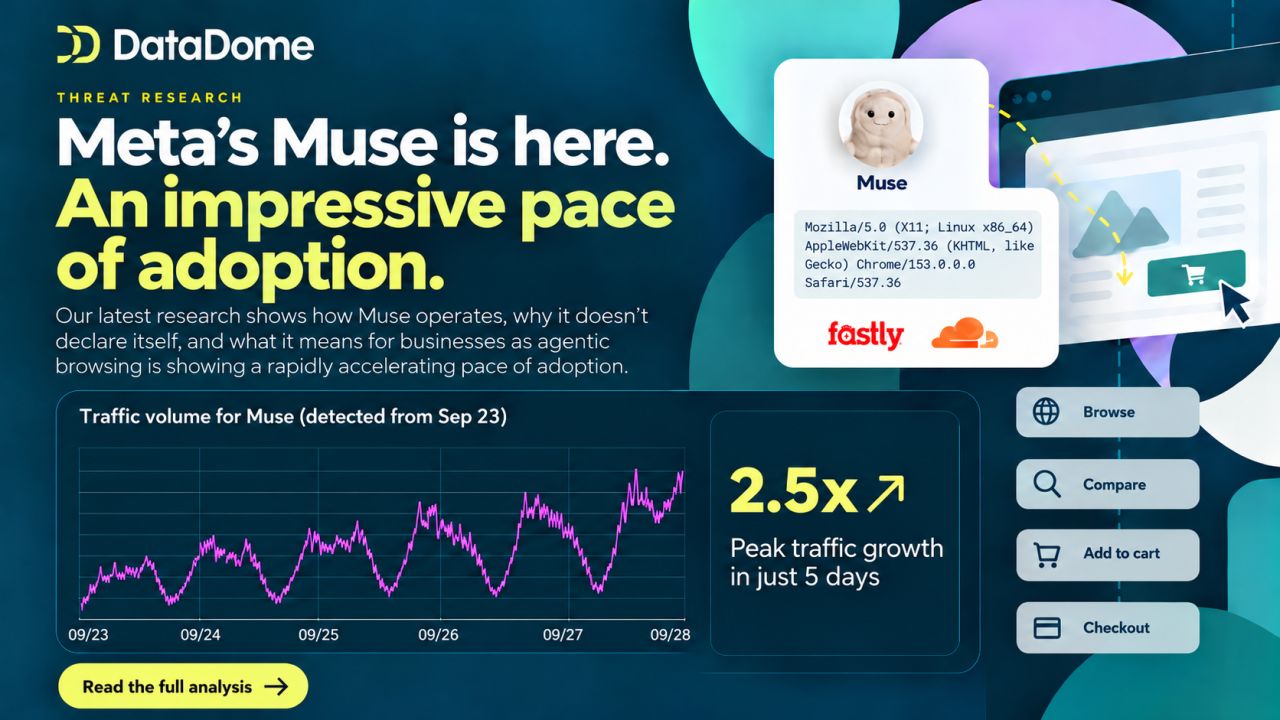
The agentic web is moving fast, and Meta’s Muse is one of the clearest signals yet. Our Threat Research team has been identifying Muse by analyzing complex client-side signals from the browser itself. Across live sessions, the environmental overlap is striking, revealing a highly consistent sandboxed setup behind traffic that otherwise looks like ordinary Chrome. And the growth is already significant: since September 23, peak Muse traffic across our network has increased about 2.5x. What makes Muse especially interesting is that it does not declare itself. There is no dedicated User-Agent, published IP range, or signed identity signal. But even identifying the agent is only part of the challenge. The real question is intent. A legitimate agent completing a checkout and a fleet of agents scraping a catalog can look very similar. Our latest Threat Research breaks down what Muse means for the agentic web: 👉 https://lnkd.in/gjgdiY56
- CryptomathicSince 29 Sept 2026
Before you replace your HSM estate one-for-one, ask whether you want to carry the same architecture into the next generation. A like-for-like replacement may be right. But before the plan is fixed, I’d ask three questions. 1. What genuinely needs dedicated HSM infrastructure? 2. Which cryptographic services could be shared? 3. And how much application work will the next hardware change require? Some separation is essential for resilience, isolation or performance. That needs to stay. The opportunity is to identify duplication and repeated integration work that could be reduced through shared cryptographic services. That’s the comparison I’d make before committing to the next hardware investment. I’ve written an article on what to assess, and where CK360 could fit. You’ll find it alongside this video in the comments.
- Fig SecuritySince 29 Sept 2026
Fig Security ♥️ NVIDIA We're happy to share that Fig was chosen to be a founding member of NVIDIA's new Open Agent Safety Platform! You know how agents have been being a little naughty recently and scaring the security community every other week? Right, so NVIDIA built a platform that controls what AI agents are allowed to do, from the software they run in all the way down to the chip. The Agentic SOC Alliance, of which we are a part, was chosen to be a founding partner to this initiative. While NVIDIA governs what agents can do, Fig makes sure the detections and data those agents rely on keep working.
- ControlMonkeySince 29 Sept 2026
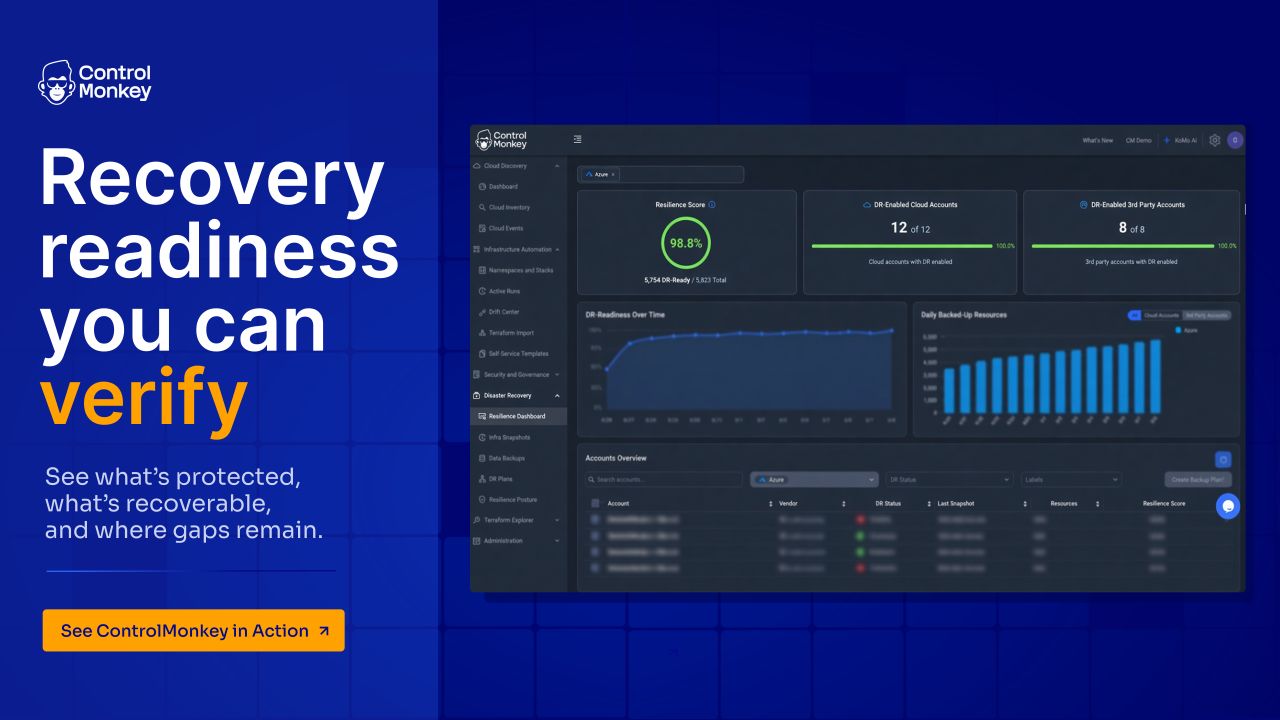
You’ve got backups. But do you actually know how recovery-ready your environment is? ControlMonkey gives teams a clear view of DR coverage, protected resources, and recovery gaps across cloud and third-party environments - so recovery readiness can be measured before it’s tested by a real incident.
- Fort CyberSince 29 Sept 2026
Pe 22 septembrie, WordPress a publicat un fix pentru o vulnerabilitate critică în core: CVE-2026-87902, CVSS 9.2. Primele tentative de exploatare au apărut la doar câteva ore după publicare. Patch-ul există pentru fiecare versiune afectată, de la 4.7 la 7.1.1, și se aplică repede. Întrebarea de azi pentru organizații e alta: a ajuns patch-ul pe fiecare site, inclusiv pe mediile de staging, pe site-urile de campanie și pe cele administrate de terți, adică tocmai acolo unde rămâne cel mai des fără patch? În noul Fort Cyber Brief explicăm ce s-a întâmplat tehnic, ce recomandăm echipelor IT și ce întrebări poate pune azi și cineva care nu e tehnic. Pentru entitățile sub NIS2 și DORA, contează și ce poți demonstra la audit: când și cum s-a aplicat patch-ul.
- Cyber360 | Specjaliści od cyberbezpieczeństwaSince 29 Sept 2026
Seryjny haker „fingerprint” znów uderza. Tym razem na celowniku popularny system Fakturownia.pl. Dopiero co analizowaliśmy zmasowane wycieki danych medycznych (MyDr, Qbusoft/Medyc.pl), a ten sam cyberprzestępca poinformował o kolejnym udanym ataku. Ofiarą padła Fakturownia.pl – jeden z najpopularniejszych systemów do fakturowania online w Polsce. Według pierwszych doniesień serwisu Zaufana Trzecia Strona, haker uzyskał dostęp do wewnętrznych baz danych, wystawiając na ryzyko dane tysięcy polskich przedsiębiorców, kontrahentów oraz rejestry finansowo-księgowe. Dlaczego to krytyczny incydent dla sektora B2B? 1️⃣ Cyfrowy łańcuch dostaw pod lupą: Przestępcy coraz rzadziej atakują pojedyncze korporacje. Celują w dostawców oprogramowania SaaS (finansowych, medycznych, ERP). Przełamując zabezpieczenia jednego dostawcy, uzyskują dostęp do danych setek tysięcy firm i ich klientów. 2️⃣ Ryzyko wtórnych ataków wyłudzeniowych: Dostęp do historii wystawionych faktur to dla przestępców idealny materiał do ataków typu Business Email Compromise (BEC) oraz precyzyjnego phishingu. Podstawianie fałszywych numerów kont na fakturach czy podszywanie się pod kontrahentów staje się dziecinnie proste. 3️⃣ Weryfikacja dostawców (Third-Party Risk): Przypadek ten pokazuje, jak krytycznym elementem architektury bezpieczeństwa staje się bezwzględny audyt bezpieczeństwa zewnętrznych narzędzi, z których korzystają Państwa działy księgowe i operacyjne. Dalej zastanawiacię się czy warto zainwestować w cyberochronę 24/7? Potrzebujesz wsparcia? Skorzystaj z formularza w komentarzu.
- FaciaSince 30 Sept 2026
Digital identity fraud is getting harder to spot because the fake often looks completely normal. Deepfakes, synthetic identities, and manipulated images can all pass a basic visual check. That is why businesses need to verify more than just the face on the screen. Facia helps confirm that the person behind a digital identity is real and present during verification. Because looking genuine should never be enough. . . . #Facia #IdentityVerification #DigitalIdentity #DeepfakeDetection #FraudPrevention
- InfoGuard AGSince 29 Sept 2026
🤖 𝐊𝐈 𝐢𝐦 𝐒𝐎𝐂 𝐢𝐬𝐭 𝐳𝐰𝐢𝐧𝐠𝐞𝐧𝐝 𝐧𝐨𝐭𝐰𝐞𝐧𝐝𝐢𝐠. Doch wer bestimmt die Spielregeln? Ihre Bedeutung für die Cyberabwehr ist essenziell, um im Wettlauf gegen die Angreifer zu bestehen. Denn mit der zunehmenden Geschwindigkeit und Komplexität von Cyberangriffen wird KI zu einem entscheidenden Faktor für eine wirksame Cyber Defence. 𝐃𝐨𝐜𝐡 𝐞𝐢𝐧 𝐒𝐎𝐂-𝐏𝐫𝐨𝐯𝐢𝐝𝐞𝐫 𝐤𝐚𝐧𝐧 𝐊𝐈 𝐧𝐢𝐜𝐡𝐭 𝐞𝐢𝐧𝐟𝐚𝐜𝐡 𝐧𝐚𝐜𝐡 𝐁𝐞𝐥𝐢𝐞𝐛𝐞𝐧 𝐢𝐦𝐩𝐥𝐞𝐦𝐞𝐧𝐭𝐢𝐞𝐫𝐞𝐧. Im SOC ist die Security-Telemetrie sehr umfassend und durch EDR-basiertes Tooling erhält die KI Zugriff auf sensible Daten. Die Telemetrie liefert tiefe Einblicke in Identitäten, Berechtigungen, Schwachstellen, Systeme und potenzielle Angriffswege. Wer diese Daten für KI-gestützte Analysen nutzt, muss Datenhoheit, Zugriffsrechte und Nachvollziehbarkeit konsequent regeln. Und Kunden die Wahlmöglichkeiten bieten, die zu ihren Sicherheits- und Compliance-Anforderungen passen. Für mich bedeutet «𝐀𝐈 𝐛𝐲 𝐃𝐞𝐬𝐢𝐠𝐧», diese Kontrolle von Beginn an im Betriebsmodell zu verankern. Für CIO und CISOs stellen sich damit ganz konkrete Fragen: ➡️ Welche Daten verarbeitet die KI? ➡️ Wo werden sie verarbeitet? ➡️ Wer kann darauf zugreifen? ➡️ Welche Entscheidungen darf sie vorbereiten oder automatisieren? ➡️ Und wo braucht es zwingend menschliches Urteilsvermögen? Genau deshalb investieren wir bei der InfoGuard AG in eine dedizierte KI-Infrastruktur im eigenen Betrieb. Damit ermöglichen wir kontrollierte Datenflüsse und KI-gestützte Security Services, die sich am Schutzbedarf der jeweiligen Organisation ausrichten. Die LLM-Datenverarbeitung kann je nach Anforderung des Kunden in der EU, in der Schweiz oder auf dedizierter InfoGuard-Hardware in der Schweiz erfolgen. 𝐊𝐈 𝐯𝐞𝐫𝐚𝐫𝐛𝐞𝐢𝐭𝐞𝐭 𝐃𝐚𝐭𝐞𝐧. 𝐌𝐞𝐧𝐬𝐜𝐡𝐞𝐧 𝐯𝐞𝐫𝐚𝐧𝐭𝐰𝐨𝐫𝐭𝐞𝐧 𝐄𝐧𝐭𝐬𝐜𝐡𝐞𝐢𝐝𝐮𝐧𝐠𝐞𝐧. Genau darin liegt für mich der Kern von Human-AI-Teaming. KI korreliert, priorisiert und verdichtet. Erfahrene SOC- und CSIRT-Fachpersonen bringen den Geschäfts- und Bedrohungskontext ein, treffen kritische Entscheide und steuern im Ernstfall die Response. In unseren 24/7 durchgehend personell besetzten Cyber Defence Centern verbinden wir dieses Prinzip mit Managed Detection & Response (MDR) und Managed Risk Exposure (MRE). So entsteht eine Cyberabwehr, die laufende Bedrohungen erkennt, relevante Angriffsflächen sichtbar macht, Risiken gezielt priorisiert und diese frühzeitig reduziert. Das SOC der Zukunft wird nicht autonom entscheiden. 𝐎𝐡𝐧𝐞 𝐊𝐈 𝐰𝐢𝐫𝐝 𝐞𝐬 𝐣𝐞𝐝𝐨𝐜𝐡 𝐳𝐮 𝐥𝐚𝐧𝐠𝐬𝐚𝐦 𝐬𝐞𝐢𝐧. Mehr zu unserem Ansatz für moderne Cyber Defence mit 24/7 SOC, MDR, MRE, KI und Datensouveränität findet ihr im Link im Kommentar. 👇
- FaciaSince 30 Sept 2026
Synthetic identities are getting harder to detect. Facia is built to keep verification one step ahead. . . . #Facia #SyntheticIdentity #IdentityVerification
- Fort CyberSince 29 Sept 2026
ENISA Threat Landscape 2026 analizează 8.257 de incidente care au afectat UE în 2025. Cifrele care vor circula cel mai mult: DDoS 51,3%, activitate motivată ideologic 57,3%. Cea mai importantă stă însă într-o notă de sub un grafic. Dintre cele 941 de evenimente malițioase raportate sub NIS2, aproximativ jumătate au root cause-ul „unknown”. La ANCPI, atacatorul nu a avut nevoie de AI sau de zero-day-uri. I-au fost suficiente o vulnerabilitate cunoscută din 2021 pe o mașină expusă public și o parolă de administrator refolosită. Atacul a fost descoperit la aproximativ 86 de ore după accesul inițial, în timpul unei mentenanțe de rutină. În România, deficitul ține mai puțin de threat intelligence și mai mult de execuție. În articolul scris de Radu Ailenei vă prezentăm ce arată datele ENISA, lecțiile din România și prioritățile care decurg de aici. 👇
- BlackstoneOne - peace of mindSince 2 Oct 2026
Vi oversætter sårbarhedsdata til beslutningsklar viden for bestyrelsen.
- CryptomathicSince 30 Sept 2026
A question for my network: is AI alone enough to create a CBOM you can actually trust? I'm interested to hear how others are approaching it. Where does AI add real value, and where is human oversight still essential?
- BlackstoneOne - peace of mindSince 2 Oct 2026
Vi översätter sårbarhetsdata till beslutsunderlag för styrelsen.
- Geordie AISince 1 Oct 2026
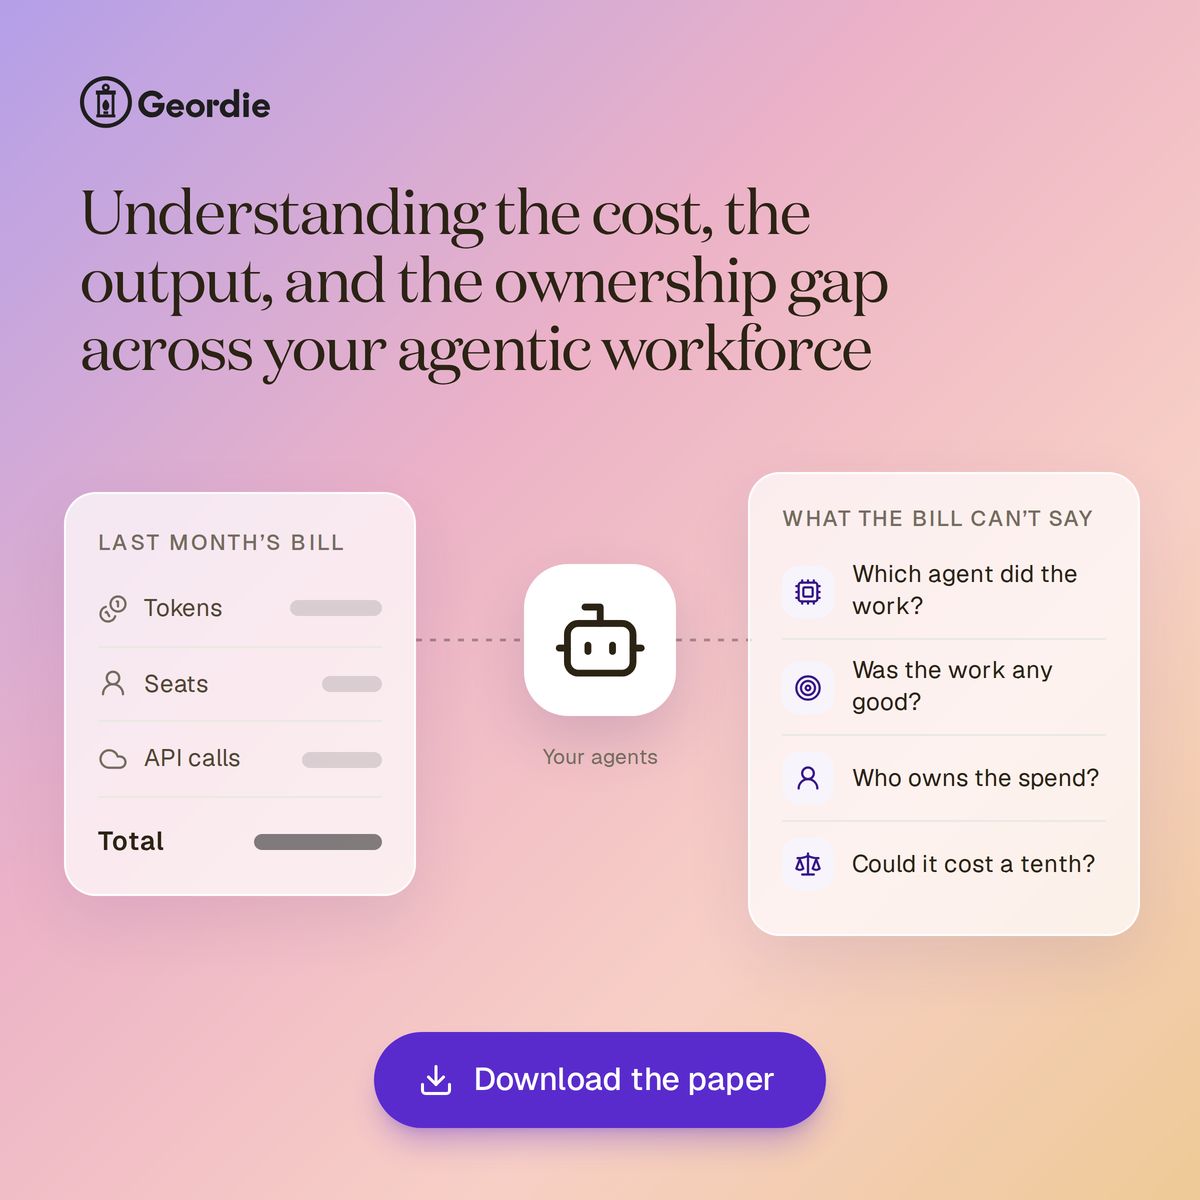
One company found a single employee spending $100K+ a year on AI, unnoticed. See how 50+ orgs trace agent spend to owners and outcomes.
- CyberheedRecorded 8 Oct 2026
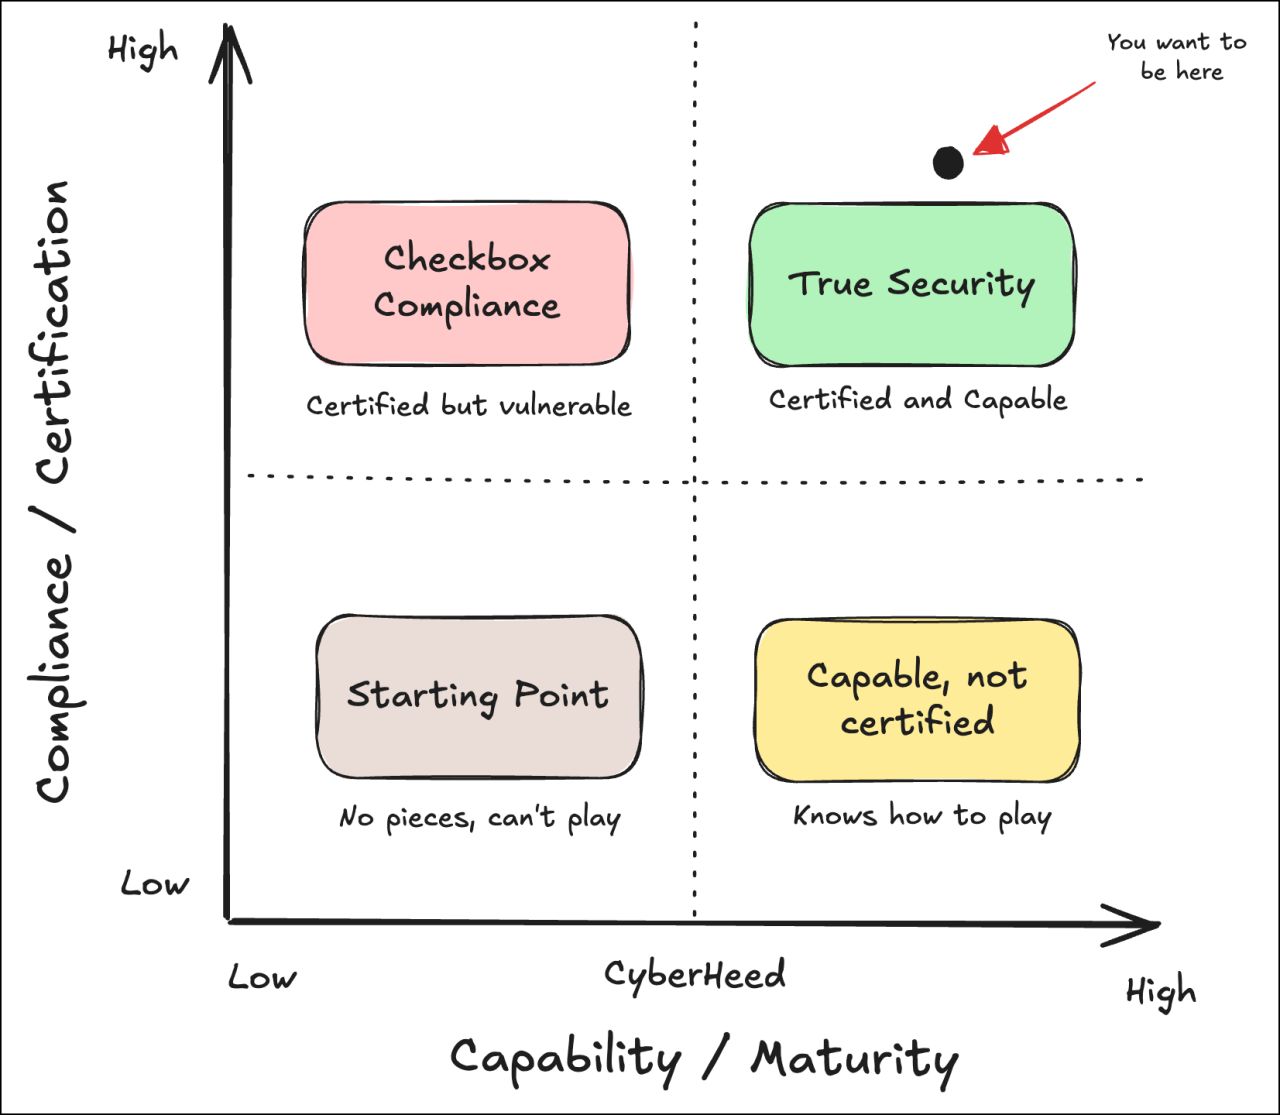
Your last audit gave you assurance on one day. What about the other 364? CyberHeed runs checks on your live systems continuously and judges them in your context, so your assurance holds every day, not just audit day.
- Human RisksSince 1 Oct 2026
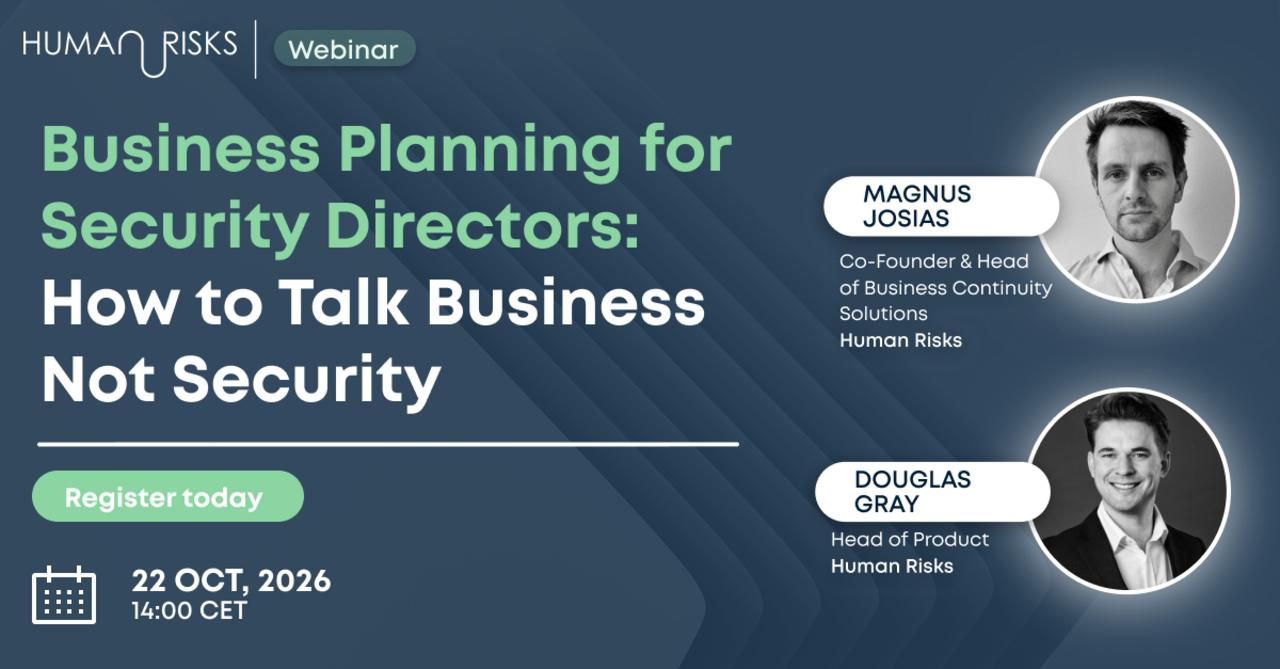
What does your security programme mean to the business? As the future budget allocations are being discussed, the window to prove security’s business value is narrowing. On October 22nd, join Magnus Josias and Douglas G. for a conversation about how to effectively communicate the value of security to key stakeholders. In this session, you'll learn: → How to align security with enterprise objectives → How to communicate security value in business terms → A practical template for prioritising your security plan 👉 Save your spot now!
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.