B2B ad examples
2 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- Bundesdruckerei-GruppeSince 29 Sept 2026
Anhand praktischer Beispiele erfahren Sie, wie Sie vertrauenswürdige KI erkennen, geordnet einführen und erfolgreich im Behördenalltag einsetzen.
- CYBEROOSince 16 Sept 2026
Identità non umane: risorsa strategica o nuovo punto di compromissione? Applicazioni, servizi e AI Agent utilizzano ogni giorno migliaia di identità non umane. Se una viene compromessa, può aprire l'accesso all'infrastruttura. Scopri come estendere la strategia Zero Trust alle Non-Human Identities. 👇
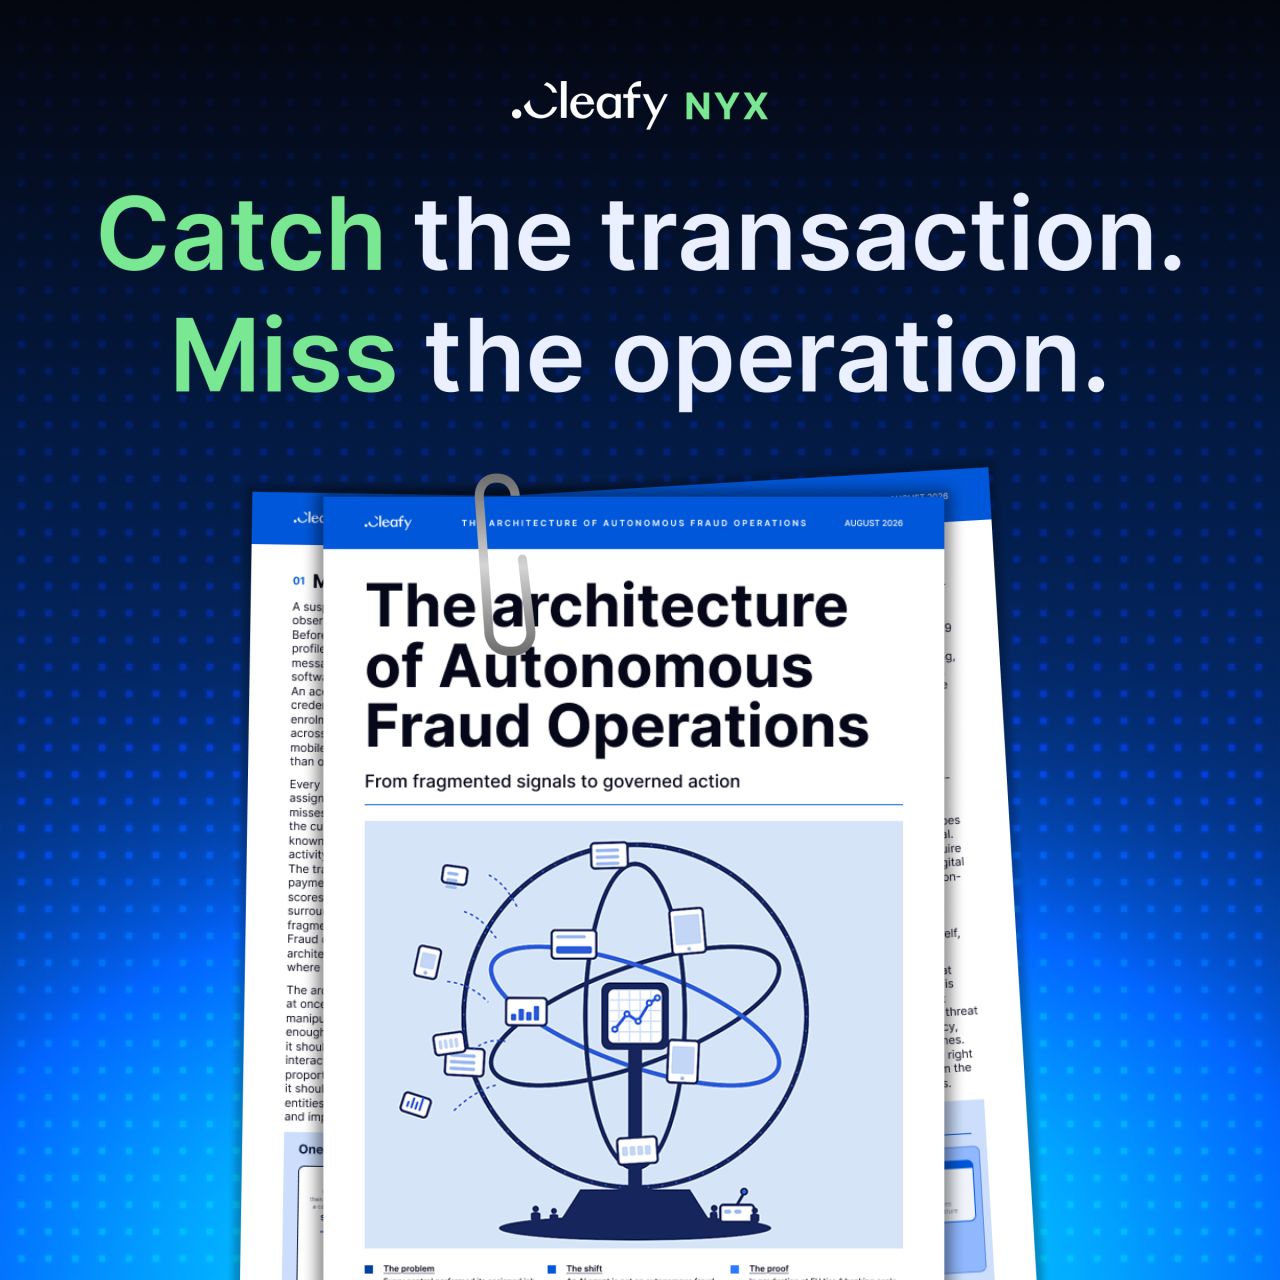
- CleafySince 17 Sept 2026
Catch the transaction. Miss the operation. That's what happens when detection stops at the signal instead of the pattern. This whitepaper shows how fraud teams can get from fragmented signals to governed action.
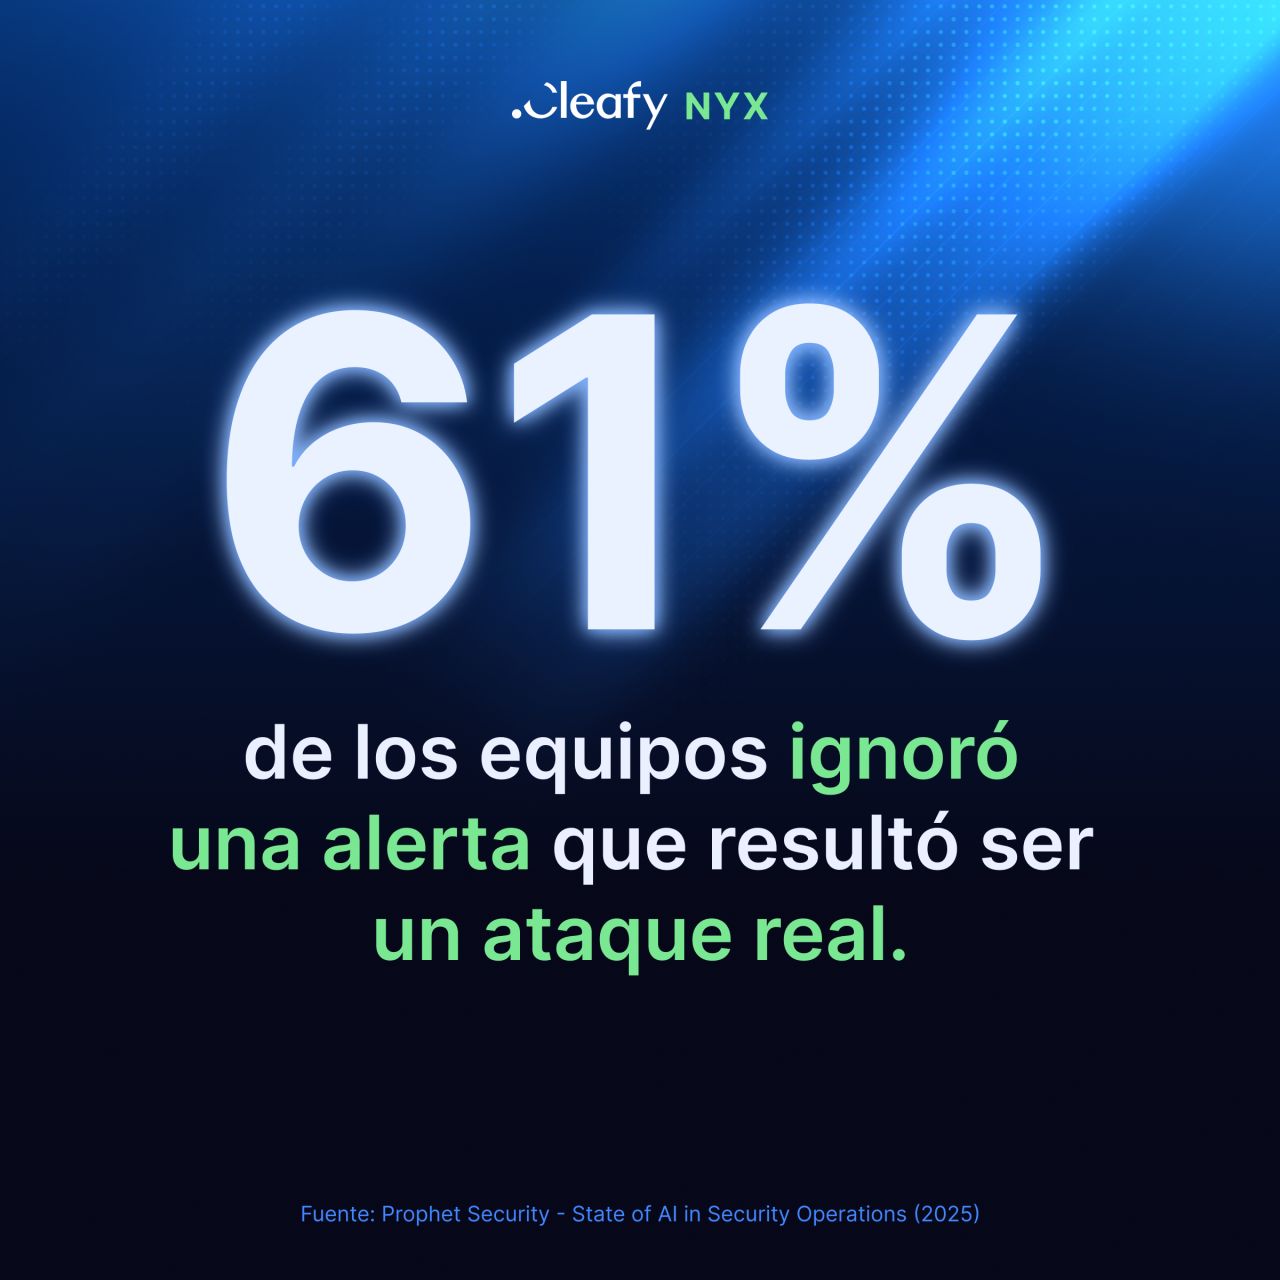
- CleafySince 17 Sept 2026
El 61% de los equipos ha ignorado una alerta que resultó ser un ataque real. No por descuido, sino por trabajar con fragmentos mientras el atacante ve toda la operación. Nuestro nuevo informe explica por qué las señales fragmentadas dejan escapar el fraude coordinado, y qué cambia con una visión conectada.
- BugHuntRecorded 8 Oct 2026
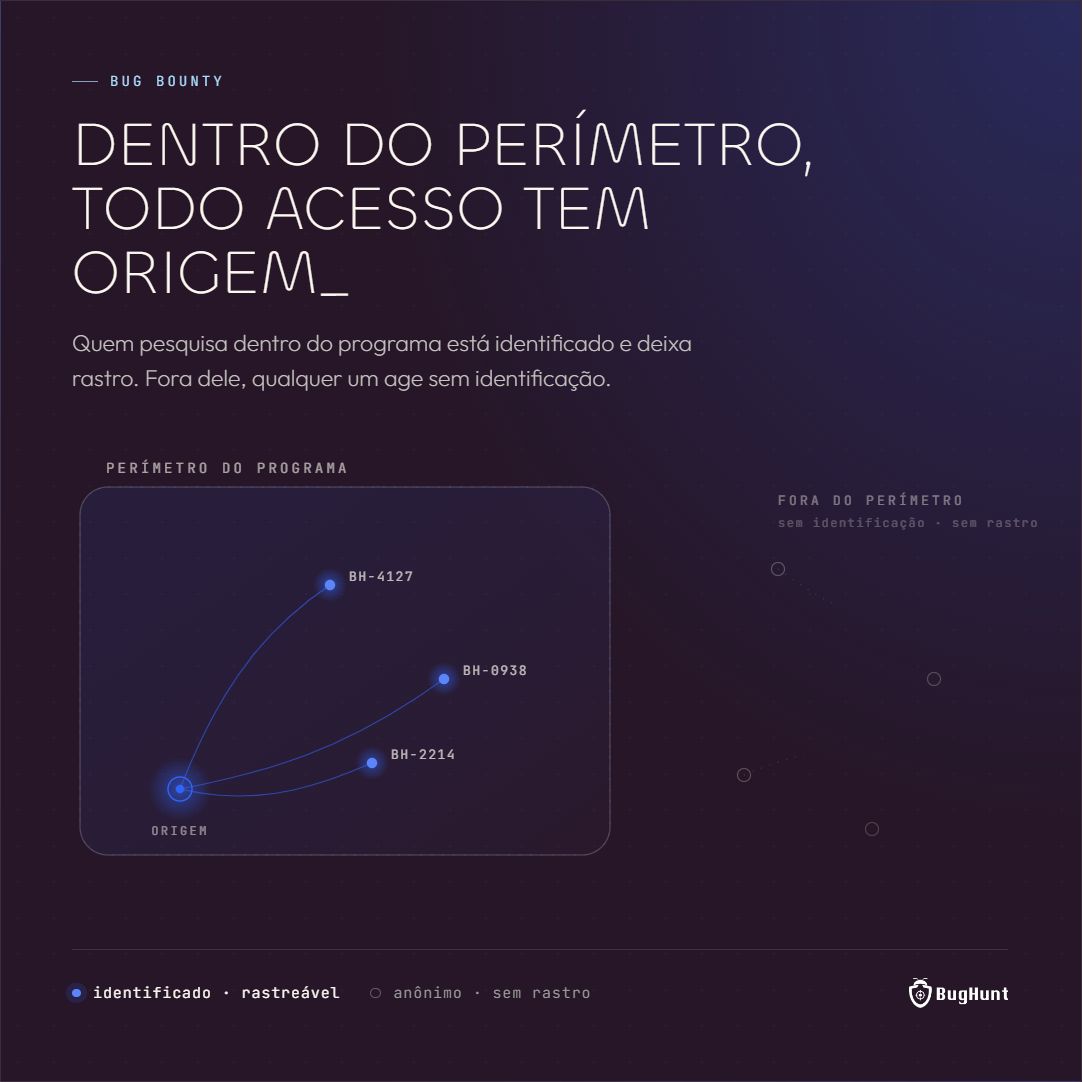
Uma das primeiras perguntas que aparece quando o programa de bug bounty chega no jurídico é se ele cria um novo risco para a empresa. A resposta técnica é não. Qualquer sistema com ativos expostos na internet já está sujeito a tentativas de teste por terceiros, com ou sem autorização. Isso acontece independentemente de haver um programa de bug bounty. O que o programa muda é o controle sobre esse processo. Vulnerabilidades que antes poderiam chegar sem identificação, sem regras e sem um canal definido passam a ser reportadas por pesquisadores identificados, seguindo a política, o escopo e os limites estipulados pela própria empresa. Sob a ótica da LGPD, um programa de identificação de vulnerabilidades pode fazer parte do conjunto de medidas técnicas e administrativas adotadas pela empresa para proteger seus dados e sistemas. Ou seja: o programa não cria a exposição. Ele estabelece regras, identifica quem participa e cria um canal para que vulnerabilidades sejam reportadas e tratadas de forma organizada.
- BugHuntRecorded 8 Oct 2026
O que impede um pesquisador de explorar o que encontrou em vez de reportar? A resposta começa pelo perfil de quem participa de um programa de bug bounty. Quem participa do programa está identificado na plataforma, aceita previamente termos de conduta e precisa seguir as regras definidas por cada empresa. Isso muda bastante a dinâmica. O pesquisador constrói uma reputação ao longo do tempo, e sua participação em novos programas depende de agir dentro das regras e reportar corretamente as vulnerabilidades encontradas. É um modelo em que os incentivos apontam na direção certa. Isso não significa que um programa elimina completamente o risco de alguém agir de forma maliciosa. Significa que, diferente de um cenário sem programa, existe identidade, regras de atuação, histórico de participação e consequências para quem ultrapassa os limites estabelecidos. Sem um programa, uma vulnerabilidade pode ser descoberta por alguém que a empresa não conhece, sem escopo definido, regras de atuação ou um canal formal para o reporte. Dentro de um programa de bug bounty, o cenário é diferente. O pesquisador sabe exatamente o que pode testar, quais são os limites e como deve reportar o que encontrou. Para o jurídico, esse é um ponto importante: não é apenas uma questão de autorização para testar. É também sobre criar regras, identificar quem participa e estabelecer um canal formal para lidar com vulnerabilidades. É isso que transforma uma interação que já poderia acontecer de maneira desestruturada em um processo com mais controle e previsibilidade.
- CyberVadisSince 18 Sept 2026
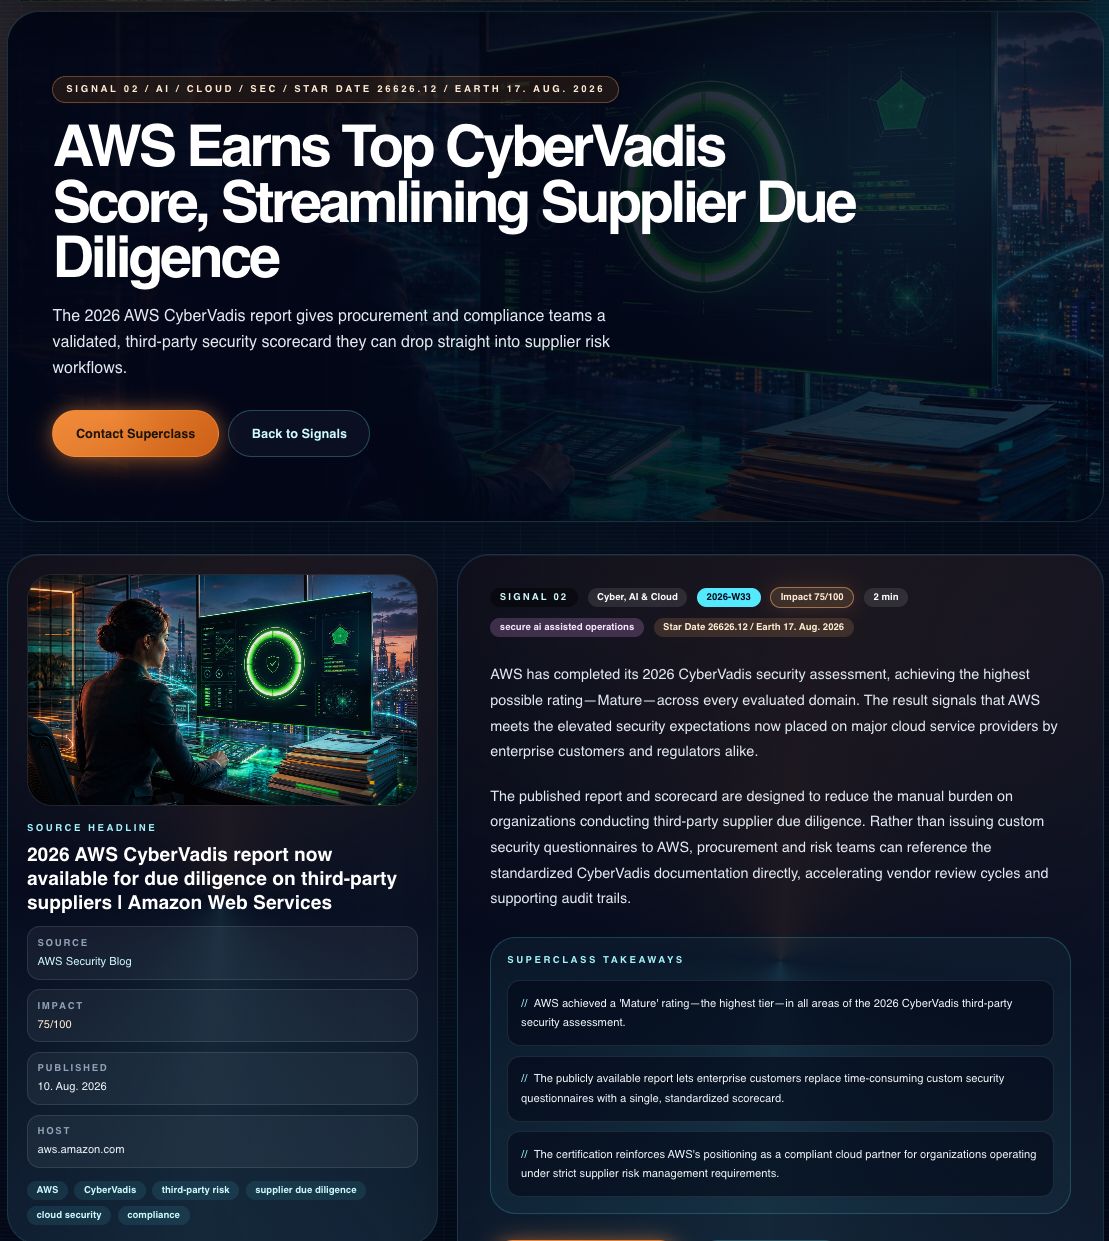
Do you need to cost-reduce and improve your due diligence on your third-parties? Let us, CyberVadis, help you to better manage your risk of your evolving third-party environment, comply with regulatory requirements and remove your supplier due-diligence burden. https://lnkd.in/eB8wfr3t (Contact CyberVadis, request a demo) https://lnkd.in/e8zfYh8r (AWS Security Blog)
- GarancySince 22 Sept 2026
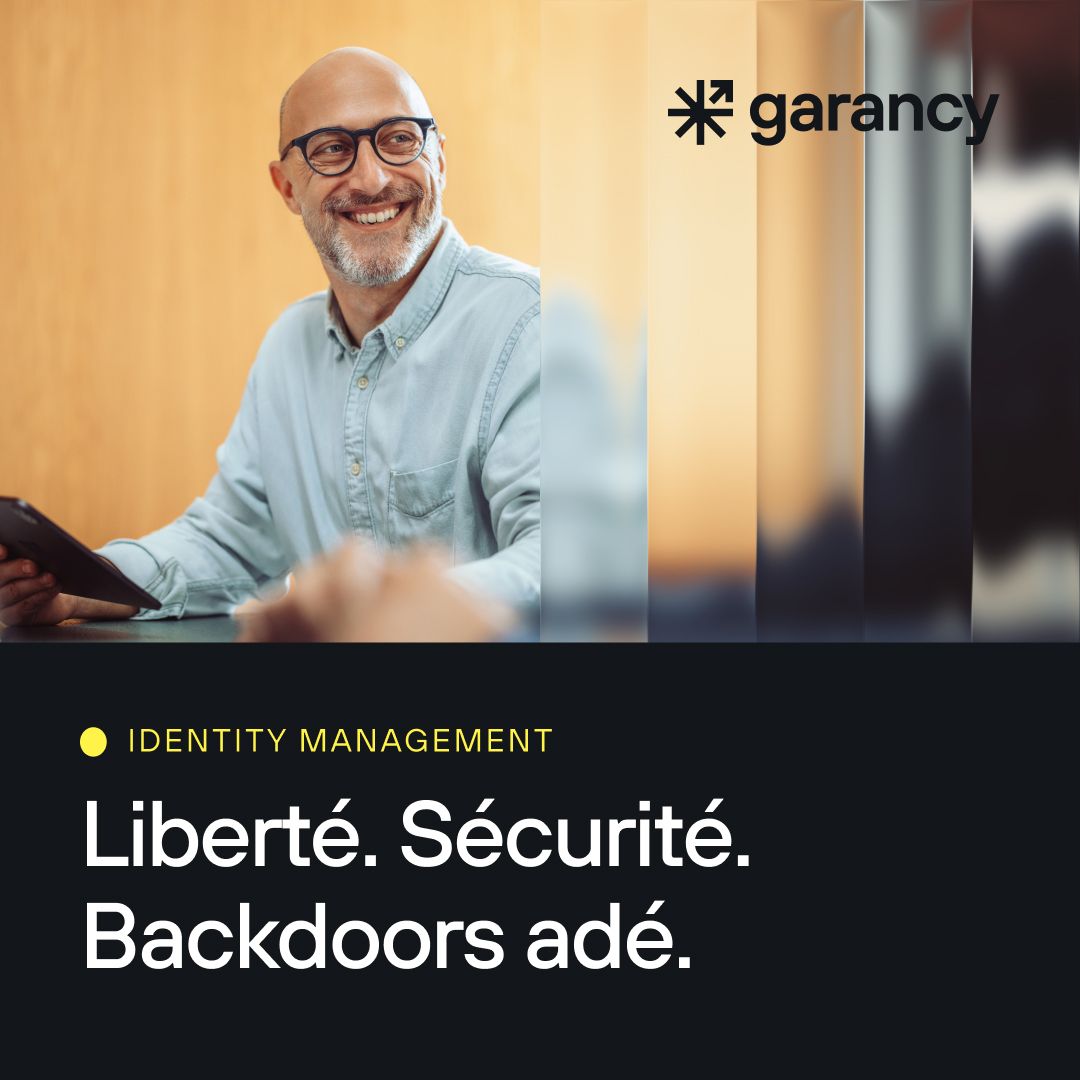
Kompromisslose Sicherheit – made in Europe. Steuern Sie Identitäten, Rollen und Berechtigungen souverän mit Identity Management von Garancy.
- Firmaprofesional, de Logalty GroupSince 18 Sept 2026
Visit the organization page for Firmaprofesional, Logalty!
- GarancySince 22 Sept 2026
Wie lückenlos ist Ihre IT geschützt? Steuern Sie Identitäten, Rollen und Berechtigungen mit Identity Management nach strengen EU-Richtlinien!
- Firmaprofesional, de Logalty GroupSince 18 Sept 2026
En auditoría y consultoría, la confianza empieza mucho antes de emitir un informe. 📑 Los certificados digitales permiten firmar documentación crítica, proteger información confidencial y aportar evidencias que refuerzan la autenticidad e integridad de cada proceso. El resultado son operaciones más seguras, trazables y alineadas con los requisitos de compliance. Porque cuando la credibilidad es el principal activo, cada documento cuenta. 👉 Más información: https://lnkd.in/dwXDyrKN #Compliance #CertificadoDigital #TransformacionDigital
- Dragos, Inc.Since 26 Sept 2026
Comparing OT security vendors? Forrester just named Dragos a Leader, ranked highest in Strategy, the only vendor to score a 5/5 in Vision. Dragos earned the highest possible score across all eight Forrester criteria, from product capabilities to services and community, so you're not betting on a platform that plateaus. Read Forrester's full assessment of Dragos.
- COMDARecorded 8 Oct 2026
כשאמצעי ההזדהות של העובדים מפוזרים בין מערכות שונות, אף אחד לא באמת יודע מה פעיל, מה פג תוקף ומה היה צריך להתבטל. מערכת CCMS לניהול גישה ארגונית מבית קומדע מרכזת את הכל במקום אחד: ⬅️ ניהול מרכזי All‑in‑One - הנפקה, הרשאות וביטול במסך אחד ⬅️ כרטיס חכם, Wallet, ביומטריה ו‑FIDO - גם בכרטיס משולב אחד ⬅️ אבטחה פיזית ולוגית לאורך כל מחזור חיי הכרטיס ⬅️ סנכרון ל‑AD, לוגים, דוחות ובקרה רציפה
- Fort CyberSince 19 Sept 2026
45% dintre organizațiile care au răspuns studiului nostru se încadrează în segmentul cu cel mai ridicat nivel de maturitate cibernetică. Când verificăm însă trei măsuri concrete, precum monitorizare permanentă, plan de răspuns testat și exerciții regulate de securitate, procentul scade la 27%. 39 de organizații considerate „mature" nu îndeplinesc simultan aceste trei criterii. Diferența dintre cele două cifre e toată povestea: a instala soluții de securitate și a scrie proceduri nu e același lucru cu a ști că funcționează. Asta se află doar înainte de un incident real, nu în timpul lui. Radiografia securității cibernetice în România 2026: 200+ respondenți, 32 de întrebări. Descarcă raportul complet👇
- ControlMonkeySince 21 Sept 2026
Recovery is not something enterprise teams can leave to assumptions. ControlMonkey helps organizations make critical cloud and SaaS configurations recoverable - with visibility into what’s protected, what can be restored, and where gaps remain. Trusted by teams at Block, Veolia, Comcast, Intel, and more.
- ExeinSince 20 Sept 2026
We’ve spent years learning how machines behave and how to protect them. With $270m in new funding, we’re taking that work further through global expansion and a foundation model for Physical AI security, trained on telemetry generated through Exein technology across over two billion devices.
- GeoComplySince 21 Sept 2026
IDComply clears real UK players in seconds and stops the accounts built to drain your offer. When Dabble launched in the UK, almost 2,000 accounts traced back to a single cluster of reset devices and emulators. IDComply caught them at registration, before they could cost the business. Real players moved straight through. At registration, fraud passes every identity check you run. At scale, it just looks like a good week. IDComply exposes what those checks can't: the emulators, the reset devices, and the dozens of accounts running off one machine. See what it can catch in your sign-up flow: https://lnkd.in/daMiFpsd
- CyberVadisSince 22 Sept 2026
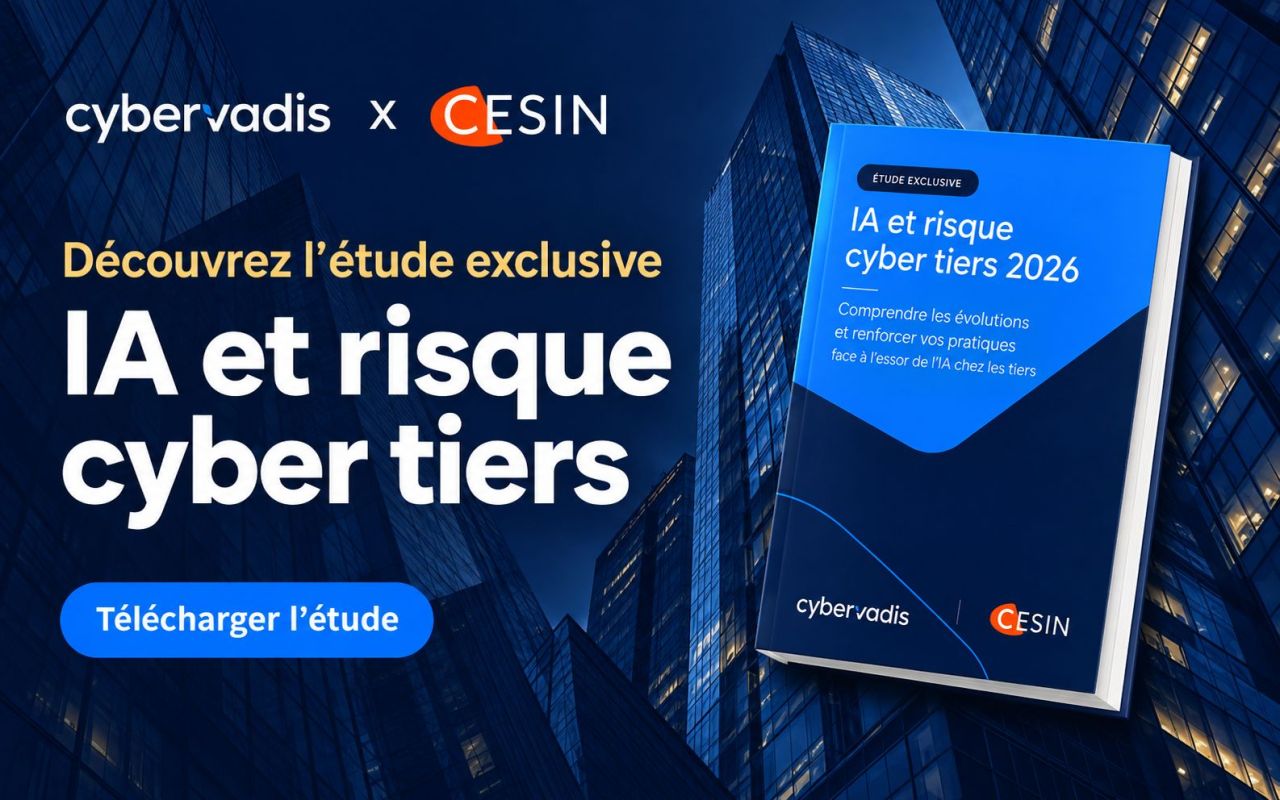
Vos fournisseurs utilisent l'IA générative. La question n'est plus "si", mais "comment" et surtout, "en avez-vous pleinement conscience ?" 💡 Chez CyberVadis, j'échange quotidiennement avec les grands groupes français sur la sécurisation de leur chaîne de valeur. Aujourd'hui, nous dévoilons avec le CESIN notre dernière étude exclusive sur la prise en compte de l'IA dans le risque cyber tiers (TPCRM). Le constat est sans appel : si les processus TPRM se consolident, la couche IA n'y est pas encore intégrée de manière structurée. Vous gérez probablement un risque IA tiers sans les outils pour le mesurer. Voici 4 "Key Takeaways" de notre étude qui méritent toute votre attention : ✔️ L'angle mort IA : 83 % des RSSI n'ont pas couvert le risque IA de leurs tiers dans leur dispositif. ✔️ Le déclaratif ne suffit plus : 65 % des tiers affirment tenir un inventaire de leurs outils IA, 4 % le prouvent. ✔️ Des contrôles à ajouter, pas un dispositif à refondre : les contrôles IA à vérifier dès votre prochaine évaluation. ✔️ Trois priorités pour agir : cartographie, clauses contractuelles et gouvernance du risque IA tiers. La bonne nouvelle ? Intégrer le risque IA ne demande pas une refonte totale de vos dispositifs, mais des mises à jour ciblées. Pour décrypter ensemble ces résultats et partager les leviers d'action concrets pour sécuriser vos écosystèmes, nous organisons un webinar de présentation exclusif : 📅 Rendez-vous le 2 octobre à 11h15 👉 Lien d'inscription : https://lnkd.in/en6wq22w Vous souhaitez recevoir l'étude complète en amont ou échanger sur la maturité TPRM de votre organisation ? Laissez un commentaire ou contactez-moi directement en message privé 📩 #CyberSecurity #TPRM #IntelligenceArtificielle #CyberVadis #CESIN #RiskManagement
- Beazley SecuritySince 23 Sept 2026
EM Protect continuously discovers and monitors your external attack surface, helping you uncover risks before attackers do. Available to eligible Beazley cyber policyholders at no cost.
- Beazley SecuritySince 23 Sept 2026
Activate EM Protect to identify exposed assets, prioritize critical vulnerabilities, and remediate what matters most. Available to eligible Beazley cyber policyholders at no cost.
- CR GroupSince 22 Sept 2026
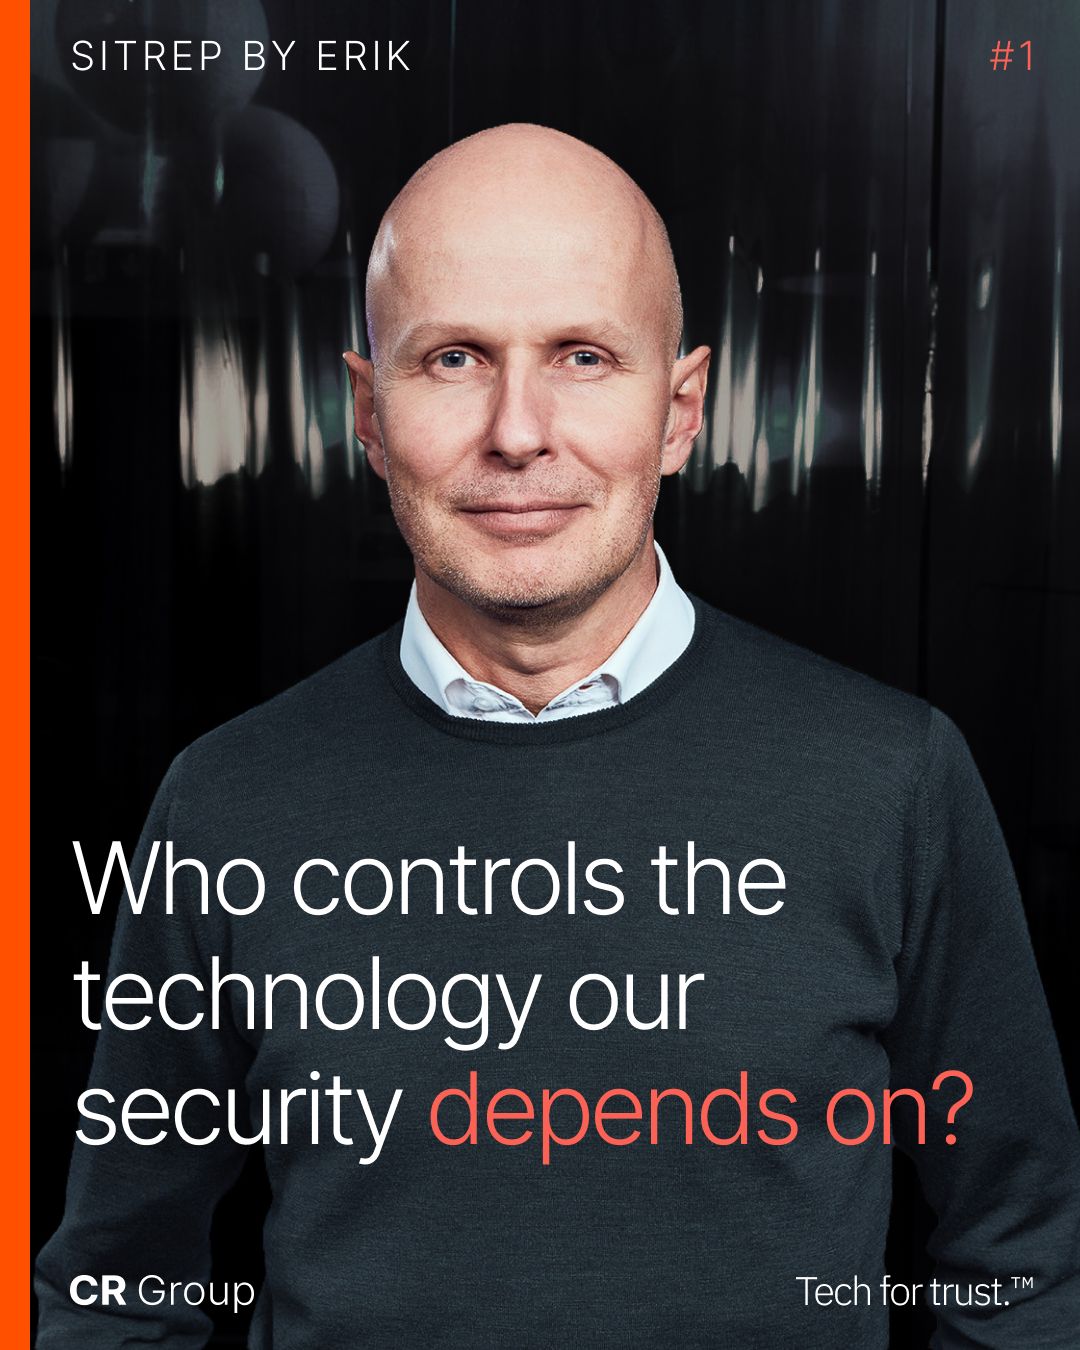
You might not have heard of CR Group . We build certified encryption and secure communications infrastructure for defense organisations, government agencies and critical infrastructure operators across Europe. Not a crowded cocktail party topic. The market we are working in are evolving. Europe is now looking much closer at the question: who controls the technology our security depends on? The answer we are arriving at is: it needs to be Europe. In my role as CEO of CR Group I bring a view on how to build an ecosystem of focused European tech leaders that are collectively stronger than they’d be alone. Tutus Data in Sweden and Sentyron in the Netherlands – certified, mission driven, and building the sovereign security infrastructure Europe needs. Over the coming months I’ll share how I think about this market and what I’m seeing from the inside. Not as an expert, but as a company builder paying close attention to current developments. Worth following if this space interests you.
- FiligranSince 23 Sept 2026
4 years ago, Julien and I founded Filigran to give a home to #OpenCTI, the open-source platform born inside a threat intelligence team, for other threat intelligence teams. The name comes from filigree, the craft of assembling fine threads into something precise and strong, and it still describes what this community does every day: pulling on a signal, patiently, until the structure appears. Today, what we build reaches far beyond threat intelligence, and the name has never fit better, as more and more threads come together around a single conviction: defense has to be proactive, and informed by the threat. None of it would exist without the analysts, engineers and contributors who have been building it with us, in open source, since before Filigran even existed. On October 15 in Paris, THREAD, our first conference, will bring this community together for a full day. I wanted it deeply rooted in our DNA: a day made for practitioners and for the leaders who rely on them, where the people who do the work are the ones on stage. Most of it happens in labs, workshops and roundtables, and part of our roadmap will be put to a vote, with a commitment on our side to build what comes out on top. Security leaders and practitioners from Accenture, Thales, Richemont, Dassault Systèmes, Centrica and many others will be with us, and more will be revealed in the coming days. THREAD takes place as Filigran turns 4. I have been looking forward to this day for a long time, and I cannot think of a better way to mark these four years than a day with the community, the customers and the partners who made them possible. It is the first edition of what we intend to make an annual gathering and, as always, only the beginning. So far, most of this community has met in threads, on Slack and GitHub. This time, we will be in the same room, and I hope you will be part of it. Come pull the thread with us! https://lnkd.in/esqa-wwx See you in Paris. #PullTheThread
- Code Blue CyberRecorded 8 Oct 2026
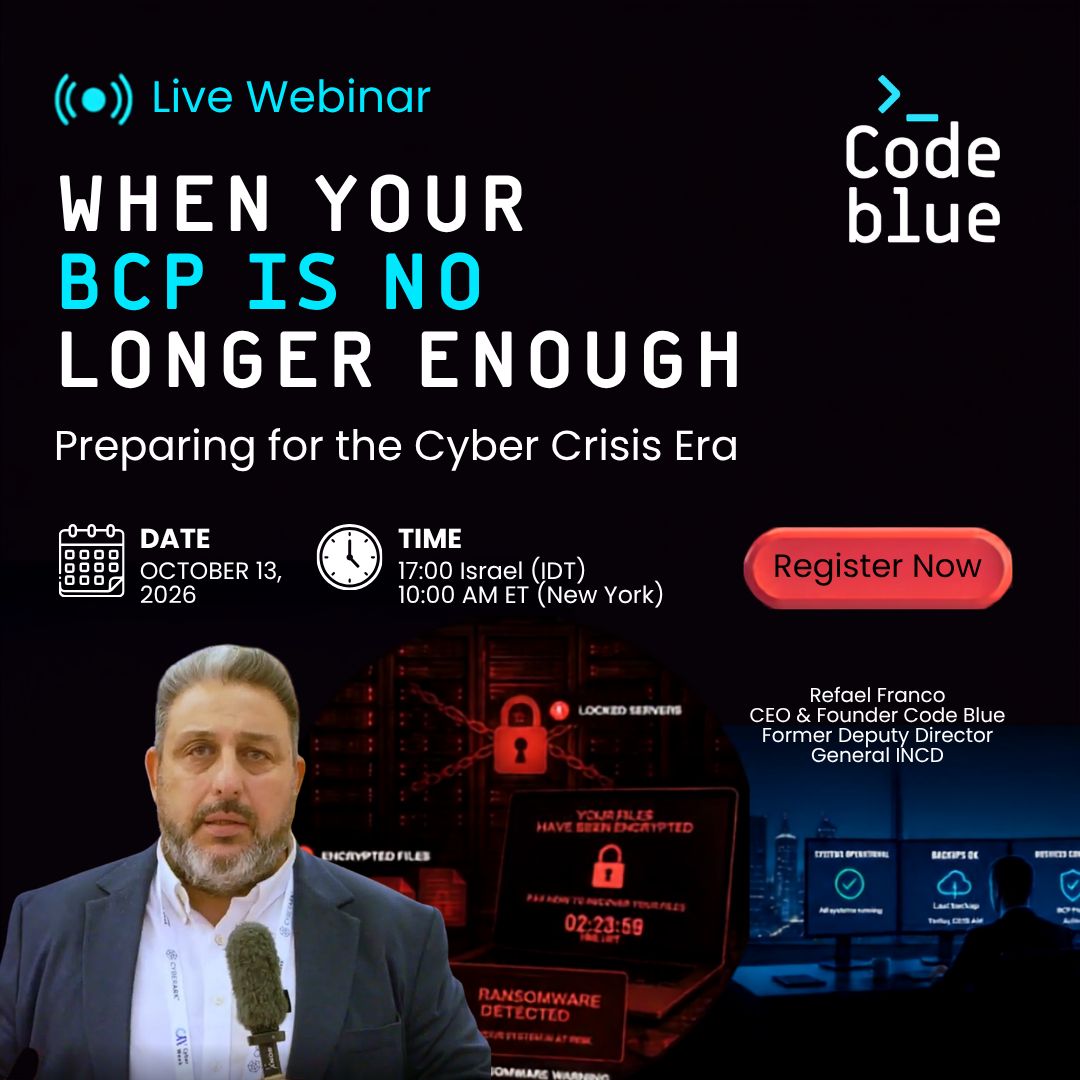
האם תוכנית ההמשכיות העסקית שלכם באמת מוכנה למציאות של משברי הסייבר של היום? תוכניות BCP מסורתיות לא נבנו להתמודד עם אירועי סייבר מתפתחים ודינמיים, שבהם כל החלטה עשויה להשפיע על הפעילות העסקית, המוניטין וקצב ההתאוששות של הארגון. הצטרפו לרפאל פרנקו, מנכ"ל ומייסד Code Blue ולשעבר המשנה לראש מערך הסייבר הלאומי, לוובינר ייחודי שבו נבחן כיצד ארגונים יכולים לעבור מתוכניות סטטיות למוכנות אמיתית לניהול משברי סייבר. במהלך המפגש נציג כיצד מערכת Blue Castle של קוד בלו מאפשרת לארגונים להיערך מראש, לנהל את המשבר בזמן אמת, ולשמור על שליטה תפעולית וקבלת החלטות אפקטיבית גם תחת לחץ
- DataDomeSince 23 Sept 2026
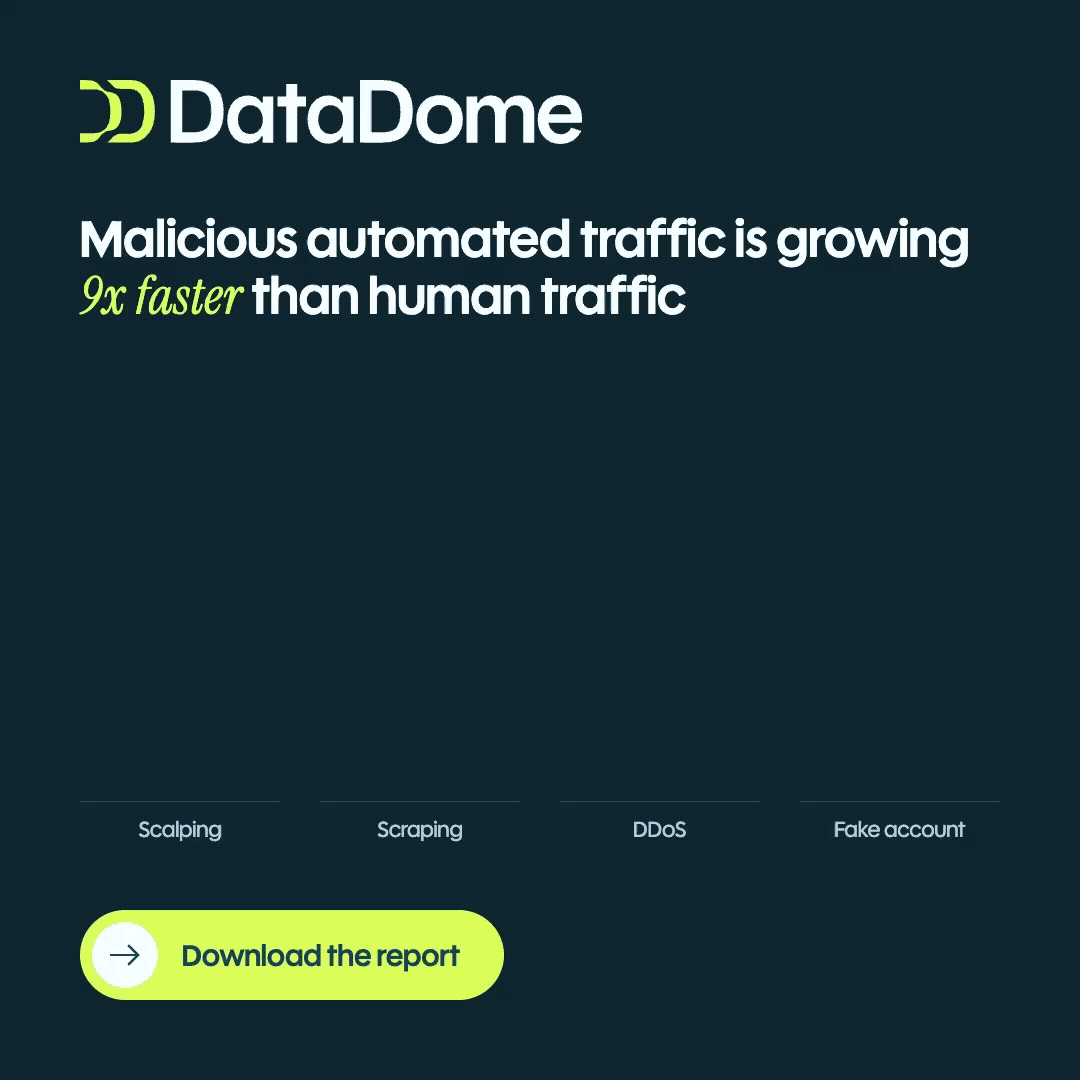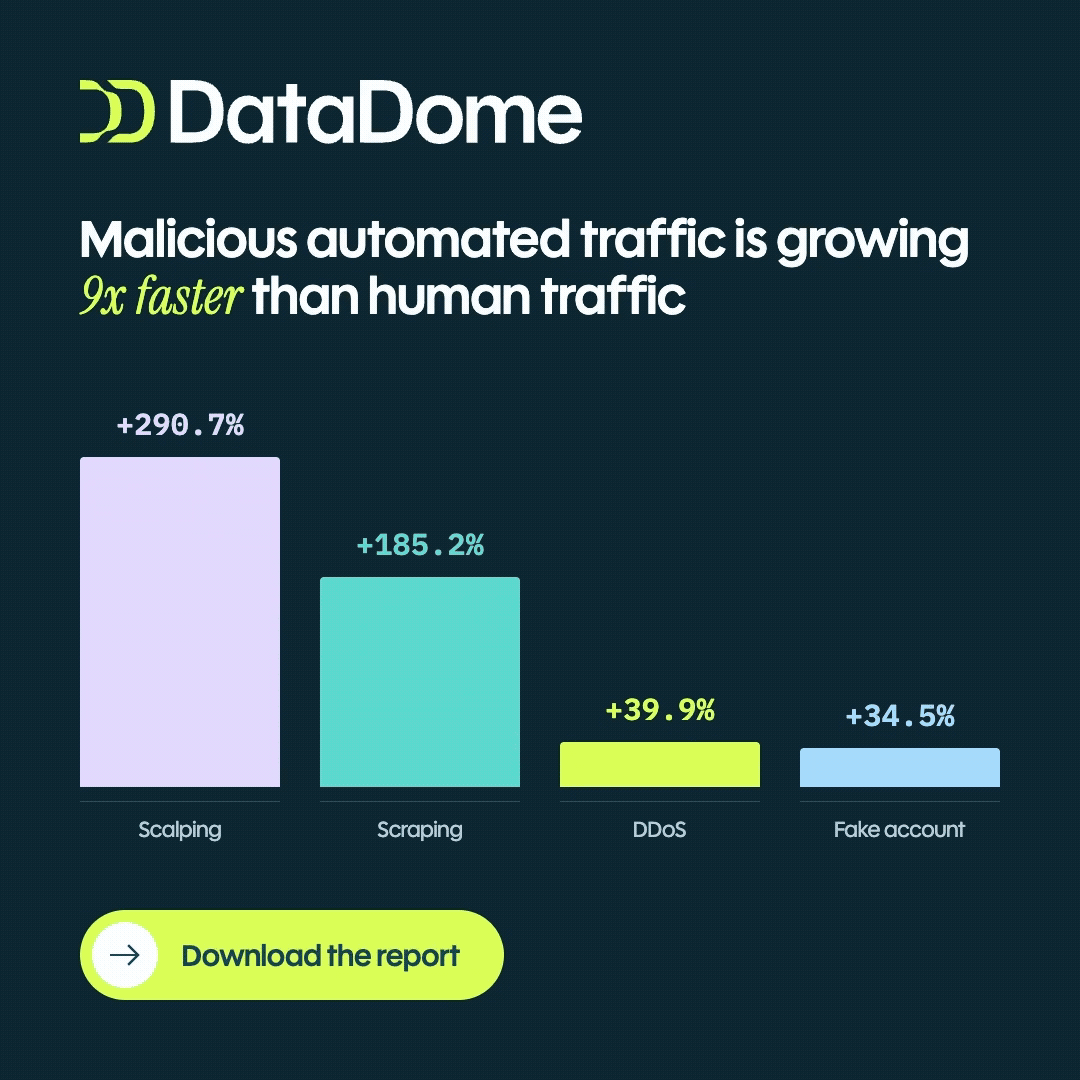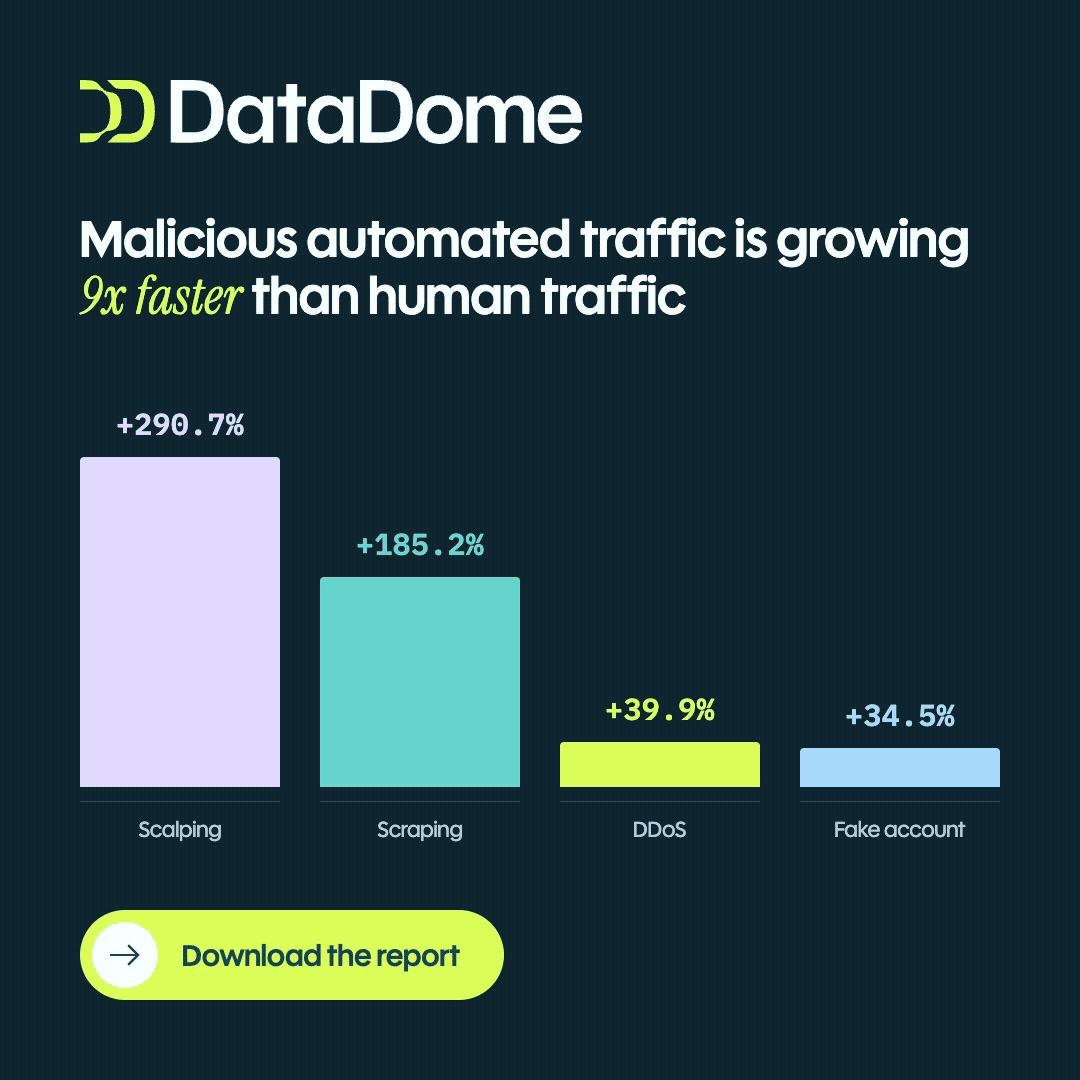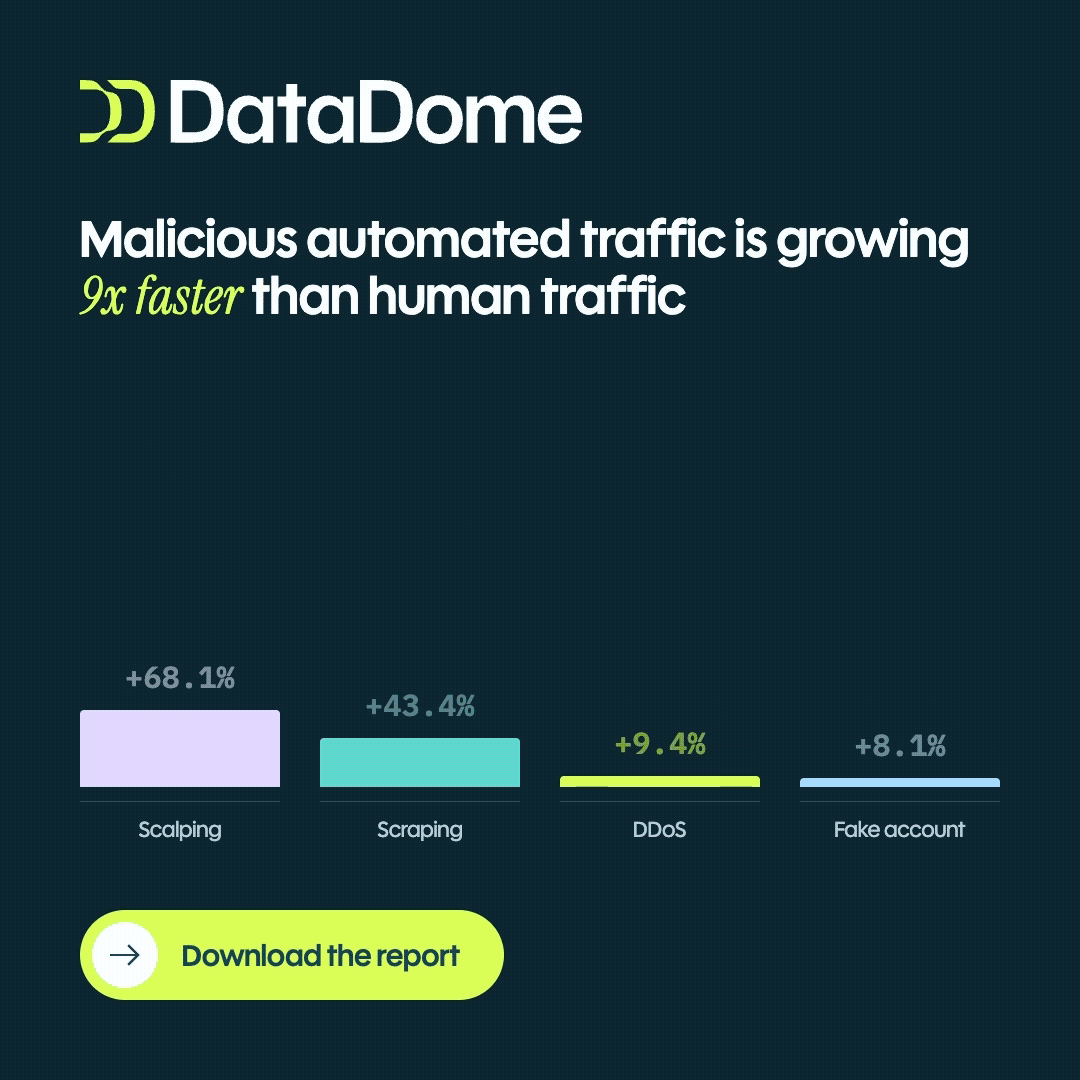
Our 2026 State of Bot and Agent Security Report is out, and one of the biggest takeaways is how fast malicious traffic is growing: 9x that of human traffic. The attacks themselves will be familiar to most security teams: scalping, scraping, DDoS, and fake account creation. What needs a closer look is the scale. Credit to Galileo, our threat research team, for doing the analysis across traffic from 20,000+ websites and 75k+ domains across our customer base. That gives us a view beyond any one company or sector. Most teams see only their own slice of the problem: their traffic, their incidents, and their customers. The value of this report is in connecting those slices and showing how automated threats are moving across industries and geographies. Read our report now: https://lnkd.in/dwpXV48c
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.