B2B ad examples
2 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- BlastWaveSince 1 Jul 2026
Inheriting an OT network as an IT CISO can feel like getting the keys to a beautiful old house… then finding 1940s wiring behind the walls. Air gaps aren’t enough. Patching can break production. Flat networks can turn one IT breach into a factory fire. So where do you start? In our latest newsletter, Tom Sego and Vince Zappula share the first step in securing inherited OT networks. Read it now ↓ #OTSecurity #NetworkCloaking #ZeroTrust #ITOTConvergence #CriticalInfrastructure
- BESECUREDSince 12 Aug 2026
Na našem zářijovém webináři se podíváme na 5 reálných bezpečnostních incidentů a technické nedostatky, které k nim vedly. 👉 Které technické zranitelnosti se nejčastěji objevují při bezpečnostních incidentech? 👉 Jaké chyby mohou útočníkům usnadnit průnik do systémů? 👉 Na co se zaměřit při kontrole vlastní infrastruktury? 👉 Jak odhalit slabá místa dříve, než způsobí bezpečnostní incident? O zkušenosti z reálných auditů a bezpečnostních projektů se podělí Radim Trávníček Kdy: 11. 9. 2026 | 10:00–11:00 Registrace: https://lnkd.in/dd6-abJb
- Bundesdruckerei-GruppeSince 29 Sept 2026
KI in der Verwaltung muss sicher und nachvollziehbar sein. Dank viel Praxisbezug erfahren Sie, welcher Technologie Sie vertrauen können.
- Bundesdruckerei-GruppeSince 29 Sept 2026
Im praxisnahen Online-Seminar erfahren Sie, wie Sie vertrauenswürdige KI in Ihrer Behörde etablieren und wo der größte Mehrwert entsteht.
- BlastWaveSince 28 Jul 2026
Triton wasn’t built to steal data. It was built to disable the safety systems that stop industrial plants from exploding. The attack failed only because the malware made a mistake. The next one may not. In our latest newsletter, we reveal how the first cyberweapon purpose-built to kill almost worked—and how network cloaking, Zero Trust, and microsegmentation can stop its successor. Read it now ↓ #OTSecurity #IndustrialCybersecurity #ZeroTrust #NetworkCloaking #CriticalInfrastructure
- CyberneticaSince 1 Oct 2026
🔐 With this many new EU regulations, tackling cybersecurity can quickly become a headache. Cybernetica is here to help. 💡 We offer an entire suite of security testing and reviews, compliance services, expert consultation, AI security services, as well as Entity Behavioural Analytics. 🌟 Our team of highly skilled experts is ready to work alongside your technical staff to help you approach cybersecurity in a proactive manner. 💬 Book your consultation below!
- CyberVadisSince 15 Sept 2026
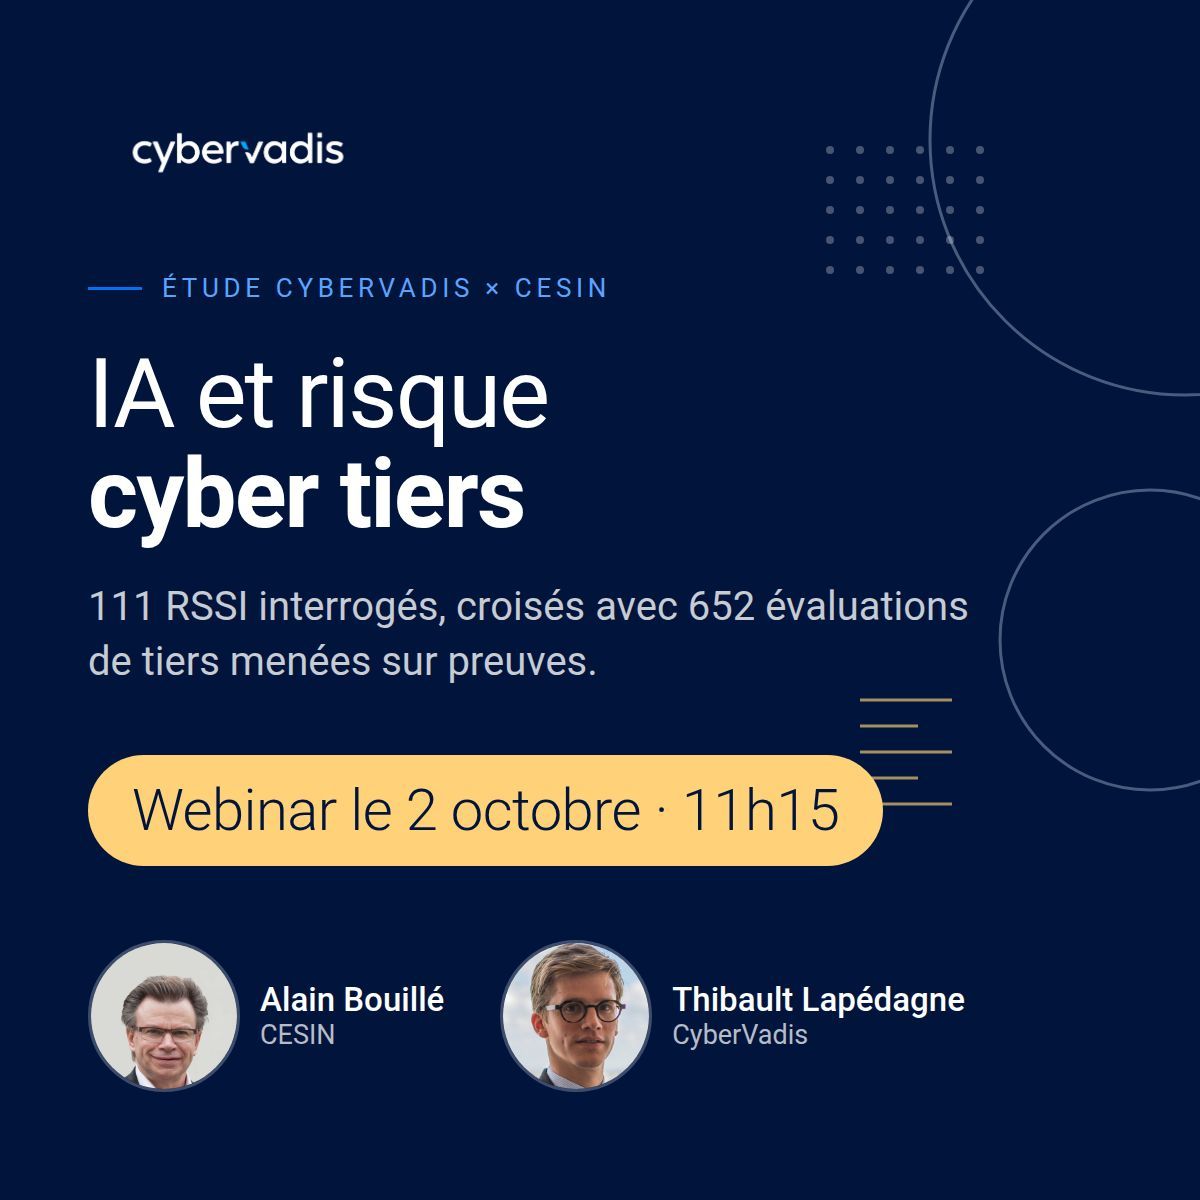
83 % des RSSI n’ont pas encore couvert le risque IA de leurs tiers. Et vous ? CyberVadis et le CESIN ont croisé les réponses de 111 RSSI avec 652 évaluations de tiers menées sur preuves. 📅 Le 2 octobre à 11h15, découvrez les écarts entre perception et réalité — et 3 priorités concrètes pour agir. 👉 Inscrivez-vous au webinar.
- Centro Nacional de Cibersegurança (CNCS) - Portuguese National Cybersecurity CentreSince 15 Sept 2026
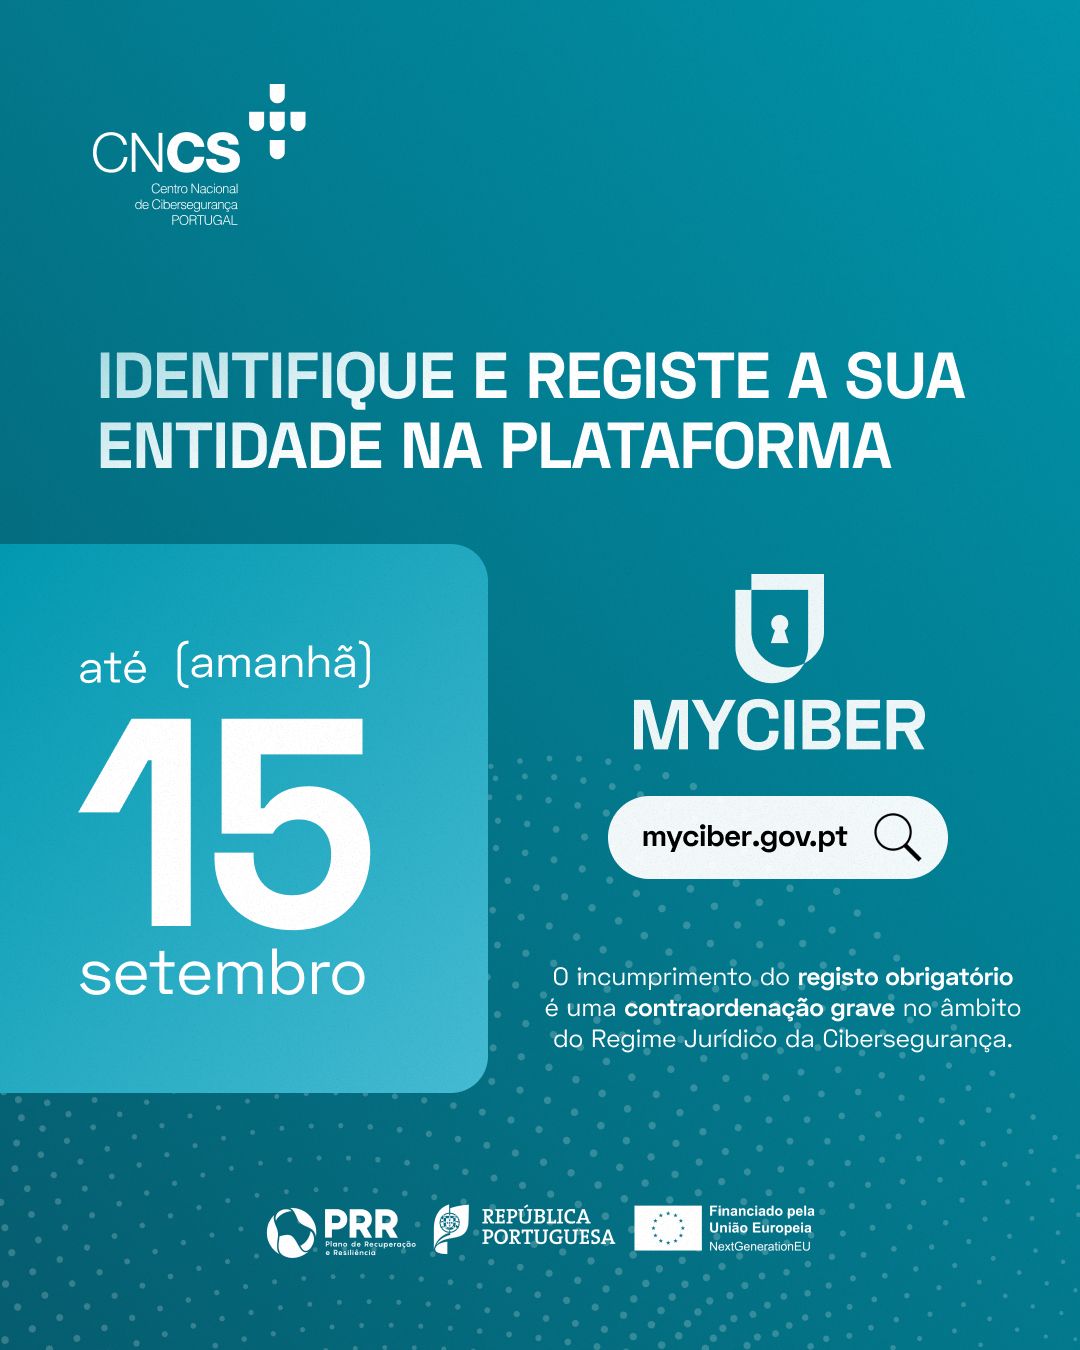
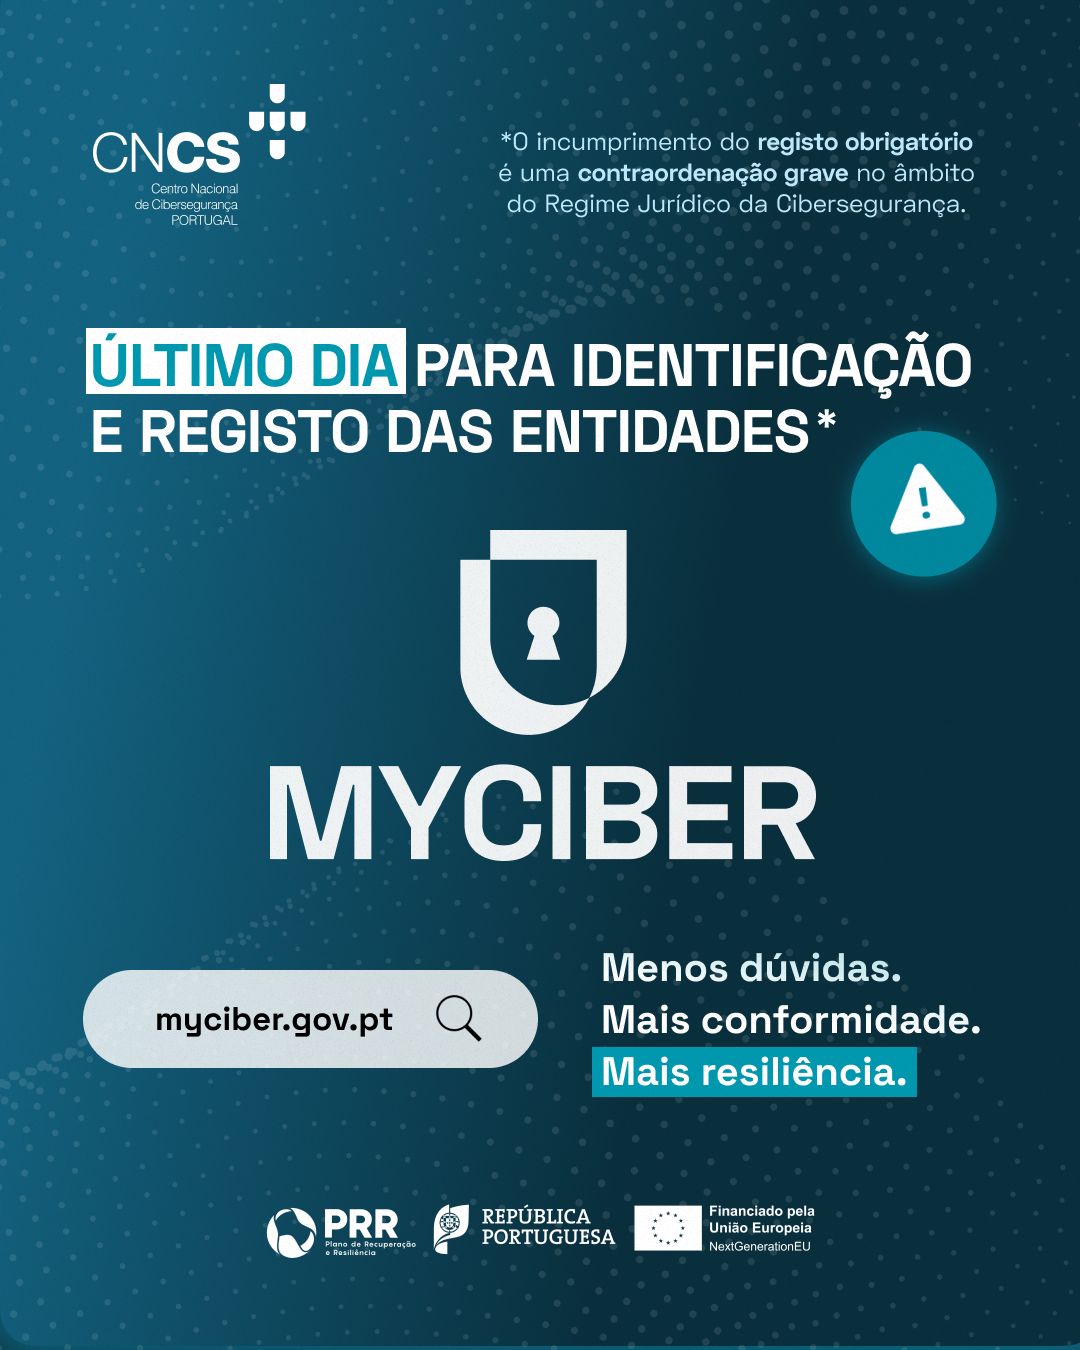
🚨 Termina amanhã o prazo final a que estão obrigadas as entidades abrangidas no artigo 3.º do Regime Jurídico da Cibersegurança, para cumprirem a sua obrigação de autoidentificação e registo na Plataforma MyCiber. Este é o primeiro passo para garantir o processo de qualificação das entidades e evitar o seu incumprimento, punível com coima. Para além dos setores já abrangidos pelo anterior regime, o novo enquadramento legal passou também a abranger setores como a gestão de serviços de tecnologias da informação ou comunicação, águas residuais, espaço, indústria transformadora, serviços postais e de estafeta, gestão de resíduos, produção, fabrico e distribuição de produtos químicos, produção, transformação e distribuição de produtos alimentares, prestação de serviços digitais e investigação. ⚠️ O processo de registo não constitui uma tarefa técnica exclusiva dos serviços de informática. O registo apenas pode ser realizado pelo representante legal da entidade ou uma pessoa a quem tenham sido atribuídos poderes específicos para o efeito, que deve autenticar-se na plataforma através da Chave Móvel Digital ou do Cartão de Cidadão. 📌 A utilização do Sistema de Certificação de Atributos Profissionais (SCAP), quando disponível, pode simplificar o processo de validação dos poderes de representação. Antes de concluir o processo: ✅ Verifique se a sua entidade está abrangida ✅ Identifique corretamente o setor de atividade da entidade para efeitos de enquadramento nos Anexos I e II do Regime Jurídico da Cibersegurança ✅ Complete o registo e a autoidentificação ✅ Conheça as obrigações que lhe são aplicáveis 👉 https://myciber.gov.pt 🔗 Saiba mais: https://lnkd.in/dtEhu_fd A conformidade começa pela identificação. Não deixe esta obrigação legal para depois do prazo. 🔐 Mais do que uma obrigação legal, a cibersegurança é um investimento na resiliência, na confiança e na continuidade da atividade das organizações. #MyCiber #NIS2 #RecuperarPortugal #ConstruirOFuturo #PRR
- CoplaSince 15 Sept 2026
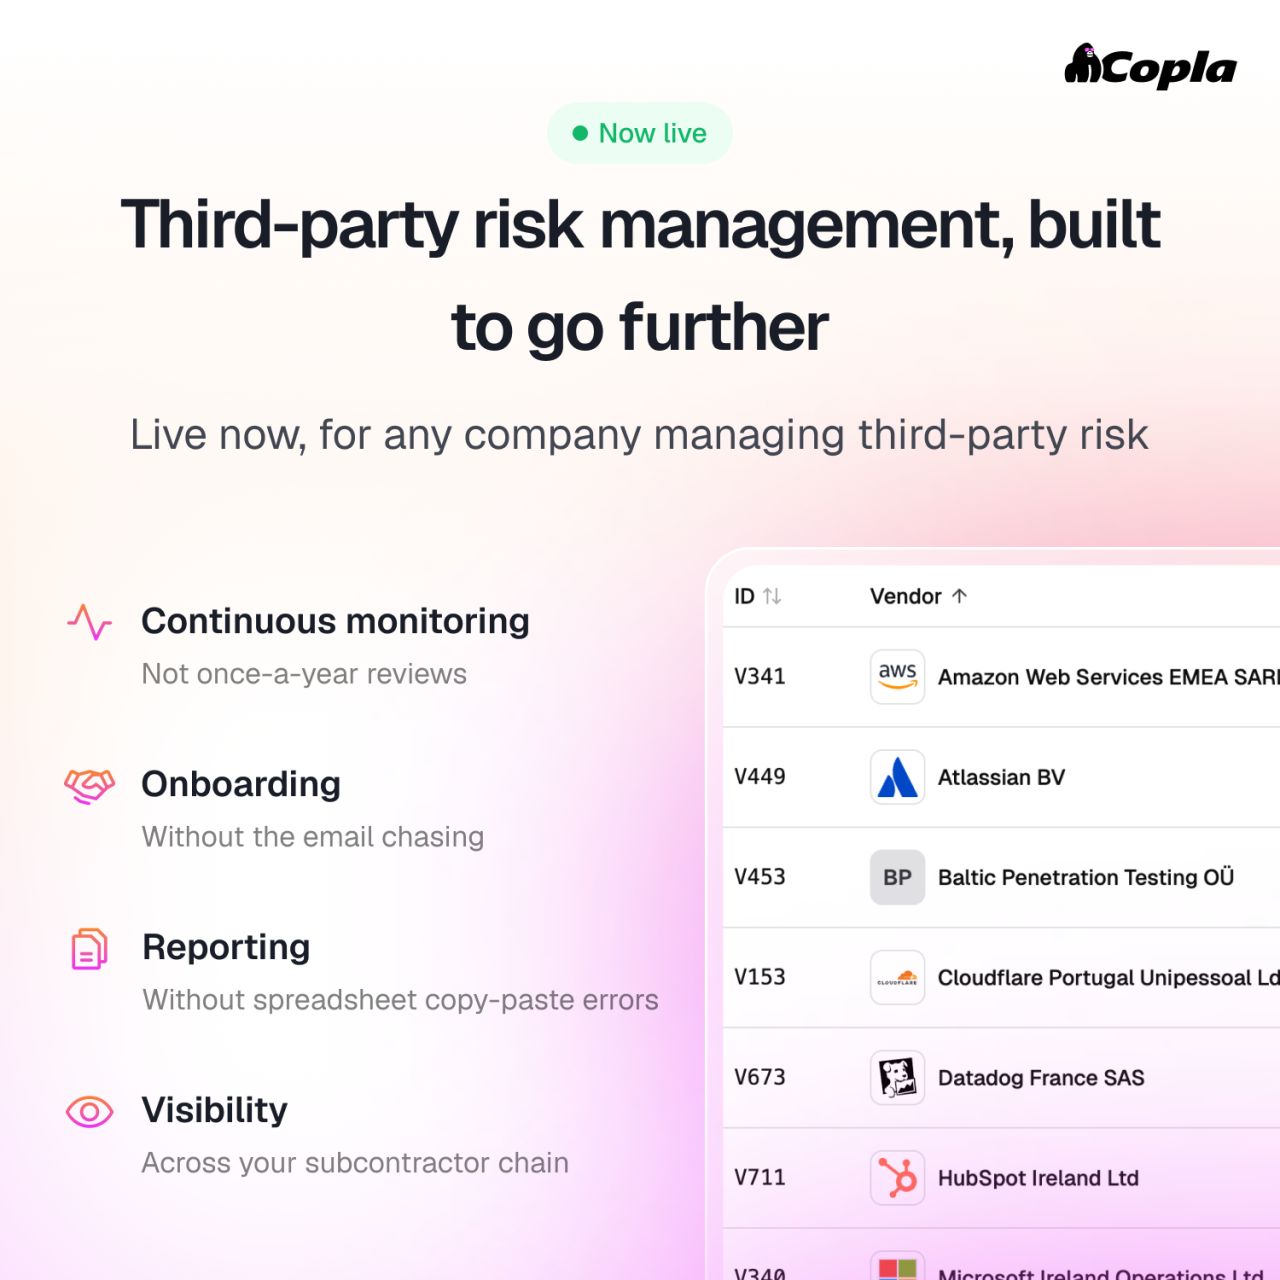
Today we're launching our third-party risk management software at Copla, and it's one of the products I'm proudest of this year. It covers ICT third-party risk under DORA, and goes further. It's live now, for any company managing vendor relationships. If your process still runs on spreadsheets, book a meeting with me and let’s talk about how Copla’s TPRM software can improve your processes: https://lnkd.in/dHF9SeEr
- CyCognitoSince 15 Sept 2026
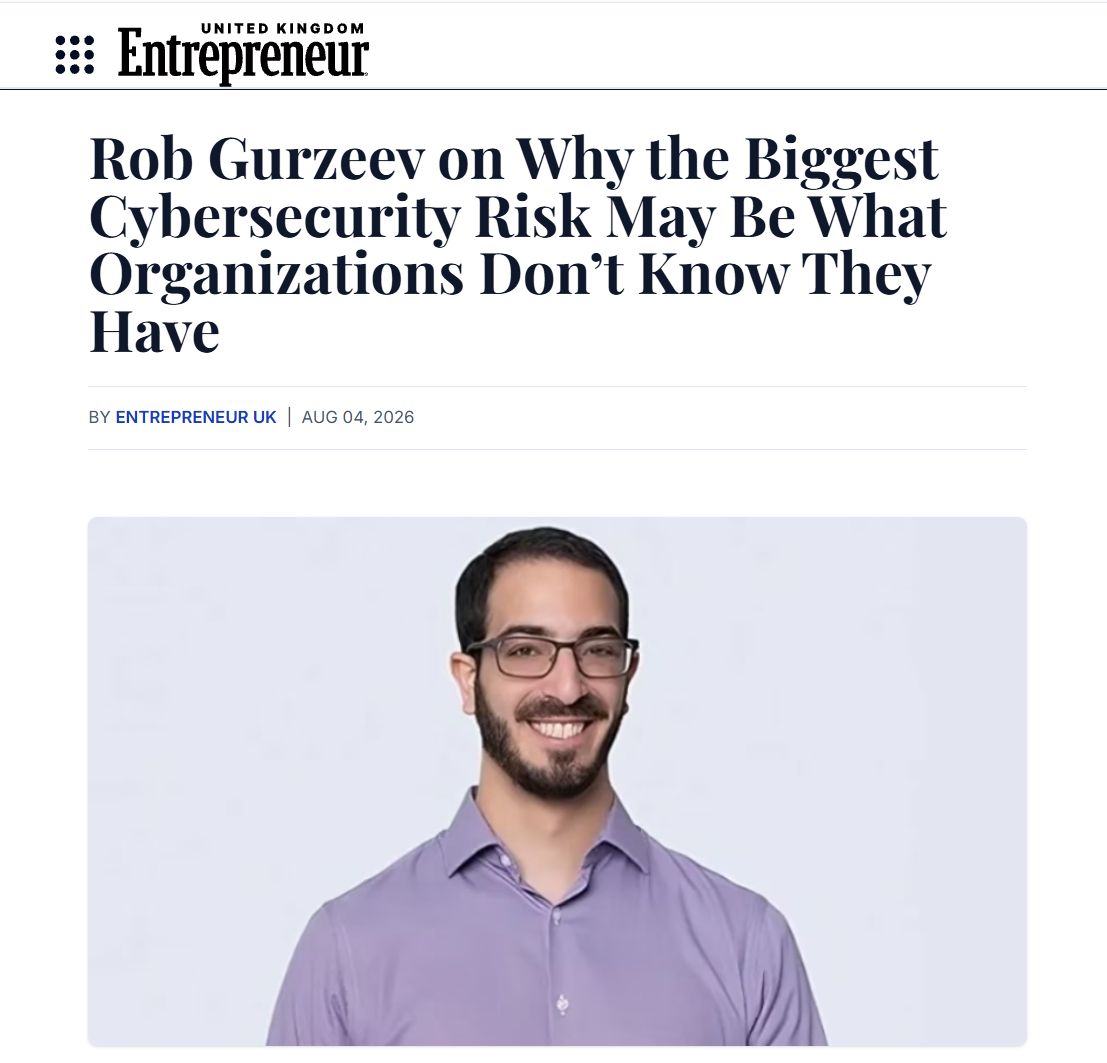
Big thanks to Entrepreneur Magazine for this conversation with our CEO Rob N. Gurzeev, about dark corners in which risk accumulates. Bottom line: the assets that were never on your list are the ones attackers get in through, and AI is creating more of them every day. Someone in finance can build an app with a prompt and put it on the internet. AI-written code reaches production without passing the secure pipelines built for human developers. Neither one arrives looking like a vulnerability with a patch, so neither one gets flagged. As Rob put it: "Guarding the front door while you leave the windows open is not a strategy." Read here to learn more: https://lnkd.in/dRhwqiz5
- Centro Nacional de Cibersegurança (CNCS) - Portuguese National Cybersecurity CentreSince 15 Sept 2026
⏳ Termina hoje o prazo para autoidentificação e registo na plataforma MyCiber As entidades abrangidas pelo artigo 3.º do Regime Jurídico da Cibersegurança devem cumprir a obrigação de autoidentificação e registo na plataforma MyCiber até ao final do dia de hoje, 15 de setembro. Antes de concluir o processo: ✅ Verifique se a sua entidade está abrangida ✅ Identifique corretamente o setor de atividade da entidade para efeitos de enquadramento nos Anexos I e II do Regime Jurídico da Cibersegurança ✅ Complete o registo e a autoidentificação ✅ Conheça as obrigações que lhe são aplicáveis 👉 https://myciber.gov.pt/ ⚠️ A autoidentificação e o registo constituem uma obrigação legal das entidades abrangidas pelo Regime Jurídico da Cibersegurança. 📌 Recorde-se igualmente que, com a publicação do Regulamento do Regime Jurídico da Cibersegurança, iniciou-se a contagem do prazo legal de 24 meses para a implementação das medidas de cibersegurança aplicáveis e para a produção de efeitos das obrigações associadas às entidades abrangidas. 🔗 Saiba mais: https://lnkd.in/eusgte24 Cumprir começa pela identificação. 🔐 A identificação e o registo são apenas o início de um caminho para uma maior resiliência e maturidade em cibersegurança. #MyCiber #NIS2 #RecuperarPortugal #ConstruirOFuturo #PRR
- CYBEROOSince 16 Sept 2026
Le identità non umane sono il nuovo obiettivo degli attaccanti. Ogni credenziale associata ad applicazioni, servizi o AI Agent rappresenta un potenziale punto di accesso se non viene gestita secondo i principi del least privilege e del monitoraggio continuo. Scopri come proteggerle con un approccio Zero Trust nel video. 👇
- BehaavSince 9 Sept 2026
At Cybersec Netherlands, Alicia and Nabil put their nerves to the test in the Behaav Jenga Challenge. Think you can handle the pressure better? Come visit us at stand E035, take on the challenge and compete for a free Cybersecurity Escape Experience. #cybersecurity #cybersec #securityawareness #behaav #jenga
- EchoSince 16 Sept 2026
Find out how long you really have before a CVE can be exploited - read our Mythos Readiness report.
- CYBEROOSince 16 Sept 2026
Le identità non umane sono una delle superfici d'attacco meno visibili nel cloud. Senza monitoraggio continuo e una corretta gestione delle credenziali, possono trasformarsi in un rischio concreto per la sicurezza aziendale. Scopri di più nel video. 👇
- CleafySince 17 Sept 2026
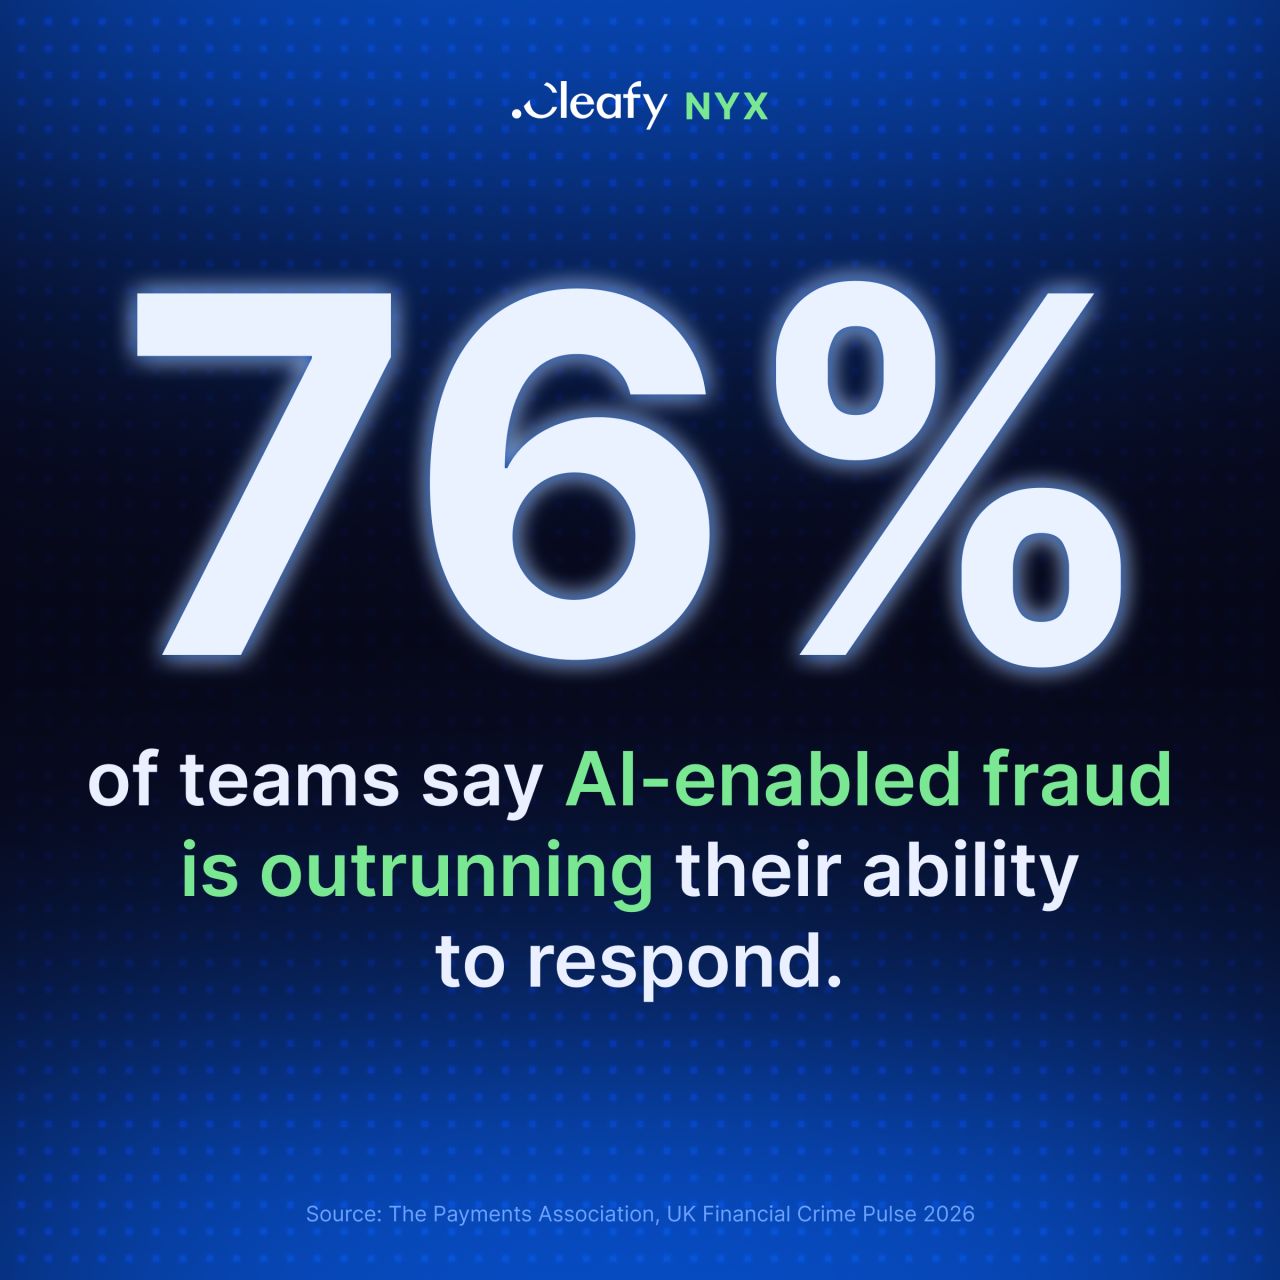
76% of teams say AI-enabled fraud is outrunning their ability to respond. Yours doesn't have to. Our new report maps the architecture that takes fraud operations from fragmented signals to governed, autonomous action.
- CleafySince 17 Sept 2026
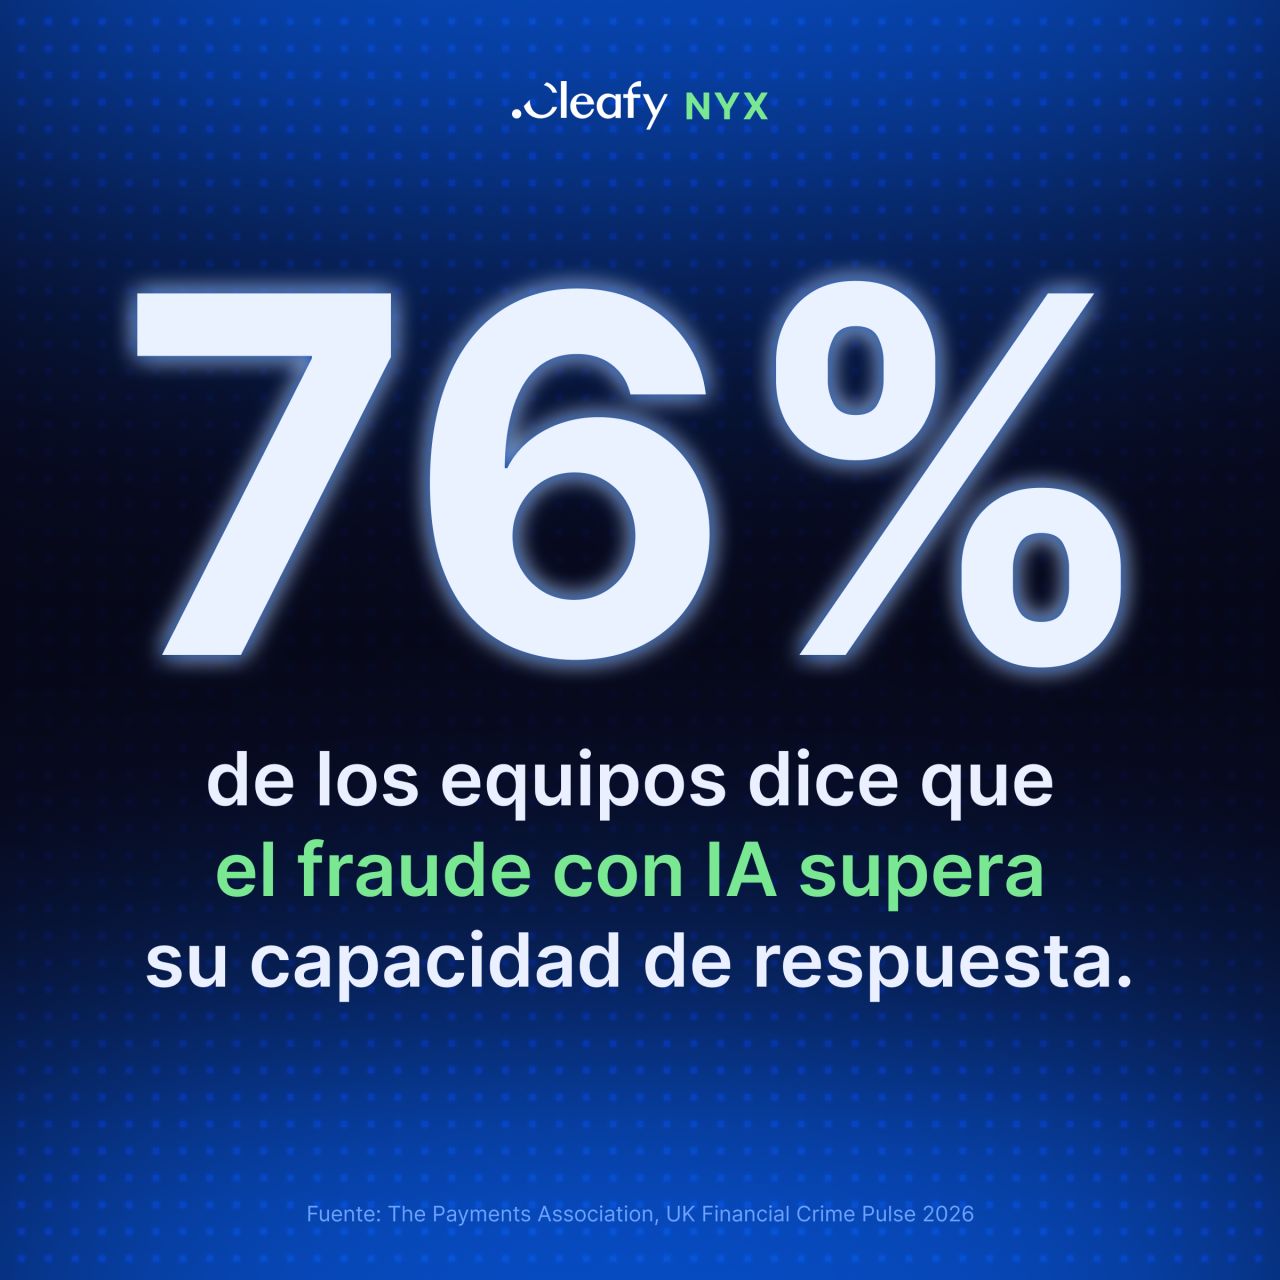
El 76% de los equipos afirma que el fraude impulsado por IA está superando su capacidad de respuesta. El tuyo no tiene por qué. Nuestro nuevo informe traza la arquitectura que lleva las operaciones de fraude de señales fragmentadas a una acción autónoma y gobernada.
- ESET Česká republikaSince 17 Sept 2026
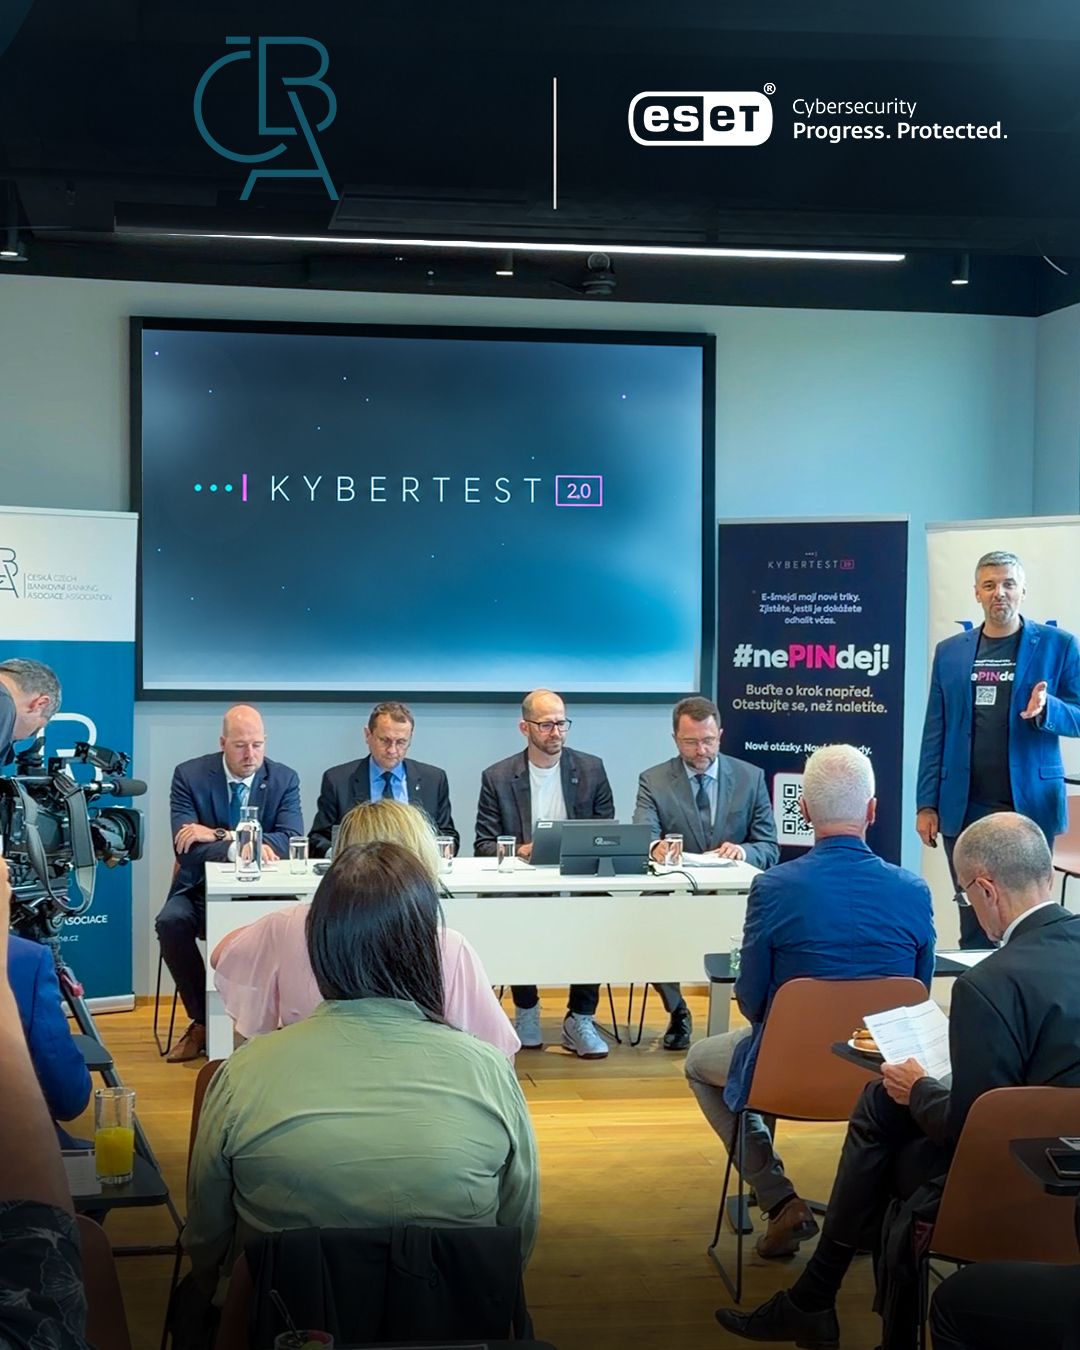
🤝 Spojujeme síly s Českou bankovní asociací. Stali jsme se technologickým partnerem České bankovní asociace a součástí kyberkampaně #nePINdej!. Společně chceme pomáhat lidem lépe rozpoznat online podvody a posilovat důvěru v digitální svět. Naši odborníci se zapojí do vzdělávacích aktivit, sdílení zkušeností i tvorby obsahu založeného na reálných hrozbách. Protože bezpečnější internet začíná informovanými uživateli. #ESET #nePINdej #Kyberbezpecnost
- CryptomathicSince 17 Sept 2026
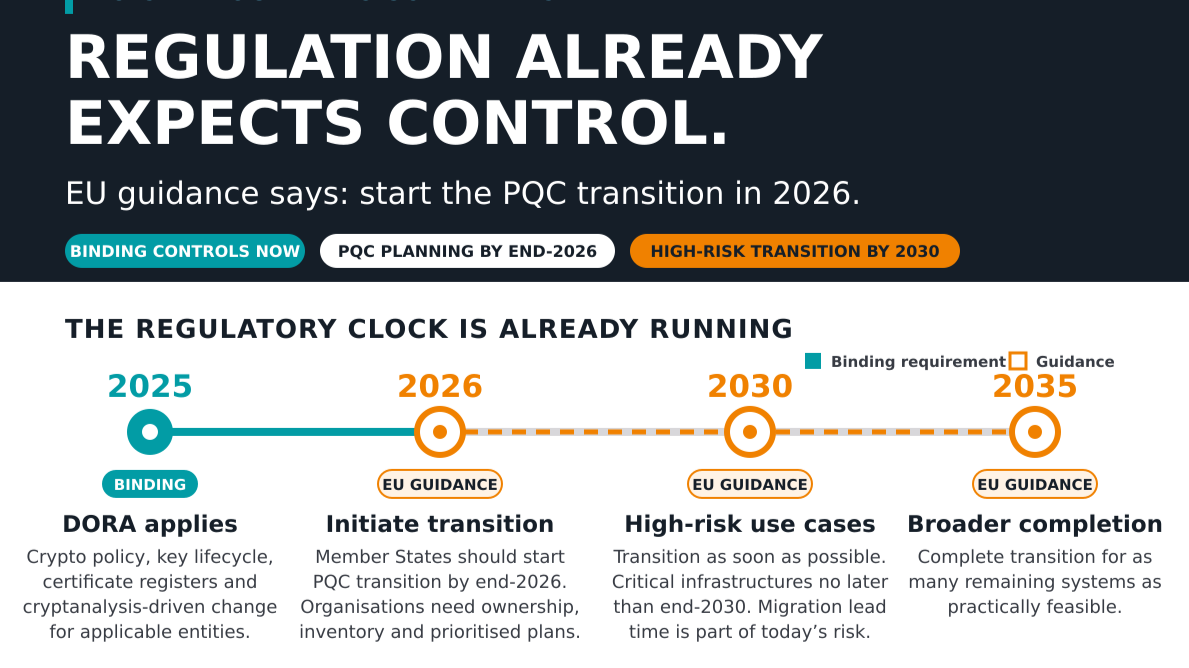
In this article https://lnkd.in/epmFkHTH I navigate the implicit and explicit cryptography and PQC requirements derived from EU regulation, DORA and NIS2 DORA and NIS2 do not mandate a particular PQC algorithm or technology platform. But they establish clear expectations around cryptographic policy, key lifecycle management, asset visibility, accountability, periodic review and the ability to respond to technological change. That means organisations should already be able to show: → where cryptography is used → who owns it → which critical services depend on it → how keys and certificates are controlled → how vulnerable technology can be replaced safely Cryptographic control (and PQC migration) is a present governance, evidence and operational-control challenge. Cryptomathic is fully positionned to address the cryptographic control challenge. #DORA #NIS2 #PQC #CryptoAgility #Cryptography #RiskManagement #Compliance Sudeep Venkatesh Anthony Da Ponte Laurent Leloup René Martin Guillaume Petipas Rob Purcell Herve M.
- Dragos, Inc.Since 26 Sept 2026
Your equipment will run for decades. Your OT security strategy should too. That means protecting what's running today while preparing for how your OT environment will evolve. Forrester ranked Dragos highest in Strategy, and Dragos was the only vendor to score a 5/5 in Vision. See Forrester's full assessment.
- BugHuntRecorded 8 Oct 2026
Uma das primeiras perguntas feitas durante a análise de um programa de bug bounty é: “Estamos autorizando terceiros a testar os sistemas da empresa?” A resposta é: não de forma ampla ou irrestrita. Um programa bem estruturado estabelece uma autorização específica e delimitada. Ele define: > Quais sistemas podem ser testados; > Quais atividades são permitidas; > Quais técnicas são proibidas; > Durante qual período as regras são válidas; > Como uma vulnerabilidade deve ser reportada. O pesquisador que segue essas regras atua dentro dos limites expressamente definidos pelo programa. Já qualquer atividade fora desse escopo não está autorizada e deve ser tratada conforme as regras do programa, os instrumentos contratuais e a legislação aplicável. Essa distinção é essencial. O programa não elimina limites. Ele os torna mais claros. Quando isso fica bem compreendido, a conversa deixa de ser sobre uma autorização genérica e passa a tratar de uma questão mais concreta: > Como definir um escopo seguro, controlado e adequado à realidade da empresa? É justamente essa clareza que transforma uma iniciativa de segurança em um processo de governança.
- ESET Česká republikaSince 17 Sept 2026
„To je pro velké korporáty, ne pro nás.“ Přesně tahle věta stojí za tím, proč řada českých firem zjistí, že spadá pod ZoKB, až na poslední chvíli. 🧐 Nový zákon o kybernetické bezpečnosti se může týkat i středních firem z oborů, které regulaci dosud neřešily. Příprava navíc není otázkou týdne – je potřeba zjistit, zda pod zákon spadáte, zmapovat povinnosti a připravit potřebná opatření. 🛡️ Dobrá zpráva? Máme pro vás praktického průvodce novým ZoKB, který si můžete zdarma stáhnout. Zjistíte v něm, koho se zákon týká, jaké povinnosti přináší a co budete muset řešit. 📘 Stáhněte si příručku zdarma: https://lnkd.in/dMgyT-iz
- BugHuntRecorded 8 Oct 2026
A IA aumentou muito a capacidade de identificar possíveis vulnerabilidades. E isso já está aparecendo nos programas de bug bounty. O problema é que identificar um comportamento suspeito não significa necessariamente ter encontrado uma vulnerabilidade. Tenho visto reports construídos a partir do output de uma ferramenta, mas sem validação suficiente do pesquisador. A ferramenta aponta um comportamento, gera uma hipótese e, às vezes, até ajuda a estruturar o report. Mas alguém ainda precisa entender o que está acontecendo, reproduzir o cenário, validar o impacto e explicar o problema com clareza. Quando essa etapa não acontece, o volume aumenta, mas a qualidade não acompanha. E isso fica evidente na triagem. Para mim, esse será um dos efeitos mais importantes da IA no bug bounty: quanto mais fácil ficar identificar possíveis falhas, mais importante será saber separar sinal de ruído. Não vejo a IA como um problema. Pelo contrário, ela já é uma ferramenta muito poderosa para pesquisa. Mas a validação continua sendo papel do pesquisador. A IA pode acelerar a descoberta. Entender se aquilo realmente é uma vulnerabilidade ainda exige conhecimento.
- CryptomathicSince 17 Sept 2026
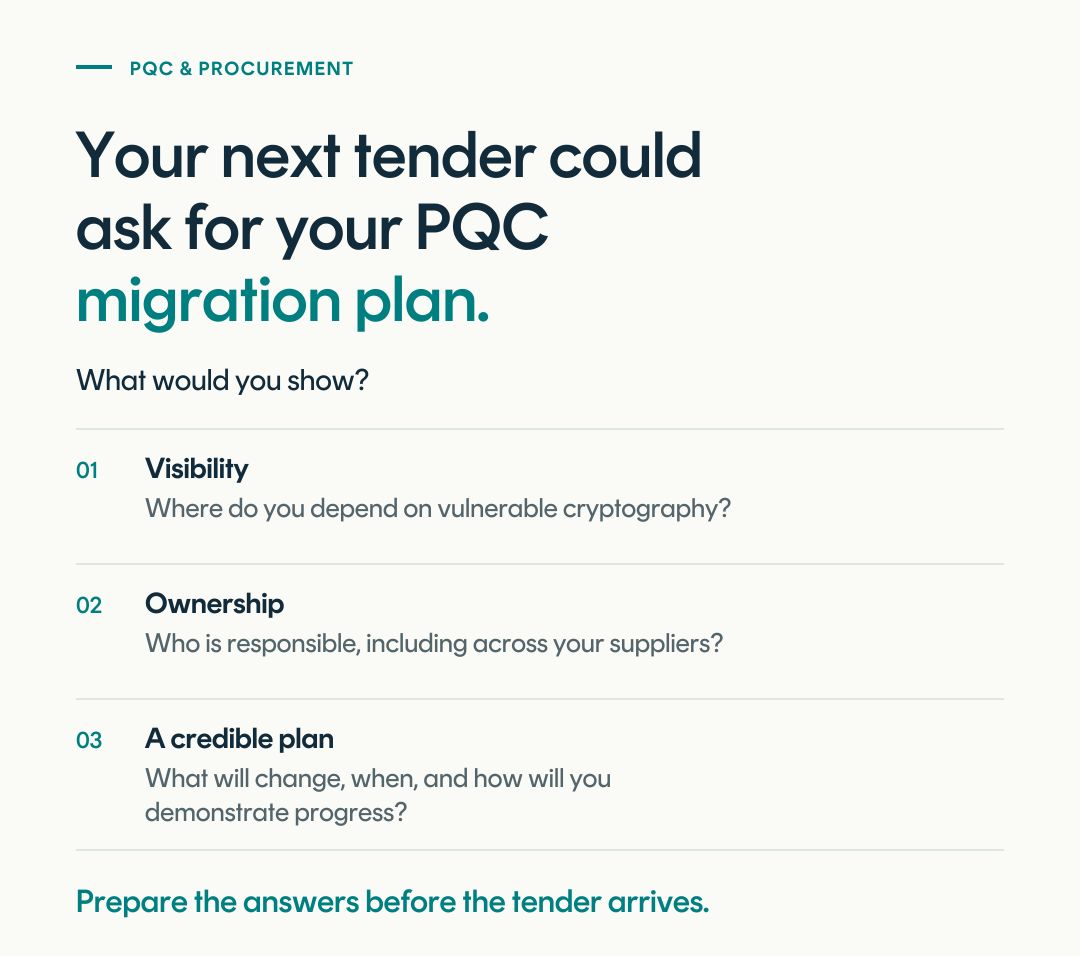
Your next customer security assessment could ask for your post-quantum migration plan. What would you show them? The G7 Cybersecurity Working Group has called for organisations across sectors to begin their transition to post-quantum cryptography as soon as possible. Its recommendations include incorporating PQC requirements into public procurement. This is policy guidance, not a binding mandate. But it gives suppliers a reason to prepare: customer requirements could arrive before a direct regulatory obligation does. As buyers assess their own readiness, they will need answers from the companies they depend on: • Where does your product or service rely on vulnerable cryptography? • Which changes depend on your suppliers? • Who owns the migration, and what is the plan? • What evidence of progress can you provide? Those answers take time to assemble, particularly when cryptography is spread across applications, infrastructure and third-party services. For anyone building the internal case to get started, procurement adds a commercial consideration. A credible migration plan could become part of what customers expect when deciding who to buy from. Read the G7 call to action in the comments.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.