B2B ad examples
1,817 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- Cato NetworksSince 24 Oct 2026
Your SD-WAN can optimize traffic at the branch. What about the rest of the journey? Cato's private backbone helps improve global performance and resiliency. See Cato in action.
- Duo SecuritySince 26 Oct 2026
With Duo Proximity Verification, remote attacks are stopped in their tracks.
- Duo SecuritySince 26 Oct 2026
Phishing attacks now target session cookies and bypass traditional MFA. See how to protect every stage of the identity lifecycle—not just app login.
- TenableSince 26 Oct 2026
Fix it or shut it down. That’s been the reality for security teams worldwide over the last four days. PHP2Shell is shaping up to be one of the most significant vulnerability events of 2026. Two flaws in PHP’s core memory allocator (CVE-2026-109618, CVE-2026-109619) enable unauthenticated remote code execution. Each is unreliable on its own. Chained, they’re reliable enough against default configurations that any PHP endpoint accepting file uploads becomes a target. At Tenable’s EXPOSURE event in May, I shared Mandiant’s time-to-exploit data: 63 days in 2018, 5 days in 2023, and 𝑚𝑖𝑛𝑢𝑠-7 days this year. The line has crossed zero. PHP2Shell is what that looks like in practice: ✴️ Amazon’s MadPot honeypots recorded active exploitation on Oct 17, four days before public disclosure. ✴️ The embargo leaked 18 hours early via a Hacker News post. ✴️ Cloudflare saw “thousands” of exploitation attempts within hours of the advisory, rising to “millions” after publication. ✴️ Nine government agencies across seven countries issued advisories or directives. Six ordered preemptive shutdowns of PHP-dependent services. The exposure is immense. More than 22M PHP server headers are visible online, and patch adoption is 2.8%. About 59% of exposed hosts run end-of-life versions with no official patch. For most of this surface, the patch cycle isn’t slow. 𝐈𝐭 𝐝𝐨𝐞𝐬𝐧’𝐭 𝐞𝐱𝐢𝐬𝐭. This is structurally different from past web vulnerabilities. The flaws were found with the help of frontier AI, and AI is compressing exploit development from weeks to days. Ironically, major cybercriminal forums (more here: https://lnkd.in/d_yUAxPs) took themselves offline within hours, because their own PHP infrastructure was at risk. Many organizations didn’t even know they ran PHP. Let alone how to patch or mitigate it. 𝐘𝐨𝐮 𝐜𝐚𝐧’𝐭 𝐬𝐞𝐜𝐮𝐫𝐞 𝐰𝐡𝐚𝐭 𝐲𝐨𝐮 𝐜𝐚𝐧’𝐭 𝐬𝐞𝐞. In 2026 that principle has a second half: 𝐲𝐨𝐮 𝐜𝐚𝐧’𝐭 𝐝𝐞𝐟𝐞𝐧𝐝 𝐚𝐭 𝐡𝐮𝐦𝐚𝐧 𝐬𝐩𝐞𝐞𝐝 𝐚𝐥𝐨𝐧𝐞. To borrow an analogy from forest firefighting, the six government agencies who shut down their services cleared the fuel the hard way. The better way is to clear it before the fire arrives. That means continuous discovery, inventory, reachability, and business context - at AI speed combined with human judgment. The same AI that found these flaws is the best tool defenders have to get ahead of the next ones. Tenable Research’s FAQ, updated as this develops: https://lnkd.in/dUaVyNUq #ExposureManagement #AI #PHP2Shell
- GuardeySince 22 Oct 2026
Een boete van €10 miljoen of 2% van de wereldwijde jaaromzet, als dat hoger is. Voor essentiële organisaties die onder de Cyberbeveiligingswet vallen, is dit bij bepaalde overtredingen geen theoretisch scenario. Cyberveiligheid is daarmee ook een verantwoordelijkheid op bestuursniveau. Alleen: beleid op papier maakt medewerkers nog niet cyberbewust. Guardey helpt je met doorlopende security awareness training. Medewerkers oefenen iedere week met digitale risico's en via rapportages volg je hun deelname en voortgang. Wil je zien hoe je dit binnen jouw zorgorganisatie aanpakt? Plan een demo en ontdek de mogelijkheden van Guardey.
- GuardeySince 22 Oct 2026
Een sterk spamfilter houdt veel verdachte mails tegen, maar een hergebruikt wachtwoord of een patiëntendossier bij de verkeerde ontvanger niet. Niet ieder digitaal risico begint met phishing. Daarom traint Guardey medewerkers met wekelijkse security awareness challenges over onder andere privacy, wachtwoordbeveiliging en online bedreigingen. Zo leren ze risico's herkennen die technische beveiliging niet altijd kan voorkomen. Wil je zien hoe je jouw medewerkers bewust maakt van deze risico's? Plan een demo en bekijk de interactieve trainingen van Guardey.
- FortanixSince 23 Oct 2026
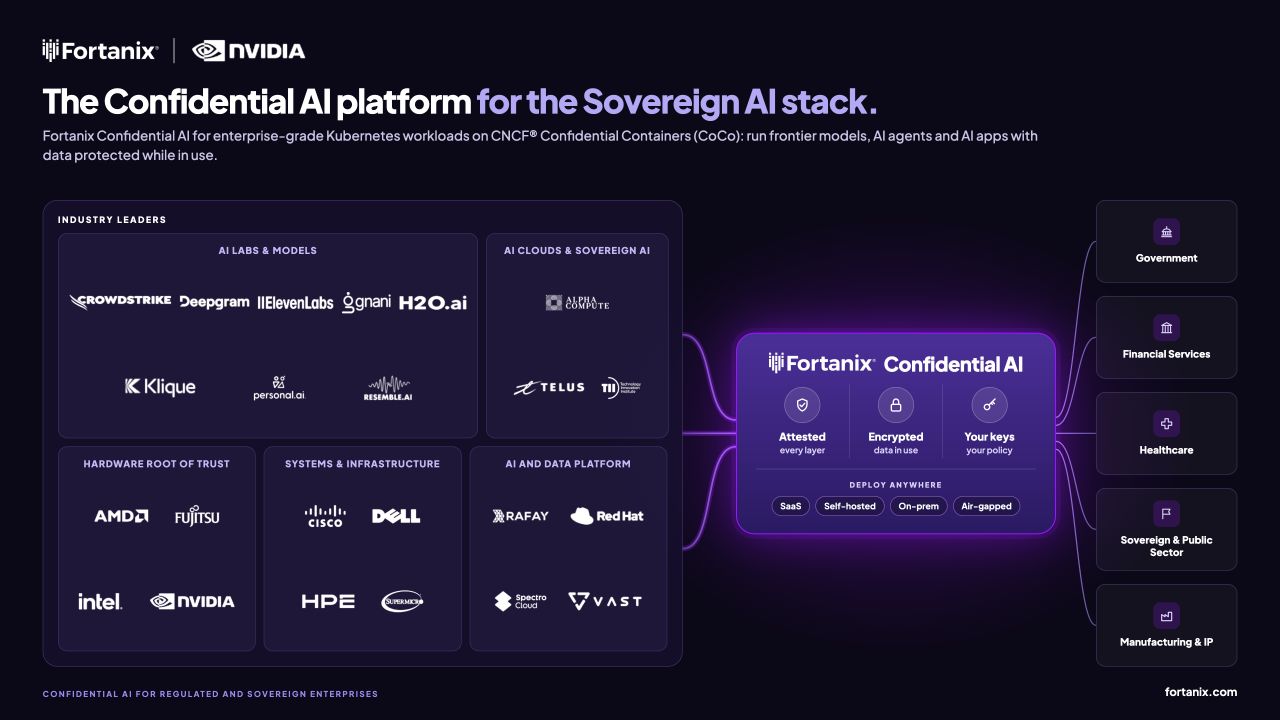
Confidential AI is now enterprise-grade on Kubernetes! Today, ahead of NVIDIA GTC Berlin, Fortanix announced Confidential AI for enterprise-grade Kubernetes workloads on Cloud Native Computing Foundation (CNCF) Confidential Containers (CoCo), available now. Containers are how the world ships AI. Now every container running a frontier model, an AI agent or an AI application can run inside a hardware-based Trusted Execution Environment, with data, models and agents protected while in use. Attestation is a process. Trust is an operation. That's the principle we built this on. And we're not doing it alone. Industry leaders NVIDIA, Alpha Compute, AMD, Cisco, Dell Technologies, CrowdStrike, Deepgram, ElevenLabs, Fujitsu, gnani.ai, H2O.ai, Hewlett Packard Enterprise, Intel, Klique, Personal AI, Rafay, Red Hat , Resemble AI, Spectro Cloud, Supermicro,Technology Innovation Institute, TELUS, VAST Data are supporting it. Confidential AI is where enterprise and sovereign AI go next, and Fortanix is leading the way. None of this happens without the Fortanix team. Months of relentless engineering went into making trust operational. Proud of every one of you. See it live at NVIDIA GTC Berlin, Booth 7017, Oct 20–22. Read the announcement: https://lnkd.in/gqS4uXNh #ConfidentialAI #ConfidentialComputing #Kubernetes #CNCF #SovereignAI #AISecurity #gtcberlin2026
- IncogniaSince 24 Oct 2026
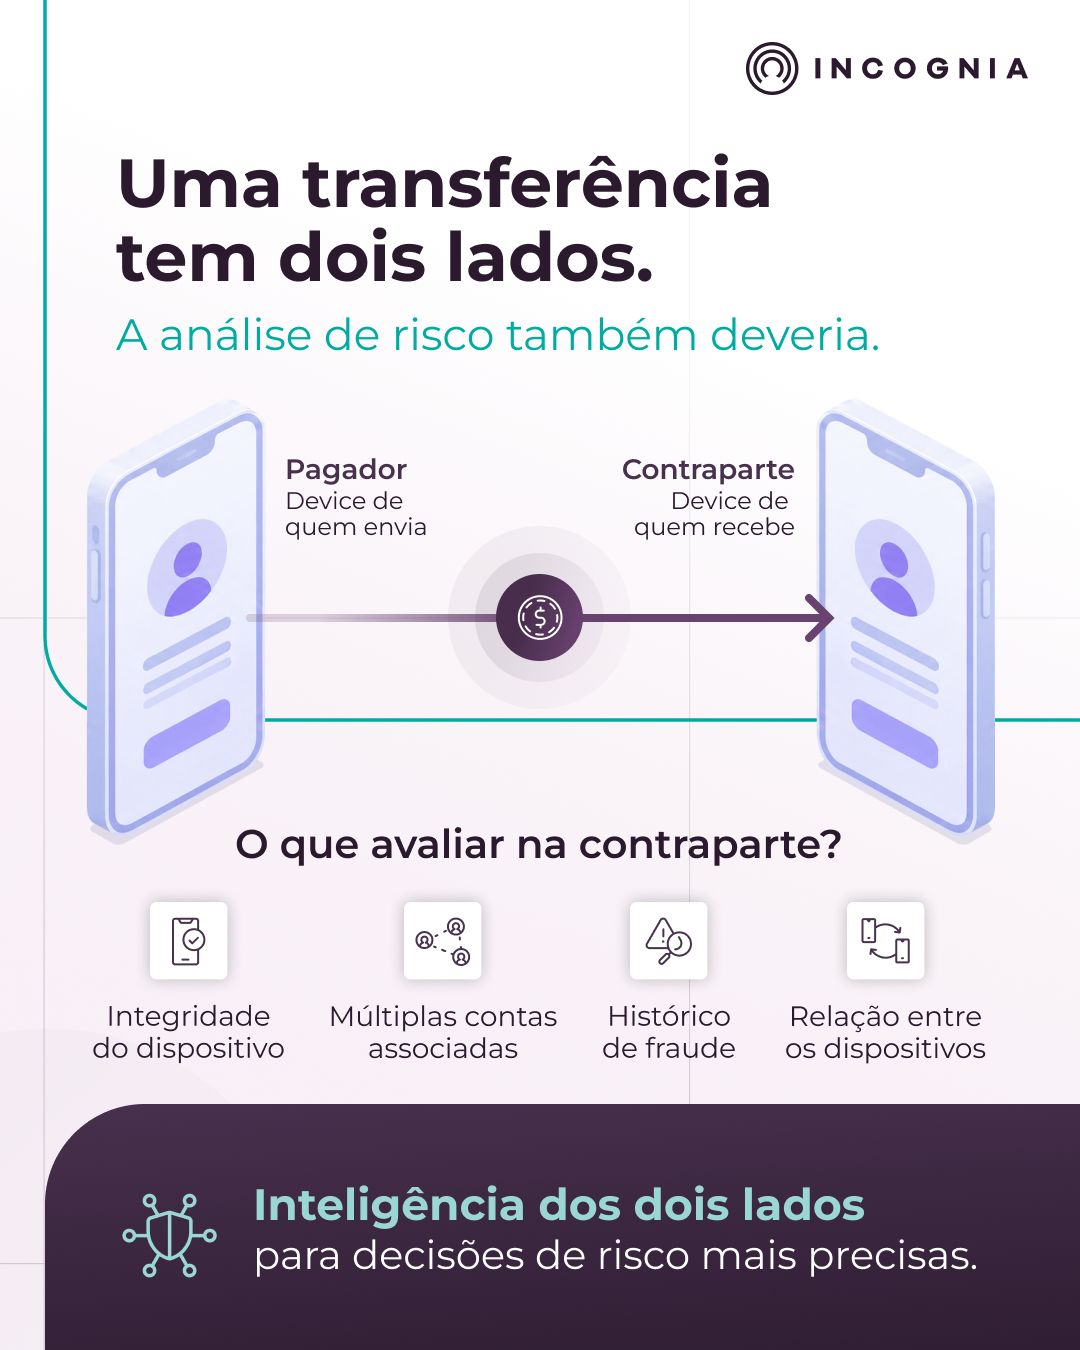
Quanto sabemos sobre quem está recebendo o dinheiro em uma transação financeira? Grande parte das análises de prevenção à fraude se concentra no pagador: seu dispositivo, localização, comportamento e histórico de transações. Essas informações são fundamentais, mas existe uma oportunidade importante de ampliar a análise de risco ao considerar também o dispositivo de quem recebe o dinheiro. Nos golpes de engenharia social, essa visão ganha ainda mais relevância. Afinal, o próprio cliente pode autorizar uma transferência para uma conta controlada por um fraudador. A inteligência do dispositivo da contraparte permite investigar situações que dificilmente seriam identificadas analisando apenas o pagador. Por exemplo, um dispositivo associado a diversas contas recebedoras pode indicar uma operação coordenada. Se esse mesmo dispositivo apresenta histórico de fraude, sinais de integridade comprometida ou comportamento sistemático, temos mais elementos para avaliar o risco daquela transferência. Outra variável interessante é a relação de localização entre as partes. Em uma análise sobre golpes de engenharia social, observamos que a incidência aumenta conforme cresce a distância entre pagador e recebedor, com uma elevação mais acentuada a partir de 200 km. É preciso considerar que a distância, isoladamente, não determina o risco. Uma transferência entre pessoas em cidades diferentes pode ser perfeitamente legítima. Mas, quando essa informação é analisada junto à reputação dos dispositivos, ao histórico das contas e às relações entre pagador e destinatário, conseguimos identificar padrões que antes poderiam passar despercebidos. Isso também permite investigar situações em que diferentes contas estão associadas ao mesmo dispositivo ou em que um recebedor concentra transações originadas de dispositivos com sinais de risco. Para bancos e fintechs, conhecer melhor a contraparte significa ter mais informações para identificar possíveis contas mulas, redes de fraude e operações coordenadas. A análise de risco de uma transferência fica mais completa quando considera os dispositivos envolvidos e a relação entre as duas partes da operação.
- IST AMERICASRecorded 27 Oct 2026
La banca del futuro no solo será digital. Será AI-native. Gracias a Revista Ekos por destacar esta perspectiva de IST AMERICAS en su espacio de Micro Noticias. ▶️ Mira la nota: https://lnkd.in/eEsDrRvF La inteligencia artificial está redefiniendo los productos financieros, pero también plantea un desafío estratégico: innovar sin comprometer la seguridad y la confianza. #ISTAMERICAS #BancaDigital #InteligenciaArtificial #Ciberseguridad
- IncogniaSince 23 Oct 2026
Com sua tecnologia patenteada, a 𝗜𝗻𝗰𝗼𝗴𝗻𝗶𝗮 está lançando uma solução para detectar golpes, baseado em conexões no mundo físico, mesmo em transferências autorizadas pelo próprio usuário📍👇 Essa é uma das aplicações da tecnologia da Incognia que mais me impressionam, especialmente agora com o lançamento do nosso 𝗥𝗲𝗮𝗹-𝗧𝗶𝗺𝗲 𝗦𝗰𝗮𝗺 𝗣𝗿𝗲𝘃𝗲𝗻𝘁𝗶𝗼𝗻. Um dos grandes desafios na prevenção de golpes de engenharia social é que, muitas vezes, quem realiza a transferência é a própria vítima. Ela está usando seu celular habitual, em um local conhecido, com suas credenciais legítimas e passando corretamente por todas as etapas de autenticação. Para o banco, praticamente tudo indica uma transação legítima. Só que, do outro lado, pode existir um fraudador orientando cada passo da vítima. E como identificar esse risco quando o comportamento digital parece normal? Uma das respostas está em entender a relação entre quem envia e quem recebe o dinheiro. Com o 𝗣𝗵𝘆𝘀𝗶𝗰𝗮𝗹 𝗦𝗼𝗰𝗶𝗮𝗹 𝗚𝗿𝗮𝗽𝗵, conseguimos identificar conexões entre pessoas a partir do histórico de localização de seus dispositivos. Essa análise utiliza o Trusted Locations, 𝘁𝗲𝗰𝗻𝗼𝗹𝗼𝗴𝗶𝗮 𝗽𝗮𝘁𝗲𝗻𝘁𝗲𝗮𝗱𝗮 𝗱𝗮 𝗜𝗻𝗰𝗼𝗴𝗻𝗶𝗮, para avaliar, por exemplo, se o pagador e o destinatário apresentam padrões de convivência ou proximidade recorrente no mundo físico, avaliando padrões de localização no nível de apartamento. Claro que a ausência dessa relação não significa fraude. Todos nós fazemos transferências legítimas para pessoas que nunca encontramos pessoalmente. Por isso, o contexto é tão importante. Podemos combinar essa informação com outros sinais, como a reputação e a integridade do dispositivo, a existência de uma chamada telefônica durante a transação, sinais de acesso remoto e o histórico de risco da conta de destino, incluindo possíveis conexões com contas laranja. Cada sinal contribui com uma parte da análise. Juntos, permitem identificar situações de risco que dificilmente seriam percebidas avaliando apenas a autenticação ou o comportamento do pagador. É justamente essa capacidade que estamos ampliando: conectar informações sobre dispositivos, comportamento, localização e relações entre pessoas para avaliar o risco de uma transferência em tempo real, 𝗶𝗻𝗰𝗹𝘂𝘀𝗶𝘃𝗲 𝗾𝘂𝗮𝗻𝗱𝗼 𝗲𝗹𝗮 𝗳𝗼𝗶 𝗮𝘂𝘁𝗼𝗿𝗶𝘇𝗮𝗱𝗮 𝗽𝗲𝗹𝗼 𝗽𝗿ó𝗽𝗿𝗶𝗼 𝗰𝗹𝗶𝗲𝗻𝘁𝗲. A instituição financeira recebe essa inteligência e decide como utilizá-la em suas políticas de prevenção. Sobre os resultados da aplicação da solução? → 79,2% das transações legítimas ocorreram entre usuários com uma relação no mundo físico. → 86,2% dos golpes reportados envolveram transações entre usuários sem relação no mundo físico. Conhecer o dispositivo é importante. Conhecer o comportamento e as relações entre as pessoas permite ir muito além na prevenção à fraude.
- IST AMERICASRecorded 27 Oct 2026
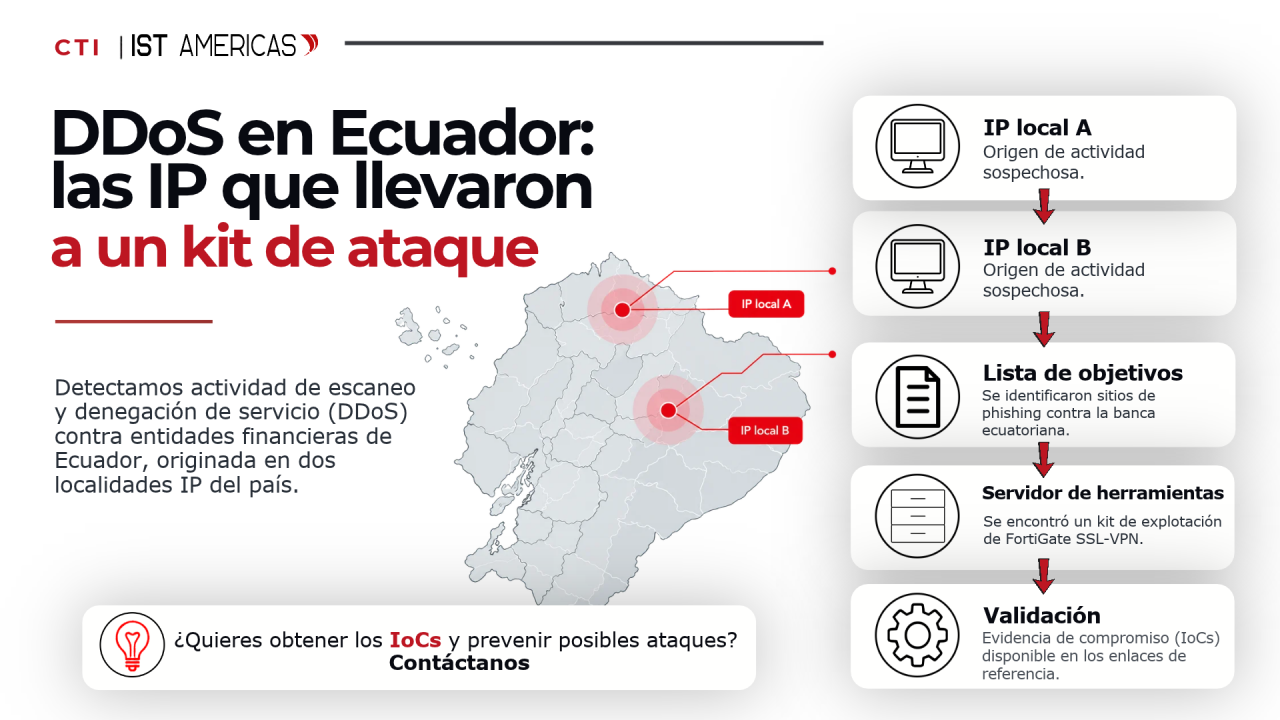
#BoletinCTI En esta edición analizamos actividad de DDoS y escaneo contra entidades financieras de Ecuador, los IoC identificados y cómo la Ciberinteligencia permite contextualizar estos indicadores para detectar posibles riesgos y tomar decisiones de seguridad con mayor precisión. 🔐 Conoce los hallazgos y descubre cómo utilizar esta inteligencia para fortalecer la prevención de posibles ataques. #ciberseguridad #ISTAmericas #TheThreatIntelligence #DDoS #Ecuador
- HuskeysRecorded 27 Oct 2026
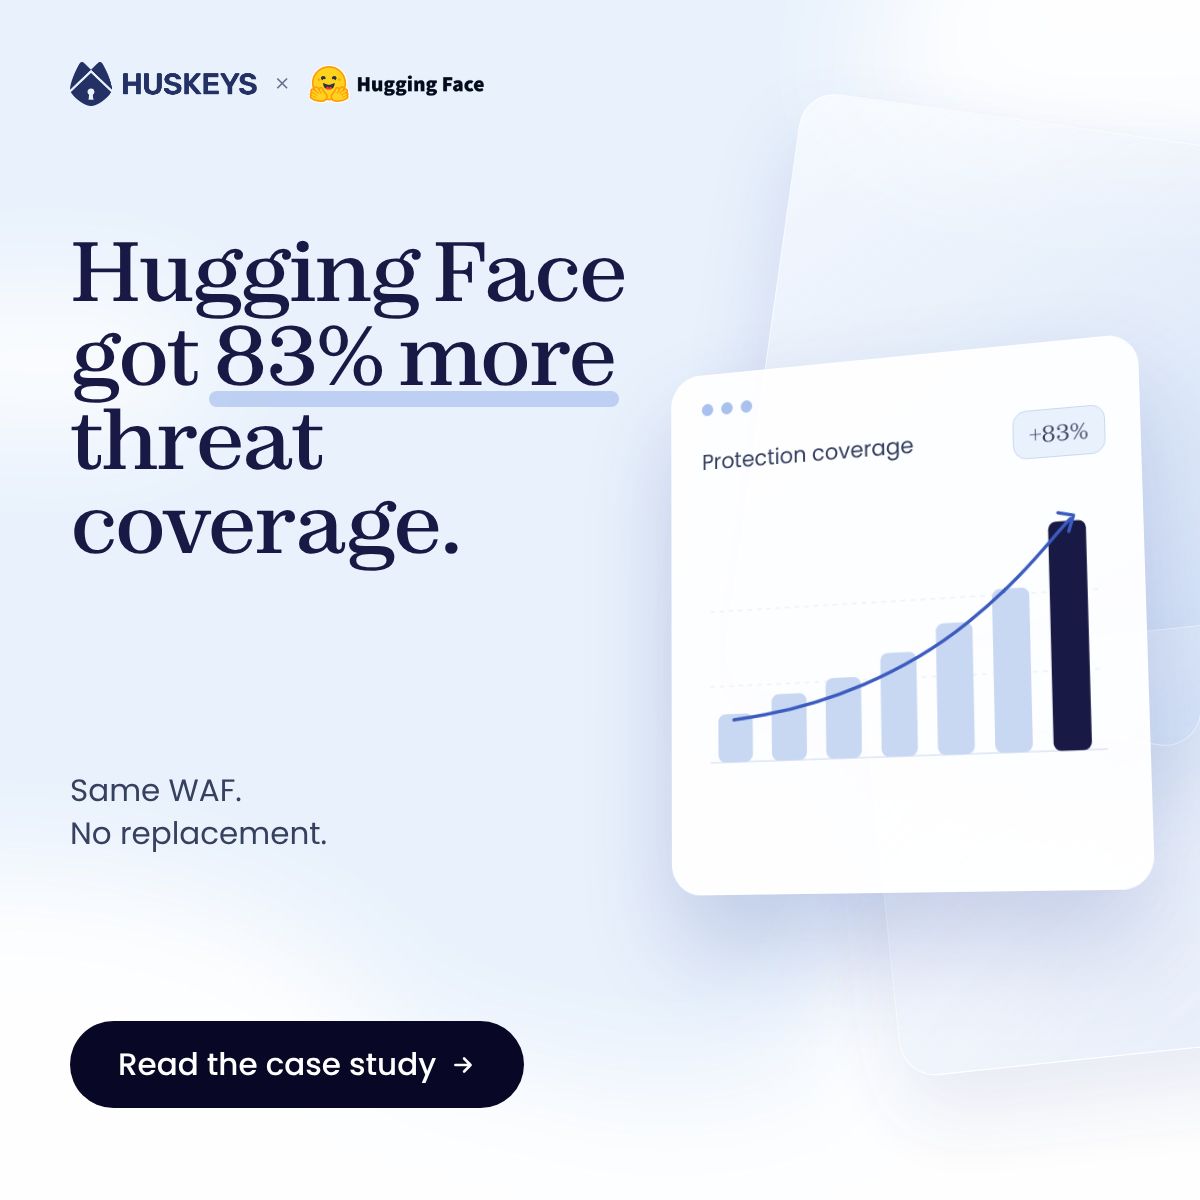
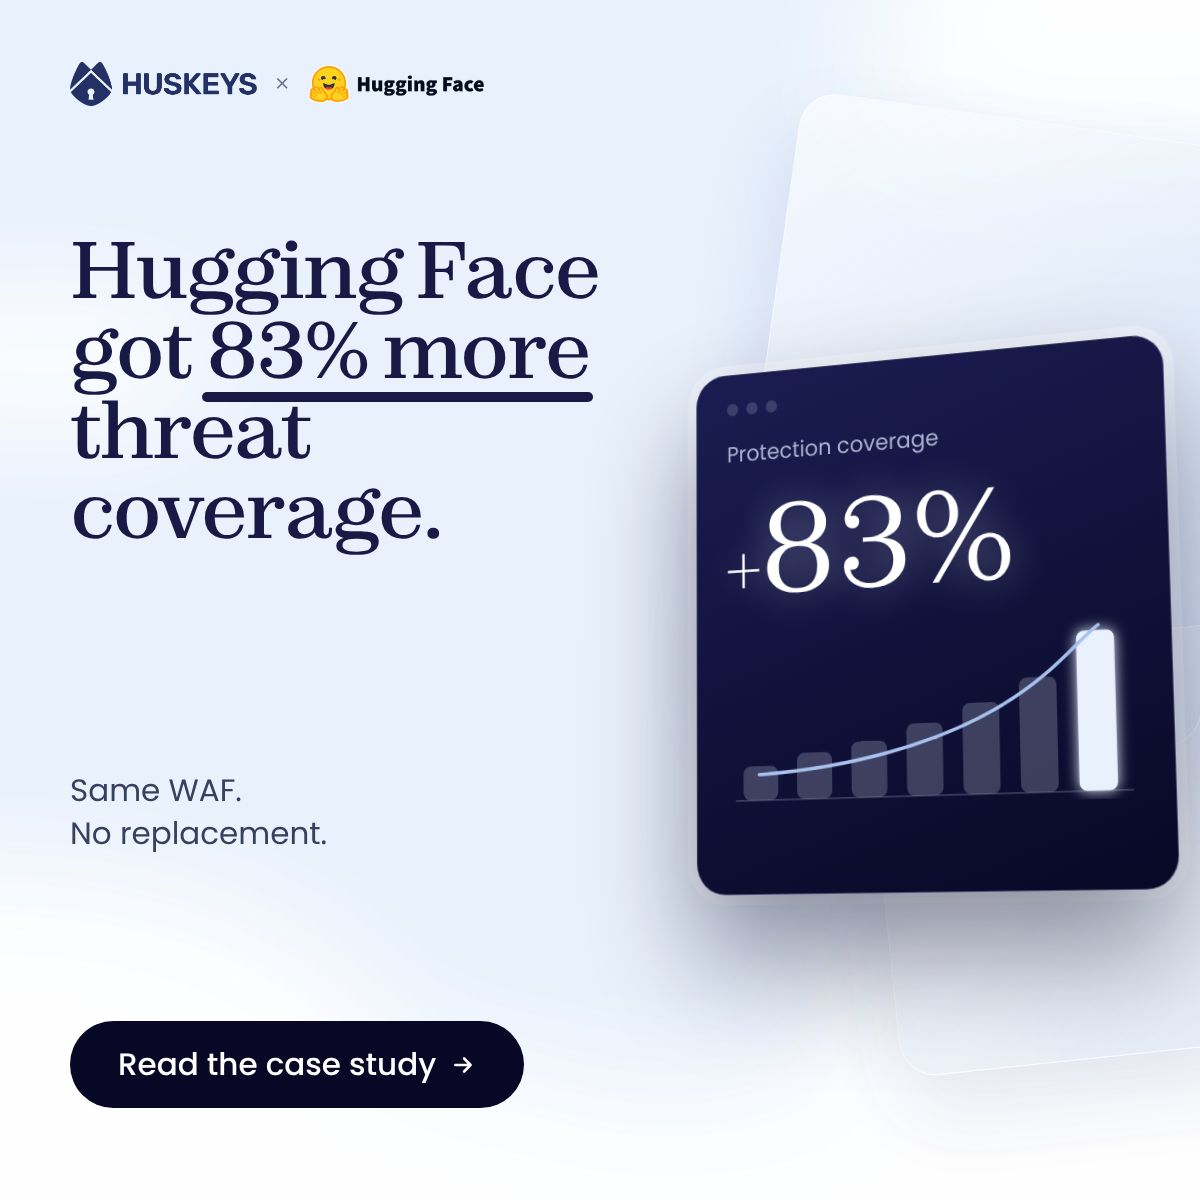
How do you increase WAF protection coverage by 83% while reducing unnecessary inspections by 40%? Read the case study to see what changed →
- ESET DACHSince 23 Oct 2026
Wir wollten es wissen: Wie gut haben sich deutsche KMU gegen Cyberangriffe abgesichert? In unserem Auftrag hat das Marktforschungsinstitut Go4insight 500 Personen befragt, die IT-Sicherheitsentscheidungen mit 25 bis 1.000 Endgeräten treffen oder beeinflussen. 🔖Sie möchten die vollständige Studie lesen? Jetzt downloaden (Dateneingabe benötigt): ⬇️
- HuskeysRecorded 27 Oct 2026
What if you could get 83% more protection coverage without replacing your AWS WAF? Hugging Face did. Here's how.
- FortanixSince 23 Oct 2026
Containers are how the world ships applications. In the AI era, they’re also how AI scales. ⤵️ https://hubs.li/Q04Bw6sg0 But the threat hasn’t changed: models, agents, and applications still touch your most sensitive data, and that data is exposed when it’s decrypted for inference. Today, Fortanix announced support for Confidential AI with CNCF Confidential Containers (CoCo). Teams can now deploy Kubernetes AI workloads to hardware-based Trusted Execution Environments with one click, and every workload is verified before any key is released. Thanks to our partners 🤝 NVIDIA Intel AMD Microsoft Dell Technologies Hewlett Packard Enterprise L&T Technology Services Cisco Red Hat ElevenLabs Deepgram gnani.ai Supermicro Technology Innovation Institute Resemble AI Rafay Spectro Cloud TELUS Klique H2O.ai Fujitsu CrowdStrike Personal AI VAST Data Alpha Compute This gives enterprises: - Protection for data, models, and agents while they run (not just at rest and in transit) - The ability to run frontier models on-premises or air-gapped, right next to sensitive data - High availability, 24x7 support, and FIPS 140-2 Level 3 key management, built for production Anand Kashyap Anand Balasubrahmanyan Anuj Jaiswal Jethro Beekman Patrick Conte Vishal Saxena Connie Chung Rohit Pasam Bob Wallace Read the announcement ⤵️ https://hubs.li/Q04Bw6sg0 #ConfidentialComputing #ConfidentialAI #ConfidentialContainers #CoCo #AISecurity #SecureAI #EnterpriseAI
- esentryRecorded 27 Oct 2026
3 DAYS TO GO! 🚶🏽♂️ We’re Walking for More Than Just the Distance. We’re walking for safer digital experiences, stronger businesses, protected personal information, and a future where everyone understands the importance of cybersecurity. For every member of our team, there’s a reason to take that step. But we’re all moving towards one goal: a safer digital world. In just 3 days, we’re taking cybersecurity awareness beyond conversations and into our communities. 10KM. One Mission. A Safer Digital World. 📅 Saturday, 24 October 2026 ⏰ 8:00 AM 📍 Takeoff: esentry Office, Yaba, Lagos 👕 Dress Code: White Top, comfortable pants and shoes for walking. Come walk with us. Let’s Outpace the Threat! Register at https://lnkd.in/e8ScwfYC to be a part. Don’t Make It Easy for Them. #OutpaceTheThreat #DontMakeItEasyForThem #CybersecurityAwarenessMonth #CyberAwareness #esentry
- EvidencySince 22 Oct 2026
Un bon de livraison numérique peut-il offrir le même niveau de confiance que le papier, tout en simplifiant les opérations sur site ? C’est tout l’enjeu du projet mené avec VINCI Construction France et Axians Industrial Applications & Services autour de la dématérialisation des bons de livraison, conformément aux exigences de la norme NF P98-750. Dans la construction routière, le bon de livraison atteste des quantités produites et livrées. Il intervient dans la facturation et constitue une pièce de référence lors des audits, contrôles ou litiges. Sur le terrain, nous avons filmé le fonctionnement concret du dispositif : • Le bon de livraison est généré par le logiciel VAS Yard Management fourni par Axians IAS, et transmis automatiquement à Evidency. • Il reçoit un numéro unique, puis est scellé, horodaté et enrichi d’un QR code permettant de vérifier son authenticité. • Il est ensuite archivé de manière sécurisée. • Le conducteur le reçoit par SMS, e-mail ou sous forme de ticket imprimé. Le résultat : un processus dématérialisé qui associe efficacité opérationnelle, traçabilité et prévention de la fraude documentaire. Merci aux équipes VINCI Construction France, VINCI CONSTRUCTION SI, Romain PERNET-SOLLIET, Zakary Millat, et Axians Industrial Applications & Services, Stefanie Marszalkowski, Carl-Philip Scheitterlein, pour leur collaboration et pour nous avoir permis de montrer cette transformation au plus près des opérations. 🎥 Regardez la vidéo complète. --------------------- ENGLISH VERSION Can a digital delivery ticket provide the same level of trust as paper, while simplifying operations on site? This is the challenge addressed by our work with VINCI Construction France and Axians Industrial Applications & Services around the digitisation of delivery tickets, in line with the requirements of the NF P98-750 standard. In road construction, delivery tickets record the quantities produced and delivered. They support invoicing and provide a reference document for audits, inspections and disputes. We went on site to film how the process works in practice: • The delivery ticket is generated by the VAS Yard Management software provided by Axians IAS, and automatically transmitted to Evidency. • It is assigned a unique number, then electronically sealed, timestamped and provided with a QR code allowing its authenticity to be verified. • It is then securely archived. • The driver receives it by SMS, email or as a printed ticket. The result is a digital process combining operational efficiency, traceability and documentary fraud prevention. Thank you to the VINCI Construction France, VINCI CONSTRUCTION SI, Romain PERNET-SOLLIET, Zakary Millat, and Axians Industrial Applications & Services teams, Stefanie Marszalkowski, Carl Philip Scheitterlein for their collaboration and for enabling us to document this transformation where it actually takes place: on site. 🎥 Watch the full use case in our video.
- EvidencySince 22 Oct 2026
Digitising industrial documents is one thing. Being able to guarantee their reliability is another. Every day, thousands of documents accompany the flow of materials and goods across industrial operations: weighbridge tickets, delivery notes, processing certificates, transport documents... Digitising these documents represents a significant step forward in operational efficiency. But it also raises an important question: How can we guarantee their origin, integrity and traceability throughout their lifecycle and transmission? This is precisely the challenge that Evidency addressed alongside Axians Industrial Applications & Services as part of a project for VINCI Construction France to digitise asphalt delivery notes in compliance with the NF P98-750 standard. This challenge extends far beyond the construction sector. In recycling, maritime transport, logistics and manufacturing, the reliability of digital documents plays a key role in securing exchanges between the various stakeholders. The next step in industrial digitalisation is not simply about going paperless. It is about building trust directly into digital processes. Watch our video to discover the project developed jointly with VINCI CONSTRUCTION SI and Axians IAS.
- Hunt & HackettSince 24 Oct 2026
AI is speeding up how vulnerabilities are found and exploited. Most attacks still rely on familiar weaknesses, but you will have less time to detect and contain them. Choosing a new MDR provider? The MDR Buyer's Guide shows how to assess detection, investigation and response capabilities for this changing threat landscape. Download the guide 👇
- inforcerSince 22 Oct 2026
No Conditional Access on your customers' devices? You're one phishing email from a breach. This checklist covers 14 Intune best practices, from enforcing device compliance to blocking personal device access to company data. Most of it runs on Intune Plan 1. All of it matters.
- Hunt & HackettSince 23 Oct 2026
Regulated organisations need more from MDR than alert handling. Before you choose a provider, make sure they can show what happened, what was affected, how decisions were made and how your security coverage improves over time. Download the guide 👇
- GigamonSince 23 Oct 2026
As AI reshapes defense, move from point‑in‑time detection to continuous validation. Read more.
- Eye SecuritySince 23 Oct 2026
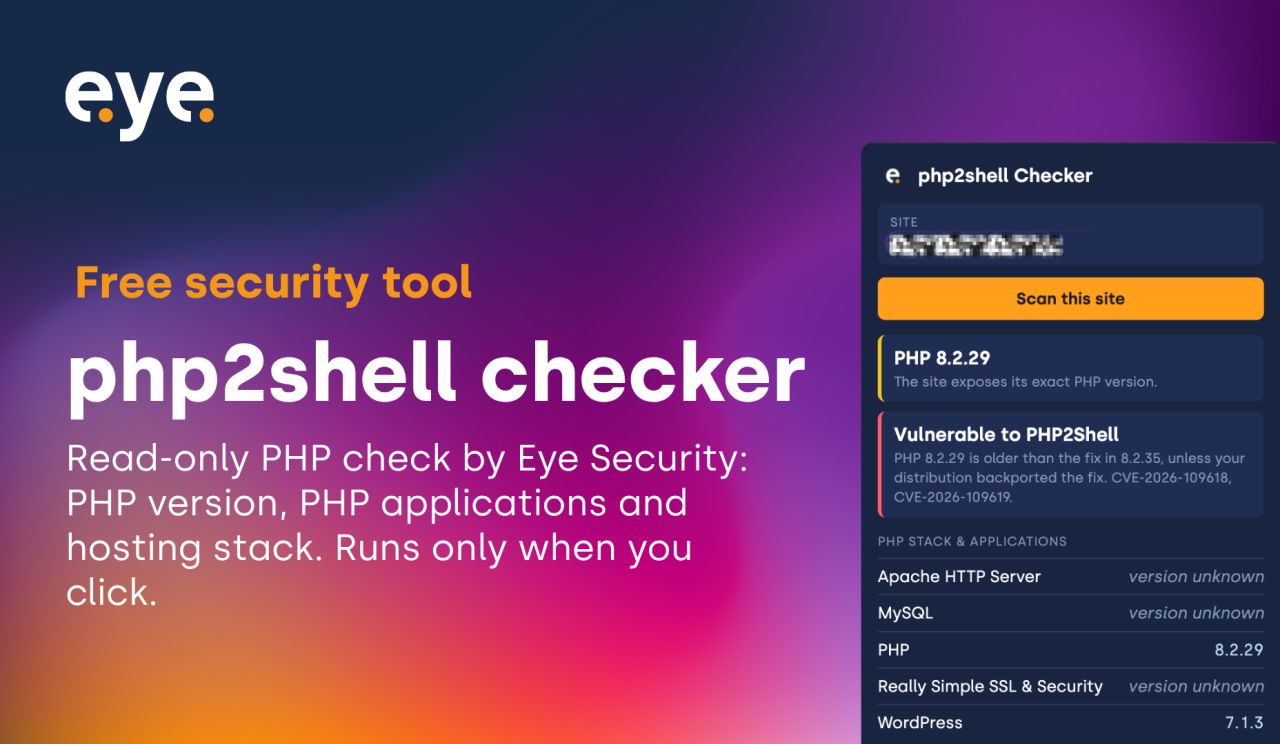
Our new php2shell Checker is now available for Google Chrome and Microsoft Edge! It's a free browser extension from Eye Security that gives IT teams a quick, read-only check of the PHP version a website exposes. Click 'Scan' to check the version shown in the site’s response headers, compare it with php2shell affected versions and view detected technologies in the web stack. The scan runs in your browser, only when you start it. It does not send an exploit or probe to the site, and there is no server-side backend. The result is based on the PHP version the website exposes. Some sites hide this information, and a version check alone is not a definitive vulnerability assessment. Confirm the PHP version and patch status with the server or hosting provider. We’ve also published new php2shell research based on controlled testing. It outlines forensic traces, logs and indicators defenders can look for when investigating potential exploitation. Download the extension and read the research via the links in the comments. #PHP #php2shell #Chrome #Edge #CyberSecurity #ThreatResearch
- Eye SecuritySince 23 Oct 2026
Bedrohungen machen keinen Feierabend, aber die meisten Security Teams schon. Cyberangriffe halten sich nicht an Geschäftszeiten. Sie treten nachts auf, am Wochenende und an Feiertagen, genau dann, wenn die Abdeckung am geringsten und die Reaktionszeiten am längsten sind. Das ist kein Versagen Ihres Teams, sondern die Realität moderner Angriffe. Ein 24/7 Sicherheitsbetrieb bedeutet kontinuierliches Monitoring, sofortige Erkennung und Analysten, die in dem Moment reagieren, in dem etwas auffällig wird, unabhängig von der Uhrzeit. Genau diese Lücke schließt Eye Security.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.