B2B ad examples
1,817 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- AcronisSince 26 Oct 2026
L'interruption d'activité ne se résume plus à problème informatique. Il s'agit d'un enjeu majeur pour la continuité des activités qui affecte le chiffre d'affaires, les opérations et la réputation.
- AcronisSince 26 Oct 2026
Vom Schutz bis zur Wiederherstellung: Umfassende Cyber-Resilienz auf einer einzigen Plattform
- GuardsquareSince 26 Oct 2026
91% of mobile developers say they prefer mobile app security that covers the entire software development lifecycle. Guardsquare provides that.
- GuardsquareSince 26 Oct 2026
For this Central American bank, mobile app security was a top priority. They found Guardsquare provided the best code hardening and RASP solution.
- InvictiSince 27 Oct 2026
Extend AppSec testing beyond signature-based detection with AI-assisted business logic and abuse-case testing.
- KasperskySince 26 Oct 2026
Uma tentativa de deepfake a cada 5 minutos. Uma videochamada falsa custou US$ 25 milhões a uma empresa. Sua equipe perceberia? Veja o plano.
- CyberFortifySince 26 Oct 2026
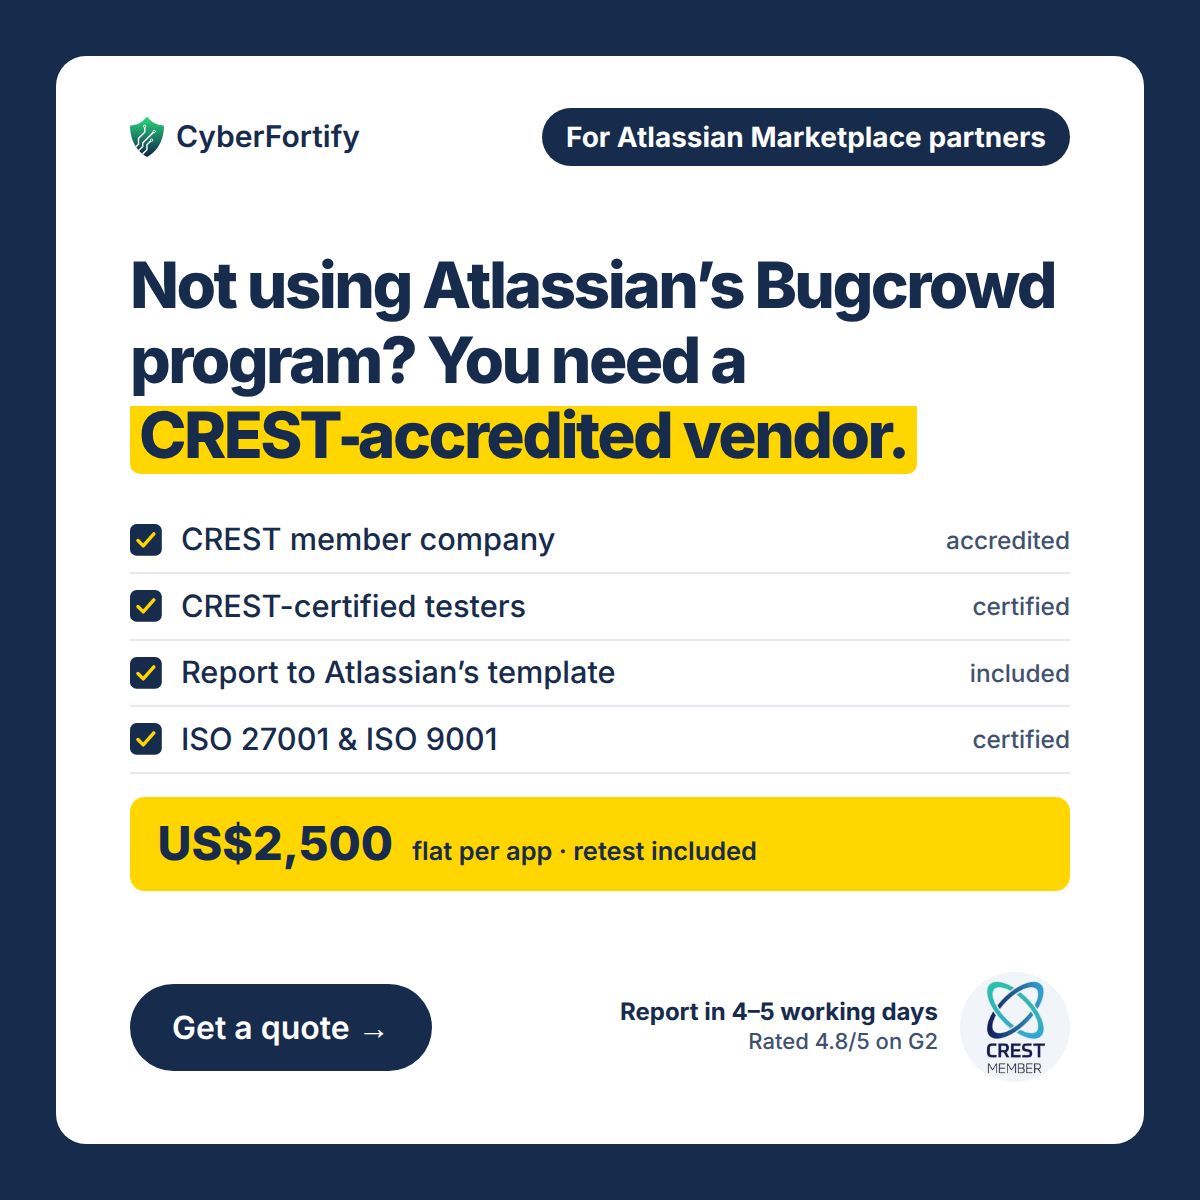
Atlassian Marketplace partners not using Atlassian’s Bugcrowd program: the self-managed AEC route needs a CREST-accredited testing vendor. CyberFortify is a CREST member company with CREST-certified testers. US$2,500 flat per app.
- Ahlan CyberRecorded 28 Oct 2026
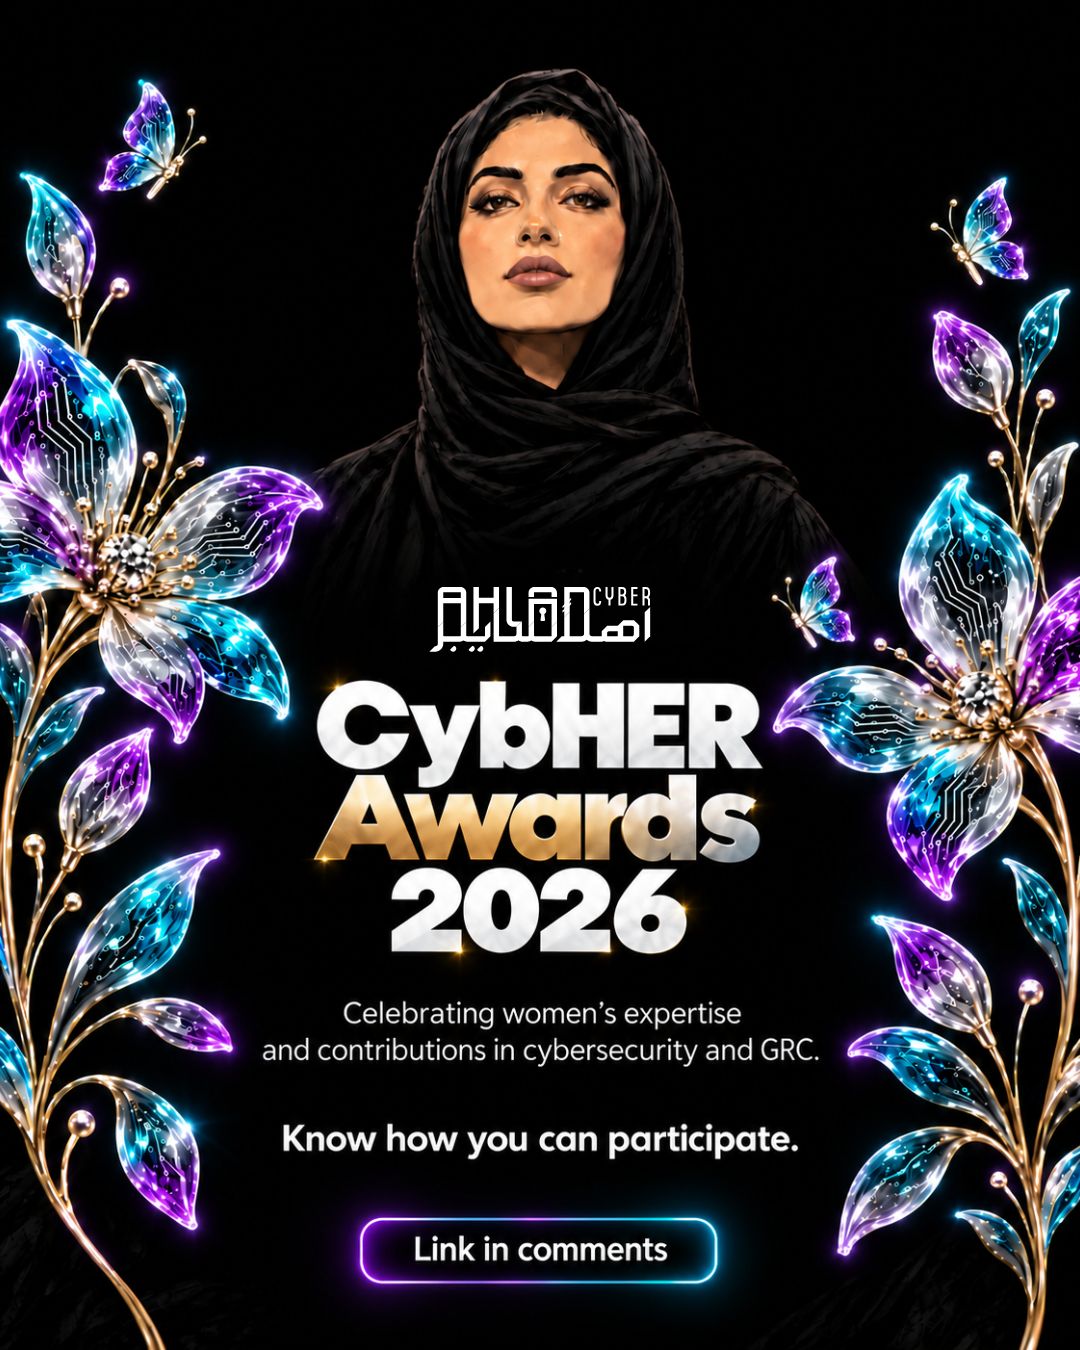
Introducing CybHER Awards 2026*, an initiative celebrating women whose expertise, experiences, and contributions are helping shape the future of cybersecurity. Through your work in cybersecurity, you’ve gained valuable insights, whether it’s a fresh perspective on managing risk, a framework you’ve developed, or a lesson that could inspire others. Sharing that knowledge could help another professional take their next step. CybHER recognises the expertise of women in cybersecurity and GRC, providing a platform to share experiences, exchange knowledge, and contribute to the growth of the cybersecurity community. Who can participate? The awards are open to eligible women cybersecurity and GRC professionals working in end-user organisations. Employees of cybersecurity vendors, service providers, consultancies, and MSSPs, or professionals primarily serving external cybersecurity clients, are not eligible. How to participate? Choose one of the following formats: - A blog of up to 1,000 words - A presentation of up to 10 slides - A one-minute video Complete the registration form and upload your entry through the CybHER page. What’s in it for the winners? Five winners will each receive *USD 1,000 in Amazon gift cards, or the local-currency equivalent, alongside recognition and professional visibility. Terms apply. Submission deadline: 30 November 2026, 11:59 pm GST (UTC+4). At Ahlan Cyber, we believe that sharing knowledge and recognising the contributions of women in cybersecurity can inspire more professionals to learn, grow, and lead. What do you know today that you wish you had known earlier? Your experience could be the inspiration someone else needs. Find the participation details and submission link in the comments. Hala Alsadi, Ashok Chandrasekharan, Premchand Kurup, Namith Najeeb, Divya Raj, Divya N T, Priyankaa Venkateswar #CybHER2026 #WomenInCybersecurity #Cybersecurity #GRC
- CyberFortifySince 26 Oct 2026
Atlassian Marketplace partners going for Enterprise Certified: requirement 1.1 asks for a current annual pentest. We write the report to Atlassian’s scoping template, so it drops straight into your ECOHELP ticket. US$2,500 flat per app.
- ClarotySince 24 Oct 2026
Strengthening your OT security shouldn't come at the cost of operational downtime. Are your critical systems protected? Join our live webinar to discover how the SANS 5 ICS Critical Controls and AI-driven capabilities can help improve your security posture, simplify compliance, and maintain continuous device availability. What you'll learn in the webinar: - Applying the SANS 5 ICS Critical Controls to strengthen security and operational resilience. - Using AI-driven tools to streamline compliance and improve reporting accuracy. - Exploring how agentic AI can automate risk correlation and threat containment. Register now to secure your spot!
- ChainguardSince 24 Oct 2026
Frontier AI is breaking cybersecurity. Chainguard helps banks protect their critical data from malware, zero-days, and CVE exploits.
- ChainguardSince 24 Oct 2026
Chainguard secures the foundation that banks build on to prevent AI-driven supply chain attacks.
- Akeyless SecuritySince 23 Oct 2026
𝗪𝗮𝗿𝘂𝗺 𝗞𝗜-𝗔𝗴𝗲𝗻𝘁𝗲𝗻 𝗭𝘂𝗴𝗮𝗻𝗴𝘀𝗱𝗮𝘁𝗲𝗻 𝗴𝗲𝗯𝗲𝗻, 𝗱𝗶𝗲 𝘀𝗶𝗲 𝗴𝗮𝗿 𝗻𝗶𝗰𝗵𝘁 𝗯𝗿𝗮𝘂𝗰𝗵𝗲𝗻? So ermöglicht Akeyless Just-in-Time-Zugriff, ohne Secrets gegenüber KI-Agenten offenzulegen: https://lnkd.in/ePKwHf8K/?utm_campaign=WebvisitsCampaignGroup&utm_source=linkedin&utm_medium=paid&utm_id=734991773&hsa_acc=504077772&hsa_cam=734991773&hsa_grp=897278023&hsa_ad=1593017303&hsa_net=linkedin&hsa_ver=3
- FTAPISince 26 Oct 2026
Zertifikate verwalten, Plugins pflegen, Rückfragen beantworten: Die E-Mail-Verschlüsselung landet schnell bei der IT. Der Praxisguide zeigt, wie ihr Regeln einmal zentral festlegt. Danach greifen sie bei jeder E-Mail, egal aus welchem E-Mail-Programm sie kommt. Mitarbeiter klicken nur auf Senden.
- Akeyless SecuritySince 23 Oct 2026
𝗪𝗮𝗿𝘂𝗺 𝗞𝗜-𝗔𝗴𝗲𝗻𝘁𝗲𝗻 𝗭𝘂𝗴𝗮𝗻𝗴𝘀𝗱𝗮𝘁𝗲𝗻 𝗴𝗲𝗯𝗲𝗻, 𝗱𝗶𝗲 𝘀𝗶𝗲 𝗴𝗮𝗿 𝗻𝗶𝗰𝗵𝘁 𝗯𝗿𝗮𝘂𝗰𝗵𝗲𝗻? So ermöglicht Akeyless Just-in-Time-Zugriff, ohne Secrets gegenüber KI-Agenten offenzulegen: https://lnkd.in/e_cEQHnB/?utm_campaign=WebvisitsCampaignGroup&utm_source=linkedin&utm_medium=paid&utm_id=734991773&hsa_acc=504077772&hsa_cam=734991773&hsa_grp=897278023&hsa_ad=1593130423&hsa_net=linkedin&hsa_ver=3
- CINI Cybersecurity National LabSince 26 Oct 2026
🌟 Ci sono occasioni che vanno oltre ciò che accade davanti agli schermi. E l’European Cybersecurity Challenge 2026 è stata una di queste. La competizione annuale di sicurezza informatica promossa da ENISA e svoltasi a Bochum, in Germania, ha riunito studenti e studentesse, tutor e professionisti del settore, accomunati da una stessa passione: la #cybersicurezza. 🚀 Per TeamItaly e le altre Nazionali è stata una settimana piena, tra l’attesa prima delle challenge, la ricerca della soluzione giusta durante le prove e la voglia di dare il meglio. 👏 Grazie a tutti coloro che hanno preso parte alla 12ª edizione! 🎞️ Guarda il reel per ripercorrere i momenti più emozionanti. #CybersecurityNationalLab #TeamItaly #ECSC2026 #cybersecurity
- FTAPISince 26 Oct 2026
Verschlüsseln oder nicht? Wenn Mitarbeiter das bei jeder E-Mail selbst entscheiden müssen, passieren Fehler. Nicht aus Nachlässigkeit, sondern weil der Alltag voll ist. Der Praxisguide zeigt, wie aus dieser Entscheidung ein Standard wird, der im Hintergrund läuft.
- Fox-ITSince 26 Oct 2026
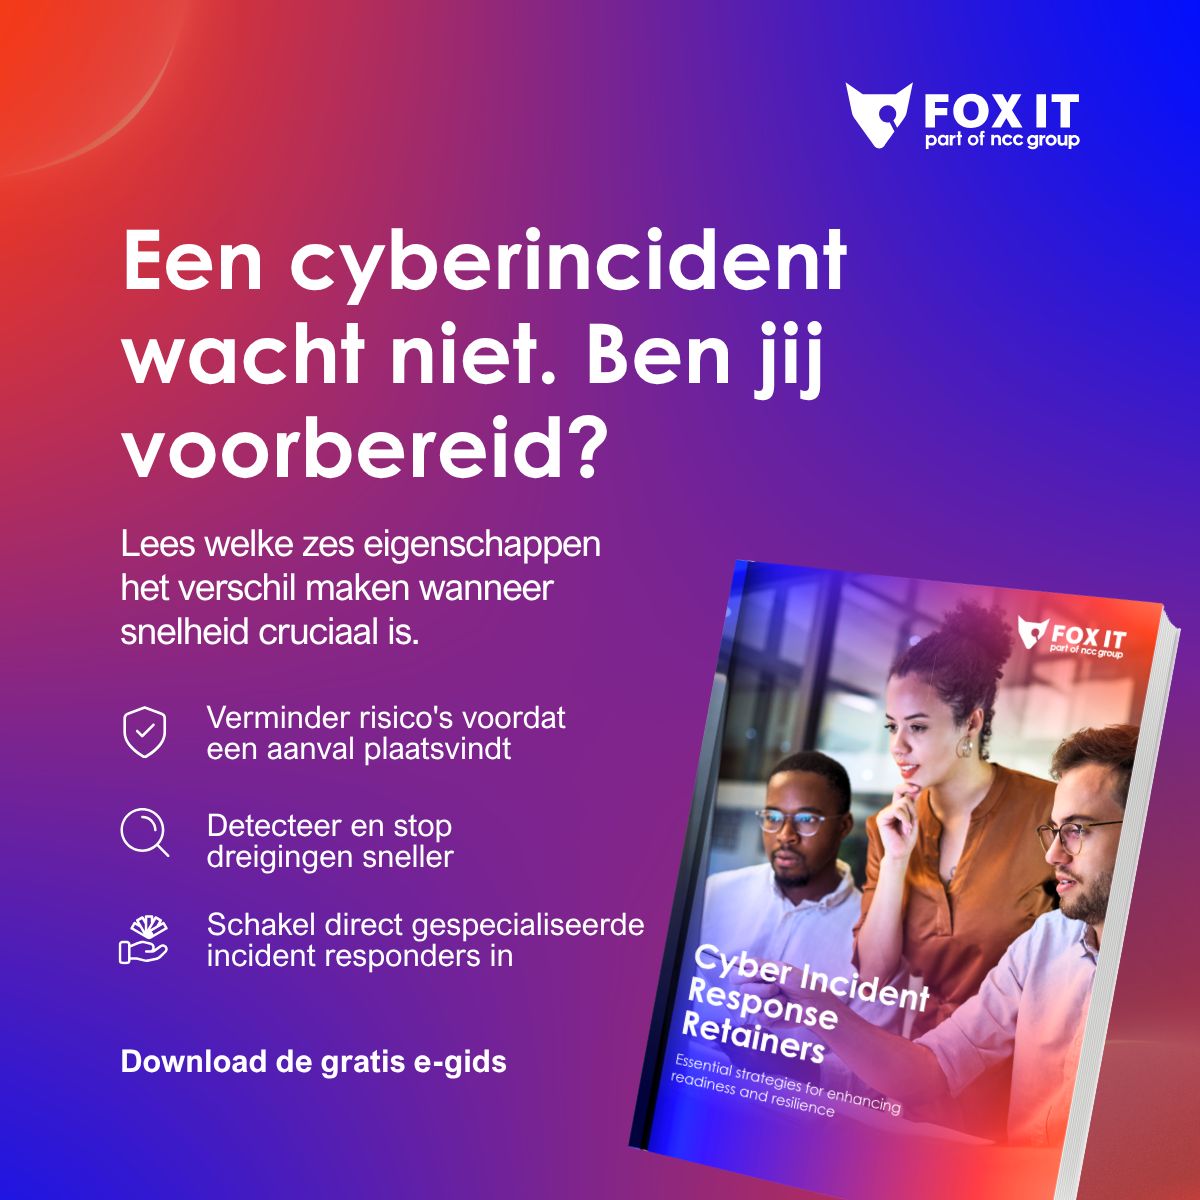
Wanneer elke minuut telt, maakt de juiste partner het verschil. Met de juiste expertise op het moment dat het erop aankomt, beperk je risico's, reageer je sneller en houd je de impact op je organisatie zo klein mogelijk. Ontdek de belangrijkste strategieën om je cyberweerbaarheid te versterken en beter voorbereid te zijn op een incident.
- Fort CyberSince 26 Oct 2026
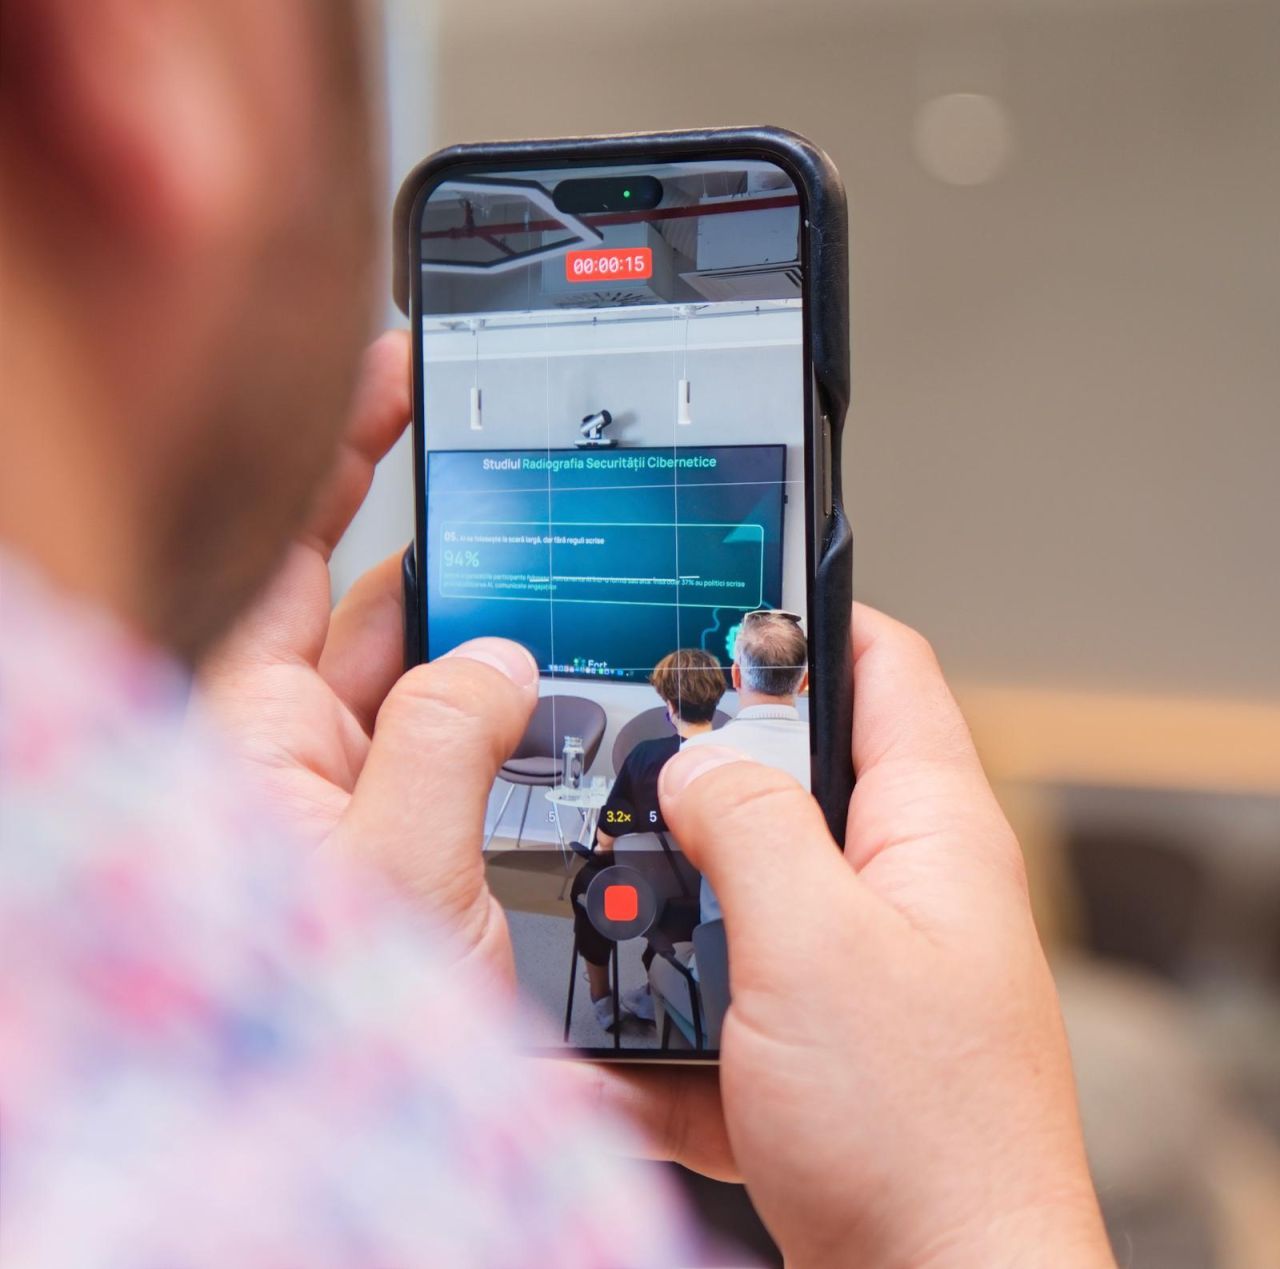
Un alt insight din studiul nostru este poate mai predictibil și n-ar trebui să surprindă pe nimeni: AI se folosește intens, dar fără să existe reguli scrise care să prevină riscurile asociate. Organizațiile participante la studiu au menționat că utilizarea instrumentelor AI este larg răspândită, de la activități de productivitate până la procese de business. Problema care ne-a atras atenția e că regulamentele interne nu sunt conforme din punct de vedere al ritmului. Este unul dintre exemplele în care tehnologia a avansat mai repede decât guvernanța care ar trebui să o însoțească. Sperăm ca peste ani, dacă vom repeta acest studiu, să observăm că s-a remediat problema, organizațiile definind clar cum să folosească AI pentru eficientizare, dar fără a lăsa porți deschise vulnerabilităților. Poți accesa și tu raportul în linkul din comentarii.
- EnclaveSince 26 Oct 2026
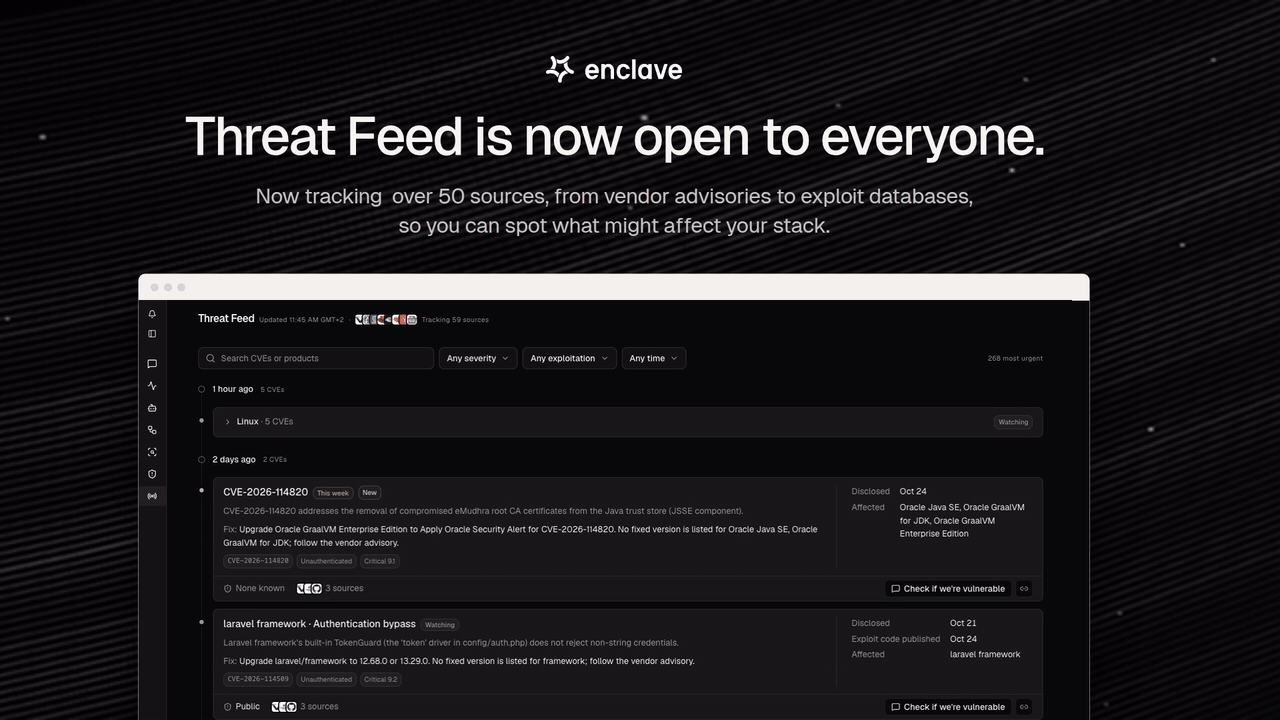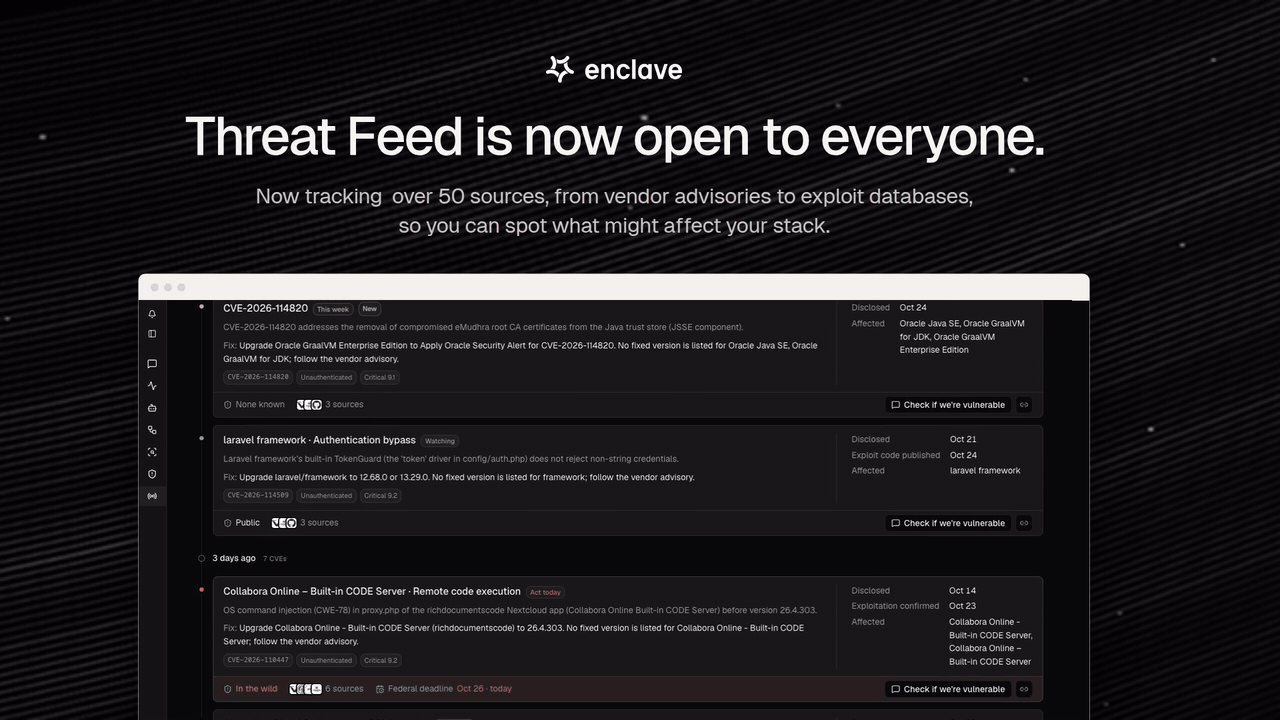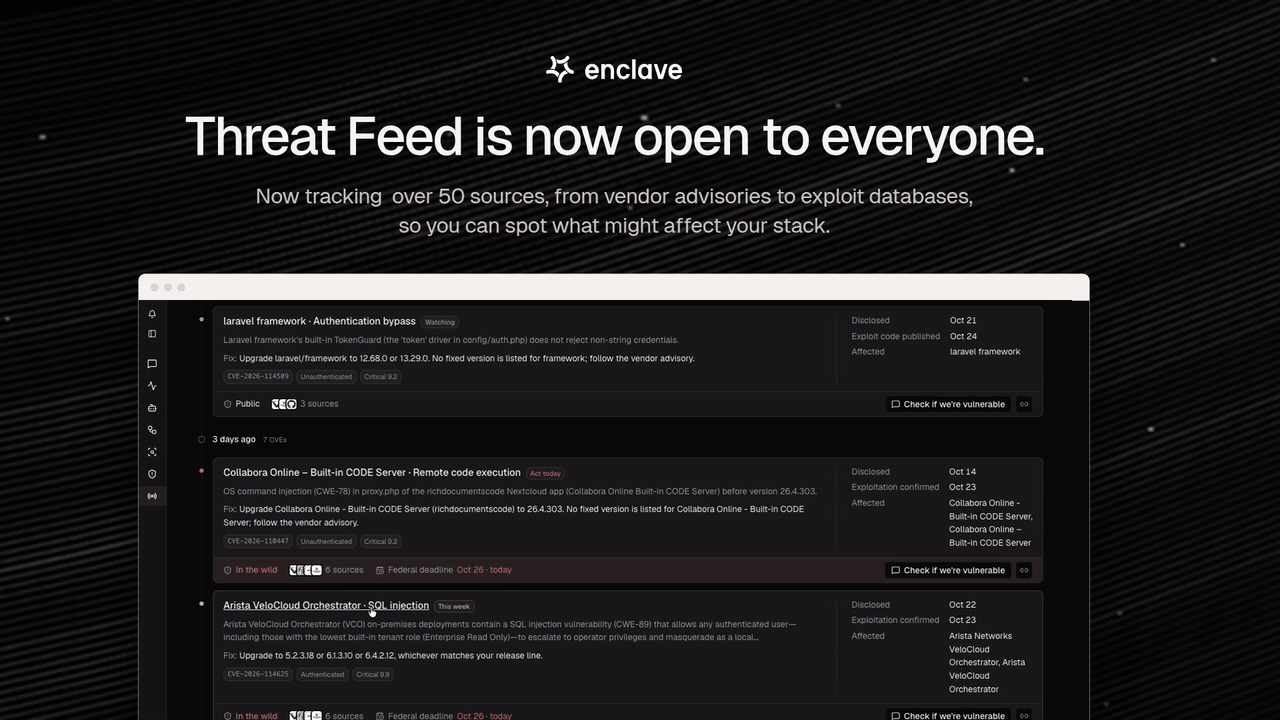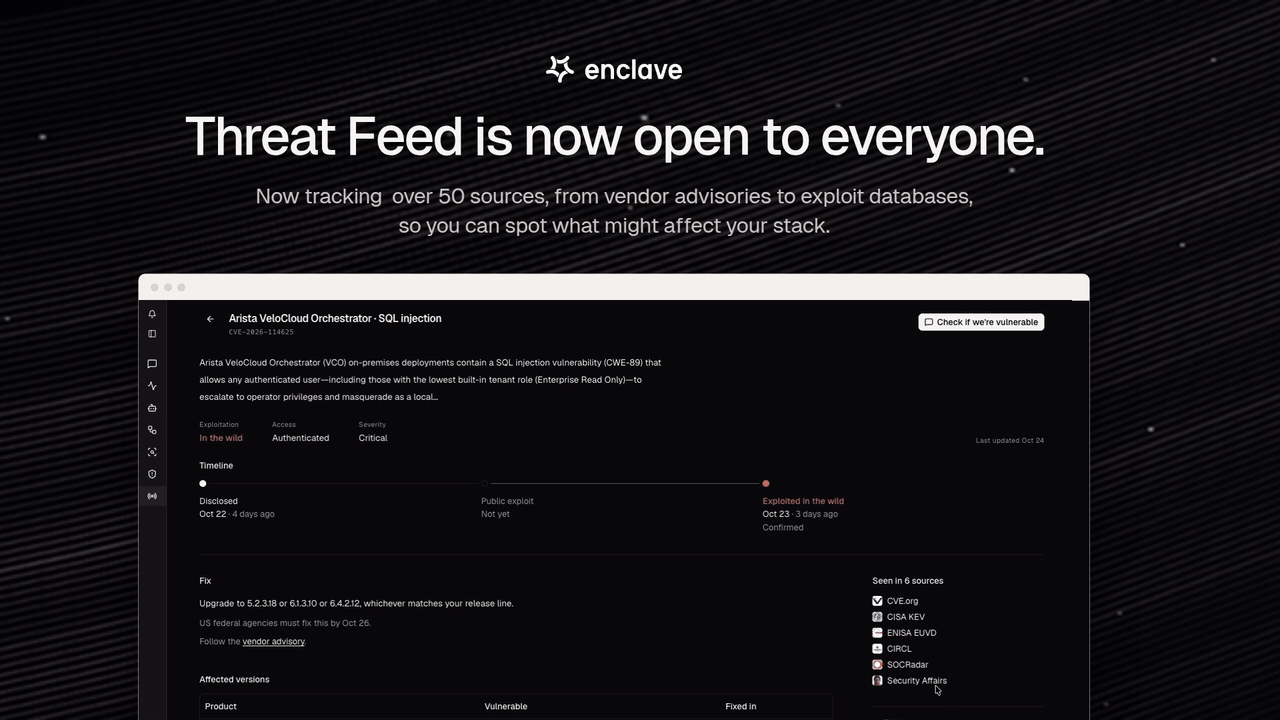
Enclave’s Threat Feed now covers over 50 sources and is open to everyone. Threat Feed brings together vendor advisories, Linux distributions, CERTs, disclosure programs, and exploit databases such as MSRC, Red Hat, CERT/CC, ZDI, and Metasploit. Each entry shows which sources reported it, and ZDI reports can appear before a CVE is assigned. We want to helps teams keep track of what has been disclosed or exploited and spot threats that may affect their stack. Threat Feed provides visibility into reported vulnerabilities; it doesn’t scan your applications or assess code exposure. Explore the Threat Feed: https://lnkd.in/ds5X3Z2E To check whether these threats affect your code, sign up for a 14-day free trial of Enclave.
- Ahlan CyberRecorded 28 Oct 2026
Your cybersecurity experience deserves a bigger stage. 🏆 Ahlan’s inaugural CybHER Awards 2026 celebrate women in cybersecurity and GRC. ✅ Eligibility: Women in cybersecurity or GRC at end-user organisations. Vendors, MSSPs and consultancies are not eligible. 🎁 Rewards: 5 winners get USD 1,000 in Amazon gift cards (or local equivalent) plus industry visibility. 📝 How to enter: Choose a blog (up to 1,000 words), a deck (up to 10 slides) or a 1-minute video. Upload via the CybHER page. Deadline: 30 Nov 2026, 11:59 pm GST. Terms apply.
- Fort CyberSince 26 Oct 2026
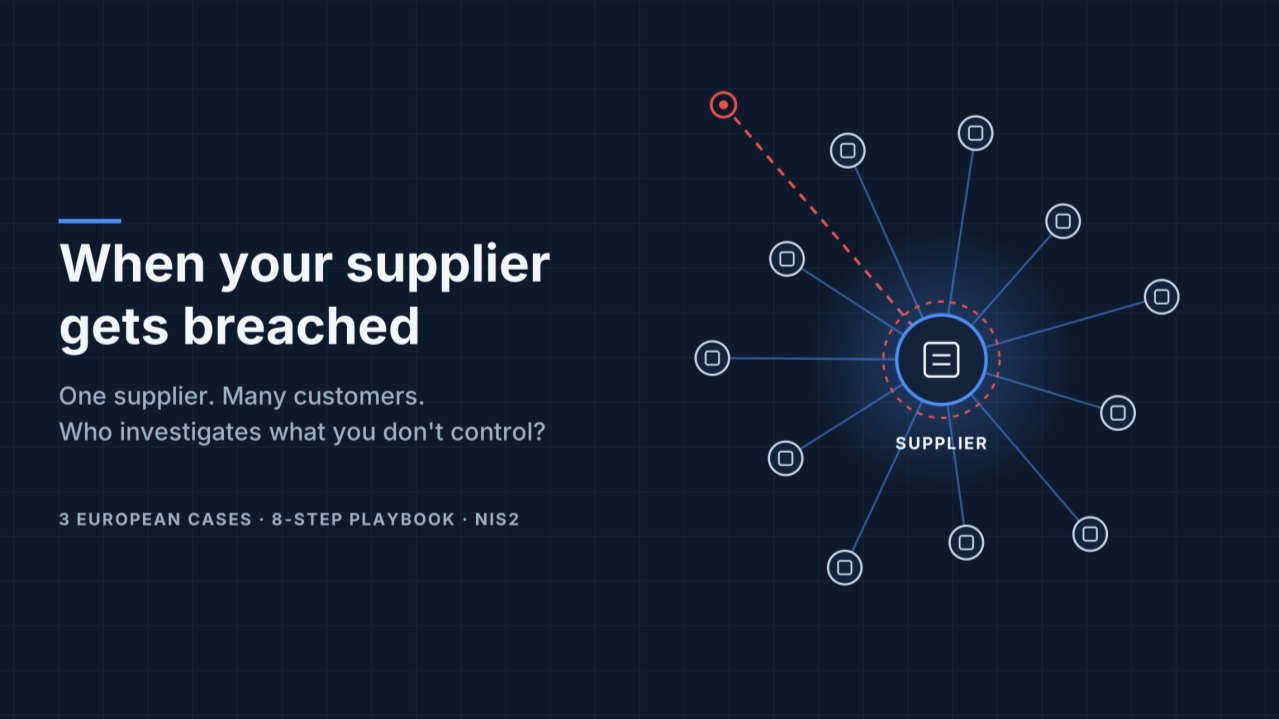
PHP2Shell is a good reason to look beyond your own servers. Radu Ailenei’s suggestion: ask your critical suppliers this week whether any systems that hold your data or access your environment run PHP, and whether they’re on 8.5.12, 8.4.27, 8.3.36 or 8.2.35. For PHP 5 or 7 there is no patch, and according to the PHP team, configuration changes alone don’t fully fix it. His new article shows why the question matters: three European third-party incidents, three different causes, one shared pattern. It also includes an 8-step playbook for incidents in infrastructure you don’t control. Take a look.
- Fox-ITSince 26 Oct 2026
Een cyberincident wacht niet. Ben jij voorbereid? Lees welke zes eigenschappen het verschil maken wanneer snelheid cruciaal is. ✓ Verminder risico's voordat een aanval plaatsvindt ✓ Detecteer en stop dreigingen sneller ✓ Schakel direct gespecialiseerde incident responders in ✓ Beperk downtime en bedrijfsverstoring ✓ Krijg toegang tot geavanceerde digitale forensische expertise ✓ Profiteer van deskundig advies vóór, tijdens en na een incident
- Adversa AISince 26 Oct 2026
Claude Code's official security controls are a floor, not a containment story. We created a new breakdown of what Anthropic's native security settings cover and where they stop by Anthropic's own account. The short version: managed settings help on locked-down fleets, but they bind one tool, not the rest of the agent zoo on the same laptop. If developers have local admin, cloud-hosted sessions, long-running jobs, or side-channel credentials, the neat policy picture gets messy fast. Nice touches you could have missed in your recent security review: 🔻 Auto mode is not a security control. Anthropic's own numbers show a 17% miss rate on risky actions. That's convenience, not assurance. 🔻 The real attacks hit the harness. The model is less of a target. Pre-trust config execution, approval prompts, config hooks detonating on project open. 🔻 The efficient controls are environmental. Scoped short-lived credentials, egress denied by default, treating config and docs as code, disposable rooms for unattended runs, and runtime visibility into what the agent actually did. Read the full analysis: https://lnkd.in/esa2x244 #ClaudeCode #AIsecurity #AgenticAI #codingagents
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.