LinkedIn image ad examples
1,352 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- EscapeSince 7 May 2026
"Claude Code is just hype" they said... Every model drop floods LinkedIn and Reddit with the same takes. I've been skeptical too. "We have created a monster" narrative has been used by AI labs at every major model release since GPT-2. Yet, I've watched security teams start shipping real workflows with Claude. Just keep in mind that there is a gap between the marketing and what actually works in production. So we're bringing in someone who's lived it. On May 20, Geet Pradhan, sr. Security Engineer, is joining me live to break it down: → Where Claude genuinely changes how security engineers operate → Which models are worth using and for what → Real practical examples (threat modeling, detection & response...) Then I'll show the new Escape × Claude integration live: One-click OAuth into Claude Desktop, Claude.ai, and Claude Code → discover crown-jewel assets via ASM → run human-grade pentests → triage with your org context → hand developers a clean remediation If you're trying to do more with a small team, link in the comments 👇
- EscapeSince 19 May 2026
Everyone's talking about Claude in security. But how can we integrate it into Security Engineering workflows without token bankruptcy? Claude can do amazing things. But implementation can get real messy, real quick. Token economics matter. Workflow integration matters. Context management matters. Geet Pradhan has spent the last year watching how Claude fits into his organization’s security program. He’s built significant security automation internally and learned hard lessons about where AI actually helps vs. where it's hype. Join us for a live conversation as Geet breaks down the pragmatic path from proof-of-concept to production security. In Part 1: Building 0→1 Security Functions with Claude, Geet will cover: - What actually works in real ProdSec workflows - Where Claude genuinely changes how teams operate (and where it's just noise) - What Claude model to choose and when - Scaling security without proportional headcount, including examples of real operational workflows In Part 2, see directly from Escape’s CEO, Tristan Kalos, new Claude × Escape integration in action. We’ll show - How to connect Escape to Claude Desktop, Claude.ai, and Claude Code over a one-click OAuth 2.1. No API key copy-paste. - Discover your crown-jewel assets with ASM through simple prompting - Run human-grade pentests against them - Triage findings by adding your org’s context - And hand developers a clean remediation, all without leaving the assistant. If you want to move from "cool proof-of-concept" to "this is part of how we enable small security teams to scale security testing efficiently ", this webinar is for you. Don't miss this opportunity to learn from your peers and ask your questions live!
- EmpowerIDSince 29 Jul 2026
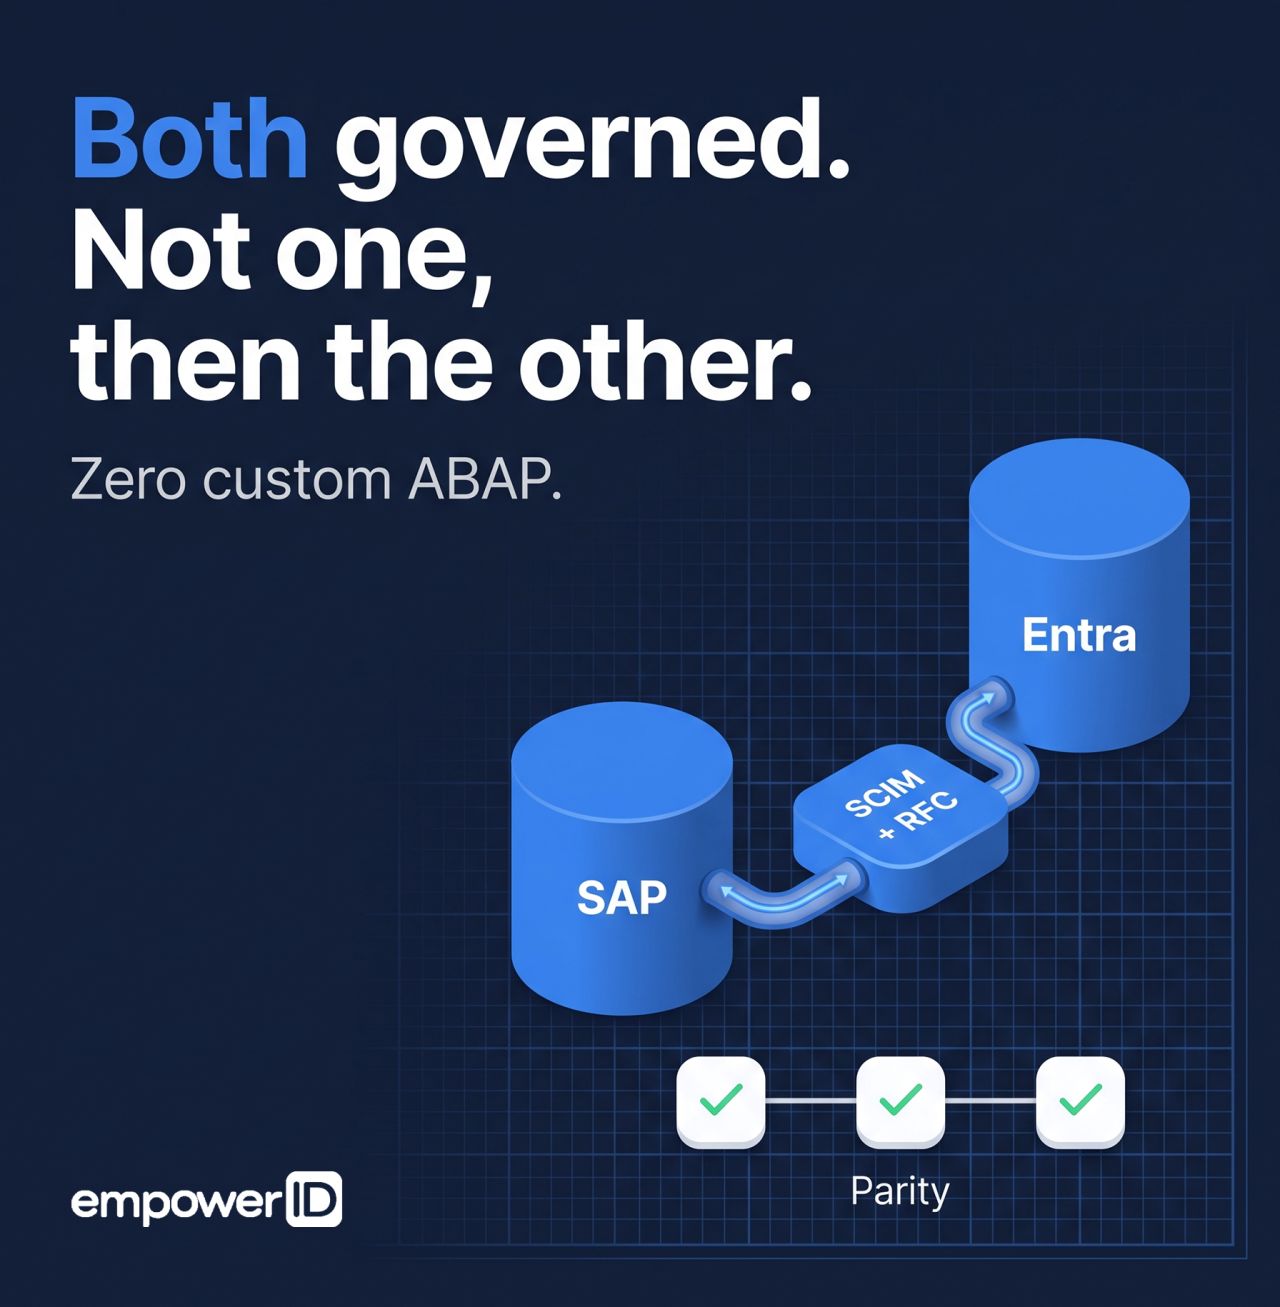
Entra ID Governance rollouts stall in the same place, over and over. Everything works until the project reaches SAP. Entra speaks SCIM and REST. SAP speaks RFC - deep, hierarchical, role-composite, decades of business logic underneath. That's not a connector gap. It's two different paradigms trying to shake hands. Most teams discover this mid-project, after the governance model is already designed around the cloud side. A translation layer changes the sequencing. Provision and govern SAP and non-SAP identities from one control plane - config-driven, zero custom ABAP — with parity validation before anything cuts over. Stalled Entra Governance projects aren't usually a licensing problem. They're an untranslated-protocol problem. Where did your last SAP integration project actually stall - design, build, or validation? ✅Full guide linked below. https://bit.ly/4vQt6oj
- EmpowerIDSince 29 Jul 2026
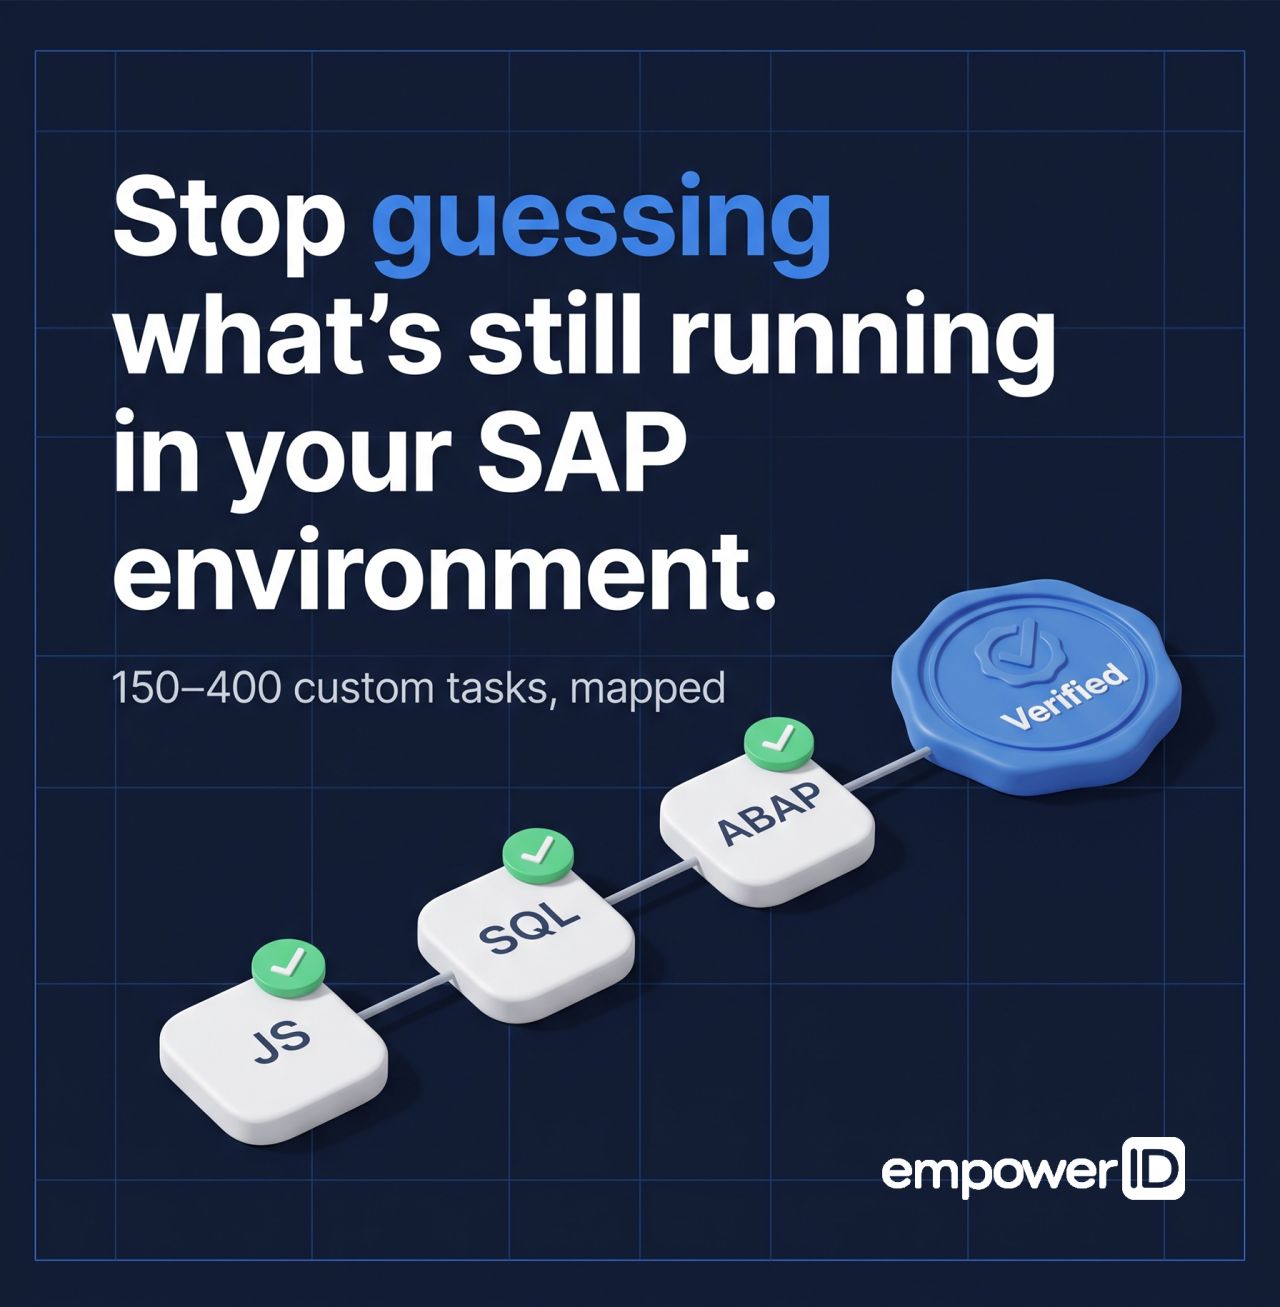
Every SAP Basis team we talk to eventually asks the same question. Not "when do we migrate", they already know the deadline. It's "what happens to GRC?" GRC's Access Control and Process Control modules run on an LDAP call that's worked the same way for years. It doesn't know or care what's behind that call, as long as the answer still looks the way it always has. Repoint that call to the standards-based Virtual Directory instead of rebuilding GRC's integration, and the approval chains that took a decade to get right never have to notice the backend changed. That's one piece of a bigger question every SAP-driven enterprise is asking before December 2027: how do you modernize SAP identity governance without breaking what already works? ✅Full guide linked below. https://bit.ly/4vQt6oj
- Enginsight GmbHSince 9 Sept 2026
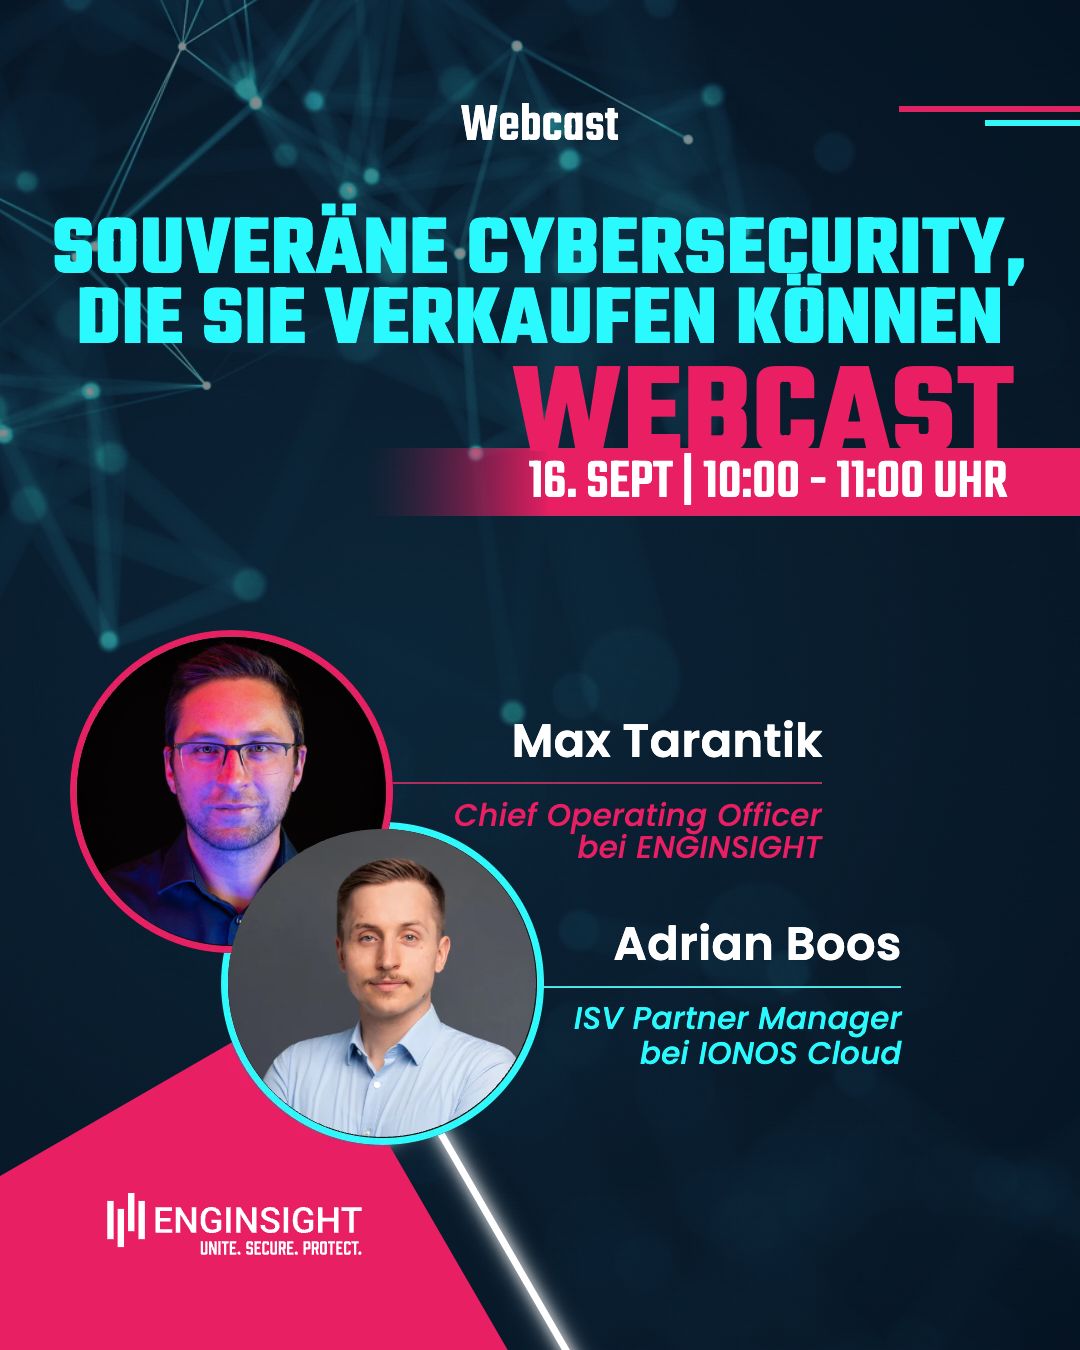
85 Prozent der Unternehmen in Deutschland halten das Land für zu abhängig von US-Cloud-Anbietern, ein Jahr zuvor waren es 78 Prozent. (Bitkom Cloud Report 2026, Juni 2026) Ihre Kunden stellen diese Frage längst nicht mehr nur sich selbst. Sie stellen sie auch Ihnen: Wo liegen unsere Daten, und wer hat Zugriff darauf? Wer als IT-Dienstleister darauf keine belastbare Antwort hat, verliert Ausschreibungen an Wettbewerber mit einem eigenen EU-Cloud-Nachweis. Seit dem 6. Dezember 2025 gilt zusätzlich das NIS2-Umsetzungsgesetz ohne Übergangsfrist. Rund 29.500 Unternehmen stehen unter BSI-Aufsicht, bei Verstößen drohen Bußgelder bis 10 Millionen Euro und die persönliche Haftung der Geschäftsführung. Am 16. September zeigen wir im Webcast „Souveräne Cybersecurity, die Sie verkaufen können", wie Sie eine eigene Enginsight-Instanz in der IONOS Cloud betreiben und damit die Systeme Ihrer Kunden absichern. IONOS betreibt seine Cloud-Plattform mit über 100.000 Servern auf sieben Rechenzentren in Deutschland und 18 weiteren in Europa, vollständig unter deutscher Jurisdiktion. → Die Architektur: eine Instanz, ein Mandant pro Kunde, Ihre Marke → Die Live-Demo: was die Plattform im Kundennetz tatsächlich sieht → Die Argumente: Souveränität und NIS2 im Kundengespräch platzieren Mit dabei: Adrian Boos, ISV Partner Manager bei IONOS Cloud, und Max Tarantik , Mitgründer und COO von Enginsight GmbH. Für Teilnehmende: bis zu 1.000 IONOS Cloud Credits für den eigenen Proof of Concept. 16. September, 10:00 bis 11:00 Uhr, online und kostenfrei. Anmeldung im ersten Kommentar. #Cybersecurity #NIS2 #DigitaleSouveränität #ITPartner #CloudSecurity
- EndaceRecorded 17 Sept 2026
Shine a light on hidden network threats with Endace’s always-on packet capture solutions. Gain total visibility and uncover the details you need to secure your network with confidence.
- EndaceRecorded 17 Sept 2026
Discover how Endace can transform your Security Analysis platforms. Bring clarity to every incident, alert or issue with a full packet capture platform that integrates with all your commercial, open-source or custom-built tools. Our always-on packet capture solutions are used by some of the world's largest public and private organizations to defend and protect some of the biggest, fastest, and most critical networks on the planet.
- Envysion, a Motorola Solutions CompanyRecorded 17 Sept 2026
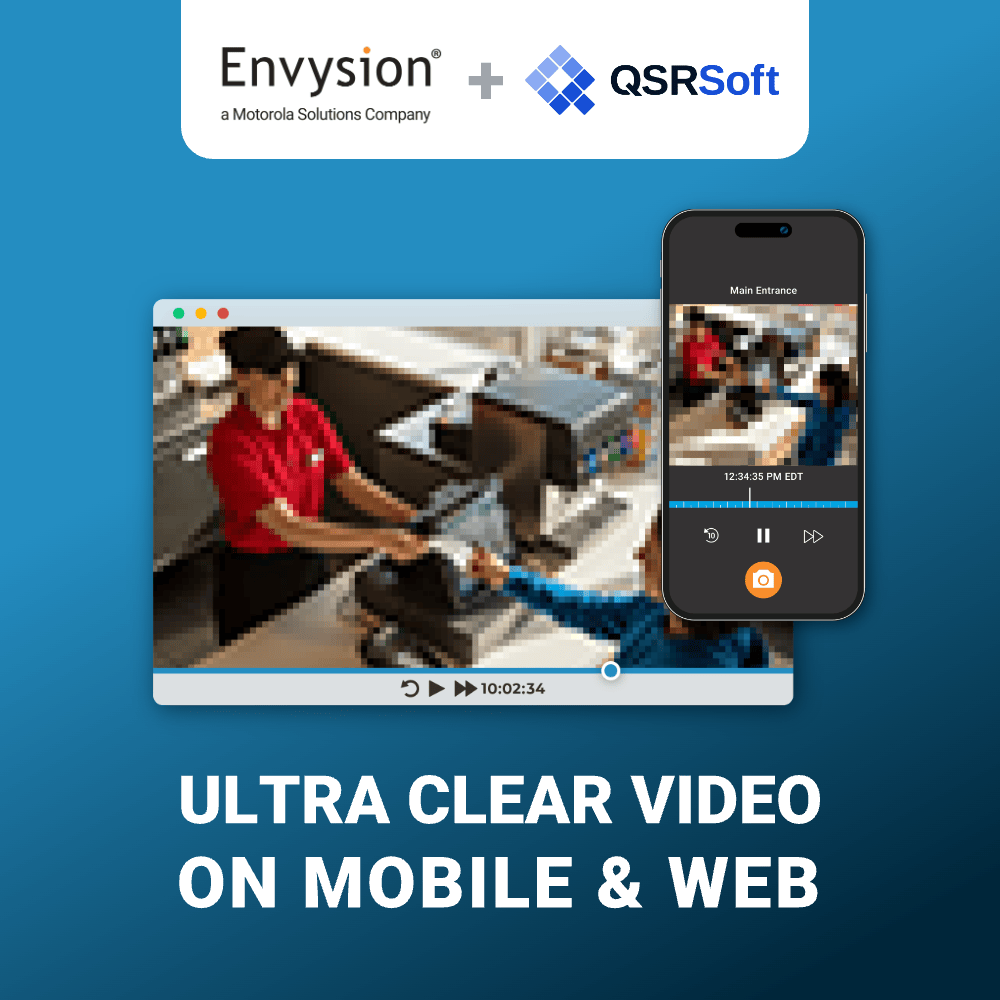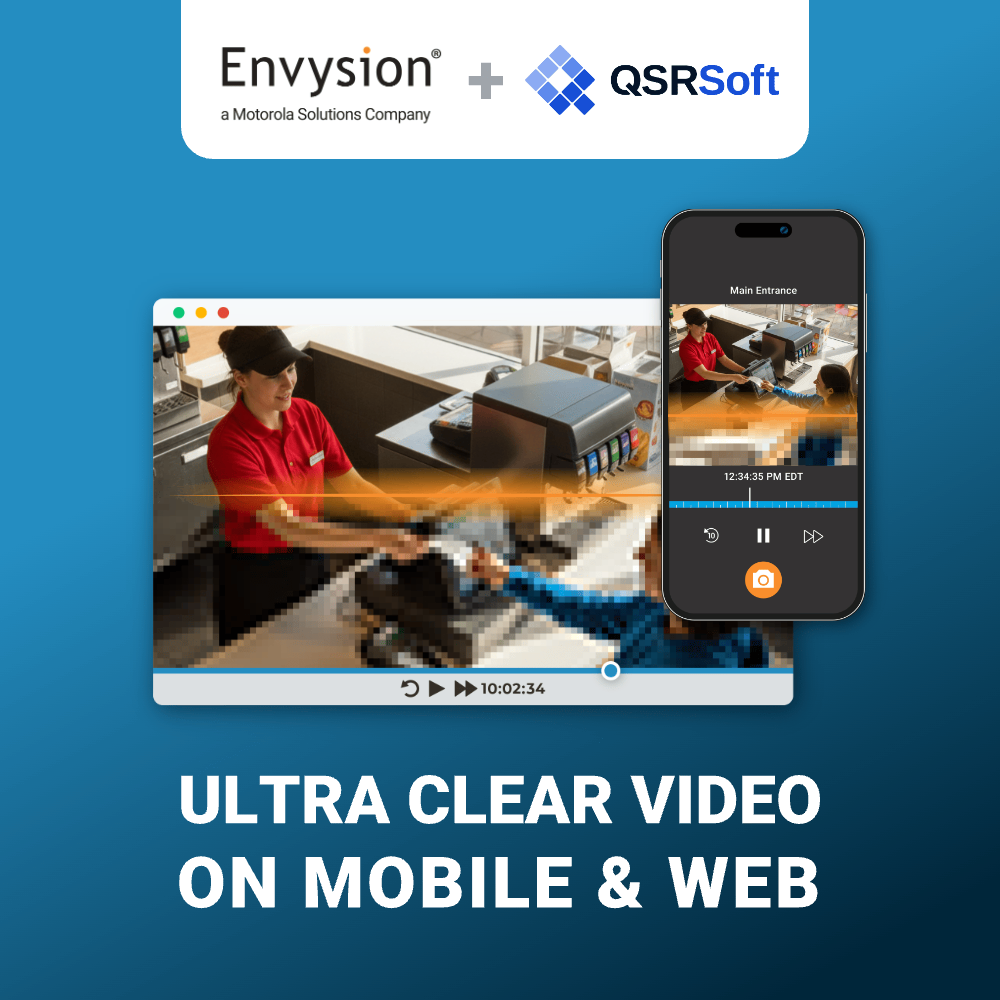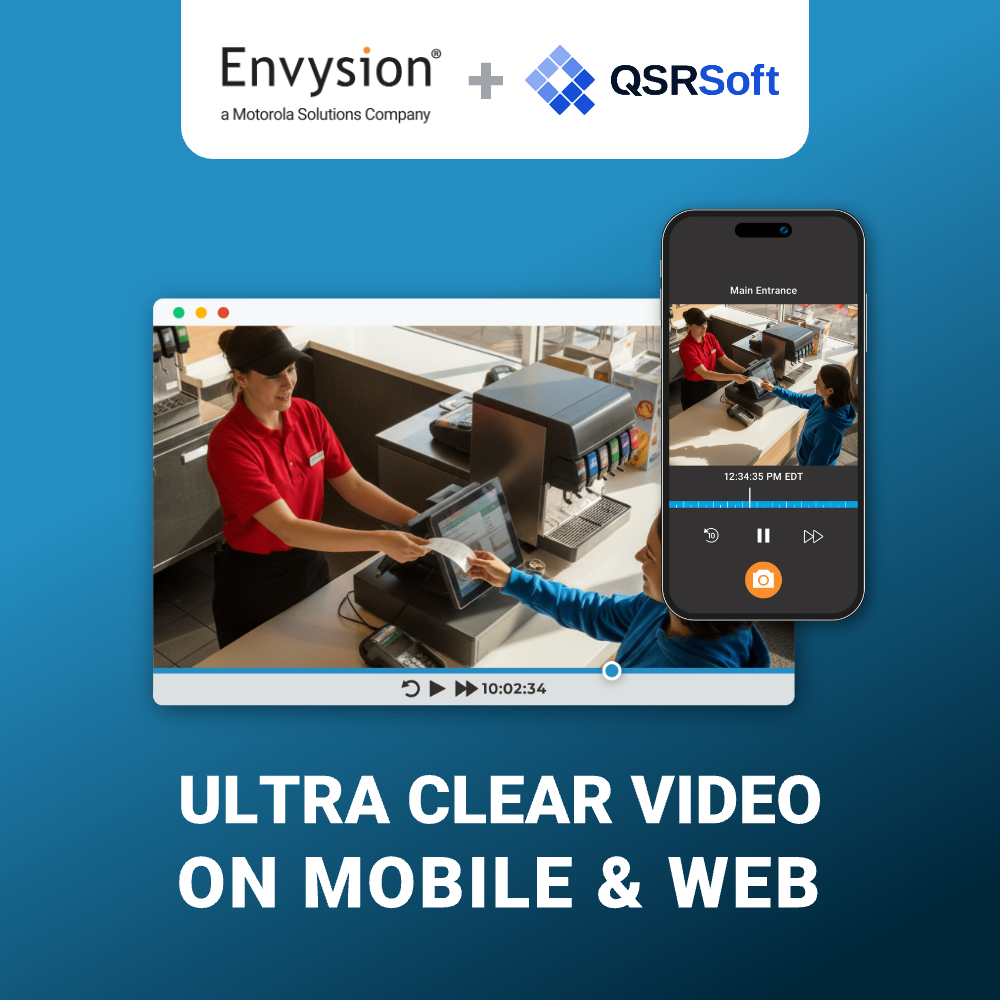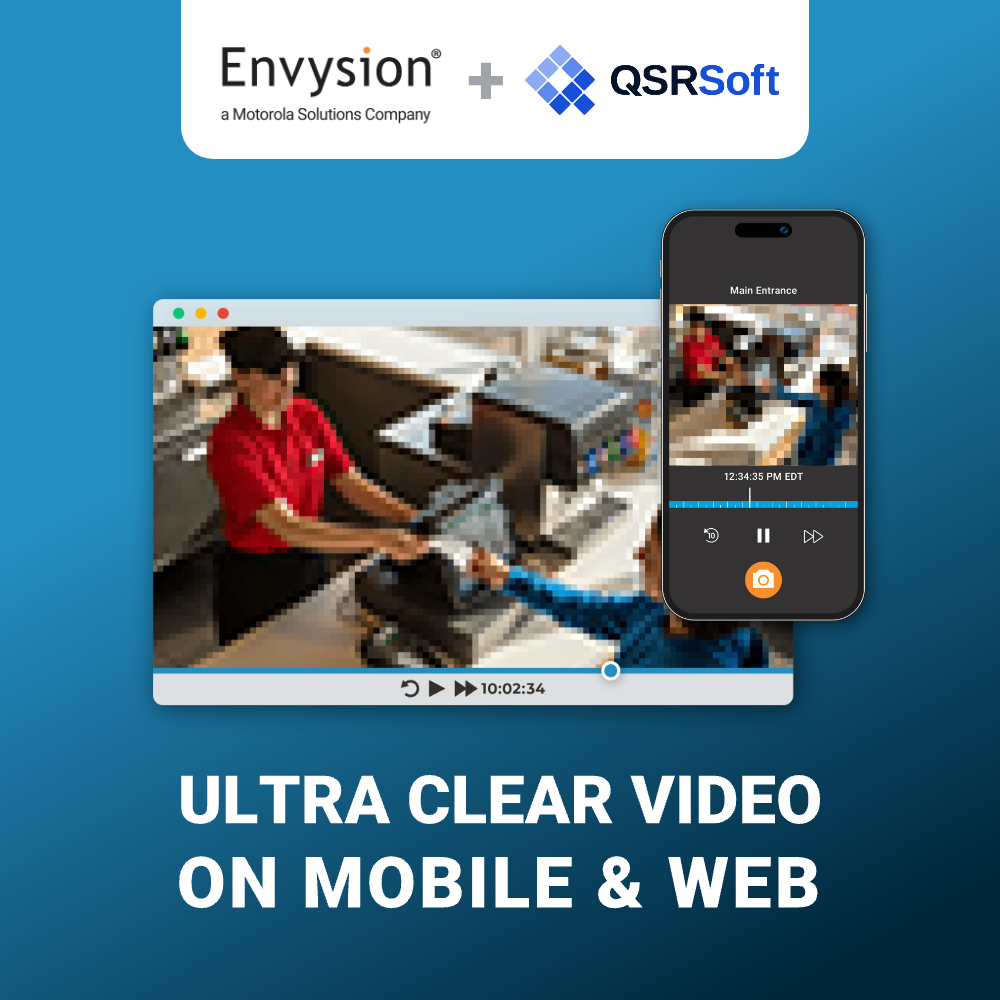
Envysion shows you clear video inside QSRSoft so you can see the full story, fast. On mobile & web.
- LogpressoRecorded 17 Sept 2026
🚩로그프레소 CTI 신규 위협 분석 사례 - '건강검진 안내 위장 스캠 주의!' 요즘 건강검진 시즌을 노린 가짜 안내문이 돌고 있습니다. 압축파일 안에 있는 ‘건강검진 xn--220b442ar7c.pdf’처럼 보이는 파일을 클릭하게 만들어, 백그라운드에서 악성 프로그램을 내려받고 정보 탈취까지 시도합니다. 🔔 이렇게 구분하세요: ✔️ 압축파일·이중 확장자 주의: …pdf.xn--jse-ln7ml83f 낯선 확장자는 열지 않기 ✔️ 링크는 직접 입력: 문자·메일의 링크 말고, 공식 사이트 주소를 직접 열기 ✔️ 발신처 확인: 처음 보는 주소·번호라면 바로 열람 금지 ✅ 자세한 분석 및 IoC 확인: https://lnkd.in/eACcqvr9 #로그프레소 #CTI #위협분석 #건강검진사칭 #피싱주의 #사이버보안 #SecOps
- LogpressoRecorded 17 Sept 2026
🧑🏻🏫 로그프레소의 Gartner Security & Risk Management Summit 2025 UK 참관기 4부에서는 ‘에이전트 AI’에 대해 다룹니다. ✔️ 왜 자율성이 곧 공격 표면이 되는가 ✔️ 멀티 에이전트 환경에서 발생하는 새로운 공격 시나리오 ✔️ 에이전트 관리 전략 이제 AI는 단순 '챗봇'이 아니라, 스스로 판단하고 실행하는 에이전트 단계로 넘어가고 있습니다. 하지만 자율성이 커질수록 공격 표면도 함께 폭발적으로 늘어나고, CISO 입장에서는 "언제, 어디까지, 어떻게 써야하는가"라는 새로운 숙제가 생겼습니다. 링크에서 자세한 내용을 확인해보실 수 있으며, 다음 편은 AI와 관련된 거버넌스, 법률로 이어집니다. 📌 4부 전문 읽기: https://lnkd.in/gi8b-aV8 #로그프레소 #Gartner #AI보안 #SecOps #자율형SOC #거버넌스 #보안운영
- Ensign InfoSecurityRecorded 17 Sept 2026
Speed is vital—but only if it’s secure. Explore how to embed layered protection into fast-moving cloud environments. From Zero Trust and intelligent automation to human readiness and real-world simulation, Ensign equips organisations with practical tools to stay secure without slowing down innovation. Download the eGuide now to unlock the full potential of your cloud—securely and confidently.
- Ensign InfoSecurityRecorded 17 Sept 2026
Moving to the cloud is just the beginning—securing it is what drives true agility. This eGuide covers best practices across identity, workload protection, threat response, and governance. Discover how Ensign empowers enterprises with unified visibility, proactive defence, and resilient cloud controls that scale with your needs. Download the eGuide now and turn cloud complexity into cyber confidence.
- ElisityRecorded 17 Sept 2026
Legacy NAC requires 14+ FTEs, constant change windows, and years of VLAN management. Elisity reduces specialized resources by 85% and costs by 75%—with a single cloud console for all sites. Discover the modern NAC alternative.
- ElisityRecorded 17 Sept 2026
That's what Andelyn Biosciences said after switching from legacy NAC to Elisity. Deploy Zero Trust microsegmentation in 2 weeks—no agents, no 802.1X, no infrastructure overhaul. See why enterprises are replacing their NAC.
- CyberArrowSince 12 Feb 2026
Take control of your business's regulatory responsibilities with CyberArrow GRC—a cutting-edge tool designed for modern enterprises aiming at excellence without compromise. Trusted by industry leaders like Emirates Airlines and Bupa Global, our platform ensures measurable ROI through seamless integration into existing systems. Start your journey with a free demo today!
- CyberArrowSince 12 Feb 2026
Discover how CyberArrow simplifies security and compliance for your organization. With our innovative solutions, automate adherence to ISO 27001, SOC 2, PCI DSS, HIPAA, GDPR, and 50+ more standards effortlessly—saving you time and resources. Experience the power of our SaaS offerings like Compliance Automation™ and Awareness™ firsthand with a free demo.
- E-TRUSTRecorded 16 Sept 2026
Sem governança de identidades, não existe controle real. Você perde visibilidade, rastreabilidade e capacidade de resposta. Quem acessa? O que acessa? Por quanto tempo? Se essas respostas não são imediatas, o risco já está instalado. O HORACIUS IAM da E-TRUST transforma a gestão de acessos em um processo estruturado, auditável e baseado em risco, alinhado às melhores práticas e exigências regulatórias.
- PreludeRecorded 16 Sept 2026
Most SMS invoices are a black box. You pay the bill but you have no idea what you're actually paying per route, per country, per message. We fix that.
- PreludeSince 28 Apr 2026
Scaling Europe Top 50. We’re in. 🖤 Proud to be listed among Europe’s fastest-growing tech companies. This list is based on real data and independent analysis, which makes it even more meaningful. Proud to be alongside such an inspiring group of companies! ✌
- EC-CouncilSince 13 Feb 2026
Step into the highest tier of cybersecurity leadership with the globally recognized CCISO certification from EC-Council. Develop executive-level governance, risk, compliance, and security program management skills trusted by top organizations worldwide. If you're ready to move beyond technical expertise and demonstrate true C‑Suite strategic capability, this is your path.
- EC-CouncilSince 17 Feb 2026
Advance your cybersecurity career with the EC‑Council CCISO program, built for professionals aspiring to lead mission‑critical security initiatives. Strengthen your ability to design policies, manage risk, lead teams, and influence business decisions at the highest level.
- DTiQSince 3 Jun 2026
A packed drive-thru lane should mean high volume, not high abandonment. If your speed of service is lagging, customers are pulling away before they even reach the order screen. Pre-lane abandonment is a silent profit killer because traditional metrics often miss the guests who chose not to wait. Watch this webinar replay to learn how to pinpoint the hidden operational bottlenecks clogging your lanes and implement data-driven strategies to keep cars moving. Click to access the replay and protect your drive-thru revenue.
- EDAMAME TechnologiesSince 16 Jun 2026
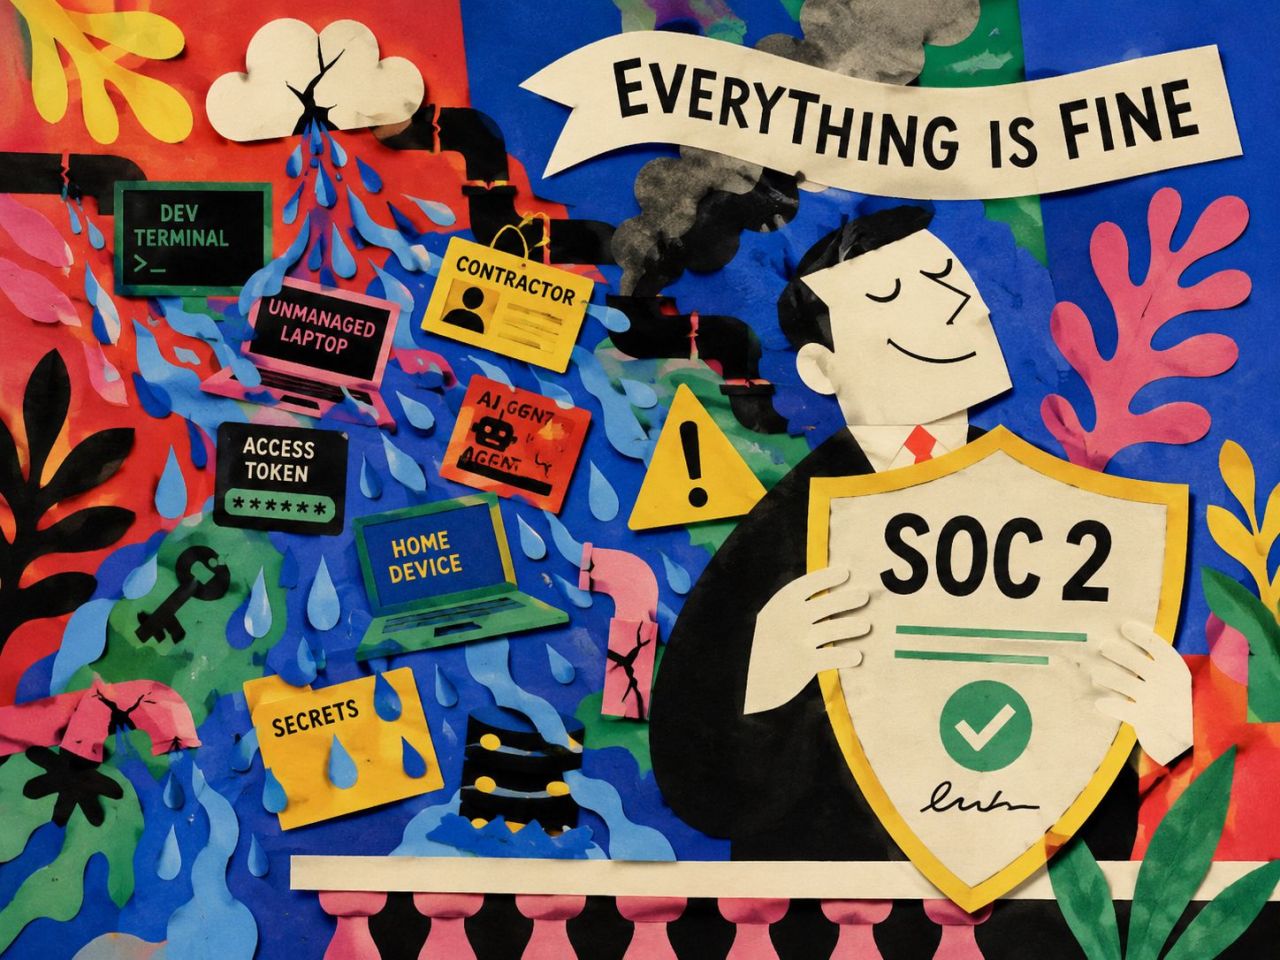
“We are SOC 2 compliant.” So were GitHub and many other serious engineering organisations before they were hacked. That is the uncomfortable point. SOC 2 is not a force field. It is an attestation that your controls exist and operate over a defined scope. But the real scope has moved. It is no longer only the corporate laptop enrolled in MDM/UEM. It is BYOD. It is BYOPC. It is contractors. It is developer workstations with admin rights. It is CI/CD runners. It is coding agents with shell access and MCP-connected tools. The old recipe — enrol the fleet in MDM, collect the screenshots, pass the audit — was built for a simpler machine boundary. That boundary is gone. The question for 2026 is sharper: Can you continuously prove that every machine touching code, secrets, customer data or production systems is trustworthy at the moment it acts? That is what we wrote about here: https://lnkd.in/eG8pCEBF Minh-Anh D., Quentin Vedrenne, Raj Mallempati, Amol Kabe, Frederic Griffoul, Kenny To, Ehsan Ahmadi, John Martin, Freddy Mallet, Antoine Clerget, Dan Newman, Mark Day
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.