LinkedIn image ad examples
1,341 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- Fluid AttacksRecorded 19 Sept 2026
¿Listo para demostrar que eres el mejor pentester de LATAM? 💥 Del 24 al 25 de enero tendrás 24 horas para poner a prueba tu talento, descubrir vulnerabilidades y competir por el gran premio de USD 1.000 en el CTF de Fluid Attacks - Reto LATAM 2026. 🗓 8:00 a. m. (UTC -5) 👤 Competencia individual ⏳ 24 horas de retos 💰 1 ganador: USD 1.000 Regístrate ya: https://lnkd.in/eDJ7qDUV
- Fluid AttacksRecorded 19 Sept 2026
Mostre que você é o pentester mais afiado da LATAM! 💥 De 24 a 25 de janeiro, serão 24 horas de puro hacking para descobrir vulnerabilidades, superar desafios e disputar o prêmio de USD 1.000 no CTF da Fluid Attacks – Desafio LATAM 2026. 👤 Competição individual ⏳ 24 horas ininterruptas de desafios 💰 1 vencedor leva USD 1.000 Garanta sua vaga e confira as regras do evento! 🚀 🔗 https://lnkd.in/eRJp-UtK
- Fideo IntelligenceRecorded 19 Sept 2026
Excited to share we'll be showcasing Fideo Verify live on stage at VentureTech 2025 next week: https://lnkd.in/gWHED4Kw The live demo of Fideo Verify will showcase how credit unions can approve good members instantly while blocking synthetic identities for fast, secure account openings and loan originations. “Credit unions need modern solutions that match the sophistication of today’s fraud landscape,” said Christopher Harrison, CEO of Fideo Intelligence. “Fideo Verify gives credit unions the ability to provide seamless member experiences without compromising security. We’re excited to show VentureTech attendees how our unified approach stops synthetic identities while keeping onboarding fast and frictionless.” #VentureTech #CreditUnions #CUs #FraudPrevention #IDV #CUSO
- Fischer IdentityRecorded 19 Sept 2026
🤔 Making Sense of the Latest IGA Guidance Analyst reports highlight trends in Identity Governance and Administration (IGA) like intelligent automation, faster deployment, cloud-first design, and specialist vendors. At Fischer Identity, these are not new discoveries. They have guided how we deliver results for over twenty years. In the seventh blog of our series, "From Buzzwords to Business Value: What the Analysts Missed," Mark C. shows how Fischer has already achieved what analysts now call the future of IGA. Modern IGA is not about terminology. It is about measurable results: reduced risk, lower cost, improved compliance, and faster business outcomes. At Fischer Identity, innovation is not theory. It is a track record. 🔗 https://buff.ly/xYv7X4u #IdentityGovernance #IGA #IAM #FischerIdentity #CyberSecurity #Leadership #DigitalTransformation #Compliance #RiskManagement #Automation #HybridIAM #CloudSecurity
- Fractional CISORecorded 19 Sept 2026
One free eBook, five short chapters, +10 to your SOC 2 audit saving throw.
- Fractional CISORecorded 19 Sept 2026
SOC 2 need not be daunting. In this free eBook, get actionable knowledge to help you scope, estimate, prepare, and ultimately succeed in your SOC 2 audit. ✅
- Fischer IdentityRecorded 19 Sept 2026
🤔 Making Sense of the Latest IGA Guidance Every journey has a beginning. Over the past several weeks, Fischer Identity has shared an eight-part blog series designed to help executives and technology leaders make sense of the noise around Identity Governance and Administration (IGA). Our final blog in the series, by Mark C., “The Beginning of the Journey: Turning Insight into Action,” reflects on the lessons from this series and offers practical guidance for organizations that are beginning or redefining their IAM and IGA programs. Identity governance does not have to be complex or intimidating. With the right approach, the right partner, and the right framework, it becomes a foundation for business efficiency, trust, and resilience. At Fischer Identity, we believe that successful identity governance begins not with technology, but with clarity, purpose, and partnership. 🔗 https://buff.ly/IOxuot0 #IdentityGovernance #IGA #IAM #FischerIdentity #Leadership #DigitalTransformation #CyberSecurity #Compliance #Automation #RiskManagement #CloudSecurity #ExecutiveLeadership
- Fortified Health SecurityRecorded 19 Sept 2026
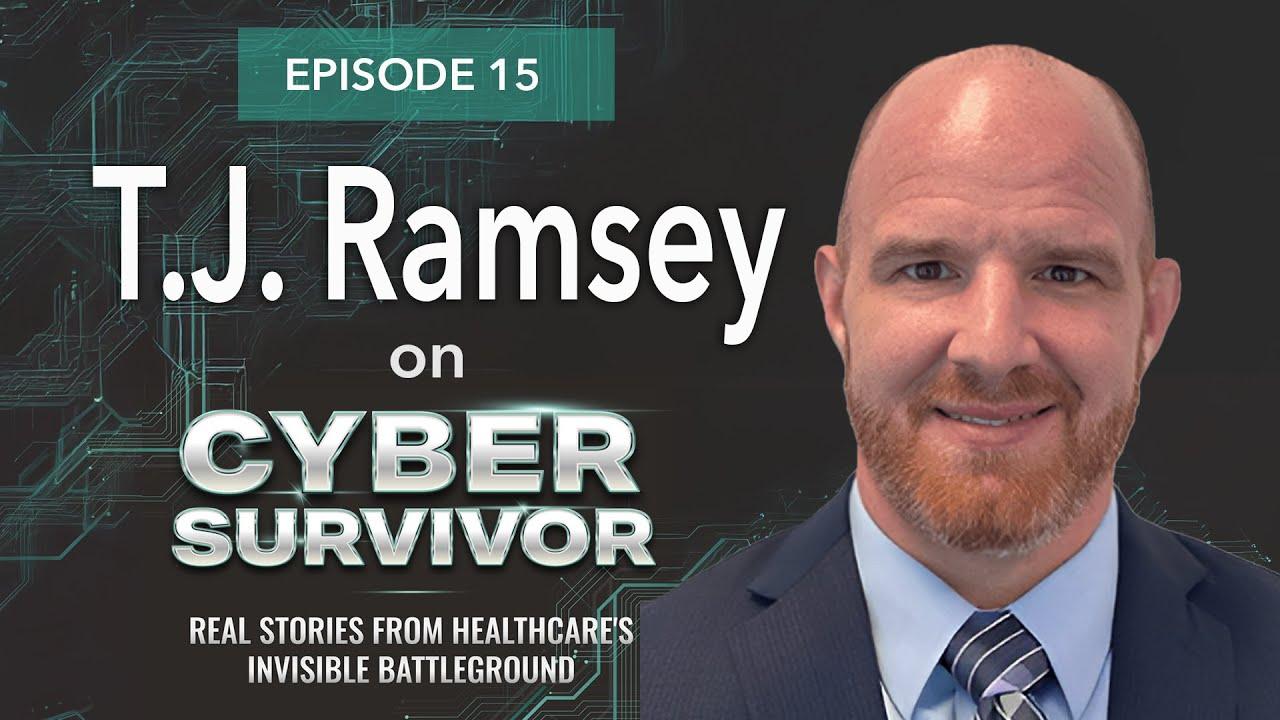
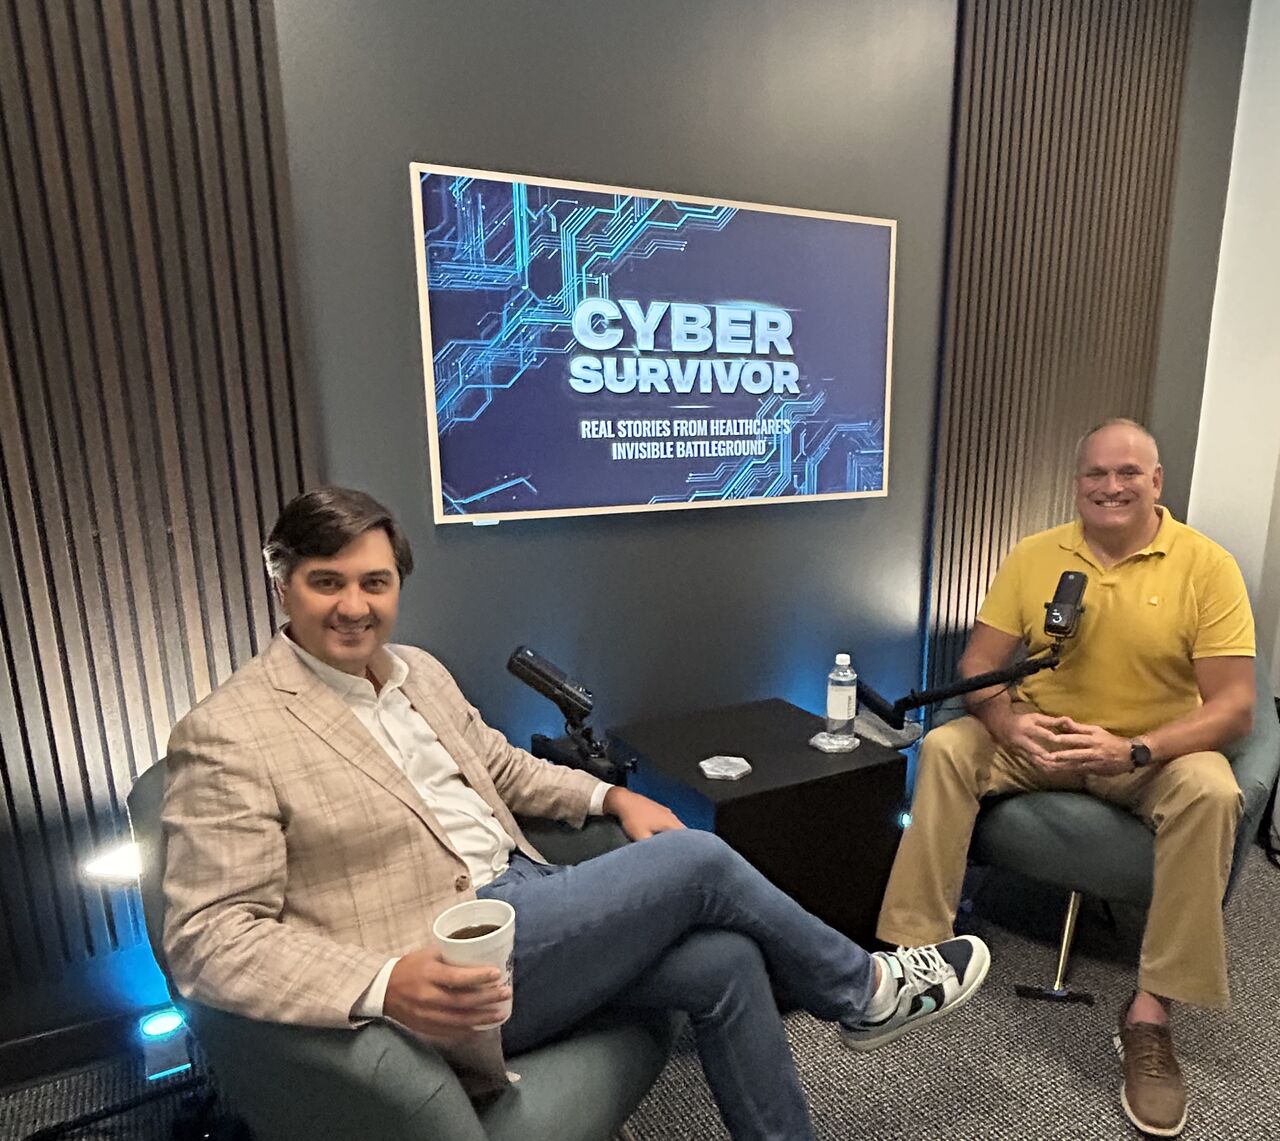
I had an amazing conversation with Tim R. about what it's like on the front lines of a ransomeware negotiation. From ransom demands and attacker tactics to the emotional toll on hospital leaders, he shares the reality of the situation and the best way to protect patient safety when every second counts. Don't miss episode 15 of Cyber Survivor here: https://lnkd.in/dCd9YHY8
- Fortified Health SecurityRecorded 19 Sept 2026
Check out my first Cyber Survivor live from our new studio! We kicked things off in person with Scott E. Augenbaum, former FBI agent, author, and all-around cybersecurity truth teller. We dug into how cybersecurity has evolved and why your mindset might be the most important tool in preventing a cyber attack. Watch here: https://lnkd.in/gGpuym9d
- FocaldataRecorded 19 Sept 2026
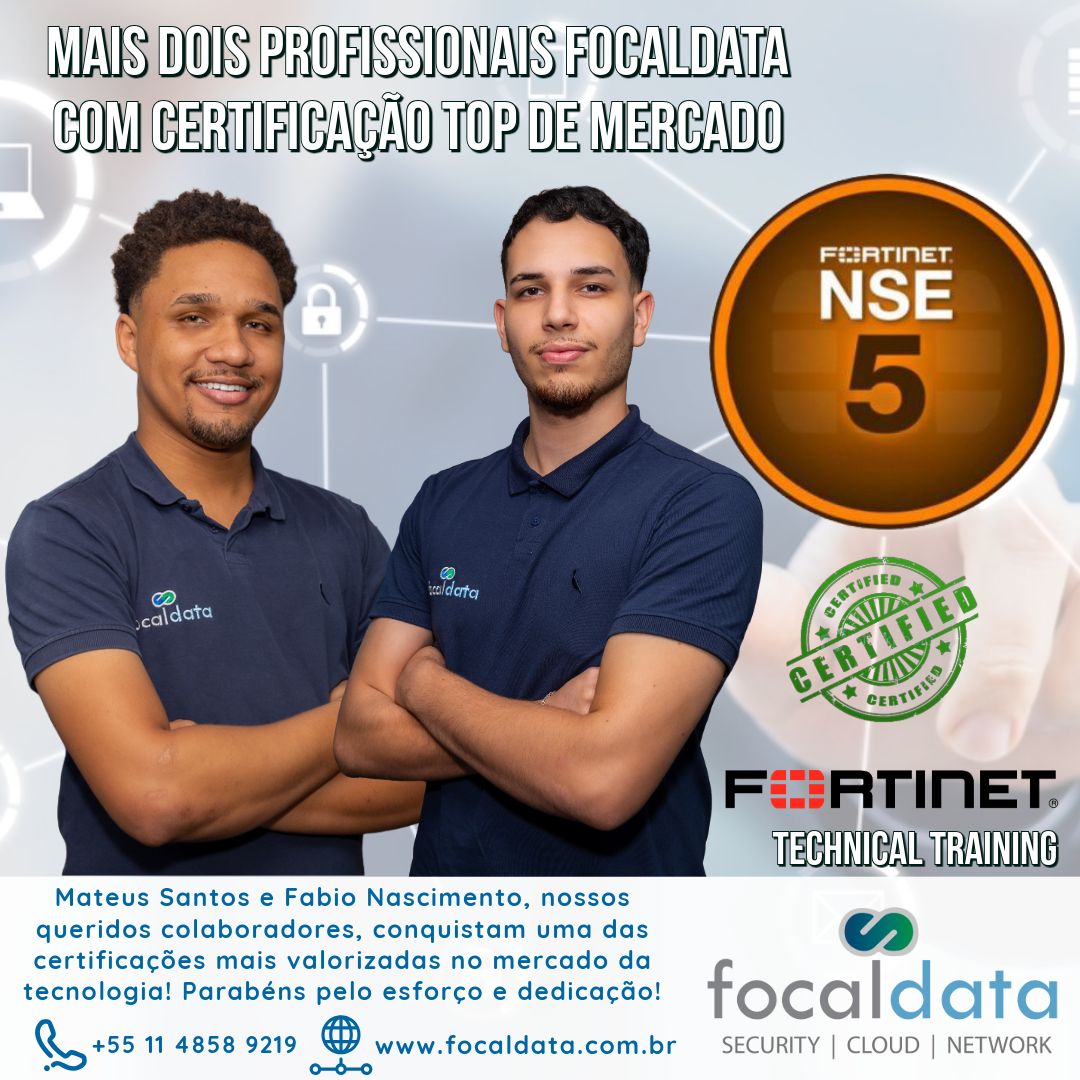
Parabenizamos Mateus Santos e Fabio Nascimento por conquistarem o título FCP (NSE5), uma certificação de alto nível da Fortinet que reconhece profissionais capazes de administrar, otimizar e fortalecer ambientes complexos. Essa vitória demonstra o compromisso contínuo de ambos com excelência técnica, atualização constante e profundo domínio das plataformas Fortinet, especialmente em gestão centralizada e políticas de segurança. Para a Focaldata, esse avanço representa um reforço direto na qualidade dos serviços entregues e na confiança dos clientes. Com especialistas certificados nesse nível, a empresa amplia sua capacidade de oferecer soluções mais robustas, seguras e alinhadas às melhores práticas do mercado. É um marco importante que fortalece nossa equipe e eleva ainda mais o padrão de entrega em cada projeto. Focaldata. Todos Nós Estamos Conectados. www.focaldata.com.br #focaldatabr #cibersegurança #fortinet #fortimanager #culturadeprevenção #posturadeprevenção
- FocaldataRecorded 19 Sept 2026
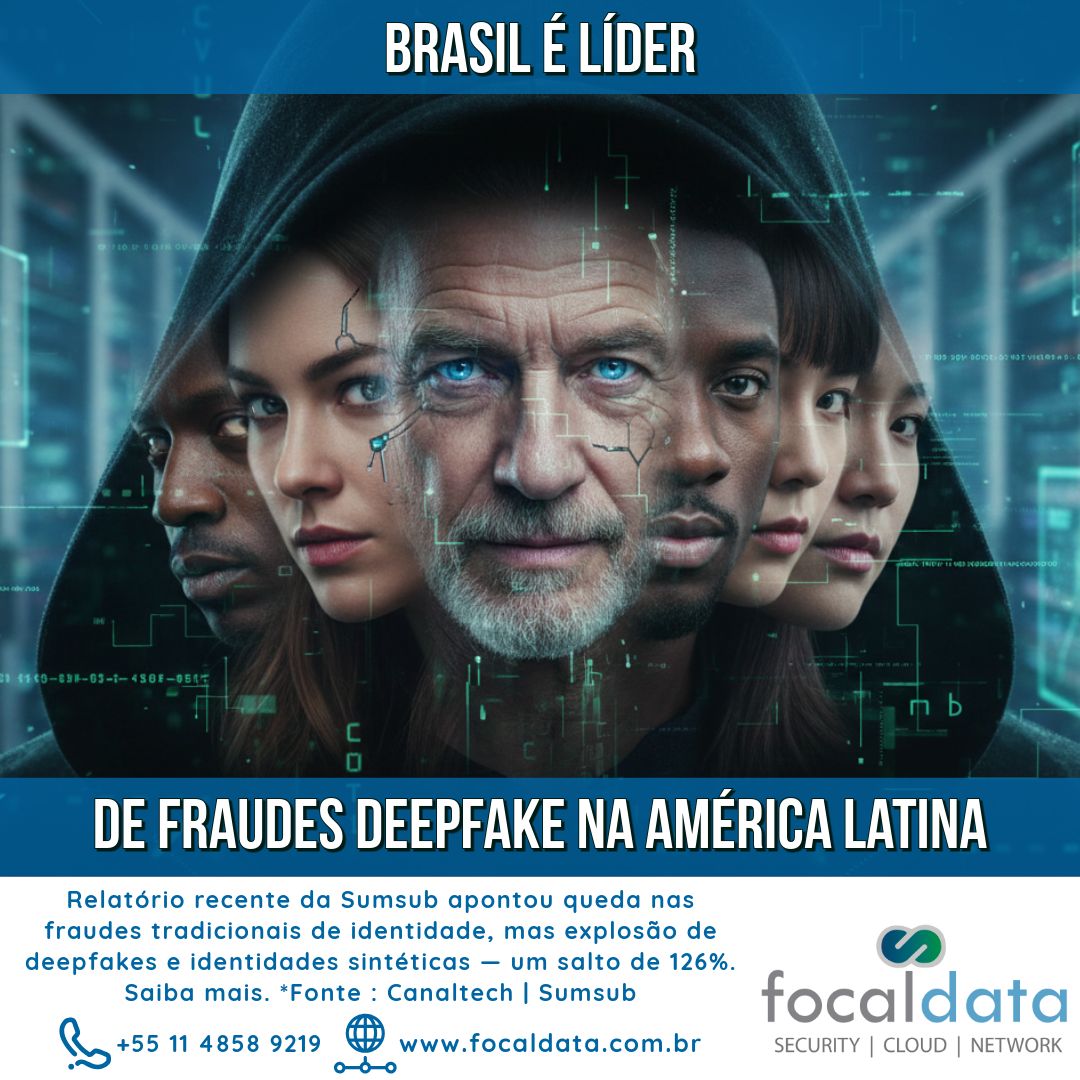
A Sumsub divulgou seu 5º Identity Fraud Report 2025-2026, resultado da análise de mais de 4 milhões de tentativas de fraude e de entrevistas com profissionais de risco e usuários finais. O relatório traça um retrato atualizado do cenário global de golpes digitais, mostrando como as ameaças evoluíram e quais setores se tornaram mais vulneráveis. Apesar da ligeira queda na taxa geral de ataques, a complexidade das fraudes disparou neste período. O estudo revela que os criminosos deixaram de focar apenas na falsificação de documentos e passaram a manipular o contexto tecnológico em si — alterando dados de dispositivos, fluxos de vídeo e chamadas de API — para iludir sistemas de verificação. Como resultado, o percentual de fraudes altamente sofisticadas subiu de 10% para 28% em apenas um ano. Esse avanço está ligado à popularização de ferramentas de golpe prontas, como serviços de phishing por assinatura, que democratizaram o acesso ao crime digital. Na América Latina e no Caribe, o impacto foi ainda mais intenso: as fraudes cresceram 13,3% entre 2024 e 2025, segundo o levantamento. A maioria das empresas relata golpes mais elaborados impulsionados por IA, e quase metade delas sofreu algum tipo de fraude no último ano, com o phishing atingindo todas. Do lado dos usuários, a exposição também aumentou, com redes sociais invadidas, acessos governamentais comprometidos e abordagens criminosas cada vez mais frequentes. O Brasil apresentou um quadro misto, com queda nas fraudes tradicionais de identidade, mas explosão de deepfakes e identidades sintéticas — um salto de 126%, que coloca o país como líder regional nesses ataques. Em outras nações latino-americanas, como Guatemala e México, o crescimento de deepfakes ultrapassou 400%. Embora a maioria das empresas já utilize modelos híbridos de prevenção, a dependência de processos manuais ainda limita sua capacidade de resposta rápida. O relatório também mostra que fraudes criadas com IA avançam rapidamente: em 2025, 1 em cada 50 documentos falsos foi gerado por ferramentas de IA generativa, e a tendência é que esses agentes automatizados consigam executar golpes completos em breve. Diante desse cenário, especialistas afirmam que as organizações precisarão acelerar a adoção de defesas impulsionadas por IA — como biometria comportamental, verificações em múltiplas camadas e monitoramento constante — para enfrentar um ambiente de ameaças cada vez mais sofisticado. Focaldata. Tudo Está Conectado. www.focaldata.com.br #cibersegurança #fortinet #infoblox #trendmicro #gigamon #crowdstrike #segura #transmitsecurity #vigilant #zadara #paloalto #f5 #cloud4wi #acronis #culturadeprevenção #posturadeprevenção
- FrenosRecorded 19 Sept 2026
Most OT teams have intrusion detection. Far fewer have intrusion understanding. Detection tells you something happened, but understanding tells you what it means. That difference is everything in industrial environments. An alert can show you a suspicious login, a blocked connection, or a policy violation. But it can’t show you: → How the attacker moved → What systems they touched → Which paths were available → What could have happened next → Or how close they came to impacting operations In OT, alerts without context create noise. Context without consequence creates false confidence. True resilience comes from understanding movement, intent, and impact, not just triggers. That’s why modern OT security is shifting toward adversary modeling. It gives operators a clear picture of how an intrusion unfolds, how far it can go, and what needs to be fixed before it matters. Detection tells you you’re under attack. Understanding tells you whether you’re vulnerable.
- FrenosRecorded 19 Sept 2026
In most OT environments, the biggest blind spots aren’t PLCs or HMIs. They’re the transient devices that come and go without leaving a trace. Think about the equipment that enters your environment every week: → Vendor laptops used for quick troubleshooting → Rental hardware that connects for long enough to fix an issue → Contractor tablets, USB adapters, and diagnostics gear → Temporary VPN access spun up for a single job Individually, they seem harmless... In combination, they create an unmanaged attack surface that bypasses traditional OT visibility. And here’s the real challenge: These devices blend into operations so naturally that teams rarely question them. They’re trusted because the people carrying them are trusted. But attackers don’t need permanent access. They just need a window. Transient devices often provide it. This is why modern OT security has to account for temporary presence, not just permanent assets. Anything that touches the environment, even for five minutes, becomes part of your risk equation. Do transient devices ever get tracked or logged in your OT environment?
- Field EffectRecorded 19 Sept 2026
Forget phishing. The real shift is AI automating exploit development at scale. This breakdown shows what’s coming and why MSPs must close patching gaps fast.
- Field EffectRecorded 19 Sept 2026
One platform. Full visibility. Field Effect MDR replaces 15+ cybersecurity tools so MSPs can deliver better protection with less manual effort.
- EvinaSince 9 Feb 2026
Evina is in the running for the MEFFYS Awards in the Anti-Fraud category! Thanks to the trust of our partners, Evina DCB 360 helps stop fraud, protect users, and strengthen the digital ecosystem every day. This is a great opportunity to highlight the collective work behind the scenes and the impact it has across the ecosystem. If building a safer, more sustainable digital economy matters to you, your support would mean a lot. 👉 Not a MEF member? Just tick “Sign me up” to register for MEF updates and cast your vote. Voting takes less than one minute: https://lnkd.in/e7RRz_38 Thank you to all our partners who make this possible. 🙏
- ExpelSince 28 Mar 2026
"Other MDRs couldn't translate cloud alerts into actions. They just didn't get it." Qlik needed detections across every surface. Not vendor excuses.
- ExpelSince 10 Apr 2026
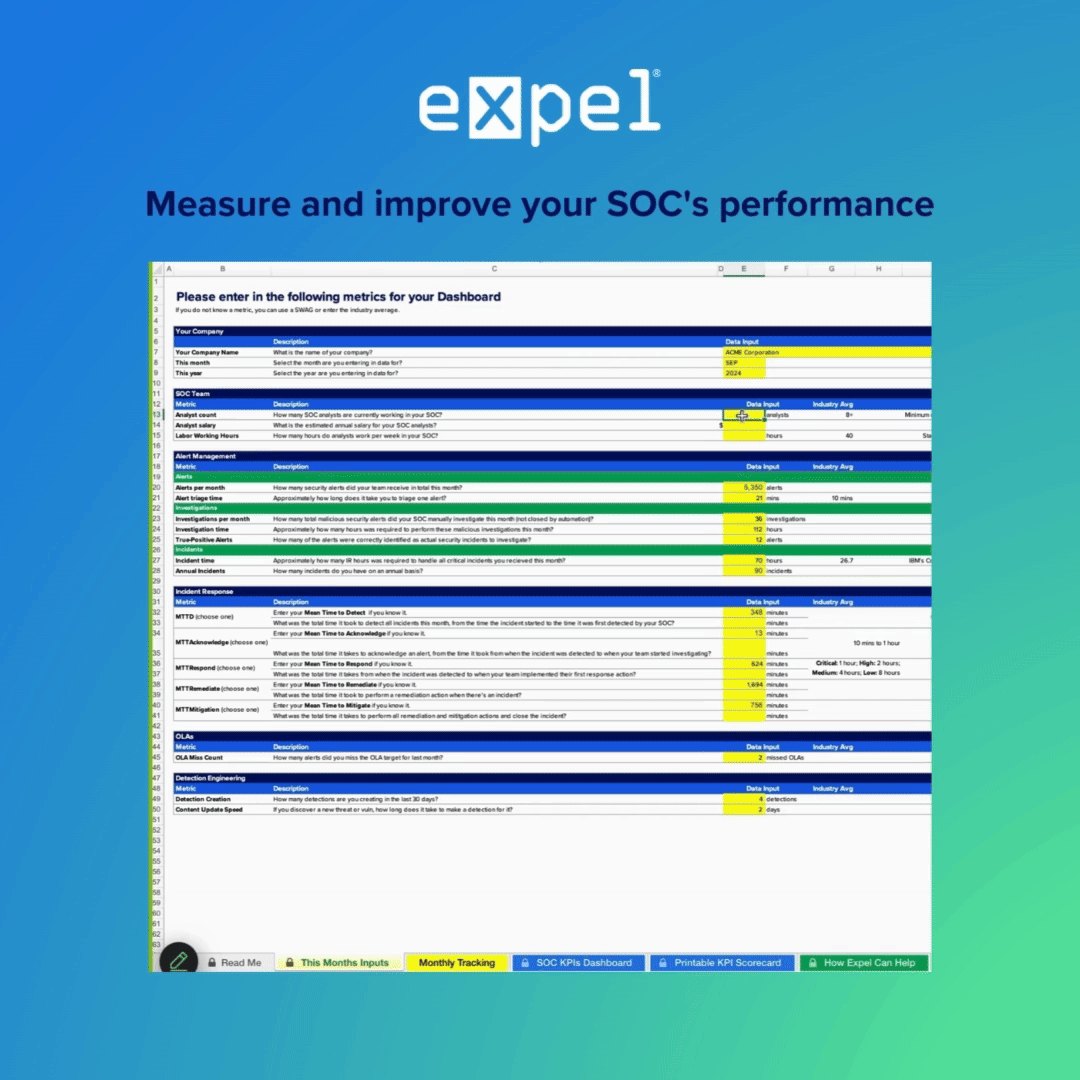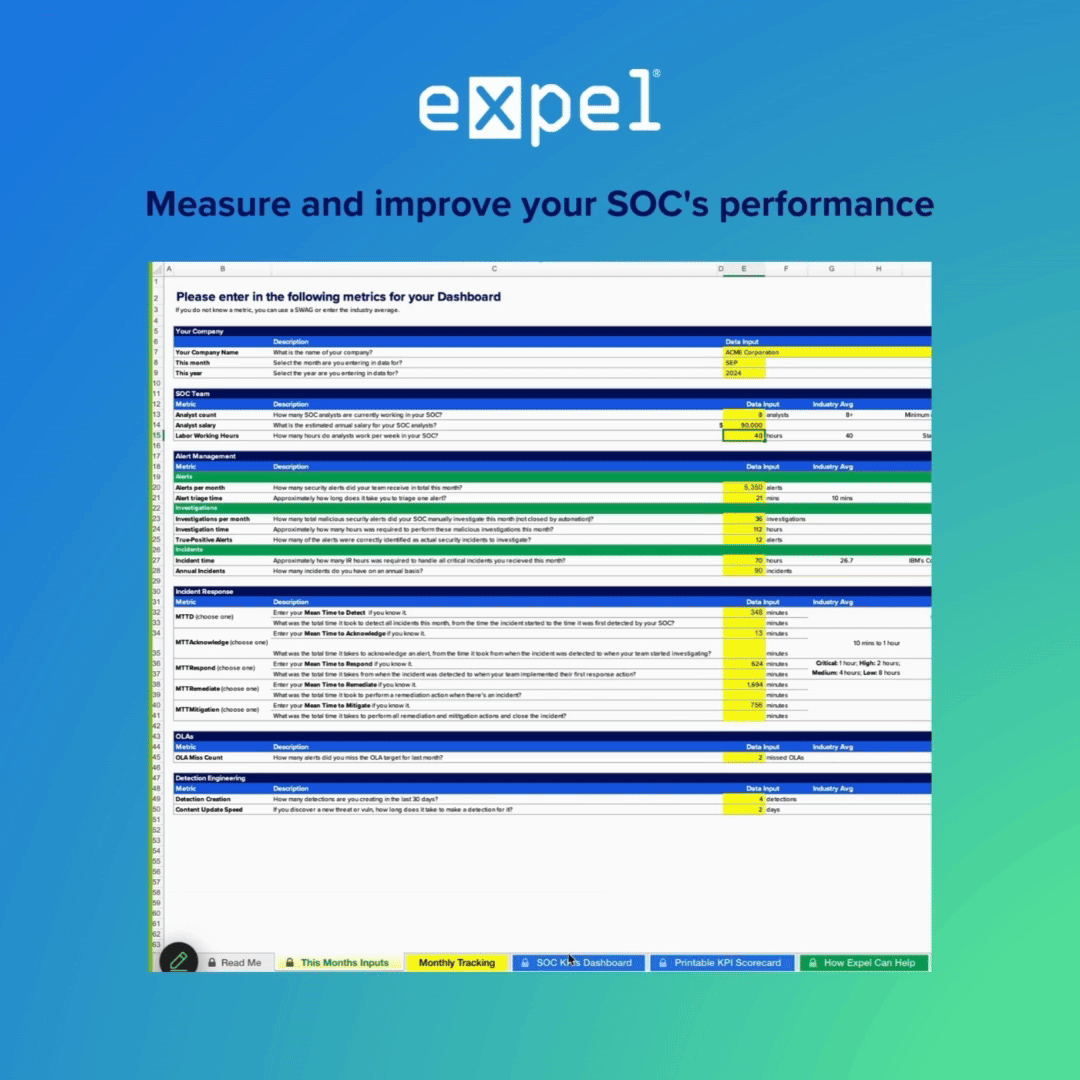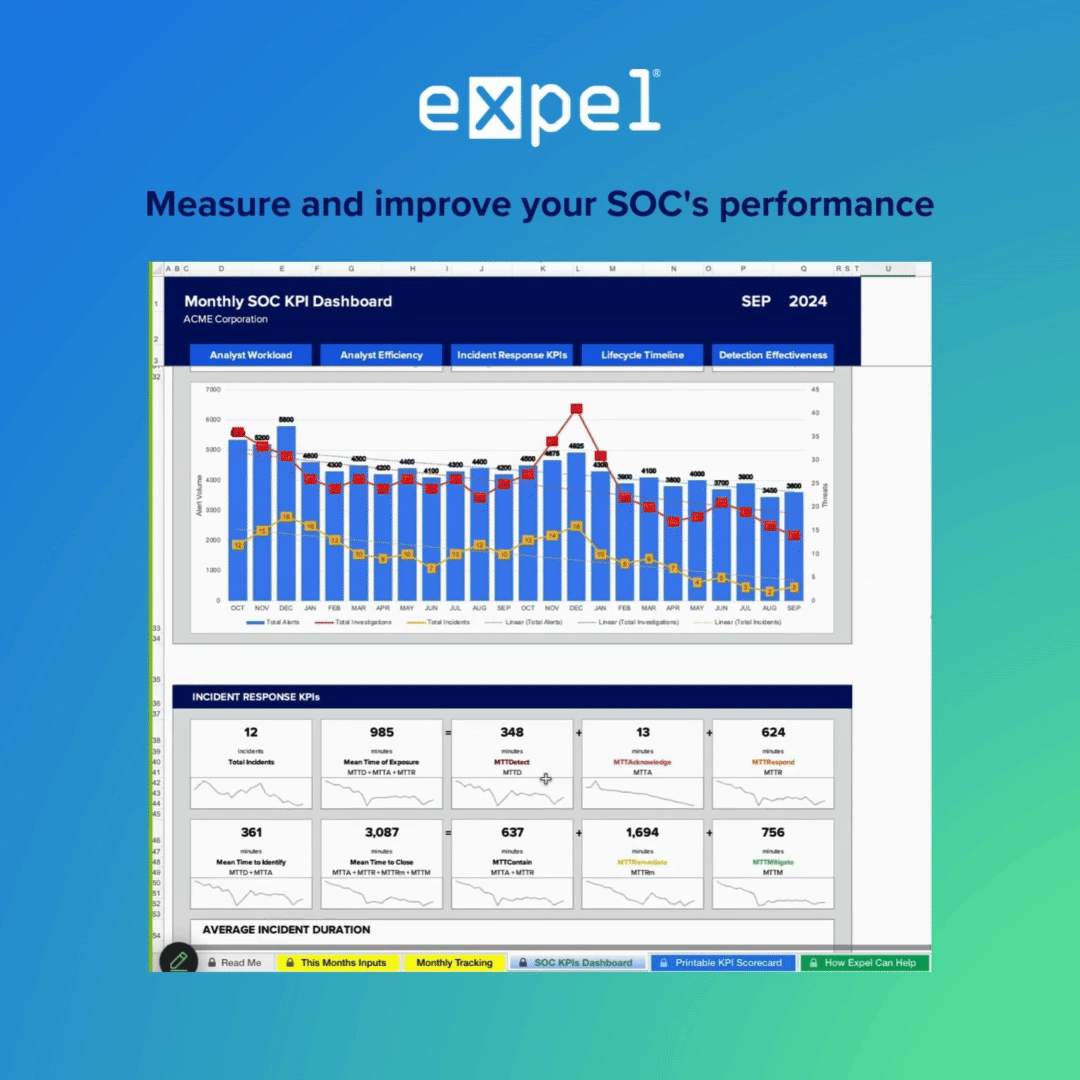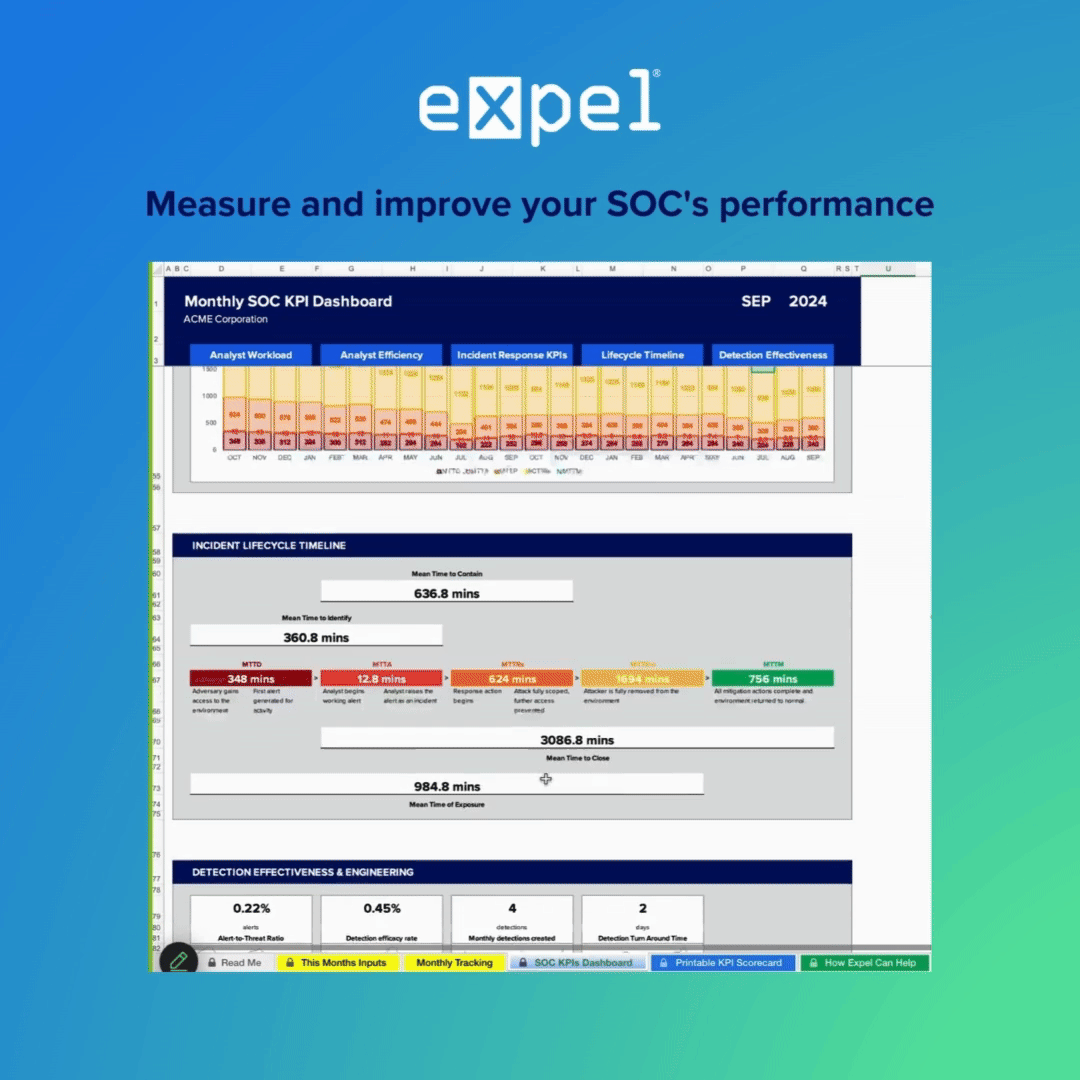
We have an inkling that a lot of SOC teams out there are currently overwhelmed. That just doesn't sit right with us. So we built a tool that'll take some of that weight off. 🧮 Use Expel's shiny new ✨ SOC metrics and KPIs dashboard tool ✨ to: • Track SOC metrics over time to identify performance trends • Discover ways to reduce your SOC’s operating costs • Identify bottlenecks slowing down your alert and incident investigations • Measure and track essential KPIs like incident response time, detection accuracy, and more
- EvinaSince 8 Apr 2026
Is your DCB strategy truly protected against 2026's malware threats? The DCB market is hitting $100 billion , but sophisticated "toll fraud" malware like Joker and Autolycos are following the money. Discover the essential technical insights to secure your payment flows and boost your conversion rates 👇
- esko-systems GmbHSince 2 Jun 2026
Was das Darknet über Ihr Unternehmen weiß❗ Zugangsdaten, Dokumente oder Backups – solche Funde tauchen regelmäßig auf, lange bevor Unternehmen davon erfahren. Im kostenfreien Erstgespräch erklären wir Ihnen, wie Darknet Monitoring funktioniert, welche Quellen wir überwachen und was das für Ihr Unternehmen konkret bedeuten würde.
- esko-systems GmbHSince 2 Jun 2026
Wissen Sie sicher, dass Ihre Unternehmensdaten nicht längst im Umlauf sind? Viele Unternehmen können diese Frage nicht belastbar beantworten. Solange das so ist, bleibt das Risiko unsichtbar – und damit unkontrollierbar. Im kostenfreien Erstgespräch zeigen wir Ihnen, wie Sie externe Bedrohungshinweise frühzeitig sichtbar machen und was das in der Praxis bedeutet.
- F-Secure CorporationSince 22 May 2026
Every customer relationship is an opportunity to deliver more value. Meet us in Amsterdam to explore how telecom providers can offer award-winning cyber security subscriptions alongside connectivity services - creating new recurring revenue opportunities. Meeting slots are limited before and during the event. Reserve your time now.
- F9C SecurityRecorded 18 Sept 2026
Cada dispositivo clínico que opera sem controle é uma fragilidade que pode comprometer desde fluxos administrativos até a capacidade de resposta em situações de urgência. Supervisão sobre ativos não é uma camada adicional de gestão, é parte do que viabiliza o cuidado contínuo no cenário de IoMT. Descubra como eliminar riscos!
- F9C SecurityRecorded 18 Sept 2026
A cada novo equipamento integrado, o cenário IoMT se torna mais complexo e mais difícil de administrar. Sem clareza sobre o que está ativo, acessível e exposto, decisões críticas são tomadas com base em uma visão parcial da estrutura. Rastreabilidade é o que mantém tudo funcionando e dentro dos limites. Entenda como mapear seu ambiente!
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.