LinkedIn image ad examples
6 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- HackerOneSince 2 Feb 2026
🤖 vs 👨💻 The future of hacking is not binary, it’s bionic Finally getting around to sharing this after all the #BlackHatUSA2025 & #defcon33 craziness! Published this Q&A piece last week about the HackerOne Leaderboard updates. We're now distinguishing between individual researchers and AI-driven collectives on our platform, giving everyone a clearer picture of how impact is achieved - whether through solo expertise or collective collaboration. What we're observing: - AI hackbots perform well with deterministic vulnerability classes (XSS, SQLi, Cache Poisoning) - Individual researchers still drive the majority of high-impact, business-critical findings that require creative insight - The most effective approach isn't choosing between AI and humans - it's combining them strategically This evolution reflects our core belief that diversity of approach - human creativity, AI scale, and everything in between - is what makes crowdsourced security so powerful. We're not replacing human hackers; we're amplifying what we can all accomplish. Come check out the rest of the Q&A here: https://lnkd.in/grzsHPbg
- HENNGE (North America)Since 15 Apr 2026
We’ll be at ASCII Newark next week. It’s always a great event to hear directly from MSPs about what’s actually happening across client environments — what’s working, what’s not, and where things are getting harder to manage. We’re also excited to have Dawn Sizer presenting on identity as part of the HENNGE session, sharing her perspective from years of experience working closely with MSPs. If you’re attending, stop by the booth. We’ll be running live demos of HENNGE Identity and are always up for a conversation around access, SaaS environments, and how things are evolving. Looking forward to connecting. #MSP #ManagedServices #CyberSecurity #ASCII
- HalcyonSince 6 May 2026
Twenty years chasing cybercriminals inside the Federal Bureau of Investigation (FBI)’s Cyber Division changes how you see the world. Ransomware stops looking like a tech problem - and starts looking like what it is: organized crime. Criminal entrepreneurs making deliberate decisions about who to target… and what consequences they’re willing to accept. This week, Halcyon’s Cynthia Kaiser brought that perspective to Congress - testifying before the House Committee on Homeland Security after two decades on the front lines. Her message was direct: #ransomware attacks on hospitals should be treated as terrorism - and when they result in patient deaths, prosecuted as homicide. And the case is getting harder to ignore. 👇 📈 Attacks on hospitals nearly doubled - from 238 in 2024 to 460 in 2025 ⚠️ At least 47 patient deaths have already been linked to hospital ransomware - a number that’s almost certainly higher today 🏥 Just months ago, an attack on the University of Mississippi Medical Center forced nine days of manual operations at the state’s only Level 1 trauma center This isn’t theoretical. It’s operational impact - at the worst possible moments, for the most vulnerable people. These groups have built their business model around a single assumption: that the consequences will never match the crime. Cynthia spent her career proving that assumption wrong. She’s not done. Read her full take on the blog: https://lnkd.in/eYEdQa2a #healthcare #cybersecurity
- HalcyonSince 6 May 2026
Ransomware attacks against energy and utilities are rising. The Cyber Security Resilience Bill is incoming. And Agentic AI is reshaping the threat landscape faster than most defenders can track. If you're a senior leader in the utilities and energy sector, this one's for you. Halcyon and Orange Cyberdefence are hosting an exclusive event in London this May: 🔒 Ransomware Resilience for Utilities: Technology, Regulation, Readiness 📅 Friday, 15 May 2026 | 2:00 PM BST 📍 Bain Capital Offices, 1 Mayfair Place, Mayfair, London Hear from Stuart Okin (Director of Cyber Regulation & Emerging Technologies, Ofgem) on the Cyber Security Resilience Bill and the real impact of Agentic AI on the energy sector, and from Oliver Newbury (Chief Strategy Officer, Halcyon) on how organisations can defeat ransomware before damage occurs. The session includes a live demo, peer-to-peer discussion, and social drinks and canapés on the terrace overlooking Green Park. Seats are limited. Register now: https://lnkd.in/gde9hR97
- Hacktron AISince 2 Jun 2026
Hacktron ❤️ Open Source TL;DR: If you maintain an open source project, we want to give you Hacktron Review for free. We’ve spent the past few months using Hacktron to hunt 0-days in popular open source projects. For each finding, we replayed the offending PR through Hacktron Review to see if the bug could have been caught before merge. It caught every single critical. So giving maintainers the same capabilities as attackers would otherwise use against them felt like the right thing to do. We’re currently prioritizing actively maintained projects with meaningful downstream usage. https://lnkd.in/e_V6Umps
- Hacktron AISince 1 Jun 2026
No, it's not too good to be true. Get security zen with the same code reviewer that found critical zero-days in NextJS, OpenAM, and Metabase.
- HOPLONaiSince 24 Jun 2026
Create a security programme in minutes, not months. Monitor readiness, manage policies, and keep evidence organised in one platform designed for continuous compliance.
- HOPLONaiSince 24 Jun 2026
Understand ISO 27001 requirements, identify gaps, and track progress with a toolkit built specifically for SMBs, by HOPLONai.
- HopaeSince 10 Jul 2026
Given their reusable dimension, eIDs are by far the easiest and quickest way to onboard a new user. It’s estimated that it usually takes less than 30 seconds for a new user to go through the eID-based onboarding process.
- HopaeSince 11 Jul 2026
EUDI Wallet login support can take a long time to deploy. You have to register relying parties and rework your existing CIAM architecture – all with the 2027 compliance deadline looming. With Hopae, you can deploy in minutes. As one of the first EU-registered intermediaries, we handle full relying party registration. And we let you activate EUDI Wallet login from your managed CIAM platform – without changing existing login architecture.
- HiltSince 17 Jul 2026
Security on trading infra usually costs microseconds. Hilt gives them back. Measured on an HFT firm that clears trades in single-digit microseconds.
- HiltSince 17 Jul 2026
That air-gapped CentOS server in colo. If data left tonight, would you know? Hilt watches offline machines too. Linux-native, kernel-level security.
- HENNGESince 18 Jul 2026
🇯🇵 Interested in pursuing a career in Japan? 🇯🇵 Experience Real Engineering Work as a Front-End Intern at Japan's Leading SaaS Security Platform. Eligible interns will receive full-time offers. 💻 Skilled in Typescript (React or Vue) 🇯🇵 Interested in pursuing a career in Japan 🗣 English-speaking workplace (No Japanese required) 💰Subsidized Program (Round-trip airfares, housing in Tokyo, and insurance) 📢 Role Focus: This is strictly a Software Engineering opening. There are no ML, AI, or Data Science components to this internship. We welcome applicants from all technical backgrounds, provided your primary goal for this internship is to focus 100% on core software development.
- Hornetsecurity FranceSince 28 Aug 2026
🖥 Partenaire Informatique ? Faites évoluer vos sauvegardes M365 sans vous soucier du stockage. Avec le stockage illimité, protégez vos clients sans limites. Découvrez le Backup Factor. 👇
- GuardzSince 5 Aug 2026
CRN named Guardz one of the 10 hottest cybersecurity startups of 2026, agentic SecOps built for MSPs.
- Guardsix (formerly Logpoint)Since 21 Aug 2026
Ingestion-based pricing looks fine on day one and unpredictable by renewal. Before you sign anything, read our quick guide to what drives SIEM costs up, and how to check for it before you commit.
- Guardsix (formerly Logpoint)Since 21 Aug 2026
Choosing a new vendor is bigger than swapping one logo for another. See how Guardsix keeps your data, deployment and costs on your terms, whatever's driving the move.
- Hillstrong Group Security, Inc.Since 24 Jul 2026
Are you ready to lose the cybersecurity chaos? Hillstrong's Resilion.io turns OT security strategies into live, trackable execution. Build, run, and prove your cybersecurity program across every site at scale. Our core services include: • Resilion.io OT Cybersecurity ProgramOps • OT Security Maturity Assessments • OT Risk and Vulnerability Analysis • OT Program Design and Security Architecture • Expert-Level OT Security Engineering • OT Staff Augmentation and Contract Specialists • Fractional CISO and Executive Advisory Support • OT Governance, Risk, and Compliance as a Service Visit us at www.hillstrongsecurity.com to learn more!
- Hornetsecurity FranceSince 9 Sept 2026
📈 Prestataire informatique ? À mesure que vos clients grandissent, leur sauvegarde Microsoft 365 doit pouvoir évoluer avec eux. Protégez leurs données à grande échelle avec Backup Factor. 👇
- Hiya Inc.Since 10 Sept 2026
El 87 % de los españoles no contesta llamadas de números que no reconoce. Eso significa que gran parte del esfuerzo de tu empresa en llamadas salientes puede quedarse sin respuesta antes de empezar la conversación. Hiya hace que tu empresa sea reconocible desde el primer tono, para que tus llamadas se reciban con confianza y no como un número desconocido. Más información sobre Hiya: hiya.com/es/spain
- Hiya Inc.Since 10 Sept 2026
Si a tu empresa le cuesta cada vez más que le contesten, seguramente el problema no son las llamadas en sí. Los clientes deciden si se fían de una llamada antes de descolgar, y un número que no reconocen rara vez se gana esa confianza. Hiya muestra el nombre de tu empresa en la pantalla, para que tus llamadas se reconozcan y se contesten en lugar de ignorarse. Más información sobre Hiya: hiya.com/es/spain
- Hirsch USARecorded 22 Sept 2026
Can your operators correlate perimeter, PACS, video and alarm events through a single operational timeline? If not, it may be time to reassess your security architecture. Book a consultation with Hirsch to assess event correlation, monitoring environments and operational readiness across critical infrastructure.
- Hirsch USARecorded 22 Sept 2026
Can your utility security architecture correlate perimeter detection, video and access events within a centralized operational environment? Explore how Protech and Velocity Central support high-probability detection, nuisance alarm reduction and coordinated security oversight across substations, generation facilities and distributed utility assets.
- GTB Technologies IncSince 7 Sept 2026
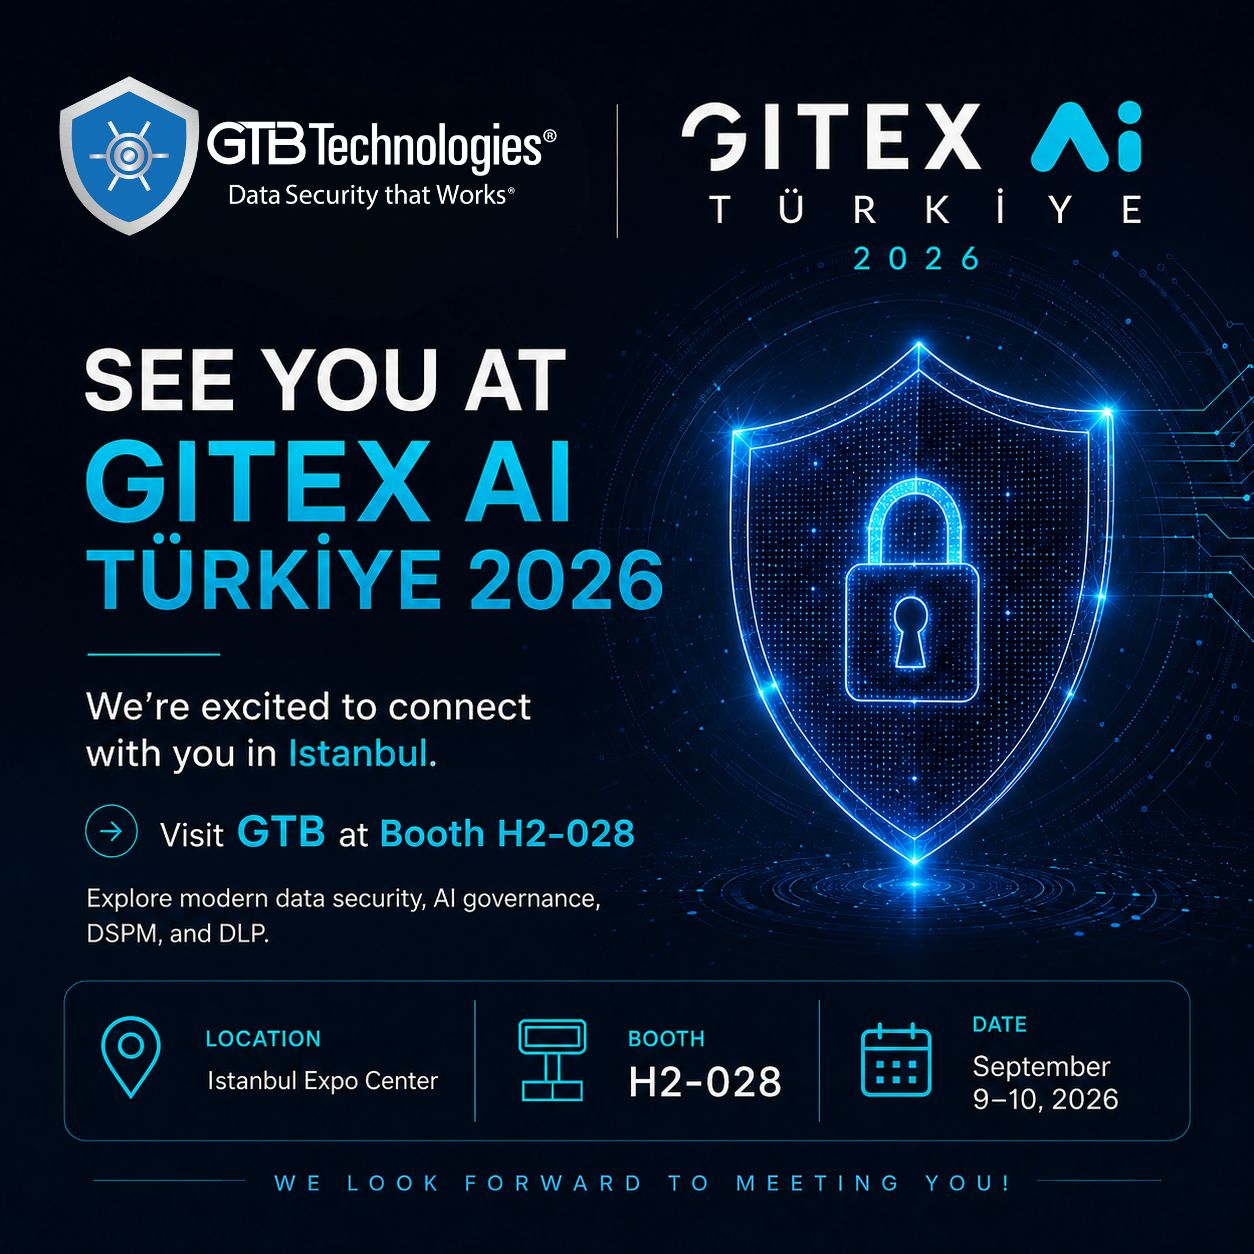
#GTBTechnologies is heading to GITEX AI Türkiye 2026! Join us in Istanbul on September 9–10 at Booth H2-028 to see how GTB is helping organizations protect sensitive data across today’s increasingly complex environments. Meet our team and explore GTB’s latest innovations in Data Security, Data Loss Prevention (DLP), DSPM, DDR, and AI Governance. September 9–10, 2026 Istanbul Expo Center Booth H2-028 We look forward to connecting with customers, partners, and security leaders from across the region. See you in Istanbul! #GITEXAI #GITEXTürkiye #GTBTechnologies #DataSecuritythatWorks #DLP #DSPM #DDR #AIGovernance #Cybersecurity #GettheBest
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.