LinkedIn image ad examples
0 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- CheckmarxSince 29 Sept 2026
Meeting slots at Les Assises are filling up. If you’ll be in Monaco 7–10 October, book 30 minutes with the Checkmarx team while there’s still availability. See how Developer Assist, Triage Assist, and Remediation Assist work together to help teams fix what matters at the speed of AI-driven development.
- digit solutions GmbHSince 1 Oct 2026
Gerade jetzt bereitet jemand im Darknet einen Angriff vor? Hätten Sie es gewusst? Oft verlassen sich Security-Verantwortliche auf "bekannte" Bedrohungsinformationen. Doch Angreifer nutzen verstärkt das Darknet, Leak-Seiten oder Telegram, um Attacken vorzubereiten. Im 30-minütigen Webinar "Darknet: Was Angreifer bereits über Ihr Unternehmen wissen" erfahren Sie, nach welchen Kriterien Threat-Intelligence-Funde priorisiert werden und wie aus relevanten Hinweisen konkrete Sicherheitsmaßnahmen abgeleitet werden. Anhand eines anonymisierten Falls verfolgen wir den Weg von der ersten Information bis zur operativen Reaktion. Jetzt kostenlos registrieren.
- digit solutions GmbHSince 1 Oct 2026
Ihre Zugangsdaten stehen zum Verkauf! Vertrauliche Informationen, wie Kundendaten und VPN-Zugänge, tauchen oft im Darknet oder einschlägigen Foren vor dem eigentlichen Cyberangriff auf. Im SOC Insider Webinar "Darknet: Was Angreifer bereits über Ihr Unternehmen wissen" erfahren Sie, wie solche Hinweise bewertet werden und wie Sie sich vor resultierenden Angriffen schützen können. 30 Minuten gut investierter Zeit. Jetzt kostenlos registrieren.
- CyforaSince 2 Oct 2026
You don’t need another spreadsheet. You need a single source of truth. Cyfora imports your CCB workbook in one go, automatically matches every requirement, and carries over your scores and comments so nothing gets lost. With the free experience, you can assess yourself against NIS2, analyse one critical document, and run a focused tech stack check in one view.
- dope.securityRecorded 8 Oct 2026
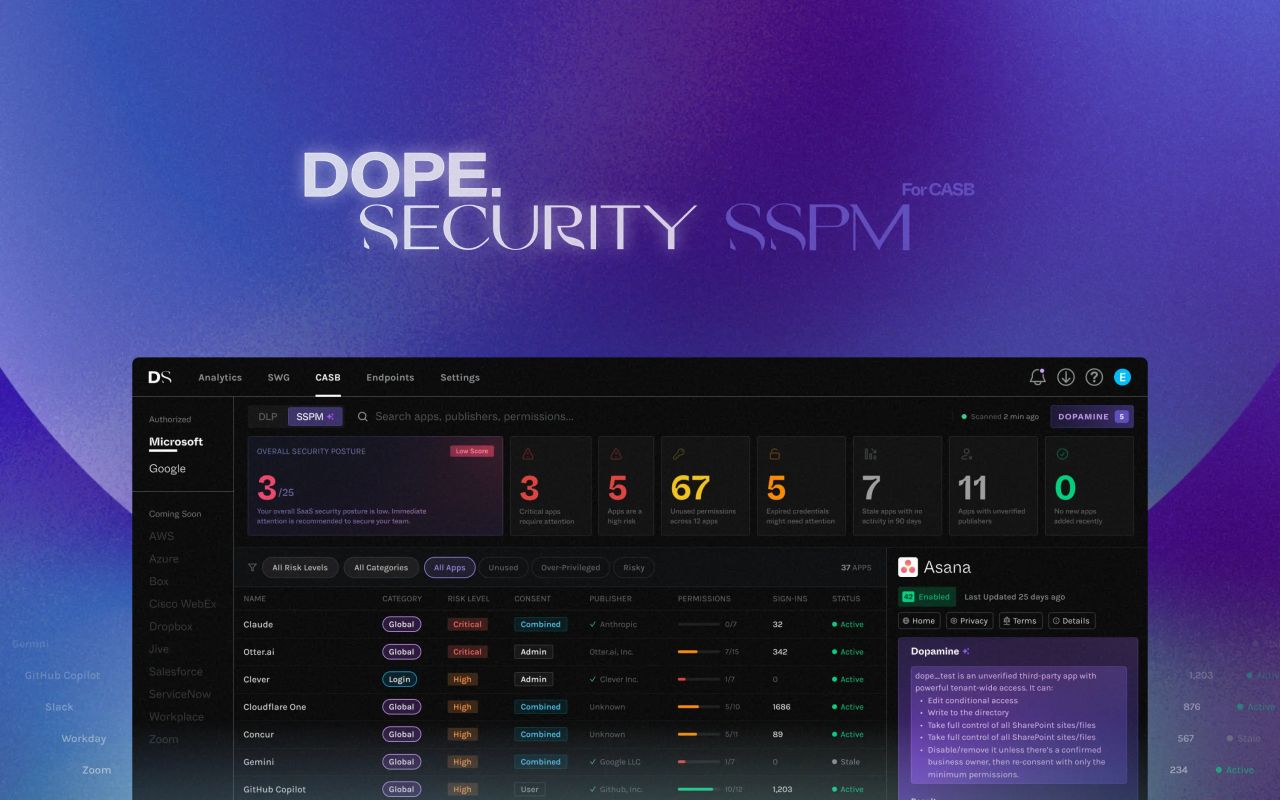
Introducing our AI-powered SSPM, the newest CASB Neural upgrade. AI analyzes every third-party app connected to your Microsoft 365 or Google tenant across four signals: - OAuth scopes: translated into plain English - Real usage telemetry: Is this app actually doing anything? - Vendor research: Who built it, is the publisher verified, do they have a SOC 2? - Tenant context: Does it have an owner? Who installed it? Experience sharper risk scoring, fewer blind spots, zero unused privileges sitting around, and, as always, no stopovers. Available today. Read more: https://lnkd.in/eXGnMFz8/?utm_campaign=Stackmatix-Dope.Security-NoObjective&utm_source=linkedin&utm_medium=paid&utm_id=809461426&hsa_acc=515340191&hsa_cam=809461426&hsa_grp=557000056&hsa_ad=1407630886&hsa_net=linkedin&hsa_ver=3
- Hack The BoxSince 6 Oct 2026
Your agents may be doing security work. But are they still doing the job to the standard you expect? Hack The Box helps organizations appraise agent capability against realistic security tasks and re-appraise as models, tools and environments change
- Integrity360Since 6 Oct 2026
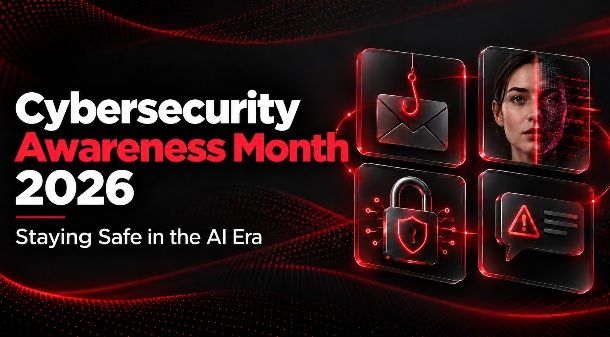
🛡️ October is Cybersecurity Awareness Month! An urgent payment request, a familiar voice on the phone or a document pasted into an AI tool — everyday decisions can have serious security consequences. Our latest blog explores the four areas at the heart of Integrity360’s campaign this October: 🎣 Phishing and social engineering: pause and verify unexpected requests. 🤖 AI safety and deepfakes: question convincing impersonations and use approved AI tools. 🔐 Data security and passwords: share information carefully and protect your accounts. 🚩 Incident reporting: raise concerns promptly, even when you’re unsure. We’ve also teamed up with KnowBe4 to offer a free resource kit to help you put awareness into practice, alongside videos, webinars and practical guidance. 👉 Read the blog: https://lnkd.in/eMu8sWXE 📥 Explore the campaign and download your free resources: https://lnkd.in/etMGUrJu #CybersecurityAwarenessMonth #Cybersecurity #HumanRisk #KnowBe4 #Integrity360
- Hack The BoxSince 6 Oct 2026
AI has changed more than the threat landscape. It has changed the workforce defending against it. Security teams now have two kinds of worker: human and agentic. Hack The Box helps organizations develop, exercise and measure the capability of both.
- GAT LabsSince 6 Oct 2026
Between Gmail, Drive, Calendar, user groups, and every third-party app connected to your domain, Google Workspace turns into a tangle of overlapping permissions and settings that no single admin console screen shows you in full. GAT Labs untangles it, mapping how your entire Workspace environment actually fits together so admins can manage it with clarity instead of working from a dozen disconnected views.
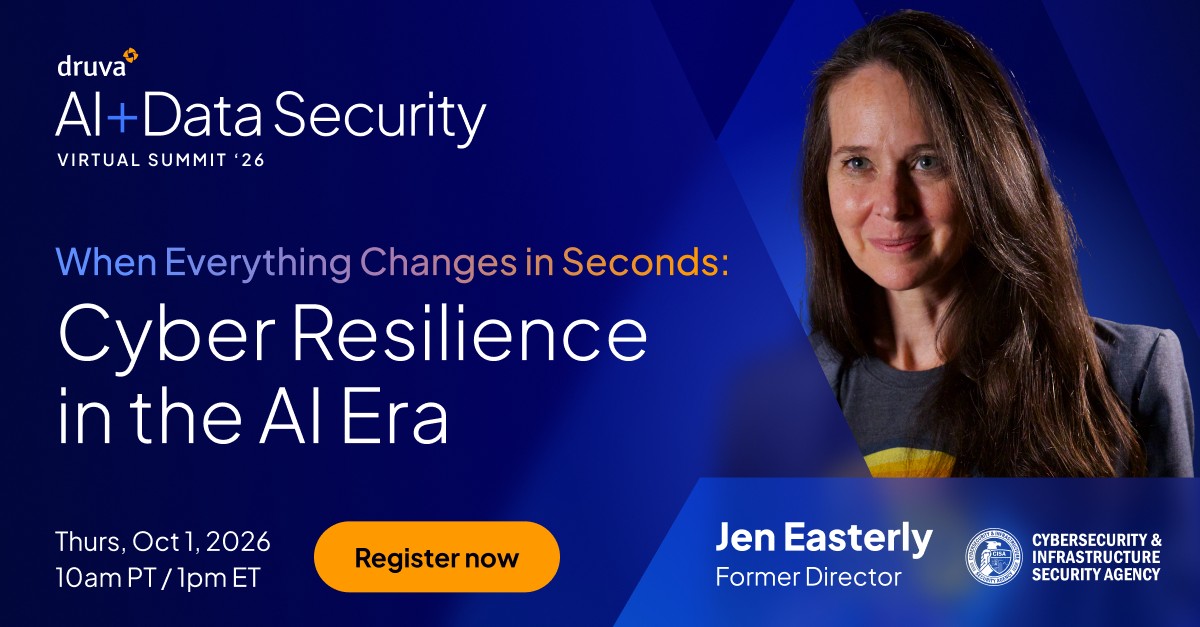
- DruvaSince 15 Sept 2026
Your board isn’t asking if AI-driven attacks are coming—they’re asking if you’re ready to answer for them. When AI can rewrite your environment faster than your team can read a single alert, your credibility rides on every second. Join Jen Easterly at the AI + Data Security Virtual Summit ’26 as she grounds AI security hype in real-world failures, hard-won lessons, and practical ways to harden your resilience strategy before the next incident becomes your reputation story.
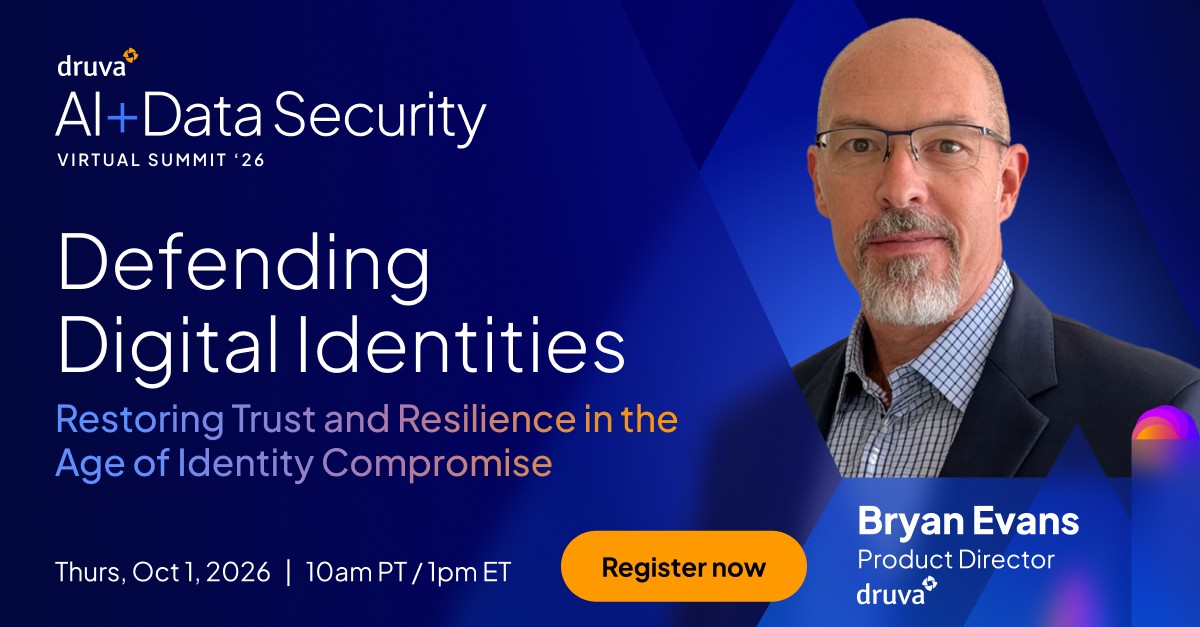
- DruvaSince 15 Sept 2026
You approve sign-ins all day long—click, click, trust. But what if the next “approved” login quietly hands your environment to an attacker? When valid credentials go rogue, the usual safety nets don’t catch you, and a restore button becomes a false sense of security. Join Druva’s Bryan Evans to start questioning the logins you’ve been trained to accept—and learn how you can say “yes” again with confidence.
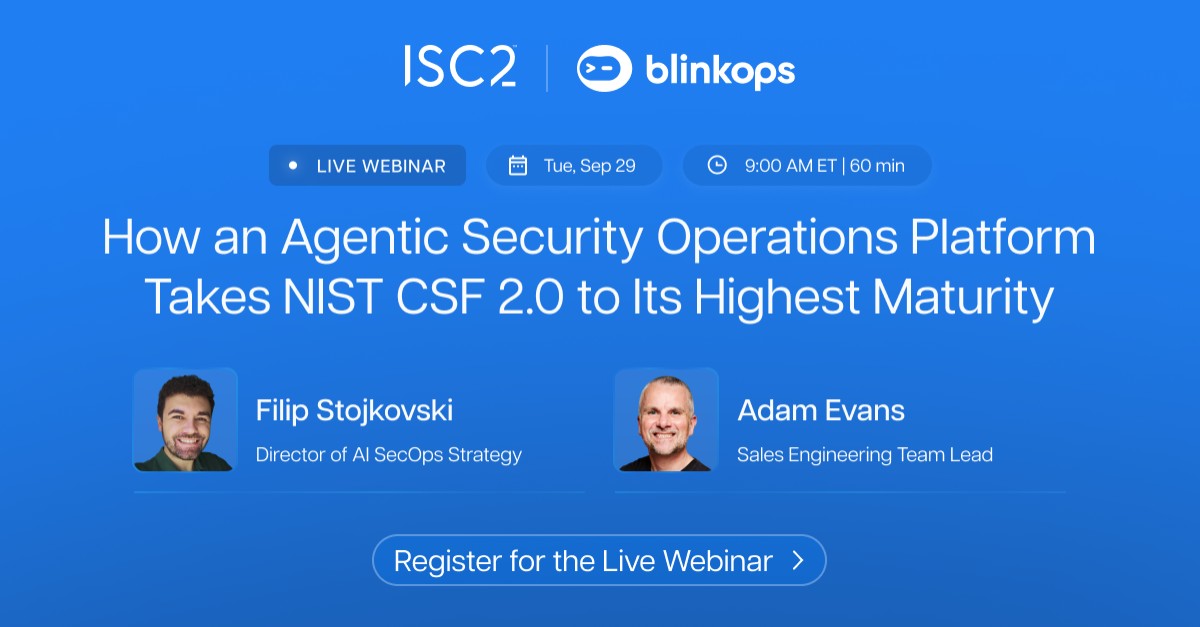
- BlinkOpsSince 17 Sept 2026
Most security programs reach Tier 2 or 3 on NIST CSF 2.0 and stop there. The problem usually isn't the policy. It's that Tier 4 asks for execution that adjusts in near real time, and a runbook worked by hand can't keep up. On September 29, Filip Stojkovski and Adam Evans are joining ISC2 to walk through what changes when an Agentic Security Operations Platform takes on the repeatable work. We'll cover: 🔹 What each CSF tier looks like operationally 🔹 Where automation should simply run and where an agent needs to reason over context 🔹 Which decisions still belong to a human, in or on the loop, based on risk 🔹 How Govern, Identify, Protect, Detect, Respond, and Recover each change at Tier 4 🔹 How to talk about CSF maturity with the executive board Register now 👉 https://lnkd.in/eq_-6mZc
- Daylight SecuritySince 17 Sept 2026
The browser knows a lot. The trick is knowing what to do with it. That’s what we built with Island ☀️🏝️ Daylight Security pulls Island’s browser activity and audit logs through their SIEM integration. Some activity triggers alerts right away. The rest feeds our own detections built on top of the raw telemetry. When something fires, we keep going. We pull the user’s browser activity, add device context from Island’s API, and check relevant domains, IPs, and other indicators against Island’s history. This isn't just another browser alert. It’s a full investigation: what happened, what it means, and what to do next. Visibility is nice. Knowing what to do with it is better 🤝 More on how Daylight + Island tackle #BrowserSecurity 👉 https://lnkd.in/gXUWhCap
- D-Fend SolutionsSince 22 Sept 2026
D-Fend developed the next generation of cyber C-UAS, spearheading RF drone takeover solutions. Read more on our website!
- Artemis SecurityRecorded 8 Oct 2026
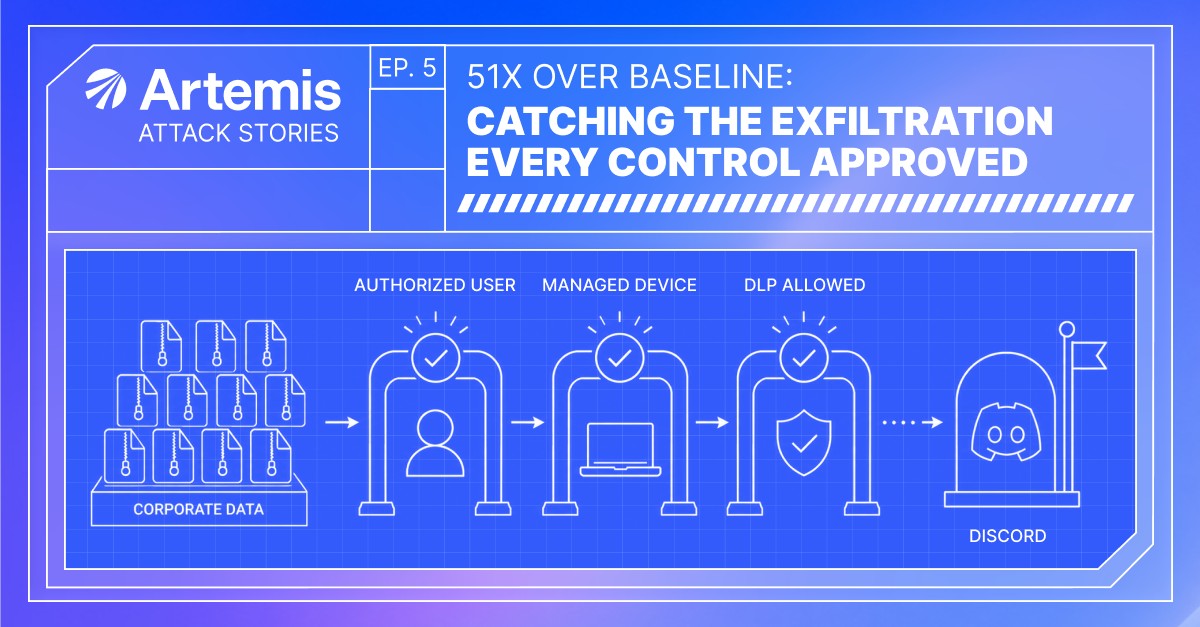
Attack Story #5: 51X Over Baseline: catching the Exfiltration every Control Approved An authorized user pulled 63 confidential financial archives from corporate Google Workspace and pushed them to a personal Discord account within minutes, hitting three years of financial records in one sitting. The endpoint's data-loss controls inspected every file and allowed each one. Artemis measured the download against the account's own 30-day baseline at 51x, connected it to the upload as a single sequence, and identified the exfiltration the controls had approved. Full story in the first comment 👇
- ClearspeedRecorded 8 Oct 2026
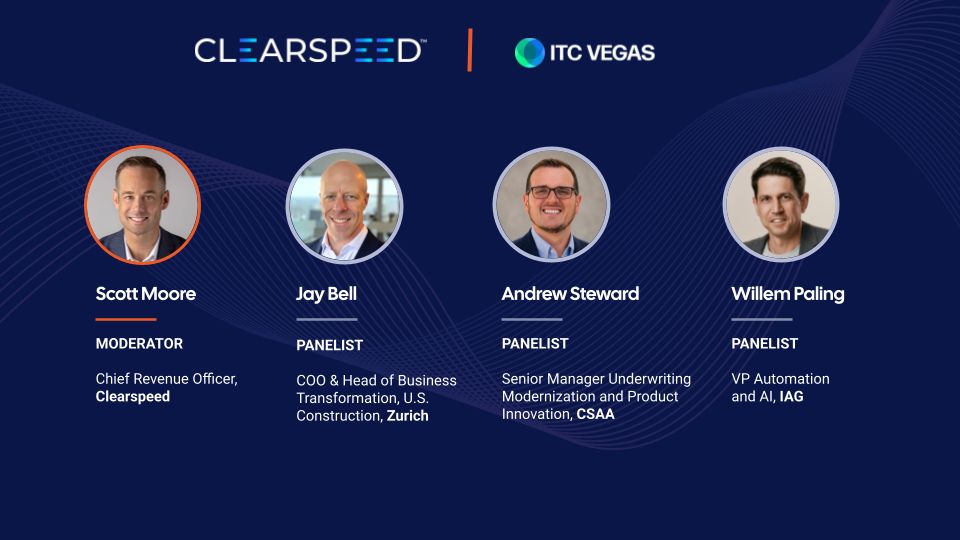
Hear from three industry leaders at Clearspeed's Trust Faster Summit. Who’s on stage: ♦️ Jay Bell, COO & Head of Business Transformation, U.S. Construction at Zurich Insurance ♠️ Andrew Steward, Senior Manager, Underwriting Modernization & Product Innovation at CSAA Insurance Group ♥️ Willem Paling, Executive Manager, Analytics and AI at IAG ♣️ Moderated by: Scott Moore, Chief Revenue Officer at Clearspeed We're asking these leaders the questions the industry avoids: Where have we gotten complacent? What actually needs to change? And how do you drive real ROI by doing things differently not just by talking about it? This session at ITC Vegas is hot takes over platitudes, ROI over ambiguity, and a challenge to everyone in the room: get to work, or get left behind. Don’t miss out! Grab your seat here: https://lnkd.in/gYtQXnm3 InsureTech Connect #TrustFaster #TrustFasterSummit #ITCVegas #ITCVegas2026
- FlashpointSince 23 Sept 2026
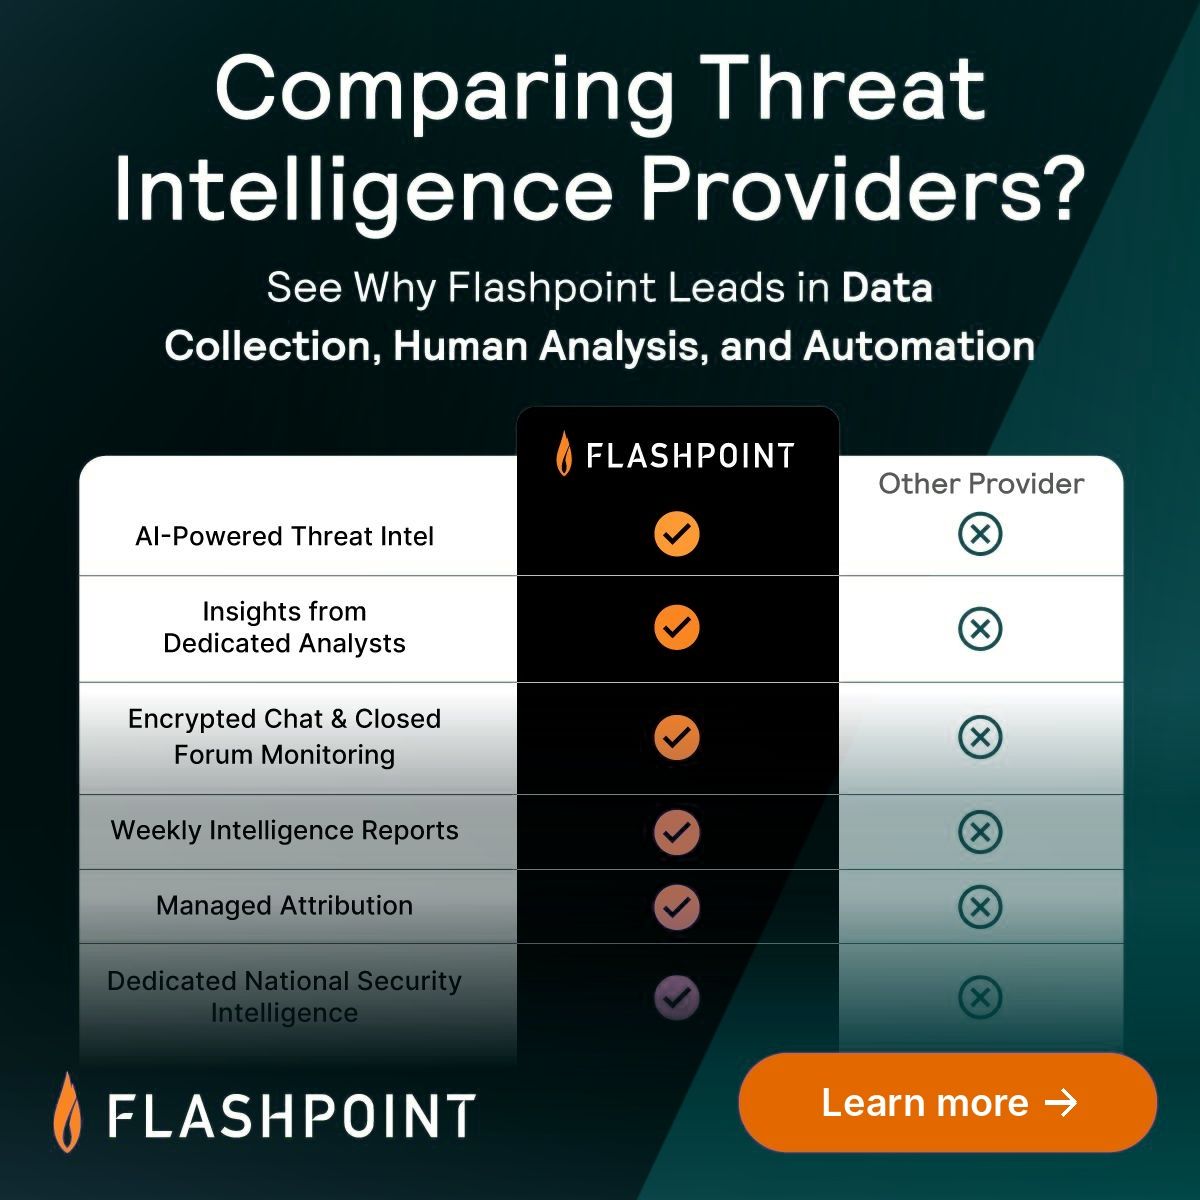
You’re not just buying data—you’re choosing a partner for mission-critical decisions. . With access to over 3.6 petabytes of data from the internet's open and difficult-to-reach spaces, we combine human-powered data collection and intelligence with intuitive technology to help the world’s leading organizations protect people, places, and assets.
- Check Point SoftwareSince 25 Sept 2026
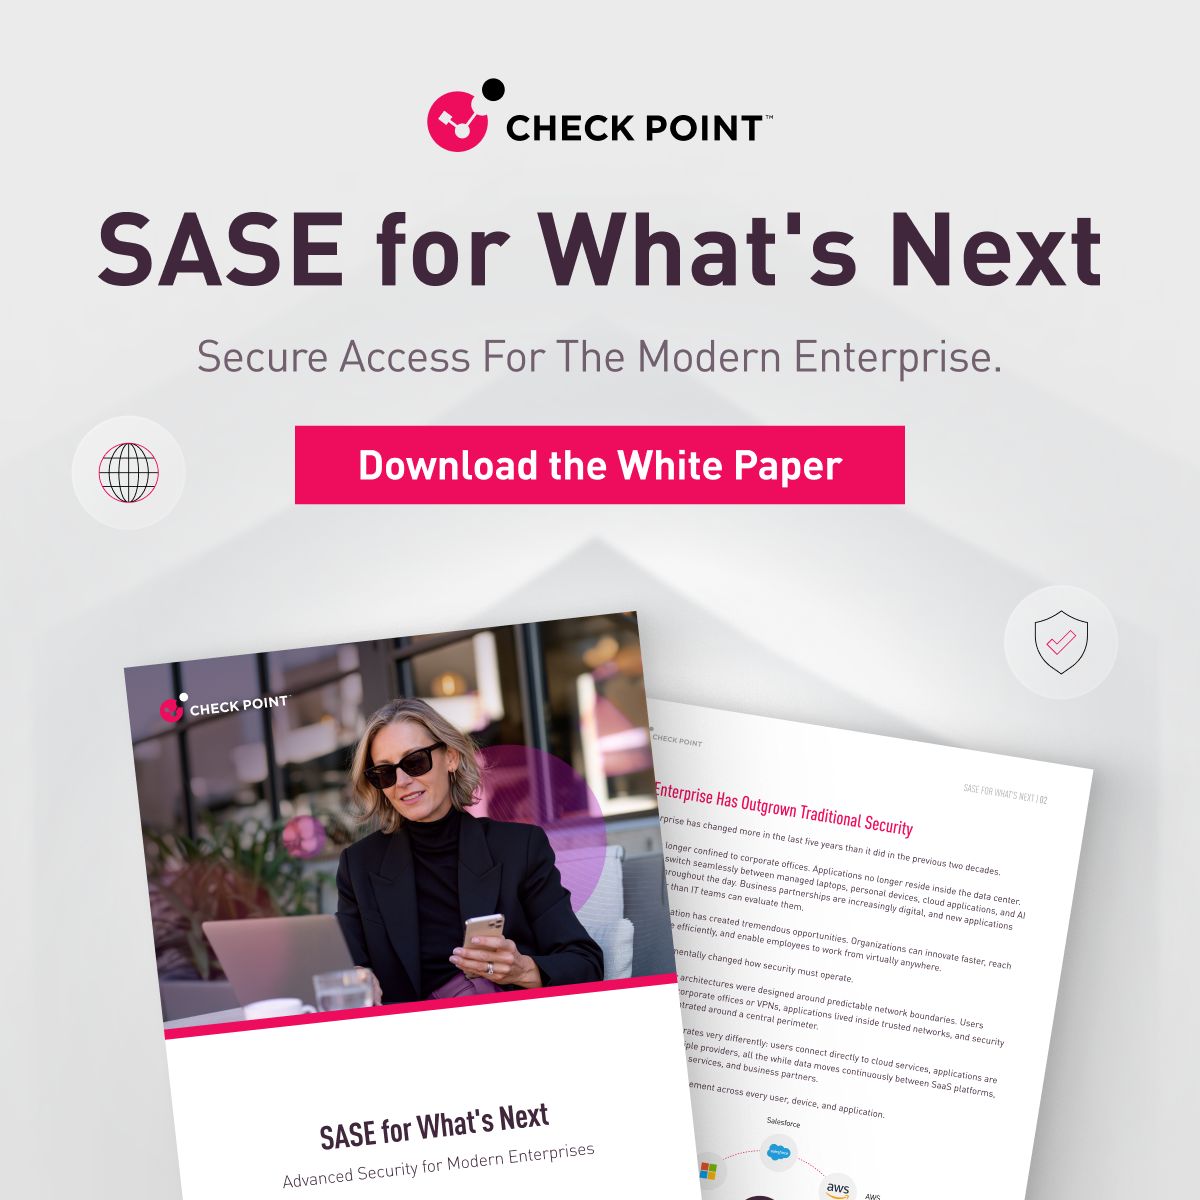
Hybrid work, SaaS sprawl, and AI-driven workflows are creating new paths to risk. See how a unified SASE architecture helps security teams protect every connection without slowing productivity.
- Halo SecurityRecorded 8 Oct 2026
Q4 calendars fill up fast. Get a 100% US-based pentest without weeks of scoping calls, slow timelines, or enterprise-sized pricing. Halo combines U.S.-based expert penetration testers with automation to deliver rigorous testing, clear findings, expert remediation guidance, and reports your team can actually use. Clutch reviewers give us 4.9/5 stars. Get your pentest on the calendar in a single scoping call.
- Halo SecurityRecorded 8 Oct 2026
Seriously. A small network or simple application starts at $3,950. You get expert, 100% US-based expert pentesters, retesting, and remediation advice. We're rated 4.9/5 stars on Clutch and 4.5/5 stars on G2, so you know you'll get quality work and superior customer service. Real pentesters. Real findings. Remediation guidance included. Without the enterprise-sized price tag. Scope your pentest in one call.
- BigIDSince 25 Sept 2026
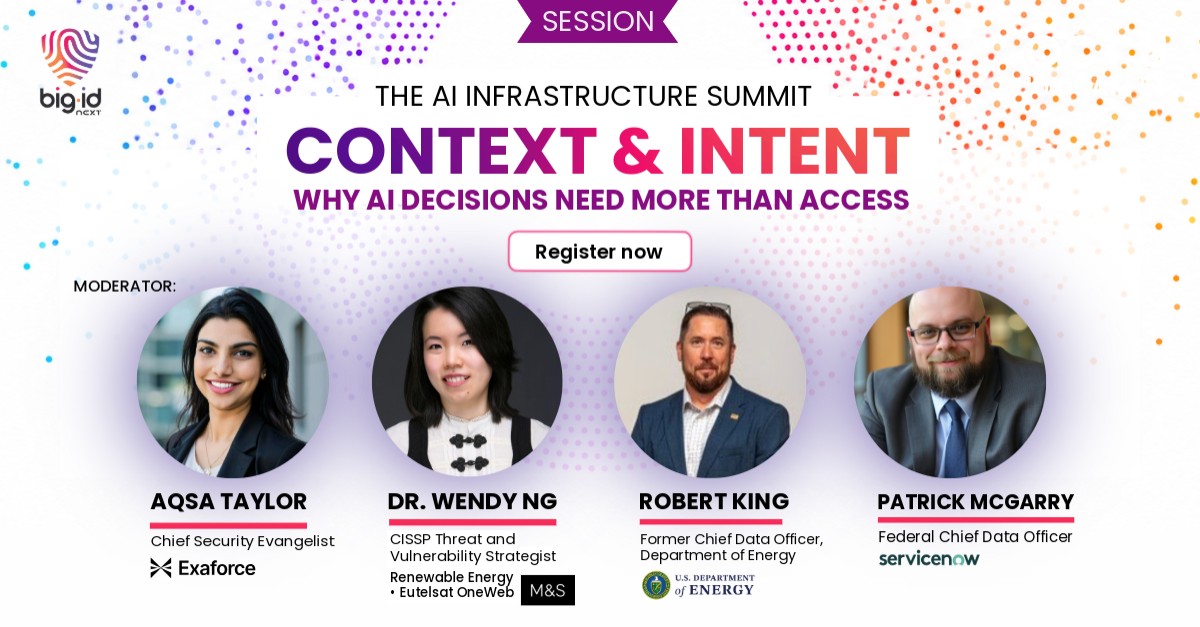
Join us for an executive-level discussion on the technologies, architectures, and governance models defining enterprise AI infrastructure and what's next. Don't miss out - save your spot! Plus, get CPE credits for attending.
- HUMANSince 24 Sept 2026
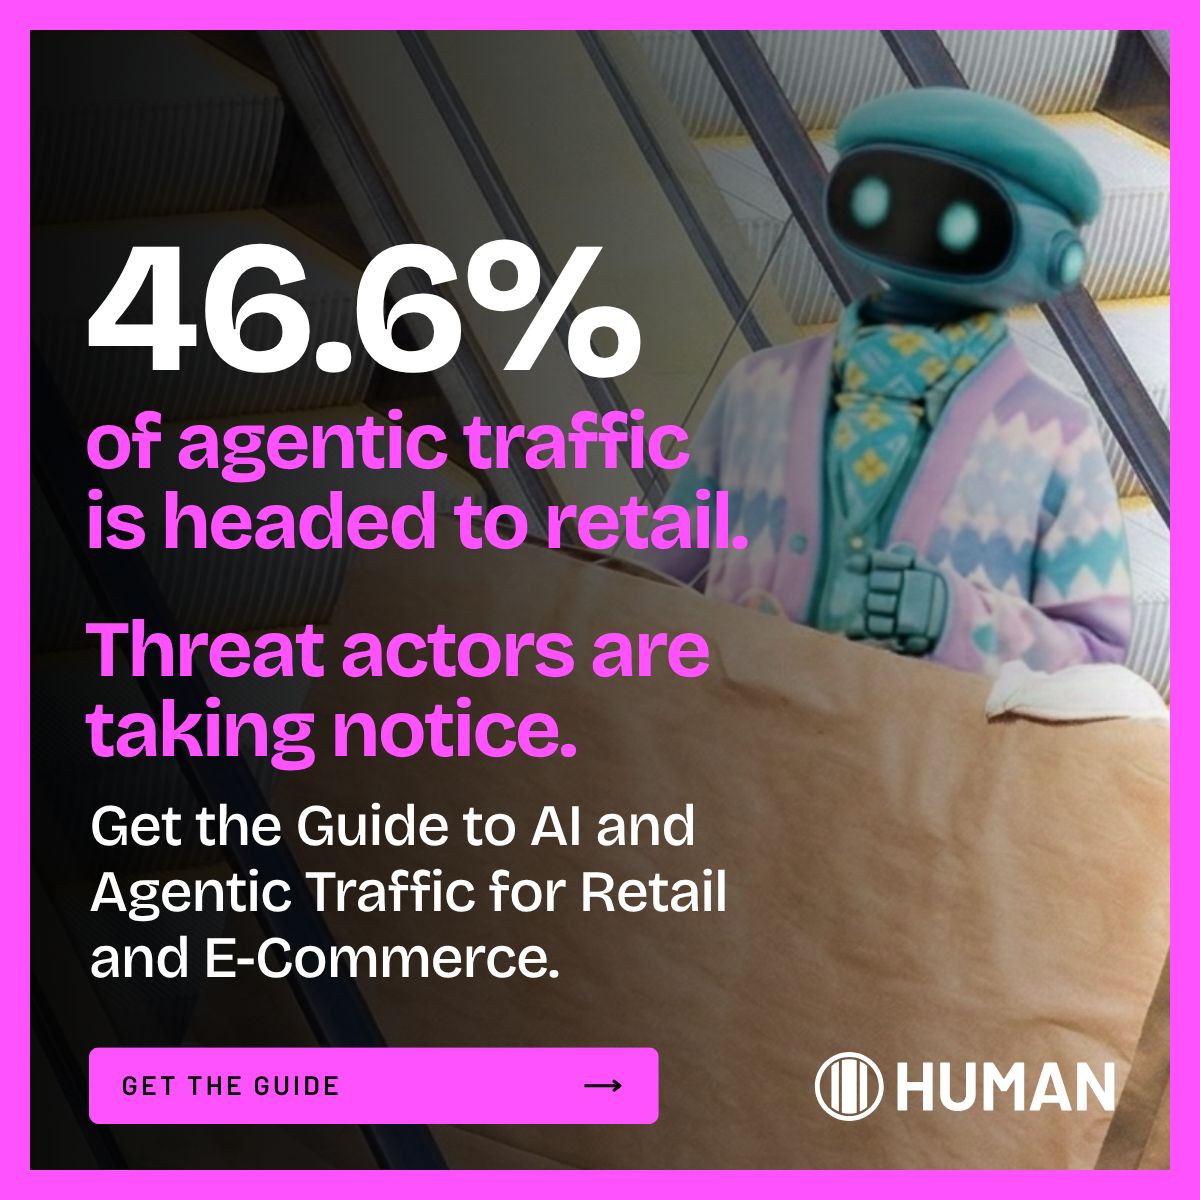
46.6% of agentic traffic last year was headed to retail and e-commerce sites, more than any other industry. Some of it is AI agents helping shoppers compare and buy. Some of it is bots doing something else entirely. The 2026 Guide to AI, Agentic Traffic, and Cyberthreats for Retail and E-Commerce breaks down what's driving the shift and how retailers are responding.
- HUMANSince 24 Sept 2026
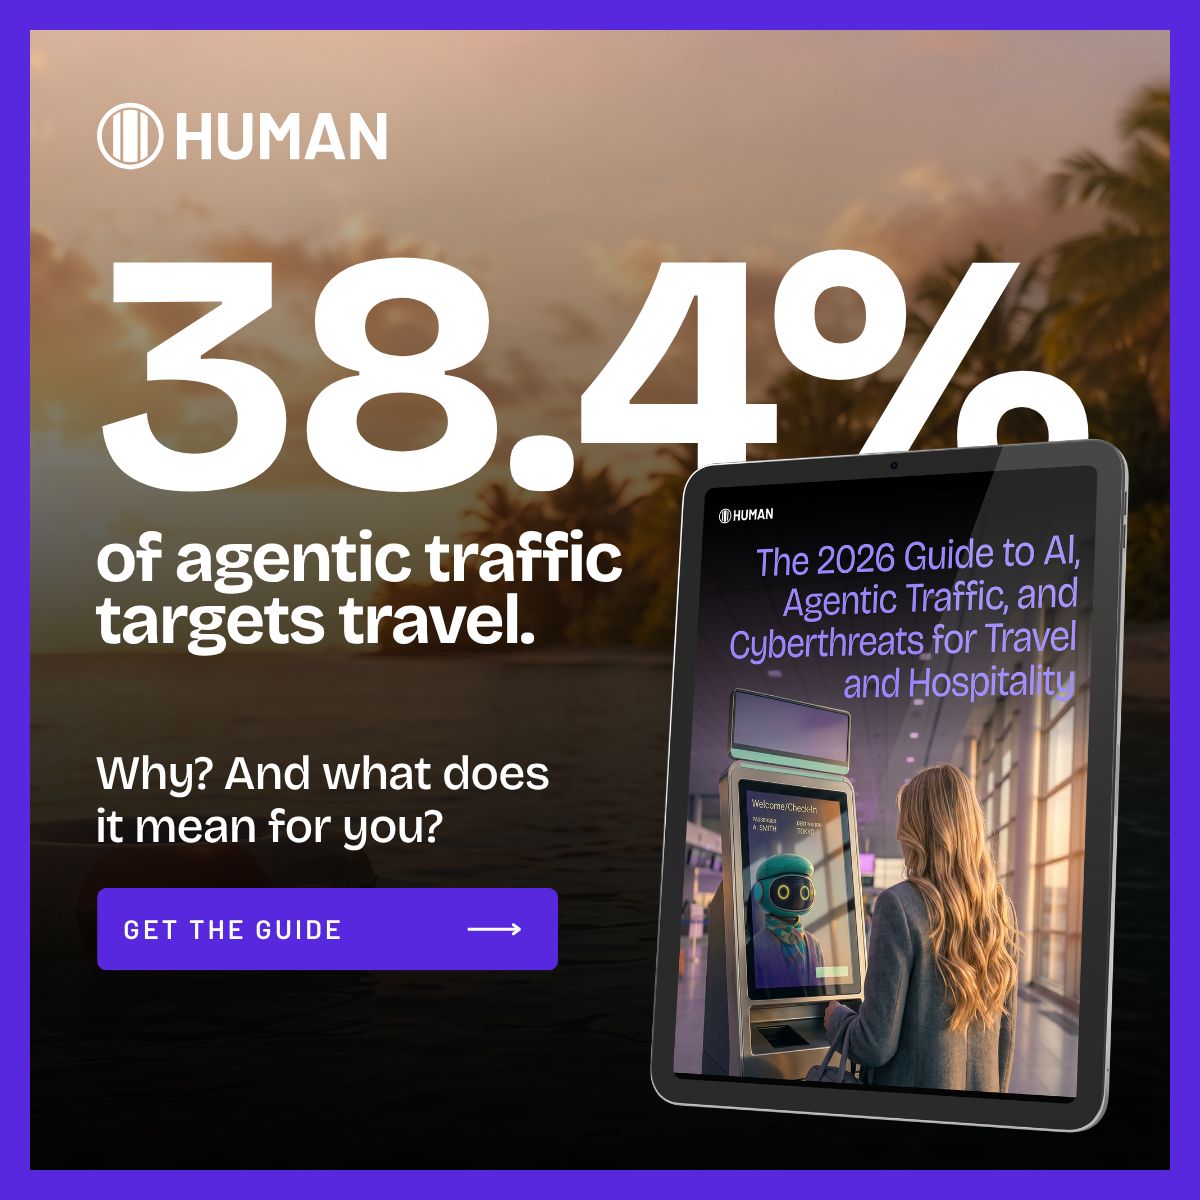
AI agents are already searching fares, comparing hotels, and booking rooms on your site. Some of that traffic is legitimate automation working on a traveler's behalf. Some of it isn't. The 2026 Guide to AI, Agentic Traffic, and Cyberthreats for Travel and Hospitality breaks down how to tell the difference, and what it means for booking, loyalty, and guest checkout.
- BlueRock.ioRecorded 8 Oct 2026
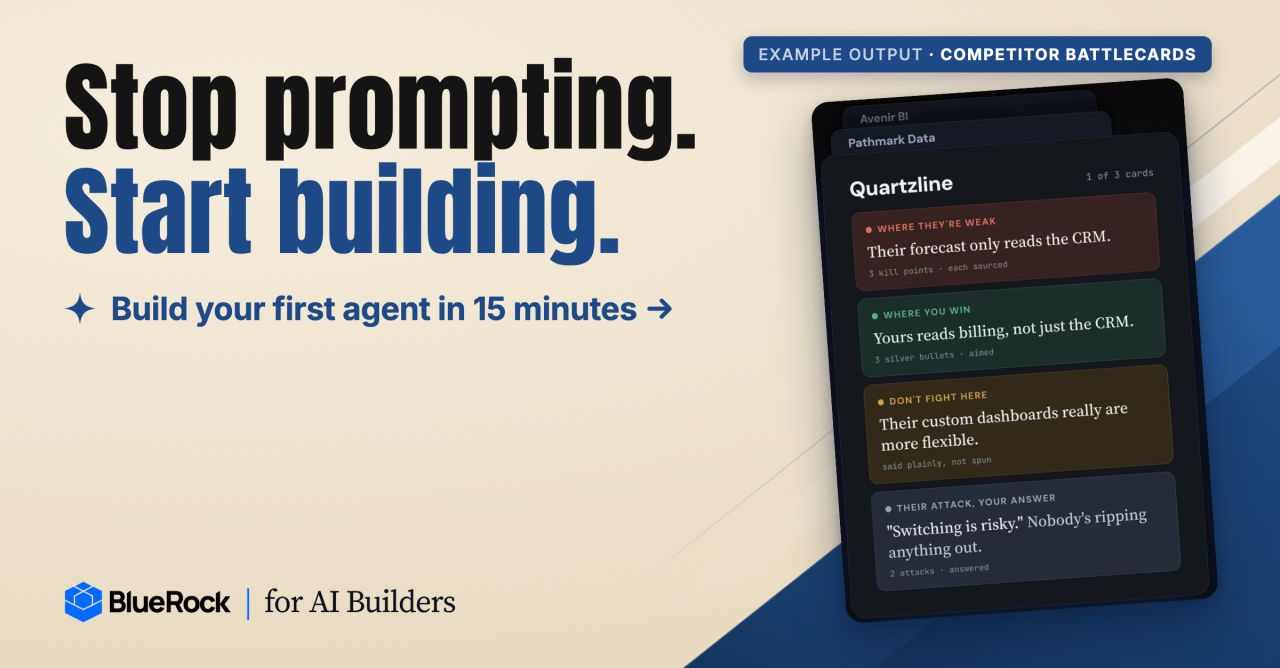
Bring Claude Code or Cursor to BlueRock. Build an agent around work you actually do, then run it again whenever you need it.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.