LinkedIn image ad examples
3 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- FaciaSince 29 Sept 2026
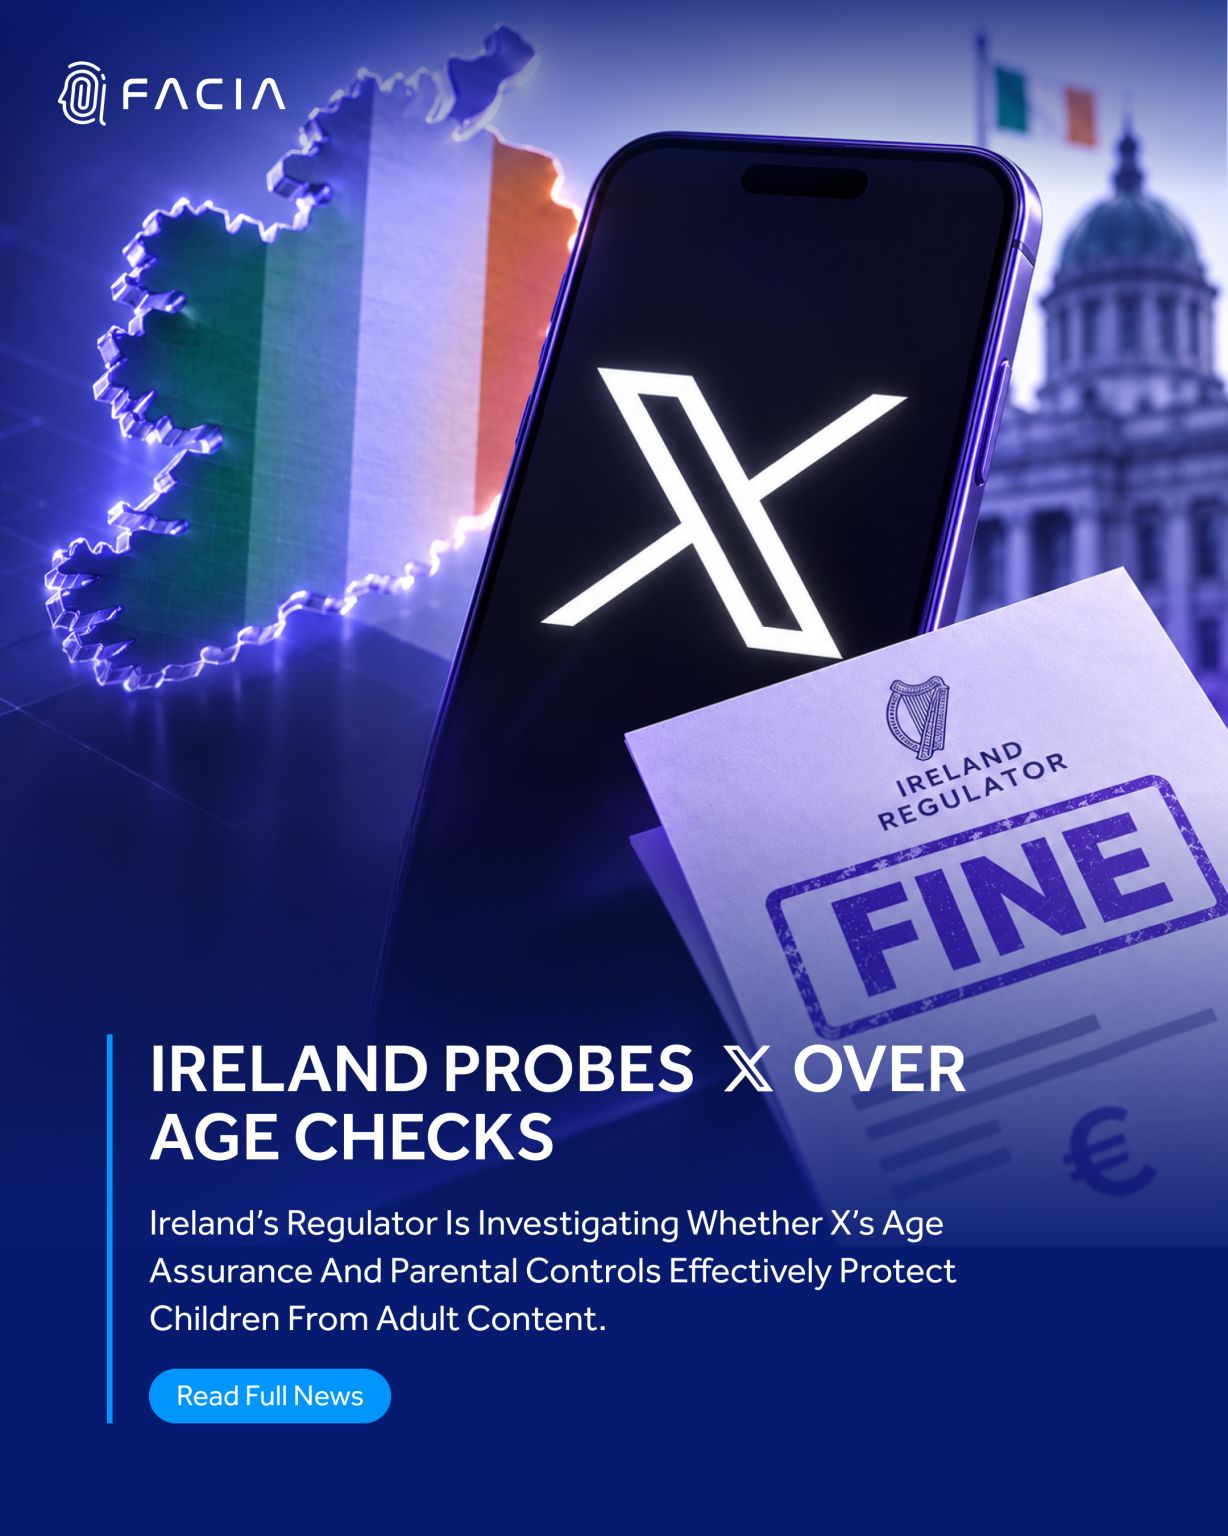
Ireland is putting X’s age assurance measures under the spotlight. Coimisiún na Meán has launched its first Online Safety Code investigation, questioning whether self-declared age checks and parental controls are enough to protect children from adult-only content. The case could push platforms toward stronger, privacy-conscious age verification methods that work in practice—not just on paper. As scrutiny grows, the investigation may help shape the next standard for online child safety across Europe. Read the full News: https://lnkd.in/dPeiBSXG
- FaciaSince 29 Sept 2026
Deepfakes are getting better at looking real. Verification must get better at proving what’s real. Facia helps detect synthetic faces, injected feeds and verify the human behind the screen. . . . #Facia #IdentityVerification #DeepfakeDetection #BiometricSecurity #FraudPrevention
- DataCheckerSince 2 Oct 2026
Of je nu tien of duizend kandidaten per maand plaatst: elk ID handmatig controleren kost tijd die je liever aan plaatsen besteedt. 👨💻 Met DataChecker verifieert elke kandidaat zijn ID zelf via de smartphone, 7 dagen per week. Meldt iemand zich in het weekend aan, dan weet je binnen 24 uur of hij klaar is om te starten. ✓ Voor kleine en grote bureaus ✓ 7 dagen per week, resultaat binnen 24 uur ✓ Vastgelegd volgens NEN 4400-1 Je betaalt per verificatie, dus je begint zo klein als je wilt. Plan een demo en zie hoe het in jouw proces werkt.
- DataCheckerSince 2 Oct 2026
Erleben Sie, was DataChecker für Ihr Unternehmen leisten kann. Wie funktioniert digitale Identitätsprüfung in der Praxis? In einer persönlichen Demo zeigen wir Ihnen, wie Sie: ✓ Identitätsdokumente digital prüfen ✓ Gesichtsvergleich & Liveness Detection einsetzen ✓ die Arbeitsberechtigung prüfen ✓ Prüfungen nachvollziehbar dokumentieren Keine allgemeine Präsentation, sondern eine konkrete Live-Demo der Technologie und ihrer Möglichkeiten, auf Deutsch oder Englisch. 📅 21. Oktober 2026 📍 RheinMain CongressCenter, Wiesbaden 📌 Stand D.05 Jetzt vorab einen Termin vereinbaren.
- FiligranSince 2 Oct 2026
The open-source project existed years before the company did. We had a community before we had customers, and it's still the reason any of this works. On October 15 in Paris, we're getting that community into a room for the first time. THREAD is our first conference: 17 external speakers, starting with Supervisory Special Agent Byron Graham of the FBI, alongside security leaders from Thales, Accenture, Hermès and Centrica. What's on the table: - Agentic AI in security operations: what works today, what doesn't yet. - Unified exposure management: going from a list of vulnerabilities to what actually matters. - Closing the loop between intelligence, validation and response. No vendor keynotes, no sales pitches. Practitioners talking to a room doing the same job. Every registration is reviewed one by one, so the room stays small enough for that to work. If you've been part of this community from the start, or since last week, I'd love to see you there. Reserve your seat: https://lnkd.in/eGemzwaE #PullTheThread
- ESET NederlandSince 2 Oct 2026
Eén Europees cybersecurityplatform geeft je minder risico en meer regie. Kies voor een geïntegreerde aanpak die inzet op preventie en continuïteit. Ontdek hoe jij de controle houdt.
- ESET NederlandSince 2 Oct 2026
Regels en audits nemen toe. Tegelijk blijft het lastig om altijd inzicht te hebben in datastromen en toegang binnen je cybersecurity.
- CorelightSince 2 Oct 2026
Own the full detection lifecycle from hypothesis to response. Get the guide to transparent AI/ML detections and defensible network evidence.
- iProovSince 4 Oct 2026
A valid credential doesn’t always establish that the person behind it is legitimate. As AI scales impersonation, that gap matters at critical workforce identity moments, from onboarding and account recovery to privileged actions. Explore the Zero Trust gap.
- CorelightSince 2 Oct 2026
AI detections should show their work. Learn how to build explainable detections backed by inspectable network evidence, not black-box scores.
- CR GroupSince 5 Oct 2026
Trust is one of society’s most fundamental assets. It takes years, sometimes generations – to build between individuals, families, teams, nations. And very little to break. When a soldier in the field sends an encrypted message, when a government agency shares classified data across a network, when a command post coordinates across allied forces, the technology carrying that information has to be trusted completely. Not assumed to be secure. Certified to be secure. That certification is hard to accomplish. It takes years of technical development, rigorous national and NATO approval processes, and a track record of operating in environments where failure isn’t an option. Tutus Data and Sentyron has been doing exactly this in Sweden and in the Netherlands for more than 30 years. “Tech for trust” is what you get when that depth of expertise is used to create and build products and solutions for these use cases. It’s not a positioning statement. It describes what we actually deliver.
- DSShield - درع الأمان الرقميRecorded 8 Oct 2026
الاستثمار في الكوادر الوطنية هو الاستثمار الأكثر استدامة. عقول سعودية متخصصة تحمي المقدرات الرقمية وتصنع مستقبلاً آمنًا لاقتصادنا الوطني. Investing in local cybersecurity talent delivers the highest long-term return on investment. Empowering Saudi specialists directly strengthens our national digital economy and safeguards critical assets. #DSSHIELD #cybersecurity #ksa #empoweringthekingdom
- HalbornSince 5 Oct 2026
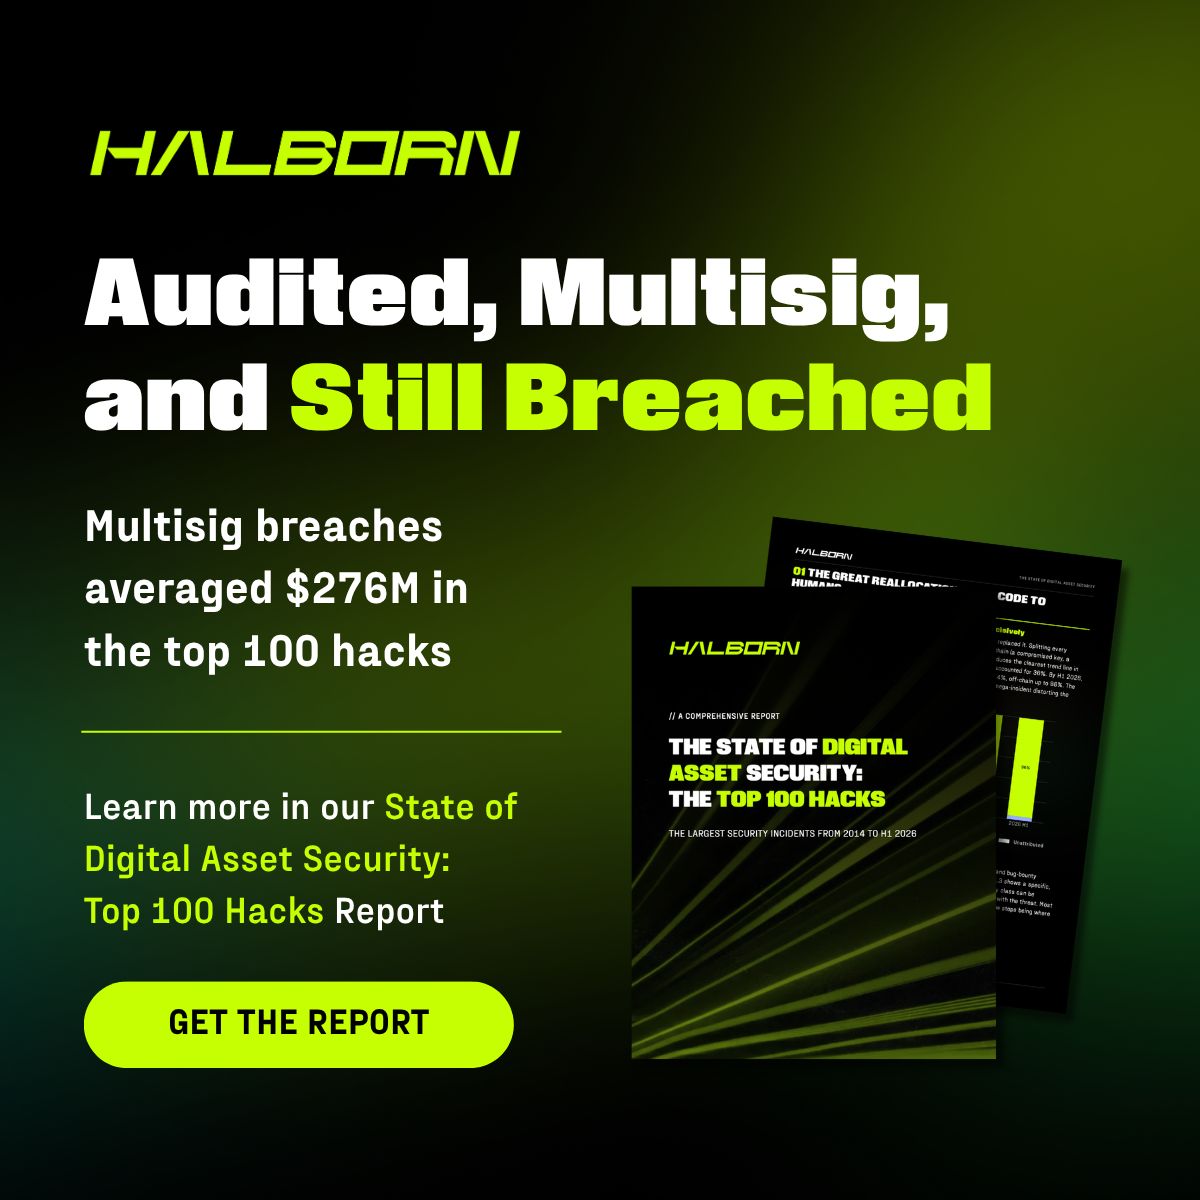
Multisig breaches averaged $276M in the top 100 digital asset hacks. Many of these firms were also audited. 👉 https://lnkd.in/dazSfKqu Every multisig breach went through the people and workflows around the keys, not the cryptography. Controls need testing for effectiveness, not existence. Learn more in Halborn's State of Digital Asset Security: Top 100 Hacks Report.
- Cyber360 | Specjaliści od cyberbezpieczeństwaSince 5 Oct 2026
Nie tylko medycyna i księgowość. Ofiarą cyberataku padł największy polski portal turystyczny Wakacje.pl (Wirtualna Polska). Jak podał Niebezpiecznik.pl, 29 września doszło do przełamania zabezpieczeń w systemach Wakacje.pl. Napastnicy uzyskali nieautoryzowany dostęp do systemu obsługi klientów oraz służbowych skrzynek e-mail pracowników. Co wykradziono? Imiona, nazwiska, adresy zamieszkania, numery telefonów, daty urodzenia oraz dane z paszportów klientów. Po seriach ataków na MyDr, FELG Dent, Fakturownię czy Enel-Med, to kolejny potężny cios w polski rynek digital. A Wy jak chronicie swoją organizację przed atakami?
- DSShield - درع الأمان الرقميRecorded 8 Oct 2026
ثغرة أمنية واحدة غير مكتشفة قد تكون كافية لإيقاف سنوات من النمو والتقدم. في عصر التحول الرقمي السريع، الحماية الاستباقية ليست خيارًا بل ضرورة لضمان استمرار العمليات. حافظ على زخم نموك وأمان أعمالك. Downtime isn't just an inconvenience, it's a risk to your market leadership and operational continuity. While threats evolve, your business operations shouldn't have to pause. DSShield delivers proactive cybersecurity frameworks designed to keep your systems operational and resilient, ensuring you stay ahead while others recover. Keep your momentum moving forward. Connect with our experts to secure your enterprise. #DSShield #Cybersecurity #Empoweringthekingdom #KSA
- HalbornSince 5 Oct 2026
Audited and multisig-protected: would your due diligence call that low risk? 👉 https://lnkd.in/dbKzFUZt In the top 100 digital asset hacks, multisig breaches still averaged $276M, each one through the workflow around the keys. Read the full control analysis in Halborn's State of Digital Asset Security: Top 100 Hacks Report.
- CINI Cybersecurity National LabSince 5 Oct 2026
📣 Una sfida europea per i migliori talenti della #cybersicurezza: è l’European Cybersecurity Challenge (ECSC) 2026, la competizione europea promossa da European Union Agency for Cybersecurity (ENISA) che, dal 12 al 16 ottobre, a Bochum, in Germania, riunirà giovani talenti provenienti da oltre 35 Paesi. 🇮🇹 Tra loro ci saranno i 10 cyber defender di TeamItaly, pronti a portare in gara l’Italia dopo un percorso di selezione e preparazione fatto di competizioni, formazione e allenamento. A Bochum non basterà sapere: serviranno rapidità, strategia e capacità di trasformare le proprie competenze in soluzioni, affrontando sfide di cybersicurezza insieme alle altre Nazionali europee. ⏳ Tra poco sarà il momento di scendere in campo. 👉 Resta con noi per seguire tutti gli aggiornamenti. #CybersecurityNationalLab #TeamItaly #ECSC2026 #cybersecurity
- helmonSince 6 Oct 2026
Il voucher lo offrono centinaia di fornitori IT. La sicurezza della tua azienda merita uno specialista. helmon è un cybersecurity service provider italiano certificato ISO/IEC 27001 e ISO/IEC 27017, e tra i fornitori ammessi dal MIMIT per il Voucher Cloud & Cybersecurity: contributo a fondo perduto del 50% della spesa, fino a 20.000 €. Con un solo interlocutore metti in sicurezza perimetro, accessi, posta aziendale e dati. Per la domanda ti accompagna il nostro partner di finanza agevolata.
- Feroot SecurityRecorded 8 Oct 2026
Clicking a “reject” button is not the same as stopping data collection. See how testing exposes the gap between the cookie banner and what executes beneath it.
- Feroot SecurityRecorded 8 Oct 2026
Your privacy policy cannot show how scripts behave inside the browser. Runtime audits revealed the activity traditional reviews overlooked.
- iProovSince 6 Oct 2026
Account recovery is a critical identity moment: the usual authenticators may no longer be available. How do you confirm the person requesting access is the real person? Explore how human identity assurance can strengthen recovery alongside existing controls.
- Human RisksSince 6 Oct 2026
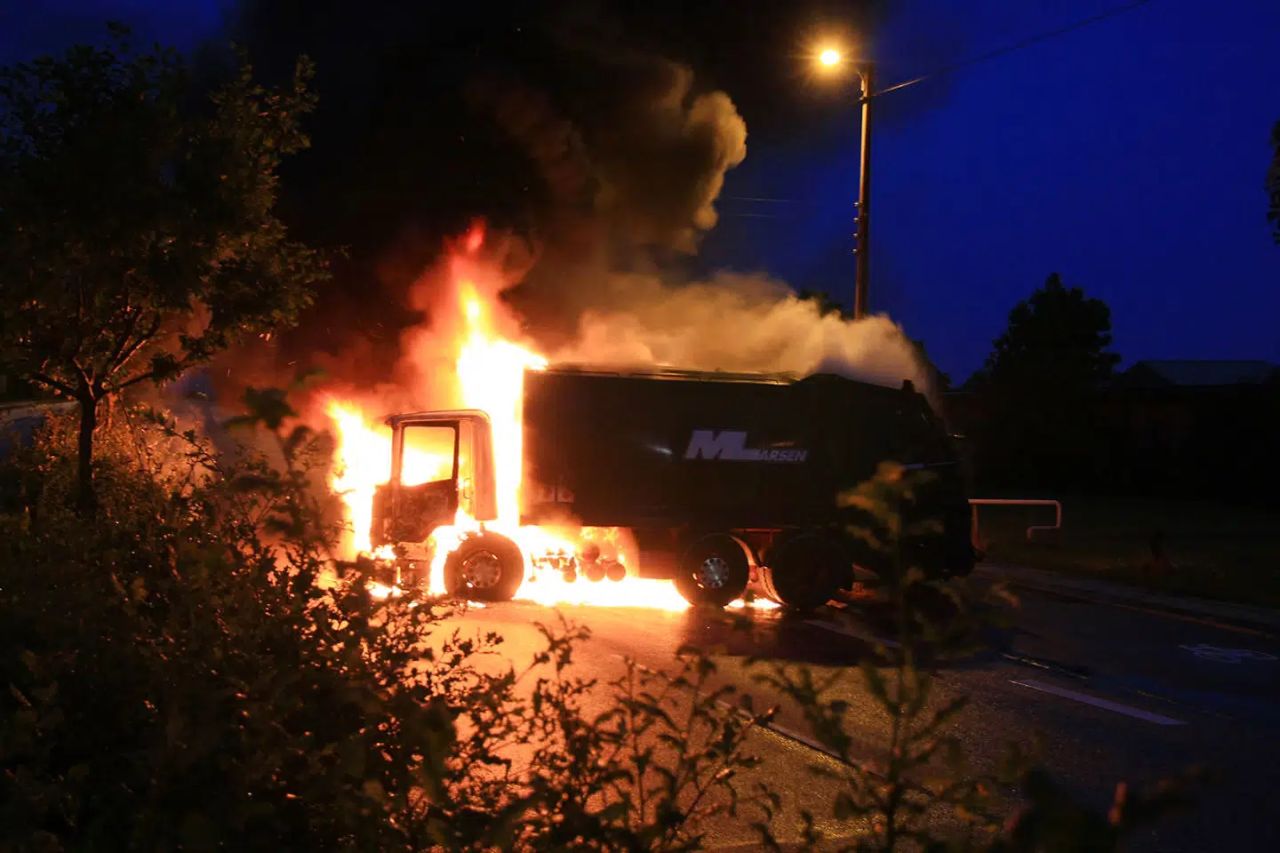
My first job as head of security was at a company that had just lost €8 million in a single night. In August 2008, robbers drove a wheel loader straight through the wall of Dansk Værdihåndtering. They'd set fire to eleven stolen garbage trucks to block the roads, scattered spike strips on the motorway, and disappeared. It's still the largest robbery in Danish history. I came in afterwards, and the brief was simple → This must never happen again. That turned out to be a long list of unglamorous work. New routines for the drivers, down to stickers on the dashboard reminding them what to do and in what order. A new Danish security standard on its way that we had to meet. There were periods where the only thing that mattered was getting through the next few weeks without incident. One of the things we did was ring the building with shipping containers filled with soil, borrowed straight from how we built camps in the military. Heavy enough that nothing was driving through them. None of it was sophisticated. It was mostly about doing a lot of ordinary things properly and consistently.
- GoldphishSince 6 Oct 2026
Over 90% of successful cyber attacks start with a phishing email. If you reduce phishing clicks, you dramatically shrink your risk, protect your operations, and save the time and cost of cleaning up a preventable mess. Start our FREE Cybersecurity Awareness Training and turn everyday inbox habits into a practical, measurable layer of protection for your business.
- IncogniaSince 6 Oct 2026
Quando um agente de IA executa uma ação, existem três perguntas diferentes: É um agente? Qual agente está fazendo a requisição? O usuário realmente autorizou aquela ação? Detecção de automação ajuda a responder a primeira. Autenticação criptográfica do agente ajuda na segunda. Mas nenhuma das duas, sozinha, comprova a intenção do usuário. Esse é o problema que a Incognia agora passa a solucionar em fluxos de Agentic AI. Imagine um agente solicitando a alteração dos dados de recuperação de uma conta bancária. O request pode estar corretamente assinado e vir de um agente legítimo. Ainda assim, isso não significa que o cliente autorizou aquela mudança. Confiar no agente e confiar na ação são problemas diferentes. Para ações de maior risco, a proposta da Incognia é trazer o humano de volta ao fluxo e combinar sua confirmação com sinais do mundo real: continuidade entre dispositivo e conta, localização precisa e conhecida, integridade do device, detecção de RATs e inteligência de risco da rede. Isso também evita o extremo oposto que é desafiar toda ação executada por IA. O nível de verificação também pode variar conforme a ação e o contexto disponível. Consultar um saldo e alterar credenciais de recuperação não deveriam necessariamente ter o mesmo tratamento. Conforme agentes começam a executar mais ações em nome dos usuários, será necessária uma evolução nas estratégias de fraude. A pergunta deixa de ser apenas “é um humano ou um bot?”. Passa a ser "quando a IA estiver agindo em nome de alguém, como garantir que o usuário continue no controle?"
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.