LinkedIn image ad examples
1,342 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- AskealSince 9 Oct 2026
In cybersecurity, the best answers rarely come from one place. They come from the vendor who tracked the threat, the researcher who spent days uncovering how it works, and the practitioners who turn that knowledge into methods, detections and tools. Askeal gives you access to that collective expertise, so you don’t have to reinvent the wheel.
- DigidentitySince 9 Oct 2026
Wacht u weken op een nieuw PKIoverheid servercertificaat? Dat hoeft niet. Bij Digidentity vraagt u uw certificaat volledig online aan. U identificeert zich met uw telefoon en ID, zonder afspraak en zonder wachttijd. Uw overstap kan binnen een dag geregeld zijn. Inclusief 10 SANs per certificaat. Geen verborgen kosten.
- DigidentitySince 9 Oct 2026
Steeds meer systeembeheerders stappen over naar Digidentity. Om een simpele reden: hun nieuwe PKIoverheid servercertificaat was dezelfde dag geregeld. U vraagt het certificaat volledig online aan en identificeert uzelf met uw telefoon en ID. Geen afspraak, geen papierwerk, geen wachttijd. Inclusief 10 SANs. Eén helder tarief.
- AppViewXSince 7 Oct 2026
The first sign of an agent shouldn’t be an incident. The whitepaper turns that gap into a level you can report.
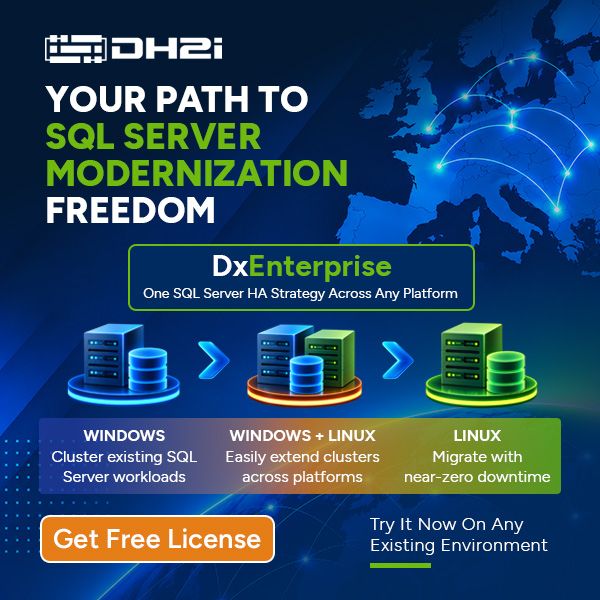
- DH2iSince 7 Oct 2026
Taking greater control of where your SQL Server workloads run? DxEnterprise provides one consistent HA approach across Windows, Linux, and containers—without tying your HA strategy to a specific platform.
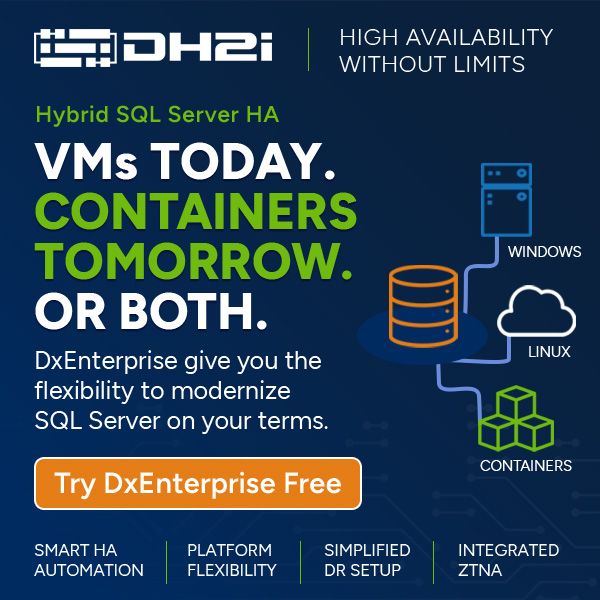
- DH2iSince 7 Oct 2026
Hybrid SQL Server HA Without the Complexity- Windows. Linux. Containers. One HA strategy.
- SharetruRecorded 11 Oct 2026
Ready to put Sharetru to the test? Start a 15-day free trial and move a real, governed file transfer today — over SFTP, FTPS & secure links, running in minutes. #MFT #SecureFileSharing #FreeTrial
- SharetruRecorded 11 Oct 2026
Start a 15-day free trial and move a real, governed file transfer today — over SFTP, FTPS & secure links, running in minutes. #MFT #SecureFileSharing #FreeTrial
- AftraSince 6 Oct 2026
Every vehicle has blind spots. So does the organization you’re driving. See your company through a hacker's eyes and uncover your digital blind spots with Aftra.
- AftraSince 6 Oct 2026
Forget smart glasses. See what hackers know about your organization through their lenses. Discover digital footprints, breached passwords, and get security training alongside continuous vulnerability scanning and attack surface management. All in one place.
- Clover SecuritySince 7 Oct 2026
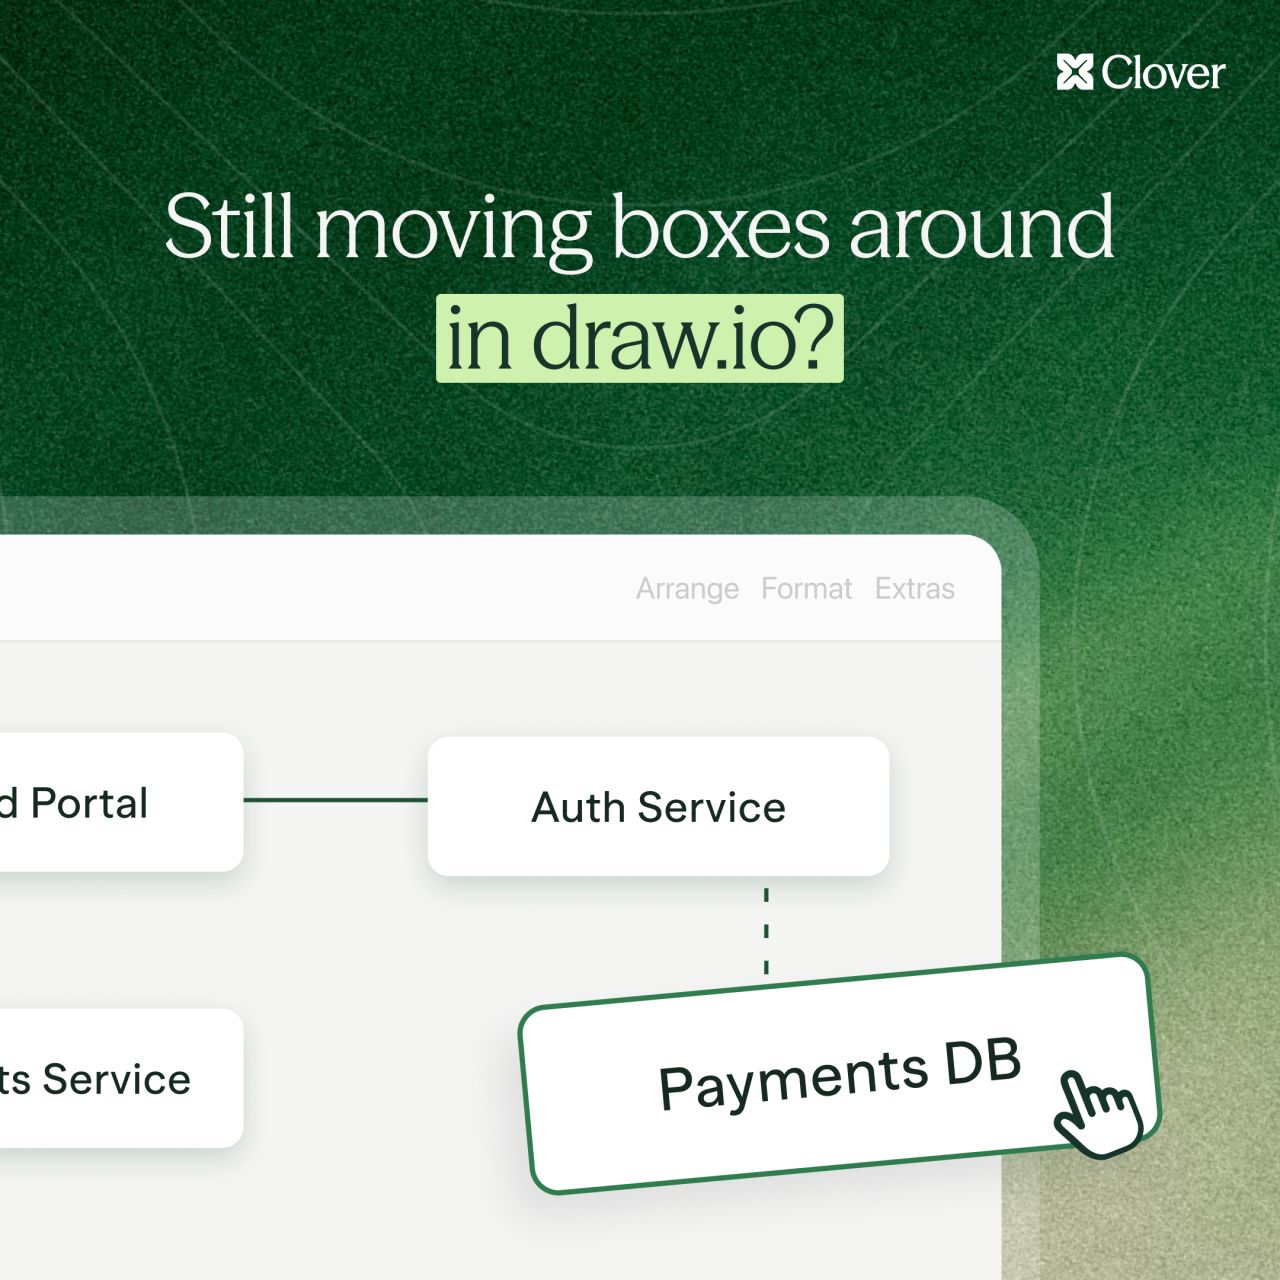
You became a security architect to find the flaw in the design, and now you spend the hour aligning arrows. Clover builds the data flow diagram, the threats and the mitigations from your architecture, tickets and code, so the hour goes back to the flaw.
- AegisAI SecurityRecorded 10 Oct 2026
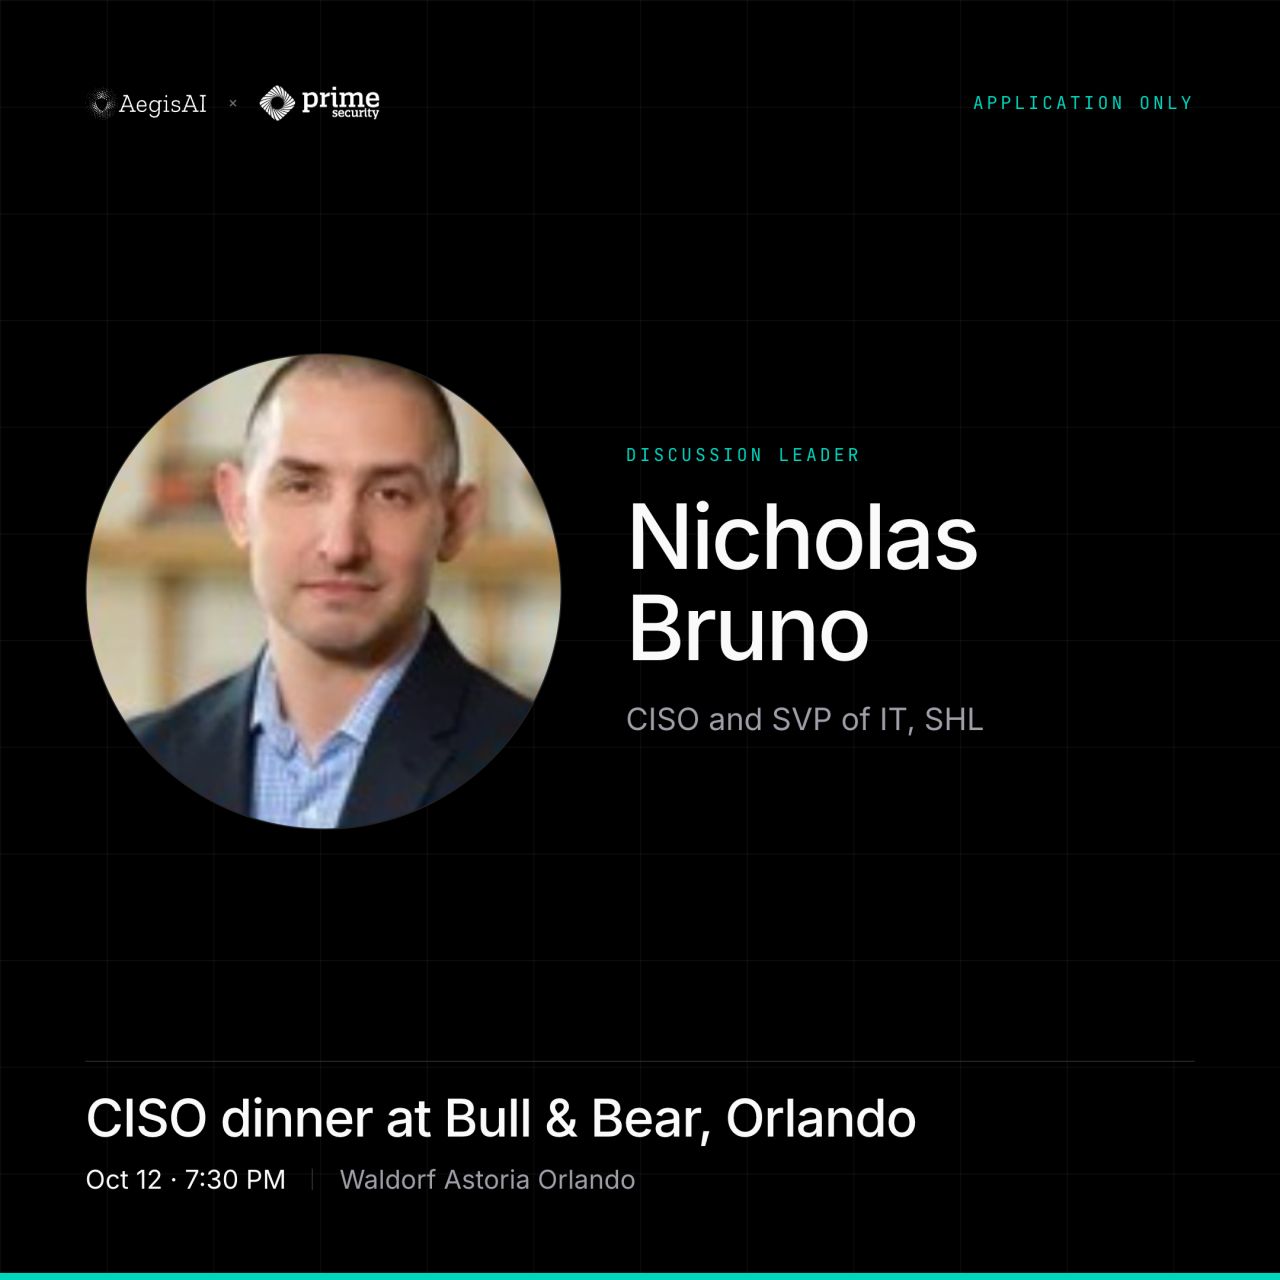
The best security conversations rarely happen on a conference floor. Join a small group of CISOs for an evening of great food and frank peer exchange at Bull & Bear Orlando.
- Cimento AIRecorded 10 Oct 2026
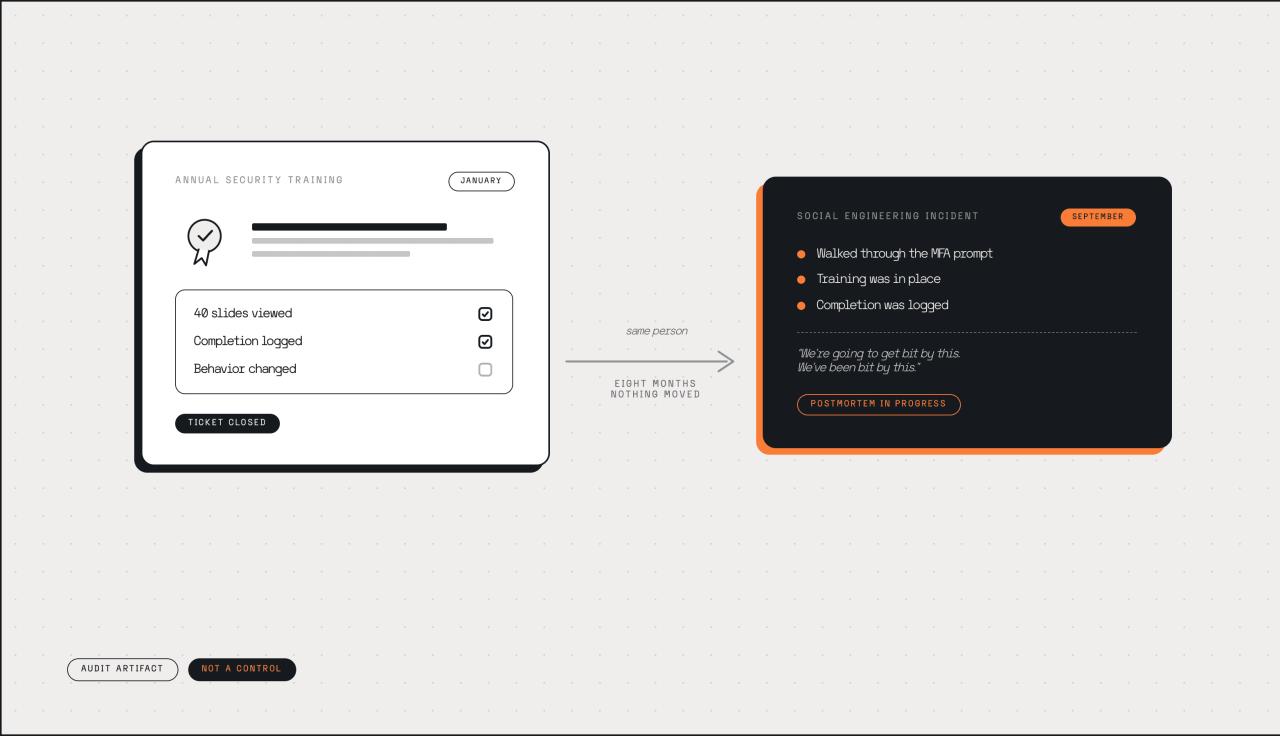
"We're going to get bit by this. We've been bit by this." A head of security said this week about his own annual training program. His team is writing a postmortem on a social engineering incident right now. The training existed. Completion was logged. The attack worked anyway. New on the blog, an uncomfortable argument: checkbox training is worse than no training, because it converts a live risk into a closed ticket. The board sees a completion rate. The attacker sees the same untested people they saw in January. It ends with four moves any security team can make this quarter, starting with this one: pull the completion rate off your board slide and replace it with repeat-failure rate per person. Read it: https://lnkd.in/gh_vynNy
- Cimento AIRecorded 10 Oct 2026
Every vendor wants to show you more signals. It makes the demo look great. It also makes your queue unusable. Our founder Zain Rizavi went on the Talking Cyber Podcast with Kyle McIntyre to talk about the CISO's signal-to-noise problem and why human risk makes it worse: more telemetry, more alerts, and still no answer to "which of my people should I actually worry about today?" Our approach is the opposite of the signal dump. Visibility across your human layer first, then we work with you to understand how your team runs security and who your riskiest users are, so what reaches you is filtered to the risk that's actually moving. More signals isn't the product. Knowing which humans need action is. Full episode: https://lnkd.in/g9_MyE_k
- Autonomous SecuritySince 5 Oct 2026
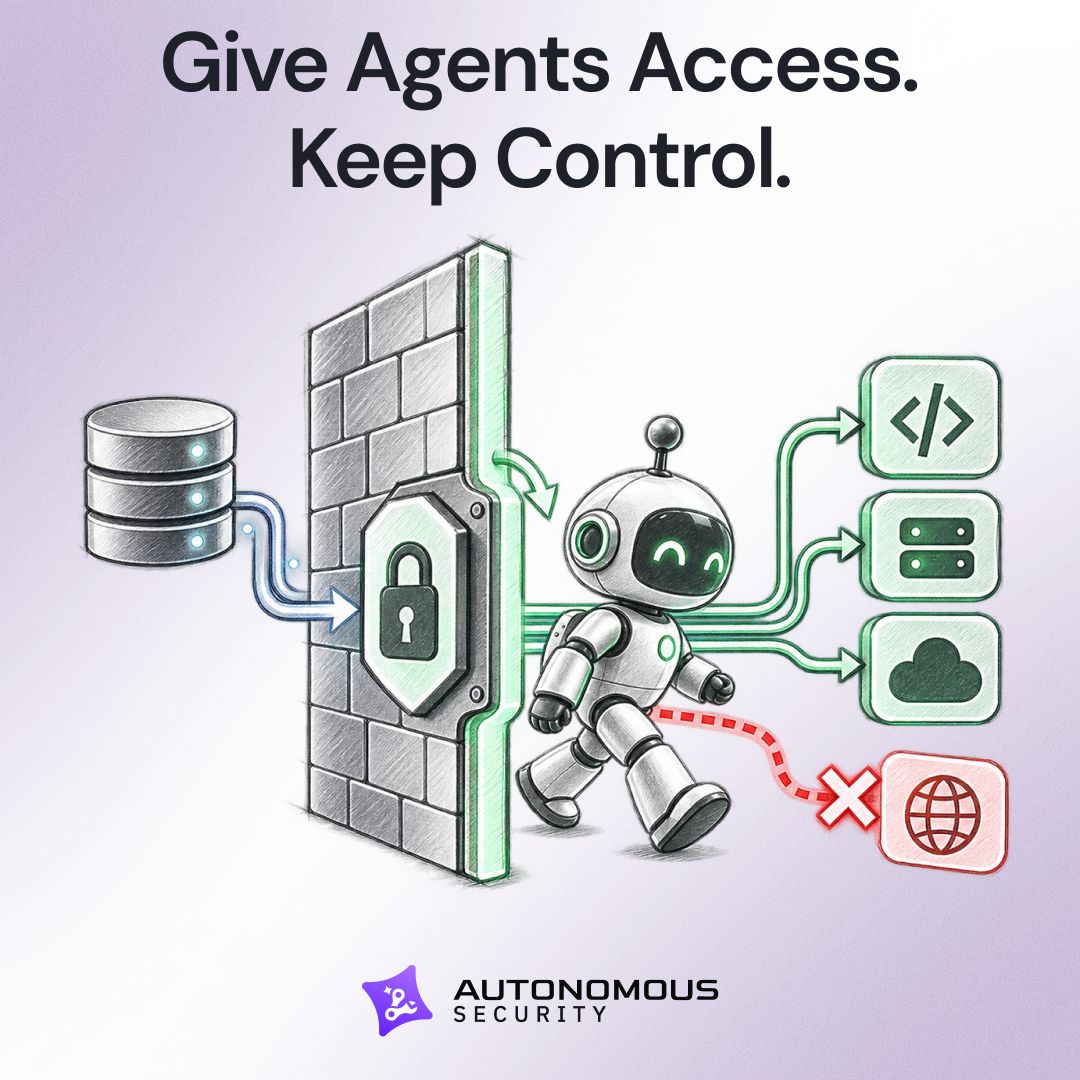
AI agents need access to enterprise data to be useful. But once they can access it, they can leak it too. Autonomous Security provides real time DLP based on *deterministic* guardrails to control what agents can access, use, and send outside your organization.
- Autonomous SecuritySince 5 Oct 2026
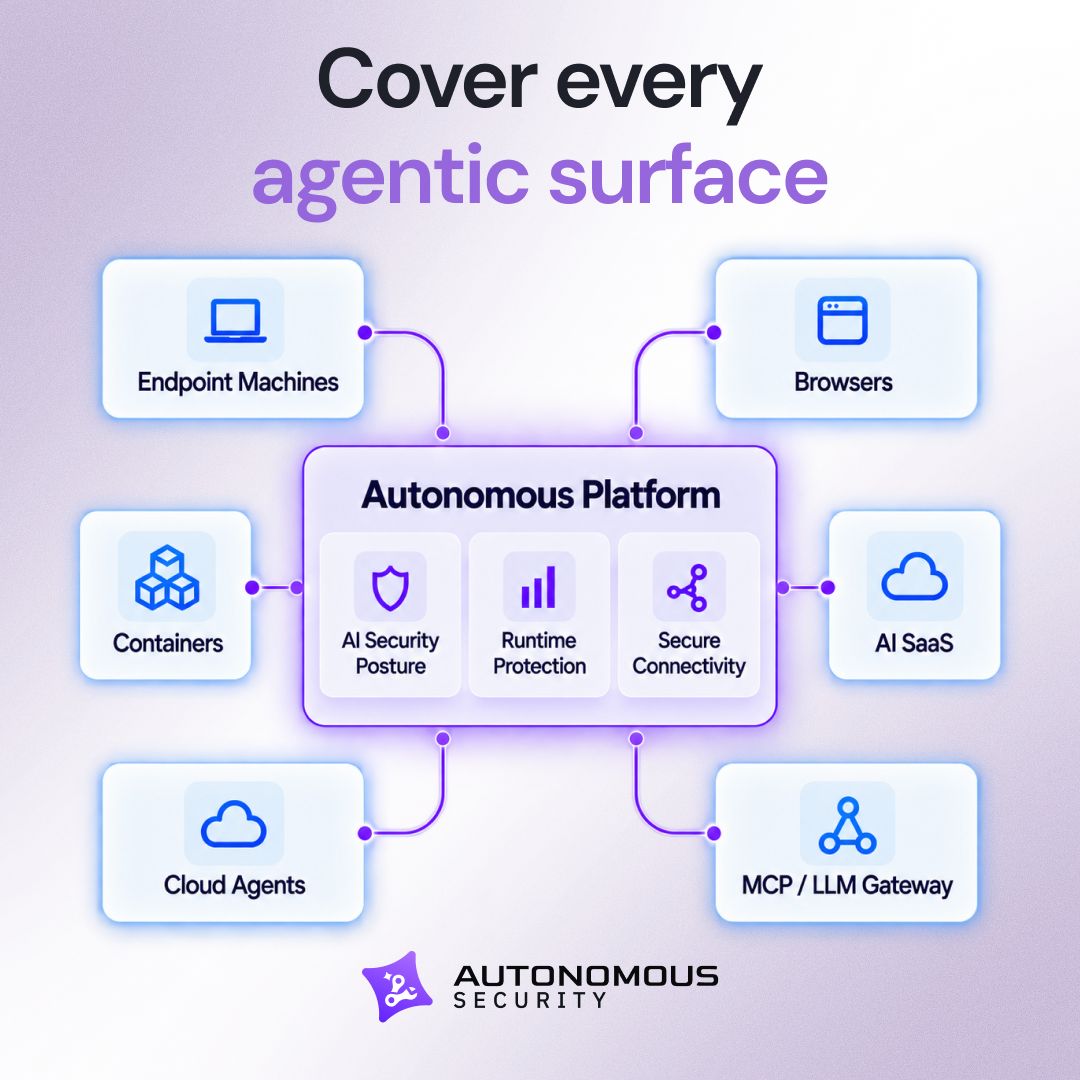
Connect endpoints, browsers, SaaS, cloud, and more to gain one place for AI visibility, control, and run-time protection across the organization.
- Above SecurityRecorded 9 Oct 2026
We're excited to announce that Above integrates with Claude's Compliance API. Security teams running Claude Enterprise can pull prompts, responses and tool calls into Above's behavioral investigations, connected to everything else a person does across browser, identity, SaaS, endpoint and email. No more prompt counts or keyword alerts. Just a finished investigation with a recommended next step. Setup takes a read-only API key and a few minutes. Learn more in our latest blog ➡️ https://lnkd.in/dgwATrbn Our thanks to our own Ariel Domb and the wonderful Anthropic team! #Anthropic #ClaudeEnterprise #ClaudeComplianceAPI #insiderrisk
- 0patchSince 1 Oct 2026
Three client deadlines on one date. On October 13, 2026, Office 2021 loses support, the cheaper first year of Windows 10 business ESU runs out and Windows Server 2012 ESU ends for good. 0patch keeps all three patched across every client with one agent – in memory, without reboots, centrally managed, at per-device pricing that beats ESU year two. See how it fits your service stack before your clients start asking.
- 0patchSince 1 Oct 2026
Clients still on Office 2021, Windows 10 or Windows Server 2021? One 0patch agent keeps both patched until 2029+, with no reboots and no migration project. Central management included.
- UltraViolet CyberSince 1 Oct 2026
9 out of 10 organizations we studied have no way to detect automated attacks against their AI systems. That's one finding from 640 structured observations across 10 enterprise security programs. The full benchmark covers 64 specific activities. See how 10 real programs scored across each one.
- Palo Alto NetworksSince 5 Oct 2026
From reducing riskAI deployments to securing day-to-day AI use for employees, Ignite London shared practical guidance on how to move your business forward securely in this AI Era
- AbstractRecorded 9 Oct 2026
Patched your NetScaler? Cool beans. The webshell doesn't care. Two NetScaler ADC and Gateway zero-days, CVE-2026-88771 and CVE-2026-88772, have been exploited since early September. Responders keep finding implants that survive the patch including modified Apache configs, setuid shells, cron entries, and PHP webshells hiding behind arbitrary extensions. And as of Friday (yesterday), there's a potential new vector affecting appliances already patched against the first round. Weekend plans: cancelled. 😭 ASTRO pulled our own guidance together with reporting from other security teams and responders into one place: → Log signatures for both CVEs → Hunting implants → What to rotate, and why to rebuild instead of clean Hunt before you patch. Patching can delete the evidence. 🤬 https://lnkd.in/guN_D2Ph
- EthiackSince 27 Sept 2026
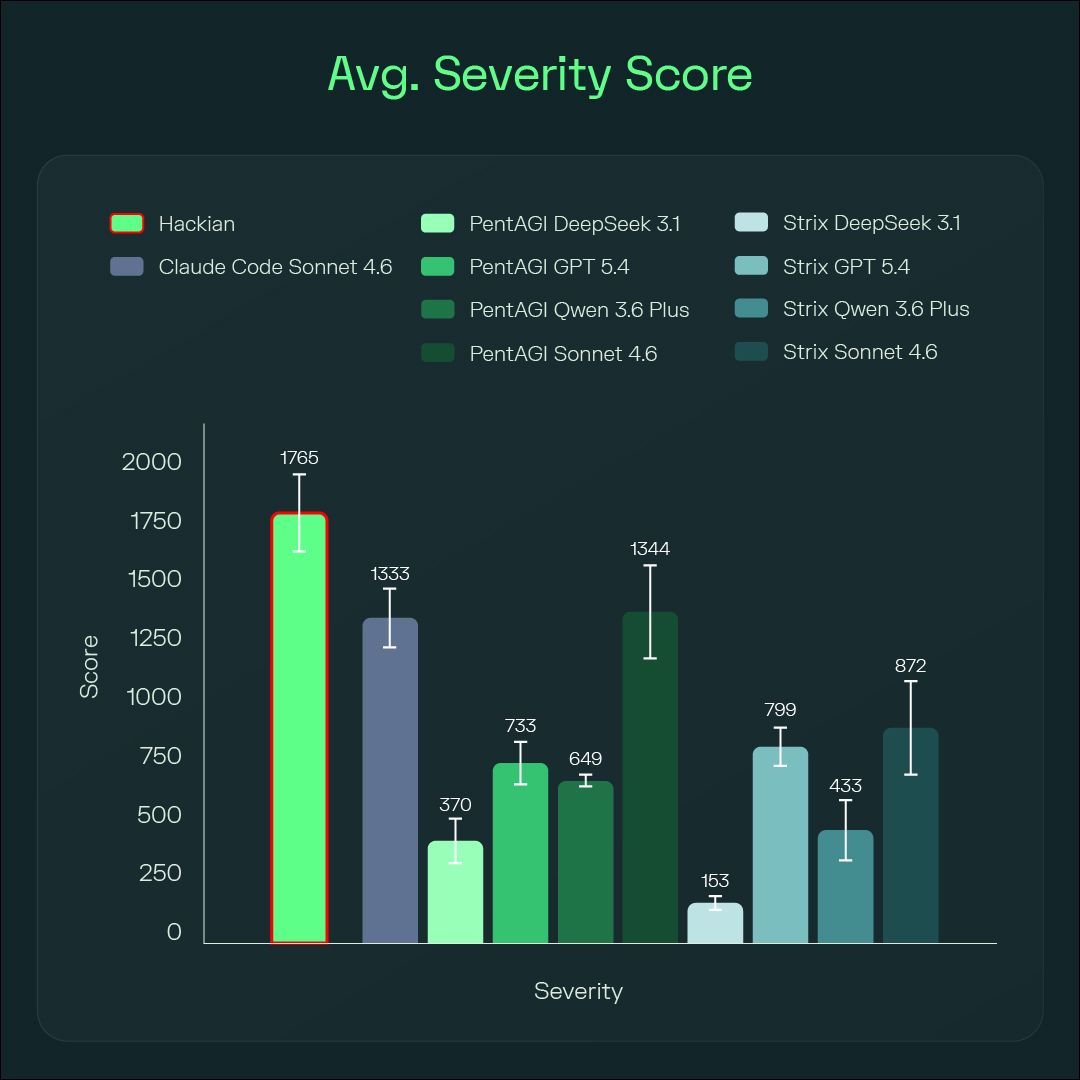
We just open-sourced EthiBench: a new evaluation protocol for AI pentesting agents. The existing benchmarking methods aren't good because they work like a CTF, which doesn't resemble real-world vulns. An agent that is terrible at finding real-world vulns can ace a CTF-style benchmark, and an agent that's great at finding real-world vulns could be underscored. In our own work, gains on controlled benchmarks didn't reliably carry over to real engagements, which is exactly what pushed us to build this. So we designed a whole new benchmarking methodology (along with a research paper) that works by assessing the agent's ability to find bugs in real-world applications. We think this is a stronger foundation for testing the efficacy and accuracy of pentesting agents. We made the benchmark methodology open source and we ranked existing agents. Read more 👇
- Board of CyberSince 22 Sept 2026
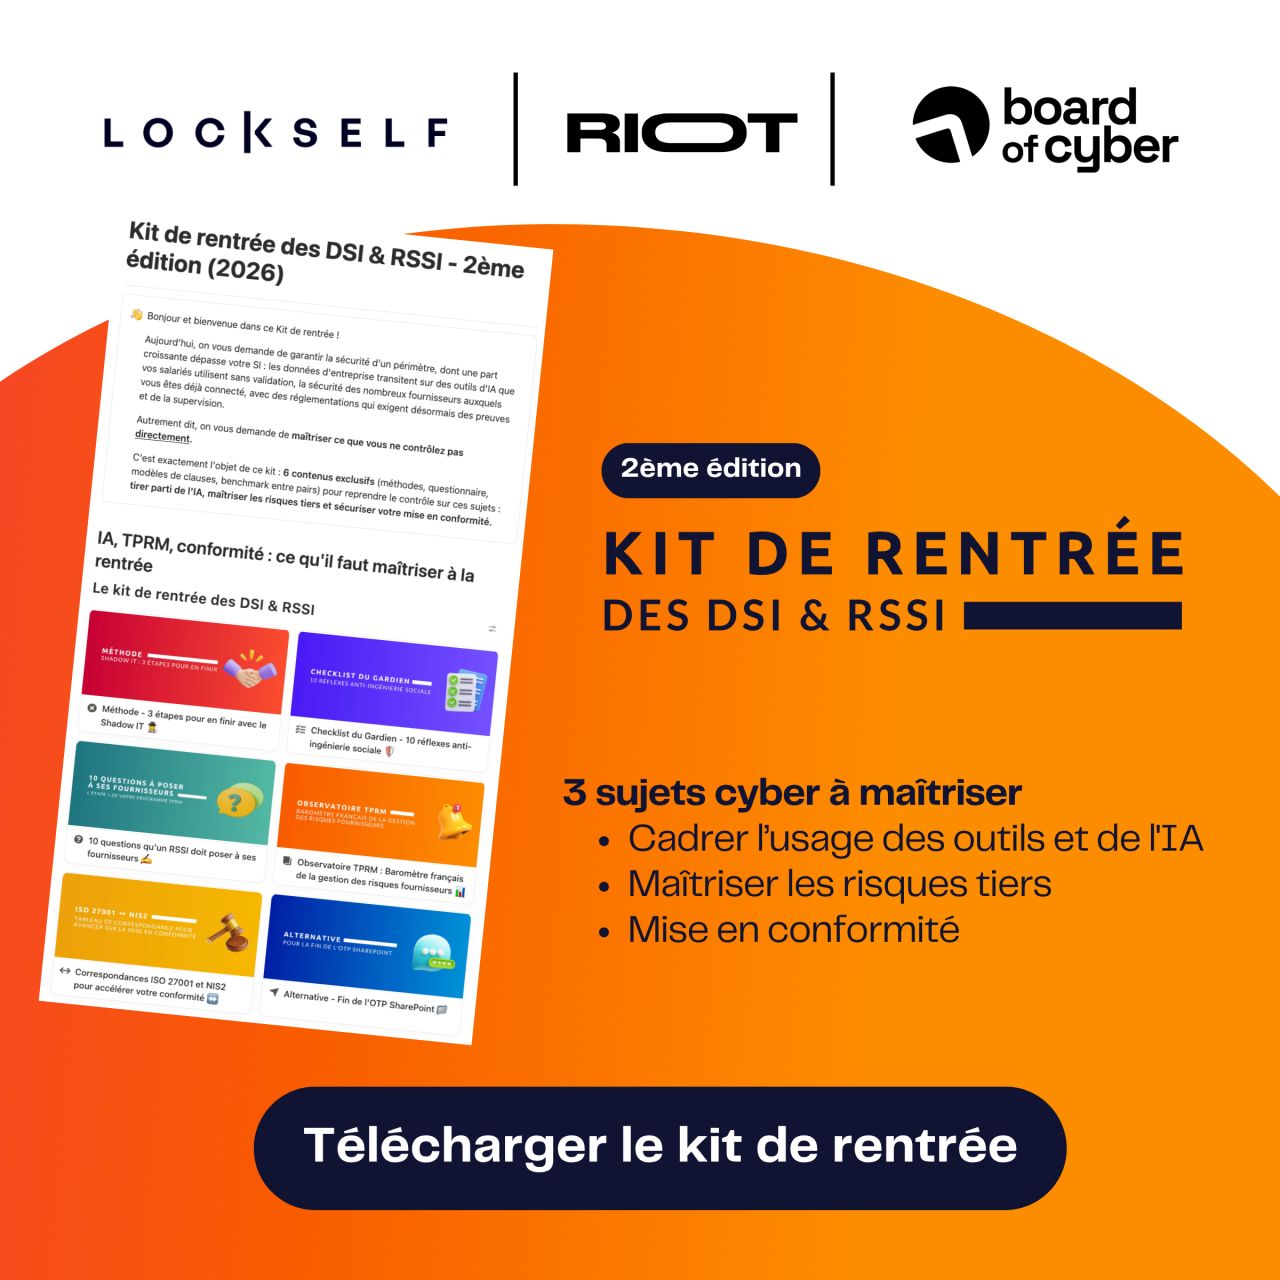
LockSelf, Riot et Board of Cyber réunissent 6 contenus concrets pour aider les DSI et RSSI à sécuriser les usages, mieux maîtriser les risques tiers et produire les éléments attendus dans leurs démarches de conformité.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.