LinkedIn image ad examples
1,342 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- Alice (Formerly ActiveFence)Since 8 Oct 2026
The most interesting attack surfaces are the ones still being discovered. Alice is building a screened network of proven offensive security specialists for selective, project-based AI red teaming. Work across emerging GenAI, LLM and agentic systems, investigate new attack surfaces, and build deeper AI security expertise alongside specialist peers. Explore what breaks next.
- CyberGlobalSince 10 Oct 2026
Your team builds applications. Add white-label security testing with PentX: starting from €2,500/year
- CyberGlobalSince 10 Oct 2026
Sell white-label pentesting service without recruiting pentesters. PentX: €2,500/year.
- ZynapSince 10 Oct 2026
Zynap's autonomous offensive security agent tests your environment inside the scope and policy you define, with every action auditable.
- 0patchSince 9 Oct 2026
One year after Microsoft Windows 10 end of support, the bill goes up: on October 13, 2026 the first year of business ESU ends and year two costs twice as much per device. 0patch keeps Windows 10 secure until 2030 for a fraction of that. Just in-memory micropatches, no reboots, no Microsoft account, central management for the whole fleet. See how it compares before you renew.
- 0patchSince 9 Oct 2026
Microsoft Office 2021 reaches end of support on October 13 – and unlike Microsoft Windows 10, there is no ESU program. 0patch keeps it patched until at least 2029, with no reboots and no forced upgrade. One license covers Windows 10 too.
- IvantiSince 7 Oct 2026
The most prepared orgs can see risk clearly, understand what matters most and confidently respond when conditions change.
- IvantiSince 7 Oct 2026
Calculate how resilient your patching process is against AI-driven threats. See where your organization really stands.
- InfoGuard AGSince 7 Oct 2026
🔐 𝐒𝐞𝐜𝐮𝐫𝐢𝐭𝐲 𝐀𝐰𝐚𝐫𝐞𝐧𝐞𝐬𝐬 𝐢𝐬𝐭 𝐦𝐞𝐡𝐫 𝐚𝐥𝐬 𝐒𝐞𝐧𝐬𝐢𝐛𝐢𝐥𝐢𝐬𝐢𝐞𝐫𝐮𝐧𝐠. Sie ist Teil unternehmerischer Verantwortung. Der «European Cyber Security Month» rückt im Oktober europaweit Cyber Security und den bewussten Umgang mit digitalen Risiken in den Fokus. Für mich ist das ein guter Anlass, eine Frage zu stellen, die auf die Agenda jeder Geschäftsleitung gehört: ❓𝐖𝐨𝐫𝐚𝐧 𝐞𝐫𝐤𝐞𝐧𝐧𝐞𝐧 𝐰𝐢𝐫, 𝐨𝐛 𝐮𝐧𝐬𝐞𝐫𝐞 𝐒𝐞𝐜𝐮𝐫𝐢𝐭𝐲 𝐀𝐰𝐚𝐫𝐞𝐧𝐞𝐬𝐬 𝐭𝐚𝐭𝐬ä𝐜𝐡𝐥𝐢𝐜𝐡 𝐰𝐢𝐫𝐤𝐭? Nicht allein an Abschlussquoten oder der Klickrate einer Phishing-Simulation. Entscheidend ist, wie Mitarbeitende handeln, wenn es darauf ankommt: ▶️ Melden sie verdächtige E-Mails – auch nach einem unbedachten Klick? ▶️ Sprechen sie Unsicherheiten frühzeitig an? ▶️ Funktionieren Meldewege auch unter Zeitdruck? ▶️ Wissen sie, was bei einem Sicherheitsvorfall zu tun ist? Für mich zeigt sich genau hier, ob Security Awareness wirklich Teil der Unternehmenskultur ist – oder am Ende doch nur ein Pflichtprogramm bleibt. Fehler werden sich nie vollständig verhindern lassen. Entscheidend ist deshalb, wie gut eine Organisation darauf vorbereitet ist und wie handlungsfähig sie bleibt, wenn etwas passiert. 𝐃𝐢𝐞 𝐔𝐦𝐬𝐞𝐭𝐳𝐮𝐧𝐠 𝐯𝐨𝐧 𝐒𝐞𝐜𝐮𝐫𝐢𝐭𝐲 𝐀𝐰𝐚𝐫𝐞𝐧𝐞𝐬𝐬 𝐥ä𝐬𝐬𝐭 𝐬𝐢𝐜𝐡 𝐝𝐞𝐥𝐞𝐠𝐢𝐞𝐫𝐞𝐧. 𝐃𝐢𝐞 𝐕𝐞𝐫𝐚𝐧𝐭𝐰𝐨𝐫𝐭𝐮𝐧𝐠 𝐝𝐚𝐟ü𝐫 𝐧𝐢𝐜𝐡𝐭. Wirksame Security Awareness beginnt deshalb bei der Führung. Regulatorische Anforderungen wie NIS2 unterstreichen diese Verantwortung für betroffene Organisationen zusätzlich. Mitarbeitende müssen Risiken einordnen und in kritischen Situationen angemessen handeln können. Gleichzeitig müssen Organisationen aus Simulationen, Meldungen und realen Vorfällen lernen. Ziel sind nicht fehlerfreie Mitarbeitende, sondern widerstandsfähige Organisationen. Und genau diese Widerstandsfähigkeit ist eine Führungsaufgabe. Wie wird Security Awareness in eurem Unternehmen gesteuert: als jährliche Pflichtübung – oder als Bestandteil der unternehmerischen Resilienz? Am 22. Oktober zeigt Sarah Mühlemann, Cyber Security Consultant bei InfoGuard AG, in unserem Webinar, wie menschenzentrierte Security Awareness in der Praxis funktioniert und wie daraus eine nachhaltig gelebte Sicherheitskultur entsteht. Den Link zur Anmeldung findet ihr im Kommentar. 👇
- IntelliGRCRecorded 12 Oct 2026
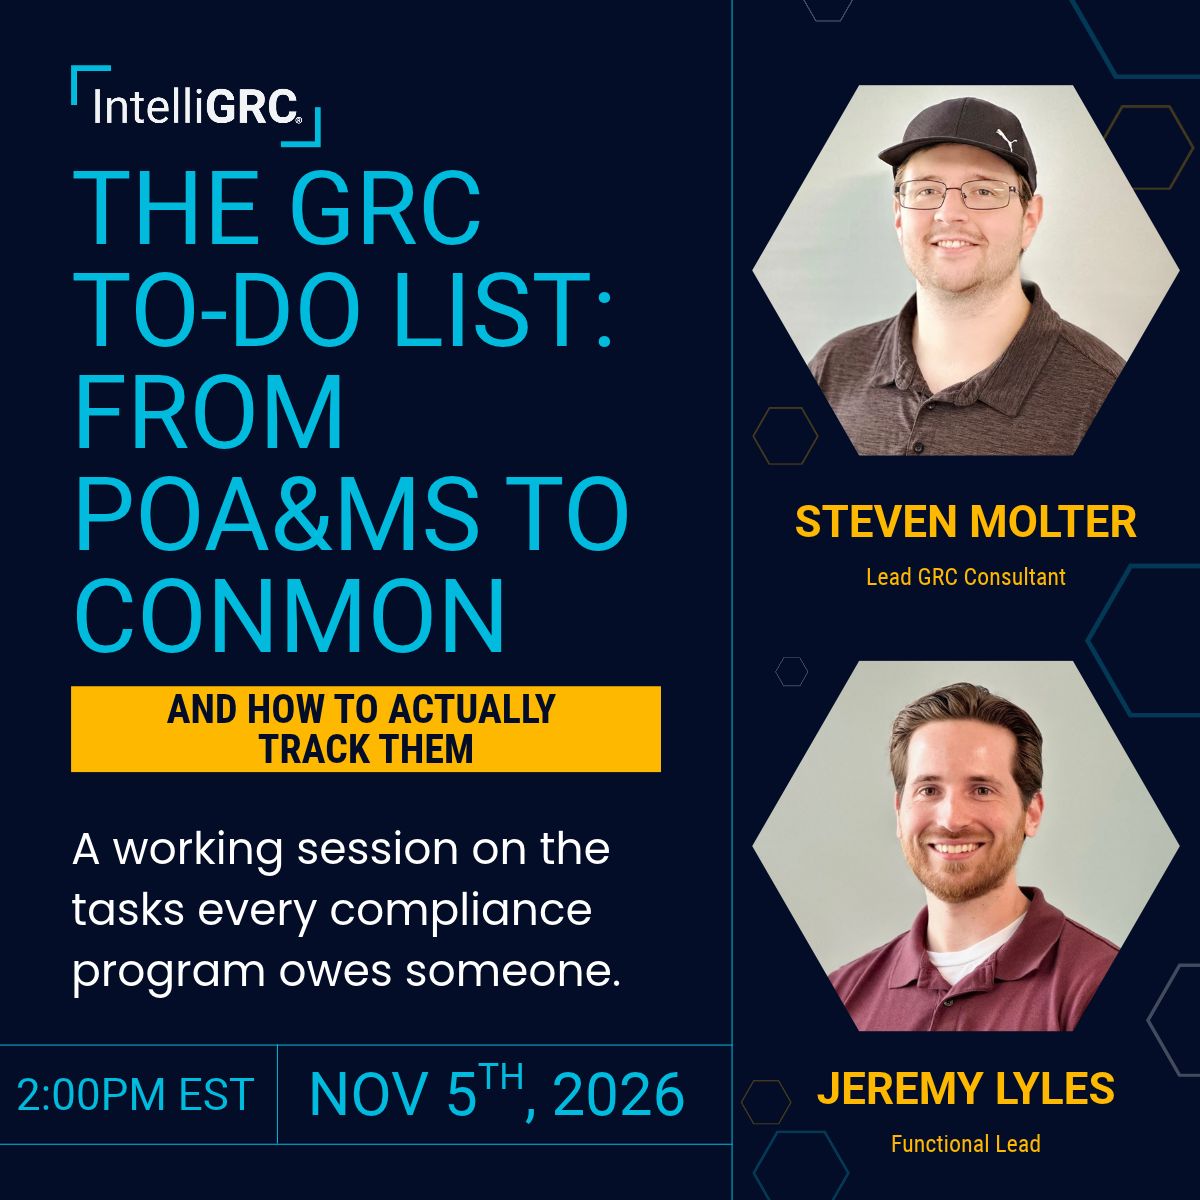
Every compliance program comes with a to-do list nobody hands you. Initial implementation POA&Ms. Post-assessment POA&Ms. Operational POAs under 3.12.2. ConMon activities. Evidence requests before your assessment. If you're tracking all of that in a spreadsheet, you're probably one missed row away from a finding. On November 5, join Steven Molter and Jeremy L. as they break down what separates each of these. Then watch as they go live in the IntelliGRC platform to show how to turn them into tracked, auditable action items with Action Plan and ConMon. You'll leave knowing what has to get done. And with a way to prove it got done. Thursday, Nov 5 | 2:00 to 3:00 PM ET Register here: https://hubs.li/Q04zsf500 #CMMC #NIST800171 #GRC #POAM #ContinuousMonitoring
- 1PasswordSince 9 Oct 2026
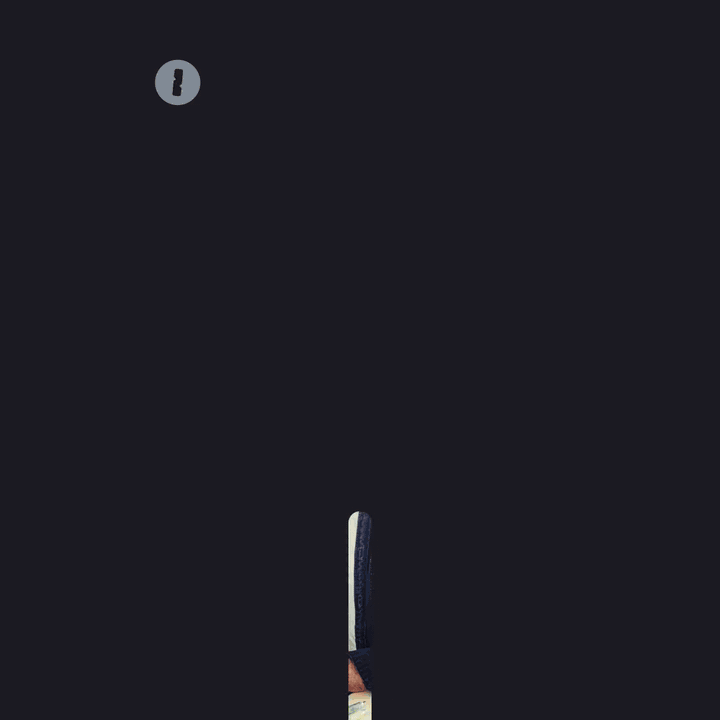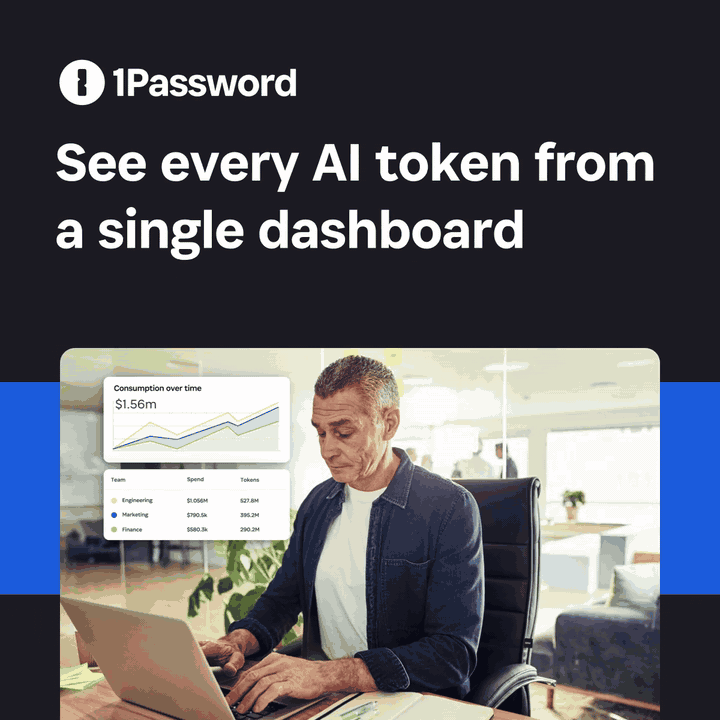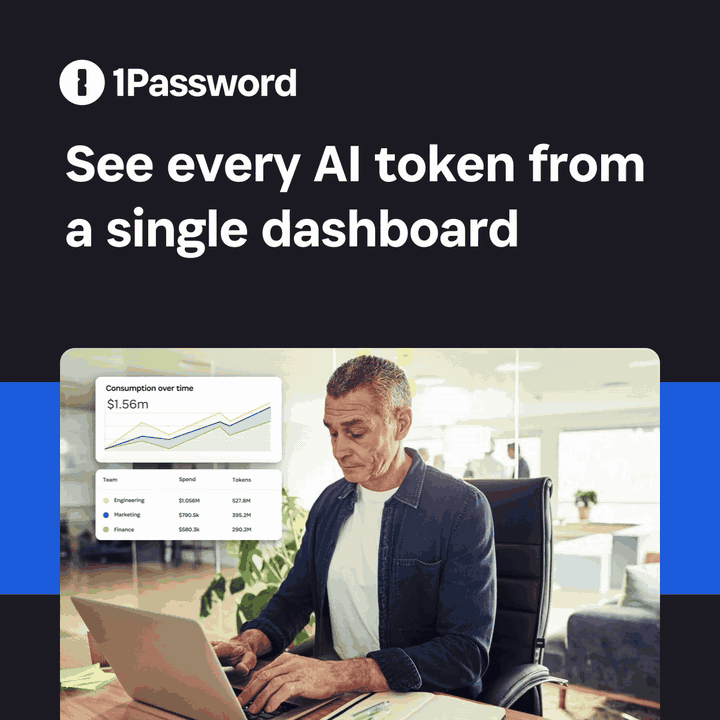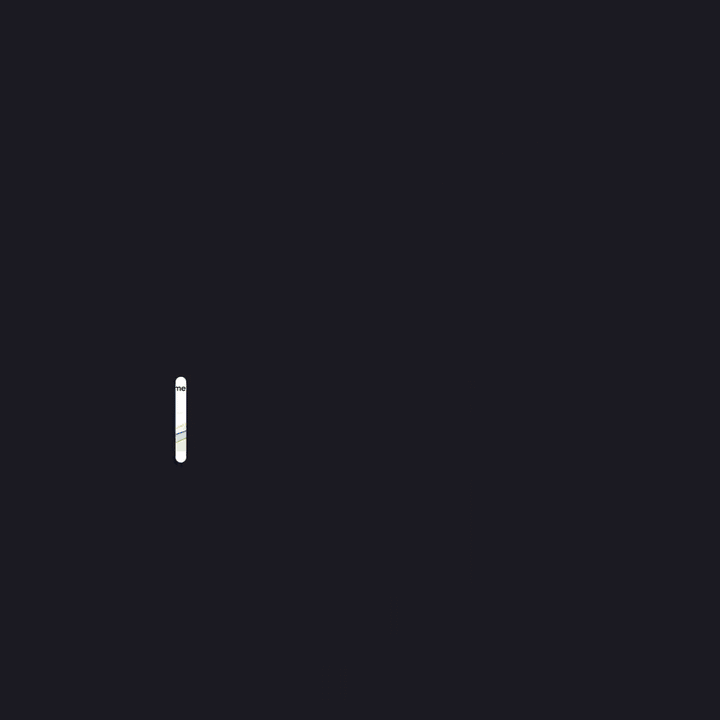
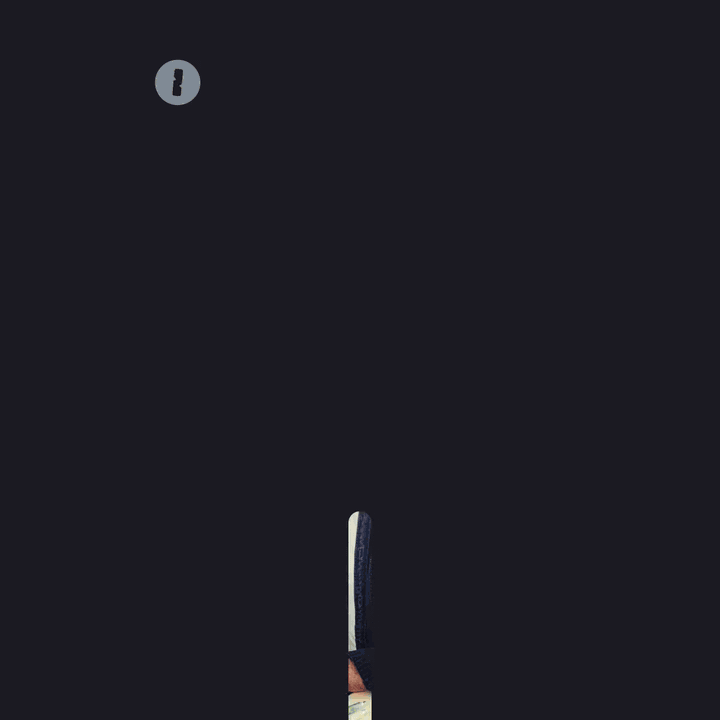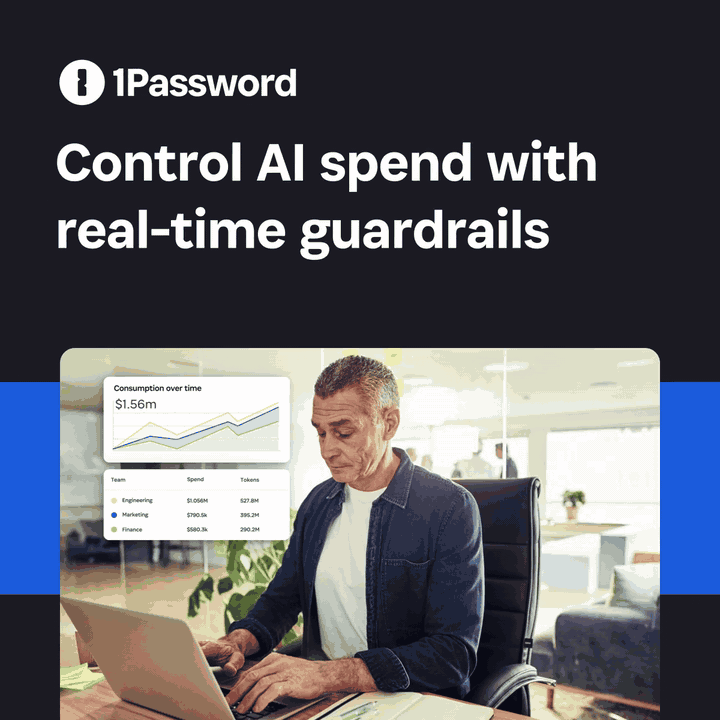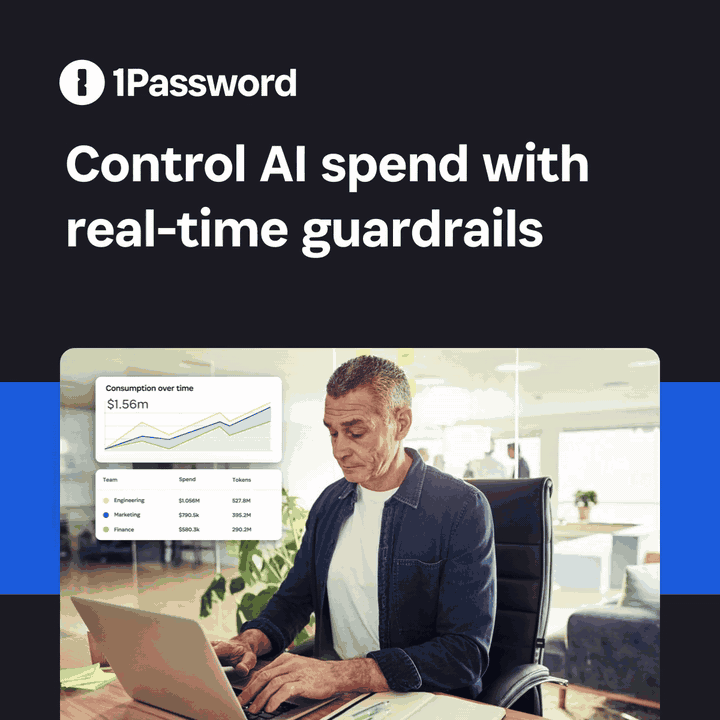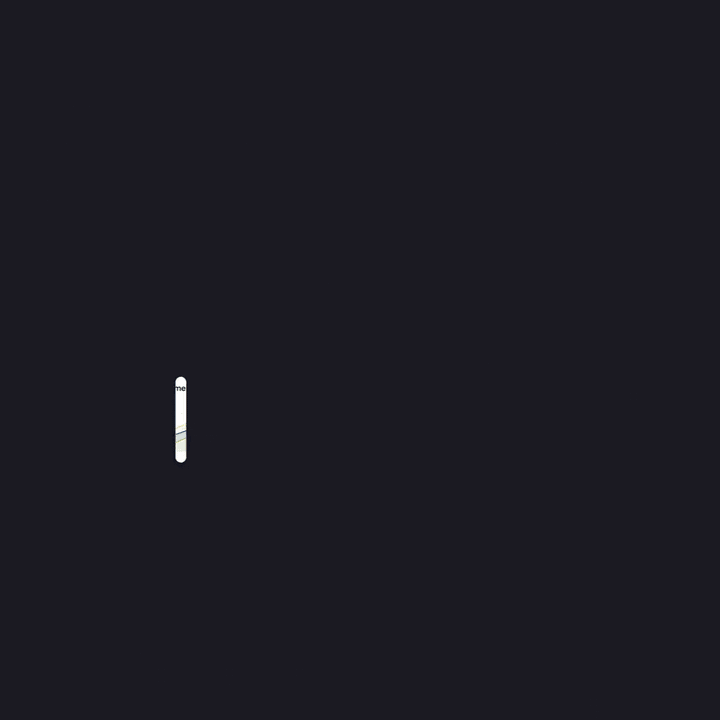
Stop reacting to bills, and start monitoring AI spend. See what your stack costs, who’s driving consumption, and where the budget is going.
- 1PasswordSince 10 Oct 2026
Get the complete picture of your company’s AI consumption. Make the shift from fragmented vendor dashboards to user-level insight in one dashboard.
- ECOS Technology GmbHSince 7 Oct 2026
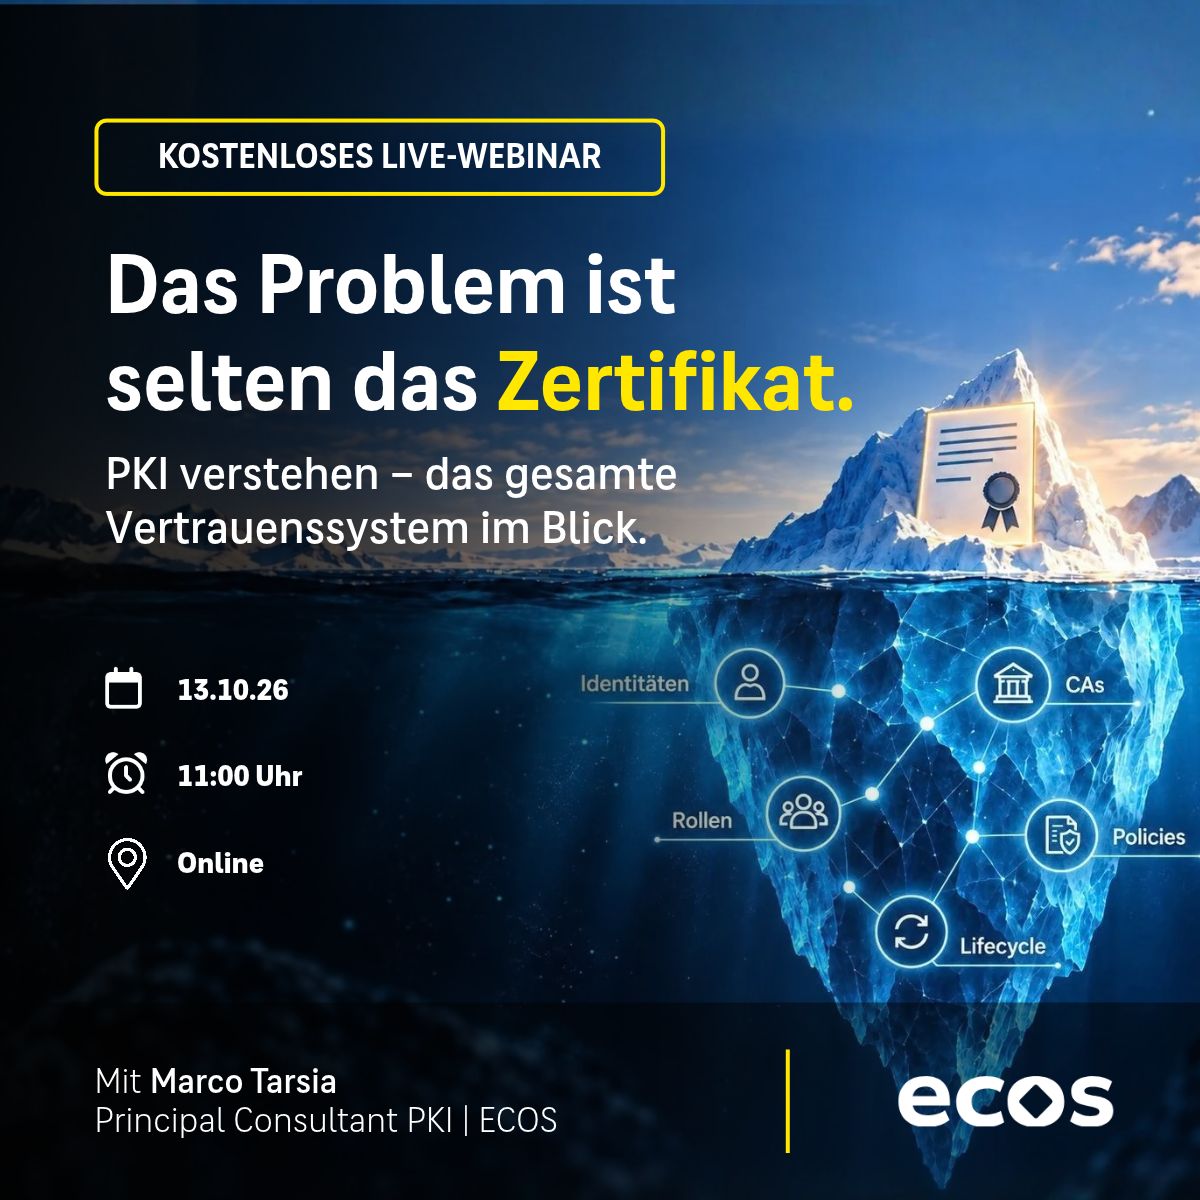
Entscheidend ist selten das einzelne Zertifikat – sondern das Zusammenspiel dahinter. 𝗘𝗿𝗳𝗮𝗵𝗿𝗲𝗻 𝗦𝗶𝗲, 𝘄𝗶𝗲 𝗚𝗼𝘃𝗲𝗿𝗻𝗮𝗻𝗰𝗲, 𝗥𝗼𝗹𝗹𝗲𝗻 𝘂𝗻𝗱 𝗟𝗶𝗳𝗲𝗰𝘆𝗰𝗹𝗲 für 𝗸𝗹𝗮𝗿𝗲 𝗩𝗲𝗿𝘁𝗿𝗮𝘂𝗲𝗻𝘀𝘀𝘁𝗿𝘂𝗸𝘁𝘂𝗿𝗲𝗻 sorgen.
- ECOS Technology GmbHSince 7 Oct 2026
Das Zertifikat ist oft nur die sichtbare Spitze. Im Live-Webinar zeigen wir, was darunterliegt: Identitäten, CAs, Rollen, Policies und Lifecycle.
- DarktraceSince 7 Oct 2026
Prompt injection hides inside ordinary email, with no links or attachments for a human reader to catch. Here's how it works.
- ControlMonkeySince 7 Oct 2026
Your Okta is backed up. But can you actually recover it when something breaks? AI and automation are making the recovery gap harder to ignore.
- DAGMASince 7 Oct 2026
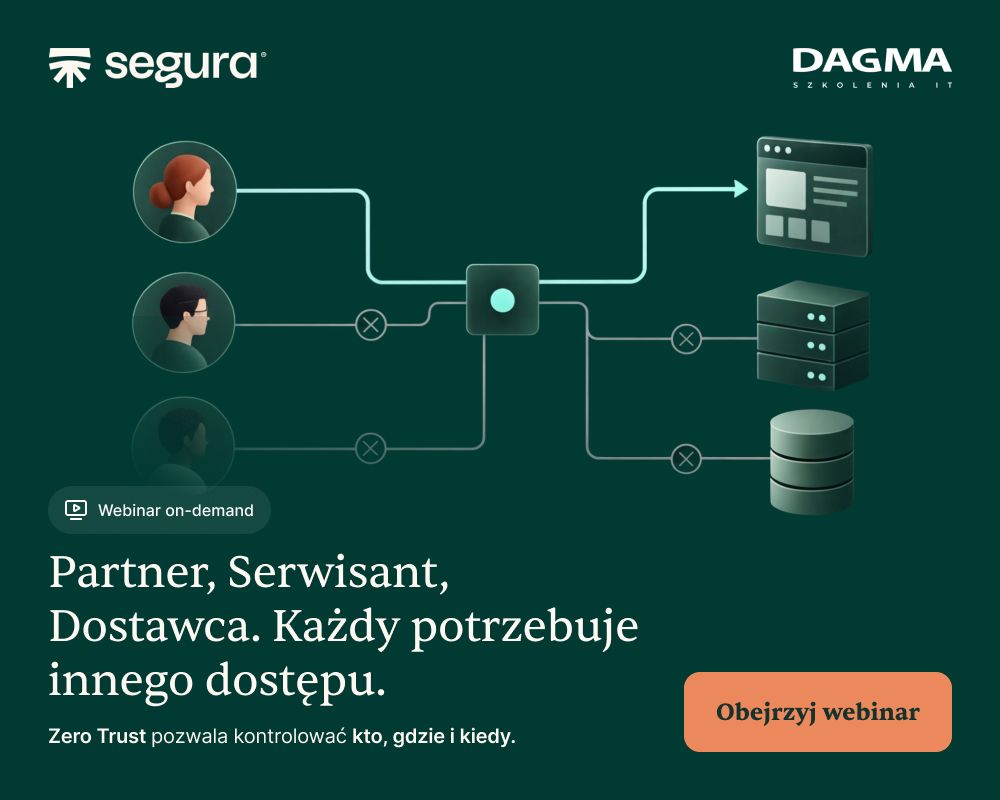
Kto naprawdę ma dostęp do Twojej infrastruktury? Administratorzy, partnerzy, serwisanci i zewnętrzni dostawcy potrzebują dostępu do firmowych zasobów. Problem zaczyna się wtedy, gdy dostęp oznacza zbyt szerokie uprawnienia. Zero Trust odwraca tę logikę: nie ufaj domyślnie. Weryfikuj. Ograniczaj dostęp do tego, co rzeczywiście potrzebne. W webinarze ON-DEMAND pokazujemy, jak wygląda to w praktyce z wykorzystaniem Domum SEGURY. ▶ ZAPISZ SIĘ I OBEJRZYJ KIEDY MASZ CZAS
- Fig SecuritySince 9 Oct 2026
How can you ship SecOps changes like software? You know, without breaking prod, breaking the SIEM, or breaking your soul and spirit... We're hosting a live webinar to show you exactly how! Join Gal Shafir and John Port, Sr. Detection Engineer at CLEAR, and discover how to ship SecOps changes so smoothly that your SecOps infrastructure sends you a thank-you note. October 13th - 11:00 AM ET. Link to register: https://lnkd.in/dpZZrBRR
- ESET ItaliaSince 9 Oct 2026
☕️ La Colazione da ESET arriva a Bologna! Il 20 ottobre ci troviamo a Palazzo Gnudi per una mattinata dedicata a confronto, #innovazione e #cybersecurity, con uno sguardo alle nuove sfide legate all’Intelligenza Artificiale. Un momento per incontrare il team ESET, scambiare idee e punti di vista e, naturalmente, fare colazione insieme. 😉 📅 20 ottobre 2026 | dalle 10:00 📍 Palazzo Gnudi, Via Riva di Reno 77/a, Bologna Prenota il tuo posto 👉 https://bit.ly/4dtlzom
- Fig SecuritySince 9 Oct 2026
Andddd Fig Security wins Best SIEM Innovation of 2026! 🎉🍾 We just won the Cybersecurity Breakthrough Awards for Best SIEM Innovation without being a SIEM... or a pipeline... or anything that ends in -OAR. How, you may ask? Well, we let SecOps engineers build, test, and ship SecOps changes to prod like software, so the SIEM can finally do the thing you bought it for. Breakthrough innovation, we know! Thanks CyberSecurity Breakthrough!
- ForcepointSince 7 Oct 2026
Most organizations can't name every AI agent running in their environment. Find out how to close the visibility and enforcement gap.
- ForcepointSince 7 Oct 2026
An agent using every permission exactly as granted can still cause a breach. Governance has to check behavior, not just access.
- IduraSince 8 Oct 2026
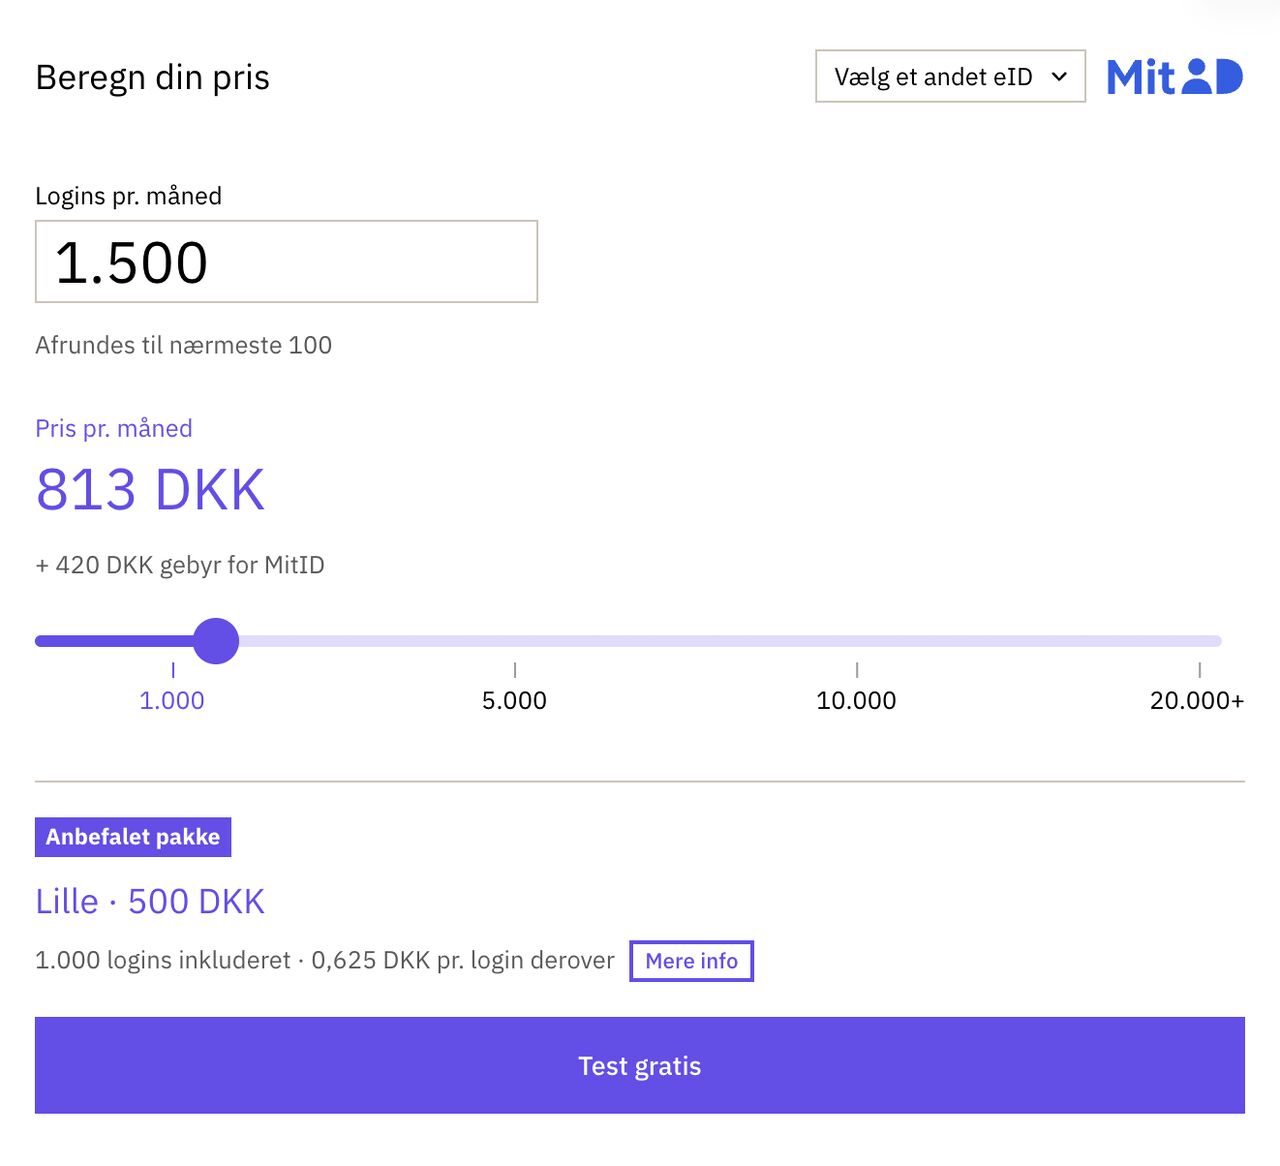
"Vi vender tilbage til dig, så snart vi kan," får man ofte at vide, når man spørger om prisen hos mange udbydere af eID-løsninger. Hos Idura tager det 10 sekunder og 1 klik. Med vores nye prisberegner ser du præcis, hvad I kommer til at betale, baseret på antal login eller signaturer om måneden. Du slipper for at vente på svar eller booke møder bare for at finde ud af, hvad det koster. Du kan nå at læse dette opslag, klikke dig ind, indtaste jeres volumen og komme i gang - hurtigere end andre udbydere overhovedet når at svare på din formular. 👉 Prøv den og se om du kan nå at tælle til 10, før du har prisen: https://lnkd.in/eXjZhwCM/?utm_campaign=2026(DK):PrisberegnerafSarahTimann&utm_source=linkedin&utm_medium=paid&utm_id=1219103694&hsa_acc=502678833&hsa_cam=1219103694&hsa_grp=901343104&hsa_ad=1585840744&hsa_net=linkedin&hsa_ver=3
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.