LinkedIn image ad examples
1,341 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- F5Since 14 Oct 2026
AI is creating new runtime attack surfaces every day. Learn how to secure AI models, agents, tools, and data before they become business risks.
- F5Since 14 Oct 2026
Watch this on-demand session to learn how AI-powered risk scoring, API discovery, and consistent policy enforcement stop AI-based attacks and exploits before they launch.
- DriveLock SESince 14 Oct 2026
⏰ Es ist Zeit für die it-sa 2026! Wir freuen uns, Sie auf der führenden Messe für IT-Sicherheit willkommen zu heißen. Besuchen Sie unseren Stand und erleben Sie die HYPERSECURE IT Platform live in Aktion! 👉 Buchen Sie jetzt Ihren Termin und sichern Sie sich Ihr kostenfreies Ticket. Lassen Sie uns gemeinsam Ihre IT-Sicherheit auf das nächste Level heben! Wir freuen uns auf Sie!
- DriveLock SESince 14 Oct 2026
Wir freuen uns, Sie auf der führenden Messe für IT-Sicherheit willkommen zu heißen. Besuchen Sie unseren Stand und erleben Sie die HYPERSECURE IT Platform live in Aktion! 📢 Sichern Sie sich unten Ihr kostenloses Ticket. Neben spannenden Präsentationen und Demos unserer innovativen Lösungen, laden wir Sie herzlich zu einem persönlichen Gespräch ein. Genießen Sie einen exquisiten Kaffee von unserem Barista – auf uns! ☕ Lassen Sie uns gemeinsam Ihre IT-Sicherheit auf das nächste Level heben! Wir freuen uns auf Sie! 👇
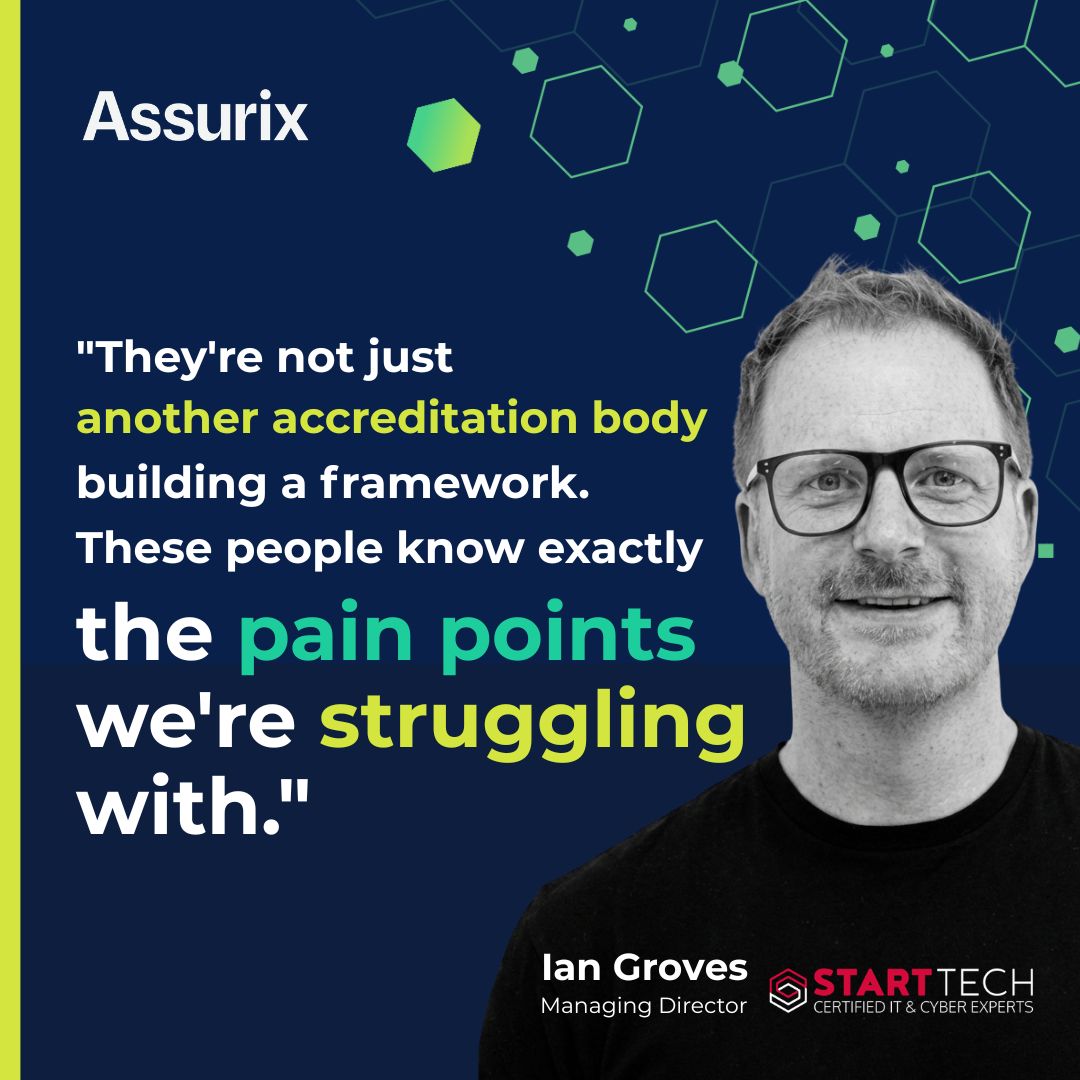
- AssurixRecorded 16 Oct 2026
"When we were looking out on the market, there wasn't really anything that had the depth and breadth that Assurix brings." - Ian Groves, Managing Director, Start Tech
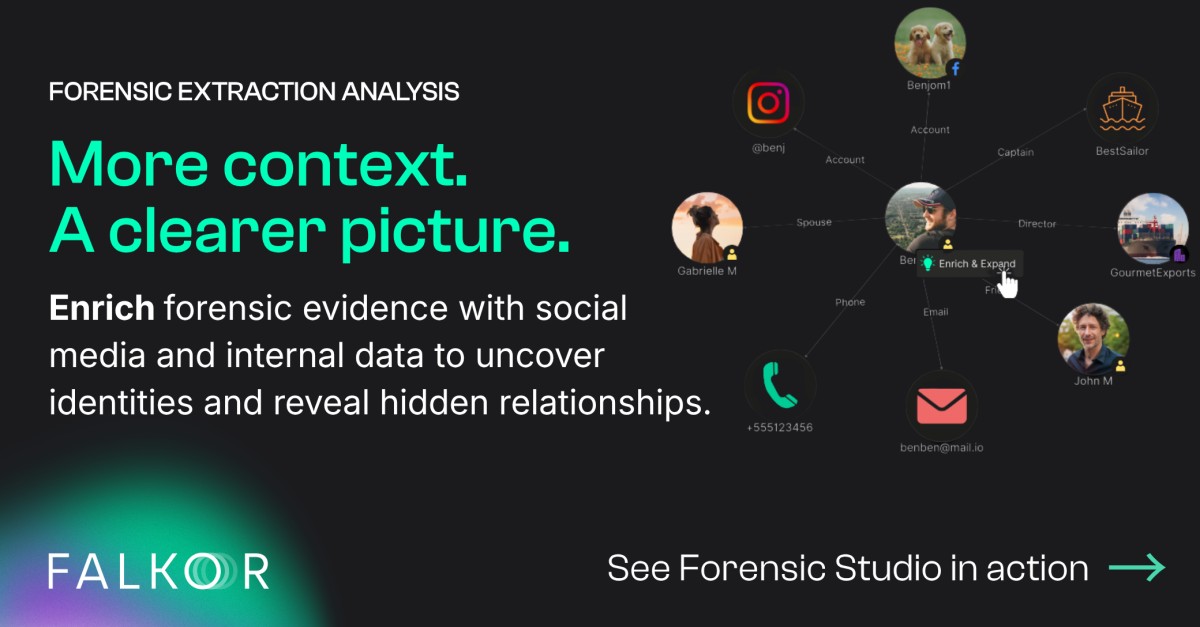
- FalkorSince 14 Oct 2026
Find what matters. Faster. Upload forensic extractions and quickly surface relevant messages, contacts, and activity, so you can focus your review and move the investigation forward. Separate devices. Shared leads. Uncover shared contacts, locations, and activity patterns across devices to reveal connections and open new lines of investigation. More context. A clearer picture. Connect digital forensic evidence with social media and internal databases to identify people, understand relationships, and see how the evidence fits together. See Falkor in action.
- FalkorSince 14 Oct 2026
Find what matters. Faster. Upload forensic extractions and quickly surface relevant messages, contacts, and activity, so you can focus your review and move the investigation forward. Multiple devices. Shared leads. Uncover shared contacts, locations, and activity patterns across devices to reveal connections and open new lines of investigation. More context. A clearer picture. Bring digital forensic evidence together with social media and internal databases to identify people, understand relationships, and see how the evidence fits together. See Falkor in action.
- AssurixRecorded 16 Oct 2026
If you run a high quality MSP, you’ve probably lost deals to cheaper competitors. Not because your service is worse - but because buyers can’t see the difference. Most MSPs sound identical on paper. Buyers don’t know how to judge operational maturity, so they default to price. This checklist breaks down the 7 proof points buyers actually use to decide between MSPs - and how premium providers make those differences visible.
- IDnowSince 14 Oct 2026
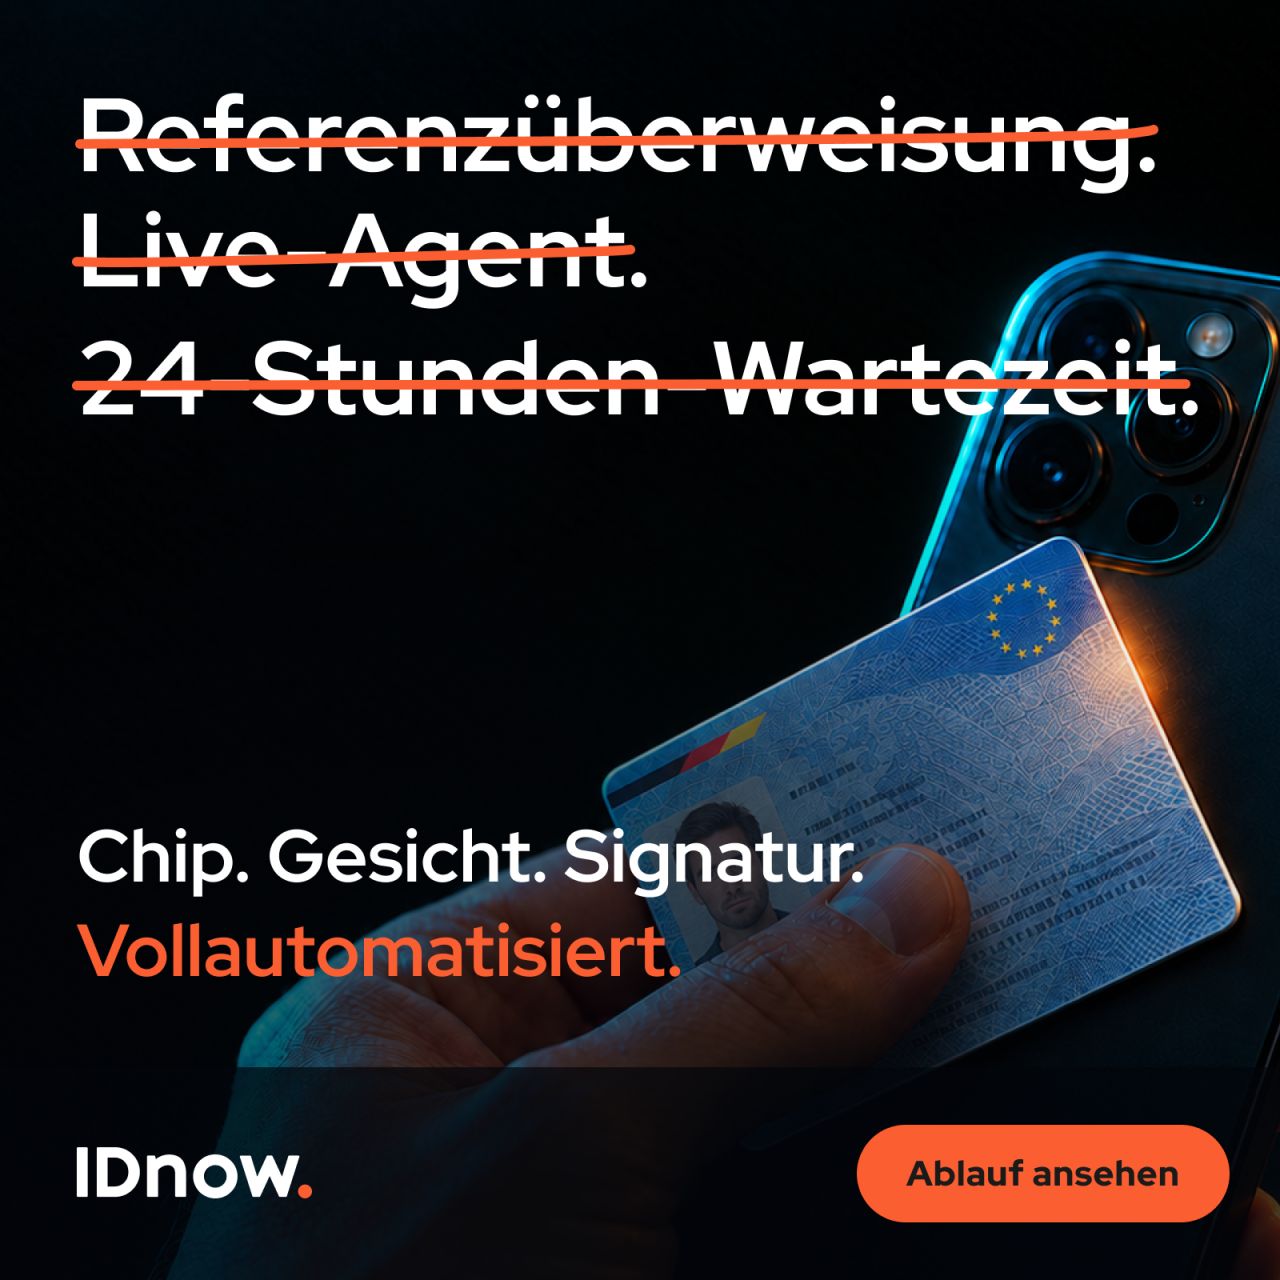
Referenzüberweisung, Live-Agent, 24-Stunden-Wartezeit: Für einen wachsenden Anteil der Customer Journeys ist das nicht mehr nötig. Chip, Gesicht, Signatur, vollständig automatisiert.
- DruvaSince 14 Oct 2026
When I look at customer trends, read the news about breaches, one trend that is clear - Blindly restoring a #backup after an identity breach can trigger your next incident. Attackers (humans and NHIs) who log in with valid credentials don’t go rouge right away. They quietly set themselves up to stay: shadow admins, tweaked conditional access policies, rogue OAuth permissions. Restore an unverified snapshot and you put all of it back into production. Same backdoors. Same attacker. Round two. Recovered isn’t the same as trusted. What matters is "Mean Time to Good State": how fast you get back to an environment you can trust. Getting past “restore and hope” takes: * Behavioral insight that maps human and non-human activity to known attacker techniques * A clear view of impact and blast radius * Containment and #recovery recommendations backed by evidence. Less guesswork, faster response, a shorter "Mean Time to Good State". Really proud of what our team built here. See how Druva Identity Resilience breaks the reinfection loop: https://ow.ly/FQLj50ZOWwe #IdentitySecurity #CyberResilience #IncidentResponse #ZeroTrust #Druva
- Avaneidi S.p.A.Since 12 Oct 2026
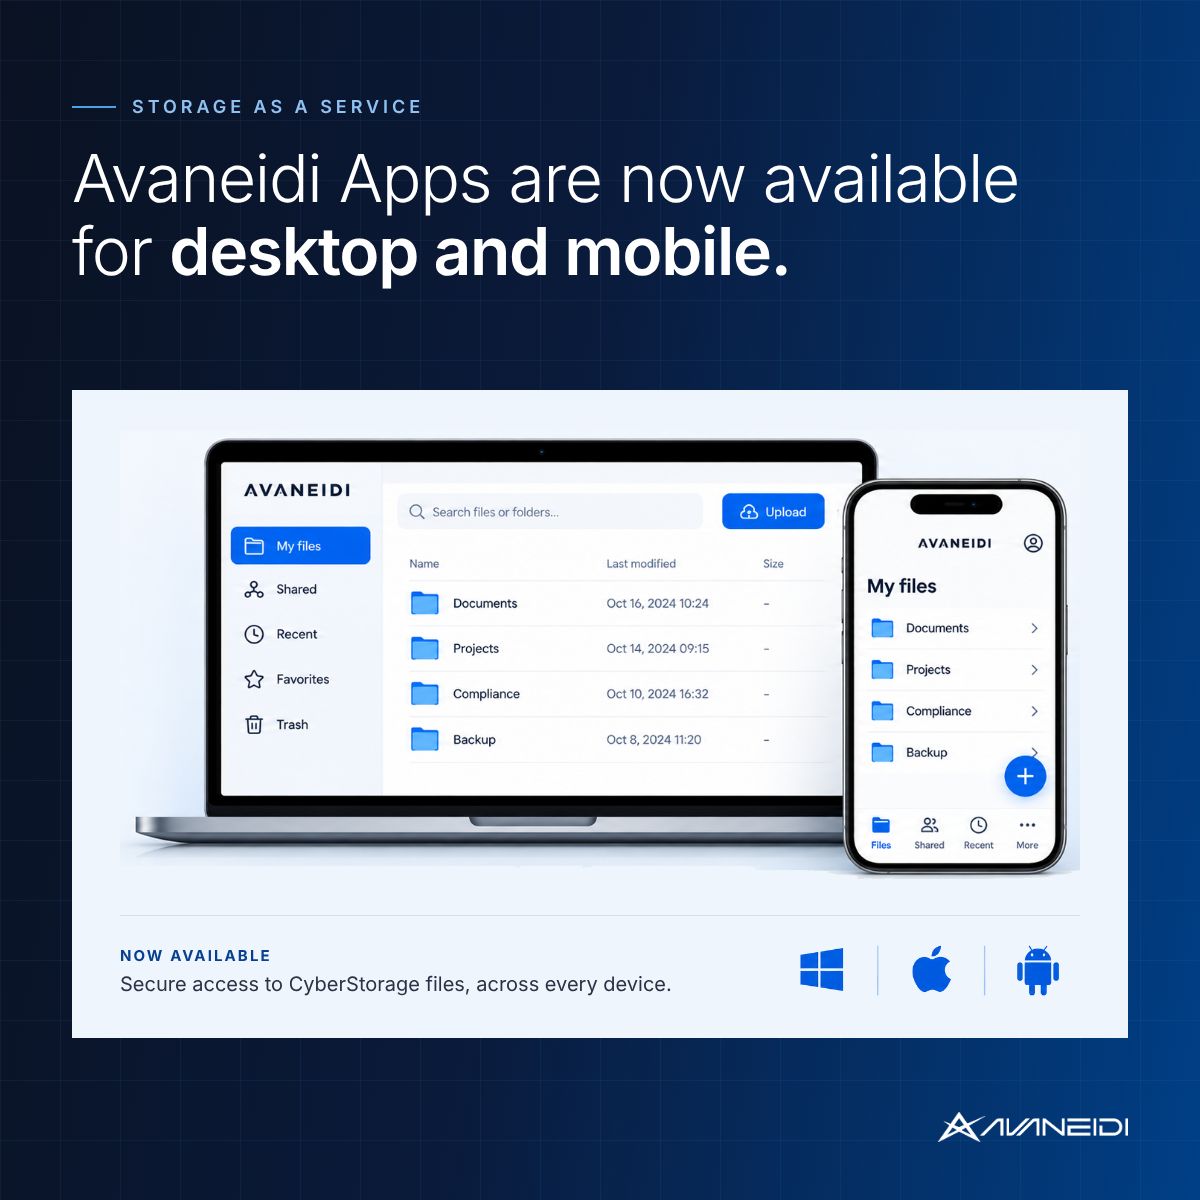
💻📱 𝗔𝘃𝗮𝗻𝗲𝗶𝗱𝗶 𝗔𝗽𝗽𝘀 𝗮𝗿𝗲 𝗻𝗼𝘄 𝗮𝘃𝗮𝗶𝗹𝗮𝗯𝗹𝗲 𝗳𝗼𝗿 𝗱𝗲𝘀𝗸𝘁𝗼𝗽 𝗮𝗻𝗱 𝗺𝗼𝗯𝗶𝗹𝗲. They provide secure access to your data and simpler data management, across devices. Behind the Apps is our 𝗦𝘁𝗼𝗿𝗮𝗴𝗲 𝗮𝘀 𝗮 𝗦𝗲𝗿𝘃𝗶𝗰𝗲 𝗽𝗹𝗮𝘁𝗳𝗼𝗿𝗺. It combines the flexibility of a private cloud with our proprietary CyberStorage technology, integrating security and data protection at every level: hardware, firmware, storage management and governance. Because the flexibility of the cloud and hardware-level security should not require a trade-off. 𝗪𝗵𝗮𝘁 𝘆𝗼𝘂 𝘀𝗲𝗲 𝗶𝘀 𝗮 𝘀𝗶𝗺𝗽𝗹𝗲 𝗮𝗽𝗽. 𝗪𝗵𝗮𝘁 𝘆𝗼𝘂 𝗱𝗼𝗻'𝘁 𝘀𝗲𝗲 𝗶𝘀 𝘀𝗲𝗰𝘂𝗿𝗶𝘁𝘆 𝗲𝗻𝗴𝗶𝗻𝗲𝗲𝗿𝗲𝗱 𝗶𝗻𝘁𝗼 𝘁𝗵𝗲 𝘀𝘁𝗼𝗿𝗮𝗴𝗲 𝗶𝘁𝘀𝗲𝗹𝗳. More at https://lnkd.in/d6B-sb8e #Avaneidi #StorageAsAService #PrivateCloud #CyberStorage #SecurityByDesign
- EnclaveSince 13 Oct 2026
We ran Meta's Muse Wonder through our AI Hacking Race. It verified 6 of 11 vulnerable runs, tied GPT-6 Sol for fourth, and tripped none of the patched controls. On the same benchmark, Muse Spark 1.3 verified none. One generation closed almost the entire gap to the frontier of what we've measured. https://lnkd.in/dXgMP-n7
- HalbornSince 13 Oct 2026
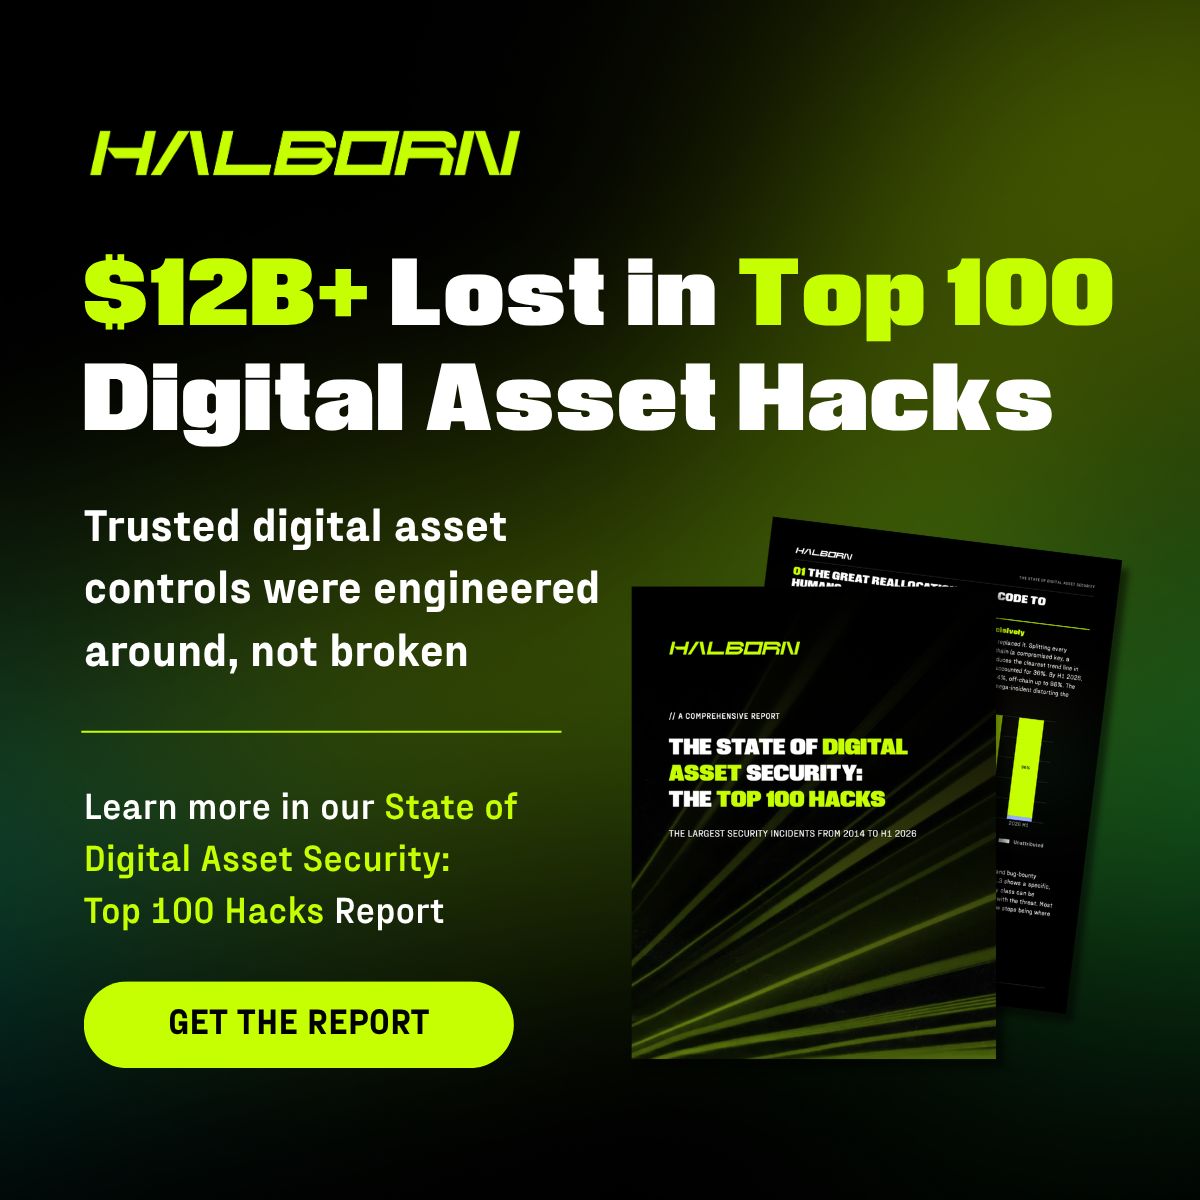
The 100 largest digital asset hacks since 2014 cost more than $12 billion. 👉 https://lnkd.in/d39mqkNF Off-chain causes drove 36% of losses in 2021 and 96% in H1 2026. Keys, signing workflows, and vendors are now where the money is lost. See where the attack surface moved in Halborn’s Top 100 Hacks research.
- CantinaSince 13 Oct 2026
Your security backlog isn’t just alerts. Investigations, access reviews, and exposures all compete for your team’s time. Put Clarion’s AI agents to work across your security stack, with your team setting the policies and approvals.
- CYB3R OPERATIONSSince 13 Oct 2026
Nobody has ever asked you for a security rating. They ask you to produce the register, show which services depend on which suppliers, and answer quickly when one of them is hit. That's what Averro is built to produce, from the list you already keep. Fourteen days. 250 suppliers. No card.
- CYB3R OPERATIONSSince 13 Oct 2026
You keep the register. You also know it's out of date the moment you save it. Averro audits the list you already keep, in both directions: what's on it that nobody has looked at in two years, and what's missing that was never declared. Then it tells you which handful sit under a service that can't stop. Fourteen days. 250 suppliers. No card.
- CantinaSince 13 Oct 2026
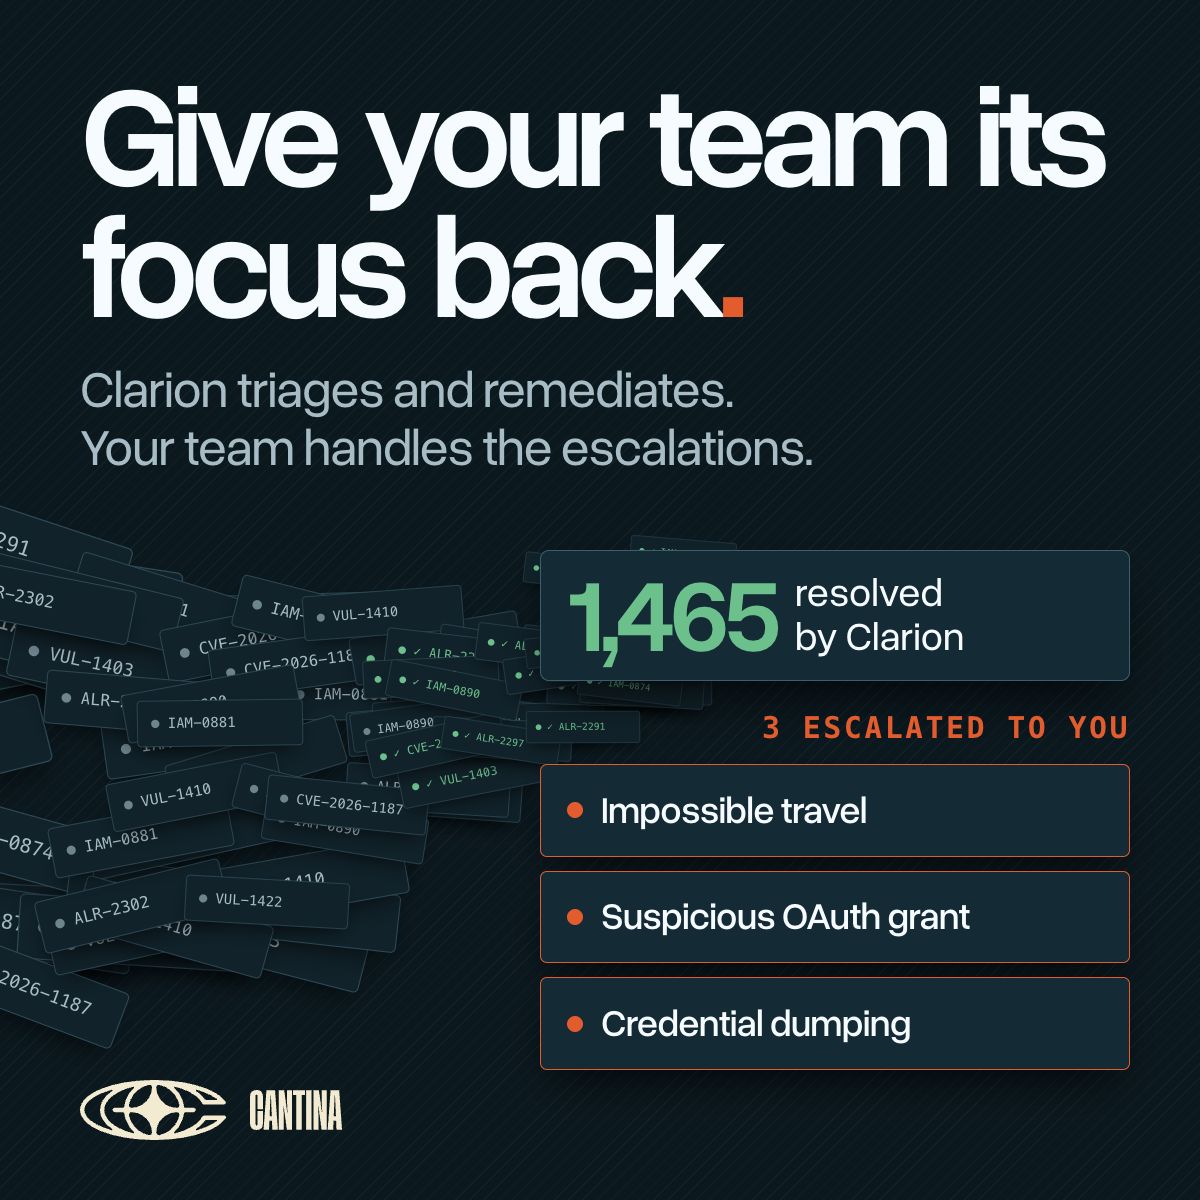
Your security team’s attention is too valuable to spend on noise. In seven days, Clarion triaged 1,468 alerts for one customer and escalated just 3 for human review. Give your team more time for security work that needs its judgment.
- DarktraceSince 13 Oct 2026
AI risk shows up across five distinct areas, from misuse to oversight. Get one framework that covers all five, enterprise-wide.
- HalbornSince 13 Oct 2026
More than $12 billion lost in the 100 largest digital asset hacks since 2014. 👉 https://lnkd.in/d7ahFmX5 Hybrid attacks pair months of social engineering with a technical exploit. No single control, an audit or a hardware wallet alone, stops that chain. Learn how layered controls close the gap in Halborn’s Top 100 Hacks research.
- DarktraceSince 13 Oct 2026
A sales pitch and a real AI capability can look identical from the outside. Our CISO's Guide to Buying AI shows you how to tell them apart.
- Hornetsecurity FranceSince 13 Oct 2026
💻 Prestataire informatique ? Moins de complexité, plus de sérénité pour vos sauvegardes M365. Protégez les données de vos clients en toute simplicité. 👇
- CakewalkSince 13 Oct 2026
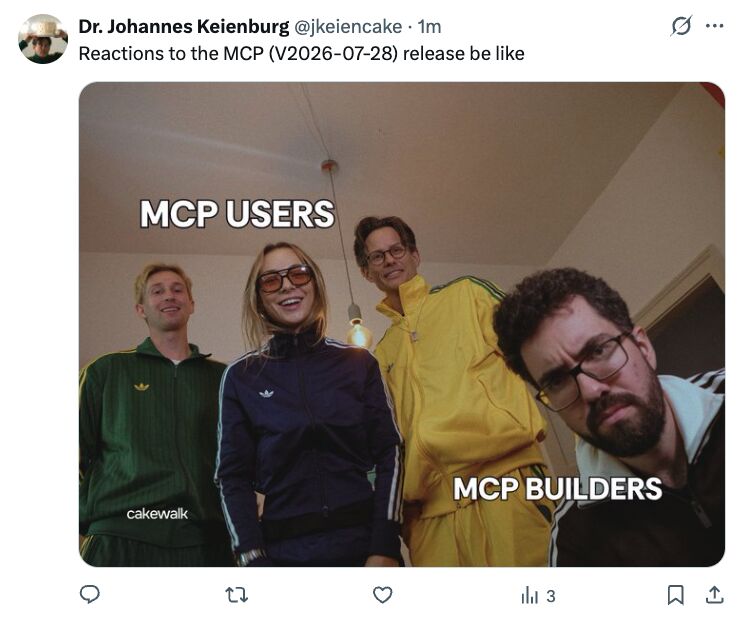
The new MCP standard is very important for anyone who's connecting agents with apps. the Agentic AI Foundation recently released a new MCP standard (V2026-07-28) so here's our read: WHATS NEW: the V2 moves to a stateless protocol core, removing the initialization handshake and protocol-level sessions. Requests become self-contained, making MCP much closer to a standard HTTP workload. OUR TAKE: Good change. Once the ecosystem converges on the new standard, this significantly simplifies MCP infrastructure: no sticky sessions or shared session stores, easier horizontal scaling and recovery, and cleaner routing and authorization, particularly valuable for gateways. BUT it's more promise than control: (tbc in the comments)
- CakewalkSince 13 Oct 2026
agentic auto provisioning is the future of IAM. Fast growing companies are drowning in access provisioning and access removal work. Its one of the most tedious aspects of access management - esp as provisioning is a distributed task with multiple stakeholders across a company. today, modern IT / security / tech ops teams have two options to solve this (none of them are great): PROVISIONING TODAY 🥹 ↳ SCIM based auto provisioning (costs you thousands of dollars for enterprise plans in the apps you want to provision into) ↳ manual provisioning hell AGENT CAKE 🤖🎂 Thats why we’ve built Agent Cake - an AI agent that can provision at no cost. After approval has been given for an employee to get access to an app, Agent Cake does the provisioning work on your behalf. this is a paradigm shift in IAM, and its working like a charm.. Some Agent Cake stats: ↳ Today, 60 applications supported ↳ 93% success ratio (in case the agent cant complete a job, it redirects it to a human); thats one HELL of a ratio!! ↳ Even provisioning and deprovisioning distribution (52% of jobs are provisioning, 48% deprovisioning) We've spoken a lot about controlling AI agent access to other company systems in the last months. But using AI agents to automate access control is as exciting
- Armor DefenseRecorded 15 Oct 2026
Your teams adopted AI faster than security could review it. Now people are pasting unvetted prompts and skills into their agents, and leadership can’t see it. On October 21, Armor CISO Chris Stouff walks through the threats that are real, why the tool already watching your estate was built for people, and what it takes to stop an agent before it acts. 30 minutes plus Q&A, and we'll send the recording if you can't make it live.
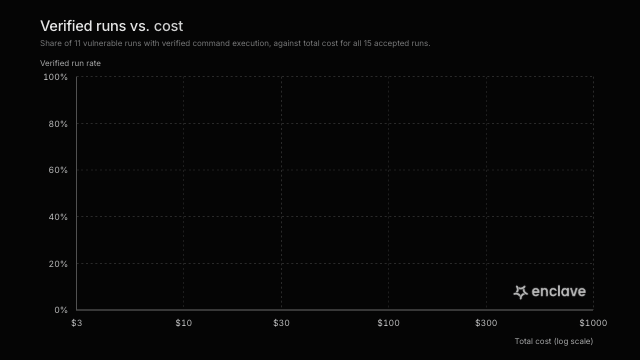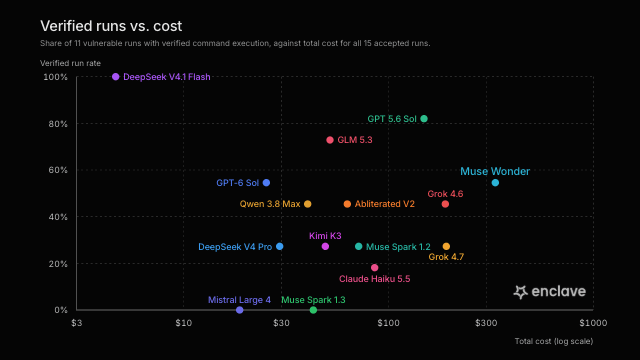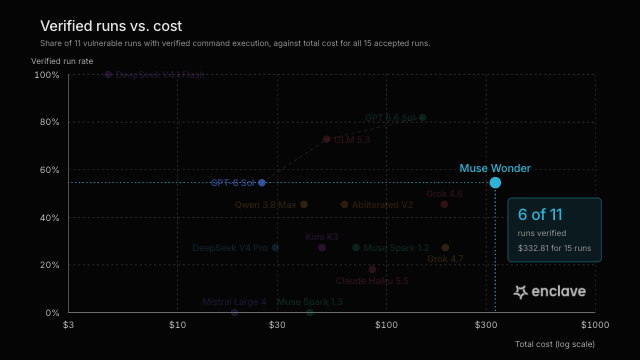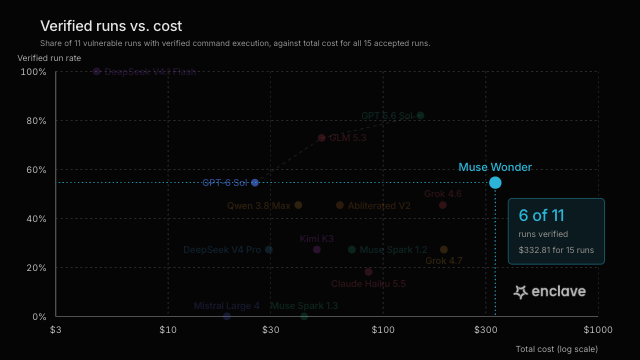
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.