LinkedIn image ad examples
1,352 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- GuardeySince 22 Oct 2026
Een sterk spamfilter houdt veel verdachte mails tegen, maar een hergebruikt wachtwoord of een patiëntendossier bij de verkeerde ontvanger niet. Niet ieder digitaal risico begint met phishing. Daarom traint Guardey medewerkers met wekelijkse security awareness challenges over onder andere privacy, wachtwoordbeveiliging en online bedreigingen. Zo leren ze risico's herkennen die technische beveiliging niet altijd kan voorkomen. Wil je zien hoe je jouw medewerkers bewust maakt van deze risico's? Plan een demo en bekijk de interactieve trainingen van Guardey.
- GuardeySince 22 Oct 2026
Patiënten vertrouwen jouw zorgorganisatie hun meest persoonlijke gegevens toe. Wat als die door een menselijke fout in verkeerde handen terechtkomen? Een datalek raakt niet alleen de privacy van patiënten. Het kan ook hun vertrouwen in jouw organisatie beschadigen. Met Guardey volgen zorgmedewerkers wekelijkse security awareness training over onder andere privacy, wachtwoorden en online bedreigingen. Zo leren ze bewuster omgaan met gevoelige informatie. Hoe je dat vertaalt naar de dagelijkse zorgpraktijk? Plan een demo en ontdek de zorgspecifieke training van Guardey.
- Hunt & HackettSince 23 Oct 2026
Every MDR provider promises 24/7 monitoring, rapid response and AI-assisted analysis. On paper, they all look the same. So how do you tell the difference? Our MDR Buyer's Guide gives you ten dimensions to evaluate providers, from visibility and response authority to evidence retention and data control. Download the guide 👇
- Eye SecuritySince 23 Oct 2026
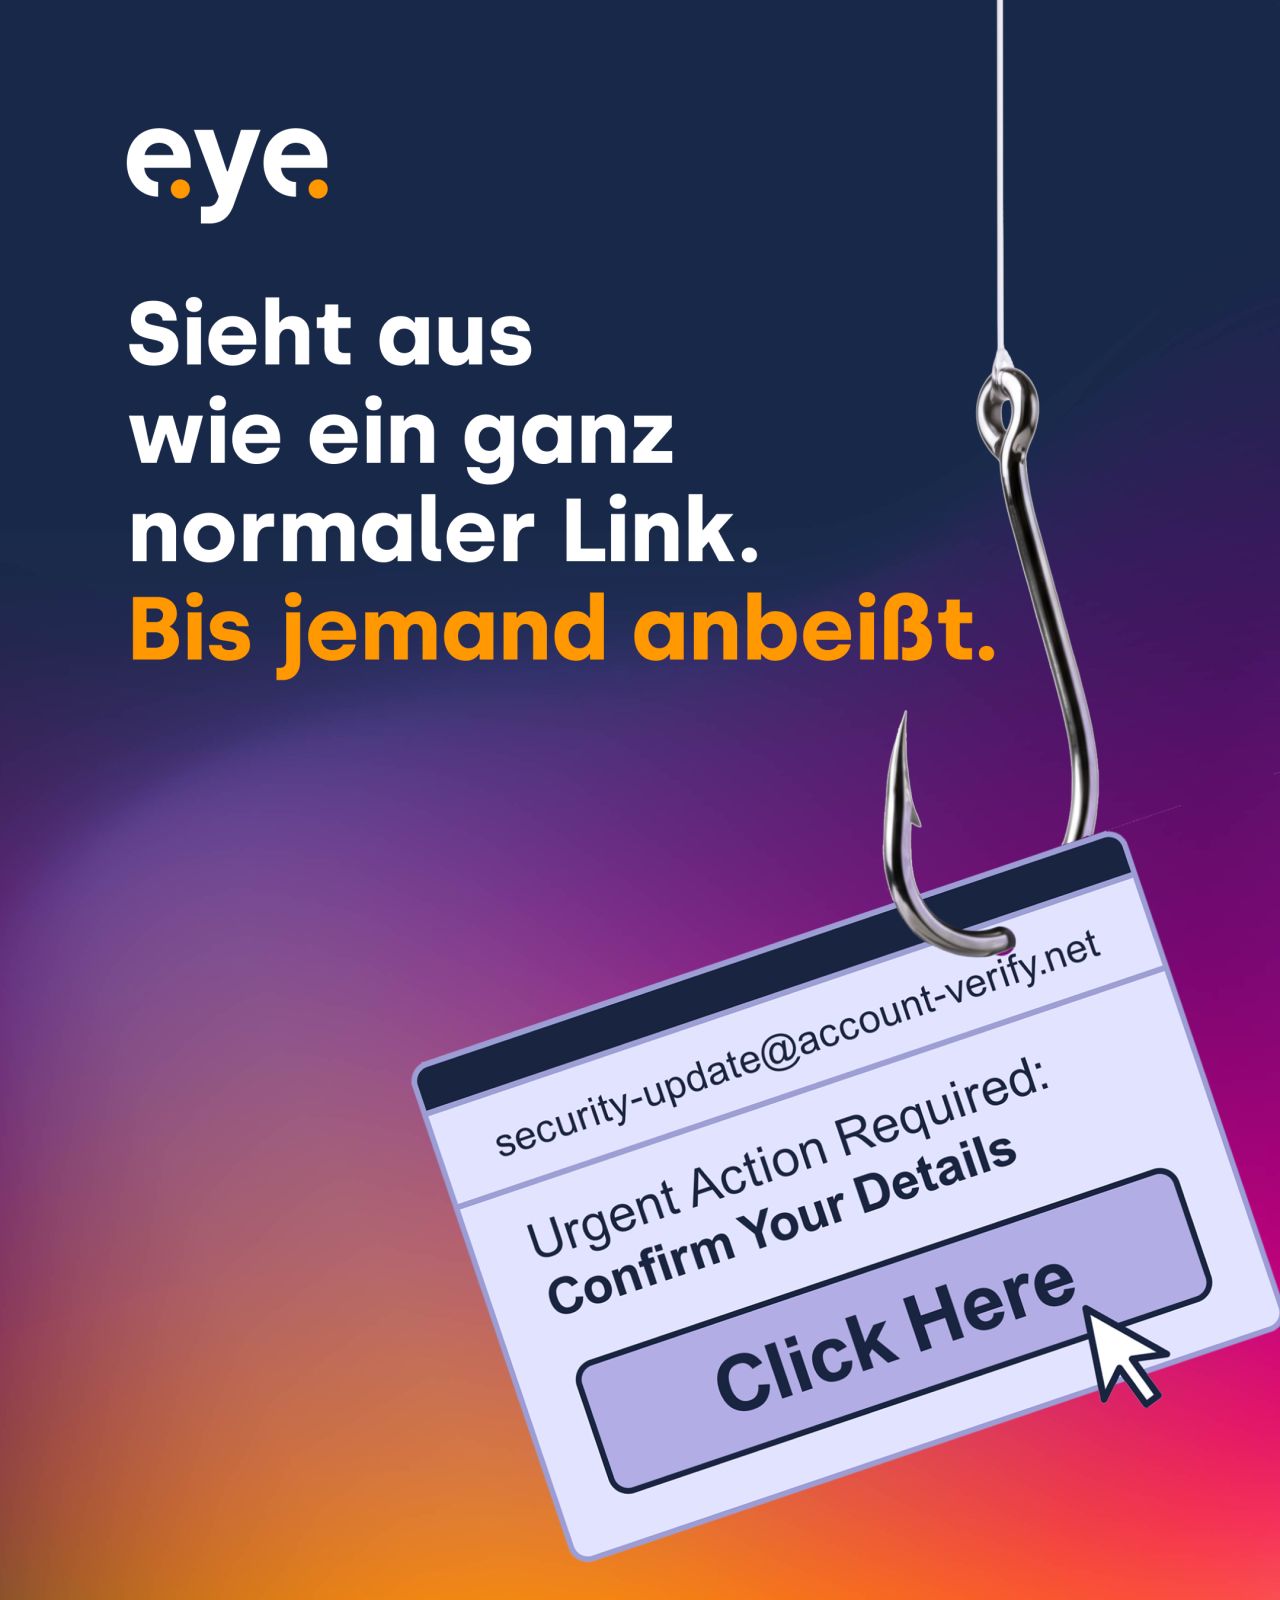
Die meisten Angriffe beginnen nicht mit einem Einbruch, sondern mit einer Anmeldung. Gestohlene Zugangsdaten, ein kompromittiertes Konto oder eine völlig unauffällige Sitzung. Sobald sich ein Angreifer legitim anmelden kann, muss er nichts mehr aufbrechen. Er bewegt sich unbemerkt, erweitert schrittweise seine Berechtigungen und arbeitet sich durch Ihre Umgebung, ohne einen Alarm auszulösen. Wenn etwas verdächtig erscheint, ist er oft schon seit Wochen im System. Eye Security überwacht das Verhalten in Ihrer gesamten Umgebung, erkennt, wenn legitimer Zugriff vom Normalen abweicht, und stoppt Angriffe, bevor daraus eine Sicherheitsverletzung wird.
- GigamonSince 23 Oct 2026
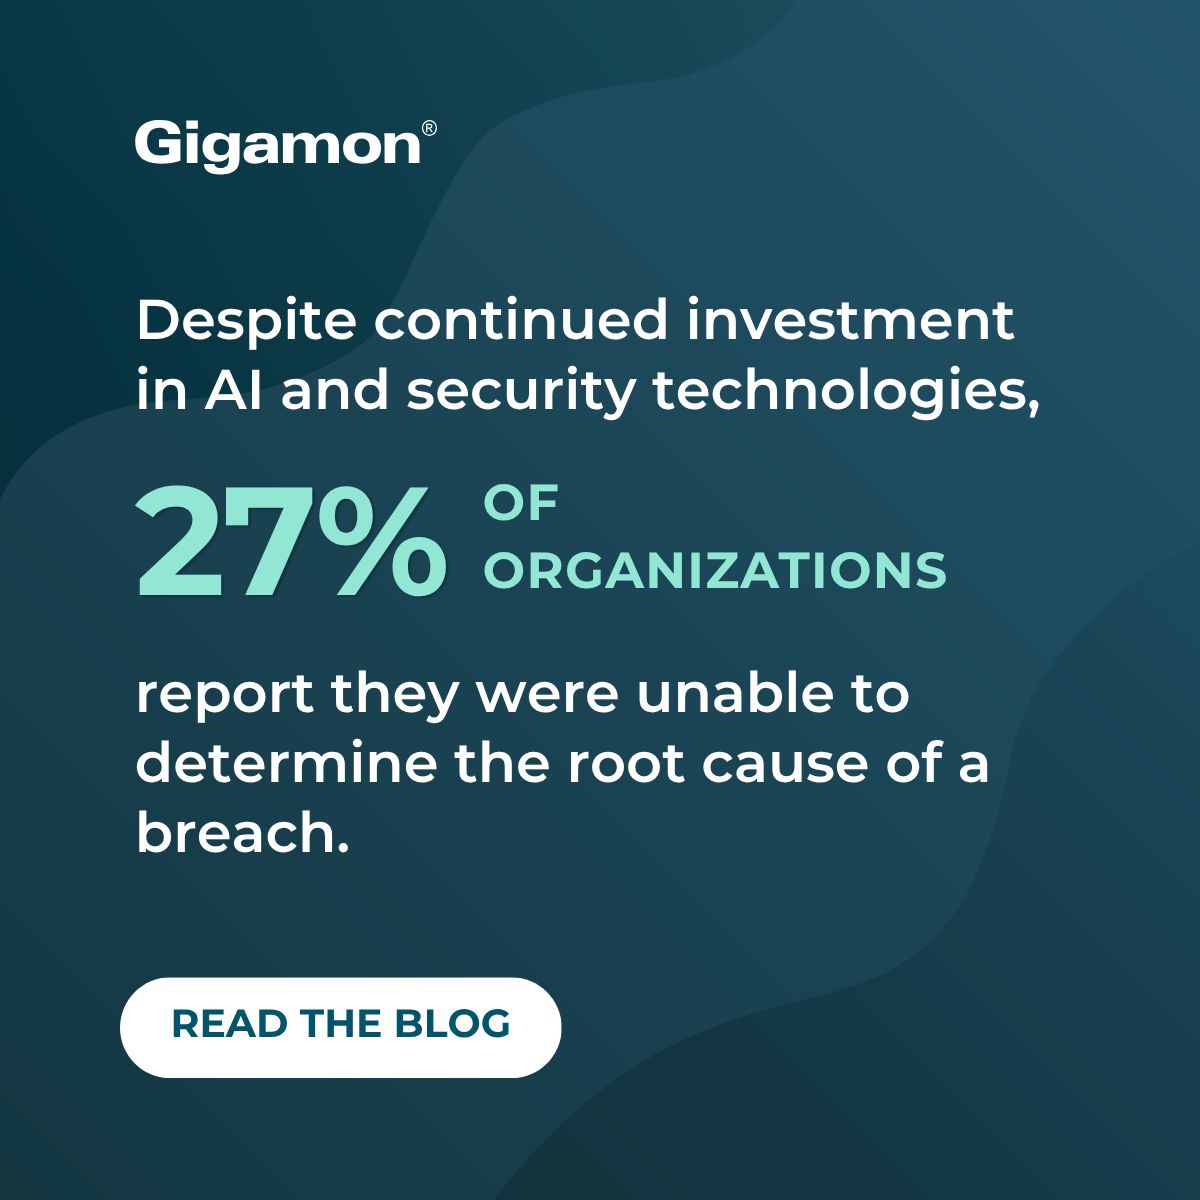
27% could not find a breach root cause. Strengthen decisions with trusted telemetry. Read more.
- Eve SecuritySince 25 Oct 2026
This CISO’s guide shares a structured approach to securing and governing AI agents, plus a readiness checklist. Download below.
- Industrial DefenderSince 23 Oct 2026
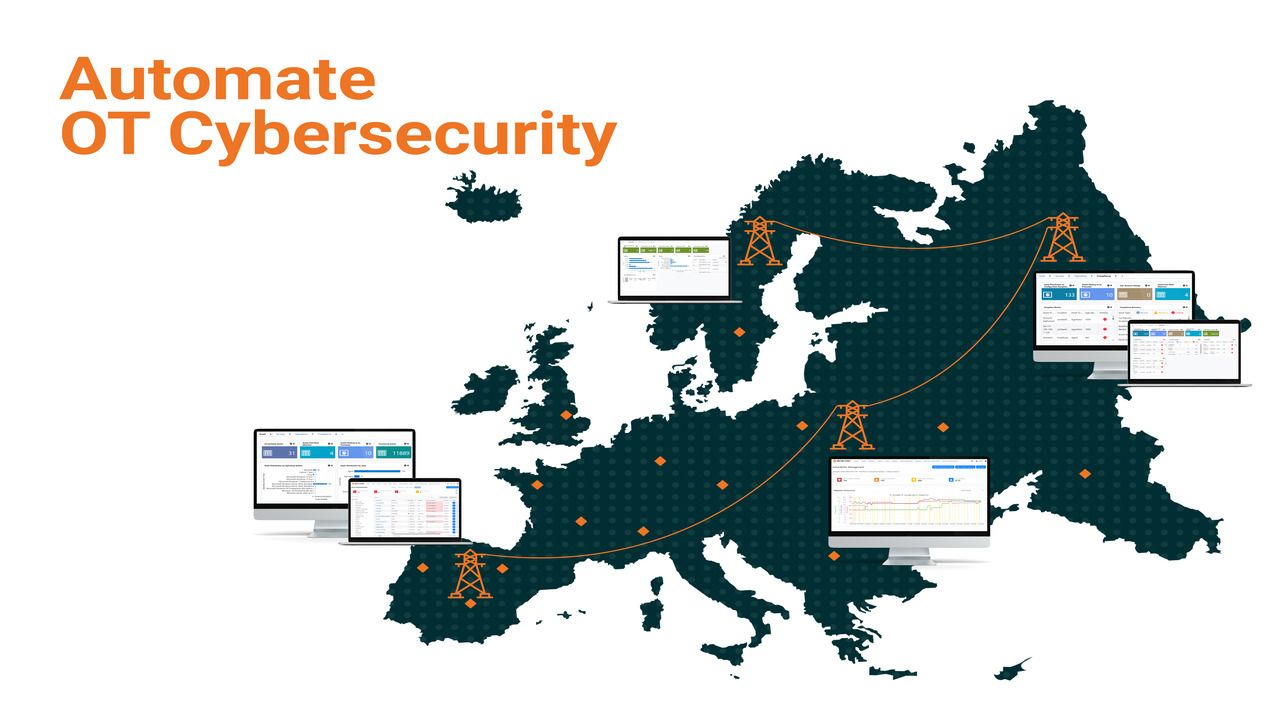
Watch our expert panel discuss the practical realities of NIS2 for industrial operators—transposition divergence, asset visibility requirements, and the 24-hour early warning obligation.
- Eve SecuritySince 24 Oct 2026
This guide is designed to help CISOs assess their AI agent readiness, with a checklist and maturity test. Download below.
- ESETSince 24 Oct 2026
Are you passionate about creating seamless customer experiences, optimizing online performance, and turning data into business impact? We are looking for a Senior Marketing Automation Specialist (m/f/n) who will take ownership of our global customer journey ecosystem, lead experimentation initiatives, support strategic product launches, and champion AI-driven innovation across marketing operations. In this role, you'll have the opportunity to influence customer engagement across email and in-product customer journeys, collaborate with international stakeholders, and help define the next generation of marketing automation, personalization, and AI-driven engagement capabilities.
- Industrial DefenderSince 23 Oct 2026
Watch our expert panel discuss the practical realities of NIS2 for industrial operators—transposition divergence, asset visibility requirements, and the 24-hour early warning obligation.
- GitGuardianSince 22 Oct 2026
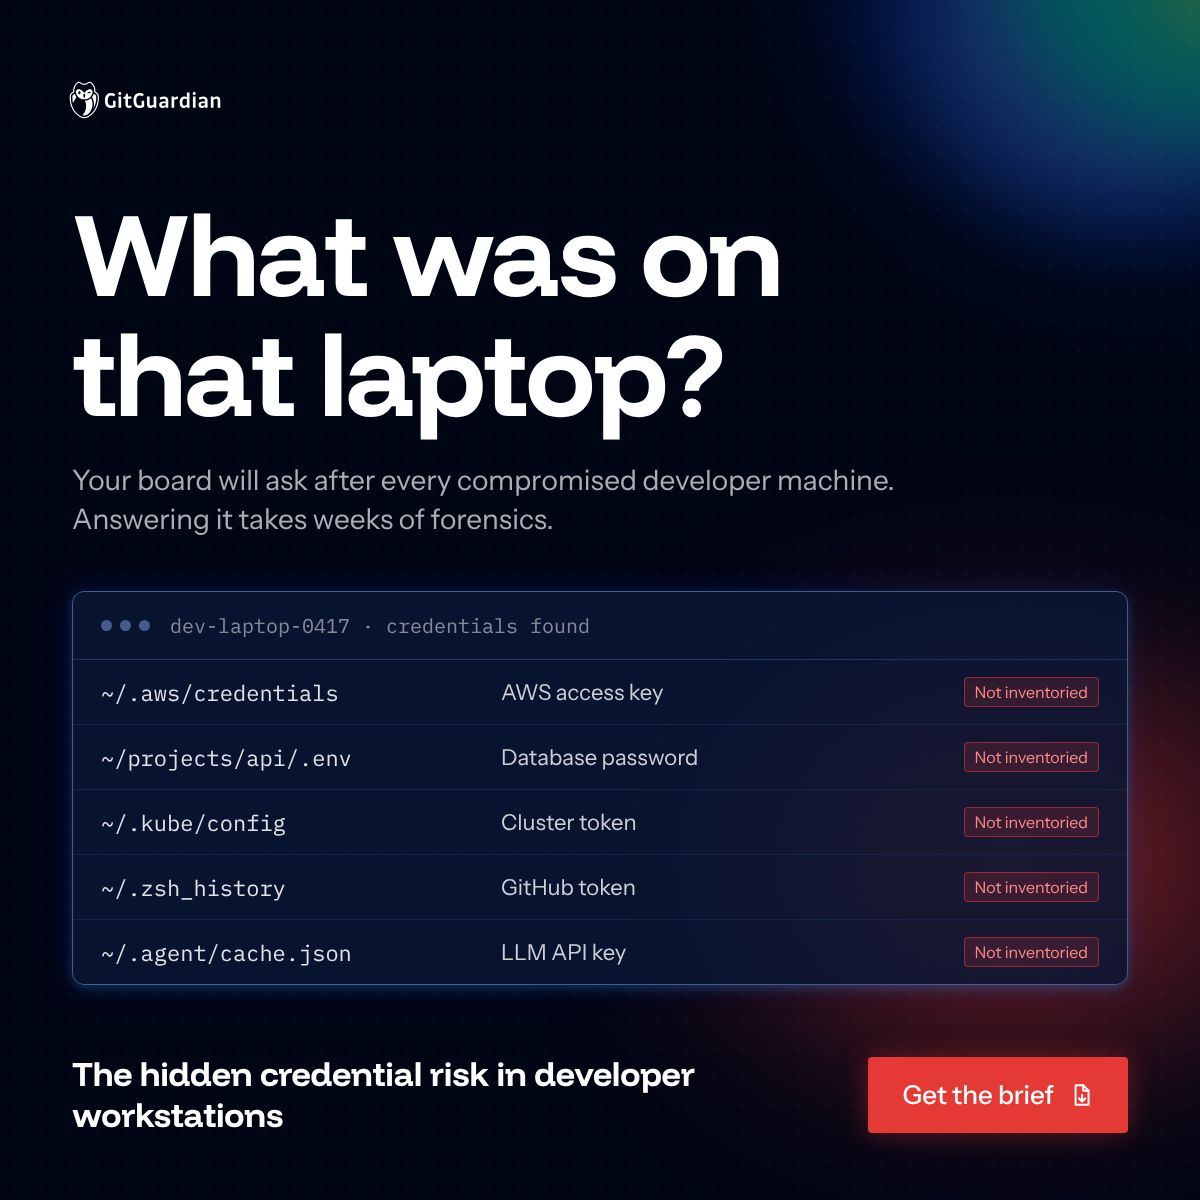
A developer laptop gets popped. The board asks one thing: which credentials were on it? Most security teams need weeks of forensics to answer.
- TeleportSince 22 Oct 2026
I recently built an AI SRE agent for a client but it almost got hacked. The agent could investigate incidents, access infrastructure, and take corrective actions. Basically, an SRE that never sleeps. It was doing exactly what we had given it permission to do. - It could access the logs. - It could execute commands. - It could restart services. - It could make changes. - The permissions were restricted. - The access was authenticated. But we still ran into a problem. A malicious prompt injection (an instruction hidden in something the agent was reading) could influence what it decided to do next. The agent wasn't compromised. Nobody stole its credentials. It was simply being influenced by something it was supposed to treat as data. That's when I realized one of the biggest challenges with AI agents isn't just what they're allowed to do, it's what they can be convinced to do. A prompt injection can manipulate an agent into using its legitimate permissions in ways you never intended. I started looking at: → Short-lived, just-in-time access → Strong agent identity → Ephemeral runtimes → Continuous enforcement → Complete auditability → Constraining agent autonomy I figured out Teleport can help me fix this. Instead of giving an agent permanent access to infrastructure, you can build around identity-based, short-lived access and strong session-level visibility. The bigger realization: Zero Trust tells us not to trust the agent by default. Agent Trust asks what happens after we've authenticated it and given it permission to act. That's a very different problem. There is a detailed white paper from Teleport called “From Zero Trust to Agent Trust” that goes deep into this. I learned quite a few things from it, especially around securing autonomous agents operating infrastructure. If you're building AI agents that can touch production, this is worth reading. https://fandf.co/4zU2Qfb Huge thanks to Teleport for making this wonderful resource available and also collaborating on this post.
- TeleportSince 22 Oct 2026
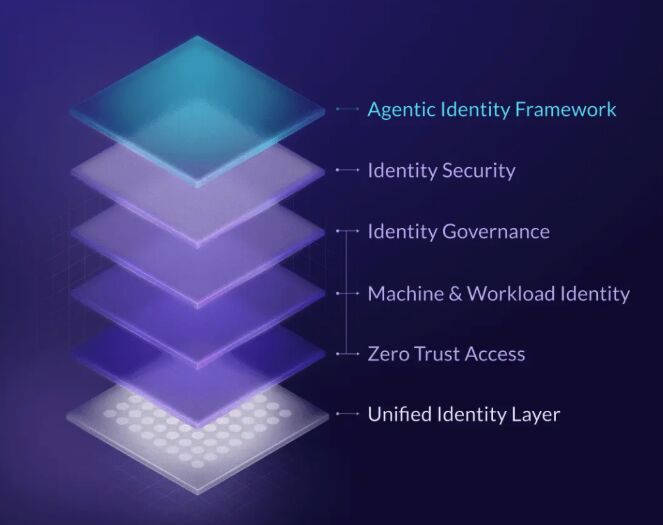
Most enterprises now have more machine and agent identities than people, and a large share have already had a breach tied to one. That is a part of the AI agent boom most organizations are still grappling with. We are deploying NHI’s at a scale no human team can track, and we’re handing them the exact thing we spent a decade trying to get rid of, which is long-lived static credentials and standing privileges. Now, an overprivileged agent can exfiltrate data at machine speed all without anyone ever phishing a human. OAuth grants, API tokens, and service accounts are the connective tissue of modern infrastructure, and agents depend on every one of them, and a quarterly access review does very little against something that acts in milliseconds. Agent identity must be treated with the same rigor as human identity, favoring short-lived credentials over static secrets and demanding full auditability of what every agent did and why. That is the shift Resilient Cyber partner Teleport frames as moving from Zero Trust to Agent Trust. Give it a read if you're putting agents into production -> https://fandf.co/4fSCD7E #Sponsored
- ExtraHopSince 23 Oct 2026
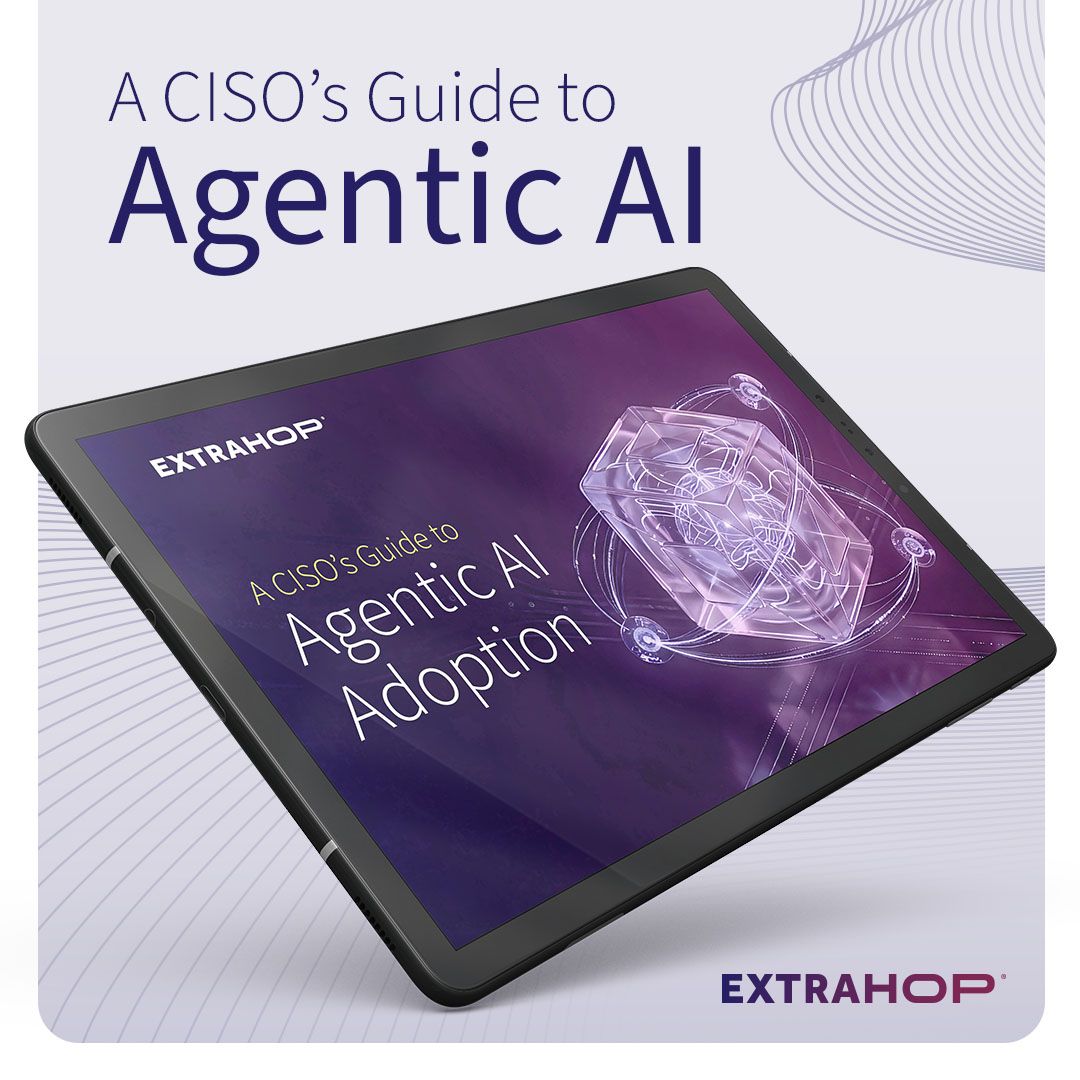
Agents are already triaging alerts, investigating incidents, correlating evidence, and taking bounded response actions. Meanwhile, security leaders are sorting through an ever-expanding market of models, agents, and platforms, each promising greater speed, accuracy, or efficiency than the next. Evaluating AI on a tool-by-tool basis introduces friction. Each standalone deployment forces lengthy procurement cycles and saddles teams with building, testing, and maintaining new data pipelines, integrations, interfaces, permission structures, and isolated controls. Security leaders need a way to absorb the next AI capability without burning cycles or going through a rebuild, keeping analysts on task, moving fast, and applying human judgment where it matters. With Context, Harness, and Model built as independent layers, a stronger model plugs into the existing system. Read A CISO’s Guide to Agentic AI Adoption: https://xtra.li/4zJ3zyK
- H2H TechnologyRecorded 27 Oct 2026
Banks and credit unions: if AI agents are accessing accounts, how do you verify their actions reflect what your customers and members intended? Reports of unvetted agents operating inside bank accounts make that question urgent. H2H Technology is ready to engage. We can help your team assess agent risks, define permitted actions, and establish external guardrails that require approval or block actions before execution. With Tutela Agentic Security, we help turn AI policies into runtime controls—with an audit trail of the decisions made. Let’s discuss your institution’s exposure and practical next steps. Message me directly or visit https://h2htech.com. Read the reporting: U.S. News / Reuters: https://lnkd.in/gNUzSCba Axios: https://lnkd.in/dEPB--ww #AISecurity #AgenticAI #Banking #CreditUnions #AIGovernance #Tutela #H2HTechnology #tutelacloud #tutelabyh2h
- AbstractRecorded 27 Oct 2026
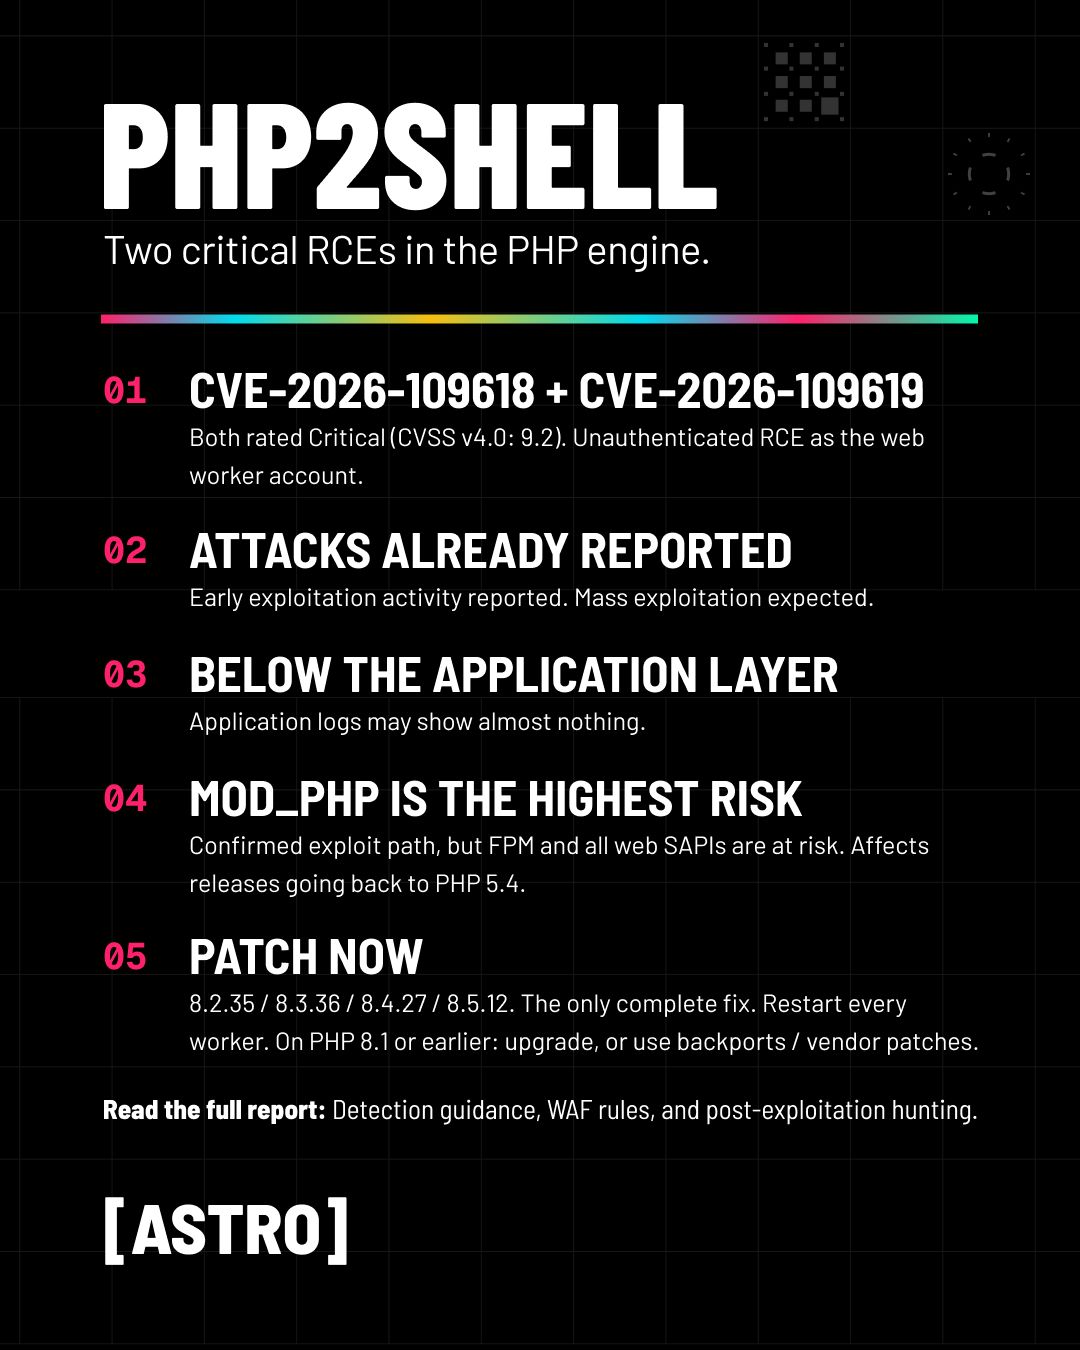
Yesterday, ASTRO published new research on PHP2Shell, covering two critical vulnerabilities in the PHP engine that could allow unauthenticated remote code execution. With attacks already being reported, the team breaks down what we know so far, which environments are most at risk, and what defenders should prioritize. The full report also includes detection guidance, WAF rules, and recommendations for hunting potential exploitation. Full report linked in comments 👇
- AbstractRecorded 27 Oct 2026
Your SIEM: "you still want these logs?" Also your SIEM: billing you for every one of them, even the ones nobody ever opens. That's not a relationship, it's a billing cycle. Abstract is free to try, right next to the SIEM you have. Learn more 👉 https://lnkd.in/gXpBMUmM
- RubrikSince 23 Oct 2026
If identity fails, organizations cannot fully recover business operations. Swipe to see why I&O leaders are prioritizing identity for cyber resilience.
- IONIXSince 23 Oct 2026
🚀 The State of the WAF 2026 report is here. Our research team tested live web applications across hundreds of organizations using five attack probes. The findings revealed a major security gap: Half of live web applications that should be protected by a WAF have no protection against attacks. See what else we uncovered in the full report.
- GEM Technology International Corp.Recorded 27 Oct 2026
Now Hiring: Personnel. Security Adjudicator
- IONIXSince 23 Oct 2026
47.3% of live web applications have no firewall blocking attacks, even when hosted on platforms with WAF capabilities. IONIX researchers tested live web applications across hundreds of organizations, uncovering critical gaps in WAF coverage, configuration, and effectiveness. Explore the findings in the State of the WAF 2026 report. No form, just the data. 👇
- Palo Alto NetworksSince 24 Oct 2026
Over 22M PHP instances exposed. Manual patching leaves you vulnerable.
- Eye SecuritySince 23 Oct 2026
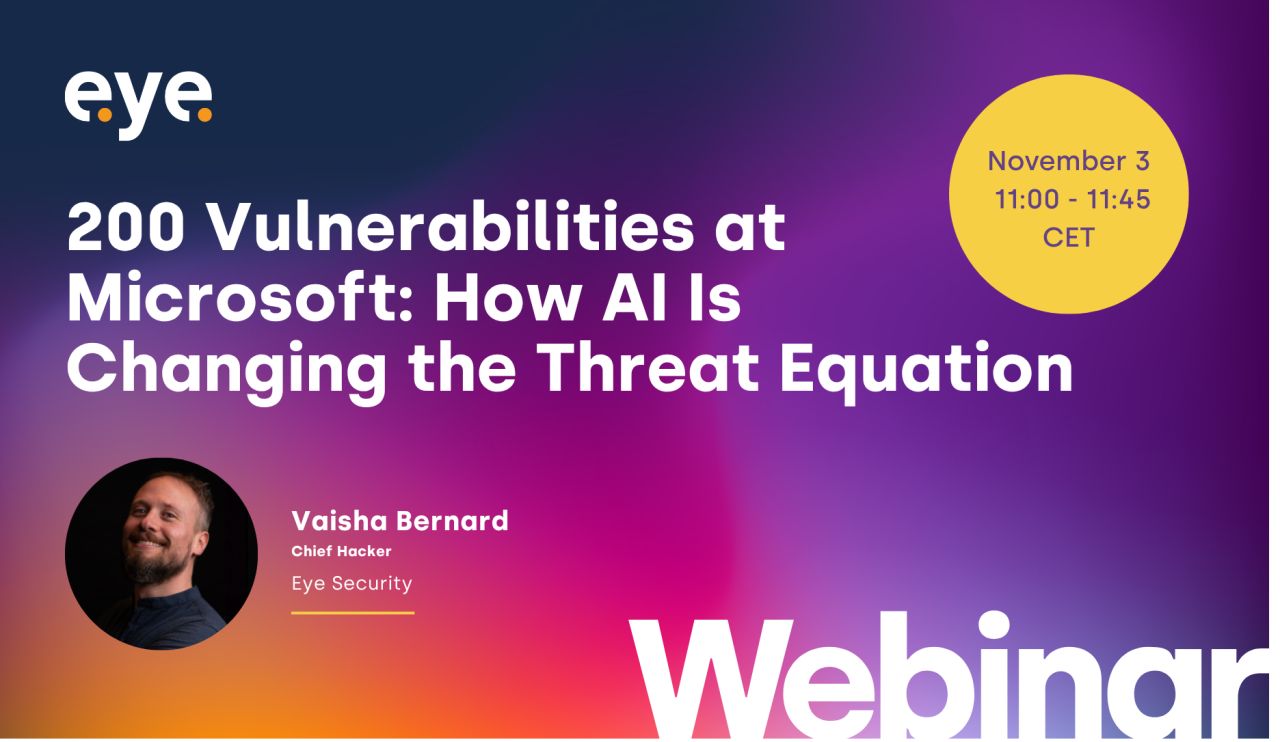
Your organisation can patch on time, and still be exposed. In one quarter, Eye Security found and responsibly reported 200 vulnerabilities at Microsoft. At the same time, newer AI models are changing what security researchers can find. The real challenge isn’t patching faster. It’s preparing for a shorter window between disclosure and exploitation. → How did one inconsistency lead to 200 vulnerabilities? → What are newer AI models changing in security research? → And how prepared is your organisation for a shorter time to exploit? On November 3, Eye Security’s Chief Hacker Vaisha Bernard breaks down the research behind these findings, how they were responsibly disclosed, and what they mean for your security strategy. November 3, 2026 | 11:00 CET
- GigamonSince 23 Oct 2026
Revisit yesterday’s assumptions with today’s evidence. Continuous validation wins. Read more.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.