B2B ad examples
1,810 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- Group 2000Since 24 Aug 2026
The EU e-Evidence Regulation is now applicable. That changes the conversation for service providers. The question is no longer only: “Are we aware of the new rules?” It is: “Can we execute the workflow correctly when an order arrives?” European Production Orders and European Preservation Orders require different operational controls. Production needs secure retrieval and delivery. Preservation needs targeted locking, expiry control and auditability. With Commission Implementing Regulation 2025/1550 linking the technical exchange layer to ETSI TS 104 144, e-Evidence is also becoming an interoperability challenge. For CSPs, day-one readiness means connecting legal intake to operational execution without losing control, timing or traceability.
- CoroSince 19 Sept 2026
Only 75% of available cybersecurity jobs can be staffed. Learn how RHTP can help rural providers build security beyond headcount.
- CoroSince 19 Sept 2026
73% of smaller hospitals report inadequate cybersecurity infrastructure. RHTP creates an opportunity to change that.
- Group 2000Since 11 Sept 2026
Electronic evidence requests are up 249%. According to the latest SIRIUS findings, EU authorities submitted 303,289 data requests in 2024 to a sample of major online service providers. Emergency requests are rising even faster. That matters because electronic evidence is no longer an occasional legal request. With the EU e-Evidence Regulation now applicable, service providers may need to handle urgent requests within tight deadlines while still validating, preserving, producing, delivering and auditing every step correctly. Manual workflows were not built for that pressure. As request volumes grow, the real question is whether service providers can keep control when speed, scale and legal sensitivity all come together.
- QueryRecorded 21 Sept 2026
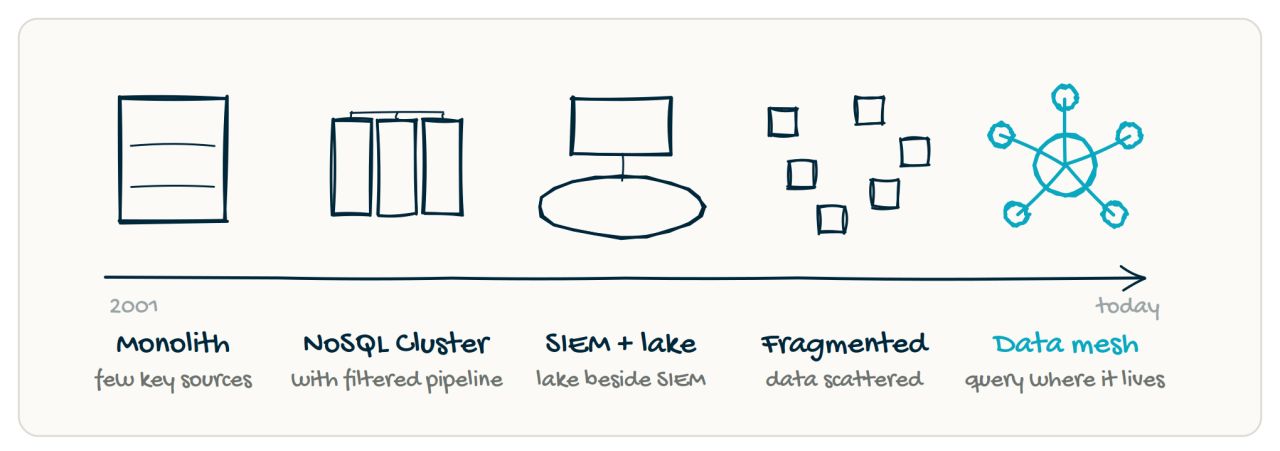
Last month I posted about my 25 years of building every SIEM architecture, and then seeing it lose to the same problem: the data outgrew the architecture. See that evolutionary journey in the diagram below. And then let’s talk about the new architecture I am proposing. It is something I have been building and refining over the last 5 years. The new architecture flips the problem. We start by accepting that distributed, heterogeneous data is the natural environment. Don't impulsively / habitually move big data to your SIEM vendor. Rather, we add a federation layer in our security stack to make the data discoverable and addressable. The federation layer creates the metadata that describes each source, its location, its data, its schema, and the APIs to reach it. It connects and joins the relevant pieces from across the environment and returns results in one unified data model. Storage, indexing, retention, and scaling get decided per source, based on what each kind of data actually needs, instead of one bill for everything. At that point the SIEM isn't a repository anymore. It becomes what it was truly meant to be – a security analytics brain running on top of the environment that already holds the data. At Query, we call this architecture a Security Data Mesh. The best part: your legacy SIEM folds into it. So does your security data lake project and so does your EDR. All without needing a major data migration. You investigate everything in place, you cut the cost of moving and duplicating data, and your AI finally performs on your whole environment instead of the fraction you could afford to centralize. Let’s stop fighting to centralize and own the data. Instead, let’s make it work for us from within its natural environment. Let me know if you agree/disagree. This has already been quite an evolutionary journey and I would love to learn from your experiences. #SIEM #cybersecurity #data #secdataops #AgenticSOC
- ConveyorSince 18 Sept 2026
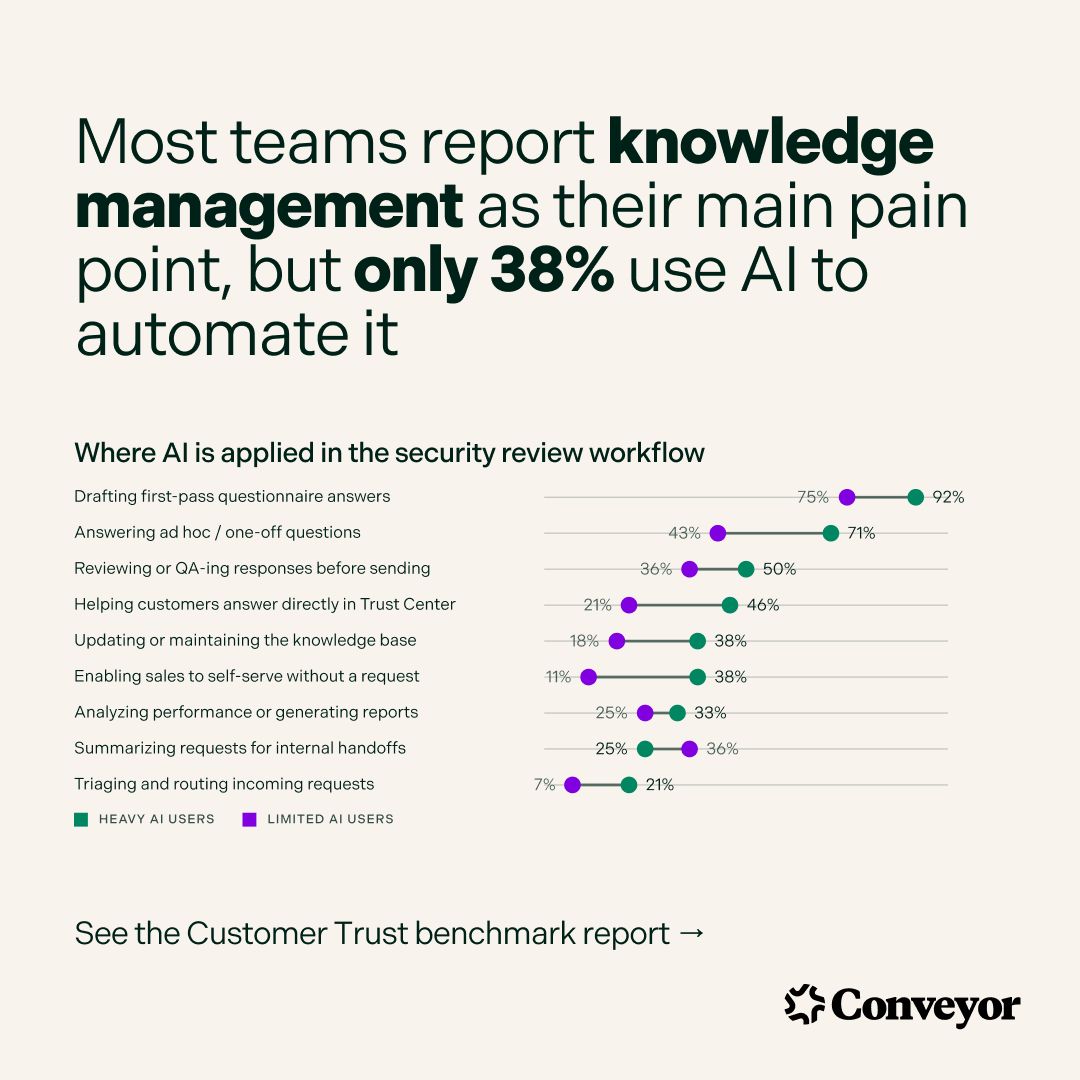
We surveyed 50+ B2B teams and learned that nearly 90% are using AI, but only 38% are using it to automate their biggest challenge. Read our 2026 Customer Trust Benchmark Report to learn more. 👇
- ConveyorSince 18 Sept 2026
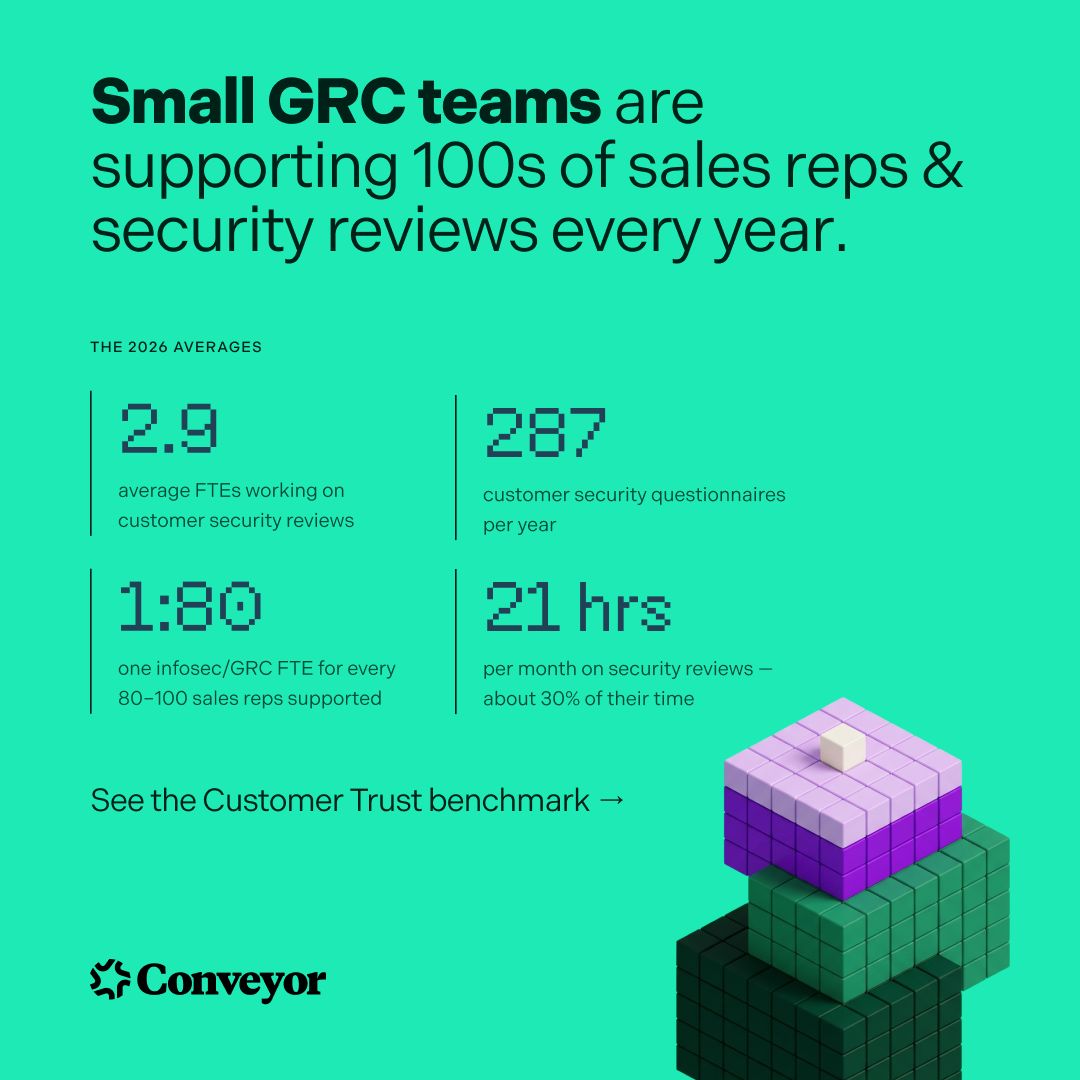
Small teams are juggling 287 security questionnaires a year, with just 1 InfoSec/GRC person for every 80 sales reps. How are they actually keeping up with that kind of volume? We surveyed 50+ B2B teams on what they're dealing with when it comes to questionnaire volume, headcount, sales support, AI adoption, operational challenges, and more. Read our 2026 Customer Trust Benchmark Report to learn more. 👇
- GreyNoise IntelligenceSince 11 Sept 2026
Artificial intelligence is insanely powerful and super duper good at lots of stuff that we mere human mortals are so meek at. But AI is, in fact, not human. And, as a result, AI's current capacity for good opsec and good tradecraft is limited. A model cannot go to jail, nor can it understand and appreciate the pain and helplessness of having its agency or livelihood clobbered, or being removed from its family, or having its assets frozen. Finding bugs and writing exploits is one skillset, but operating on other folks' computers and networks is a very different one. Anyways, we at GreyNoise Intelligence found a particularly forward-leaning actor compromising organizations (using the codex harness with the DeepSeek models) that were running vulnerable PaperCut Software. We yoinked the attacker's target list, their tools, their progress spreadsheets where they notated how many of the orgs they'd gotten domain admin on, and even their rank-ordered exclusion list of countries not to target. Couldn't tell you why, but their first three target geographies to exclude were Russia, China, and Hong Kong. At GreyNoise, we have no incident response business. We've also historically not been in the business of unprompted victim notification or ambulance chasing. That said, having come across the entirety of this campaign as it was happening, with some pretty meaty targets, we're in the process of working through victim notification now. https://lnkd.in/e29aaZCH
- Artemis SecurityRecorded 21 Sept 2026
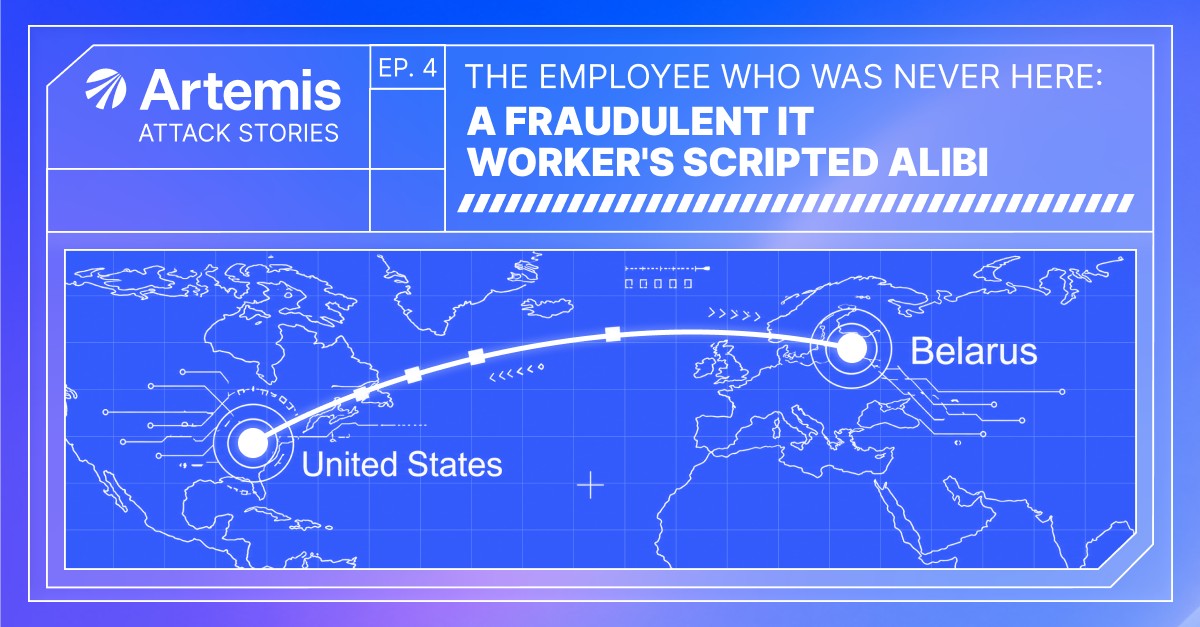
Attack Story #4: The Employee Who Was Never Here: A Fraudulent IT Worker’s Scripted Alibi A new remote IT hire's account signed into the corporate VPN hour after hour at exactly 26 seconds past the minute, while the operators actually working it sat in Belarus and Russia. His credentials were valid, his MFA factors checked out, and his exit IP looked residential, so every control waved him through. The identity provider saw a legitimate new employee and the reputation feeds saw a benign address, but neither saw the scripted alibi keeping a fake American at his desk for 18 days. Artemis read the facts together, joining two concurrent sessions 17 minutes apart across an ocean, cron-perfect login timing, and MFA factors that split cleanly by country, and confirmed in minutes what the manager had felt for weeks, deactivating an account that was never his to begin with. Full story in the first comment 👇
- CorkRecorded 21 Sept 2026
From CIS to NIST, Cork's risk insights platform makes adherence simple. Less grind, more protection.
- Graylog, Inc.Since 28 Aug 2025
For the second year in a row, GigaOm recognizes Graylog as a Leader and Outperformer in the 2025 SIEM Radar Report. Graylog delivers a full-featured SIEM with built-in anomaly detection, risk scoring, native telemetry pipeline management, and prepackaged content for smarter threat detection. It is built for fast, accurate alerting and investigation, making Graylog a great choice for organizations seeking a scalable and adaptable SIEM solution.
- Graylog, Inc.Recorded 21 Sept 2026
Too often, organizations are forced to make a choice: Reduce log volume to manage cost or keep everything for those "just in case moments" and suffer high ingestion-based pricing.
- GlobalSign APACRecorded 21 Sept 2026
Low email open rates? What’s missing? Visual trust! Make your emails instantly recognizable and trusted. VMCs provide email authentication, enhanced brand recognition and improved deliverability. Your customers will know they can trust your emails 100%! Get VMCs now! https://lnkd.in/gAikKSSr
- GlobalSign APACRecorded 21 Sept 2026
With spoofing attacks on the rise, BIMI VMC can lower phishing risk. Let your customers will see your trademarked logo in your email, gaining instant visual trust. Get VMCs and show your customers they can trust your emails. Limited-time offer: 25% off on GlobalSign VMCs! 👉https://lnkd.in/gAikKSSr
- GoldphishSince 15 Oct 2025
It’s 2025, and while security technology has never been stronger, attackers have never been smarter. 💭So here’s the real question: Can technology alone protect your business if your employees are unaware and not cyber-savvy? Join us for a live debate where we’ll unpack: ⚡ What social engineering looks like in 2025 🛡️ How even the best security stacks still get breached 📣 Why a reporting culture is your best defence 💪 How our latest solution, Goldphish Managed, addresses your pain points #Goldphish #CyberSecurity #CyberSecurityAwareness #GoldphishManaged Dan Thornton Estéffan C. https://lnkd.in/dZwBTbBH
- CorkRecorded 21 Sept 2026
When ransomware hits, prevention isn’t enough. Join our webinar on October 29th as experts reveal the financial reality behind client losses, MSP partners share real payout stories, and learn how Financial Protection as a Service can protect your clients.
- Gray AnalyticsRecorded 21 Sept 2026
Starting November 10, 2025, CMMC assessment and certification requirements will begin appearing in DoD contracts. If you're part of the Defense Industrial Base, now is the time to act. Get Scheduled: Assessment capacity is limited, and demand will spike as contracts roll out. Secure your spot early to avoid delays that could impact your eligibility. We have capacity for CMMC assessments and are ready to help you meet compliance requirements. Don't risk missing out on future contracts--reach out today to lock in your assessment date.
- Conviso Application SecurityRecorded 21 Sept 2026
Plano 12+2: firewall, rede de aceleração, SSL EV e scans contínuos. Segurança que gera confiança e mais conversões.
- Conviso Application SecurityRecorded 21 Sept 2026
Firewall, rede de aceleração, SSL EV e scans contínuos. Garanta duas Black Fridays seguras e mais conversões.
- Gray AnalyticsRecorded 21 Sept 2026
“By the time we reached our assessment phase, we knew exactly what to expect and felt fully supported.” Gray Analytics digs deeper than surface-level scans. The result? A clear picture of what’s at risk—and what to fix first. Reveal what others overlook. Book your assessment today.
- CorpiaRecorded 21 Sept 2026
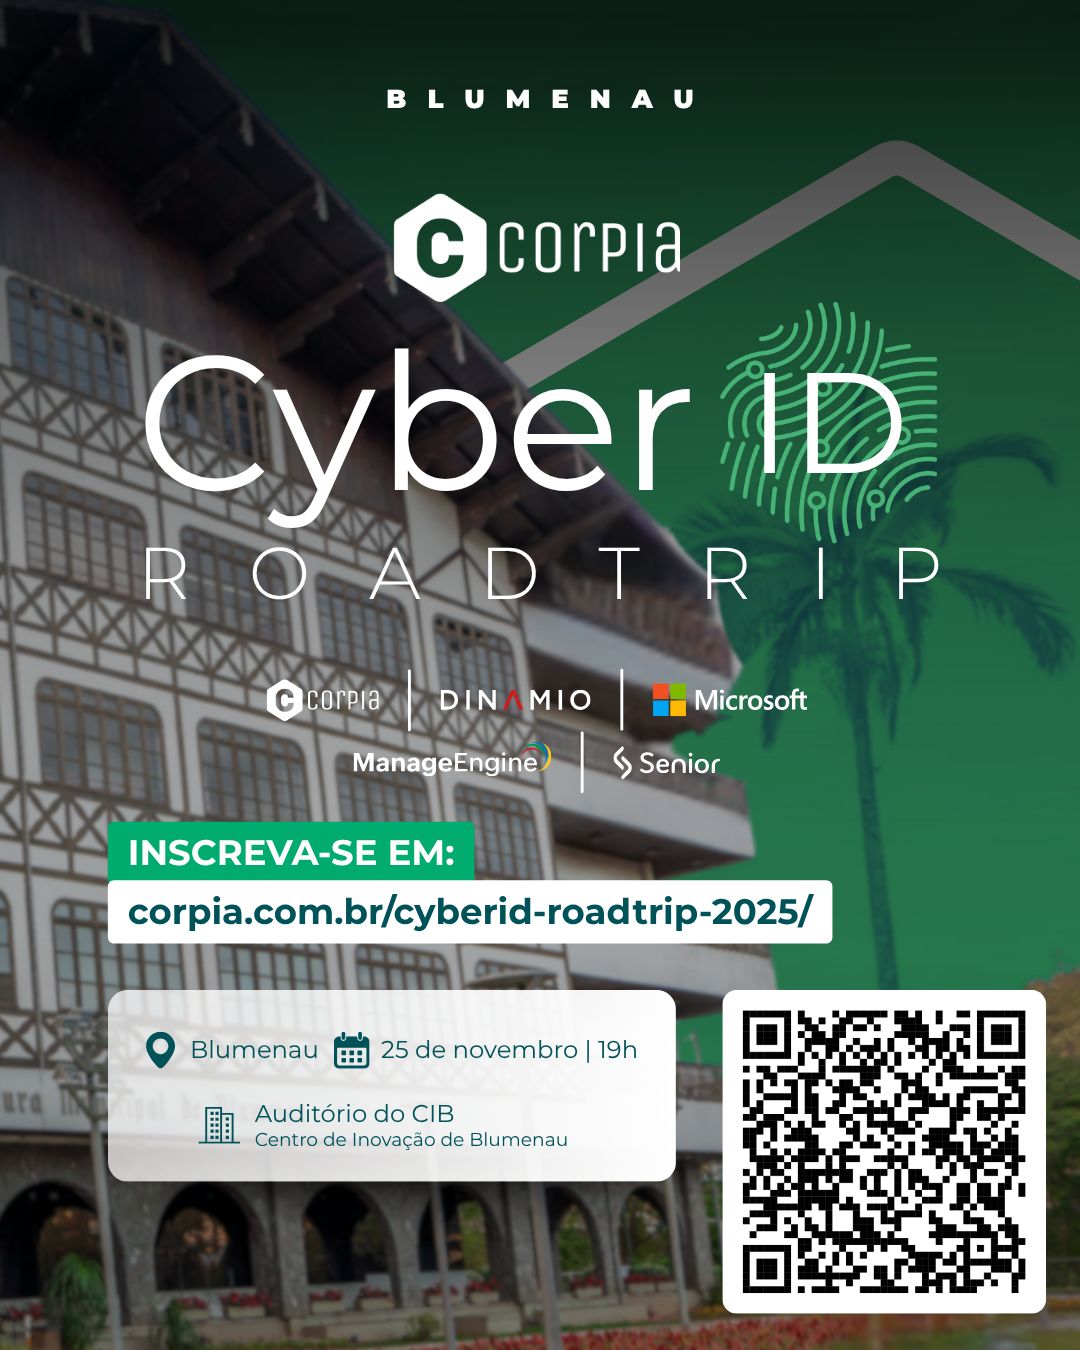
O futuro da Governança de Acessos está na estrada. A Corpia, junto de Microsoft e ManageEngine, dá início ao CyberID RoadTrip — o roadshow nacional sobre Identidade, Acessos e Governança. A terceira parada acontece em Blumenau, reunindo líderes de TI, Segurança e Compliance para discutir como unir segurança, eficiência e conformidade em um só ecossistema de acessos. Inscreva-se.
- CorpiaRecorded 21 Sept 2026
A Governança de Acessos é a base da segurança moderna. Entenda como aplicá-la no CyberID RoadTrip Blumenau.
- CorbadoRecorded 21 Sept 2026
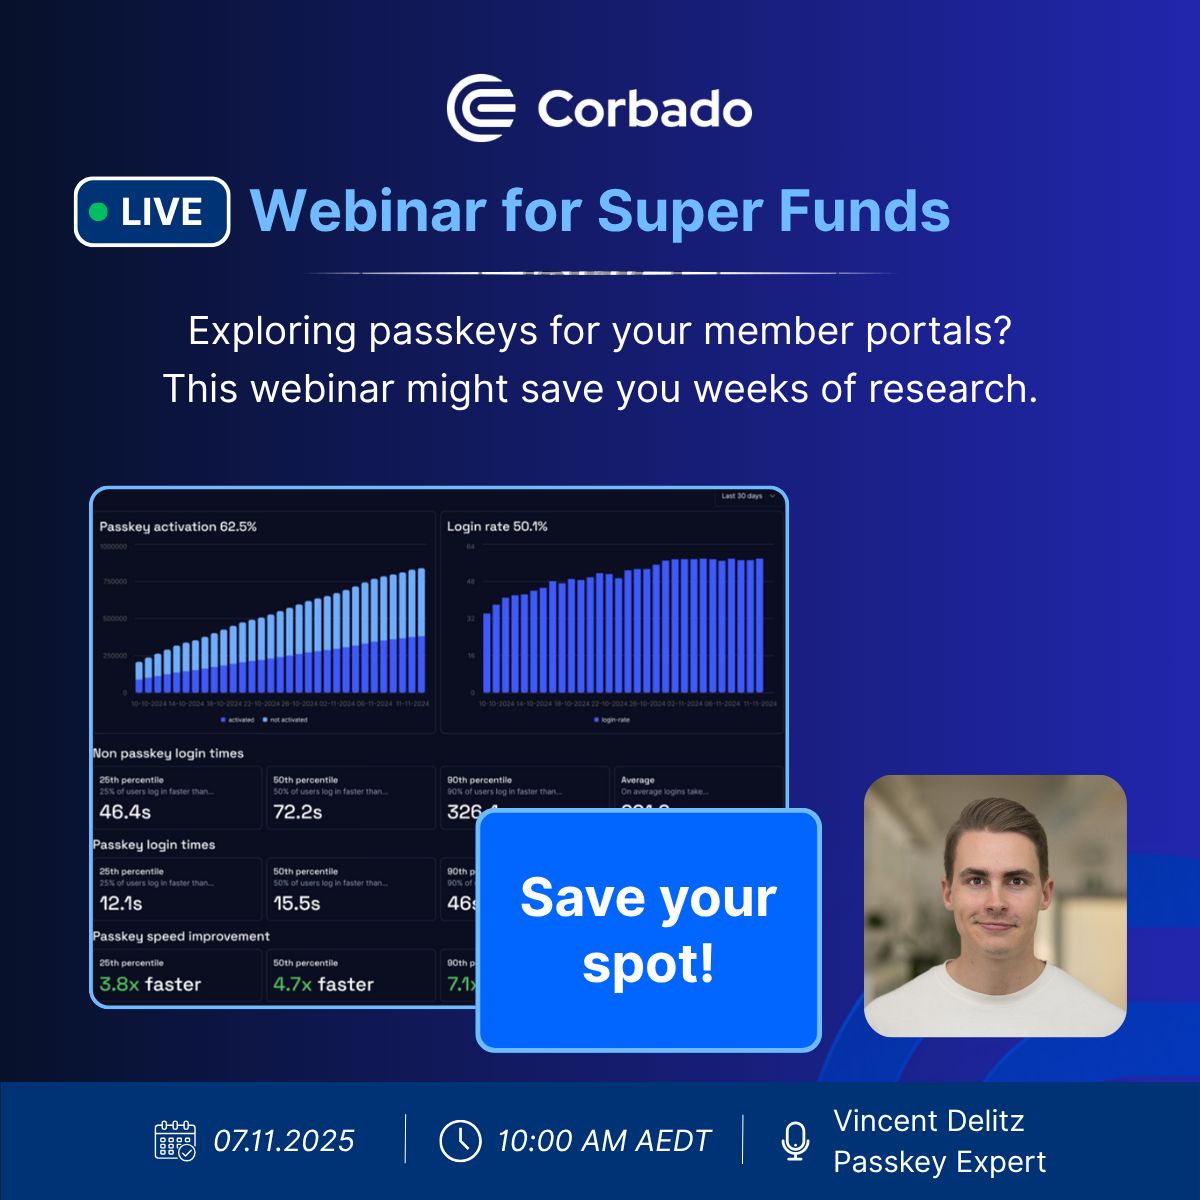
Never let a member lose their pension funds again! April’s attacks showed how quickly cyber attacks can drain accounts. Passkeys remove shared secrets and shut down phishing and credential-stuffing. ✅ Key benefits: -100% phishing-resistant MFA for members -Prevent account takeovers across member portals -Protect sensitive member data Join our upcoming webinar for executives at Australian super funds to learn how passkeys can protect millions of members, featuring lessons from AU deployments (UniSuper, VicRoads, myGov, Telstra, UBank). 🗓️ Friday, November 7, 2025 — 10:00 AM AEDT (Sydney/Melbourne) 🚀 Register: https://lnkd.in/dVgXGHFr
- CorbadoRecorded 21 Sept 2026
Stop OTP rage-quits. Passwords + OTPs frustrate members. Passkeys give members instant, effortless access to the member portal. ✅ Key benefits: - 1-tap Face ID logins: 4–6× faster member portal logins - 20–40% fewer call-centre password resets/locked-out calls - 50–70% cost reduction (SMS + recovery) Join our upcoming webinar for member services teams to learn how Australian super funds can deliver 1-tap logins, reduce lockouts and reduce authentication costs by 70%, featuring lessons from large AU deployments (UniSuper, VicRoads, myGov, Telstra, UBank). 🗓️ Friday, November 7, 2025 — 10:00 AM AEDT (Sydney/Melbourne) 🚀 Register: https://lnkd.in/dVgXGHFr
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.