B2B ad examples
1,812 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- GuidePoint SecurityRecorded 22 Sept 2026
The perimeter has dissolved. Your workforce is distributed. And identity has become the cornerstone of effective security. Learn why "Modern Security Initiatives" are replacing traditional zero trust and how the concept of privilege is evolving beyond admin accounts. Featuring insights from leaders who've helped organizations transform their approach to identity.
- HicomplyRecorded 22 Sept 2026
Regulators are paying attention to how you govern AI. Customers are asking questions. And your next audit won't wait. This checklist walks you through ISO 42001 step by step - so you're not scrambling when certification day arrives. Grab it now. Before someone else asks where your AI governance framework is.
- HITRUSTRecorded 22 Sept 2026
Traditional TPRM generates activity, not protection. 99.41% of HITRUST-certified environments reported no breaches. It’s time to implement the validated assurance that delivers the credible, defensible proof your board demands.
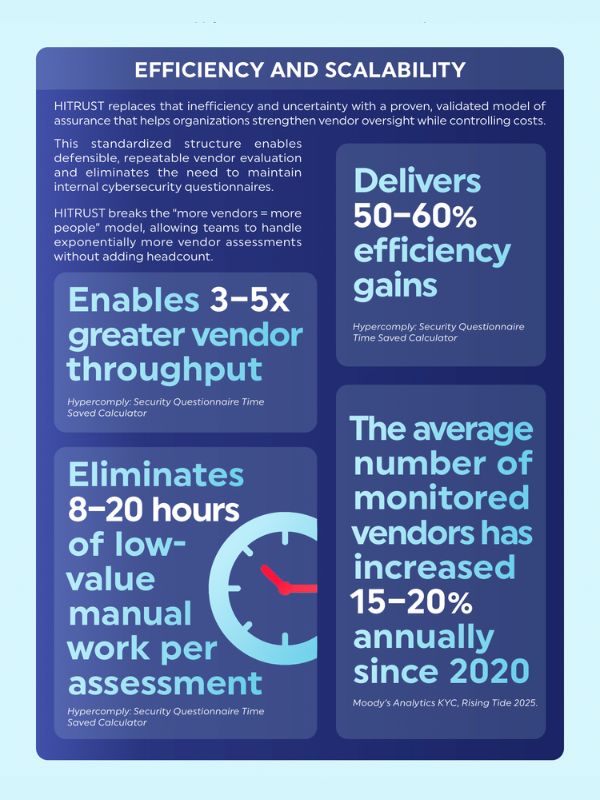
- HITRUSTRecorded 22 Sept 2026
Cut costs. Reduce friction. Strengthen assurance. HITRUST transforms third-party risk management from a fragmented, reactive function into a scalable, efficient, and defensible assurance program. For more TPRM insights, get the infographic: https://lnkd.in/gsdCg7kZ #VendorRiskManagement #TPRM #ThirdPartyRisk
- CorelliumSince 12 Feb 2026
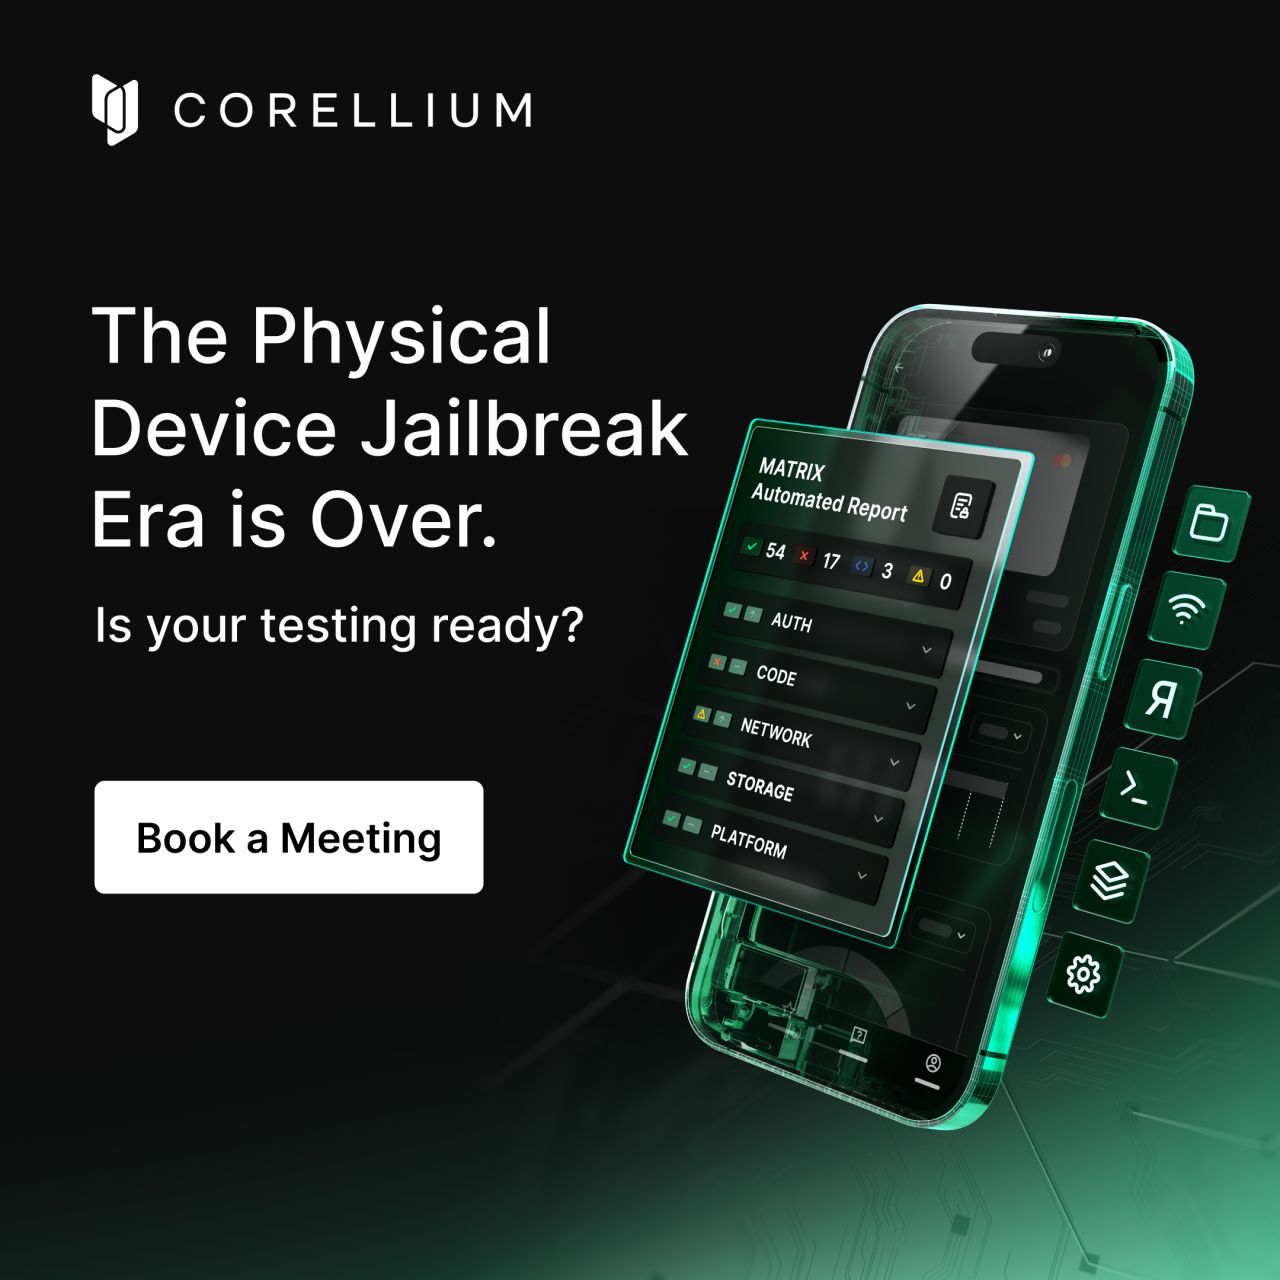
Still relying on jailbroken devices to test your mobile banking apps? With iOS 26 eliminating physical jailbreaks, many financial institutions have lost access to the visibility they need to identify fraud risks, insecure data handling, and runtime vulnerabilities. That creates blind spots regulators won’t ignore. Corellium replaces fragile device labs with virtual iOS devices that deliver root-level access, full OS version coverage, and deep runtime insight—without violating security or compliance requirements. See how leading financial institutions are modernizing mobile app testing. Book a walkthrough today.
- CorelliumSince 12 Feb 2026
Struggling to produce audit-ready evidence for your mobile banking or payments apps? With physical jailbreaks gone in iOS 26, many financial teams have lost root access—making it harder to validate controls, document secure data handling, and demonstrate compliance across OS versions. Corellium provides full runtime visibility, version-accurate iOS testing, and the artifacts financial institutions need to support SOC 2, PCI DSS, SOX, and regulatory exams. Remove compliance guesswork. Schedule time with our team to see how Corellium helps financial organizations close visibility gaps and reduce audit friction.
- GMS Information SecurityRecorded 21 Sept 2026
Phishing hiperrealista y ransomware con IA lideran los ataques en 2025. Al utilizar playbooks inteligentes y fuentes de inteligencia integradas, GMS SOC Lite gestiona alertas complejas en tiempo real y protege tus activos críticos.
- GMS Information SecurityRecorded 21 Sept 2026
Los ataques se han vuelto más rápidos y complejos: el 70% son multivectoriales. Impulsado por su motor de orquestación y automatización avanzada, nuestro GMS SOC Lite responde antes de que ocurra el daño y asegura continuidad de negocio.
- GlasswallSince 15 Jul 2026
You can't detect what you don't know exists. Glasswall rebuilds every file to a known-good standard, so zero-day threats are neutralized by default.
- GlasswallSince 15 Jul 2026
Detection-based security has a structural problem: it only works against threats it already knows about. Signature matching, behavioral analysis, sandboxing — each of those approaches starts from the same assumption. Show the tool a file, wait for it to recognize something suspicious, then act. That model worked when the threat landscape was slow-moving and well-documented. It's far less effective against zero-day exploits, where there's no prior signature to match and no behavioral history to flag. In the time between a malicious file arriving and a threat being identified, your environment is exposed. How long that window stays open depends on your detection tools, your team's response speed and whether the threat is sophisticated enough to avoid triggering any alerts at all. For some organizations, the answer to "how long were we exposed before we knew?" is measured in weeks. Content Disarm and Reconstruction (CDR) changes the question. Instead of scanning for known threats, Glasswall rebuilds every file to a known-good standard — inspect, repair, clean, deliver. Malicious active content isn't flagged and quarantined. It's removed, regardless of whether it matches a known signature. Zero-day threats are neutralized by default because CDR removes the conditions that allow threats to execute, not just the threats themselves. That's not a theoretical claim. Glasswall has tested it against 8.27 million malicious files under objective conditions. 100% were neutralized. Not a high success rate. Not "effective against the most common threat vectors." 100%. If your current security model depends on knowing what a threat looks like before stopping it, see what a prevention-first approach actually produces.
- PathlockSince 26 Jun 2026
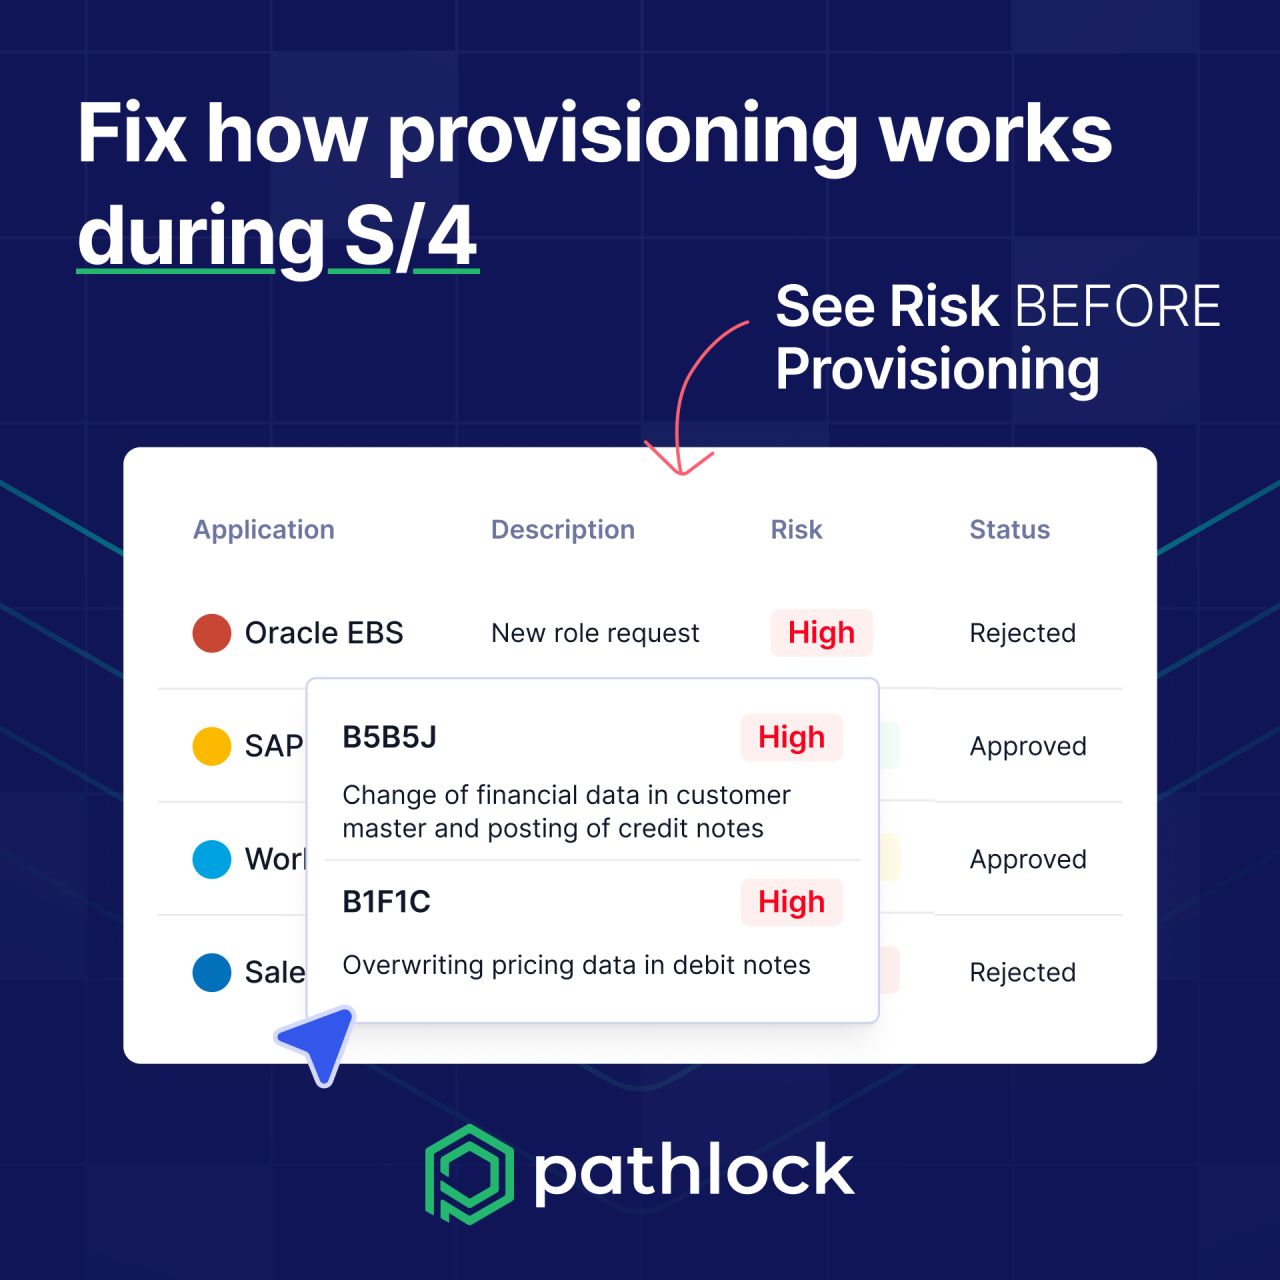
An S/4 migration almost always inherits years of accumulated access — it's rarely a clean slate. That makes it the moment to fix how provisioning works, not repeat it. If access is still granted by manual approval and cleaned up afterward, the new system carries the old habits forward. Compliant provisioning runs a preventive SoD check at the point of request, so access is right before it's granted instead of remediated at the first audit.
- PathlockSince 27 Jun 2026
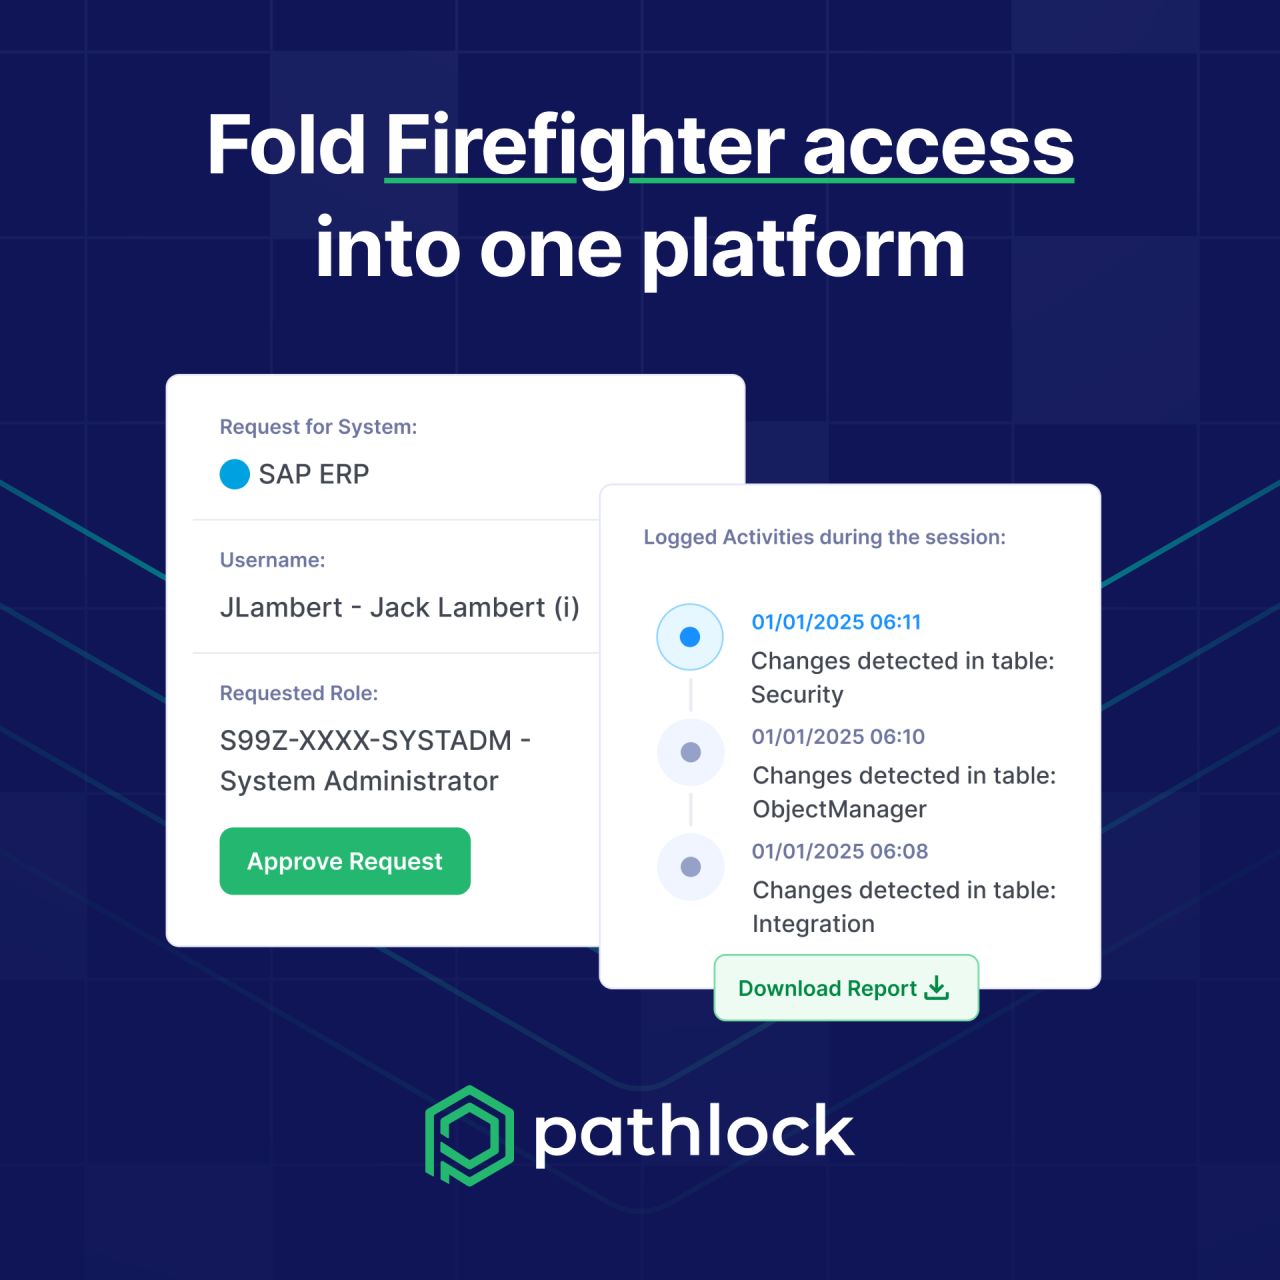
Emergency (Firefighter) access has always been its own tool, separate from SAP IDM. A move off IDM is a chance to reduce the number of separate tools, not add to them — bringing elevated access management onto the same platform as identity and access governance. Time-boxed, monitored, with the audit trail written automatically, so privileged access is governed in the same place as everything else.
- Core ImpactSince 13 Jun 2026
Upskill team capabilities by building on existing expertise. Give your pen testers the tools and training to go further. https://lnkd.in/eUd4DDwd
- Group 2000Since 16 Jul 2026
You do not grow by solving the same problem over and over again. At Group 2000, you work on complex technical challenges alongside experienced software engineers and architects. You get the room to deepen your expertise, contribute your own ideas and gradually take ownership of increasingly important components. Discover a place where you can genuinely grow as an engineer.
- Group 2000Since 16 Jul 2026
Innovation does not have to mean uncertainty. Since 1978, Group 2000 has developed specialist technology for customers around the world. Today, we combine that stability with complex technical challenges, international projects and plenty of room for individual responsibility. Build your future with a company that is here for the long term.
- CorbadoSince 27 Aug 2026
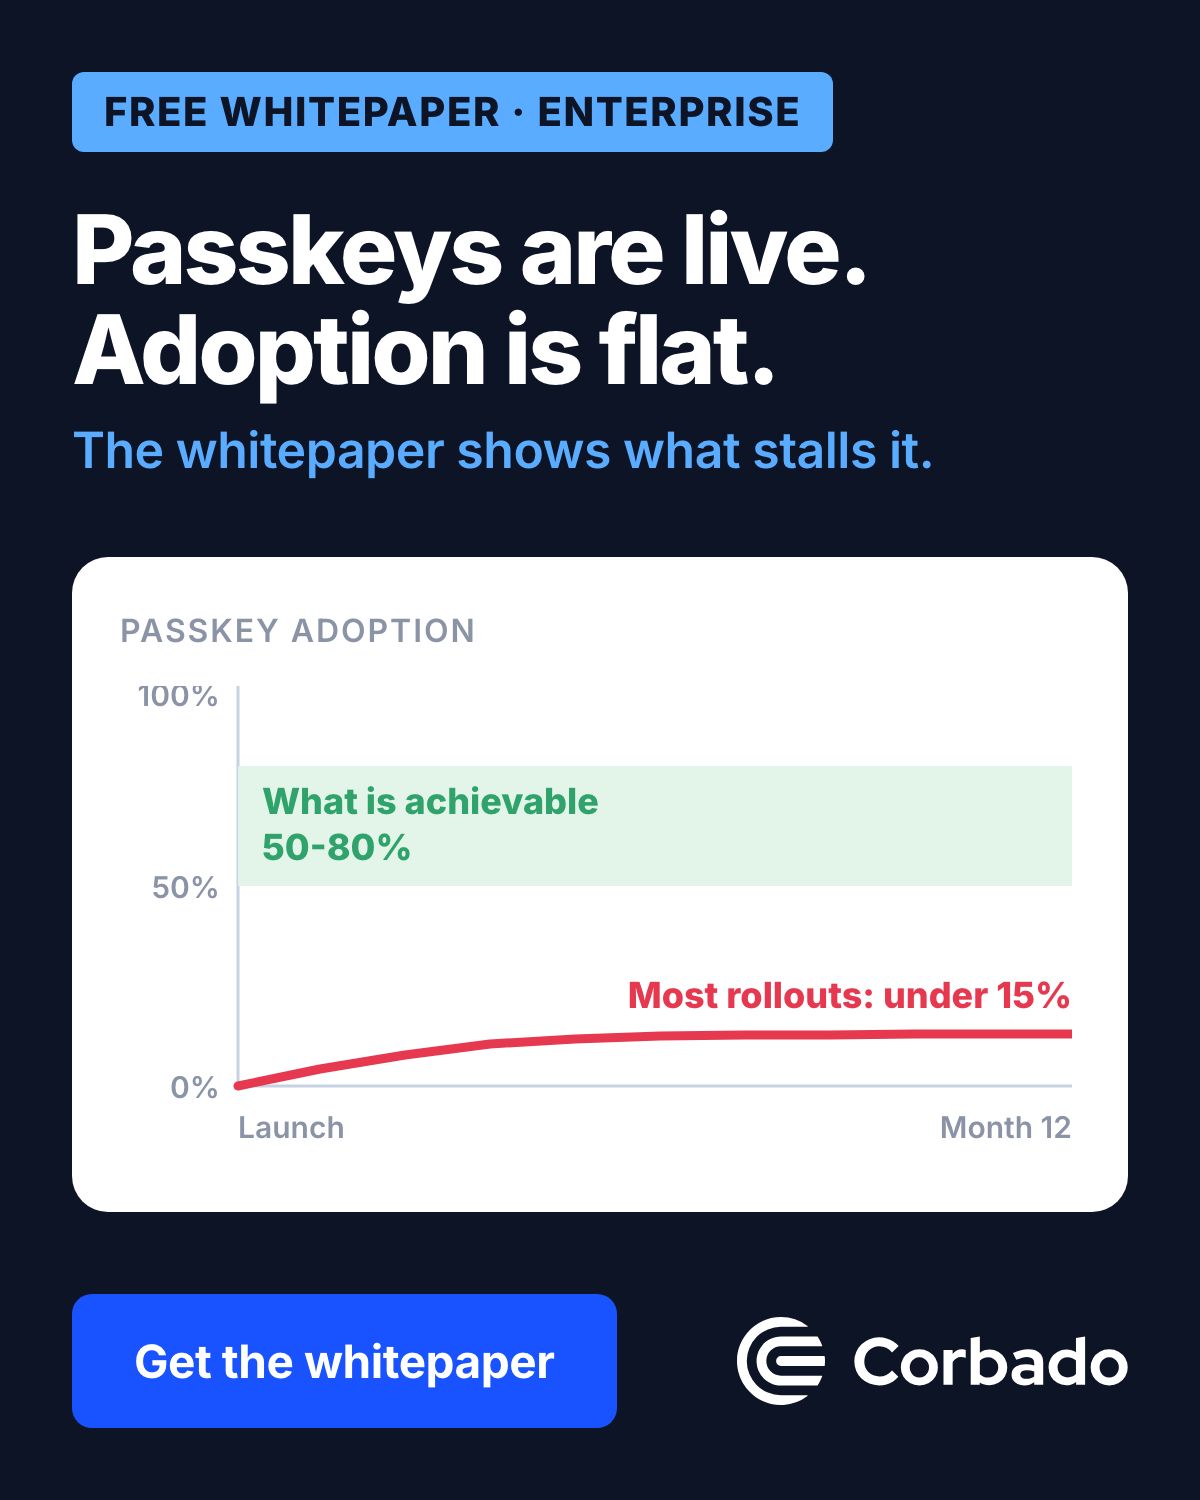
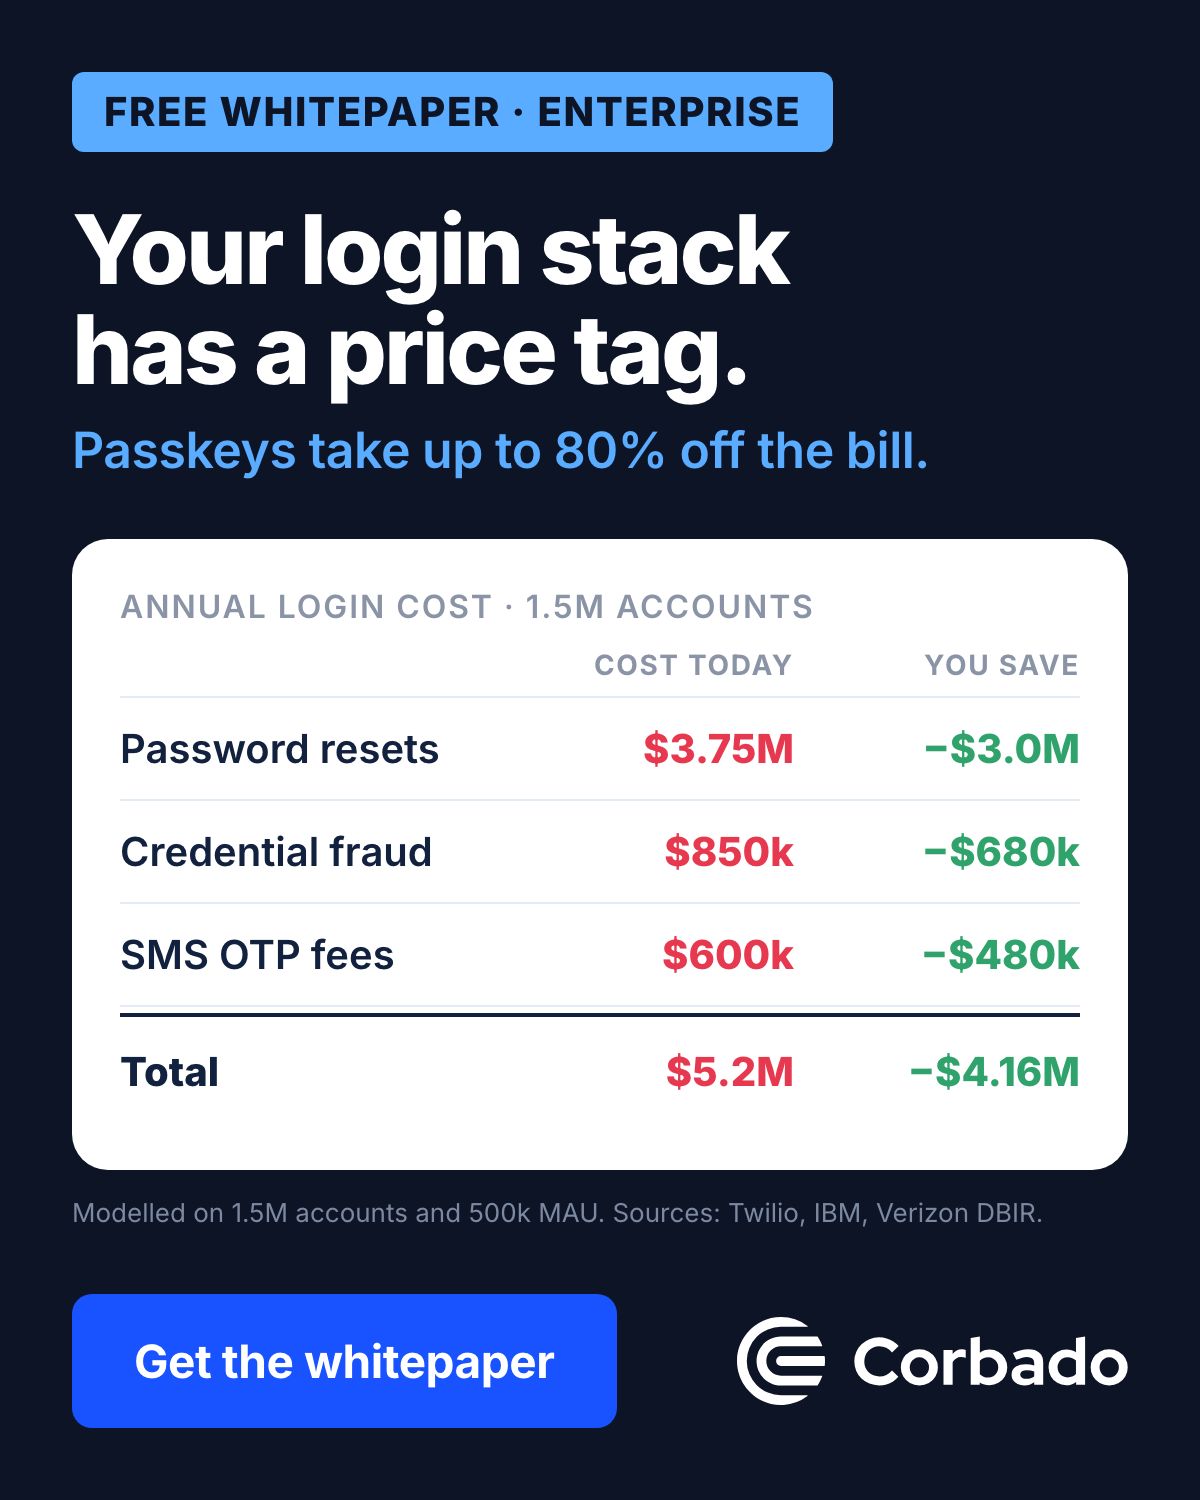
Passkeys are usually live long before anyone actually uses them. The whitepaper covers what stalls adoption and how the rollouts that worked got past it.
- CorbadoSince 27 Aug 2026
Most teams treat authentication as a cost line they cannot avoid. Passkeys can flip that. The whitepaper has the full ROI model behind these numbers and the rollout plan that goes with it.
- Group-IBSince 8 Sept 2026
⚡ A reorganization triggers internal power struggles nobody wants. A new platform purchase demands an ROI business case nobody can yet prove. So institutions stay siloed, and adversaries win by default. You don’t need a new budget, extra headcount, or a massive software overhaul to fix this. You just need 90 days and the team you already have. Your staff can: 🔹 Unify language: Adopt MITRE F3 across both functions. 🔹 Audit the gap: Walk one live incident end-to-end to map where intelligence died. 🔹 Track what matters: Measure one shared metric—signal-to-action time. 📖 Read the full 90-day plan
- Group-IBSince 8 Sept 2026
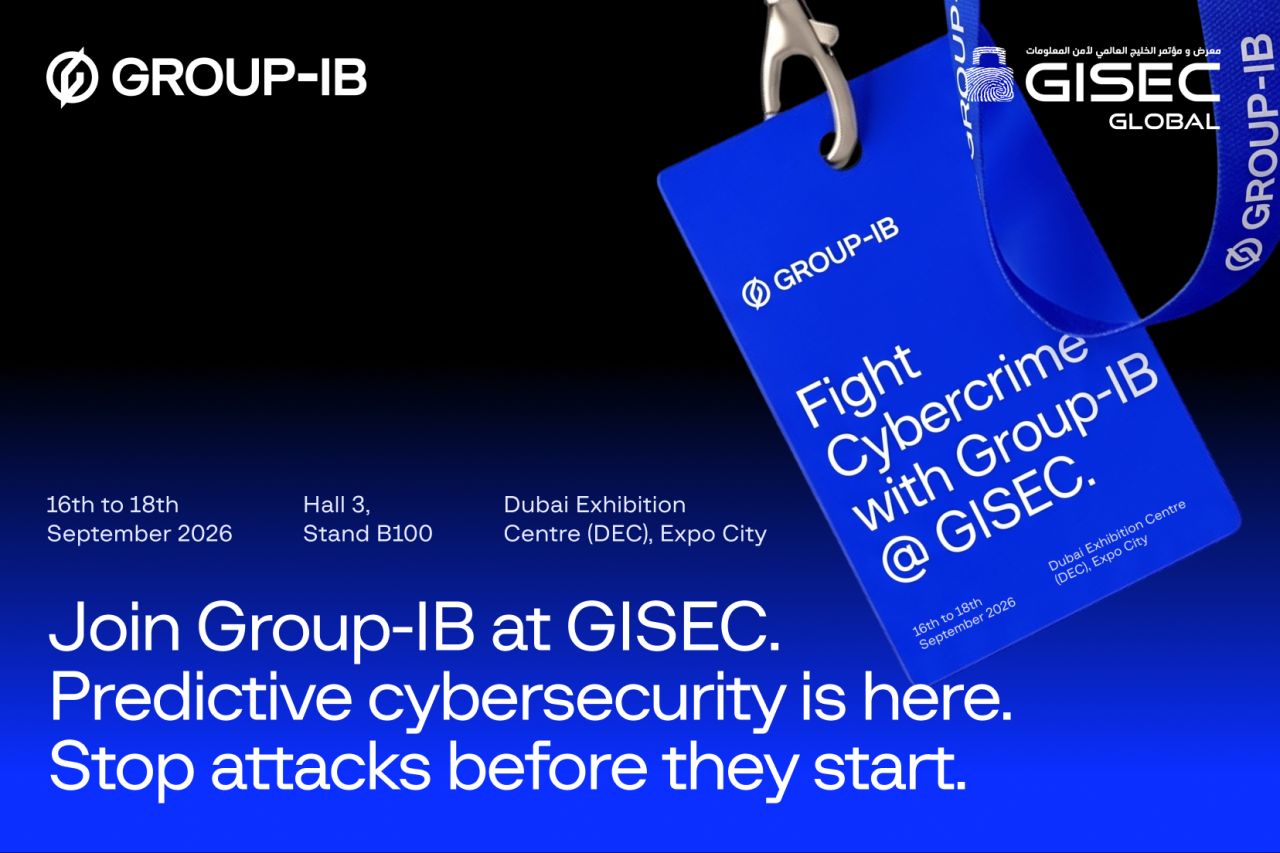
✨ If you make it to one cybersecurity event this year, make it this one. GISEC Global is where the region's security community gathers. And this year, Group-IB isn't there to make a bold claim about the future of cybersecurity. We're there to prove it. Prediction isn't a direction we're pointing at. It's already running. Book twenty minutes with our team at the stand, and we'll show you what that looks like: 🔹 Cyber and fraud signals, fused into one defence. 🔹 Every major release of our year, in the Innovation Hub. 🔹 A Threat Exposure Assessment that maps your blind spots, live. No pitch. A working session on what your defence could catch before the first alert with the team behind two decades of operations alongside INTERPOL, EUROPOL, and AFRIPOL. 📍 Dubai Exhibition Centre (DEC), Expo City, Hall 5, Stand B100 📅 16th – 18th September 2026. Book your slot: https://lnkd.in/eh9Ayr-y/?utm_campaign=NewCampaignGroup&utm_source=linkedin&utm_medium=paid&utm_id=626082903&hsa_acc=509945487&hsa_cam=626082903&hsa_grp=889361033&hsa_ad=1531642593&hsa_net=linkedin&hsa_ver=3 #Cybersecurity #GISECGlobal #ThreatDetection #FraudPrevention #CyberDefense #GISEC2026 #FightAgainstCybercrime
- Core6Since 9 Sept 2026
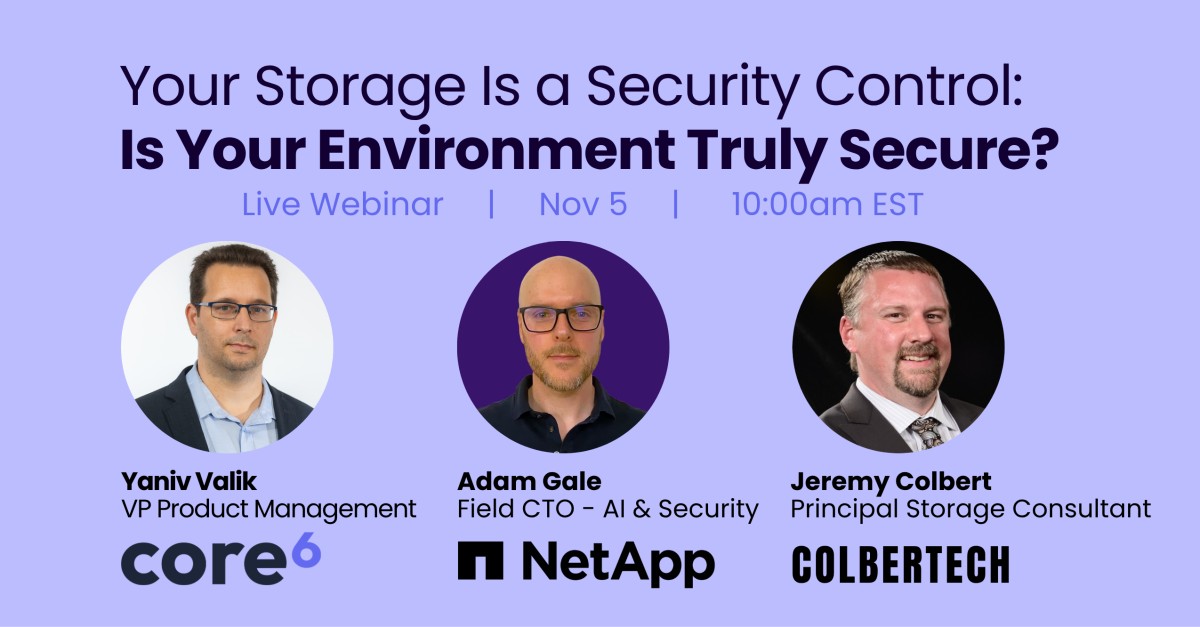
On November 5, join NetApp and Core6 to see how storage and infrastructure teams are turning primary storage into a frontline defense against modern threats. This webinar also features the former Storage Director at Royal Bank of Canada.
- QueryRecorded 21 Sept 2026
Your security team, multiplied. Same analysts. Same shift. More alerts investigated, more hunts run, a backlog that finally gets worked. Query Workers run the cases your team never had time for: evidence assembled, every query logged, every gap flagged. Your analysts make every call. AI for the SOC that makes your job easier.
- QueryRecorded 21 Sept 2026
Detection coverage is constrained by your ingestion budget. Every source that never lands in your SIEM is a source your detections can't see. That blind spot isn't a tuning problem. It's an architecture decision, made by an opex budget. Federated Detections break the dependency. Write a rule once and run it across every connected source, wherever the data lives. No ETL, no duplication, no re-platforming required. Extend detection coverage across all your security data, including sources your SIEM will never ingest.
- ControlMonkeySince 18 Sept 2026
Your customers can recover their data. Can they recover the configuration that keeps the business running? 🔐 Identity. 🌐 Networking. 🛡️ Security. 📊 Observability. ☁️ Cloud infrastructure.
- CoroSince 19 Sept 2026
59% of smaller hospitals lack dedicated 24/7 threat monitoring. See how RHTP can support stronger, sustainable protection.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.