B2B ad examples
1,817 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- Bureau Veritas Cybersecurity NordicsSince 12 Jun 2026
Sådan bruger du Assume Breach til at beslutte, hvad der skal fixes først i jeres systemer. I webinaret Assume Breach i praksis viser Michael Dyrmose (tidl. ansat i FE og grundlægger af cyberlandsholdet), hvordan du antager foothold og bruger et offensivt mindset til at gøre sårbarheder prioriteringsklare. 👉 Se webinaret lige når du vil her
- Bureau Veritas Cybersecurity NordicsSince 12 Jun 2026
"Antag, at en angriber allerede har kompromitteret jeres netværk" 🧑💻 Det er udgangspunktet for en Assume Breach. I stedet for kun at teste jeres ydre forsvar, simulerer vi en hacker, der allerede har fodfæste. Vi finder de svagheder, der reelt bliver udnyttet: ✅ Sårbarheder i jeres interne systemer ✅ Misbrug af rettigheder og konti ✅ Kritiske konfigurationsfejl I får et klart billede af jeres reelle modstandsevne og en prioriteret plan for, hvor I skal styrke sikkerheden først. Se mere på vores hjemmeside.
- Integrity360 FranceSince 12 Jun 2026
Nous sommes ravis d’accueillir Vectra AI en tant que Sponsor Platinum de Security First 2026. La plateforme pilotée par l’IA de Vectra détecte les comportements des attaquants à travers les réseaux, le cloud et les identités, permettant aux organisations d’identifier et de stopper des menaces que les outils traditionnels laissent souvent passer. Rejoignez-nous pour découvrir comment l’automatisation intelligente, combinée à l’expertise humaine, redéfinit la cyber-résilience moderne. 📍 Rendez-vous le 24 juin 2026 à L’Apostrophe, 83 avenue Marceau, Paris 16e 👉 Inscrivez-vous dès maintenant : https://lnkd.in/evX-qi8S #SecurityFirst2026 #Cybersécurité #IA #IdentitéMachine #Cyberrésilience #InfoSec #ÉvénementsCybersécurité #HumanAI #TendancesCybersécurité #LeadershipCybersécurité
- Integrity360 FranceSince 12 Jun 2026
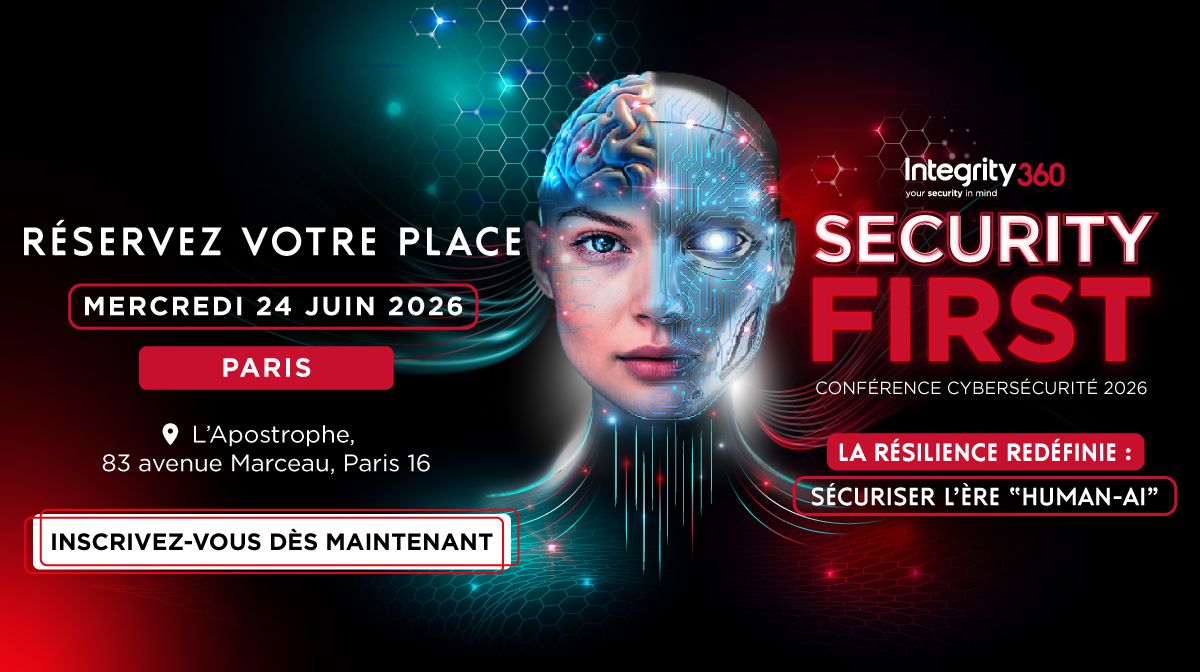
Le 24 juin 2026, Integrity360 France lance la première édition de Security First à Paris. https://lnkd.in/evX-qi8S Un format pensé pour aller à l’essentiel : du contenu de « pure thought leadership », des échanges sans détour et une vision concrète des enjeux cyber d’aujourd’hui et de demain. Ici, pas de discours commerciaux ni de surface. L’événement réunira uniquement des pairs du secteur, des spécialistes d’Integrity360, des experts reconnus et quelques partenaires technologiques de premier plan. L’objectif est simple : confronter les points de vue, partager des retours d’expérience concrets et ouvrir des perspectives actionnables. Si vous cherchez un rendez-vous où la qualité des échanges prime sur la quantité, Security First a été conçu pour vous. Les places sont volontairement limitées afin de préserver la richesse des discussions. 📆 Mercredi 24 juin 2026 📍 L’Apostrophe, 83 avenue Marceau, 75116 Paris 📢 La résilience redéfinie – protéger l’ère Humain-IA. 👉 Les inscriptions sont ouvertes dès maintenant sur la page dédiée d’Integrity360 France : https://lnkd.in/evX-qi8S #Securityfirst2026 #cybersecurity #events #infosec #ai
- IDGateway® LimitedSince 16 Jun 2026
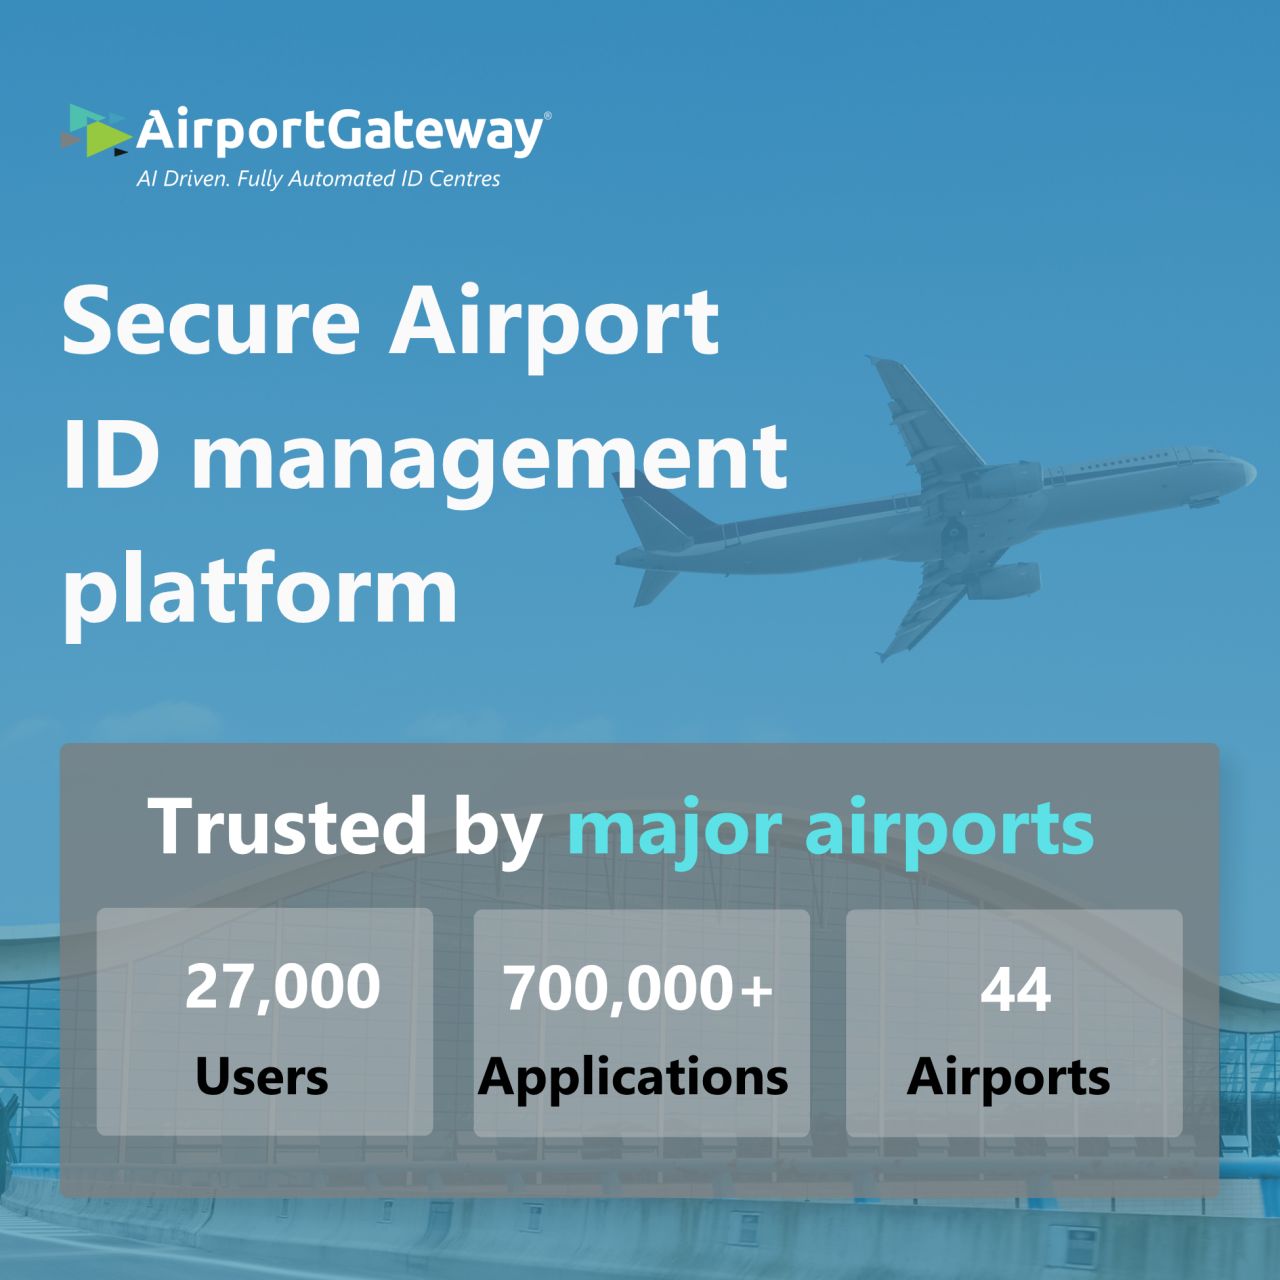
Trusted by major airports worldwide to manage ID pass applications securely.
- IDGateway® LimitedSince 16 Jun 2026
Reduce admin and improve control across your ID Centre.
- IDECSISince 26 Jun 2026
7 à 10 risques identifiés par utilisateur. C'est ce que révèle un diagnostic DETOX sur Microsoft 365. La plupart des entreprises ne les voient pas venir. Faites le point avant qu'il soit trop tard.
- IDECSISince 26 Jun 2026
Vos utilisateurs prennent des risques sans le savoir. Pas par négligence. Parce qu'ils n'ont jamais vu ce qui est exposé sur leurs propres données. IDECSI leur montre. Et transforme chaque collaborateur en premier rempart contre les incidents. Demandez une démo.
- IntorqaSince 13 Jul 2026
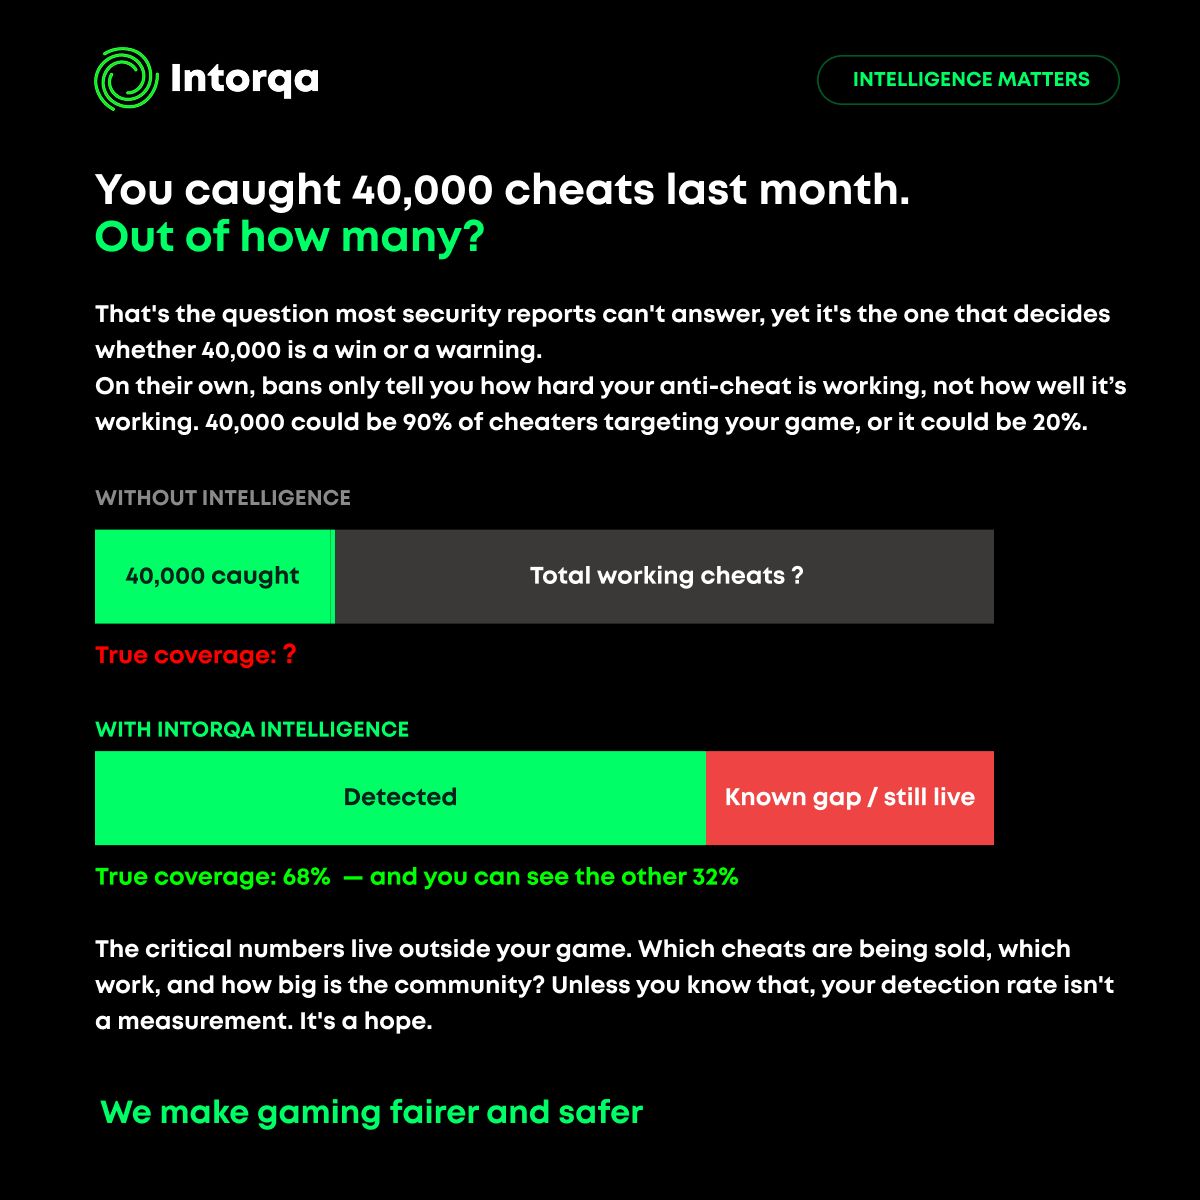
When it comes to evaluating your latest ban wave, intelligence matters. Contact us to find out how we can help you protect your game.
- IntorqaSince 13 Jul 2026
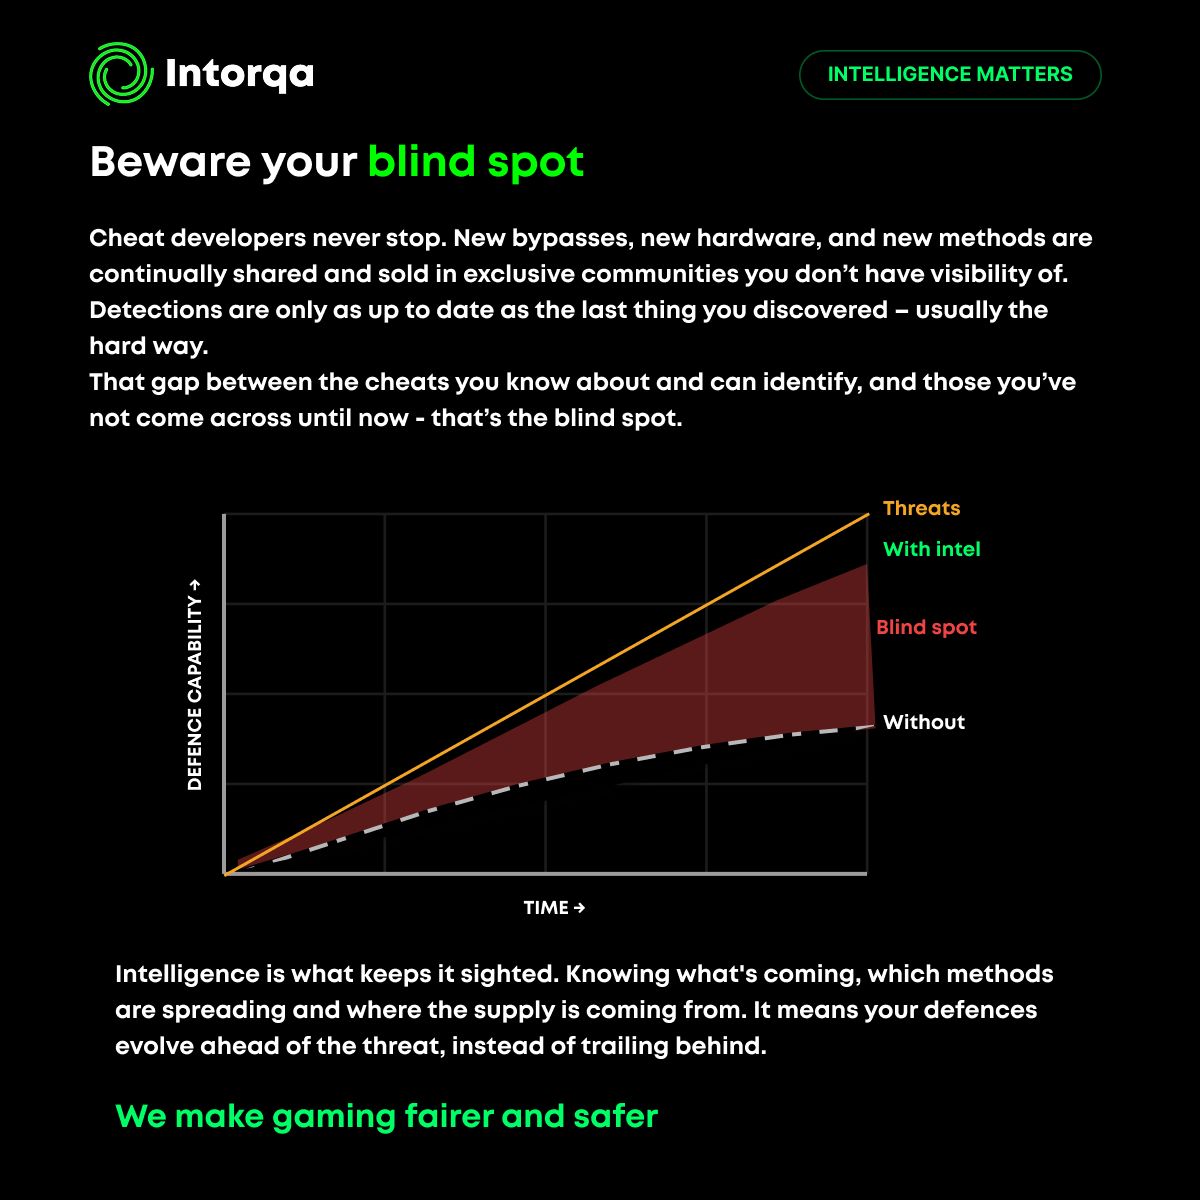
When it comes to ensuring your anti-cheat isn't missing the latest cheats, intelligence matters. Contact us to find out how we can help you protect your game.
- imper.aiRecorded 23 Sept 2026
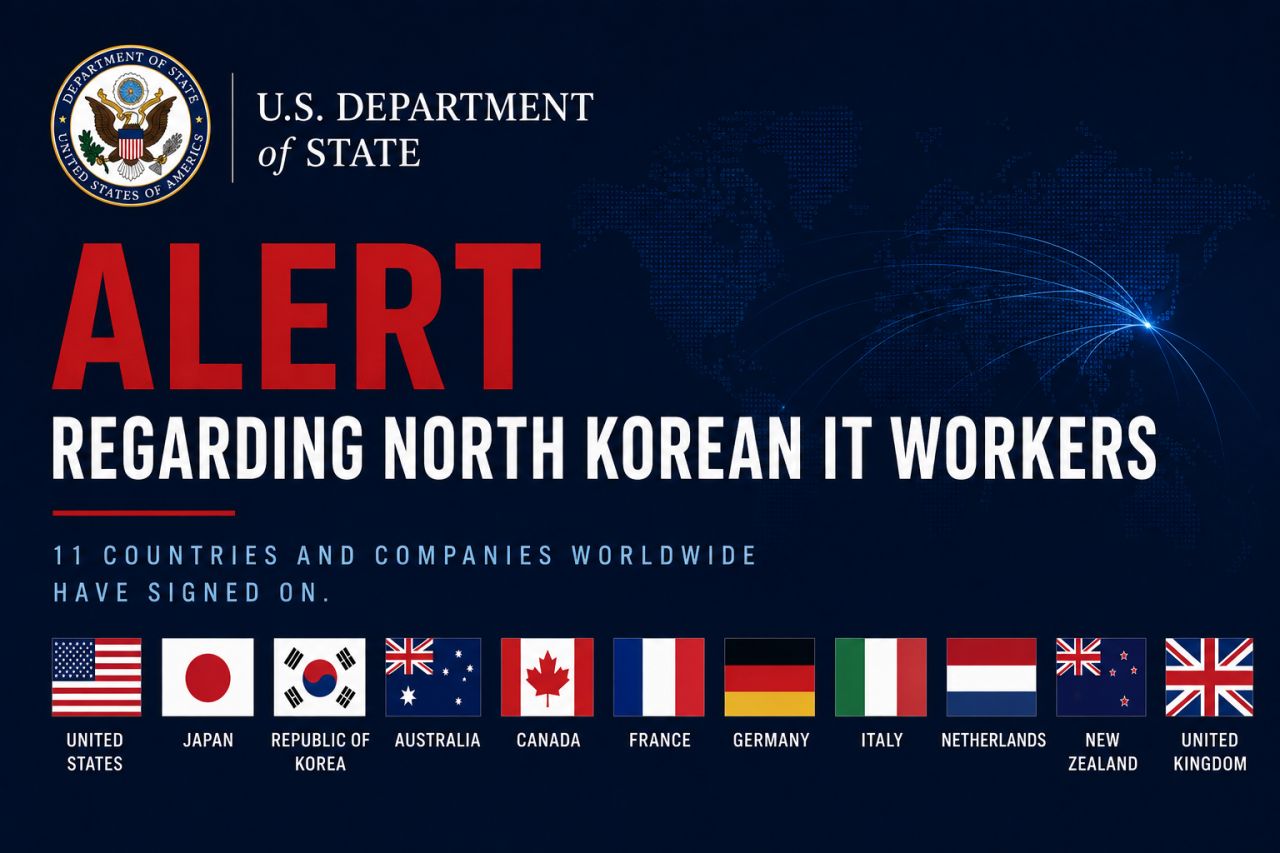
You have been warned. By 11 countries. On July 31, all seven G7 nations plus four allies issued a joint alert on North Korea's IT worker scheme. First time France, Germany, Italy and the Netherlands have signed on. This is no longer a US and Korea problem. What the alert describes: •Pose as locals. Get hired. Collect a salary. Send it home. •Increasingly AI-built: fake personas, polished resumes, manipulated interview video. •Once inside, the paycheck is not the point. Insider access is. Data theft follows. •The money funds North Korea's nuclear and missile programs. •Paying these workers can break domestic law and UN sanctions, not just security policy. How far it has spread: •One laptop farm alone: $17M for the regime, and 300+ US companies affected (DOJ). •Eight US-based laptop farm operators jailed in about five months (DOJ). •FAMOUS CHOLLIMA activity doubled in 2025 (CrowdStrike). What to do: •Treat identity as a process, not a one-time check. •Put a signal layer in front of every interview, not just the last. •Correlate across interviews. One "hire" is often a team. •Treat onboarding as the point of no return. Verify before access. The warning is on the record. What you do next is a choice. Full breakdown: https://lnkd.in/gYksdYNP//?utm_source=linkedin&utm_medium=paid&utm_id=1201173964&utm_campaign=Boost_Post_WebsiteVisits_Aug13,2026&hsa_acc=517492235&hsa_cam=1201173964&hsa_grp=879583074&hsa_ad=1504295504&hsa_net=linkedin&hsa_ver=3 Read the alert: https://lnkd.in/ewHNxdv5//?utm_source=linkedin&utm_medium=paid&utm_id=1201173964&utm_campaign=Boost_Post_WebsiteVisits_Aug13,2026&hsa_acc=517492235&hsa_cam=1201173964&hsa_grp=879583074&hsa_ad=1504295504&hsa_net=linkedin&hsa_ver=3 #HiringFraud #DPRK #NorthKoreanITworkers
- imper.aiRecorded 23 Sept 2026
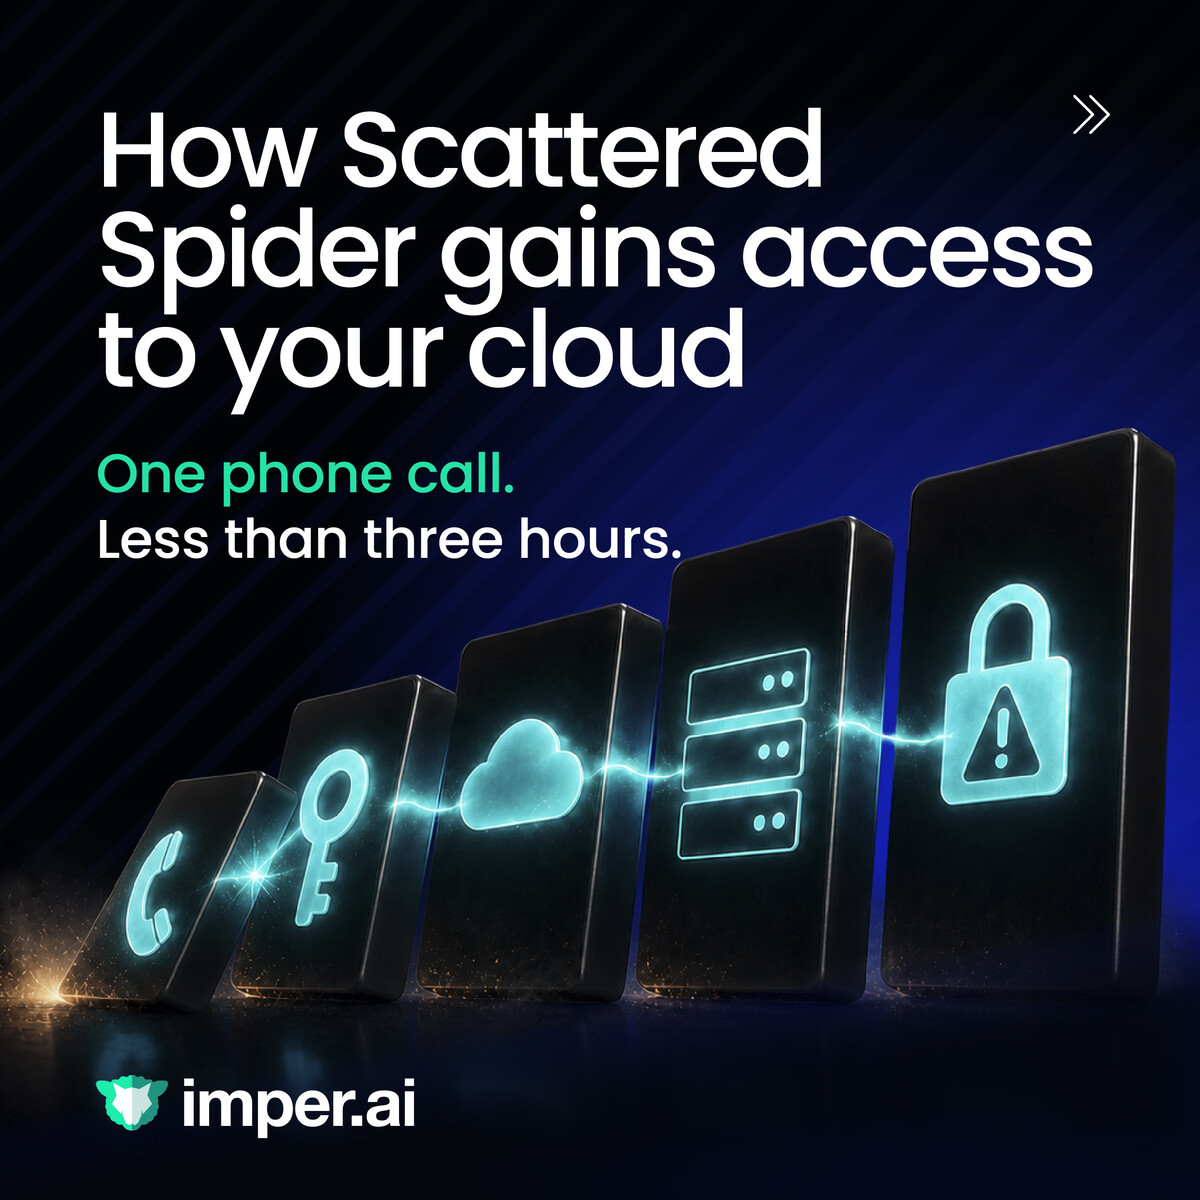
All it takes: one phone call, less than 3 hours to account takeover. Understand the attack and how to catch it before the reset.
- Industrial DefenderSince 17 Aug 2026
Article 21 requires risk analysis, incident handling, supply chain security, and encryption policies across your OT environment. Which of the ten measures can you evidence today? Map your gaps in the training. Watch on demand.
- Industrial DefenderSince 17 Aug 2026
Watch our expert panel discuss the practical realities of NIS2 for industrial operators—transposition divergence, asset visibility requirements, and the 24-hour early warning obligation.
- IntragenSince 20 Jul 2026
Attackers don't look for perfect security. They watch for overlooked identities: shared accounts, excessive access, or hidden identity gaps. Intragen's PAM specialists help organisations across EMEA find and close privileged access gaps before they're exploited.
- IntragenSince 20 Jul 2026
Shared accounts, excessive permissions, poor governance and unmanaged privileged access are common ways in for attackers. Intragen's specialists enable organisations to secure identities and build a stronger security posture.
- InfoGuard AGSince 1 Sept 2026
📢 𝟭𝟱𝟬 𝗖𝘆𝗯𝗲𝗿𝘃𝗼𝗿𝗳ä𝗹𝗹𝗲. 𝟴 𝗣𝗿𝗶𝗼𝗿𝗶𝘁ä𝘁𝗲𝗻. 𝗘𝗶𝗻 𝗥𝗲𝗮𝗹𝗶𝘁ä𝘁𝘀𝗰𝗵𝗲𝗰𝗸 𝗳𝘂̈𝗿 𝗱𝗶𝗲 𝗖𝘆𝗯𝗲𝗿𝗮𝗯𝘄𝗲𝗵𝗿 𝟮𝟬𝟮𝟲. Zwischen offenen Patches, Identitätsrisiken, Cloud-Umgebungen und knappen Ressourcen entscheidet die richtige Priorisierung über die Wirksamkeit eurer Cyberabwehr. Wo sollte dein Unternehmen heute ansetzen? Knapp 150 Cybervorfälle, die unser CSIRT im 𝗲𝗿𝘀𝘁𝗲𝗻 𝗛𝗮𝗹𝗯𝗷𝗮𝗵𝗿 𝟮𝟬𝟮𝟲 bearbeitet hat, liefern ein klares Lagebild: ➡️ 34 % der Einfallsvektoren entfallen auf Phishing. ➡️ Bei 6 von 10 Ransomware-Fällen war fehlende MFA ein entscheidender Faktor. ➡️ Exponierte Lücken, Fehlkonfigurationen und Supply-Chain-Risiken bleiben relevant. ➡️ Public LLMs schaffen neue, schwer kontrollierbare Datenrisiken. Die entscheidende Frage für CISOs und IT-Verantwortliche deines Unternehmens lautet deshalb: 𝗪𝗶𝗲 𝗴𝘂𝘁 𝗽𝗮𝘀𝘀𝗲𝗻 𝗲𝘂𝗿𝗲 𝗦𝗶𝗰𝗵𝗲𝗿𝗵𝗲𝗶𝘁𝘀𝗽𝗿𝗶𝗼𝗿𝗶𝘁𝗮̈𝘁𝗲𝗻 (𝗻𝗼𝗰𝗵) 𝘇𝘂𝗿 𝗮𝗸𝘁𝘂𝗲𝗹𝗹𝗲𝗻 𝗔𝗻𝗴𝗿𝗶𝗳𝗳𝘀𝗽𝗿𝗮𝘅𝗶𝘀? 💡 Unsere Halbjahresanalyse 2026 liefert den Realitätscheck und 𝟴 𝗸𝗼𝗻𝗸𝗿𝗲𝘁𝗲 𝗠𝗮𝘀𝘀𝗻𝗮𝗵𝗺𝗲𝗻 für eure Cyber-Security-Strategie: https://lnkd.in/erxsbAaN
- iC ConsultSince 7 Sept 2026
Microsoft E5 and E7 include powerful security capabilities that can significantly strengthen your organisation's protection. Join our live webinar to see where your existing investment can make the biggest security impact.
- IncogniaSince 5 Sept 2026
It isn’t hard to bypass most internal IDs. Turn to Incognia for an ID that persists through it all so you can see through the smoke screen, reset after reset.
- iC ConsultSince 7 Sept 2026
Microsoft E5 and E7 include powerful security capabilities that can significantly strengthen your organization's protection. Join our live webinar to see where your existing investment can make the biggest security impact.
- HypernativeSince 26 Aug 2026
Your onchain pilot works. Scaling it is a different conversation, one that runs through your risk committee, your board, and your regulator. Security isn't the cost you add after you scale. It's the proof point that gets you the green light. Hypernative secures 350+ institutions and $100B+ in onchain assets, with the audit trails and controls your ARB already asks for. Start at pilot scale. Don't let security be what stops it reaching production.
- HypernativeSince 26 Aug 2026
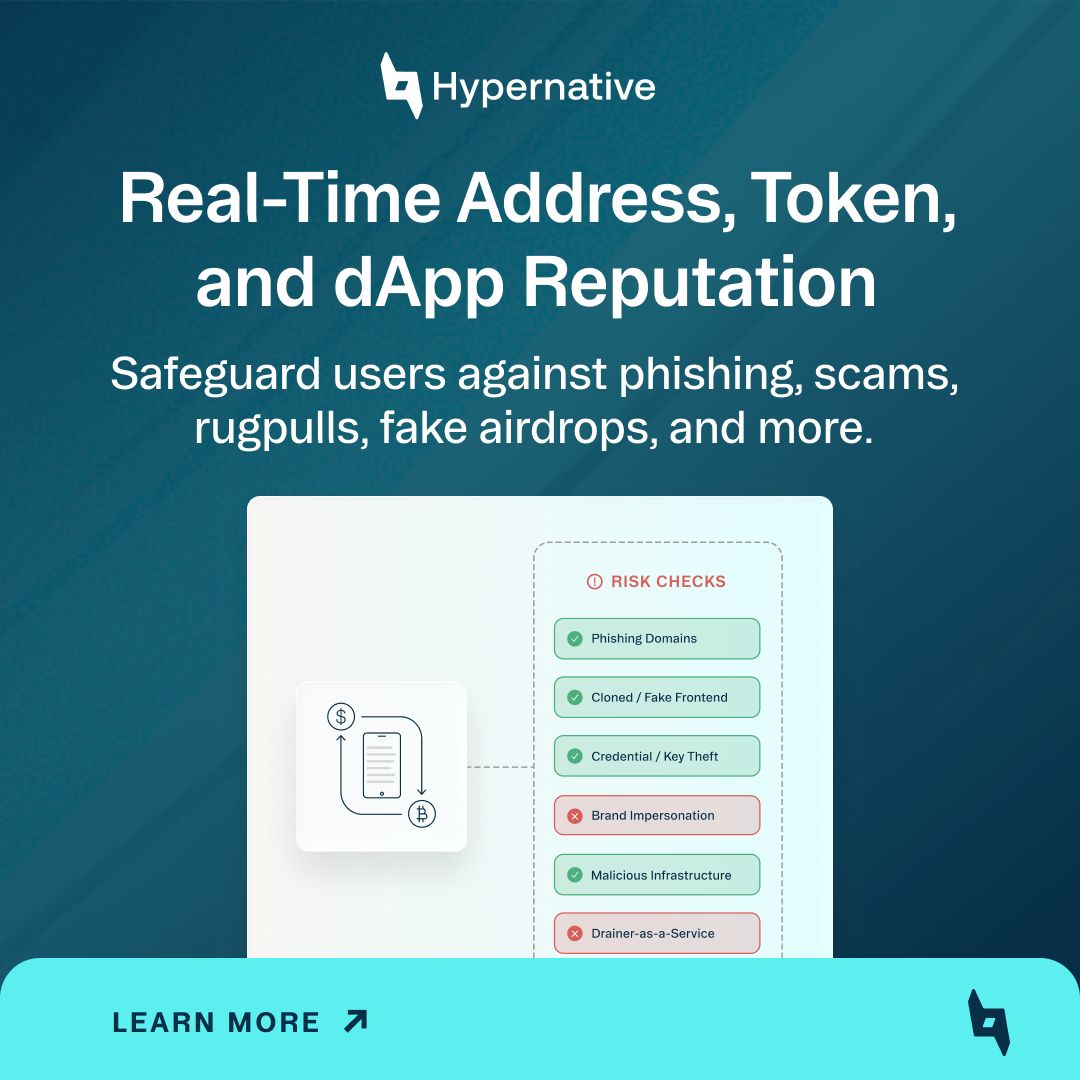
Your users can't spot the threat. Real-time reputation checks every address, token, and dApp before your user signs. It flags phishing domains, cloned dApps, drainer contracts, malicious airdrops, honeypot tokens, and address poisoning inside the signing flow, then translates each transaction into plain language before it goes through. Safe interactions pass. Risky ones get caught first. Give your users a wallet they can trust with their assets.
- IrdetoSince 27 Aug 2026
Fleet maintenance delays are often caused by something surprisingly simple: vehicle access. How much time could your team save by replacing physical keys with secure digital access? Swipe through the customer story to see the results →
- idgard GmbHSince 8 Sept 2026
🛡️ Gesundheitsdaten brauchen mehr als nur Standard-Verschlüsselung. Arztbriefe, Laborbefunde und Forschungsdaten sind hochsensibel. Erfahren Sie in unserem Whitepaper, wie Sie Patientendaten absolut versiegelt teilen und alle Vorgaben erfüllen: - DSGVO-, KRITIS- & NIS-2-konform - Sicherer Austausch mit Ärzten, IT-Abteilungen & Partnern - Revisionssichere Dokumentation aller Dateitransfers - Zero-Knowledge: Kein Zugriff für Administratoren oder Provider 👉 Jetzt erfahren, wie sich Gesundheitsorganisationen wirksam schützen können.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.