B2B ad examples
6 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- ESET NederlandSince 2 Oct 2026
Krijg Europees cybersecurityadvies dat past bij jouw organisatie en ontdek waar je risico’s liggen en hoe je die aanpakt.
- ESET NederlandSince 2 Oct 2026
Ervaar Europese cybersecurity en zie direct hoe je jouw organisatie beter beschermt tegen dreigingen.
- CorelightSince 2 Oct 2026
Post-quantum migration starts before Q-Day. See The Gartner® guidance on what security leaders should inventory prioritize and plan now.
- CorelightSince 2 Oct 2026
Your AI flagged a threat. Can you prove why? Learn how to build detections backed by verifiable network evidence, not just a confidence score.
- DSShield - درع الأمان الرقميRecorded 8 Oct 2026
نحمي الاستثمارات التي تبني مستقبلنا. بحماية مشاريع بلغت قيمتها 1.5 مليار ريال سعودي، يواصل "درع الأمان الرقمي" كونه الركيزة الأساسية للأمان الرقمي في السوق السعودي. 🇸🇦 #درع_الأمان_الرقمي #الأمن_السيبراني
- Feroot SecurityRecorded 8 Oct 2026
Your privacy policy cannot show how scripts behave inside the browser. Runtime audits revealed the activity traditional reviews overlooked.
- Feroot SecurityRecorded 8 Oct 2026
See what survey data and live-site audits reveal about CMP confidence and the difference between capturing cookie consent and enforcing it.
- iProovSince 6 Oct 2026
Account recovery is a critical identity moment: the usual authenticators may no longer be available. How do you confirm the person requesting access is the real person? Explore how human identity assurance can strengthen recovery alongside existing controls.
- HalbornSince 5 Oct 2026
If your digital assets were compromised, how much would you be able to get back? 👉 https://lnkd.in/ddndkcwP In the top 100 digital asset hacks, recovery rates fell to 11%, and key compromises fared worse at under 8%. Security spend has to go into prevention, ahead of recovery. Learn more in Halborn's State of Digital Asset Security: Top 100 Hacks Report.
- iProovSince 6 Oct 2026
Deepfakes, synthetic identities, and social engineering are creating new ways to exploit the gap between the right credential and the right human. See where that gap appears across the workforce identity lifecycle and how human identity assurance can help.
- Human RisksSince 6 Oct 2026
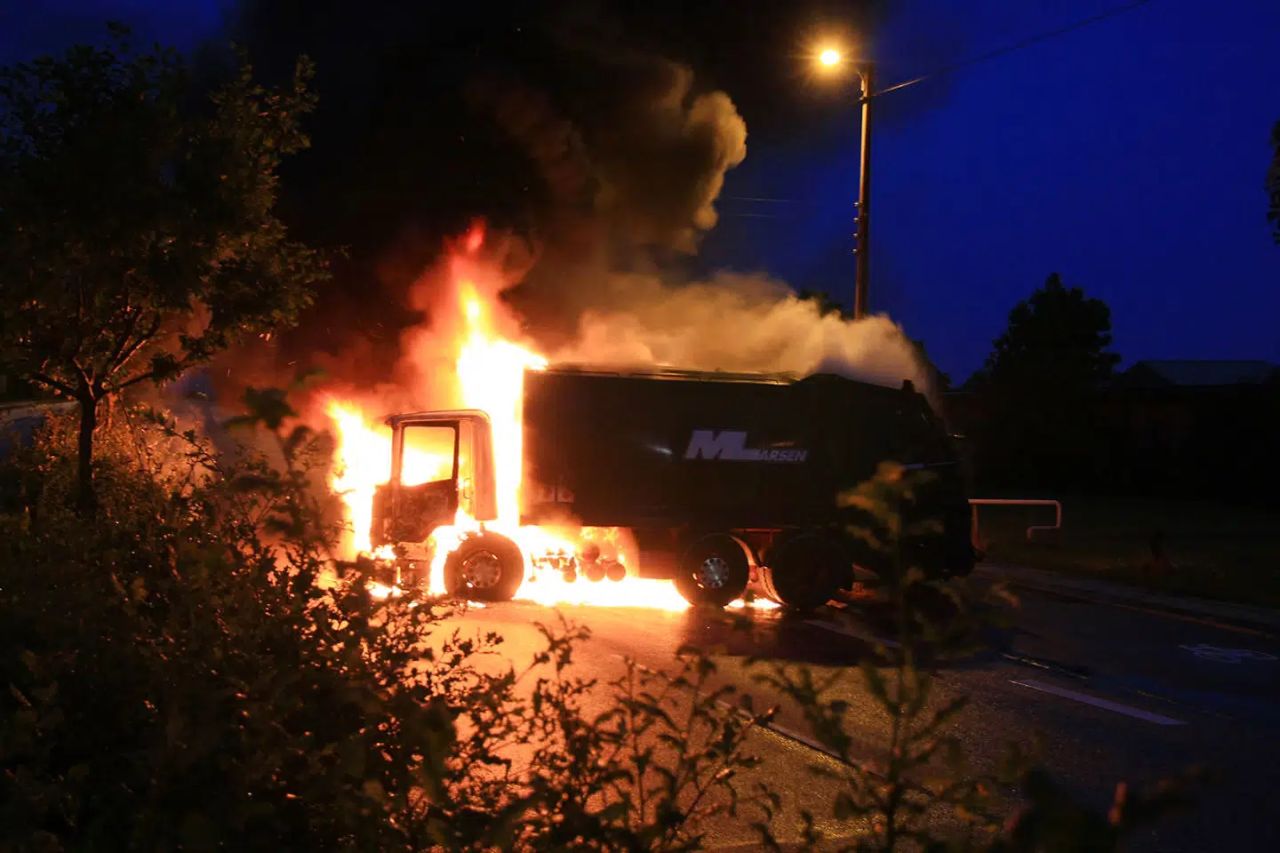
My first job as head of security was at a company that had just lost €8 million in a single night. In August 2008, robbers drove a wheel loader straight through the wall of Dansk Værdihåndtering. They'd set fire to eleven stolen garbage trucks to block the roads, scattered spike strips on the motorway, and disappeared. It's still the largest robbery in Danish history. I came in afterwards, and the brief was simple → This must never happen again. That turned out to be a long list of unglamorous work. New routines for the drivers, down to stickers on the dashboard reminding them what to do and in what order. A new Danish security standard on its way that we had to meet. There were periods where the only thing that mattered was getting through the next few weeks without incident. One of the things we did was ring the building with shipping containers filled with soil, borrowed straight from how we built camps in the military. Heavy enough that nothing was driving through them. None of it was sophisticated. It was mostly about doing a lot of ordinary things properly and consistently.
- GoldphishSince 6 Oct 2026
Over 90% of successful cyber attacks start with a phishing email. If you reduce phishing clicks, you dramatically shrink your risk, protect your operations, and save the time and cost of cleaning up a preventable mess. Start our FREE Cybersecurity Awareness Training and turn everyday inbox habits into a practical, measurable layer of protection for your business.
- IncogniaSince 6 Oct 2026
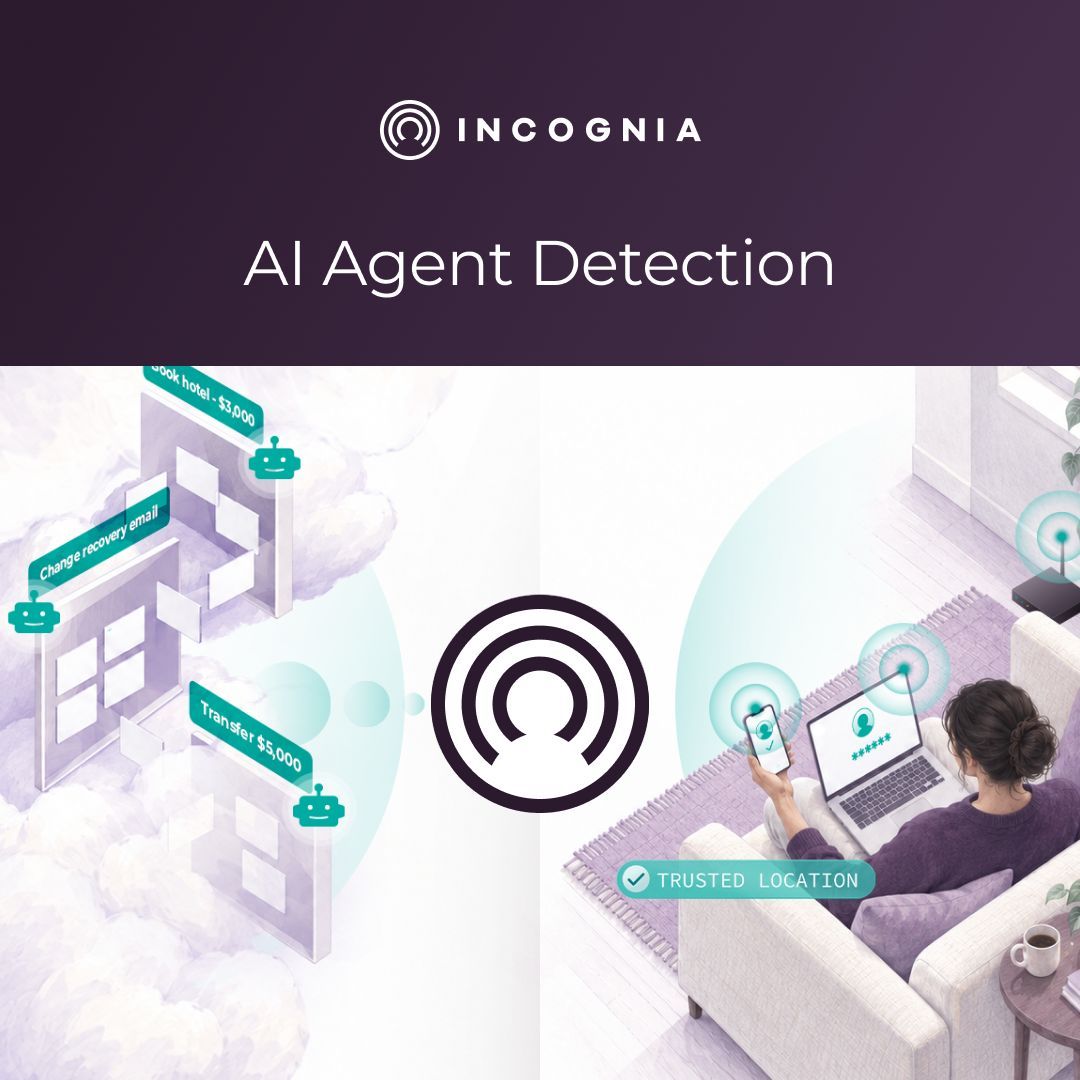
Quando um agente de IA executa uma ação, existem três perguntas diferentes: É um agente? Qual agente está fazendo a requisição? O usuário realmente autorizou aquela ação? Detecção de automação ajuda a responder a primeira. Autenticação criptográfica do agente ajuda na segunda. Mas nenhuma das duas, sozinha, comprova a intenção do usuário. Esse é o problema que a Incognia agora passa a solucionar em fluxos de Agentic AI. Imagine um agente solicitando a alteração dos dados de recuperação de uma conta bancária. O request pode estar corretamente assinado e vir de um agente legítimo. Ainda assim, isso não significa que o cliente autorizou aquela mudança. Confiar no agente e confiar na ação são problemas diferentes. Para ações de maior risco, a proposta da Incognia é trazer o humano de volta ao fluxo e combinar sua confirmação com sinais do mundo real: continuidade entre dispositivo e conta, localização precisa e conhecida, integridade do device, detecção de RATs e inteligência de risco da rede. Isso também evita o extremo oposto que é desafiar toda ação executada por IA. O nível de verificação também pode variar conforme a ação e o contexto disponível. Consultar um saldo e alterar credenciais de recuperação não deveriam necessariamente ter o mesmo tratamento. Conforme agentes começam a executar mais ações em nome dos usuários, será necessária uma evolução nas estratégias de fraude. A pergunta deixa de ser apenas “é um humano ou um bot?”. Passa a ser "quando a IA estiver agindo em nome de alguém, como garantir que o usuário continue no controle?"
- GoldphishSince 6 Oct 2026
Your clients trust you with their data; your team’s inbox is the front door to that trust. Use our FREE Cybersecurity Awareness Training to show your customers, partners, and board that you’re leading by example, not waiting for a breach to force your hand.
- CryptomathicSince 6 Oct 2026
You can’t migrate cryptography you can’t see. Without visibility and ownership, every cryptographic change becomes slower, harder and riskier. In this clip, Glen Leonhard explains why crypto-agility starts with bringing unmanaged cryptography under control. Watch the full Cryptomathic and Solid8 Technologies Pty Ltd - South Africa webinar: https://lnkd.in/eMXbSTpi #cryptoagility #cryptography #PQC
- ESET ItaliaSince 6 Oct 2026
Le votazioni per gli Italian Channel Awards sono aperte! Un riconoscimento alle eccellenze che ogni giorno contribuiscono a innovare e far crescere l’ecosistema ICT italiano. Sostieni l’innovazione nella cybersecurity: vota ESET Italia agli Italian Channel Awards. 👉 https://bit.ly/3TrqYpb ✅ Il tuo supporto fa la differenza. #ESET #ItalianChannelAwards #Cybersecurity #ICTChannel #Innovation #VoteESET
- EasyDMARCSince 6 Oct 2026
Most platforms in our space are a login page over four separate products. That was the trap we refused to build into. If crucial modules of your email security are not governed in one place, you do not have a platform. You have a bundle. And a bundle still leaves you correlating incidents by hand at 2am. The whole point of the Email Trust Platform is the connective layer underneath the four modules. One problem, traced across all of them, in one view. See what connected actually means: www.easydmarc.com/platform #EasyDMARC #EmailSecurity #EmailTrust #EmailInfrastructure
- ESET East AfricaRecorded 8 Oct 2026
Replace multiple tools with one affordable cybersecurity platform and reduce overheads, not protection.
- IncogniaSince 6 Oct 2026
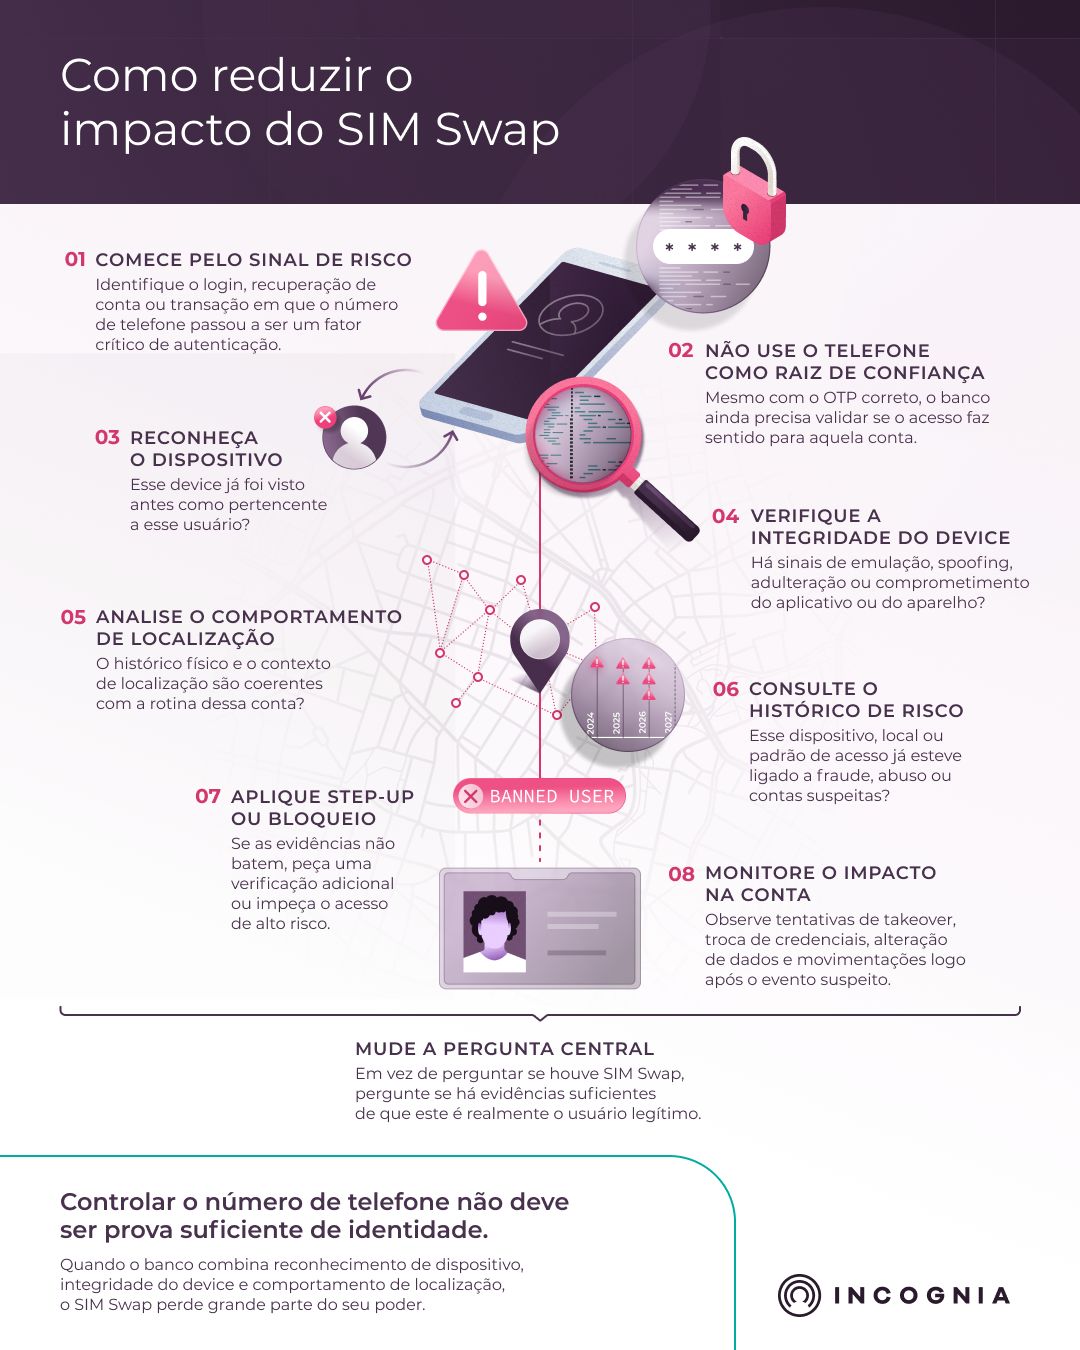
Muitos bancos ainda nos procuram com o desafio de resolver SIM Swap. E quero fazer uma afirmação direta: a Incognia já resolveu esse problema para seus clientes sem precisar validar o número de telefone ou consultar informações da operadora. Porque o objetivo do fraudador ao executar um SIM Swap não é trocar o chip da vítima. É assumir uma conta. A troca do SIM é apenas o mecanismo usado para interceptar SMS, receber OTPs e superar uma camada de autenticação que trata o controle do número de telefone como evidência de identidade. Mas imagine que, mesmo com o OTP correto, o banco ainda consiga responder duas perguntas: Esse é um dispositivo que eu reconheço como pertencente a esse usuário? E o comportamento desse dispositivo no mundo físico, considerando seu histórico de localização, é consistente com essa conta? Se a resposta for não, pouco importa que o fraudador tenha assumido o número, recebido o SMS e digitado o código corretamente. O acesso continua sendo de alto risco. É por isso que vejo SIM Swap menos como um problema que exige uma solução específica e mais como uma consequência de uma arquitetura de autenticação excessivamente dependente do telefone. A Incognia combina reconhecimento persistente de dispositivo, integridade do device e comportamento de localização para avaliar se aquele acesso faz sentido para aquela conta. Isso muda a pergunta. Em vez de: “Esse número acabou de sofrer um SIM Swap?” Passamos a perguntar: “Tenho evidências suficientes de que este é realmente o usuário legítimo acessando a conta?” Essa diferença é importante porque evita transformar cada nova modalidade de ataque em mais uma ferramenta específica adicionada ao stack de fraude. O banco pode continuar utilizando dados de telefone para outras finalidades e até manter soluções de validação de SIM quando houver um caso de uso específico para isso. Mas, para mitigar account takeover decorrente de SIM Swap, o telefone não precisa ser a raiz de confiança. Na prática, o SIM Swap não desaparece como técnica de fraude. Ele perde grande parte do seu poder quando controlar o número de telefone deixa de ser suficiente para se passar pelo usuário.
- Human RisksSince 6 Oct 2026
I'm in the UK this week meeting with clients. It's expensive and time-consuming, and it doesn't scale. You'd think software companies would avoid this. But we keep doing it because the feedback is completely different when you're in the room. At GSK, we're spending 2-3 hours going through product strategy and getting hands-on feedback. Not just from their security chiefs, but from the on-site teams who actually use our system out on their sites. That's the part most software companies miss. The people who sign the contracts aren't always the ones living with your product decisions every day. The teams tell us what's working, what's frustrating, how they're actually using the features. That's worth more than any survey or support ticket. HSBC is also hosting a networking event with an intelligence firm and invited us along. Looking forward to that. It's not efficient. But it's how you build products people want to keep using.
- COMDARecorded 8 Oct 2026
סיסמאות שעוברות מיד ליד ונשמרות מקומית, פורטים חשופים לרשת, תוכנות שצריך להתקין ולתחזק בכל עמדה, ושליטה מוגבלת במה שקורה אחרי ההתחברות. וכשמשהו משתבש, צוותי האבטחה נשארים עם אותן שאלות: - מי התחבר? לאן? - מה הוא עשה? - אדם או סוכן AI? - האם היה צריך לעצור אותו מוקדם יותר? הכירו את פלטפורמת Secure Gateway של Comda שער כניסה אחד, מאובטח ומבוקר, לכל גישה מרחוק בארגון, ישירות מהדפדפן. לפרטים נוספים והדגמה לחצו>> https://lnkd.in/dJQk3C3S
- ESET East AfricaRecorded 8 Oct 2026
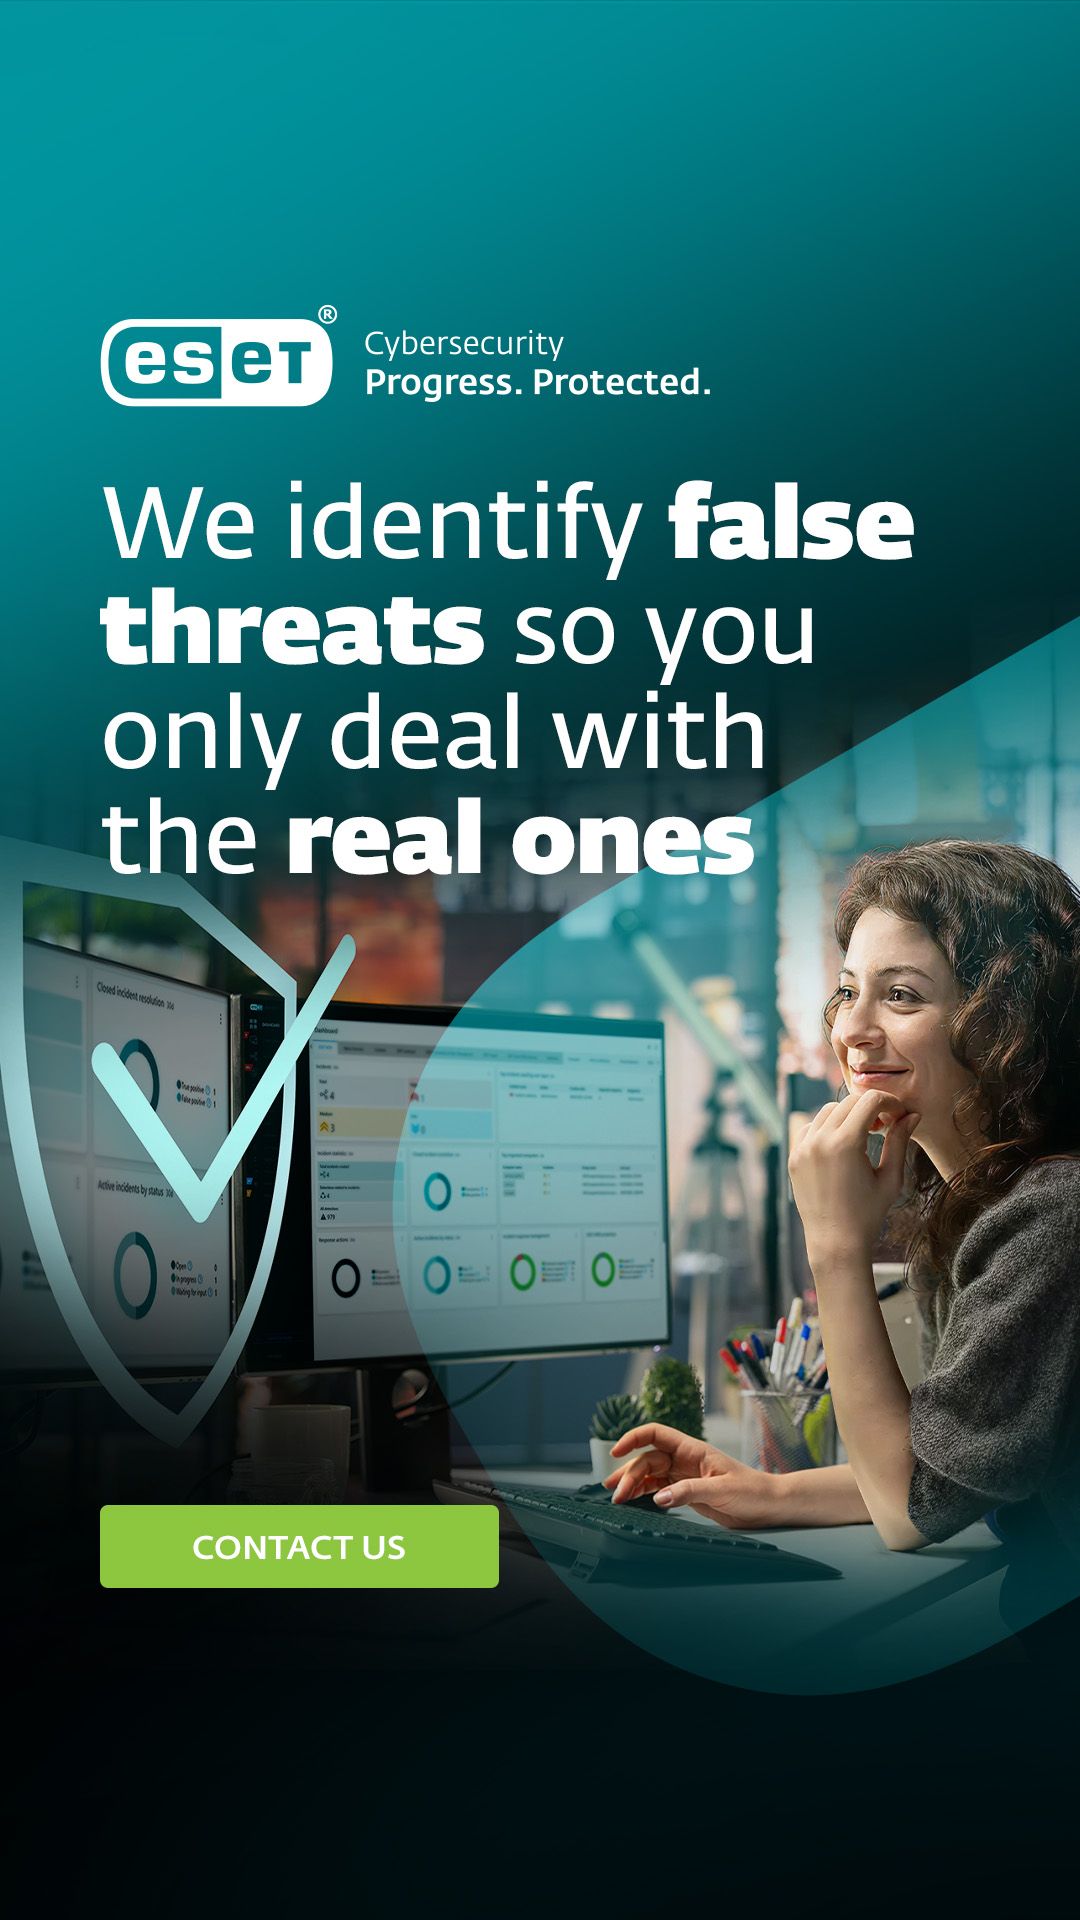
Overwhelmed by cyberthreats? ESET defends against real threats and flags the false ones so you can grow your business.
- Clavis Segurança da InformaçãoRecorded 8 Oct 2026
Relatórios, e-books e análises de risco para gestores de TI.
- Clavis Segurança da InformaçãoRecorded 8 Oct 2026
Análises sobre ataques, LGPD e riscos que afetam empresas no Brasil.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.