B2B ad examples
3 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- BioCatchSince 13 Oct 2026
Detect a wider range of scams in real time.
- CounterfakeSince 12 Oct 2026
Your AI-powered detective, built to eliminate global counterfeiting. Autonomous. Scalable. Always on.
- CounterfakeSince 12 Oct 2026
Counterfake empowers your platform with an always-on AI agent built to detect, report, and eliminate counterfeit products across every digital channel #counterfake #brandprotection #counterfeitdetection #dupedetection #marketplacesafety #digitalrisk #aiagent
- Gambit SecurityRecorded 13 Oct 2026
Sometime when we think about resilience we only see what's immediately in front of us and not the wider landscape so before you spend another $1 on resilience, tell me what actually matters that isn't right in front of your face. All of it?! A company recently told me they had to temporarily halt US production following a ransomware attack. Think about what “restart production” actually means in a business like that. Applications have to work. Infrastructure has to work. Identity and data have to be available. Operational technology matters. So do the third parties sitting somewhere in that chain. Miss one critical dependency and your recovery plan can look great while the business is still standing still. This is where I think we're spending resilience budgets in the wrong order. Cyber spending grew 12% last year according to Boston Consulting Group (BCG), with more than 80% of the security leaders they surveyed continuing to increase budgets into 2027. More money is coming. I'd spend the first part of it on understanding the business. Pick the process that absolutely has to restart after an attack. Map every application, identity, dataset, piece of infrastructure and external service it needs to function. Then decide where the resilience investment goes. That's how I think about Minimum Viable Business at Gambit Security. Start with what makes the business run, understand everything underneath it, then use that evidence to decide what deserves your time and money. Otherwise we risk spending more on resilience without actually knowing what we're trying to keep alive. Book your Resilience Assessment: https://lnkd.in/eiMCnq9b
- Gambit SecurityRecorded 13 Oct 2026
Wandering through the woods on a firday random thought... One of the last items left in a trust center that's purely a PDF...recovery testing! People can have a crasy amount of audits per year! DORA. NIST. SOC 2. ISO 42001. Cyber insurance. Customer assurance. Different acronyms. Same question...Can you prove you can recover? And somehow the answer is still screenshots, spreadsheets and chasing engineers...At best a PDF done once a year. Every. Single. Time...That's insane! Your resilience evidence should already exist. Did recovery work? How long did it take? What broke? Can you prove it? If you do this once a year then one week later it's all irrelevant because something changed in the application or company. If you're rebuilding the evidence every time an auditor asks, you don't have evidence...You have an arts & crafts project. Book your Resilience Assessment: https://lnkd.in/e4fF2maj
- GAT LabsSince 11 Oct 2026
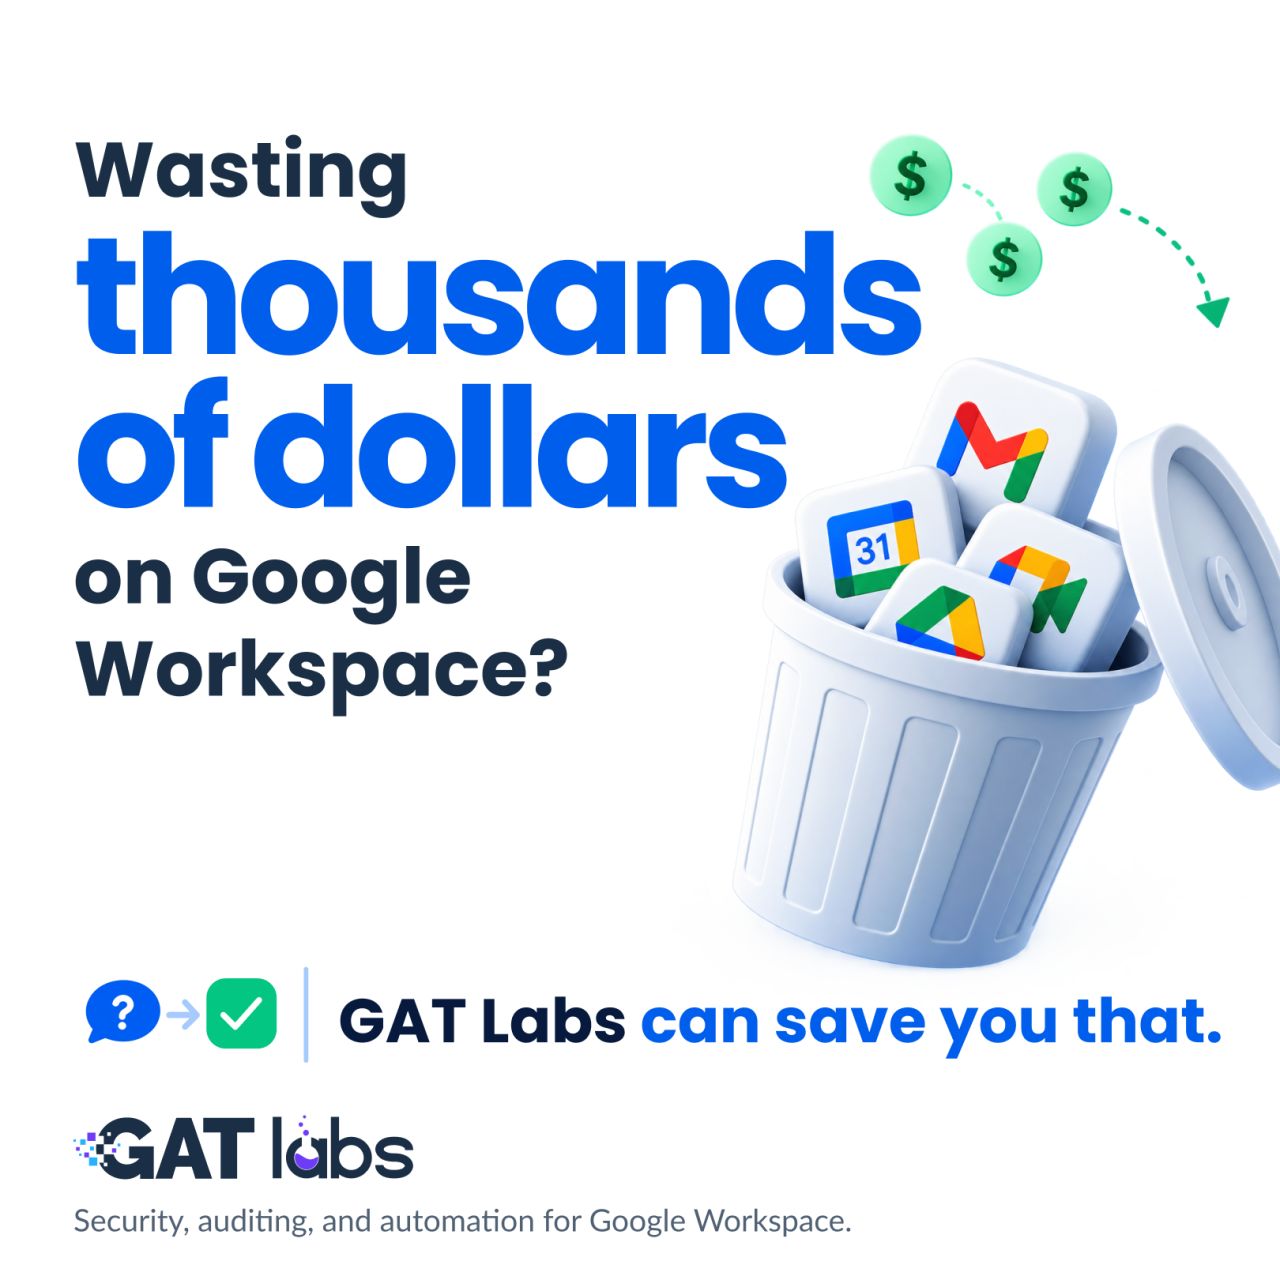
Most finance teams have no idea how much of their Google Workspace spend is going toward licenses nobody's using, storage nobody needs, or apps nobody remembers connecting, and that invisible waste adds up fast. GAT Labs surfaces exactly where your Workspace budget is leaking so you can reclaim it before the next renewal, turning guesswork into a clear, actionable picture of your actual usage.
- FortraSince 10 Oct 2026
AI is only as secure as the data behind it. AI can access, move, and act on sensitive data in ways traditional controls were never designed to govern. Fortra helps you protect the sensitive data your AI depends on, from discovery to enforcement.
- Alice (Formerly ActiveFence)Since 8 Oct 2026
Alice is building a screened network of proven offensive security specialists for selective, project-based AI red teaming. Take on technically demanding engagements alongside practitioners you respect, while keeping the independence you chose in the first place. Bring the expertise. We’ll bring the problems worth solving.
- Alice (Formerly ActiveFence)Since 8 Oct 2026
Built for experienced offensive security practitioners. Join the Alice Collective for flexible, project-based work testing GenAI, LLMs and AI agents against emerging attack surfaces.
- CyberGlobalSince 10 Oct 2026
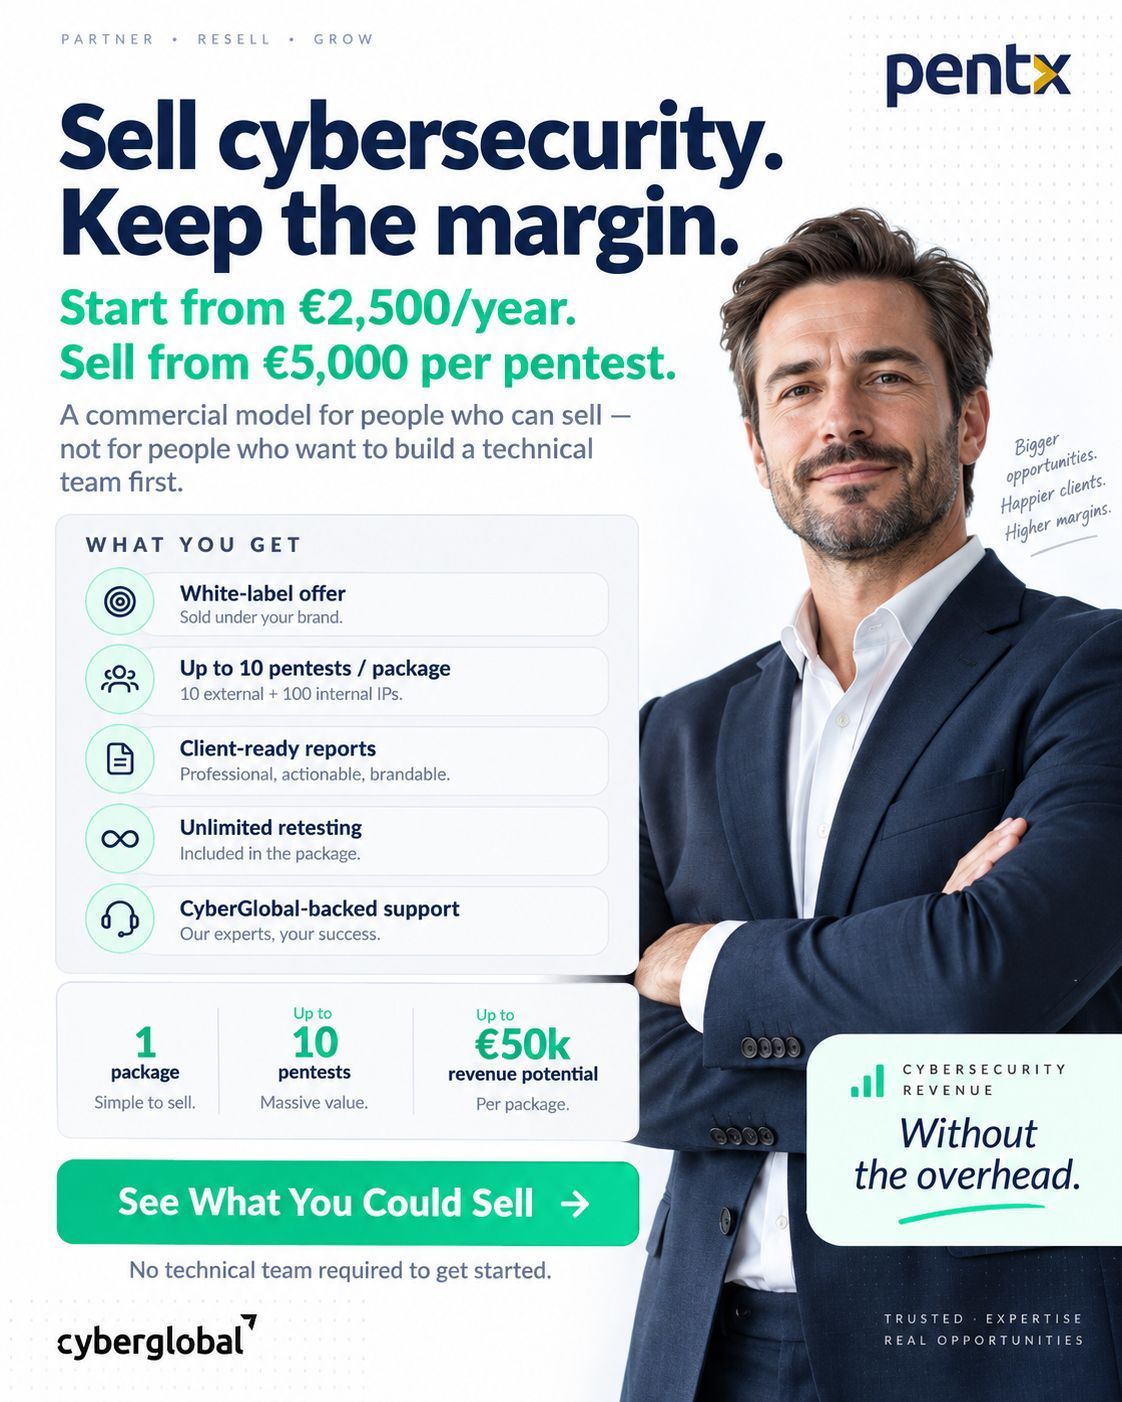
Built revenue for others? Build your own B2B security offer. PentX: €2,500/year
- ZynapSince 10 Oct 2026
Your last pentest describes one day. New exposure appears every week. Zynap validates it continuously and reduces what is exploitable, with evidence.
- ZynapSince 10 Oct 2026
The tools you already own can close exposure. Zynap turns them into one executing arm for preemptive action, vendor-agnostic, no rip and replace.
- CyberGlobalSince 10 Oct 2026
Add a security offer, not another department. PentX: €2,500/year, with white-label reports and sales materials. Explore the partner model.
- Accredit SolutionsRecorded 12 Oct 2026
Most training platforms record a completed course. But they can't can stop someone walking through the gate without it. Accredit Induct is embedded in the accreditation workflow, so completed training directly decides whether a credential is issued and which zones someone can enter. No induction. No access.
- Accredit SolutionsRecorded 12 Oct 2026
A training record sitting in a separate system can't stop the wrong person reaching a restricted area. With Accredit Induct, every accreditation is linked to the individual's identity, role and completed training, with a full audit trail showing who approved access and why.
- Ping IdentitySince 8 Oct 2026
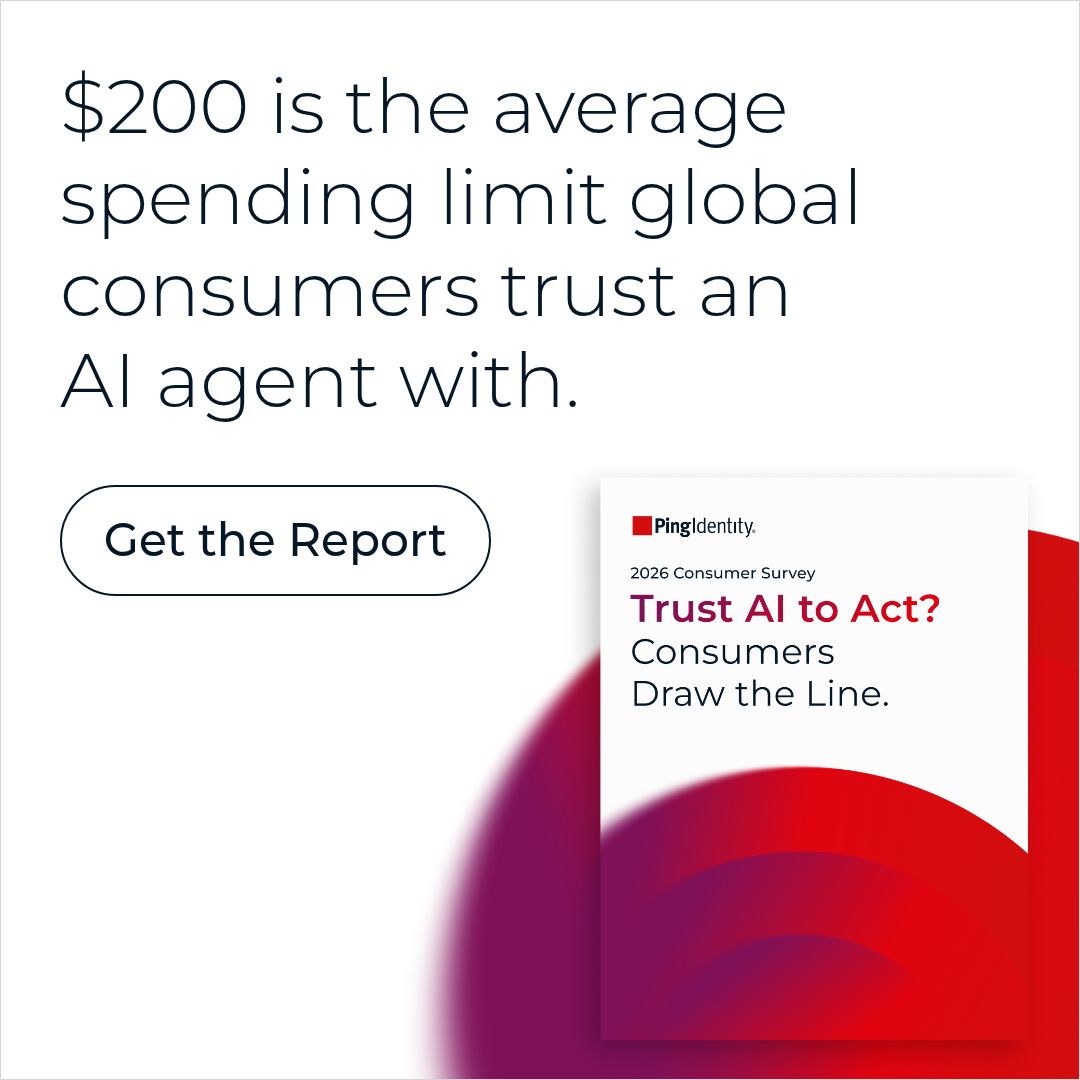
Consumers are putting limits on AI autonomy. The average they'd let an agent spend? $200. See where else they limit their comfort with AI automation.
- Ping IdentitySince 8 Oct 2026
Attackers don't just target login anymore. This KuppingerCole Analysts report shows why securing the full journey is critical to protecting and growing your enterprise.
- 0patchSince 9 Oct 2026
One year after Microsoft Windows 10 end of support, the bill goes up: on October 13, 2026 the first year of business ESU ends and year two costs twice as much per device. 0patch keeps Windows 10 secure until 2030 for a fraction of that. Just in-memory micropatches, no reboots, no Microsoft account, central management for the whole fleet. See how it compares before you renew.
- 0patchSince 9 Oct 2026
Microsoft Office 2021 reaches end of support on October 13 – and unlike Microsoft Windows 10, there is no ESU program. 0patch keeps it patched until at least 2029, with no reboots and no forced upgrade. One license covers Windows 10 too.
- IvantiSince 7 Oct 2026
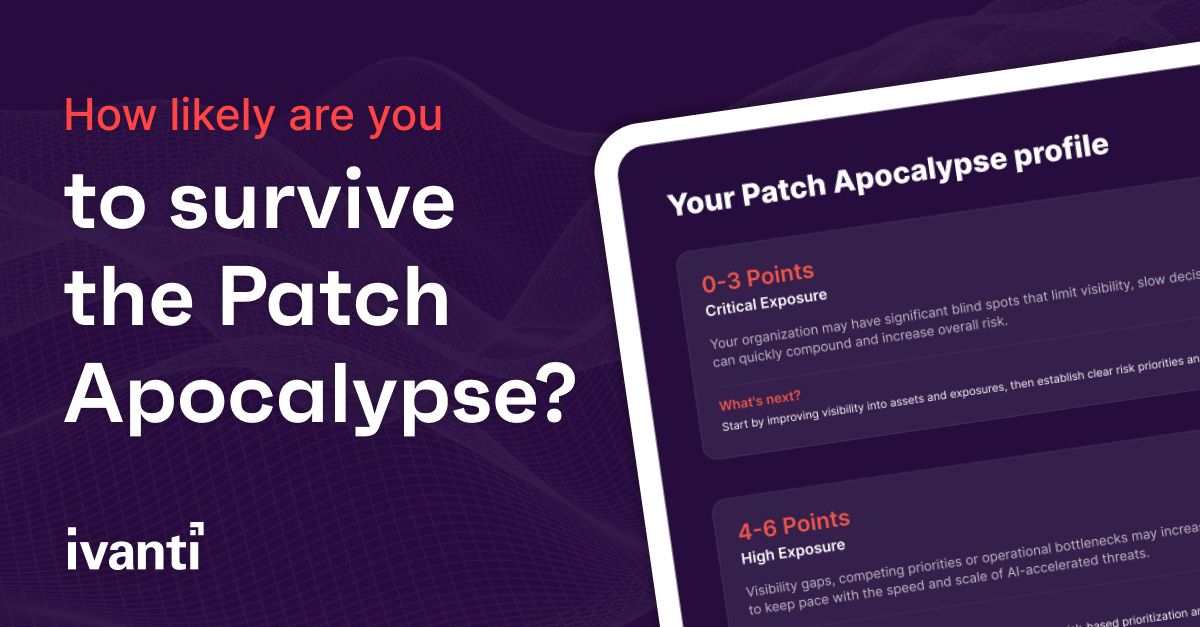
The most prepared orgs can see risk clearly, understand what matters most and confidently respond when conditions change.
- IvantiSince 7 Oct 2026
Calculate how resilient your patching process is against AI-driven threats. See where your organization really stands.
- InfoGuard AGSince 7 Oct 2026
🔐 𝐒𝐞𝐜𝐮𝐫𝐢𝐭𝐲 𝐀𝐰𝐚𝐫𝐞𝐧𝐞𝐬𝐬 𝐢𝐬𝐭 𝐦𝐞𝐡𝐫 𝐚𝐥𝐬 𝐒𝐞𝐧𝐬𝐢𝐛𝐢𝐥𝐢𝐬𝐢𝐞𝐫𝐮𝐧𝐠. Sie ist Teil unternehmerischer Verantwortung. Der «European Cyber Security Month» rückt im Oktober europaweit Cyber Security und den bewussten Umgang mit digitalen Risiken in den Fokus. Für mich ist das ein guter Anlass, eine Frage zu stellen, die auf die Agenda jeder Geschäftsleitung gehört: ❓𝐖𝐨𝐫𝐚𝐧 𝐞𝐫𝐤𝐞𝐧𝐧𝐞𝐧 𝐰𝐢𝐫, 𝐨𝐛 𝐮𝐧𝐬𝐞𝐫𝐞 𝐒𝐞𝐜𝐮𝐫𝐢𝐭𝐲 𝐀𝐰𝐚𝐫𝐞𝐧𝐞𝐬𝐬 𝐭𝐚𝐭𝐬ä𝐜𝐡𝐥𝐢𝐜𝐡 𝐰𝐢𝐫𝐤𝐭? Nicht allein an Abschlussquoten oder der Klickrate einer Phishing-Simulation. Entscheidend ist, wie Mitarbeitende handeln, wenn es darauf ankommt: ▶️ Melden sie verdächtige E-Mails – auch nach einem unbedachten Klick? ▶️ Sprechen sie Unsicherheiten frühzeitig an? ▶️ Funktionieren Meldewege auch unter Zeitdruck? ▶️ Wissen sie, was bei einem Sicherheitsvorfall zu tun ist? Für mich zeigt sich genau hier, ob Security Awareness wirklich Teil der Unternehmenskultur ist – oder am Ende doch nur ein Pflichtprogramm bleibt. Fehler werden sich nie vollständig verhindern lassen. Entscheidend ist deshalb, wie gut eine Organisation darauf vorbereitet ist und wie handlungsfähig sie bleibt, wenn etwas passiert. 𝐃𝐢𝐞 𝐔𝐦𝐬𝐞𝐭𝐳𝐮𝐧𝐠 𝐯𝐨𝐧 𝐒𝐞𝐜𝐮𝐫𝐢𝐭𝐲 𝐀𝐰𝐚𝐫𝐞𝐧𝐞𝐬𝐬 𝐥ä𝐬𝐬𝐭 𝐬𝐢𝐜𝐡 𝐝𝐞𝐥𝐞𝐠𝐢𝐞𝐫𝐞𝐧. 𝐃𝐢𝐞 𝐕𝐞𝐫𝐚𝐧𝐭𝐰𝐨𝐫𝐭𝐮𝐧𝐠 𝐝𝐚𝐟ü𝐫 𝐧𝐢𝐜𝐡𝐭. Wirksame Security Awareness beginnt deshalb bei der Führung. Regulatorische Anforderungen wie NIS2 unterstreichen diese Verantwortung für betroffene Organisationen zusätzlich. Mitarbeitende müssen Risiken einordnen und in kritischen Situationen angemessen handeln können. Gleichzeitig müssen Organisationen aus Simulationen, Meldungen und realen Vorfällen lernen. Ziel sind nicht fehlerfreie Mitarbeitende, sondern widerstandsfähige Organisationen. Und genau diese Widerstandsfähigkeit ist eine Führungsaufgabe. Wie wird Security Awareness in eurem Unternehmen gesteuert: als jährliche Pflichtübung – oder als Bestandteil der unternehmerischen Resilienz? Am 22. Oktober zeigt Sarah Mühlemann, Cyber Security Consultant bei InfoGuard AG, in unserem Webinar, wie menschenzentrierte Security Awareness in der Praxis funktioniert und wie daraus eine nachhaltig gelebte Sicherheitskultur entsteht. Den Link zur Anmeldung findet ihr im Kommentar. 👇
- IntelliGRCRecorded 12 Oct 2026
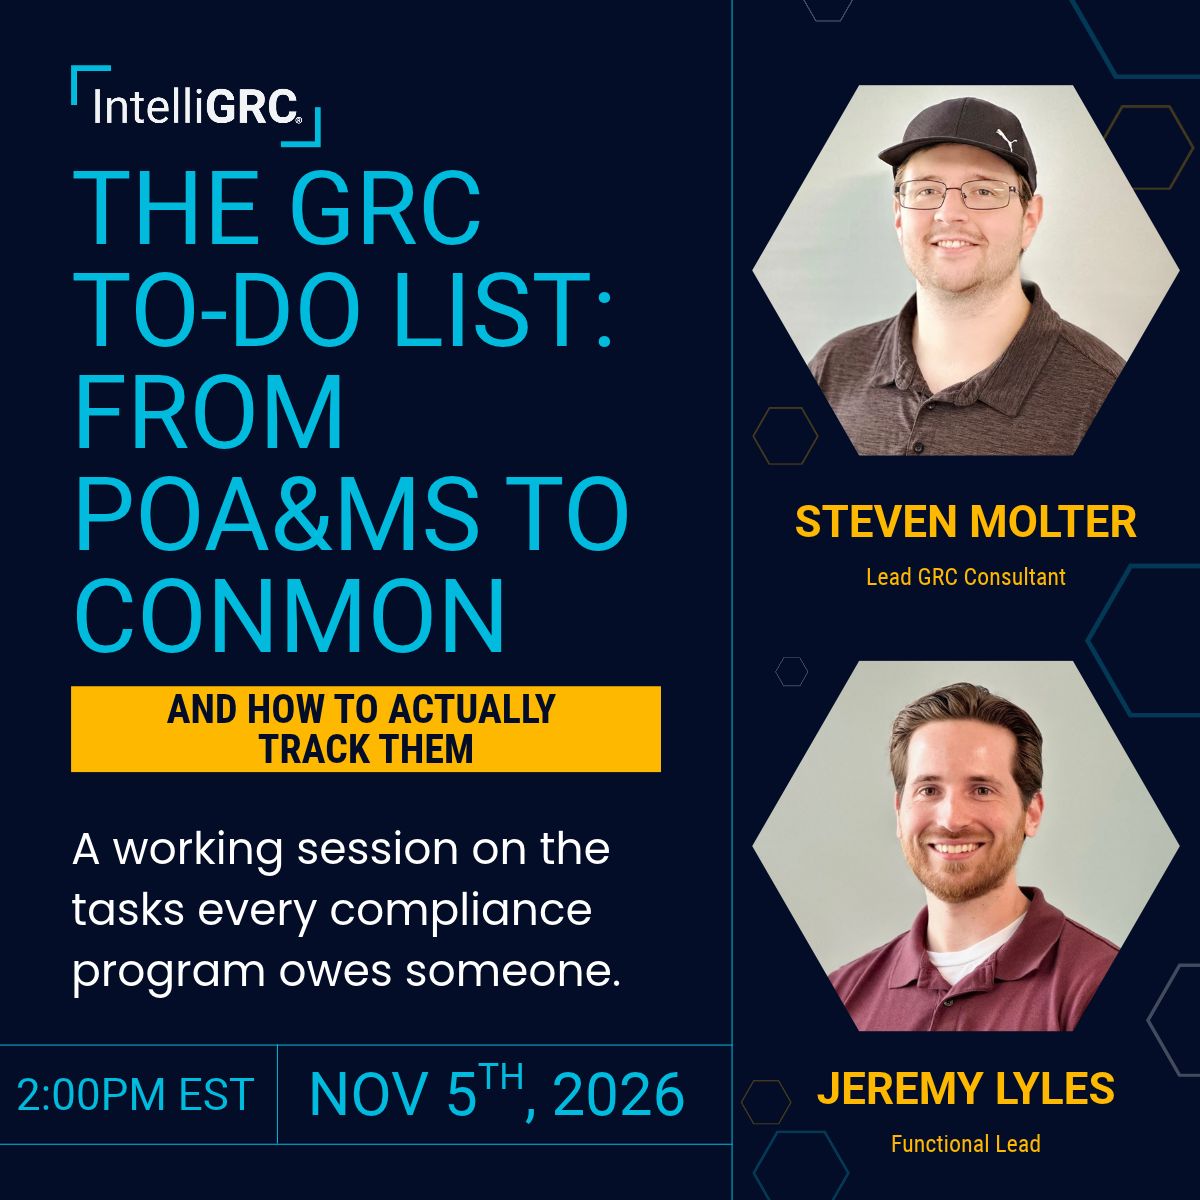
Every compliance program comes with a to-do list nobody hands you. Initial implementation POA&Ms. Post-assessment POA&Ms. Operational POAs under 3.12.2. ConMon activities. Evidence requests before your assessment. If you're tracking all of that in a spreadsheet, you're probably one missed row away from a finding. On November 5, join Steven Molter and Jeremy L. as they break down what separates each of these. Then watch as they go live in the IntelliGRC platform to show how to turn them into tracked, auditable action items with Action Plan and ConMon. You'll leave knowing what has to get done. And with a way to prove it got done. Thursday, Nov 5 | 2:00 to 3:00 PM ET Register here: https://hubs.li/Q04zsf500 #CMMC #NIST800171 #GRC #POAM #ContinuousMonitoring
- Nomios NetherlandsSince 9 Oct 2026
Veel organisaties hebben nog niet door hoe groot de impact van 47-daagse certificaten gaat worden. Wat begint als een wijziging in certificaatgeldigheid kan uitgroeien tot een operationele uitdaging voor IT- en securityteams... Hoe bereid je je organisatie hierop voor? In deze video leggen we uit waarom browserleveranciers deze verandering doorvoeren en wat dit betekent voor certificaatbeheer, security en continuïteit.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.